セキュリティレポートへ移動
このドメインは悪意のあるものとして報告されています
検出を報告するセキュリティ エンジン: 8。 一致を報告する公開ブロックリスト: 1。 細心の注意を払ってください — 資格情報や個人情報を入力しないでください。
ドメインのセキュリティと脅威インテリジェンス
cerrrwei.help のファビコン

cerrrwei.help

要点

cerrrwei.help:フィッシング。PhishDestroy が 2026-10-25 に検出しました。リスク:クリティカル(90/100)。レジストラ:NameSilo。ステータス:最後に確認されたアクティブな状態。ホスティング:Shenzhen Tencent Computer Systems Company Limited。PhishDestroy は1 件の不正利用報告を送信しました。VirusTotal:8/92 のエンジンが検出。認証情報を入力したり、ウォレットを接続したりしないでください。

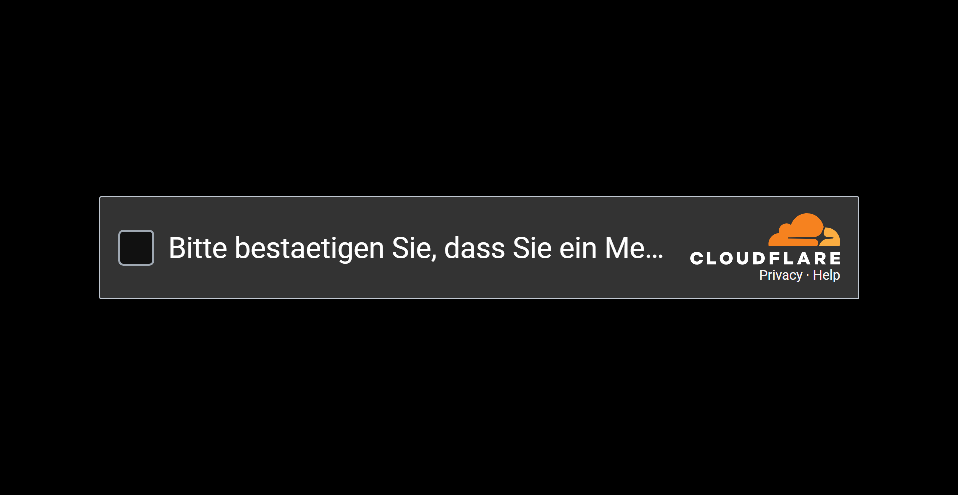
“Verify you are human”

レジストラ
NameSilo
Resolved IP
43.165.68.243
登録日
2026年10月18日
PhishDestroyの評価 クリティカル
可用性 最後に確認されたアクティブな状態 最新の保存された到達可能性の観測 確認日時 HTTP プローブ
VirusTotal 検出数: 8/92 保存されたブロックリストの一致: 1 若いドメイン: 7 日経過
VirusTotal
エンジンの検知 ·
OTX
コミュニティの参考資料
Cloudflare Radar
ページキャプチャ
ギャラリーを開く
ドメイン年齢
送信済み報告
タイムラインを表示
2026年10月25日 1 Report Sent
X Telegram API
レポート概要

フィッシング: cerrrwei.help — 最後に確認されたアクティブな状態 (HTTP 200). 証拠の概要: VirusTotal 8/92 (alphaMountain.ai, Emsisoft, Fortinet, Gridinsoft, Kaspersky); URLScan capture; 1…

元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。

分析

ドメインの概要

cerrrwei.help:フィッシング。PhishDestroy が 2026-10-25 に検出しました。リスク:クリティカル(90/100)。レジストラ:NameSilo。ステータス:最後に確認されたアクティブな状態。ホスティング:Shenzhen Tencent Computer Systems Company Limited。PhishDestroy は1 件の不正利用報告を送信しました。VirusTotal:8/92 のエンジンが検出。認証情報を入力したり、ウォレットを接続したりしないでください。

クリティカル
VirusTotal
8 / 92
ページキャプチャ
8

PhishDestroyの脅威レポート

Overview

PhishDestroy added cerrrwei.help to its internal blocklist on 2026-10-25 following an admin report that the domain was only six days old. The site responded with HTTP 200 and a page title of “Verify you are human”, but no substantive content was captured, leading the prior AI assessment to label the verdict as unknown. The first time PhishDestroy observed the domain was on the same date, 2026-10-25. No further activity has been recorded since that capture.

How the scam works

The detections associated with this domain indicate a phishing risk, meaning attackers could use a page that pretends to be a legitimate service to harvest credentials or personal data. Because the captured page contained only a human‑verification prompt, no specific credential‑collection form or malicious payload was observed. Consequently, the exact method of abuse cannot be confirmed for this site, only the general category of phishing remains possible.

証拠

VirusTotal scanned the domain on 2026-10-25 and reported 8 detections out of 92 engines, with 7 labeling it malicious and 1 as suspicious. Google Safe Browsing checked on the same day and did not flag the domain. OpenPhish listed the domain, and PhishDestroy’s own internal list also marks it as blocked. URLScan captured the site on 2026-10-25, its machine‑learning engine gave a malicious score of 98, though the overall verdict was clean. Cloudflare Radar on 2026-10-25 categorized the domain as phishing and malicious. OTX showed zero pulses for the domain.

インフラ

The domain was registered with NameSilo, LLC on 2026-10-18. The recorded IP was 43.165.68.243, belonging to ASN 132203 and listed as Shenzhen Tencent Computer Systems Company Limited in the United States. The site used a Let's Encrypt TLS certificate valid until 2027-01-17. Authoritative nameservers were ns1.dnsowl.com, ns2.dnsowl.com, and ns3.dnsowl.com.

What to do

Visitors should not enter any credentials, personal information, or download files from cerrrwei.help; if any data was submitted, change related passwords and monitor accounts for suspicious activity. Security teams should block the domain at the network perimeter and add it to threat‑intel feeds. Review web and DNS logs for any connections to 43.165.68.243 and investigate potential credential exposure. Continue to monitor the domain for any changes in behavior or additional detections.

ソース別の証拠VirusTotal 8 / 92 9 sources

VirusTotal

8 / 92 エンジンの検知 · 保存された要約

レポートを開く
VirusTotal取得元の元レコード確認日時: 14 項目

確認日時: · 取得日:

ベンダーごとの結果件数

タイムアウト
0
無害
50
悪意あり
7
不審な
1
未検出
34

ベンダーラベル

Webroot
malicious
Emsisoft
phishing
Fortinet
phishing
ネットクラフト
malicious
カスペルスキー
phishing
LevelBlue
phishing
Gridinsoft
suspicious
alphaMountain.ai
malicious

レピュテーションスコア

0

タグ

  • dga

レジストラ

NameSilo, LLC

作成日

有効期限

更新されました

初回確認

DNS レコード

  • TTL(秒)
    21600
    種類
    NS
    値
    ns3.dnsowl.com
  • TTL(秒)
    7207
    種類
    A
    値
    43.165.68.243
  • TTL(秒)
    21600
    種類
    NS
    値
    ns2.dnsowl.com
  • TTL(秒)
    21600
    種類
    NS
    値
    ns1.dnsowl.com
  • TTL(秒)
    21600
    種類
    SOA
    責任者のメールアドレス
    hostmaster.dnsowl.com
    値
    ns1.dnsowl.com

DNS レコードの取得日時

JARM フィンガープリント

40d40d40d00000000043d43d00043d6aff5ab0f4fc31897186312c9e639319

証明書

サブジェクト代替名(SAN)
  • cerrrwei.help
発行者
Let's Encrypt / YE1
シリアル番号
5ed172d764391391aed4b92e297d9a4aa4c
SHA-256
d633d8c32f8c0c6d830f44c5cec24dafabbe7af4c948f36a46551684147e3b12
サブジェクト
cerrrwei.help
有効期間の終了
有効期間の開始

登録記録

レジストラ
NameSilo, LLC
レジストラ IANA ID
1479
レジストラの URL
https://www.namesilo.com
登録日
更新されました
有効期限
ステータス
  • addPeriod
  • client
  • clientTransferProhibited
  • serverTransferProhibited
ネームサーバー
  • ns1.dnsowl.com
  • ns2.dnsowl.com
  • ns3.dnsowl.com
DNSSEC
unsigned
取得元の元フィールド · JSON
ベンダーごとの結果件数
{
    "timeout": 0,
    "harmless": 50,
    "malicious": 7,
    "suspicious": 1,
    "undetected": 34
}
ベンダーラベル
{
    "Webroot": "malicious",
    "Emsisoft": "phishing",
    "Fortinet": "phishing",
    "Netcraft": "malicious",
    "Kaspersky": "phishing",
    "LevelBlue": "phishing",
    "Gridinsoft": "suspicious",
    "alphaMountain.ai": "malicious"
}
評判
0
タグ
[
    "dga"
]
レジストラ
NameSilo, LLC
作成日
2026-10-18T17:52:28Z
有効期限
2027-10-18T23:59:59Z
更新されました
2026-10-18T17:52:32Z
初回確認
2026-10-19T02:36:20Z
DNS レコード
[
    {
        "ttl": 21600,
        "type": "NS",
        "value": "ns3.dnsowl.com"
    },
    {
        "ttl": 7207,
        "type": "A",
        "value": "43.165.68.243"
    },
    {
        "ttl": 21600,
        "type": "NS",
        "value": "ns2.dnsowl.com"
    },
    {
        "ttl": 21600,
        "type": "NS",
        "value": "ns1.dnsowl.com"
    },
    {
        "ttl": 21600,
        "type": "SOA",
        "rname": "hostmaster.dnsowl.com",
        "value": "ns1.dnsowl.com"
    }
]
Dns at
2026-10-25T00:52:43Z
Jarm
40d40d40d00000000043d43d00043d6aff5ab0f4fc31897186312c9e639319
証明書
{
    "san": [
        "cerrrwei.help"
    ],
    "issuer": "Let's Encrypt / YE1",
    "serial": "5ed172d764391391aed4b92e297d9a4aa4c",
    "sha256": "d633d8c32f8c0c6d830f44c5cec24dafabbe7af4c948f36a46551684147e3b12",
    "subject": "cerrrwei.help",
    "valid_to": "2027-01-17T01:34:01Z",
    "valid_from": "2026-10-19T01:34:02Z"
}
登録記録
{
    "registrar": "NameSilo, LLC",
    "registrar_iana_id": "1479",
    "registrar_url": "https://www.namesilo.com",
    "created": "2026-10-18T07:00:00Z",
    "updated": "2026-10-18T07:00:00Z",
    "expires": "2027-10-18T07:00:00Z",
    "status": [
        "addPeriod",
        "client",
        "clientTransferProhibited",
        "serverTransferProhibited"
    ],
    "nameservers": [
        "ns1.dnsowl.com",
        "ns2.dnsowl.com",
        "ns3.dnsowl.com"
    ],
    "dnssec": "unsigned"
}
個別のソースレコード · 7 malicious + 1 suspicious / 92 · 2026-10-25 00:52:01 UTC

上記の概要とこのプロバイダーの記録は、異なる時期に収集されたものです。どちらも引き続き閲覧可能であり、悪意のあるものと不審なものの分類は別々に表示されています。

record_source
collected_observations.vt
analysis_at
2026-10-25T00:52:01Z
fetched_at
2026-10-25T16:26:20Z
stats
{"timeout":0,"harmless":50,"malicious":7,"suspicious":1,"undetected":34}

Cloudflare Radar

フィッシング

レポートを開く
Cloudflare Radar取得元の元レコード確認日時: 14 項目

確認日時: · 取得日:

レポート ID

2cdb00d6-d216-4016-bc7f-8b06805a36dc

最終URL

https://cerrrwei.help/

HTTP レスポンス

200

遷移履歴

  • URL
    https://cerrrwei.help/
    ステータス
    200

DOM構造のハッシュ

7656b9b1f13f5f8d674a14c127722e9170fdbc4e0889f4581978d6cbfc3824fd

ドキュメントのハッシュ値

adebbd0e6a1c602b83d3ac29ccb4569b3e94cc61a5d35d6220dd47c42b28fbf4

フィッシング分類器の結果

  • phishing

ドメインのリスクカテゴリ

  • New Domains
  • Security Risks
  • フィッシング
  • Security threats
  • Newly Seen Domains
  • CIPA Filter
  • CIPA

Cloudflare Radar の順位

順位の範囲
>200000

DNS レコード

  • 名前
    cerrrwei.help
    種類
    A
    値
    43.165.68.243

DNSSEC の有効性

いいえ

IP アドレス

43.165.68.243

判定

タグ
  • phishing
悪意あり
はい
カテゴリー
  • phishing

登録記録

レジストラ
NameSilo, LLC
登録日
更新されました
有効期限
ネームサーバー
  • ns1.dnsowl.com
  • ns2.dnsowl.com
  • ns3.dnsowl.com
取得元の元フィールド · JSON
Uuid
2cdb00d6-d216-4016-bc7f-8b06805a36dc
Final url
https://cerrrwei.help/
ステータス
200
沿革
[
    {
        "url": "https://cerrrwei.help/",
        "status": 200
    }
]
DOM構造のハッシュ
7656b9b1f13f5f8d674a14c127722e9170fdbc4e0889f4581978d6cbfc3824fd
ドキュメントのハッシュ値
adebbd0e6a1c602b83d3ac29ccb4569b3e94cc61a5d35d6220dd47c42b28fbf4
Phishing v2
[
    "phishing"
]
ドメインのリスク
[
    "New Domains",
    "Security Risks",
    "Phishing",
    "Security threats",
    "Newly Seen Domains",
    "CIPA Filter",
    "CIPA"
]
Radar rank
{
    "bucket": ">200000"
}
DNS レコード
[
    {
        "name": "cerrrwei.help",
        "type": "A",
        "value": "43.165.68.243"
    }
]
DNSSEC 有効
false
Ip
43.165.68.243
判定
{
    "tags": [
        "phishing"
    ],
    "malicious": true,
    "categories": [
        "phishing"
    ]
}
登録記録
{
    "registrar": "NameSilo, LLC",
    "created": "2026-10-18T17:52:28Z",
    "updated": "2026-10-18T17:52:32Z",
    "expires": "2027-10-18T23:59:59Z",
    "nameservers": [
        "ns1.dnsowl.com",
        "ns2.dnsowl.com",
        "ns3.dnsowl.com"
    ]
}

URLScan

悪意あり · エンジン判定 · スコア 98

レポートを開く
URLScan取得元の元レコード確認日時: 19 項目

確認日時: · 取得日:

レポート ID

01a173eb-7054-7095-8427-c2485631733f

最終URL

https://cerrrwei.help/

HTTP レスポンス

200

リダイレクトの種類

https-only

リダイレクト

  • 転送先
    https://cerrrwei.help/
    転送元
    http://cerrrwei.help/
    ステータス
    307

IP アドレス

43.165.68.243

アクセスがあったIPアドレス

  • 43.165.68.243

自律システム(ASN)

  • 132203

サーバーの所在国

  • US

ドキュメントのハッシュ値

2ab490122b605116c393a0d2c5a91d10361a3879dce75ab8bebd3a4afbebcfce

クッキー

  • PHPSID

TLS セッションと証明書

サブジェクト代替名(SAN)
  • cerrrwei.help
暗号スイート
AES_128_GCM
発行者
YE1
サブジェクト
cerrrwei.help
プロトコル
TLS 1.3
有効期間の終了
有効期間の開始

ドメインの経過日数

5

登録ドメインの経過日数

5

証明書の経過日数

6

証明書の有効日数

89

ページのリクエスト数

2

プロバイダーの評決

エンジン判定
タグ
  • urlscan-ml
  • urlscan-ml-60c5e22
スコア
98
悪意あり
はい
総合判定
スコア
0
悪意あり
いいえ

HTTPヘッダー

サーバー
workerman
Content-type
text/html;charset=utf-8
X-frame-options
SAMEORIGIN
X-content-type-options
nosniff
Referrer-policy
strict-origin-when-cross-origin
取得元の元フィールド · JSON
Uuid
01a173eb-7054-7095-8427-c2485631733f
Final url
https://cerrrwei.help/
ステータス
200
リダイレクト
https-only
リダイレクト
[
    {
        "to": "https://cerrrwei.help/",
        "from": "http://cerrrwei.help/",
        "status": 307
    }
]
Ip
43.165.68.243
アクセスがあったIPアドレス
[
    "43.165.68.243"
]
Asns
[
    "132203"
]
Countries
[
    "US"
]
ドキュメントのハッシュ値
2ab490122b605116c393a0d2c5a91d10361a3879dce75ab8bebd3a4afbebcfce
クッキー
[
    "PHPSID"
]
Tls
{
    "san": [
        "cerrrwei.help"
    ],
    "cipher": "AES_128_GCM",
    "issuer": "YE1",
    "subject": "cerrrwei.help",
    "protocol": "TLS 1.3",
    "valid_to": "2027-01-17T01:34:01Z",
    "valid_from": "2026-10-19T01:34:02Z"
}
ドメイン年齢(日数)
5
Apex age days
5
Tls age days
6
TLS 有効日数
89
リクエスト
2
プロバイダーの評決
{
    "engines": {
        "tags": [
            "urlscan-ml",
            "urlscan-ml-60c5e22"
        ],
        "score": 98,
        "malicious": true
    },
    "overall": {
        "score": 0,
        "malicious": false
    }
}
HTTPヘッダー
{
    "server": "workerman",
    "content-type": "text/html;charset=utf-8",
    "x-frame-options": "SAMEORIGIN",
    "x-content-type-options": "nosniff",
    "referrer-policy": "strict-origin-when-cross-origin"
}
個別のモニター記録 · 日付は記録されていない

保存済みのモニターのスナップショットを個別に保持します。プライマリのレポートレコードを置き換えるものではなく、現在の可用性を確立するものでもありません。

record_source
domain_monitor.urlscan
uuid
01a17329-2b27-7652-8022-7d493af03c60
スコア
null
malicious
null
result_at
null
enriched_at
null
source_timestamps
{"urlscan_result_at":null,"urlscan_enriched_at":null}
timestamp_basis
既存のレポートで使用されている「Europe/Berlin」;ソースのタイムスタンプはそのまま保持されています

Spamhaus DBL

記録は確認済み。評決は保存されていない

レポートを開く

PhishDestroy DOM

88 / 100 · ヒューリスティックスコア · 0 brand references · 0 classifications

レポートを開く

PhishDestroyのストーリー

ナラティブ生成のメタデータ

レポートを開く
タイトル、説明、および生成記録

ナラティブの生成日は、観測日とは別ものです。これらは保存された公開フィールドであり、追加の独立した検出結果ではありません。

ai_title
cerrrwei.help — Suspicious Domain
ai_description
PhishDestroy flagged cerrrwei.help as a suspicious domain after it appeared with a generic “Verify you are human” page and multiple security‑engine detections.
ai_generated_at
2026-10-25T16:31:13Z
ai_generated_by
threat-v3-groq
interpretation
プロバイダーの観察日とは別の、ナラティブ生成メタデータ。

結果は各ソースの収集時点のものです。検出ゼロは安全性を保証しません。OTX の参照情報はコミュニティによる公開情報です。

収集したソースの詳細

保存されたページ、ネットワーク、スキャナーの観測結果を、ソースと観測時刻ごとにまとめています。

保存されたすべての項目と、その取得元・日時
ウェブサイトの確認取得元の元レコード取得日: 23 項目

メールの設定

SPF ルックアップ数
0

CAA レコード

ドメイン
cerrrwei.help

DNS保護の結果

確認したリゾルバー数
12
ブロック元
  • CloudFlare Family
ブロックしたリゾルバー数
1

ウェブアーカイブに関する所見

最終観測
最初の観測
記録された変更数
0
アーカイブ日数
1
平均ページサイズ(バイト)
8436

ページタイトルとメタデータ

ページタイトル
Verify you are human

トラッカー

リクエスト
1

フォームと混合コンテンツ

サードパーティスクリプト
0

HTTP レスポンス

到達可能
はい
HTTPステータス
200
リクエストの所要時間(ms)
DNS
16
TLS
119
待つ
133
接続
162
ダウンロード
102
応答時間(ms)
532

TLS接続

ALPN
h2
暗号スイート
TLS_AES_128_GCM_SHA256
プロトコル
TLSv1.3
対応バージョン
  • TLSv1.2
  • TLSv1.3
証明書の検証済み
はい
前方秘匿性
はい

ポート

開いているポート
  • 22
  • 80
  • 443
  • 8080

炭素排出量の推定

バイト
22882
CO₂(グラム)
0.0008
他ページより環境負荷が低い割合(%)
54

DNS サーバー

ネームサーバー
  • IP アドレス
    162.159.26.234
    ホスト
    ns3.dnsowl.com
  • IP アドレス
    162.159.26.136
    ホスト
    ns1.dnsowl.com
  • IP アドレス
    162.159.26.49
    ホスト
    ns2.dnsowl.com
DNS ゾーン
cerrrwei.help

クッキー

クッキー
  • 名前
    PHPSID
    HTTP-only
    はい

場所

IP アドレス
43.165.68.243
ASN
132203
組織
Shenzhen Tencent Computer Systems Company Limited
都市
Ashburn
国
US

TLS証明書

発行者
Let's Encrypt / YE1
サブジェクト
cerrrwei.help

DNS レコード

A
  • 43.165.68.243
NS
  • ns3.dnsowl.com
  • ns1.dnsowl.com
  • ns2.dnsowl.com
SOA
プライマリネームサーバー
ns1.dnsowl.com
ホストマスター
hostmaster.dnsowl.com
シリアル番号
1792350815
リフレッシュ(秒)
7200
リトライ(秒)
1800
失効(秒)
1209600
最小 TTL(秒)
600

DNSSEC

DS レコード
いいえ
RRSIG
いいえ
DNSKEY
いいえ

HSTS

観測結果
Site does not serve any HSTS headers.

HTTPセキュリティポリシー

X-Frame-Options
SAMEORIGIN
Referrer-Policy
strict-origin-when-cross-origin
X-XSS-Protection
いいえ
Permissions-Policy
いいえ
X-Content-Type-Options
nosniff
Content-Security-Policy
いいえ
Strict-Transport-Security
いいえ
Cross-Origin-Opener-Policy
いいえ
Cross-Origin-Embedder-Policy
いいえ
Cross-Origin-Resource-Policy
いいえ

IP 検索

IP アドレス
43.165.68.243
IP バージョン
4

リダイレクト

リダイレクトチェーン
  • https://cerrrwei.help

登録記録

レジストラ
NameSilo, LLC
登録日
更新されました
有効期限
ステータス
  • serverTransferProhibited https://icann.org/epp
  • clientTransferProhibited https://icann.org/epp
ネームサーバー
  • ns1.dnsowl.com
  • ns2.dnsowl.com
  • ns3.dnsowl.com

HTTPヘッダー

レスポンスヘッダー
サーバー
workerman
Content-type
text/html;charset=utf-8
X-frame-options
SAMEORIGIN
X-content-type-options
nosniff
Referrer-policy
strict-origin-when-cross-origin
取得元の元フィールド · JSON
メールの設定
{
    "spf_lookups": 0
}
CAA レコード
{
    "domain": "cerrrwei.help"
}
DNS保護の結果
{
    "resolvers": 12,
    "blocked_by": [
        "CloudFlare Family"
    ],
    "blocked_count": 1
}
ウェブアーカイブに関する所見
{
    "last": "2026-10-25T16:23:17Z",
    "first": "2026-10-25T16:23:17Z",
    "changes": 0,
    "days_archived": 1,
    "avg_page_bytes": 8436
}
ページタイトルとメタデータ
{
    "title": "Verify you are human"
}
トラッカー
{
    "requests": 1
}
フォームと混合コンテンツ
{
    "third_party_scripts": 0
}
ステータス
{
    "up": true,
    "code": 200,
    "timings": {
        "dns": 16,
        "tls": 119,
        "wait": 133,
        "connect": 162,
        "download": 102
    },
    "response_ms": 532
}
TLS接続
{
    "alpn": "h2",
    "cipher": "TLS_AES_128_GCM_SHA256",
    "protocol": "TLSv1.3",
    "versions": [
        "TLSv1.2",
        "TLSv1.3"
    ],
    "authorized": true,
    "forward_secrecy": true
}
ポート
{
    "open": [
        22,
        80,
        443,
        8080
    ]
}
Carbon
{
    "bytes": 22882,
    "co2_grams": 0.0008,
    "cleaner_than": 54
}
DNSサーバー
{
    "ns": [
        {
            "ip": "162.159.26.234",
            "host": "ns3.dnsowl.com"
        },
        {
            "ip": "162.159.26.136",
            "host": "ns1.dnsowl.com"
        },
        {
            "ip": "162.159.26.49",
            "host": "ns2.dnsowl.com"
        }
    ],
    "zone": "cerrrwei.help"
}
クッキー
{
    "cookies": [
        {
            "name": "PHPSID",
            "http_only": true
        }
    ]
}
場所
{
    "ip": "43.165.68.243",
    "asn": "132203",
    "org": "Shenzhen Tencent Computer Systems Company Limited",
    "city": "Ashburn",
    "country": "US"
}
SSL
{
    "issuer": "Let's Encrypt / YE1",
    "subject": "cerrrwei.help"
}
DNS レコード
{
    "A": [
        "43.165.68.243"
    ],
    "NS": [
        "ns3.dnsowl.com",
        "ns1.dnsowl.com",
        "ns2.dnsowl.com"
    ],
    "SOA": "{\"nsname\": \"ns1.dnsowl.com\", \"hostmaster\": \"hostmaster.dnsowl.com\", \"serial\": 1792350815, \"refresh\": 7200, \"retry\": 1800, \"expire\": 1209600, \"minttl\": 600}"
}
DNSsec
{
    "ds": false,
    "rrsig": false,
    "dnskey": false
}
Hsts
{
    "message": "Site does not serve any HSTS headers."
}
HTTPセキュリティポリシー
{
    "xFrameOptions": "SAMEORIGIN",
    "referrerPolicy": "strict-origin-when-cross-origin",
    "xXSSProtection": false,
    "permissionsPolicy": false,
    "xContentTypeOptions": "nosniff",
    "contentSecurityPolicy": false,
    "strictTransportPolicy": false,
    "crossOriginOpenerPolicy": false,
    "crossOriginEmbedderPolicy": false,
    "crossOriginResourcePolicy": false
}
Get ip
{
    "ip": "43.165.68.243",
    "family": 4
}
リダイレクト
{
    "chain": [
        "https://cerrrwei.help"
    ]
}
登録記録
{
    "registrar": "NameSilo, LLC",
    "created": "2026-10-18T17:52:28Z",
    "updated": "2026-10-18T17:52:32Z",
    "expires": "2027-10-18T23:59:59Z",
    "status": [
        "serverTransferProhibited https://icann.org/epp",
        "clientTransferProhibited https://icann.org/epp"
    ],
    "nameservers": [
        "ns1.dnsowl.com",
        "ns2.dnsowl.com",
        "ns3.dnsowl.com"
    ]
}
HTTPヘッダー
{
    "headers": {
        "server": "workerman",
        "content-type": "text/html;charset=utf-8",
        "x-frame-options": "SAMEORIGIN",
        "x-content-type-options": "nosniff",
        "referrer-policy": "strict-origin-when-cross-origin"
    }
}
ネットワークセキュリティインテリジェンス レジストラの背景情報
レジストラの背景情報 NameSilo
Stored registration data identifies NameSilo as the registrar. PhishDestroy maintains separate registrar investigations; that broader material is contextual and is not an independent detection for this domain.
Review source investigation
CF Cloudflare Radar Verdict 悪意あり
Security threats Security Risks フィッシング フィッシング New Domains

cerrrwei.help についての質問

cerrrwei.help は正規のサイトですか?

いいえ。PhishDestroy は cerrrwei.help を「フィッシング」に分類しています(リスク:クリティカル、90/100)。初回検出は 2026-10-25 です。VirusTotal:8/92 のエンジンが検出。安全でないサイトとして扱ってください。

cerrrwei.help にウォレットを接続しても安全ですか?

いいえ。cerrrwei.help でウォレットを接続したり、メッセージに署名したり、トークンを承認したりしないでください。フィッシングサイトは運営者があなたの資産を移動できる承認(approve、setApprovalForAll、Permit2)を求め、確定した取引は取り消せません。

cerrrwei.help を利用してしまった場合はどうすればよいですか?

そこで入力したパスワードをすべて変更し、二要素認証を有効にしてください。ウォレットを接続したり署名したりした場合は、承認を取り消し、残りの資金を新しいウォレットに移してください。シードフレーズは決して共有しないでください。手順ガイド:緊急対応ガイド。

関連情報

ブロックリストの一致OpenPhish · PhishDestroy 2
OpenPhish 掲載あり ソースを表示
PhishDestroy PhishDestroy list ソースを表示

最終確認

保存済みキャプチャ · 8 件のキャプチャ

すべてのキャプチャリンクとハッシュ (8)
検出されたページタイトル
Verify you are human
TLS証明書
発行者 Let's Encrypt / YE1 · 保存された有効期限まで残り 83 日

ドメインの詳細

ドメイン
IPレピュテーション 不正利用スコア 0/100 0 reports checked 2026年10月25日
レジストラ NameSilo US(US) PhishDestroyに関する調査
不正利用連絡先abuse@tencent.com, abuse@namesilo.com
ICANNレジストリICANN Lookup (RDAP) →
ホスティング事業者の不正利用窓口 abuse@tencent.com Shenzhen Tencent Computer Systems Company Limited · AS132203
登録情報作成日 2026年10月18日 (7d · Very New!) — 有効期限 2027年10月18日
HTTPステータス200
技術詳細出所とタイムスタンプ
初確認2026年10月25日
DOM解析analyzed 2026年10月25日score 88/100
送信されたURLhttp://cerrrwei.help/
ファビコン・ハッシュ
ケース ID
ICANN OVERSIGHT

認定と RAA の背景

レジストラの認定と DNS 不正利用対策の義務

この gTLD では、上記のレジストラは ICANN の認定契約に基づいて運営されています。以下のリンクから、公式の料金表と現行の DNS 不正利用に関するコンプライアンスガイダンスを確認できます。

認定は契約であり、安全性の認証ではありません。

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft 自動送信は一切行われません。

ネットワーク & 証明書

保存済みの技術的証拠

ネットワーク & DNS

Resolved IP
43.165.68.243
ネットワーク ASN
AS132203
組織
Shenzhen Tencent Computer Systems Company Limited
観測地点
Ashburn, US
サーバーヘッダー
workerman

ネームサーバー 3

  • ns1.dnsowl.com
  • ns2.dnsowl.com
  • ns3.dnsowl.com

所在地は IP ネットワークの位置を示します。

TLS証明書

発行者
Let's Encrypt / YE1
有効期間の開始
2026-10-19 01:34:02
有効期間の終了
2027-01-17 01:34:01
ホスト名の対象範囲
保存された証明書の日付は有効
有効期間
保存された有効期間内
収集元
PhishDestroy collector
証明書のフィンガープリントd633d8c32f8c0c6d830f44c5cec24dafabbe7af4c948f36a46551684147e3b12
証明書の名前 · 1 件の SAN
  • cerrrwei.help

保存された証明書のメタデータです。タイムゾーンのない証明書の日付は、保存時の値のまま表示しています。通信の暗号化は、サイトが信頼できることを示すものではありません。

使用技術 · 2 identified
検出元: Cloudflare Radar ・Wappalyzerエンジン
このドメインを報告する 証拠を提出し、他の人を守る手助けをしましょう

VirusTotalによる分析

8 / 92 セキュリティ ベンダーがこのドメインにフラグを立てました
VT で表示
最終分析
alphaMountain.ai
Emsisoft
Fortinet
Gridinsoft
カスペルスキー
LevelBlue
ネットクラフト
Webroot

アーカイブ済み証拠

Wayback Machineのスナップショット
アーカイブを表示
サイトパフォーマンス分析

Google PageSpeed Insights — 次のドメインのモバイルパフォーマンス監査: cerrrwei.help · checked Oct 25, 2026

100
良い
パフォーマンス
FCP
0.76 s
First Contentful Paint
LCP
0.76 s
Largest Contentful Paint
CLS
0
累積レイアウトシフト
TBT
0 ms
総ブロック時間
SI
0.76 s
スピード指数
データ提供: Google PageSpeed Insights ・モバイル戦略 ・スコア: 90~100 良好 50~89 改善の余地あり 0~49 低
保存済みキャプチャの証拠 1 snapshot

ローカル収集パイプラインが保持している、タイムスタンプ付きのレスポンスメタデータです。以下の各値は、表示されているアーカイブ時刻のものです。

アーカイブされたHTTPレスポンス HTTP 200
リクエストされたURL: http://cerrrwei.help/
Verify you are human
対応
HTTP 200
HTMLのbody要素
22.3 KB
圧縮済み
7.1 KB
リンク
0 internal · 0 external
選択されたレスポンスヘッダー
Content-Encoding: gzip
Content-Type: text/html;charset=utf-8
サーバー: workerman
HSTS:観測されず DNSSEC:観測されず WAF / firewall: observed クローキングフラグ:観測されず
ファビコンのフィンガープリント: b33fdf4b3658410bbba8cf05720431d2bd1ce1e0ee7fc1cd04b4e85f4dc5b619
Saved response-header values · 11
Access-Control-Allow-Credentials
true
Access-Control-Allow-Headers
*
Access-Control-Allow-Methods
*
Access-Control-Allow-Origin
*
Content-Encoding
gzip
Content-Type
text/html;charset=utf-8
日付
Sun, 25 Oct 2026 16:22:33 GMT
サーバー
workerman
Transfer-Encoding
chunked
Vary
Accept-Encoding
Via
1.1 Caddy

コレクターが保持している値です。長い値は収集時に短縮されている場合があります。

保存済みの観測履歴1

モニターと各ソースのコレクターが保持している、日付付きの変更履歴です。新しい観測から順に表示されます。ソースの状態はテイクダウンの証明ではありません。

  1. ドメイン監視 · 最初の収集記録

    到達可能

保存されたすべての可用性観測データ3

出典:可用性モニター。保持されている観測データはすべて個別に扱われます。これには、日付やエビデンスハッシュが同じであっても、ソースやDNSの状態が異なるレコードも含まれます。状態が「不明」であるからといって、そのサイトがオフラインであるとは限りません。

  1. current_state_backfillunknown
    Observation source
    current_state_backfill
    原因
    http_2xx_unclassified
    Availability state
    unknown
    Content state
    unknown
    DNS state
    stale
    記録されたHTTPステータス
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    40
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    元のソースのタイムスタンプ
    2026-10-25 17:37:50.000000
    証拠の SHA-256
    b94359cfb326f61bc06651d28c5e858dd61319098902adad3415abe4380aab8e
    HTTP probe value as recorded
    200
    Evidence timestamp as recorded
    2026-10-25 17:37:50
    Evidence reason
  2. http_observationunknown
    Observation source
    http_observation
    原因
    http_2xx_unclassified
    Availability state
    unknown
    Content state
    unknown
    DNS state
    unknown
    記録されたHTTPステータス
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    40
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    元のソースのタイムスタンプ
    2026-10-25 17:37:50.000000
    証拠の SHA-256
    b94359cfb326f61bc06651d28c5e858dd61319098902adad3415abe4380aab8e
    HTTP probe value as recorded
    200
    Evidence timestamp as recorded
    2026-10-25 17:37:50
    Evidence reason
  3. current_state_backfillunknown
    Observation source
    current_state_backfill
    原因
    stale_current_evidence
    Availability state
    unknown
    Content state
    unknown
    DNS state
    stale
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    0
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    元のソースのタイムスタンプ
    2026-10-25 17:29:19.030122
    証拠の SHA-256
    f3049ef8aa957a0c75d1f37b703ae6008630522768f5aca88bbd9915c9e1400b
    DNS evidence marked stale
    true
    HTTP evidence marked stale
    true

記録されたアクティビティ

6 entries
  1. 不正利用報告が送信されました

    PD-20261025-AC6E18

    abuse@tencent.com
  2. URLScan

    ページのスクリーンショット

    ソースを表示
  3. Cloudflare Radar

    フィッシング

    ソースを表示
  4. VirusTotal

    8/92 エンジンの検知

    ソースを表示
  5. ウェイバック・マシン

    ページのアーカイブ

    ソースを表示
  6. PhishDestroy に登録

    cerrrwei.help

    ソースを表示
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

クローキングの確認

ブラウザとクローラーが受け取る内容を比較し、Keitaro によるトラフィック振り分けの有無を確認します。

cerrrwei.help

証拠および外部報告書

送信済み証拠のスナップショット
送信日時: 台帳レコード: 1 ケースID: PD-20261025-AC6E18 宛先: abuse@tencent.com
生成されたPDF通知 Notice text archived (859 chars)
事業者に送信した不正利用通知の本文
AUP & Terms of Service Violations:
Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices.
Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension.
Applicable Legal Framework (US):
18 U.S.C. § 1343 - Wire Fraud
18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA)
15 U.S.C. § 45 - FTC Act (Deceptive Practices)
Federal laws prohibit wire fraud, computer fraud, and deceptive business practices.
Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
詳細な分析
ヘルプと報告

このサイトによって何か影響を受けましたか?

5 件の証拠シグナルグループを関連付け済み 1 件の保存済み通知記録 最後に確認されたアクティブな状態
あなたは一人ではありません。恥ずかしいことは何もありません。 詐欺師は信頼につけ込む巧妙な犯罪者です。被害を報告することは詐欺に対抗する最も強力な手段です。あなたの報告が、他の人が被害に遭うのを防ぎ、捜査機関の対応を後押しします。 沈黙こそ詐欺師にとって最大の武器です。 沈黙を破りましょう。
認証情報が漏えいした場合は、すぐに報告してください。 被害回復をうたう詐欺業者とは関わらないでください。

アカウント資格情報、個人情報、支払い情報を入力した場合、またはこのドメインからファイルをダウンロードした場合は、すぐに対処してください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。

公式の報告ルート

お住まいの地域の当局へ報告してください

サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。

97か国のディレクトリ

AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます

自分で確認して送信する
フィッシング被害発生後

被害者への推奨事項とアドバイス

共有してしまった情報に応じて、該当する手順を選んでください。このレポートの写しを、ご自身の記録と一緒に保管してください。

今すぐ何をすべきでしょうか?

至急

不審なサイトの利用を中止してください。正規のサービスには、公式アプリか、すでに信頼しているアドレスからアクセスしてください。

  • すべてのパスワードを変更する — メール、Exchangeアカウントなど、同じパスワードを使用しているものすべて
  • 2段階認証を有効にする 認証アプリ(SMSではない)を使用する。SMSによる復旧機能を無効にする
  • カードの凍結 フィッシングサイトに銀行口座情報を入力してしまった場合

レポート作成のために、どのような情報を収集すべきでしょうか?

FBIのガイドライン

元のメール、領収書、メッセージ、スクリーンショットを安全な場所に保管してください。事実に基づく時系列があると、受理する機関が状況を把握しやすくなります。 IC3の証拠に関するガイダンス ↗

  • 支払い記録 — お支払いをされた場合は、領収書、金額、日付、決済業者、および受取人の詳細を保管しておいてください。
  • 正確な日時 — 各取引および詐欺師との最初の接触について
  • スクリーンショット — 詐欺サイト、チャットメッセージ、メール、ウォレットでの取引、ソーシャルメディア
  • すべてのURLおよびドメイン 詐欺師が使用した(以下を含む) cerrrwei.help)
  • コミュニケーション — 詐欺師が使用したメール、テキストメッセージ、電話番号、ユーザー名

たとえすべての詳細がわかっていなくても―― とにかく報告を提出する. 不完全な情報であっても、捜査には役立つ。

この詐欺はどこに通報すればいいですか?

  • FBI IC3 — インターネット犯罪通報センター(米国連邦政府の通報窓口)
  • ユーロポール — 欧州におけるサイバー犯罪の報告(EU)
  • ご利用の銀行または決済サービス事業者 — 金銭やカード情報が漏洩した場合は、公式の連絡先を通じて速やかに同社の不正対策チームに連絡してください。
  • 地元の警察 — たとえ直ちに行動を起こせなくても、公式な記録が残される

報告したからといって、被害の回復や捜査が保証されるわけではありません。しかし、迅速かつ正確な取引データは、当局やサービス事業者がインシデントを追跡する助けになります。

How do phishing scams typically work?

  • 偽のウェブサイト — 正規サイトのドメインをわずかに変更した、ピクセル単位で完璧に再現されたクローンサイト
  • pig butchering — TelegramやWhatsApp、出会い系アプリを通じて数週間にわたって信頼関係を築き、その後、金銭をだまし取られる
  • 詐欺による金銭の返還を装った詐欺 — 詐欺師が資金回収業者を装い、前払い手数料を要求します。業者を独自に確認するまでは、シードフレーズを教えたり支払ったりしないでください
  • AIを利用した詐欺 — ディープフェイク、自動化されたフィッシング、AI生成サイトにより、詐欺の発見が難しくなっている

今後、どうすれば身を守ることができるでしょうか?

  • 公式サイトをブックマークする — メール、DM、広告に含まれるリンクは絶対にクリックしないでください
  • ドメインの確認 — 確認する PhishDestroy 操作を行う前に、HTTPS、スペル、ドメインの登録期間を確認してください。
  • 「良すぎて怪しい」=詐欺 — 確実なリターン、有名人の推薦、差し迫った締め切り

その他のガイダンス: NIST・フィッシングへの対応FBI IC3 · 報告および証拠FTC・返金詐欺

最新情報を入手し、安全を確保しましょう

リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください

復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 回復詐欺について詳しくはこちら →
このレポートについてソース、観測日、訂正

このレポートは、保存されたページキャプチャ、登録・ネットワーク記録、スキャナーの結果、PhishDestroy の報告履歴をまとめたものです。各ソースにはそれぞれの観測日が保持されています。元の結果を確認するには、各ソースのレポートを開いてください。

AI 支援による分析の作成日時: . これは当時入手可能だった証拠について述べたものであり、その後の情報源の確認によって内容が変更される可能性があります。

キャプチャは、表示されていた内容を記録したものです。スキャナーの結果は、チェック時点におけるその提供元の評価を記録したものです。有効な証明書も、検出ゼロの結果も、安全性を保証するものではありません。

このレポートを埋め込む証拠へのリンク付きのコンパクトなウィジェット
HTML · IFRAME

このレポートを埋め込む

この脅威情報を、ご自身のウェブサイトやブログで共有してください

embed.html
<iframe
  src="https://phishdestroy.io/ja/embed/domain/cerrrwei.help"
  title="PhishDestroy threat report for cerrrwei.help"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>