This site mimics Booking.com to collect stay details and reservation numbers through a fake refund form, and 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it. Close the tab immediately and do not submit any personal or travel information.
元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Page layout and booking cancellation lure
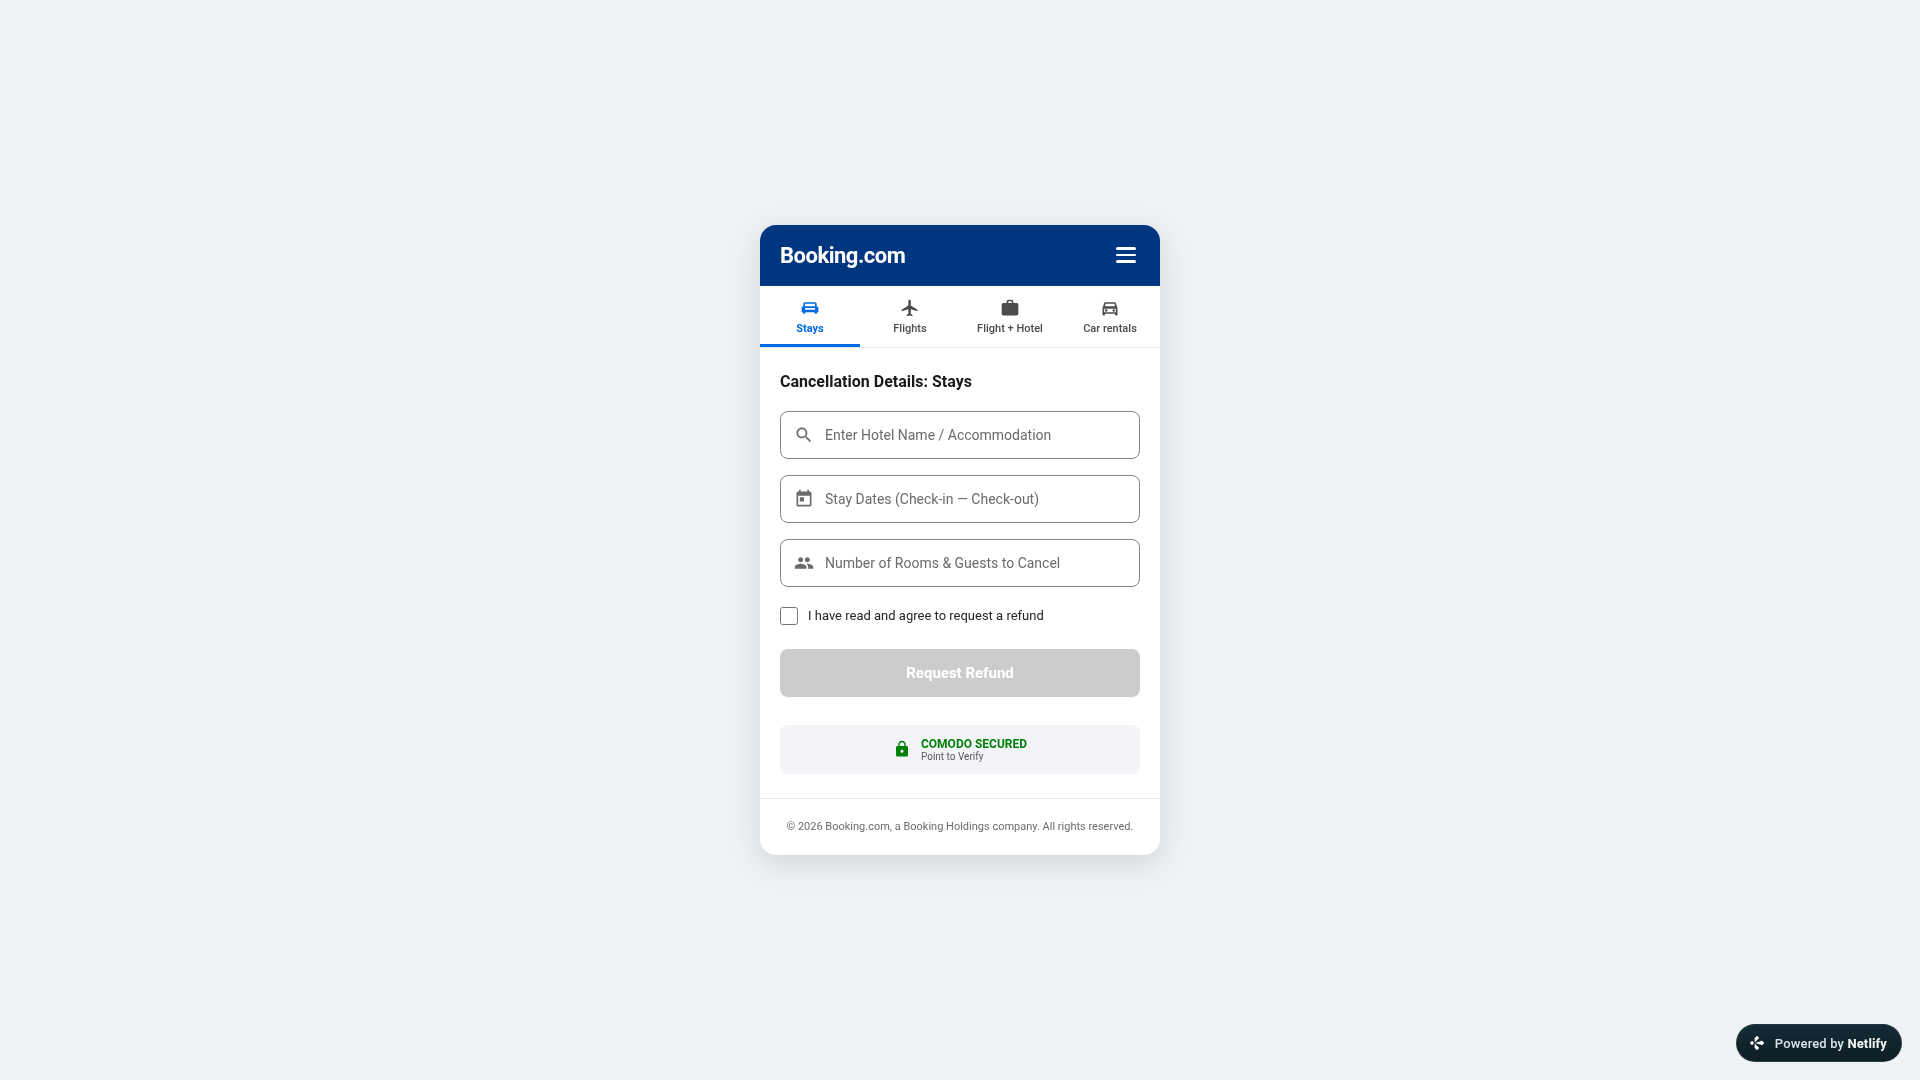
The page replicates the Booking.com interface using the brand's dark blue header and navigation icons for Stays, Flights, Flight + Hotel, and Car rentals. Below the navigation, the main heading reads "Cancellation Details: Stays" accompanied by form fields labeled "Enter Hotel Name / Accommodation", "Stay Dates (Check-in — Check-out)", and "Number of Rooms & Guests to Cancel". A checkbox states "I have read and agree to request a refund" above a grey "Request Refund" button. At the bottom, a badge displays "COMODO SECURED Point to Verify" alongside a copyright notice referencing Booking Holdings company. The address buat-laporan-bookingcom.netlify.app runs on netlify.app rather than the legitimate Booking.com infrastructure. 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it. Security vendors such as Kaspersky, ESET and BitDefender flag the URL as malicious, and its PhishDestroy evidence score is 75/100 (critical). Because the site still answered requests on 21 Nov 2026 at 18:36 UTC, visitors continue to encounter the active form.
Risks of entering reservation details
Fraudsters typically use this travel data to orchestrate secondary phishing calls or emails pretending to be customer support. Submitting credentials or reservation codes lets attackers manipulate bookings or extract further personal data.
Recommended precautions for visitors
If you visited this page, close the tab immediately and do not enter any reservation numbers or personal data. Always manage your bookings directly through the official Booking.com mobile app or by typing the genuine domain into your browser. If you already submitted information, contact your bank or travel provider to secure your account.
buat-laporan-bookingcom.netlify.app mimics Booking.com to collect stay details through a fake refund form, flagged by 19 VirusTotal engines, close the tab.
AIによる要約
Page layout and booking cancellation lure The page replicates the Booking.com interface using the brand's dark blue header and navigation icons for Stays, Flights, Flight + Hotel, and Car rentals. Below the navigation, the main heading reads "Cancellation Details: Stays" accompanied by form fields labeled "Enter Hotel Name / Accommodation", "Stay Dates (Check-in — Check-out)", and "Number of Rooms & Guests to Cancel". A checkbox states "I have read and agree to request a refund" above a grey "Request Refund" button. At the bottom, a badge displays "COMODO SECURED Point to Verify" alongside a copyright notice referencing Booking Holdings company. The address buat-laporan-bookingcom.netlify.app runs on netlify.app rather than the legitimate Booking.com infrastructure. 19 of 92 engines on VirusTotal flagged it on 21 Nov 2026, and PhishFeed blocks it. Security vendors such as Kaspersky, ESET and BitDefender flag the URL as malicious, and its PhishDestroy evidence score is 75/100 (critical). Because the site still answered requests on 21 Nov 2026 at 18:36 UTC, visitors continue to encounter the active form. Risks of entering reservation details Fraudsters typically use this travel data to orchestrate secondary phishing calls or emails pretending to be customer support. Submitting credentials or reservation codes lets attackers manipulate bookings or extract further personal data. Recommended precautions for visitors If you visited this page, close the tab immediately and do not enter any reservation numbers or personal data. Always manage your bookings directly through the official Booking.com mobile app or by typing the genuine domain into your browser. If you already submitted information, contact your bank or travel provider to secure your account.
エビデンスレイヤーAvailability: Content servingContent: Content served at rootDNS: Stale
最新のHTTP観測結果コンテンツ公開中通常のHTTPコンテンツが配信される90%2026-11-22 11:59 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:59 UTClast content: 2026-11-22 11:59 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 2 identified
N
Netlify
PaaSCDN
Netlify providers hosting and server-less backend services for web applications and static websites.

 63.176.8.218


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT