元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
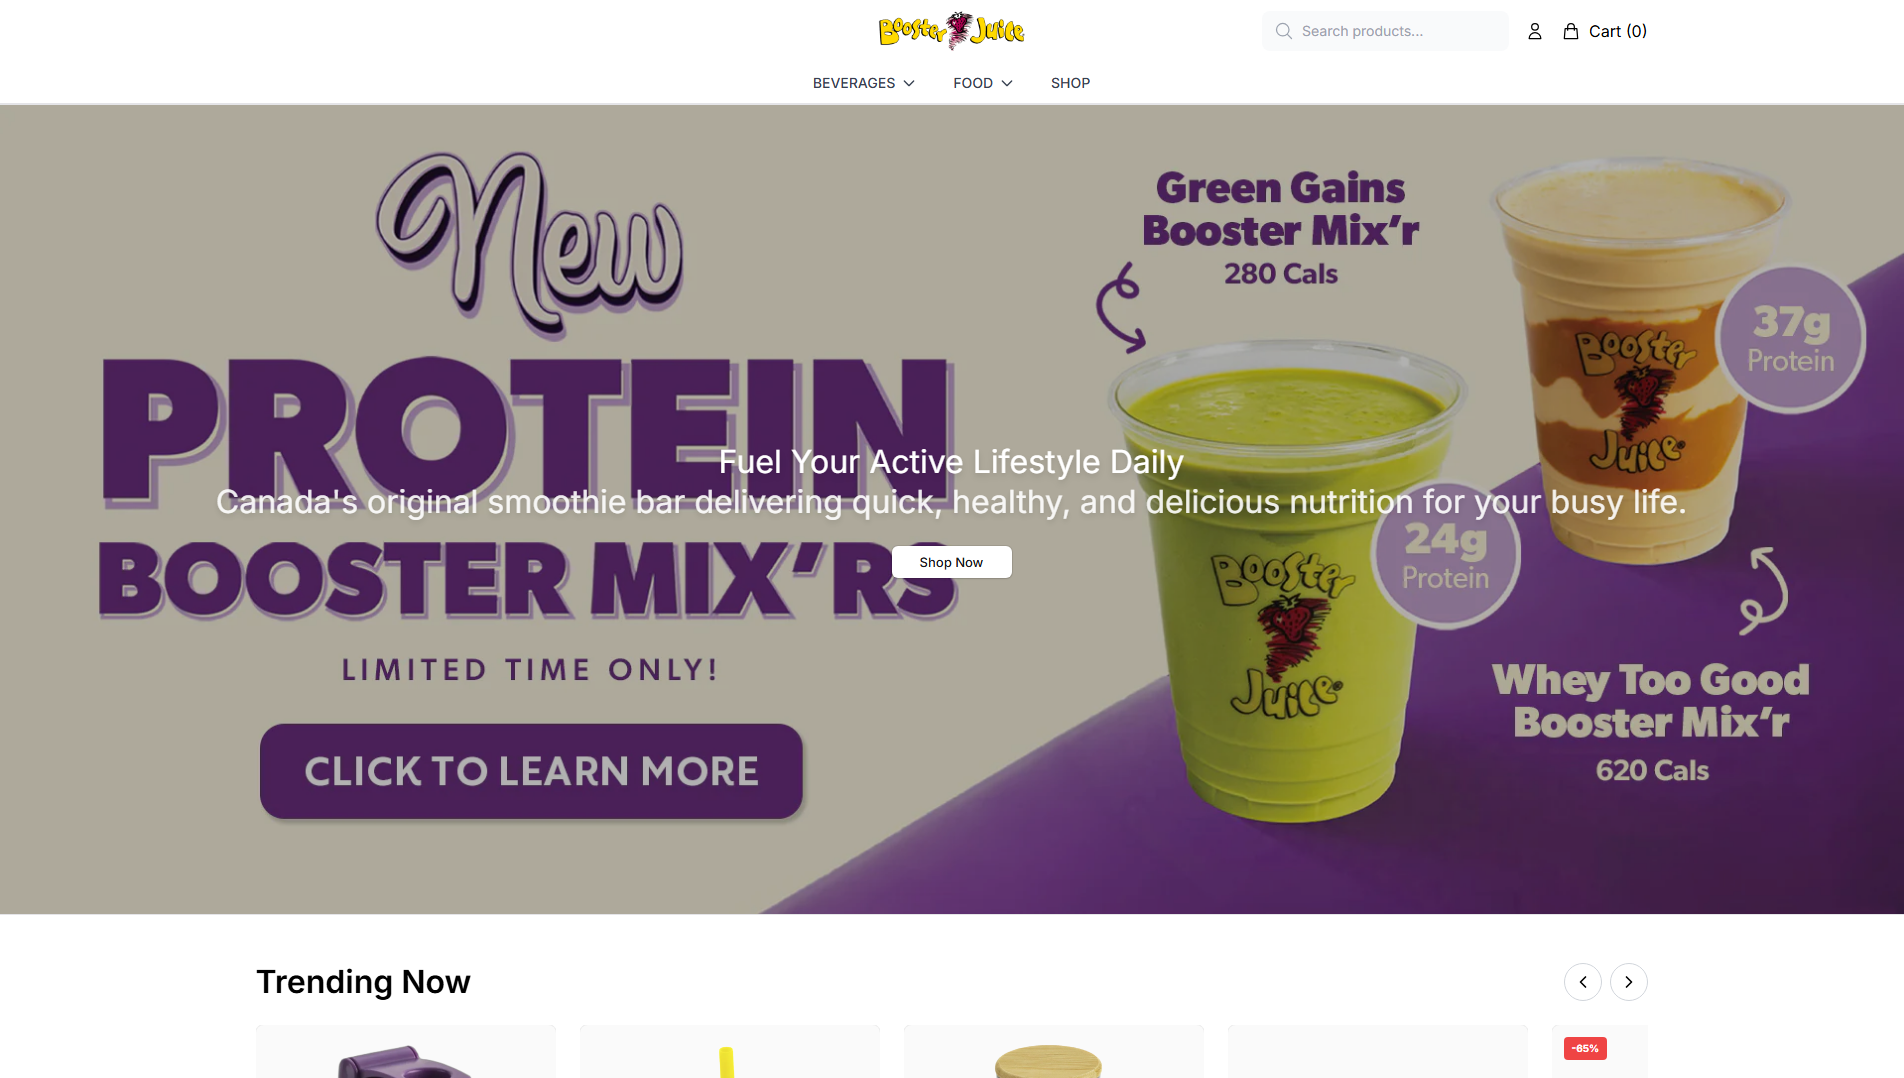
PhishDestroy added boosterjuicefresh.shop to its internal malicious list after its intake system detected brand impersonation and a fake‑store layout. The intake assessment observed a page header reading “Booster Juice Canada” together with product listings and deep‑discount prices, which do not match any official Booster Juice site. The domain was first seen by PhishDestroy on 2026-10-27, returning HTTP 200 after a 307 redirect from http to https.
詐欺の手口
Fake‑store scams copy the visual identity of a well‑known brand and advertise goods at unreal discounts to trick visitors into submitting payment details, personal information or credentials, which can then be used for fraud or credential stuffing.
証拠
VirusTotal scanned the domain on 2026-10-11 (retrieved 2026-10-27) and reported two detections out of 92 engines: LevelBlue marked it malicious and Gridinsoft flagged it as suspicious. Google Safe Browsing checked on 2026-10-27 and did not flag the URL. urlscan.io analysis on 2026-10-27 gave a malicious verdict with a score of 100, categorising the page as phishing and labeling it a fake shop. OTX listed four pulses referencing the domain as of 2026-10-27. No external blocklists reported the domain, while PhishDestroy’s internal list marks it malicious.
インフラ
The domain is 152 days old and resolves to IP 162.222.90.203 (ASN 199242, Malakmadze Web LLC, Georgia). It uses Cloudflare nameservers emerson.ns.cloudflare.com and irma.ns.cloudflare.com. TLS is provided by Let’s Encrypt, valid from 2026-09-24 to 2026-12-23. Open ports observed were 22, 80, 443 and 8000.
What to do
Visitors should not enter credentials or payment information on the site; anyone who has already done so should change related passwords and monitor financial accounts for unauthorized activity. Defenders can add boosterjuicefresh.shop to phishing denial lists and block the exact domain in web filters, and should review access logs for any requests to this host.
PhishDestroy flagged boosterjuicefresh.shop as a fake‑store impersonating Booster Juice, citing brand misuse and phishing signals from VirusTotal and urlscan.
AIによる要約
Overview PhishDestroy added boosterjuicefresh.shop to its internal malicious list after its intake system detected brand impersonation and a fake‑store layout. The intake assessment observed a page header reading “Booster Juice Canada” together with product listings and deep‑discount prices, which do not match any official Booster Juice site. The domain was first seen by PhishDestroy on 2026-10-27, returning HTTP 200 after a 307 redirect from http to https. How the scam works Fake‑store scams copy the visual identity of a well‑known brand and advertise goods at unreal discounts to trick visitors into submitting payment details, personal information or credentials, which can then be used for fraud or credential stuffing. Evidence VirusTotal scanned the domain on 2026-10-11 (retrieved 2026-10-27) and reported two detections out of 92 engines: LevelBlue marked it malicious and Gridinsoft flagged it as suspicious. Google Safe Browsing checked on 2026-10-27 and did not flag the URL. urlscan.io analysis on 2026-10-27 gave a malicious verdict with a score of 100, categorising the page as phishing and labeling it a fake shop. OTX listed four pulses referencing the domain as of 2026-10-27. No external blocklists reported the domain, while PhishDestroy’s internal list marks it malicious. Infrastructure The domain is 152 days old and resolves to IP 162.222.90.203 (ASN 199242, Malakmadze Web LLC, Georgia). It uses Cloudflare nameservers emerson.ns.cloudflare.com and irma.ns.cloudflare.com. TLS is provided by Let’s Encrypt, valid from 2026-09-24 to 2026-12-23. Open ports observed were 22, 80, 443 and 8000. What to do Visitors should not enter credentials or payment information on the site; anyone who has already done so should change related passwords and monitor financial accounts for unauthorized activity. Defenders can add boosterjuicefresh.shop to phishing denial lists and block the exact domain in web filters, and should review access logs for any requests to this host. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17ba9-b209-75da-b859-28dc7a4809a8/ Cloudflare Radar report: https://radar.cloudflare.com/scan/6bfd61ec-a3cf-4ade-bb0a-988027d74db9 URLQuery report: https://urlquery.net/report/50021f5e-4b54-449e-bbbc-ff2c5a093073 Stored capture screenshot: https://i.ibb.co/0RqQcVDY/0176b95c8397.png Cloudflare Radar screenshot (2026-10-27T05:16:34Z): https://screenshots.phishdestroy.io/cf/6bfd61ec-a3cf-4ade-bb0a-988027d74db9.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/50021f5e-4b54-449e-bbbc-ff2c5a093073.png URLScan screenshot (2026-10-27T04:54:10Z): https://screenshots.phishdestroy.io/us/01a17bb5-4e93-7768-8b91-1fbdf0cf2a1d.png URLScan capture report: https://urlscan.io/result/01a17bb5-4e93-7768-8b91-1fbdf0cf2a1d/ VirusTotal report: https://www.virustotal.com/gui/domain/boosterjuicefresh.shop Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=boosterjuicefresh.shop Archived copy: https://web.archive.org/web/20261027044427/https://boosterjuicefresh.shop/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
This website does not have many visitors IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
This website offers payment methods which allow you to get your money back This site seems to sell products online (how to check if it is a shop scam) According to the SSL check the certificate is valid DNSFilter considers this website safe
出典mechanism: Access Restrictionsource: Current Http Probe
エビデンスレイヤーAvailability: Reachable but protectedDNS: Resolved
最新のHTTP観測結果アクセス可能だが保護されているHTTP access restrictedAccess Restriction50%2026-11-22 11:16 UTC
RDAP登録
観測されたタイムラインlast reachable: 2026-11-22 11:16 UTClast content: 2026-11-21 02:21 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 1 identified
H
HTTP/3
その他
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
As the original juice and smoothie bar in Canada, we aim to build lasting customer loyalty by providing consistently tasty, quick, and healthy products that complement an active way of life.
Open Graph の説明:As the original juice and smoothie bar in Canada, we aim to build lasting customer loyalty by providing consistently tasty, quick, and healthy products that complement an active way of life.


 Dynadot
 162.222.90.203





 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT