元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。
Overview
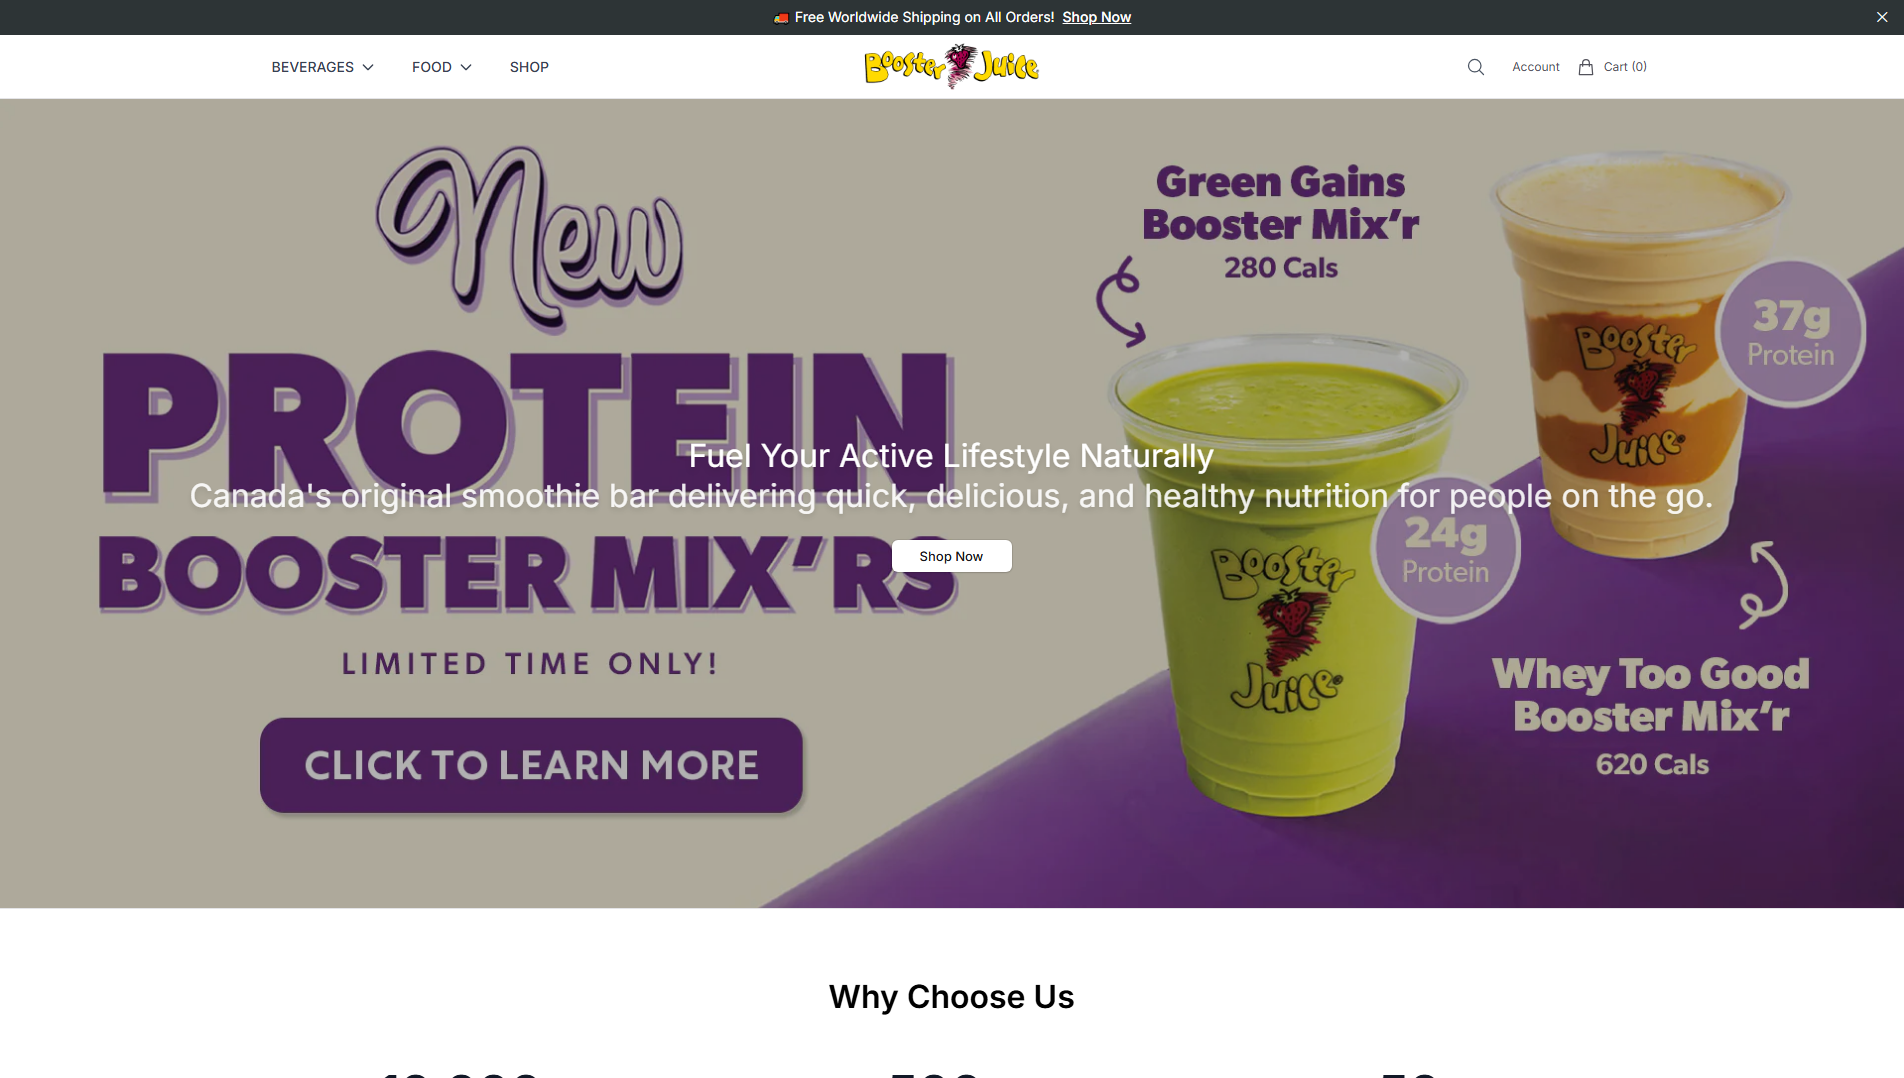
PhishDestroy added boosterjuicedirect.shop to its blocklist on 2026-10-27 after an intake review highlighted three malicious detections on VirusTotal. The page fetched on that date returned HTTP 200 and URLScan’s automated analysis labeled the site as a phishing fake‑shop. No page title was recorded in the capture.
詐欺の手口
The listing and detections indicate the site is likely a fake‑shop that mimics legitimate online stores to collect credentials or payment information. No specific wallet‑draining, malware, or credential‑harvesting behavior was observed on this domain.
証拠
VirusTotal scanned the domain on 2026-10-27 and recorded four detections, three marked malicious by CRDF, Netcraft and LevelBlue and one suspicious by Gridinsoft. Google Safe Browsing checked the same day and did not flag the site. URLScan captured the page on 2026-10-27, gave it a malicious score of 100, and categorized it as phishing and a fake‑shop. OTX listed four pulses referencing the domain, and PhishDestroy’s internal blocklist marks the domain as blocked.
インフラ
The domain was 157 days old at the time of observation and used a Let’s Encrypt certificate issued on 2026-09-19, valid until 2026-12-18. The recorded IP was 23.252.79.252, belonging to ASN 199242 (Malakmadze Web LLC) in Georgia. DNS was served by Cloudflare nameservers gabe.ns.cloudflare.com and ollie.ns.cloudflare.com, and open ports 22, 80, 443 and 8000 were observed.
What to do
Visitors should avoid entering any credentials, payment details or personal data on this site; if they have already done so, they should change passwords on affected accounts and monitor for unauthorized activity. Defenders can block the domain, log DNS and HTTP requests to it, and add the host to internal blocklists to prevent future connections.
PhishDestroy flags boosterjuicedirect.shop as a suspicious domain; URLScan classifies it as a fake‑shop and VirusTotal reports four detections from 92 engines.
AIによる要約
Overview PhishDestroy added boosterjuicedirect.shop to its blocklist on 2026-10-27 after an intake review highlighted three malicious detections on VirusTotal. The page fetched on that date returned HTTP 200 and URLScan’s automated analysis labeled the site as a phishing fake‑shop. No page title was recorded in the capture. How the scam works The listing and detections indicate the site is likely a fake‑shop that mimics legitimate online stores to collect credentials or payment information. No specific wallet‑draining, malware, or credential‑harvesting behavior was observed on this domain. Evidence VirusTotal scanned the domain on 2026-10-27 and recorded four detections, three marked malicious by CRDF, Netcraft and LevelBlue and one suspicious by Gridinsoft. Google Safe Browsing checked the same day and did not flag the site. URLScan captured the page on 2026-10-27, gave it a malicious score of 100, and categorized it as phishing and a fake‑shop. OTX listed four pulses referencing the domain, and PhishDestroy’s internal blocklist marks the domain as blocked. Infrastructure The domain was 157 days old at the time of observation and used a Let’s Encrypt certificate issued on 2026-09-19, valid until 2026-12-18. The recorded IP was 23.252.79.252, belonging to ASN 199242 (Malakmadze Web LLC) in Georgia. DNS was served by Cloudflare nameservers gabe.ns.cloudflare.com and ollie.ns.cloudflare.com, and open ports 22, 80, 443 and 8000 were observed. What to do Visitors should avoid entering any credentials, payment details or personal data on this site; if they have already done so, they should change passwords on affected accounts and monitor for unauthorized activity. Defenders can block the domain, log DNS and HTTP requests to it, and add the host to internal blocklists to prevent future connections. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17ba9-ad01-76ed-abef-3cecc59d56e7/ Cloudflare Radar report: https://radar.cloudflare.com/scan/4f87cf13-bcf3-460d-9c83-0e16d12b15a3 URLQuery report: https://urlquery.net/report/6cc882ee-77ca-4489-aae9-edac0d348b36 Stored capture screenshot: https://i.ibb.co/S4K0xG36/de5df9ed62a8.png Cloudflare Radar screenshot (2026-10-27T05:16:34Z): https://screenshots.phishdestroy.io/cf/4f87cf13-bcf3-460d-9c83-0e16d12b15a3.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/6cc882ee-77ca-4489-aae9-edac0d348b36.png URLScan screenshot (2026-10-27T04:57:10Z): https://screenshots.phishdestroy.io/us/01a17bb7-e7b0-77f9-a0b3-4e8fadc1e53e.png URLScan capture report: https://urlscan.io/result/01a17bb7-e7b0-77f9-a0b3-4e8fadc1e53e/ VirusTotal report: https://www.virustotal.com/gui/domain/boosterjuicedirect.shop Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=boosterjuicedirect.shop Archived copy: https://web.archive.org/web/20261027044412/https://boosterjuicedirect.shop/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Technologies: Cart Functionality, Node.js, Headless UI, React, Next.js, Priority Hints, Google Font API, Webpack, Prism, Open Graph, Module Federation, HTTP/3
セキュリティシグナル
Scamadviserの警告56/100
This website does not have many visitors IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
This website offers payment methods which allow you to get your money back This site seems to sell products online (how to check if it is a shop scam) According to the SSL check the certificate is valid DNSFilter considers this website safe
主要評価項目DNS 非アクティブreason: DNS NXDOMAIN80% confidence
出典source: Dns Cache
エビデンスレイヤーAvailability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP登録
観測されたタイムラインlast reachable: 2026-10-27 12:30 UTClast content: 2026-10-27 12:30 UTCcurrent episode first observed: 2026-10-28 16:03 UTCobserved RIP window: 2026-10-27 12:30 UTC → 2026-10-28 16:03 UTC · 27.54hmidpoint estimate ≈ 2026-10-28 02:17 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 1 identified
H
HTTP/3
その他
HTTP/3 is the third major version of the Hypertext Transfer Protocol used to exchange information on the World Wide Web.
As the original juice and smoothie bar in Canada, we aim to build lasting customer loyalty by providing consistently tasty, quick, and healthy products that complement an active way of life.
Open Graph の説明:As the original juice and smoothie bar in Canada, we aim to build lasting customer loyalty by providing consistently tasty, quick, and healthy products that complement an active way of life.


 Dynadot
 23.252.79.252


 Microsoft
 Cloudflare
 Yandex
 ESET
 ビットディフェンダー
 Norton
 Symantec
 Avira
 Avast / AVG
 カスペルスキー
 Dr.Web
 ネットクラフト
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT