VirusTotal
0 / 92
engines flag the domain


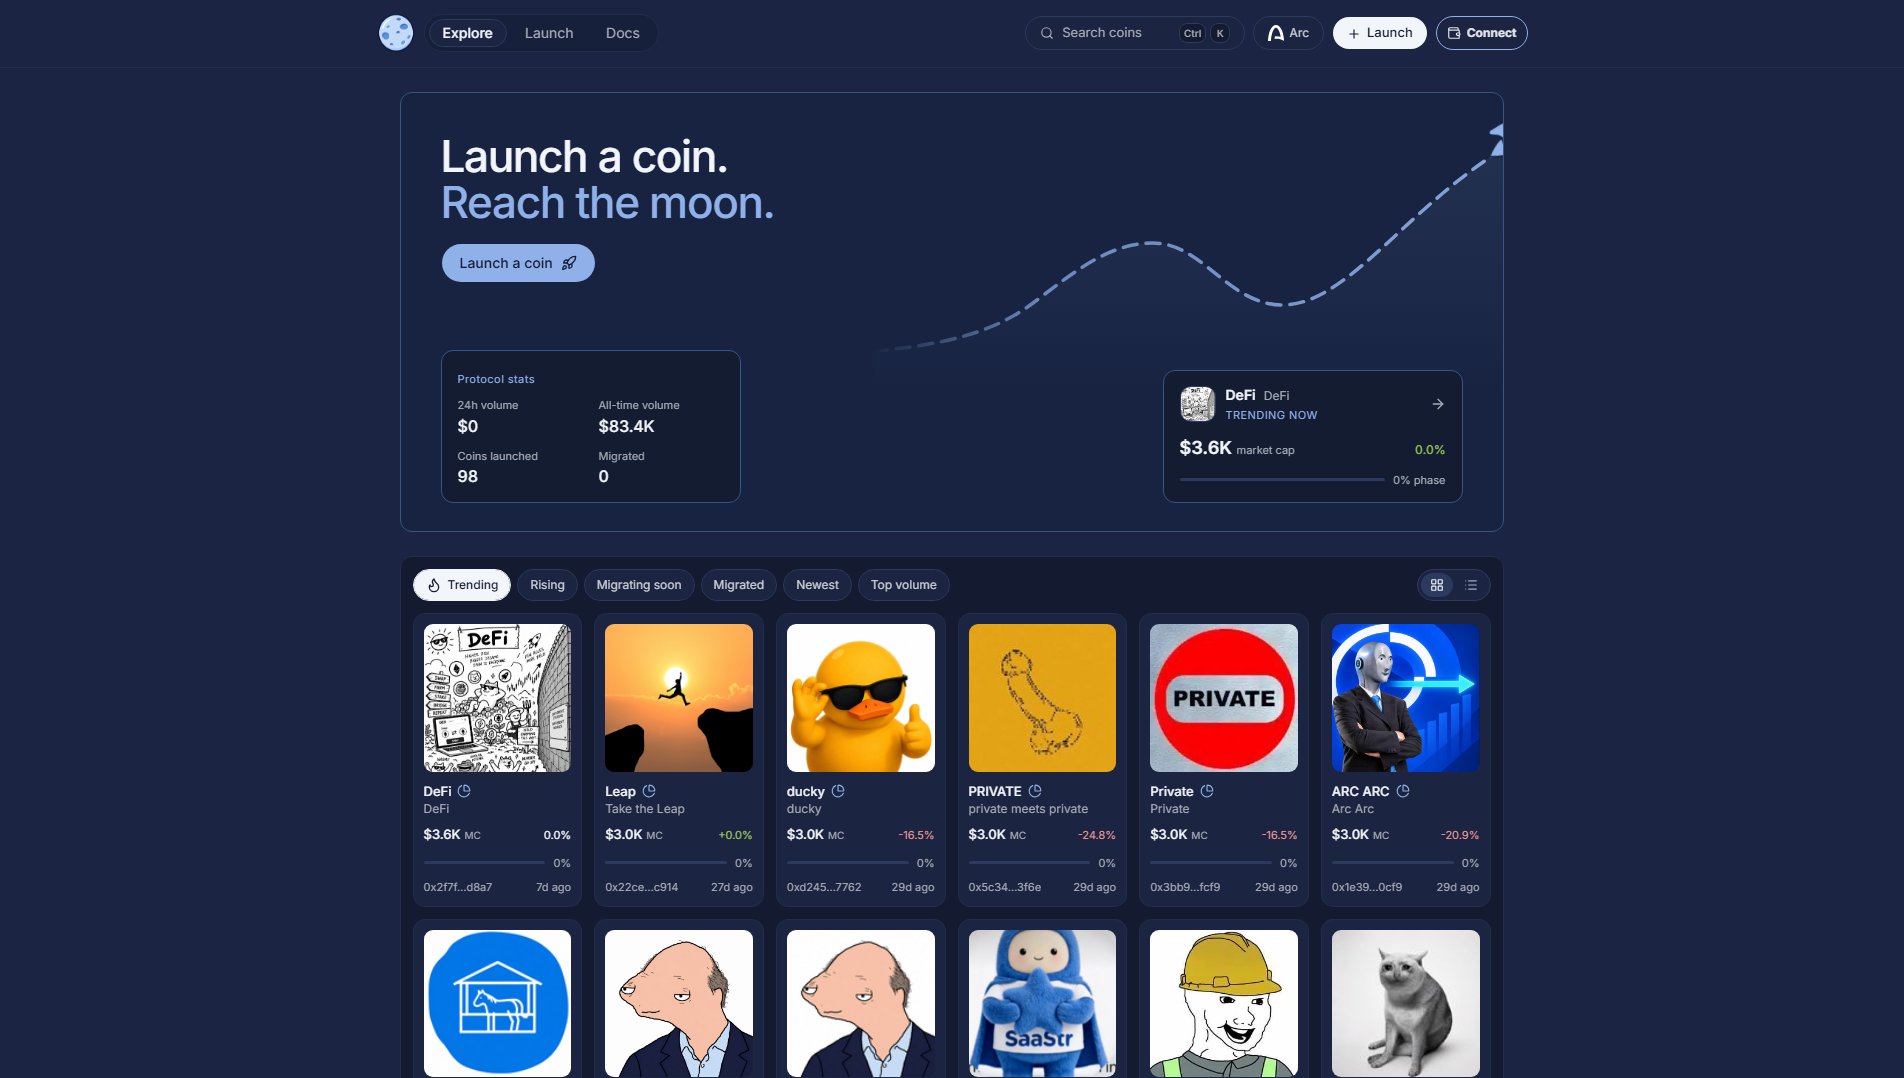
“Explore | moon”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@namecheap.com.
The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
0 / 92
engines flag the domain
No threat flag
Not on Google threat lists at check time
No malicious flag
Browser scan with screenshot
0
threat pulses mention the domain
Online · HTTP 403
Cloudflare · 188.114.96.1 · TLS: Google Trust Services
Each check shows its own collection time. Zero detections do not guarantee safety.
Domain dalam daftar blokir: moon.family — Terakhir diketahui aktif (HTTP 200). Ringkasan bukti: VirusTotal 4/92 (alphaMountain.ai, CRDF, Forcepoint…
Analisis terperinci PhishDestroy AI di bawah tetap berbahasa Inggris untuk menjaga catatan forensik asli.
4 / 92 engine detections
Buka laporanScan report
Buka laporanno community references
Buka laporanprovider verdict: clean
Buka laporanNo threat flag
Buka laporanNo malicious flag
Buka laporanResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
moon.family is a live site on the PhishDestroy blocklist that presents itself as "Explore | moon", a generic title that names no recognizable project, exchange or wallet. PhishDestroy first saw the domain on 2026-10-16. It has not yet been assigned a specific scheme type. As of 2026-10-19 the site was still online and serving content, so anyone browsing from crypto community links can still reach it.
An "Explore" landing page under a vague brand like "moon" is the kind of front often used to pull visitors into connecting a wallet, signing a message or entering account details. We have not confirmed which of these this page asks for. The risk is that any wallet connection, signature or typed credential is handed to an operator nobody can identify or hold accountable. Treat every prompt on this site as untrusted, especially requests to approve token spending or sign transactions you cannot read.
On 2026-10-19, 4 of 92 VirusTotal engines flagged the domain: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker and SOCRadar. That count is low, but these four vendors work independently of one another. Their verdicts point the same way as PhishDestroy's listing, which is currently the only blocklist carrying the domain. Most engines staying silent reflects how new the site is rather than a clean bill of health.
The domain was registered through NameCheap, Inc. on 2026-08-30, about seven weeks before PhishDestroy detected it. That is a short lifespan for a site presenting itself as an established platform. Traffic resolves to Cloudflare, Inc. address space, with the network geolocated to Canada. This means the actual origin server sits behind Cloudflare's proxy and is not exposed. The TLS certificate is a standard automated one, so the padlock in the browser says nothing about who runs the site.
Do not connect a wallet, sign messages or enter any login details on moon.family. If you already connected a wallet and signed anything there, move your assets to a fresh wallet created from a new seed phrase. Never type your seed phrase into any site. If you entered a password, change it wherever you reused it and turn on app-based two-factor authentication. Defenders should block the domain at DNS and proxy level and report it to Cloudflare and NameCheap so the hosting and registration can be reviewed.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
0x025324070d4721ac85a8d0006e8f24ca8ce85a2bFormat validated · Domain analysis0x04397988571cb50e2f6323d6b469202f61c227c9Format validated · Domain analysis0x0849e910f05c801634b053fa20a789537031bf4aFormat validated · Domain analysis0x095ff5a65f6d98646c1cd285c8542f711a52239eFormat validated · Domain analysis0x09bed6a2b2f490214d2bed9c1e7acc02c63110ddFormat validated · Domain analysis0x0a233496c9962a34f327bf0061e345044403f4eaFormat validated · Domain analysis0x0a888ae1d57e635aa5632e113fbc53e62a28c2b9Format validated · Domain analysis0x0adf215167ad481128a7660150848fe40525caefFormat validated · Domain analysis0x0be6be74fe9133a8d243db339d0efa99d151dd3aFormat validated · Domain analysis0x0d6db905106caadc3845c1fd18a491688290ac95Format validated · Domain analysis0x0f4e7c073bd77e9d1f380c31f2fcda32926ce873Format validated · Domain analysis0x0fee2837104e493ffab5e867a6d7d0cfc2cdc6dcFormat validated · Domain analysis0x105745ddffb36fe16348f60d25356da2a30bc0c1Format validated · Domain analysis0x10d18540c0fce8cf8ee85d4c81285f6f7d5c4193Format validated · Domain analysis0x1316b8b3d5ac254a357ba58001d087ff11d04cacFormat validated · Domain analysis0x13af4dd439e3a6052848d13b480ce564e82dcd49Format validated · Domain analysis0x13bd88d0eb78369b5c3705253abf64a19ba98499Format validated · Domain analysis0x14b5cfc369e6f5442ff383e9da9bfaf06896f965Format validated · Domain analysis0x17749748416f37a59ae8d029af44eec935f3c860Format validated · Domain analysis0x17c77537eed99705fc8dddfce1bea0fbd2577bcdFormat validated · Domain analysisIoC extraction recorded 2026-10-16 04:00:13 UTC
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
Reputasi Edge-IP tidak dikaitkan dengan domain ini.
opal.ns.cloudflare.compeyton.ns.cloudflare.comroute1.mx.cloudflare.netpriority 33route3.mx.cloudflare.netpriority 33route2.mx.cloudflare.netpriority 78Location describes the IP network.
f3b9ca8969144363b191396d155c4696ccacb56b124ae86ba8ce7094831e1fc0Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.
staging.moon.familyDomain recordThe original observation time is not recorded for these hostnames.
Google PageSpeed Insights — mobile performance audit of moon.family · checked Oct 16, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
https://moon.family/Content-Type: text/htmlCF-Cache-Status: DYNAMICContent-Encoding: gzipServer: cloudflareea49fcf4233f6590057f35c2507c37186c928fda682ec76d2ecdd9b87cedac42summary_large_imageh3=":443"; ma=86400DYNAMICa4b2efcb8cdface5-EWRkeep-alivegziptext/htmlFri, 16 Oct 2026 00:27:15 GMT; rel="preload"; as="style"; nopush, ; rel="preload"; as="style"; nopush, ; rel="preload"; as="style"; nopush, ; rel="preload"; as="style"; nopush, ; rel="preload"; as="style"; nopush, ; rel="preload"; as="style"; nopush, ; rel="moduleprelo{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=jdO0NUttIi5j4nMqFSWSE6qKAP4CMJjPfGJUTqeVuCdWt9m79G6BVwOoYJTvB8iGRmACfNEaD1sYq%2F84EH185zkjvPWo%2FeWgI3yotOpGYjVeJZCFlOUT3VZPa0Ewrg%3D%3D"}]}cloudflarecfCacheStatus;desc="DYNAMIC"chunkedAccept-Encoding1.1 CaddytrueValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Tidak diketahui→live_content
content_served
Tidak diketahui→live_content
content_served
Tidak diketahui→live_content
content_served
Tidak diketahui→live_content
content_served
No threat flag
View source4/92 engine detections
View sourcePD-20261016-B284F8
Page captured
View sourcemoon.family
View sourceSetiap jalur merupakan salah satu alasan mengapa sebuah domain terhubung ke host ini. Ukuran node menandai deteksi VirusTotal, sedangkan node bergaris putus-putus menunjukkan bahwa node tersebut sudah offline. Daftar lengkapnya tercantum di bawah ini.
Laporan-laporan ini diselesaikan dengan IP edge bersama yang sama. Mereka membantu penemuan laporan tetapi tidak menyiratkan kepemilikan bersama atau server asal bersama.
Didaftarkan melalui penyedia layanan pendaftaran yang sama. Sebuah penyedia layanan pendaftaran melayani jutaan pelanggan yang tidak saling terkait, sehingga hal ini sekadar mengelompokkan laporan-laporan tersebut, bukan membuktikan adanya hubungan.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
moon.family
PD-20261016-B284F8 Recipient: abuse@namecheap.com Registrar: Namecheap Inc (United States) Policy Violations: Domain Registration Agreement prohibits hacking, misuse of domain to conduct attacks, scam and fraudulent activities; AUP allows immediate suspension Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Jika Anda memasukkan kredensial akun, informasi pribadi atau pembayaran, atau mengunduh file dari domain ini, segera ambil tindakan. Di bawah ini adalah sumber daya untuk membantu Anda melaporkan insiden tersebut dan melindungi diri Anda sendiri.


Pilih negara Anda untuk mendapatkan kontak resmi kejahatan dunia maya, atau membuat draf pengaduan →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
moon.family)Meskipun kamu belum mengetahui semua detailnya — tetap saja ajukan laporan. Informasi yang tidak lengkap tetap dapat membantu penyelidikan.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Analisis ancaman menggunakan daftar blokir yang disimpan, WHOIS, DNS, dan bukti pemindaian publik
Pindai SekarangLaporkan domain yang mencurigakan ke basis data ancaman kami — lindungi komunitas
LaporanLaporan phishing terbaru dan perubahan ketersediaan yang diamati
PantauPantau ancaman secara langsung atau ajukan keberatan terhadap daftar ini jika Anda yakin ini merupakan false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.