VirusTotal
5 / 91
Report

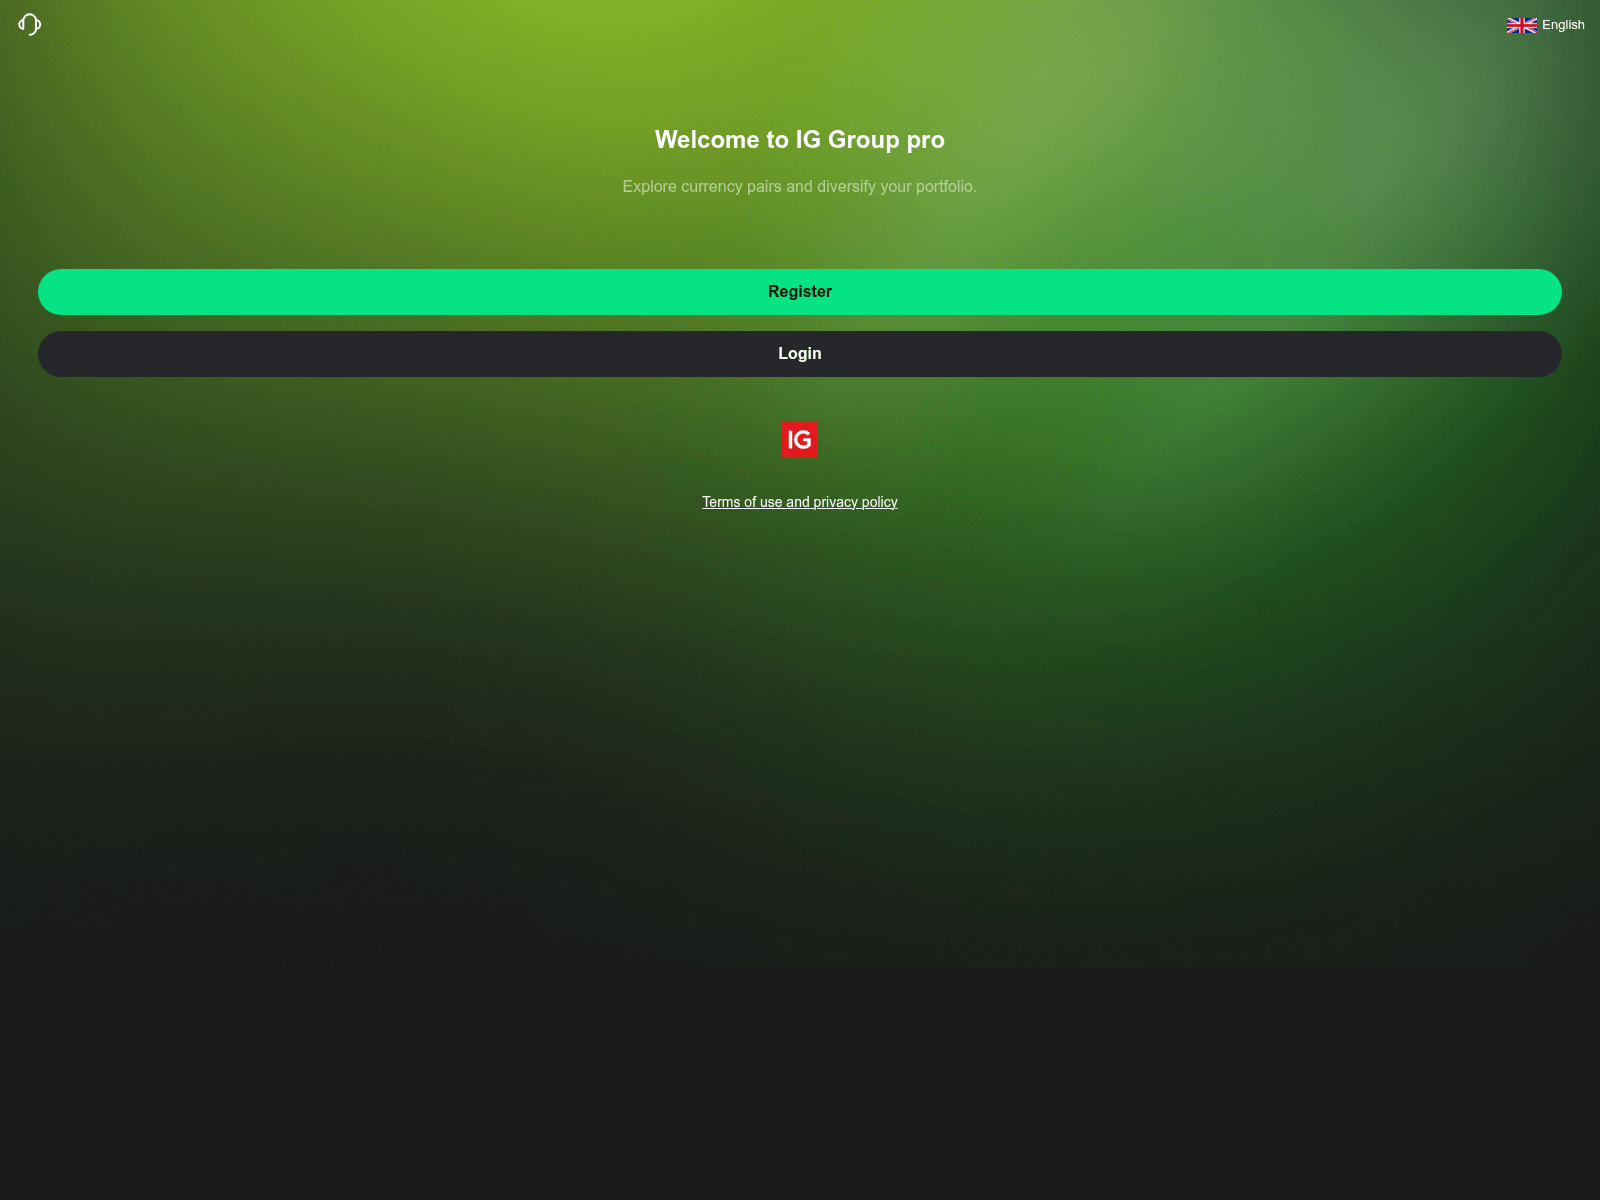
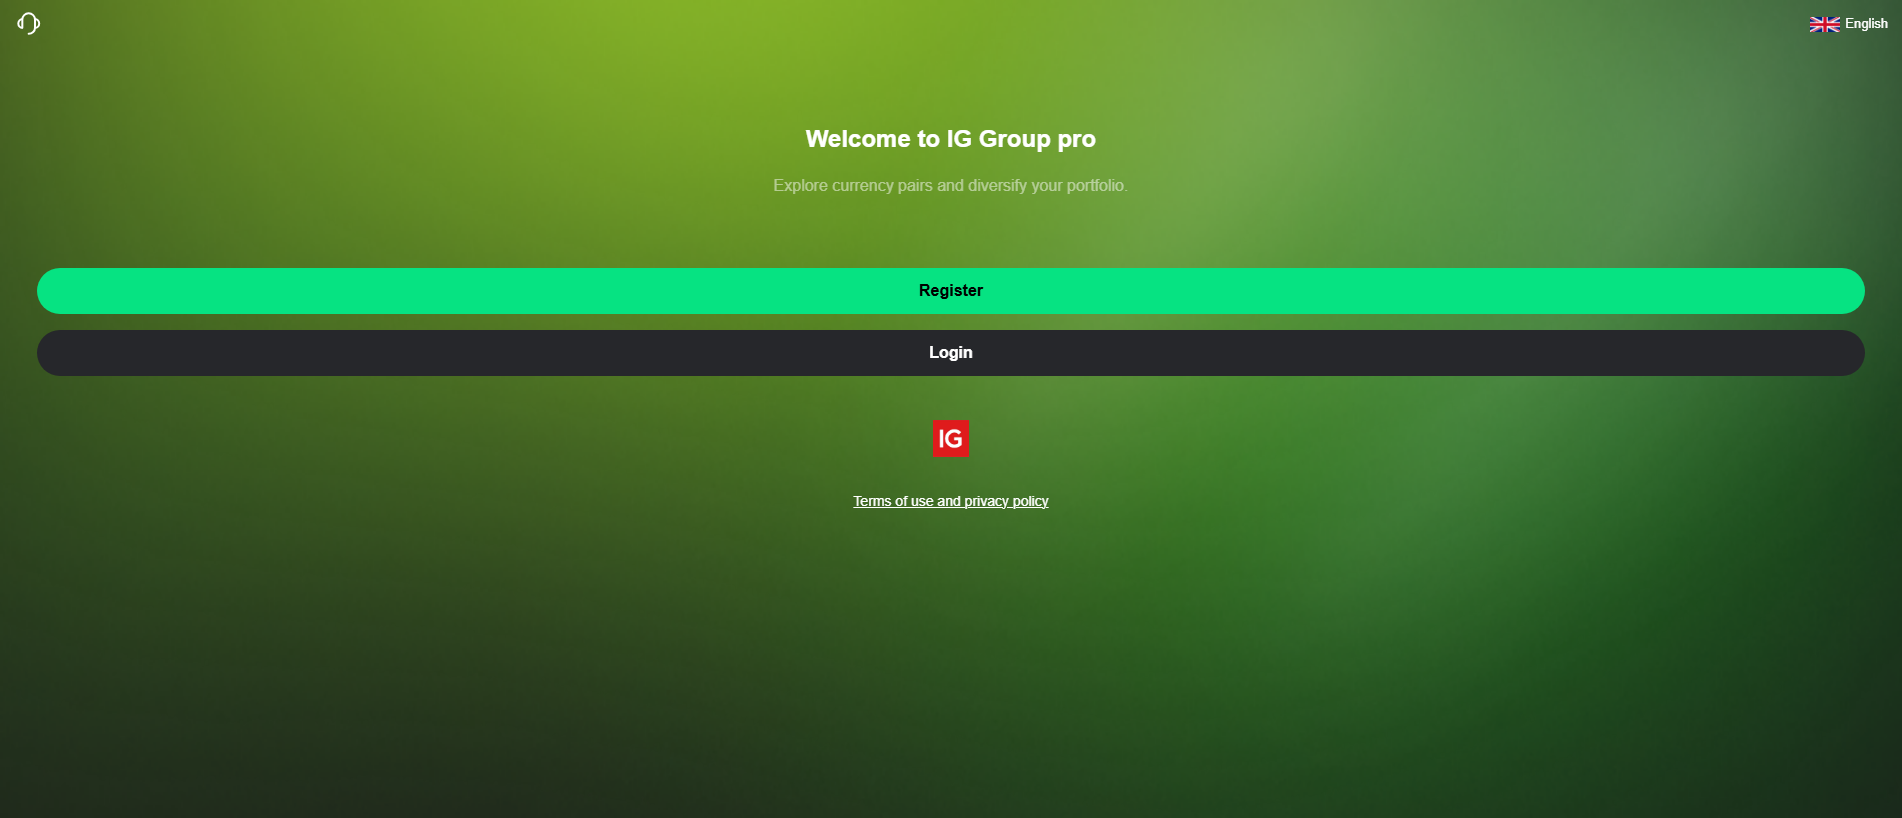
“IG Group pro”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@microsoft.com.
The latest stored availability evidence still shows the domain reachable; 39 hours has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
Stored evidence for vkloe.com: VirusTotal recorded 3 detections among 91 scanners on 2026-09-30. That ratio reproduces the stored check in its original units and is not converted into another measure. MetaMask and SEAL appear as named external blocklist observations for vkloe.com. Each item in this report remains at the scope supplied by its dated source record.
VirusTotal records 3 detections among 91 scanners in the stored snapshot dated 2026-09-30. The numerator describes scanners that produced detections, while the denominator describes scanners included in that check. The reverse order would materially alter the stored result. The VirusTotal snapshot dated 2026-09-30 supplies no common rationale covering the included scanners, and this report adds none. A later VirusTotal snapshot may contain different values, so any comparison should preserve the exact ratio and date of each snapshot.
MetaMask and SEAL are recorded as named external blocklist observations for vkloe.com in the snapshot dated 2026-09-30. The stored MetaMask and SEAL blocklist records supply names and entries, but they supply no shared method or common rationale. PhishDestroy’s catalogue also contains vkloe.com as a publisher record. That PhishDestroy record is counted separately from the MetaMask and SEAL external blocklist observations. This separation keeps the origin of every entry visible and prevents a single stored item from being counted again under another source label.
The record first observed vkloe.com on 2026-09-30. The MetaMask and SEAL blocklist snapshot is dated 2026-09-30 and remains a separate event in the stored timeline. The registration date is separately recorded as 2026-09-24. A URLScan reference was stored on 2026-09-30 as a dated artifact for review. Each timestamp qualifies only the adjacent observation in this timeline. Later collection results should be compared with these dated values without replacing the earlier snapshot.
The source stores 4.190.162.64 as the observed address in this record. The registration date for vkloe.com is recorded as 2026-09-24. These fields preserve registration, network, and certificate context stored in this record. The report preserves each label and number as a separate source value instead of combining them into an invented aggregate. Keeping the fields separate leaves every infrastructure value traceable to the record that supplied it.
The vkloe.com record states that VirusTotal recorded 3 detections among 91 scanners on 2026-09-30. MetaMask and SEAL remain named blocklist observations from the snapshot dated 2026-09-30. PhishDestroy remains a separate publisher catalogue entry in the stored record. The observed address field in this record contains 4.190.162.64. The supported conclusion is bounded to the exact stored observations for vkloe.com. Any statement beyond those source values would require additional dated material.
Avoid submitting sensitive information to vkloe.com during review. Use a known service address obtained separately from this report for any necessary access. Defenders can retain vkloe.com as an exact indicator and preserve relevant DNS, proxy, and endpoint records. Compare later VirusTotal snapshots and MetaMask and SEAL blocklist records with the dated values above instead of replacing them. Keep each later observation with its source date so changes remain visible during follow-up review. If a defensive rule is needed, keep its scope to vkloe.com. The stored record does not justify extending that rule to 4.190.162.64 or to other infrastructure records.
Stored crawler-versus-browser observations for this host, plus a live fingerprint check for Keitaro-style traffic distribution systems.
nginxScanner note: alive_content: raw=ok; http=200; via=https_proxy; server=nginx
 (US)
dayana.ns.cloudflare.comevan.ns.cloudflare.comLocation describes the IP network.
71d8763a32ecf84cb667ba432c3cccae4d906e437f9f2ad4cca53f724bcaeb40iggrouppro.vkloe.comiggroupprodown.vkloe.comiggroupprosuper.vkloe.comiggroupproweb.vkloe.comwww.vkloe.comSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
4.190.162.64. 11 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
79 stored lookalike domains
PD-20260930-7C6CF4 Recipient: abuse@microsoft.com Registrar: Gname.com Pte. Ltd. (Singapore) Policy Violations: Illegal Activities section forbids phishing, fraud, fake sites, malware distribution; registrar investigates and may suspend or delete domain Applicable Laws: Computer Misuse Act 1993 §§3+, Penal Code §§415–420 (cheating), Online Criminal Harms Act (OCHA)
If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Each lane is one reason a domain is linked to this host. Node size marks VirusTotal detections and dashed nodes are already offline. The full lists follow below.
These domains also target MetaMask users. View all MetaMask threats →
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive