198.251.84.236
URLScan

Malicious
SHA-256 32cae0e4be5da6c59681ae9a068d8291bdc190a5c3ea4dd2f82559e56ae8a03d
URLScanOriginal source recordObserved: 22 fields
Observed: · Retrieved:
Report ID
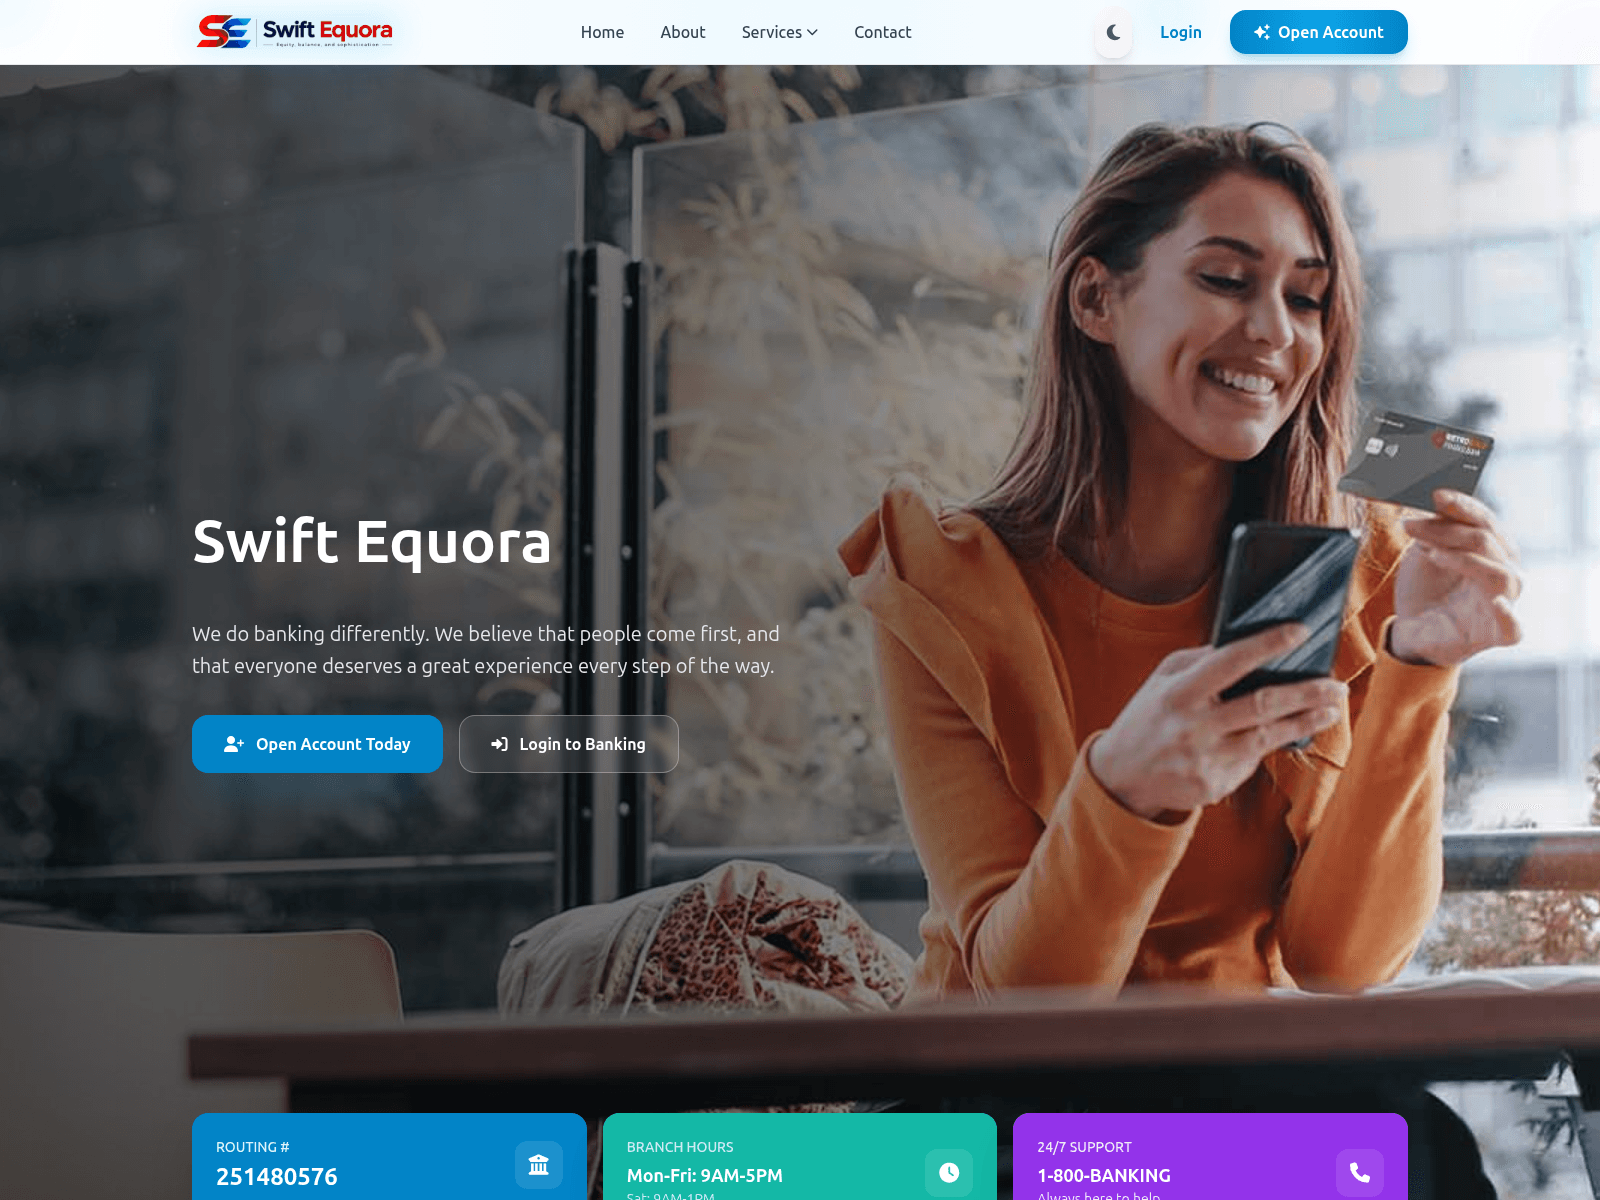
01a19c35-63e5-7728-a58b-ee52f235bfdcFinal URL
https://swiftequora.com/HTTP response
200Redirect type
https-onlyRedirects
- To
- https://swiftequora.com/
- From
- http://swiftequora.com/
- Status
- 307
IP address
198.251.84.236Reverse DNS (PTR)
d7.my-control-panel.comContacted domains
- cdn.jsdelivr.net
- widget-v3.smartsuppcdn.com
- images.unsplash.com
- cdn.tailwindcss.com
- websocket-visitors.smartsupp.com
- bootstrap.smartsuppchat.com
- www.smartsuppchat.com
- fonts.googleapis.com
Contacted IP addresses
- 109.61.91.194
- 18.184.200.240
- 109.61.91.195
- 151.101.2.208
- 142.251.163.95
- 104.16.179.112
- 104.26.3.143
- 198.251.84.236
Autonomous systems (ASN)
- 60068
- 16509
- 54113
- 15169
- 13335
- 53667
Server countries
- US
- DE
- LU
Document hash
32cae0e4be5da6c59681ae9a068d8291bdc190a5c3ea4dd2f82559e56ae8a03dJavaScript globals
- tailwind
- /template.html
- changeLanguage
- updateFlagDisplay
- translatePage
- translateBatch
- translateText
- translateWithLibre
- translateBasic
- getLanguageName
- showTranslationLoading
- hideTranslationLoading
- _smartsupp
- smartsupp
- Alpine
- SMARTSUPP_LOADED
- $smartsupp
- isDarkMode
- observerOptions
- observer
- currentLanguage
Cookies
- XSRF-TOKEN
- swift_equora_session
TLS session and certificate
- Subject alternative names
- *.swiftequora.com
- swiftequora.com
- Cipher
- AES_128_GCM
- Issuer
- YE2
- Subject
- *.swiftequora.com
- Protocol
- TLS 1.3
- Valid until
- Valid from
Domain age, days
0Registered domain age, days
0Certificate age, days
0Certificate validity, days
89Page requests
36Provider verdicts
- Engine verdict
- Tags
- urlscan-ml
- urlscan-ml-60c5e22
- Score
- 100
- Malicious
- Yes
- Overall verdict
- Tags
- phishing
- Score
- 100
- Brands
- genericbanking
- Malicious
- Yes
- Categories
- phishing
- URLScan verdict
- Tags
- phishing
- Score
- 100
- Brands
- Generic Banking
- Malicious
- Yes
- Categories
- phishing
HTTP headers
- Server
- LiteSpeed
- Content-type
- text/html; charset=UTF-8
- X-frame-options
- SAMEORIGIN
- X-content-type-options
- nosniff
- Referrer-policy
- strict-origin-when-cross-origin
Original source fields · JSON
| Uuid | 01a19c35-63e5-7728-a58b-ee52f235bfdc |
|---|---|
| Final url | https://swiftequora.com/ |
| Status | 200 |
| Redirected | https-only |
| Redirects | [
{
"to": "https://swiftequora.com/",
"from": "http://swiftequora.com/",
"status": 307
}
] |
| Ip | 198.251.84.236 |
| Ptr | d7.my-control-panel.com |
| Contacted domains | [
"cdn.jsdelivr.net",
"widget-v3.smartsuppcdn.com",
"images.unsplash.com",
"cdn.tailwindcss.com",
"websocket-visitors.smartsupp.com",
"bootstrap.smartsuppchat.com",
"www.smartsuppchat.com",
"fonts.googleapis.com"
] |
| Contacted IP addresses | [
"109.61.91.194",
"18.184.200.240",
"109.61.91.195",
"151.101.2.208",
"142.251.163.95",
"104.16.179.112",
"104.26.3.143",
"198.251.84.236"
] |
| Asns | [
"60068",
"16509",
"54113",
"15169",
"13335",
"53667"
] |
| Countries | [
"US",
"DE",
"LU"
] |
| Document hash | 32cae0e4be5da6c59681ae9a068d8291bdc190a5c3ea4dd2f82559e56ae8a03d |
| Globals | [
"tailwind",
"/template.html",
"changeLanguage",
"updateFlagDisplay",
"translatePage",
"translateBatch",
"translateText",
"translateWithLibre",
"translateBasic",
"getLanguageName",
"showTranslationLoading",
"hideTranslationLoading",
"_smartsupp",
"smartsupp",
"Alpine",
"SMARTSUPP_LOADED",
"$smartsupp",
"isDarkMode",
"observerOptions",
"observer",
"currentLanguage"
] |
| Cookies | [
"XSRF-TOKEN",
"swift_equora_session"
] |
| Tls | {
"san": [
"*.swiftequora.com",
"swiftequora.com"
],
"cipher": "AES_128_GCM",
"issuer": "YE2",
"subject": "*.swiftequora.com",
"protocol": "TLS 1.3",
"valid_to": "2027-01-30T18:31:50Z",
"valid_from": "2026-11-01T18:31:51Z"
} |
| Domain age days | 0 |
| Apex age days | 0 |
| Tls age days | 0 |
| Tls valid days | 89 |
| Requests | 36 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 100,
"malicious": true
},
"overall": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"genericbanking"
],
"malicious": true,
"categories": [
"phishing"
]
},
"urlscan": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"Generic Banking"
],
"malicious": true,
"categories": [
"phishing"
]
}
} |
| HTTP headers | {
"server": "LiteSpeed",
"content-type": "text/html; charset=UTF-8",
"x-frame-options": "SAMEORIGIN",
"x-content-type-options": "nosniff",
"referrer-policy": "strict-origin-when-cross-origin"
} |
Separate monitor record · date not recorded
Separate stored monitor snapshot; does not replace the primary report record or establish current availability.
- record_source
- domain_monitor.urlscan
- uuid
- 01a19c35-63e5-7728-a58b-ee52f235bfdc
- score
- null
- malicious
- null
- result_at
- null
- enriched_at
- null
- source_timestamps
- {"urlscan_result_at":null,"urlscan_enriched_at":null}
- timestamp_basis
- Europe/Berlin, as used by the existing report; source timestamps are retained verbatim


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 Scamadviser
 MyWOT