Skip to security report
Recorded security signals
Stored VirusTotal result: 3/92 engines flagged. malicious: 3. suspicious: 0. Analysis time (as stored): 2026-11-01T16:46:35Z. Retrieved (as stored): 2026-11-02T09:26:11Z. Exercise extreme caution — do not enter credentials or personal information.
Were you scammed by this site?Report to authorities
Domain security and threat intelligence
stmalachychicago.mohsenmeysami.com favicon

stmalachychicago.mohsenmeysami.com

In short

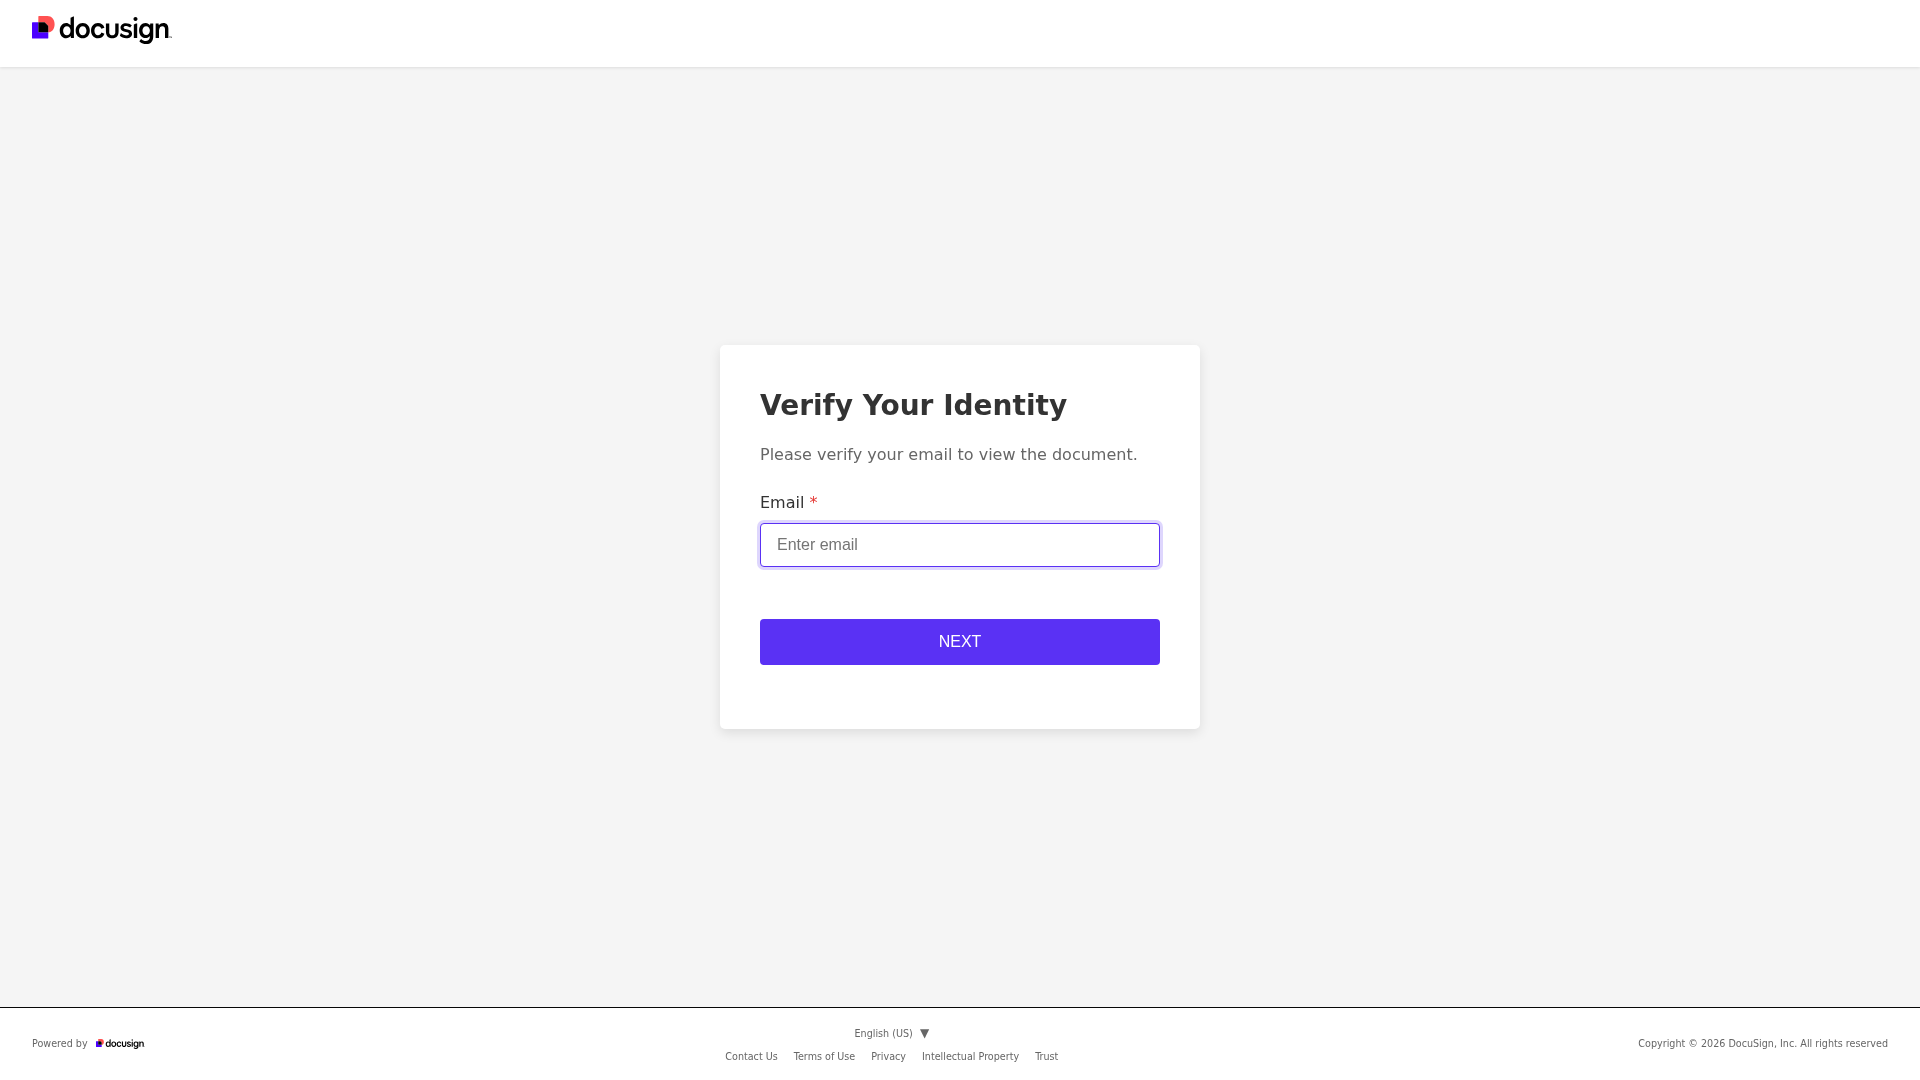
On 2026-11-02, stmalachychicago.mohsenmeysami.com displayed a page branded with the DocuSign logo and a "Verify Your Identity" heading. The page asks the visitor to verify their email to view the document, providing an email input field labeled "Email" with placeholder text "Enter email" and a purple "NEXT" button. The footer shows "Powered by docusign" and a copyright notice.

“Document - isdP”

Registrar
CanadaTUCOWS.COM, CO
Resolved IP
Australia122.201.80.143Dreamscape Networks PTY LTD
Registered
Mar 10, 2017
First observed
Nov 2, 2026
PhishDestroy assessment Critical
90/100
Evidence score
Availability Last known active Latest stored reachability observation Observed HTTP probe
VirusTotal detections: 3/92 Google Safe Browsing: threat flag recorded
VirusTotal
engine detections ·
Google Safe Browsing
URLScan
Cloudflare Radar
Page captures
open gallery
Domain age
registered 2017-03-10 according to WHOIS · source data differ
Nov 2, 2026
X Telegram API

Analysis

Domain summary

PhishDestroy first recorded stmalachychicago.mohsenmeysami.com on 2026-11-02. Stored VirusTotal result: 3/92 engines flagged. malicious: 3. suspicious: 0. Analysis time (as stored): 2026-11-01T16:46:35Z. Retrieved (as stored): 2026-11-02T09:26:11Z. Google Safe Browsing flags it. Risk: critical (90/100). Registrar: TUCOWS.COM, CO. Status: Last known active. Hosting: Dreamscape Networks PTY LTD. Do not enter credentials or connect a wallet.

Critical
Status
Last known active
VirusTotal
3 / 92
Scam type (automated label)
Credential Phishing
Hosting
Australia122.201.80.143Dreamscape Networks PTY LTD
Registrar
CanadaTUCOWS.COM, CO
Registered
Mar 10, 2017
Page captures
6

Capture recorded with this analysis · Cloudflare Radar · 2026-11-02T09:27:00Z
SHA-256: 7888cb6bc93da548d242a70285a07da57e6b0a32b975d9d14c6e8d28a0aea319

PhishDestroy analysis, reviewed version

On 2026-11-02, stmalachychicago.mohsenmeysami.com displayed a page branded with the DocuSign logo and a "Verify Your Identity" heading. The page asks the visitor to verify their email to view the document, providing an email input field labeled "Email" with placeholder text "Enter email" and a purple "NEXT" button. The footer shows "Powered by docusign" and a copyright notice.

The stored VirusTotal domain result reports 3 detections out of 92 engines. CRDF reported "malicious"; SOCRadar reported "malicious".

Source evidenceVirusTotal 3 / 92 · Google Safe Browsing: flagged 8 sources

VirusTotal

3 / 92 engine detections

Analysis:
Open report
VirusTotalOriginal source recordObserved: 13 fields

Observed: · Retrieved:

Vendor result counts

Timeout
0
Harmless
1
Malicious
3
Suspicious
0
Undetected
88

Vendor labels

CRDF
malicious
SOCRadar
malicious
Gridinsoft
phishing

Reputation score

0

Registrar

Tucows Domains Inc.

Created

Expires

Updated

First seen

DNS records

  • TTL, seconds
    14400
    Type
    A
    Value
    122.201.80.143

DNS records observed

JARM fingerprint

25d3fd00025d25d00042d43d0000001b0c486b0c0bae33c7ce67177fe8bab5

Certificate

Subject alternative names
  • *.mohsenmeysami.com
  • mohsenmeysami.com
Issuer
Let's Encrypt / YR2
Serial
5843aab3ca513e1cfb06e7bc1ae76eb4ac
SHA-256
971617e12a55e4298f26f3a5c90a7b4e9a5351fcf02596fbb56fee298c367e81
Subject
*.mohsenmeysami.com
Valid until
Valid from

Registration record

Registrar
Tucows Domains Inc.
Registrar IANA ID
69
Registrar URL
http://www.tucows.com
Registered
Updated
Expires
Status
  • clientTransferProhibited
  • clientUpdateProhibited
Nameservers
  • ns1.whois.net.au
  • ns2.whois.net.au
DNSSEC
unsigned
Original source fields · JSON
Vendor result counts
{
    "timeout": 0,
    "harmless": 1,
    "malicious": 3,
    "suspicious": 0,
    "undetected": 88
}
Vendor labels
{
    "CRDF": "malicious",
    "SOCRadar": "malicious",
    "Gridinsoft": "phishing"
}
Reputation
0
Registrar
Tucows Domains Inc.
Created
2017-03-10T12:40:35Z
Expires
2028-03-10T12:40:35Z
Updated
2026-02-12T00:56:03Z
First seen
2026-10-01T14:09:40Z
DNS records
[
    {
        "ttl": 14400,
        "type": "A",
        "value": "122.201.80.143"
    }
]
Dns at
2026-11-01T16:46:59Z
Jarm
25d3fd00025d25d00042d43d0000001b0c486b0c0bae33c7ce67177fe8bab5
Certificate
{
    "san": [
        "*.mohsenmeysami.com",
        "mohsenmeysami.com"
    ],
    "issuer": "Let's Encrypt / YR2",
    "serial": "5843aab3ca513e1cfb06e7bc1ae76eb4ac",
    "sha256": "971617e12a55e4298f26f3a5c90a7b4e9a5351fcf02596fbb56fee298c367e81",
    "subject": "*.mohsenmeysami.com",
    "valid_to": "2027-01-26T09:57:32Z",
    "valid_from": "2026-10-28T09:57:33Z"
}
Registration record
{
    "registrar": "Tucows Domains Inc.",
    "registrar_iana_id": "69",
    "registrar_url": "http://www.tucows.com",
    "created": "2017-03-10T12:40:35Z",
    "updated": "2026-02-12T00:56:03Z",
    "expires": "2028-03-10T12:40:35Z",
    "status": [
        "clientTransferProhibited",
        "clientUpdateProhibited"
    ],
    "nameservers": [
        "ns1.whois.net.au",
        "ns2.whois.net.au"
    ],
    "dnssec": "unsigned"
}
Separate collector summary

This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.

source
VirusTotal
scope
unknown
result_state
observed
numerator
3
denominator
92
malicious
null
suspicious
null
vendors
["CRDF","Gridinsoft","SOCRadar"]
observed_at
2026-11-01 16:46:35
checked_at
2026-11-02 10:26:14
fetched_at
2026-11-02 09:26:15
time_basis
as stored; legacy timezone not established

Cloudflare Radar

Phishing

Open report
Cloudflare RadarOriginal source recordObserved: 14 fields

Observed: · Retrieved:

Report ID

670818e2-61b3-44ed-a4a1-eaf7aead9956

Final URL

https://stmalachychicago.mohsenmeysami.com/

HTTP response

200

Navigation history

  • URL
    https://stmalachychicago.mohsenmeysami.com/
    Status
    200

DOM structure hash

29122162a547e0d1e7cbbcd55f08525cc5b5fa676368b2ccebb841fc4154a5fb

Document hash

9451fd3151ce51ab1c492ab36c1e3d22c0391b01d28388e4d6233603d5bb2be1

URL risk categories

  • Phishing

Domain risk categories

  • Phishing
  • Security threats
  • CIPA Filter
  • CIPA

Cloudflare Radar rank

Rank range
>200000

DNS records

  • Name
    stmalachychicago.mohsenmeysami.com
    Type
    A
    Value
    122.201.80.143

DNSSEC valid

No

IP address

127.0.1.2

127.0.1.2 is not a public internet address. It is the value stored in this source record, not the site's hosting address.

Verdict

Tags
  • phishing
Malicious
Yes
Categories
  • phishing

Registration record

Registrar
Tucows Domains Inc.
Registered
Updated
Expires
Nameservers
  • ns1.whois.net.au
  • ns2.whois.net.au
Original source fields · JSON
Uuid
670818e2-61b3-44ed-a4a1-eaf7aead9956
Final url
https://stmalachychicago.mohsenmeysami.com/
Status
200
History
[
    {
        "url": "https://stmalachychicago.mohsenmeysami.com/",
        "status": 200
    }
]
DOM structure hash
29122162a547e0d1e7cbbcd55f08525cc5b5fa676368b2ccebb841fc4154a5fb
Document hash
9451fd3151ce51ab1c492ab36c1e3d22c0391b01d28388e4d6233603d5bb2be1
Url risks
[
    "Phishing"
]
Domain risks
[
    "Phishing",
    "Security threats",
    "CIPA Filter",
    "CIPA"
]
Radar rank
{
    "bucket": ">200000"
}
DNS records
[
    {
        "name": "stmalachychicago.mohsenmeysami.com",
        "type": "A",
        "value": "122.201.80.143"
    }
]
Dnssec valid
false
Ip
127.0.1.2

127.0.1.2 is not a public internet address. It is the value stored in this source record, not the site's hosting address.

Verdict
{
    "tags": [
        "phishing"
    ],
    "malicious": true,
    "categories": [
        "phishing"
    ]
}
Registration record
{
    "registrar": "Tucows Domains Inc.",
    "created": "2017-03-10T12:40:35Z",
    "updated": "2026-02-12T00:56:03Z",
    "expires": "2028-03-10T12:40:35Z",
    "nameservers": [
        "ns1.whois.net.au",
        "ns2.whois.net.au"
    ]
}

Google Safe Browsing

Threat flag recorded

Open report

URLScan

Malicious

SHA-256 18574f7895ee9cbd9d3087d8e4a6e2a465dbc546090a9ba68eec4f098952d9a4

Open report
URLScanOriginal source recordObserved: 21 fields

Observed: · Retrieved:

Report ID

01a19b76-29a5-71e8-9be0-e70137d73313

Final URL

https://www.stmalachychicago.mohsenmeysami.com/

HTTP response

200

Redirect type

https-only

Redirects

  • To
    https://www.stmalachychicago.mohsenmeysami.com/
    From
    http://www.stmalachychicago.mohsenmeysami.com/
    Status
    307

IP address

122.201.80.143

Reverse DNS (PTR)

whois01.turboservers.com.au

Contacted domains

  • fonts.gstatic.com
  • fonts.googleapis.com

Contacted IP addresses

  • 142.250.195.131
  • 142.250.195.106
  • 122.201.80.143

Autonomous systems (ASN)

  • 15169
  • 38719

Server countries

  • US
  • AU

Document hash

18574f7895ee9cbd9d3087d8e4a6e2a465dbc546090a9ba68eec4f098952d9a4

JavaScript globals

  • swremleu
  • o
  • X
  • h

TLS session and certificate

Subject alternative names
  • *.mohsenmeysami.com
  • mohsenmeysami.com
Cipher
AES_128_GCM
Issuer
YR2
Subject
*.mohsenmeysami.com
Protocol
TLS 1.3
Valid until
Valid from

Domain age, days

0

Differs from the registration date in WHOIS (2017-03-10), which gives 3523 days on the scan date 2026-11-02. The two sources disagree; both values are kept as recorded.

Registered domain age, days

3039

Differs from the registration date in WHOIS (2017-03-10), which gives 3523 days on the scan date 2026-11-02. The two sources disagree; both values are kept as recorded.

Certificate age, days

4

Certificate validity, days

89

Page requests

5

Provider verdicts

Engine verdict
Tags
  • urlscan-ml
  • urlscan-ml-60c5e22
Score
18
Malicious
Yes
Overall verdict
Tags
  • phishing
Score
100
Brands
  • docusign
Malicious
Yes
Categories
  • phishing
URLScan verdict
Tags
  • phishing
Score
100
Brands
  • DocuSign
Malicious
Yes
Categories
  • phishing

HTTP headers

Server
Apache
Content-type
text/html; charset=UTF-8
Original source fields · JSON
Uuid
01a19b76-29a5-71e8-9be0-e70137d73313
Final url
https://www.stmalachychicago.mohsenmeysami.com/
Status
200
Redirected
https-only
Redirects
[
    {
        "to": "https://www.stmalachychicago.mohsenmeysami.com/",
        "from": "http://www.stmalachychicago.mohsenmeysami.com/",
        "status": 307
    }
]
Ip
122.201.80.143
Ptr
whois01.turboservers.com.au
Contacted domains
[
    "fonts.gstatic.com",
    "fonts.googleapis.com"
]
Contacted IP addresses
[
    "142.250.195.131",
    "142.250.195.106",
    "122.201.80.143"
]
Asns
[
    "15169",
    "38719"
]
Countries
[
    "US",
    "AU"
]
Document hash
18574f7895ee9cbd9d3087d8e4a6e2a465dbc546090a9ba68eec4f098952d9a4
Globals
[
    "swremleu",
    "o",
    "X",
    "h"
]
Tls
{
    "san": [
        "*.mohsenmeysami.com",
        "mohsenmeysami.com"
    ],
    "cipher": "AES_128_GCM",
    "issuer": "YR2",
    "subject": "*.mohsenmeysami.com",
    "protocol": "TLS 1.3",
    "valid_to": "2027-01-26T09:57:32Z",
    "valid_from": "2026-10-28T09:57:33Z"
}
Domain age days
0

Differs from the registration date in WHOIS (2017-03-10), which gives 3523 days on the scan date 2026-11-02. The two sources disagree; both values are kept as recorded.

Apex age days
3039

Differs from the registration date in WHOIS (2017-03-10), which gives 3523 days on the scan date 2026-11-02. The two sources disagree; both values are kept as recorded.

Tls age days
4
Tls valid days
89
Requests
5
Provider verdicts
{
    "engines": {
        "tags": [
            "urlscan-ml",
            "urlscan-ml-60c5e22"
        ],
        "score": 18,
        "malicious": true
    },
    "overall": {
        "tags": [
            "phishing"
        ],
        "score": 100,
        "brands": [
            "docusign"
        ],
        "malicious": true,
        "categories": [
            "phishing"
        ]
    },
    "urlscan": {
        "tags": [
            "phishing"
        ],
        "score": 100,
        "brands": [
            "DocuSign"
        ],
        "malicious": true,
        "categories": [
            "phishing"
        ]
    }
}
HTTP headers
{
    "server": "Apache",
    "content-type": "text/html; charset=UTF-8"
}
Separate monitor record · date not recorded

Separate stored monitor snapshot; does not replace the primary report record or establish current availability.

record_source
domain_monitor.urlscan
uuid
01a19b76-29a5-71e8-9be0-e70137d73313
score
null
malicious
null
result_at
null
enriched_at
2026-11-02T09:10:42Z
source_timestamps
{"urlscan_result_at":null,"urlscan_enriched_at":"2026-11-02 10:10:42"}
timestamp_basis
Europe/Berlin, as used by the existing report; source timestamps are retained verbatim

OTX

no community references

Open report

Spamhaus DBL

Check recorded; verdict not retained

Open report

PhishDestroy DOM

15 / 100 · heuristic score · 2 brand references · 1 classification

Open report
Separate monitor score · 15 / 100 · 2026-11-02T09:32:07Z

This dated monitor analysis is separate from the primary PhishDestroy analysis above. A heuristic score is not a measured probability.

record_source
domain_monitor.dom_analysis
heuristic_score
15
analyzed_at
2026-11-02T09:32:07Z
source_timestamp
2026-11-02 10:32:07
timestamp_basis
Europe/Berlin, as used by the existing report; source timestamps are retained verbatim

PhishDestroy narrative

Narrative generation metadata

Open report
Title, description and generation record

The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.

ai_title
stmalachychicago.mohsenmeysami.com: DocuSign-branded email verification page
ai_description
PhishDestroy records stmalachychicago.mohsenmeysami.com showing a DocuSign-branded page asking visitors to verify an email address to view a document.
ai_summary
On 2026-11-02, stmalachychicago.mohsenmeysami.com displayed a page branded with the DocuSign logo and a "Verify Your Identity" heading. The page asks the visitor to verify their email to view the document, providing an email input field labeled "Email" with placeholder text "Enter email" and a purple "NEXT" button. The footer shows "Powered by docusign" and a copyright notice. The stored VirusTotal domain result reports 3 detections out of 92 engines. CRDF reported "malicious"; SOCRadar reported "malicious".
ai_generated_by
threat-v6-mimo
ai_generated_at
2026-11-02 10:28:11
revision
b8fc9a5c5f96d7de02e33be58d4a9529094dda1829e54664a9da96b1acb95288
mode
reviewed
interpretation
Selected public package; text generation time is separate from source observation dates.

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Collected source details

Stored page, network and scanner observations, grouped by source and observation time.

Every stored field, with its source and date
Website checksOriginal source recordRetrieved: 22 fields

CAA records

Domain
stmalachychicago.mohsenmeysami.com

Protective DNS results

Resolvers checked
12
Blocked by
  • CloudFlare Family
Blocking resolvers
1

Web archive observations

Last observation
First observation
Recorded changes
0
Archived days
1
Average page size, bytes
26113

Page title and metadata

Page title
Document - isdP

Trackers

Requests
3
Observed services
  • Name
    Google Fonts
    Company
    Google
    Country
    US
    Category
    Hosting
    Requests
    1
  • Name
    Google Static
    Company
    Google
    Country
    US
    Category
    Hosting
    Requests
    1

Forms and mixed content

Third-party scripts
0

HTTP response

Reachable
Yes
HTTP status
200
Request timings, ms
DNS
20
TLS
295
Waiting
2769
Connection
291
Download
579
Response time, ms
3954

TLS connection

ALPN
http/1.1
Cipher
TLS_AES_256_GCM_SHA384
Protocol
TLSv1.3
Supported versions
  • TLSv1.2
  • TLSv1.3
Certificate authorized
Yes
Forward secrecy
Yes

Ports

Open ports
  • 25
  • 53
  • 80
  • 110
  • 143
  • 443
  • 587
  • 993
  • 995

Carbon estimate

Bytes
43982
CO₂, grams
0.0016
Cleaner than, %
40

DNS servers

Nameservers
  • IP address
    122.201.80.143
    Host
    ns2.australiawhois.com
  • IP address
    122.201.80.143
    Host
    ns1.australiawhois.com
DNS zone
mohsenmeysami.com

Location

IP address
122.201.80.143
ASN
38719
Organization
Dreamscape Networks PTY LTD
City
Sydney
Country
AU

TLS certificate

Issuer
Let's Encrypt / YR2
Subject
*.mohsenmeysami.com

DNS records

A
  • 122.201.80.143

DNSSEC

DS record
No
RRSIG
No
DNSKEY
No

HSTS

Observation
Site does not serve any HSTS headers.

HTTP security policies

X-Frame-Options
No
Referrer-Policy
No
X-XSS-Protection
No
Permissions-Policy
No
X-Content-Type-Options
No
Content-Security-Policy
No
Strict-Transport-Security
No
Cross-Origin-Opener-Policy
No
Cross-Origin-Embedder-Policy
No
Cross-Origin-Resource-Policy
No

IP lookup

IP address
122.201.80.143
IP version
4

Redirects

Redirect chain
  • https://stmalachychicago.mohsenmeysami.com

Page links

Internal links
1

Registration record

Registrar
Tucows Domains Inc.
Registered
Updated
Expires
Status
  • clientTransferProhibited https://icann.org/epp
  • clientUpdateProhibited https://icann.org/epp
Nameservers
  • ns1.whois.net.au
  • ns2.whois.net.au

HTTP headers

Response headers
Server
Apache
Content-type
text/html; charset=UTF-8
Original source fields · JSON
Caa records
{
    "domain": "stmalachychicago.mohsenmeysami.com"
}
Protective DNS results
{
    "resolvers": 12,
    "blocked_by": [
        "CloudFlare Family"
    ],
    "blocked_count": 1
}
Web archive observations
{
    "last": "2026-11-02T08:55:57Z",
    "first": "2026-11-02T08:55:57Z",
    "changes": 0,
    "days_archived": 1,
    "avg_page_bytes": 26113
}
Page title and metadata
{
    "title": "Document - isdP"
}
Trackers
{
    "requests": 3,
    "trackers": [
        {
            "name": "Google Fonts",
            "company": "Google",
            "country": "US",
            "category": "Hosting",
            "requests": 1
        },
        {
            "name": "Google Static",
            "company": "Google",
            "country": "US",
            "category": "Hosting",
            "requests": 1
        }
    ]
}
Forms and mixed content
{
    "third_party_scripts": 0
}
Status
{
    "up": true,
    "code": 200,
    "timings": {
        "dns": 20,
        "tls": 295,
        "wait": 2769,
        "connect": 291,
        "download": 579
    },
    "response_ms": 3954
}
TLS connection
{
    "alpn": "http/1.1",
    "cipher": "TLS_AES_256_GCM_SHA384",
    "protocol": "TLSv1.3",
    "versions": [
        "TLSv1.2",
        "TLSv1.3"
    ],
    "authorized": true,
    "forward_secrecy": true
}
Ports
{
    "open": [
        25,
        53,
        80,
        110,
        143,
        443,
        587,
        993,
        995
    ]
}
Carbon
{
    "bytes": 43982,
    "co2_grams": 0.0016,
    "cleaner_than": 40
}
Dns server
{
    "ns": [
        {
            "ip": "122.201.80.143",
            "host": "ns2.australiawhois.com"
        },
        {
            "ip": "122.201.80.143",
            "host": "ns1.australiawhois.com"
        }
    ],
    "zone": "mohsenmeysami.com"
}
Location
{
    "ip": "122.201.80.143",
    "asn": "38719",
    "org": "Dreamscape Networks PTY LTD",
    "city": "Sydney",
    "country": "AU"
}
Ssl
{
    "issuer": "Let's Encrypt / YR2",
    "subject": "*.mohsenmeysami.com"
}
DNS records
{
    "A": [
        "122.201.80.143"
    ]
}
Dnssec
{
    "ds": false,
    "rrsig": false,
    "dnskey": false
}
Hsts
{
    "message": "Site does not serve any HSTS headers."
}
HTTP security policies
{
    "xFrameOptions": false,
    "referrerPolicy": false,
    "xXSSProtection": false,
    "permissionsPolicy": false,
    "xContentTypeOptions": false,
    "contentSecurityPolicy": false,
    "strictTransportPolicy": false,
    "crossOriginOpenerPolicy": false,
    "crossOriginEmbedderPolicy": false,
    "crossOriginResourcePolicy": false
}
Get ip
{
    "ip": "122.201.80.143",
    "family": 4
}
Redirects
{
    "chain": [
        "https://stmalachychicago.mohsenmeysami.com"
    ]
}
Page links
{
    "internal_count": 1
}
Registration record
{
    "registrar": "Tucows Domains Inc.",
    "created": "2017-03-10T12:40:35Z",
    "updated": "2026-02-12T00:56:03Z",
    "expires": "2028-03-10T12:40:35Z",
    "status": [
        "clientTransferProhibited https://icann.org/epp",
        "clientUpdateProhibited https://icann.org/epp"
    ],
    "nameservers": [
        "ns1.whois.net.au",
        "ns2.whois.net.au"
    ]
}
HTTP headers
{
    "headers": {
        "server": "Apache",
        "content-type": "text/html; charset=UTF-8"
    }
}
Network Security Intelligence
CF Cloudflare Radar Verdict Malicious
Security threats Phishing Phishing

Questions about stmalachychicago.mohsenmeysami.com

Is stmalachychicago.mohsenmeysami.com legit?

PhishDestroy rates stmalachychicago.mohsenmeysami.com as critical risk (90/100) from the recorded evidence; it was first recorded on 2026-11-02. Stored VirusTotal result: 3/92 engines flagged. malicious: 3. suspicious: 0. Analysis time (as stored): 2026-11-01T16:46:35Z. Retrieved (as stored): 2026-11-02T09:26:11Z. Google Safe Browsing flags it. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.

Is stmalachychicago.mohsenmeysami.com safe to connect a wallet?

This report does not record which wallet requests stmalachychicago.mohsenmeysami.com makes. Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions there. A confirmed blockchain transaction cannot be reversed.

What should I do if I used stmalachychicago.mohsenmeysami.com?

It depends on what you did. If you entered a password, change it, and also on every other site where you used the same password; turn on two-factor authentication where it is offered. If you paid or gave card or bank details, contact your bank or payment service through the contacts on your card or its official website. If you only connected a wallet, disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds. If you signed a token approval or permit, revoke it with a token-approval checker. If you shared a seed phrase or private key, treat the wallet as compromised and move the remaining funds to a new wallet with a new seed phrase. If you downloaded a file, do not open it and scan the device with security software. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority; a report does not guarantee that money is returned. Step-by-step help: emergency guide.

Explore

Blocklist matchesPhishDestroy · no match in the other 11 1
PhishDestroy PhishDestroy list View source

Last checked

Stored Capture · 6 captures

All capture links and hashes (6)

Domain details

Domain
Google Safe Browsing Flagged Social engineering checked Nov 2, 2026
IP Reputation Australia122.201.80.143 abuse score 23/100 8 reports Email SpamHackingBrute-Force checked Nov 2, 2026 last reported
Registrar (base domain) TUCOWS.COM, CO CA(CA)
Registration (base domain)mohsenmeysami.com · Created Mar 10, 2017 — Expires Mar 10, 2028
Elapsed Since First Report 14h
What we count Raw elapsed time since the first stored abuse report. It is not a registrar response-time measurement. Latest observed status: Last known active.
What each report contains Stored outgoing-report records may reference evidence available at the time, such as vendor verdicts, registration data, hosting details, classifications, or screenshots. This page does not infer the exact payload delivered, receipt, acknowledgement, or action by a recipient.
HTTP Status200
LLM Report Plain-text dossier structured for AI agents
Technical detailsProvenance & timestamps
First DetectedNov 2, 2026
DOM Analysisanalyzed Nov 2, 2026score 15/1002 brand signals
Submitted URLhttp://www.stmalachychicago.mohsenmeysami.com/
Favicon Hash
Observed page title
Document - isdP
Automated brand references
Across Near
TLS Certificate
Issued by YR2 · stored validity ends in 84 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
Australia122.201.80.143
Network ASN
AS38719
AS name
DREAMSCAPE-AS-AP - Dreamscape Networks Limited, AU
Organization
Dreamscape Networks PTY LTD
Observed location
AustraliaSydney, AU
Server header
Apache

Nameservers 2

  • ns1.whois.net.au
  • ns2.whois.net.au

Location describes the IP network.

TLS certificate

Issuer
YR2
Valid from
2026-10-28 09:57:33
Valid until
2027-01-26 09:57:32
Hostname coverage
Stored certificate dates valid
Validity
Within stored validity dates
Collection source
PhishDestroy collector
Certificate fingerprint971617e12a55e4298f26f3a5c90a7b4e9a5351fcf02596fbb56fee298c367e81
Certificate names · 2 SANs
  • *.mohsenmeysami.com
  • mohsenmeysami.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-11-02 12:07:51 UTC

The site was serving its pages at the latest check.

Technical details
Primary outcome Live content reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Live content Ordinary HTTP content served 90% 2026-11-02 12:07:51 UTC
RDAP registration
Observed timeline last reachable: 2026-11-02 12:07:51 UTC last content: 2026-11-02 12:07:51 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologies · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

3 / 92 security vendors flagged this domain
View on VT
Last analyzed First positive detection
CRDF
SOCRadar
Gridinsoft

Archived Evidence

Wayback Machine Snapshot
View Archive
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of stmalachychicago.mohsenmeysami.com · checked Nov 2, 2026

55
Needs Work
Performance
FCP
2.58 s
First Contentful Paint
LCP
3.63 s
Largest Contentful Paint
CLS
0.823
Cumulative Layout Shift
TBT
0 ms
Total Blocking Time
SI
7.27 s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://www.stmalachychicago.mohsenmeysami.com/
Document - oFMC
Response
HTTP 200
HTML body
43.1 KB
Compressed
25.0 KB
Links
6 internal · 0 external
Detected technologies
vueapache
Selected response headers
Server: Apache
Content-Type: text/html; charset=UTF-8
HSTS: not observed DNSSEC: not observed WAF / firewall: not observed Cloaking flag: not observed
Favicon fingerprint: 23de2d934b58eb59e9fdf2cb9a9ef9049678c9ece35bdc08fb50c0c26b07c93e
Saved response-header values · 6
Connection
Keep-Alive
Content-Type
text/html; charset=UTF-8
Date
Mon, 02 Nov 2026 08:55:15 GMT
Keep-Alive
timeout=5, max=100
Server
Apache
Transfer-Encoding
chunked

Values retained by the collector; long values may be shortened during collection.

Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Captured network requests

Network requests: 5 SHA-256 hashes: 5 URLScan scan:

Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-11-02 08:57 UTC.

Open this scan on URLScan 01a19b76-29a5-71e8-9be0-e70137d73313 ↗

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

Page titles differ

Our scanner could not complete this check.

Browser
Document - isdP
Crawler
Document - AeynK
stmalachychicago.mohsenmeysami.com
Stored observation history4

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Domain monitor · Recorded state

    Reachable→Unavailable

  2. Availability monitor · Recorded state

    live_content

    content_served

  3. Google Safe Browsing · Threat flag

    No flag recorded→Flag recorded

  4. Domain monitor · First collection record

    Reachable

All retained availability observations5

Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.

  1. current_http_probelive_content
    Observation source
    current_http_probe
    Cause
    content_served
    Availability state
    content_live
    Content state
    served_at_root
    DNS state
    resolved
    DNS response code
    NOERROR
    Recorded HTTP status
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    90
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-11-02 13:07:51.000000
    Evidence SHA-256
    cac9e1d602d7fcd58c41a9e3b0bb789bfe4b61c18bef63b575ee2e0ee734ba2e
    HTTP probe value as recorded
    200
    Evidence timestamp as recorded
    2026-11-02 13:07:51
    Evidence reason
    alive_content
  2. http_observationlive_content
    Observation source
    http_observation
    Cause
    content_served
    Availability state
    content_live
    Content state
    served_at_root
    DNS state
    unknown
    Recorded HTTP status
    200
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    90
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-11-02 13:07:51.000000
    Evidence SHA-256
    cac9e1d602d7fcd58c41a9e3b0bb789bfe4b61c18bef63b575ee2e0ee734ba2e
    HTTP probe value as recorded
    200
    Evidence timestamp as recorded
    2026-11-02 13:07:51
    Evidence reason
    alive_content
  3. dns_observationunknown
    Observation source
    dns_observation
    Cause
    probe_inconclusive
    Availability state
    unreachable
    Content state
    unknown
    DNS state
    resolved
    DNS response code
    NOERROR
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    20
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-11-02 11:20:40.834886
    Evidence SHA-256
    6b72dd67b3184766be6163de1e7b9604e36c85641b1d2618e2bdbe21069459a2
    HTTP probe value as recorded
    0 · no HTTP response code recorded
    Evidence timestamp as recorded
    2026-11-02 11:20:40.834886
    Evidence reason
  4. current_state_backfillunknown
    Observation source
    current_state_backfill
    Cause
    probe_inconclusive
    Availability state
    unreachable
    Content state
    unknown
    DNS state
    stale
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    20
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-11-02 09:54:56.000000
    Evidence SHA-256
    15a8143bcb9fc35bc9aa552257c1e100d58fce83b659f5860263ebb50e394a2d
    HTTP probe value as recorded
    0 · no HTTP response code recorded
    Evidence timestamp as recorded
    2026-11-02 09:54:56
    Evidence reason
  5. http_observationunknown
    Observation source
    http_observation
    Cause
    probe_inconclusive
    Availability state
    unreachable
    Content state
    unknown
    DNS state
    unknown
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    20
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-11-02 09:54:56.000000
    Evidence SHA-256
    15a8143bcb9fc35bc9aa552257c1e100d58fce83b659f5860263ebb50e394a2d
    HTTP probe value as recorded
    0 · no HTTP response code recorded
    Evidence timestamp as recorded
    2026-11-02 09:54:56
    Evidence reason

Threat Response Pipeline

  1. Discovery · recorded
  2. Analysis · recorded
  3. Monitoring · in progress

Recorded events: 12. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Pre-emptive Discovery & IngestionThreat Ingested Recorded: 1 of 1
  • Threat Ingested
    stmalachychicago.mohsenmeysami.com detected and queued for full analysis
Threat Intelligence ChecksURLScan.io Capture · URLScan Verdict · Cloudflare Radar Report · Web Archive · VirusTotal · Google Safe Browsing · Cloudflare Radar: Malicious · Forensic Evidence Collected · Technical Analysis Recorded · Content Observed Unavailable Recorded: 10 of 10
  • URLScan.io Capture
    Stored URLScan report with capture artifacts
  • URLScan Verdict
    URLScan classified the page as malicious · Score: 100
  • Cloudflare Radar Report
    A stored Cloudflare Radar report is available. The report link alone does not mean that the domain was classified as malicious, and it does not prove that every network field was captured.
  • Web Archive
    Preserved in the Wayback Machine: historical evidence archived
  • VirusTotal
    Detections recorded on VirusTotal: 3/92
  • Google Safe Browsing
    Listed as unsafe by Google Safe Browsing (Google Transparency Report)
  • Cloudflare Radar: Malicious
    Cloudflare Radar classified this domain as Security threats, phishing
  • Forensic Evidence Collected
    Stored evidence from URLScan.io, stored screenshot
  • Technical Analysis Recorded
    The report contains stored results of technology detection or forensic analysis.
  • Content Observed Unavailable
    Monitoring recorded an unavailable response (HTTP 200); the cause was not independently established.
Publication & AvailabilityDestroyList Published · Monitoring Continues Recorded: 1 of 2
  • DestroyList Published
    Listed in the public repository PhishDestroy/DestroyList
  • Monitoring Continues
    The domain remains reachable or access-restricted; future checks may update this observation.

Recorded activity

6 entries
  1. Cloudflare Radar

    Phishing

    View source
  2. Google Safe Browsing

    Threat flag recorded

    View source
  3. Wayback Machine

    Page archived

    View source
  4. Added to PhishDestroy

    stmalachychicago.mohsenmeysami.com

    View source
  5. URLScan

    Page captured

    View source
  6. VirusTotal

    3/92 engine detections

    View source
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

All stored records by source

Browse this domain’s complete history by source. The download includes every record of the selected source. Dates retain their original field labels.

Download all records as JSON

Evidence & External Reports

Deep Analysis
Help & reporting

Were You Affected by This Site?

3 evidence signal groups linked Last known active
You are not alone and there is nothing to be ashamed of. Scammers are sophisticated criminals who exploit trust. Reporting your experience is the most powerful weapon against fraud — your report can prevent others from becoming victims and help law enforcement take action. Silence is the scammer’s greatest advantage. Break it.
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.

Official reporting routes

More official reporting routes
FTC ReportFraud United States

Report scams and fraud to the US Federal Trade Commission. Reports go into a database used by law enforcement.

IdentityTheft.gov United States

Official identity theft report with a step-by-step recovery plan.

CISA United States

Report cyber incidents and phishing to the US Cybersecurity and Infrastructure Security Agency.

CSIRTs Network European Union

Directory of national incident response teams (CSIRTs) in the EU. Find the team for your country.

FIRST Worldwide

Worldwide directory of incident response teams, searchable by country and sector.

ReportCyber Australia

Report cybercrime to the Australian Cyber Security Centre and police.

Scamwatch Australia

Report scams to the National Anti-Scam Centre run by the ACCC.

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

If you made a payment, contact your bank or payment service through its official contacts as soon as possible. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned.

Scammers are criminals. Filing a report creates a legal record and helps protect others.

97-country directory

Template-based draft • optional AI wording assistance requires separate consent

Review and submit it yourself
After a phishing incident

Recommendations & Advice for Victims

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

What should I do immediately?

Urgent

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Entered a password — change it on that service and on every other site where you used the same password
  • Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
  • Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website

What information should I collect for my report?

FBI guidelines

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Exact dates & times — of each transaction and first contact with scammer
  • Screenshots — scam website, chat messages, emails, wallet transactions, social media
  • All URLs & domains used by the scammer (including stmalachychicago.mohsenmeysami.com)
  • Communications — emails, texts, phone numbers, usernames the scammer used

Even if you don't have all details — file a report anyway. Partial information still helps investigations.

Where should I report the scam?

  • FBI IC3 — Internet Crime Complaint Center (US federal reporting)
  • Europol — European cybercrime reporting (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Local police — creates an official record, even if they can't act immediately

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
  • Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
  • Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect

How can I protect myself in the future?

  • Bookmark official sites — never click links from emails, DMs, or ads
  • Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
  • "Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/stmalachychicago.mohsenmeysami.com"
  title="PhishDestroy threat report for stmalachychicago.mohsenmeysami.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>