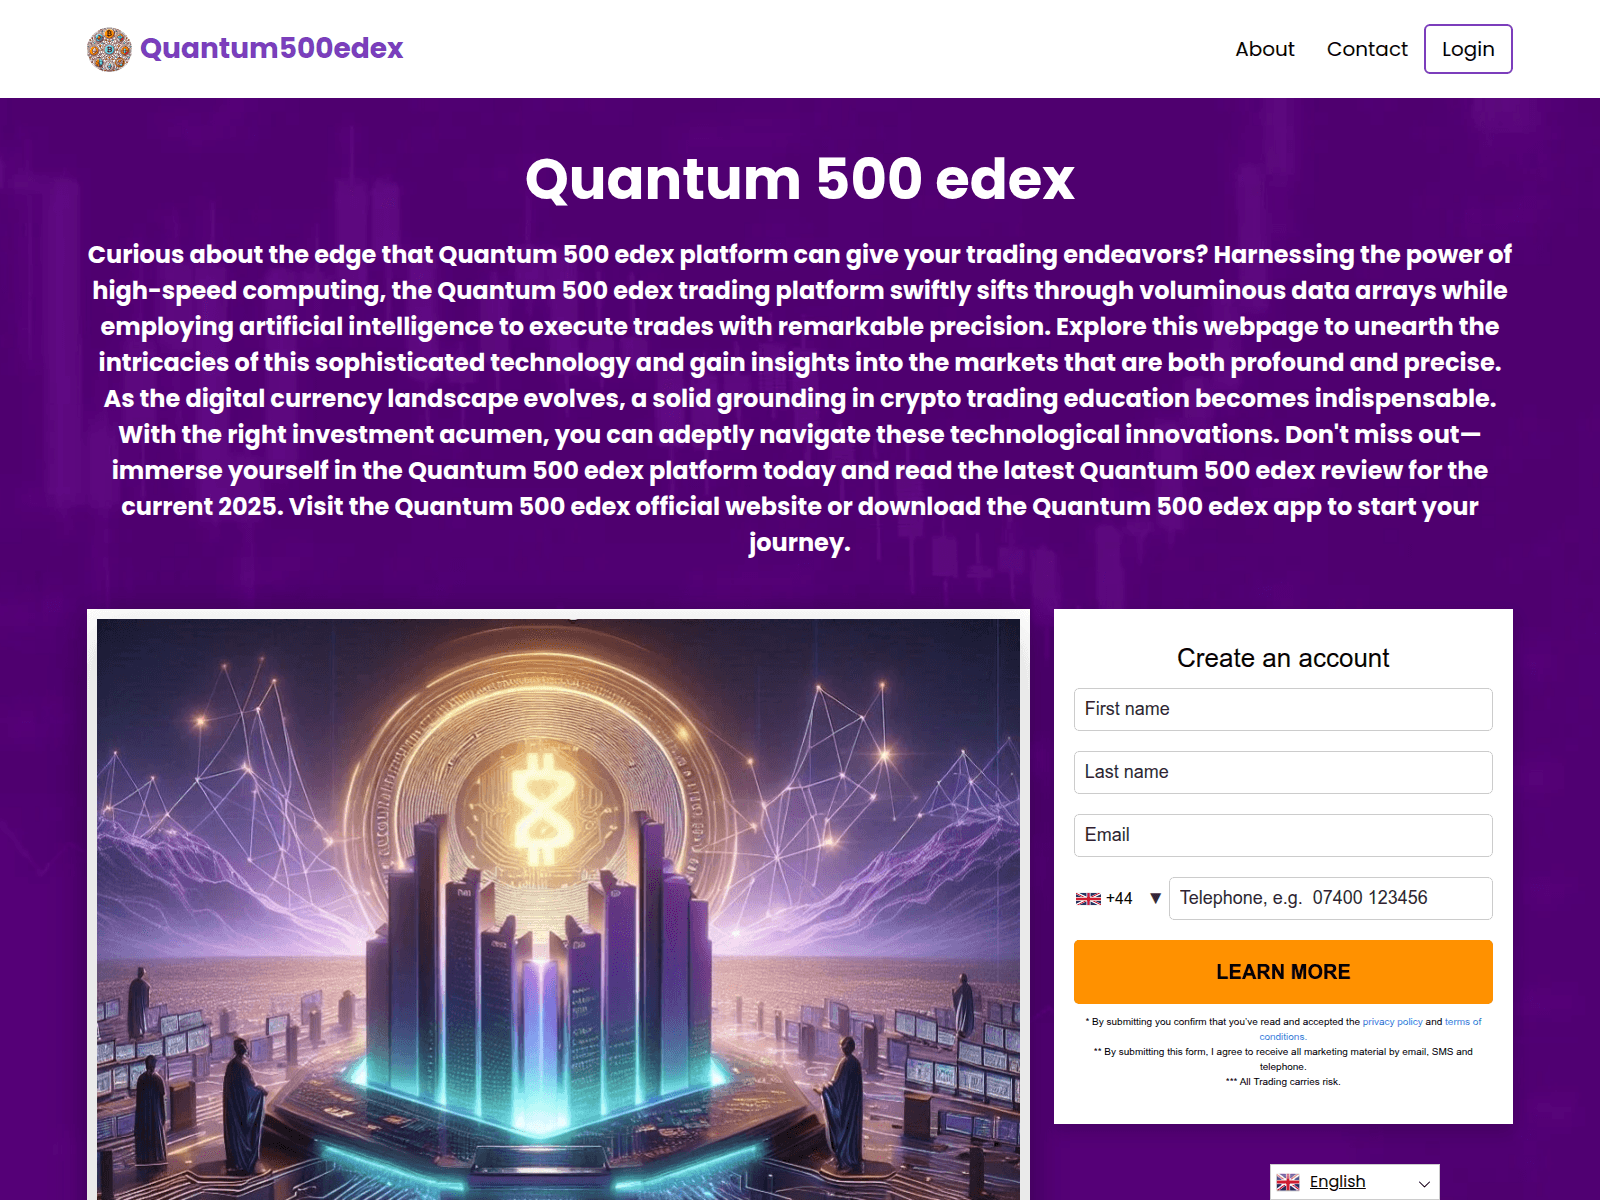

 185.98.60.138
VirusTotal

15 / 92 engine detections
Analysis:
Open report VirusTotalOriginal source recordObserved: 11 fields
Observed: · Retrieved:
Vendor result counts
- Timeout
- 0
- Harmless
- 45
- Malicious
- 14
- Suspicious
- 1
- Undetected
- 32
Vendor labels
- ESET
- phishing
- VIPRE
- malware
- G-Data
- phishing
- Lionic
- phishing
- Sophos
- phishing
- CyRadar
- phishing
- Webroot
- malicious
- Emsisoft
- malware
- Fortinet
- phishing
- SOCRadar
- phishing
- Seclookup
- malicious
- Gridinsoft
- suspicious
- BitDefender
- phishing
- alphaMountain.ai
- phishing
- Forcepoint ThreatSeeker
- phishing
Reputation score
0Created
Updated
First seen
DNS records
- TTL, seconds
- 300
- Type
- SOA
- Responsible mailbox
- admin.cryptodns.co
- Value
- ns1.cryptodns.co
- TTL, seconds
- 300
- Type
- NS
- Value
- ns2.cryptodns.co
- TTL, seconds
- 300
- Type
- NS
- Value
- ns1.cryptodns.co
- TTL, seconds
- 300
- Type
- A
- Value
- 185.98.60.138
DNS records observed
JARM fingerprint
1dd40d40d00040d00042d43d000000831b6af40378e2dd35eeac4e9311926eCertificate
- Subject alternative names
- *.quantum-edex.app
- quantum-edex.app
- Issuer
- Let's Encrypt / YE1
- Serial
- 54aac76aeba9d5f5620a4e9c57b20201d0b
- SHA-256
- 191d3a8a5fc0b2d891bb69c6560e7f6fee89e1d3685c3e3f4466ac03e35bd72b
- Subject
- quantum-edex.app
- Valid until
- Valid from
Registry data (RDAP)
- Status
- client transfer prohibited
- Registry events
- Expiration
- Last changed
- Registration
- Registrar expiration
- Last RDAP database update
- Registrar
- TLD Registrar Solutions Ltd.
- Registrar IANA ID
- 1564
Original source fields · JSON
| Vendor result counts | {
"timeout": 0,
"harmless": 45,
"malicious": 14,
"suspicious": 1,
"undetected": 32
} |
|---|---|
| Vendor labels | {
"ESET": "phishing",
"VIPRE": "malware",
"G-Data": "phishing",
"Lionic": "phishing",
"Sophos": "phishing",
"CyRadar": "phishing",
"Webroot": "malicious",
"Emsisoft": "malware",
"Fortinet": "phishing",
"SOCRadar": "phishing",
"Seclookup": "malicious",
"Gridinsoft": "suspicious",
"BitDefender": "phishing",
"alphaMountain.ai": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputation | 0 |
| Created | 2024-10-04T00:00:00Z |
| Updated | 2024-10-04T00:00:00Z |
| First seen | 2024-10-04T11:46:41Z |
| DNS records | [
{
"ttl": 300,
"type": "SOA",
"rname": "admin.cryptodns.co",
"value": "ns1.cryptodns.co"
},
{
"ttl": 300,
"type": "NS",
"value": "ns2.cryptodns.co"
},
{
"ttl": 300,
"type": "NS",
"value": "ns1.cryptodns.co"
},
{
"ttl": 300,
"type": "A",
"value": "185.98.60.138"
}
] |
| Dns at | 2026-11-01T14:27:12Z |
| Jarm | 1dd40d40d00040d00042d43d000000831b6af40378e2dd35eeac4e9311926e |
| Certificate | {
"san": [
"*.quantum-edex.app",
"quantum-edex.app"
],
"issuer": "Let's Encrypt / YE1",
"serial": "54aac76aeba9d5f5620a4e9c57b20201d0b",
"sha256": "191d3a8a5fc0b2d891bb69c6560e7f6fee89e1d3685c3e3f4466ac03e35bd72b",
"subject": "quantum-edex.app",
"valid_to": "2026-12-17T18:02:52Z",
"valid_from": "2026-09-18T18:02:53Z"
} |
| Registry data | {
"status": [
"client transfer prohibited"
],
"events": {
"expiration": "2027-10-04T10:51:38Z",
"last changed": "2026-05-20T14:03:02Z",
"registration": "2024-10-04T10:51:38Z",
"registrar expiration": "2027-10-04T10:51:38Z",
"last update of RDAP database": "2026-10-29T08:59:01Z"
},
"registrar": "TLD Registrar Solutions Ltd.",
"registrar_iana_id": "1564"
} |
Separate collector summary
This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.
- source
- VirusTotal
- scope
- unknown
- result_state
- observed
- numerator
- 15
- denominator
- 92
- malicious
- null
- suspicious
- null
- vendors
- ["alphaMountain.ai","BitDefender","CyRadar","ESET","Emsisoft","Forcepoint ThreatSeeker","Fortinet","G-Data","Gridinsoft","Lionic","Seclookup","SOCRadar","Sophos","VIPRE","Webroot"]
- observed_at
- 2026-11-01 13:09:52
- checked_at
- 2026-11-02 11:23:23
- fetched_at
- 2026-11-02 10:23:23
- time_basis
- as stored; legacy timezone not established


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT