VirusTotal
6 / 91 engine detections
Open report

mexc-partner.com is a phishing page detected by PhishDestroy on 2026-09-19. Risk: critical (95/100). Registrar: Megazone. Status: Last known active. Hosting: The Constant Company, LLC. PhishDestroy sent 1 abuse report. VirusTotal: 6/91 engines flag it. Do not enter credentials or connect a wallet.
“mexc 거래소 | MEXC Exchange”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@hosting.kr.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
6 / 91 engine detections
Open reportchecked — no detections recorded
Open report3 community references
Open reportprovider verdict: clean
Open reportNo threat flag
Open reportNo malicious flag
Open reportResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
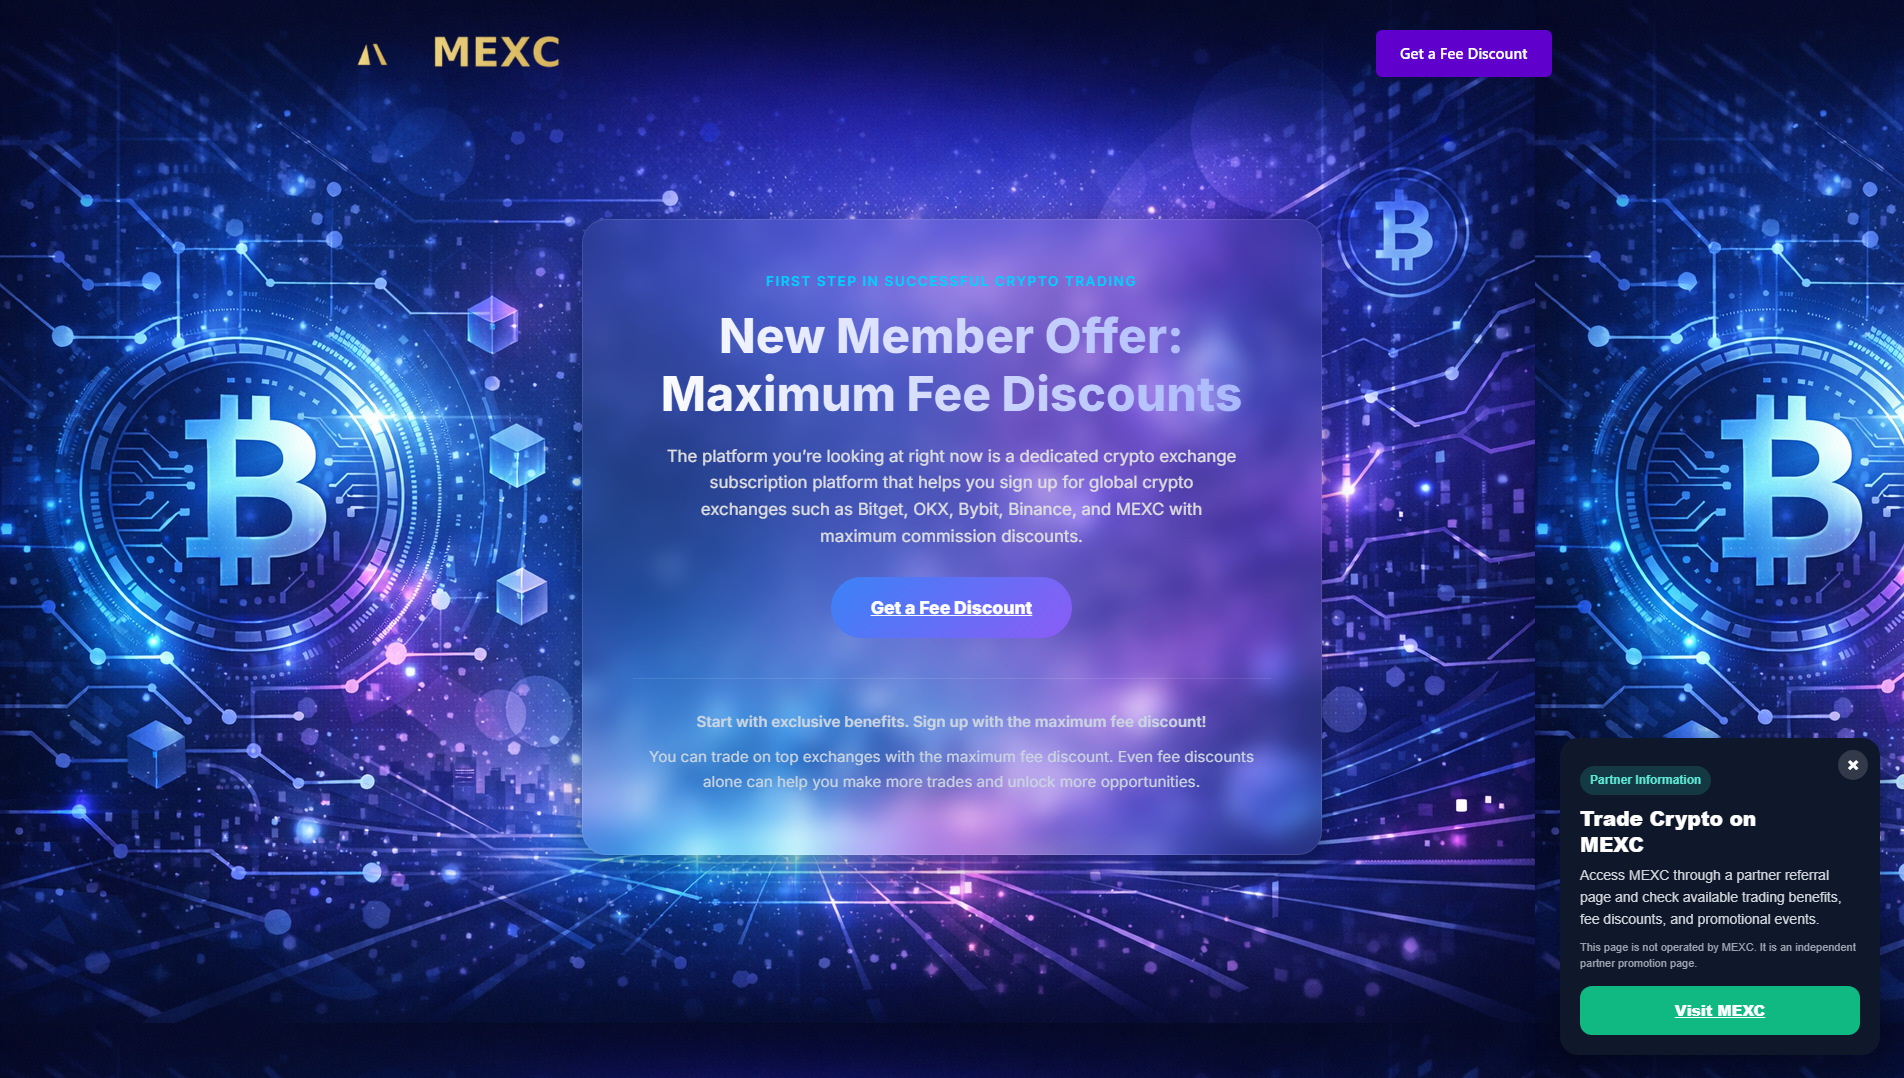
mexc-partner.com poses as the cryptocurrency exchange MEXC. Its page title, "mexc 거래소 | MEXC Exchange" (거래소 is Korean for "exchange"), shows it is aimed at Korean-speaking traders. The "partner" wording borrows the look of an official affiliate or partnership portal. PhishDestroy first flagged it on 2026-09-19, and the page was still up and serving content on 2026-10-19.
Sites that impersonate an exchange copy the real brand's look so visitors believe they are on MEXC or an authorised partner. From there, the victim is typically asked to log in, which hands account credentials and one-time codes to the operators. Alternatively, the victim is told to deposit crypto into a "partner" account that the attackers control. Funds sent there cannot be recovered, and stolen logins can be used to empty the victim's real MEXC account.
Six of 91 VirusTotal engines flagged the domain as of 2026-09-29: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar and VIPRE. That count is modest, so many security tools will still let the page load without warning. Stronger backing comes from the blocklists. MetaMask and SEAL list the domain alongside PhishDestroy, which means wallet users get protection from tools that rely on those lists. Two AlienVault OTX threat pulses also reference the domain.
The domain was registered on 2024-07-25 through Megazone Corp., dba HOSTING.KR, more than two years before PhishDestroy detected it. That gap suggests a name held in reserve or reused rather than one created just for this campaign. It resolves to 141.164.54.198 on The Constant Company, LLC network, located in South Korea. A Korean registrar, Korean hosting and a Korean page title together fit an operation focused on the Korean market.
Do not log in or deposit anything on this site. If you entered your MEXC credentials, change your password right away from the official app and reset two-factor authentication. Then review active sessions, API keys and withdrawal whitelist addresses for anything you did not add. If you sent crypto to an address shown on the page, report the transaction to MEXC support and the police, and keep your transaction hashes. Ignore anyone who later offers to recover the funds for a fee. Defenders should block the domain and its IP and alert Korean-speaking users about fake MEXC "partner" pages.
Stored page, network and scanner observations, grouped by source and observation time.
Observed: · Retrieved:
| Uuid | 01a0b8be-eb8f-7391-a82d-518db20513b9 |
|---|---|
| Final url | https://mexc-partner.com/ |
| Status | 200 |
| Redirected | https-only |
| Redirects | [
{
"to": "https://mexc-partner.com/",
"from": "http://mexc-partner.com/",
"status": 307
}
] |
| Ip | 141.164.54.198 |
| Ptr | 141.164.54.198.vultrusercontent.com |
| Contacted domains | [
"fonts.gstatic.com",
"fonts.googleapis.com",
"wordpress-1315258-5831060.cloudwaysapps.com"
] |
| Contacted IP addresses | [
"173.194.114.94",
"172.217.197.95",
"141.164.54.198"
] |
| Asns | [
"15169",
"20473"
] |
| Countries | [
"US",
"KR"
] |
| Linked domains | [
"www.mexc.com"
] |
| Document hash | e1fe33ab5347bec43d56e347d2dc2f28d8deff32099fbd7b8134a1b89b0b2b9c |
| Script hashes | [
"56fa17293a0db4bfdeea7ec26d8d6a77b4960f3f5a83a73eea8b82460597d92d",
"cb6f2d32c49d1c2b25e9ffc9aaafa3f83075346c01bcd4ae6eb187392a4292cf",
"5274f11e6fb32ae0cf2dfb9f8043272865c397a7c4223b4cfa7d50ea52fbde89",
"83eda8e5540512ca57e2216df1c90dd4bb2cb49f3f58188345de9582855648e0",
"8dd3674bae946e2e04bc962443f0994d736a761bb28e816c20aee6391ef242ed",
"c66f47147d5fe3cceeaa47a93ff7440a328f859b049deec2f9d8f414e9137474",
"b7a27a4b4abfc300eaf7d9151afeef8df2663d98586e38f59f91bbe98ef30af7",
"1842d6e4d3c7399fdb01ab4b0a7dd5c1d9c096110de0532181ed581f14e9e813",
"77c0a6d635dad44b53a9eb9f0f367a1bd3bf3620c0e41d3a4c15d1313f2553f0",
"063840b4b3f5869e0f0d078bab8bd29cfb3a59ee85e8e3edbbec35a8fe846fd3"
] |
| Globals | [
"breeze_prefetch",
"ready",
"get_prefetch_key",
"search_for_banned_links",
"breeze_ignore_special_links",
"jQuery",
"astra",
"astraGetParents",
"astraToggleClass",
"astraTriggerEvent",
"astraSmoothScroll",
"astScrollToTopHandler",
"popupTriggerClick",
"AstraToggleSubMenu",
"AstraToggleSetup",
"astraNavMenuToggle",
"webpackChunkelementorFrontend",
"elementorModules",
"elementorFrontendConfig",
"elementorFrontend",
"_wpemojiSettings",
"twemoji",
"wp",
"lazyloadRunObserver",
"events"
] |
| Storage keys | [
"wpEmojiSettingsSupports"
] |
| Tls | {
"san": [
"mexc-partner.com"
],
"cipher": "AES_256_GCM",
"issuer": "YR1",
"subject": "mexc-partner.com",
"protocol": "TLS 1.3",
"valid_to": "2026-12-09T16:11:50Z",
"valid_from": "2026-09-10T16:11:51Z"
} |
| Domain age days | 786 |
| Apex age days | 786 |
| Tls age days | 8 |
| Tls valid days | 89 |
| Requests | 25 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 60,
"malicious": true
},
"overall": {
"score": 0,
"malicious": false
}
} |
| HTTP headers | {
"server": "nginx",
"content-type": "text/html; charset=UTF-8"
} |
Observed: · Retrieved:
| Uuid | 69036e81-a3f3-41e0-989e-42d5f4134b16 |
|---|---|
| Final url | https://mexc-partner.com/ |
| Status | 200 |
| History | [
{
"url": "https://mexc-partner.com/",
"status": 200
}
] |
| DOM structure hash | f1124b7c6c510414eec022b7068a149961eff97a9b56efa263f226dfb3fe0176 |
| Document hash | fba72a1d1ccaf387e065b86ec349a9800aee68d0fd2027dc867948973a9cc793 |
| Radar rank | {
"bucket": ">200000"
} |
| DNS records | [
{
"name": "mexc-partner.com",
"type": "A",
"value": "141.164.54.198"
}
] |
| Dnssec valid | false |
| Ip | 141.164.54.198 |
| Registration record | {
"registrar": "Megazone Corp., dba HOSTING.KR",
"created": "2024-07-25T06:37:20Z",
"updated": "2026-01-04T03:58:16Z",
"expires": "2027-07-25T06:37:20Z",
"nameservers": [
"ns1.hosting.co.kr",
"ns2.hosting.co.kr",
"ns3.hosting.co.kr",
"ns4.hosting.co.kr"
]
} |
Observed: · Retrieved:
| Vendor result counts | {
"timeout": 0,
"harmless": 53,
"malicious": 4,
"suspicious": 1,
"undetected": 34
} |
|---|---|
| Vendor labels | {
"CRDF": "malicious",
"SOCRadar": "phishing",
"Gridinsoft": "suspicious",
"alphaMountain.ai": "phishing",
"Forcepoint ThreatSeeker": "phishing"
} |
| Reputation | 0 |
| Tags | [
"dga"
] |
| Registrar | Megazone Corp., dba HOSTING.KR |
| Created | 2024-07-25T12:00:00Z |
| Expires | 2027-07-25T06:37:20Z |
| Updated | 2026-01-04T12:00:00Z |
| First seen | 2024-07-28T16:03:30Z |
| DNS records | [
{
"ttl": 300,
"type": "A",
"value": "141.164.54.198"
},
{
"ttl": 180,
"type": "SOA",
"rname": "admin.mexc-partner.com",
"value": "ns1.hosting.co.kr"
},
{
"ttl": 180,
"type": "NS",
"value": "ns4.hosting.co.kr"
},
{
"ttl": 180,
"type": "NS",
"value": "ns2.hosting.co.kr"
},
{
"ttl": 180,
"type": "NS",
"value": "ns1.hosting.co.kr"
},
{
"ttl": 180,
"type": "NS",
"value": "ns3.hosting.co.kr"
}
] |
| Dns at | 2026-10-21T08:27:05Z |
| Jarm | 2ad2ad16d2ad2ad00042d42d000000df133019600a83abfb096ff3e86cd79d |
| Certificate | {
"san": [
"mexc-partner.com"
],
"issuer": "Let's Encrypt / YR1",
"serial": "6ab9b6e2ccc3740b96f409e16dc6d2e440c",
"sha256": "be1e1dfea133a7e8079b1d16fd1ef3f59fdfcbf8d57eb8c4ead5ba3a0c9f2547",
"subject": "mexc-partner.com",
"valid_to": "2026-12-09T16:11:50Z",
"valid_from": "2026-09-10T16:11:51Z"
} |
| Registration record | {
"registrar": "Megazone Corp., dba HOSTING.KR",
"registrar_iana_id": "1489",
"registrar_url": "http://HOSTING.KR",
"created": "2024-07-25T06:37:20Z",
"updated": "2026-01-04T03:58:16Z",
"expires": "2027-07-25T12:00:00Z",
"status": [
"clientTransferProhibited",
"ok"
],
"nameservers": [
"ns1.hosting.co.kr",
"ns2.hosting.co.kr",
"ns3.hosting.co.kr",
"ns4.hosting.co.kr"
],
"dnssec": "unsigned"
} |
| Registry data | {
"status": [
"transfer prohibited"
],
"events": {
"expiration": "2027-07-25T06:37:20Z",
"last changed": "2026-01-04T12:58:16Z",
"registration": "2024-07-25T06:37:20Z",
"last update of RDAP database": "2026-01-04T12:58:16Z"
}
} |
No. PhishDestroy classifies mexc-partner.com as a phishing page (risk: critical, 95/100); it was first detected on 2026-09-19. VirusTotal: 6/91 engines flag it. Treat the site as unsafe.
No. Do not connect a wallet, sign messages or approve tokens on mexc-partner.com. Phishing sites ask for approvals (approve, setApprovalForAll, Permit2) that let the operator move your assets, and a confirmed transaction cannot be reversed.
Change every password you entered there and turn on two-factor authentication. If you connected a wallet or signed something, revoke the approvals and move the remaining funds to a new wallet; never share your seed phrase. Step-by-step help: emergency guide.
Last checked
 (KR)
ns1.hosting.co.krns2.hosting.co.krns3.hosting.co.krns4.hosting.co.krLocation describes the IP network.
be1e1dfea133a7e8079b1d16fd1ef3f59fdfcbf8d57eb8c4ead5ba3a0c9f2547mexc-partner.comSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of mexc-partner.com · checked Sep 19, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
mexc-partner.com
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
Unknown→live_content
content_served
live_content
content_served
0→2
3 community references
View sourceNo threat flag
View source6/91 engine detections
View sourcePD-20260919-F53227
Page captured
View sourcemexc-partner.com
View sourceRegistered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
PD-20260919-F53227 Recipient: abuse@hosting.kr If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.


Select your country to get official cybercrime contacts, or create a complaint draft →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
mexc-partner.com)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.