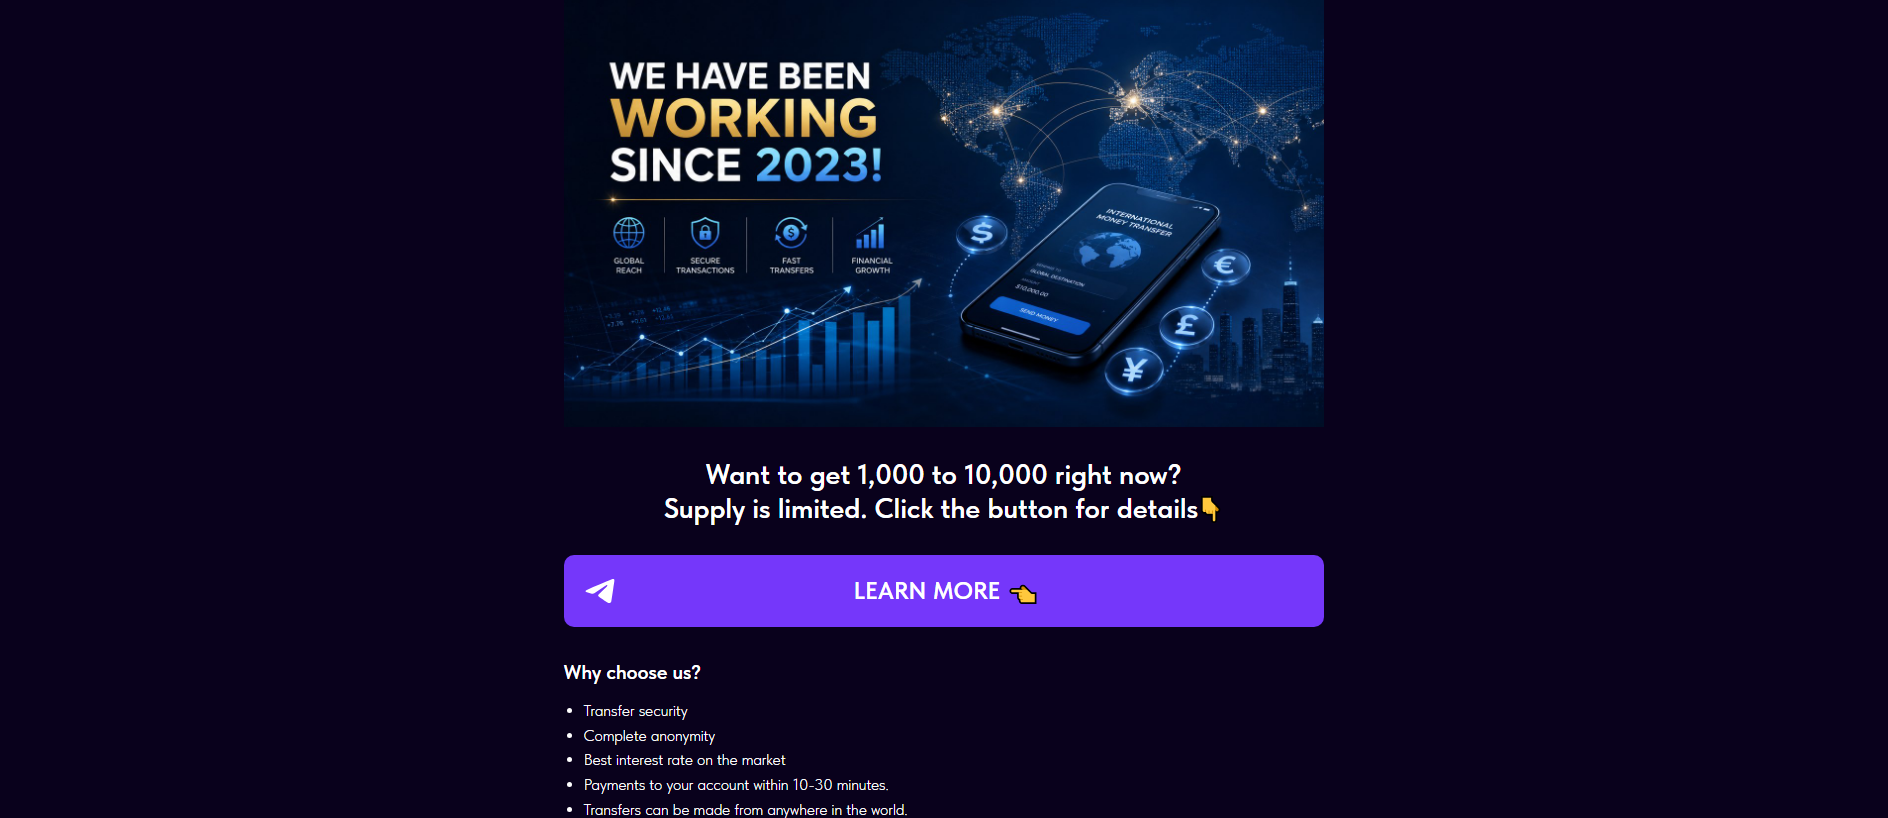
Fewmoretaps OU d/b/a T…
 172.67.136.104
URLScan

Malicious
Open reportURLScanOriginal source recordObserved: 23 fields
Observed: · Retrieved:
Report ID
01a06f2f-b2ef-70ab-81d2-4df299b6bdbfFinal URL
https://germanstakeearn.digital/HTTP response
200IP address
104.21.46.76Contacted domains
- static3.tildacdn.com
- connect.facebook.net
- stat.tildaapi.com
- static.tildacdn.com
- neo.tildacdn.com
- sysstat.tildacdn.com
Contacted IP addresses
- 185.129.100.115
- 159.69.130.130
- 5.101.37.37
- 194.48.203.181
- 157.240.0.6
- 104.21.46.76
Autonomous systems (ASN)
- 57724
- 24940
- 201589
- 205282
- 32934
- 13335
Server countries
- RU
- DE
- AM
- AE
Linked domains
- t.me
Social media links
- https://t.me/transferjames_bot
Document hash
db8f3bb8b0b2bf5ae055aa529540b7c1b10f6a31a23179b54f7aa02243d113abScript hashes
- cdf65e26b905a653bce60df182886b032b606940391badb1e3a655f434ca446c
- c82d6e0f0f4e4080e9cecc7858b8d66195e7f5896eaab04b38ae90573ff08d92
- 8cb5041c38c1a5f3f2c281ca561d6af51d5a74d27e6c6aeaccbb10e05fe00ecc
- 2f718826160d39cd3a9b9e23b5044ea7143c1413dce1779c4e68b750745193c0
- 090a7068a2209545279f858c6f41ff7ae42815e11c3d69463a2a2ea835282bd9
- 49a12dc318a43e850301b14ca9024d245a2b9cffae02180cc8b7974b12dd46ce
- 925c3cbd0a0bc5f56d8a8186b95323b2801036ce64d95db1c9c1ef63735d760c
- 5ef75137fa784d916c1731eb5c3700fdadaf7babc8c55a933cb52910249ce576
- 30299b6ef1aff24831fb728ee4edaf4fc02c8c7dd0806bfa90f3e3ea7fe2bb80
JavaScript globals
- t_fallback__init
- t_fallback__initTags
- t_fallback__reloadSRC
- t_fallback__handleTimeout
- t_fallback__loadAdvancedJS
- t_onReady
- t_onFuncLoad
- dataLayer
- fbq
- _fbq
- mainTracker
- tildastatcookie
- t_videoPlayer__init
- t_video__doRutubeCommand
- t_video__doVimeoCommand
- t_video__doBoomstreamCommand
- t_video__getPlayer
- t_video__initPlayer__youtube
- t_video__initPlayer__vimeo
- t_video__initPlayer__kinescope
- t_video__initPlayer__vkvideo
- t_video__initPlayer__rutube
- t_video__initPlayer__htmlVideo
- t_video__initPlayer__boomstream
- t_video_lazyload_init
- t_video_lazyload__addVideoWithCheckViewport
- t_video_lazyload__addVideo
- t_video_lazyload__removeVideo
- t_video_lazyload__setHeight
- t_video_lazyload__setMobileHeight
- t_video__createPlayer
- t_video_lazyload__overwriteParams
- t670_init
- t670_addImageEvents
- t670_handleRutube
- t670_show
- t670_pauseVideo
- t670_hide
- t670_addArrowHandlers
- t670_pauseAllVideos
Cookies
- _fbp
Browser storage keys
- lastExternalReferrer
- lastExternalReferrerTime
TLS session and certificate
- Subject alternative names
- germanstakeearn.digital
- *.germanstakeearn.digital
- Cipher
- AES_128_GCM
- Issuer
- WE1
- Subject
- germanstakeearn.digital
- Protocol
- TLS 1.3
- Valid until
- Valid from
Domain age, days
33Registered domain age, days
33Certificate age, days
33Certificate validity, days
90Page requests
36Provider verdicts
- Engine verdict
- Tags
- urlscan-ml
- urlscan-ml-60c5e22
- Score
- 93
- Malicious
- Yes
- Overall verdict
- Tags
- phishing
- Score
- 100
- Brands
- stake
- Malicious
- Yes
- Categories
- phishing
- URLScan verdict
- Tags
- phishing
- Score
- 100
- Brands
- Stake
- Malicious
- Yes
- Categories
- phishing
HTTP headers
- Server
- cloudflare
- Content-type
- text/html
Original source fields · JSON
| Uuid | 01a06f2f-b2ef-70ab-81d2-4df299b6bdbf |
|---|---|
| Final url | https://germanstakeearn.digital/ |
| Status | 200 |
| Ip | 104.21.46.76 |
| Contacted domains | [
"static3.tildacdn.com",
"connect.facebook.net",
"stat.tildaapi.com",
"static.tildacdn.com",
"neo.tildacdn.com",
"sysstat.tildacdn.com"
] |
| Contacted IP addresses | [
"185.129.100.115",
"159.69.130.130",
"5.101.37.37",
"194.48.203.181",
"157.240.0.6",
"104.21.46.76"
] |
| Asns | [
"57724",
"24940",
"201589",
"205282",
"32934",
"13335"
] |
| Countries | [
"RU",
"DE",
"AM",
"AE"
] |
| Linked domains | [
"t.me"
] |
| Social | [
"https://t.me/transferjames_bot"
] |
| Document hash | db8f3bb8b0b2bf5ae055aa529540b7c1b10f6a31a23179b54f7aa02243d113ab |
| Script hashes | [
"cdf65e26b905a653bce60df182886b032b606940391badb1e3a655f434ca446c",
"c82d6e0f0f4e4080e9cecc7858b8d66195e7f5896eaab04b38ae90573ff08d92",
"8cb5041c38c1a5f3f2c281ca561d6af51d5a74d27e6c6aeaccbb10e05fe00ecc",
"2f718826160d39cd3a9b9e23b5044ea7143c1413dce1779c4e68b750745193c0",
"090a7068a2209545279f858c6f41ff7ae42815e11c3d69463a2a2ea835282bd9",
"49a12dc318a43e850301b14ca9024d245a2b9cffae02180cc8b7974b12dd46ce",
"925c3cbd0a0bc5f56d8a8186b95323b2801036ce64d95db1c9c1ef63735d760c",
"5ef75137fa784d916c1731eb5c3700fdadaf7babc8c55a933cb52910249ce576",
"30299b6ef1aff24831fb728ee4edaf4fc02c8c7dd0806bfa90f3e3ea7fe2bb80"
] |
| Globals | [
"t_fallback__init",
"t_fallback__initTags",
"t_fallback__reloadSRC",
"t_fallback__handleTimeout",
"t_fallback__loadAdvancedJS",
"t_onReady",
"t_onFuncLoad",
"dataLayer",
"fbq",
"_fbq",
"mainTracker",
"tildastatcookie",
"t_videoPlayer__init",
"t_video__doRutubeCommand",
"t_video__doVimeoCommand",
"t_video__doBoomstreamCommand",
"t_video__getPlayer",
"t_video__initPlayer__youtube",
"t_video__initPlayer__vimeo",
"t_video__initPlayer__kinescope",
"t_video__initPlayer__vkvideo",
"t_video__initPlayer__rutube",
"t_video__initPlayer__htmlVideo",
"t_video__initPlayer__boomstream",
"t_video_lazyload_init",
"t_video_lazyload__addVideoWithCheckViewport",
"t_video_lazyload__addVideo",
"t_video_lazyload__removeVideo",
"t_video_lazyload__setHeight",
"t_video_lazyload__setMobileHeight",
"t_video__createPlayer",
"t_video_lazyload__overwriteParams",
"t670_init",
"t670_addImageEvents",
"t670_handleRutube",
"t670_show",
"t670_pauseVideo",
"t670_hide",
"t670_addArrowHandlers",
"t670_pauseAllVideos"
] |
| Cookies | [
"_fbp"
] |
| Storage keys | [
"lastExternalReferrer",
"lastExternalReferrerTime"
] |
| Tls | {
"san": [
"germanstakeearn.digital",
"*.germanstakeearn.digital"
],
"cipher": "AES_128_GCM",
"issuer": "WE1",
"subject": "germanstakeearn.digital",
"protocol": "TLS 1.3",
"valid_to": "2026-10-31T16:11:28Z",
"valid_from": "2026-08-02T15:15:08Z"
} |
| Domain age days | 33 |
| Apex age days | 33 |
| Tls age days | 33 |
| Tls valid days | 90 |
| Requests | 36 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 93,
"malicious": true
},
"overall": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"stake"
],
"malicious": true,
"categories": [
"phishing"
]
},
"urlscan": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"Stake"
],
"malicious": true,
"categories": [
"phishing"
]
}
} |
| HTTP headers | {
"server": "cloudflare",
"content-type": "text/html"
} |
Separate monitor record · 2026-09-05 05:08 UTC
Separate stored monitor snapshot; does not replace the primary report record or establish current availability.
- record_source
- domain_monitor.urlscan
- uuid
- 01a06f2f-b2ef-70ab-81d2-4df299b6bdbf
- score
- 100
- malicious
- true
- result_at
- 2026-09-05T05:08:25Z
- enriched_at
- 2026-09-05T08:12:28Z
- source_timestamps
- {"urlscan_result_at":"2026-09-05 07:08:25","urlscan_enriched_at":"2026-09-05 10:12:28"}
- timestamp_basis
- Europe/Berlin, as used by the existing report; source timestamps are retained verbatim




 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 Kaspersky
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT