Skip to security report
Domain security and threat intelligence
folksfinances.com favicon

folksfinances.com

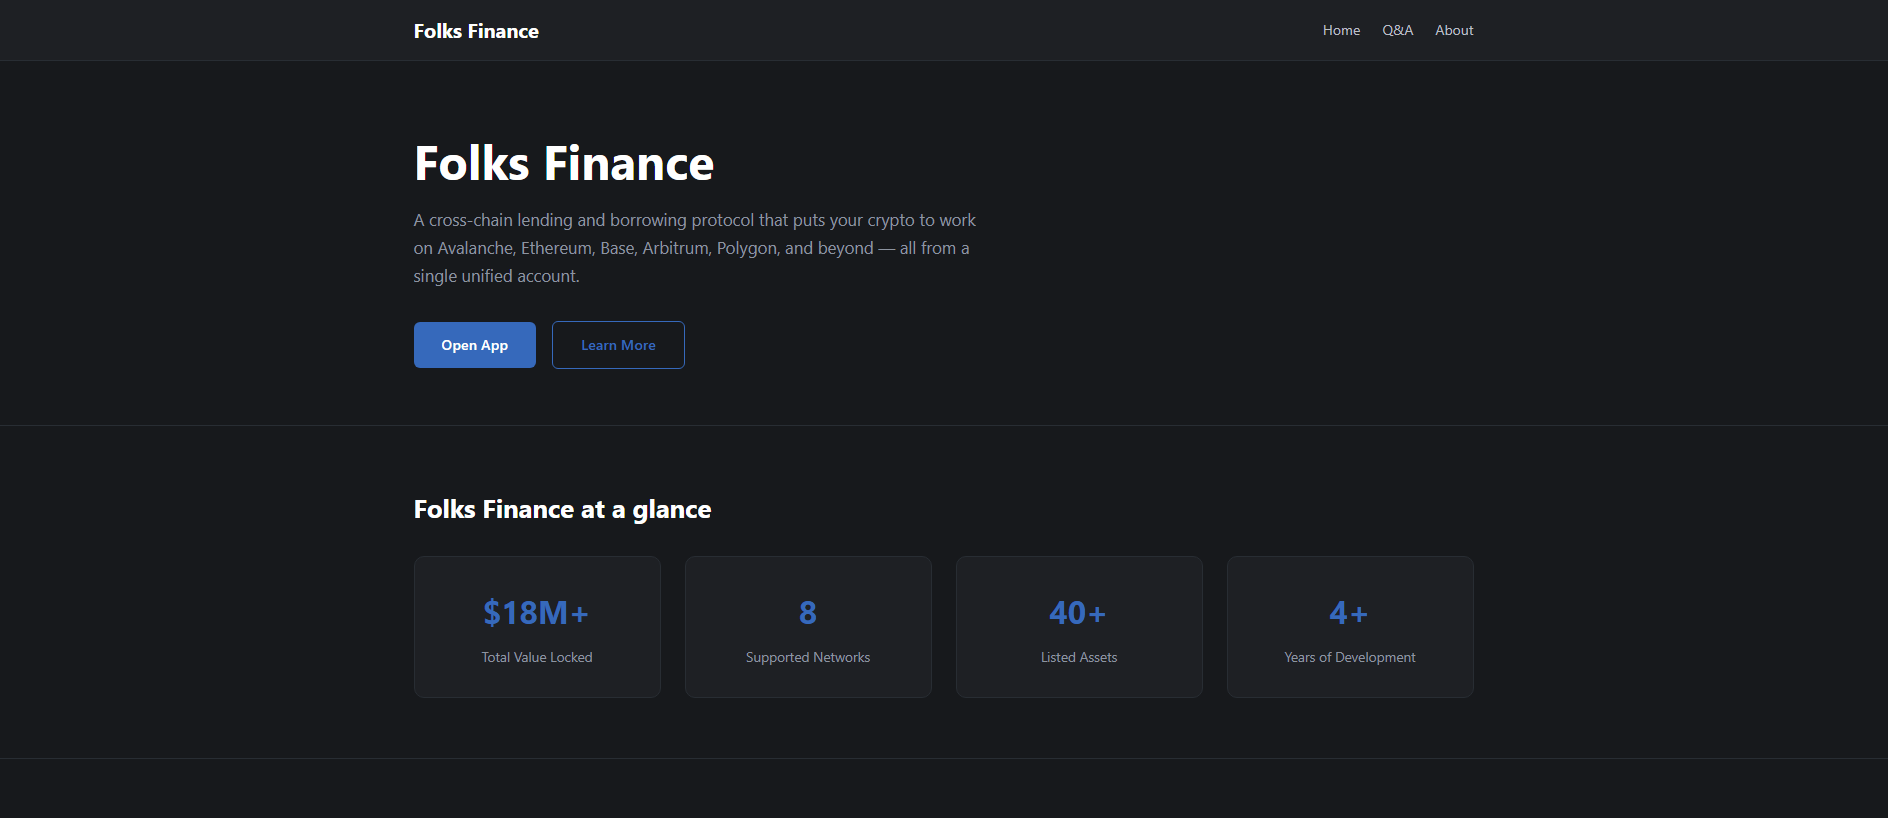
“Folks Finance — Supply, Borrow & Grow Across Chains”

Threat verdict Critical 100/100 evidence score
Availability Last known active Latest stored reachability observation
VirusTotal detections: 21/89 Spamhaus DBL: DBL_SPAM Stored blocklist matches: 2 URLQuery threat systems: 2 alerts Brand impersonation: Across Last known active
Jul 29, 2026 Across 1 Report Sent
Actions API
⚠️
This domain has been flagged as malicious
Security engines reporting a detection: 21. Public blocklists reporting a match: 2. Exercise extreme caution — do not enter credentials or personal information.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@intezio.net. The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
1 month
Reports sent
1
Latest case ID
PD-20260729-9C3F83
Current status
HTTP 200 at latest stored check

Evidence Summary

CRITICAL
Score
100/100

The domain folksfinances.com was registered on June 20, 2026 through Fewmoretaps OU d/b/a Trustname.com and is currently resolving to the IPv4 address 144.31.215.70. DNS resolution is handled by three dnspod.com nameservers (a.dnspod.com, b.dnspod.com, c.dnspod.com). The domain is actively listed on at least one security blocklist and has been blocked by the PhishDestroy service, indicating that it is recognized by upstream threat mitigation platforms.

VirusTotal analysis shows that five of ninety‑one scanned security vendors have flagged the domain, providing modest but notable detection evidence. No additional intelligence such as SSL certificate details, page title, or observed landing‑page content is available at this time, leaving the exact phishing payload and targeted brand unidentified. The infrastructure characteristics—recent registration, use of a popular DNS provider, and single‑host IP address—are consistent with a quickly deployed phishing campaign.

Defenders should add the domain to local block lists, monitor DNS queries for the associated IP address, and ensure that any email filtering rules that reference known phishing indicators are updated to include this domain. Continuous re‑evaluation is advised, as further analysis (e.g., page content inspection or additional VirusTotal scans) may reveal more specific threat actors or targeted brands.

VirusTotal
VirusTotal
21 det.
URLQuery
URLQuery
2 threat alerts
CF Radar
Malicious
URLScan
URLScan
ScamAdviser
Scamadviser
80/100Likely Safe
TLS Certificate
Let's Encrypt
Age
3 mo New
Observed status
Last known active 200
PhishDestroy
DestroyList
Listed
Reports Sent
1
Data coverage VirusTotal 21 / 89 URLQuery 2 threat-system alerts OTX no community references CF Radar provider verdict: malicious URLScan capture stored report URLScan verdict Analysis completed TLS valid certificate, 63d WHOIS 3 mo old Screenshot 4 captures · 3 sources Scamadviser 80/100
Network Security Intelligence Registrar context
Threat Detection Systems 2 alerts
Detection System Indicator Verdict Alert
DNS4EU folksfinances.com malicious Sinkholed
Cloudflare DNS folksfinances.com malicious Sinkholed
CF Cloudflare Radar Verdict Malicious
Malware Security threats Malware
Registrar context Trustname
Stored registration data identifies Trustname / Fewmoretaps OÜ (IANA 4318) as the registrar. PhishDestroy maintains a separate registrar investigation; that material is contextual and is not an independent detection for this domain.
Trustname Investigation

Forensic History & Detection Timeline

This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition Aug 5, 2026 · 00:14 UTC
    Domain state transitioned from dead to alive.
  2. Domain Status Transition Aug 4, 2026 · 12:18 UTC
    Domain state transitioned from alive to dead.
  3. Threat First Observed Jul 29, 2026 · 18:32 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 144.31.215.70.

Threat Response Pipeline

Discovery
Checks
Reports
Availability
17/18
Sent Report Recorded
Stored sent-report record for registrar Fewmoretaps OU d/b/a Trustname.com, hosting provider, 2 abuse contacts
abuse@intezio.netabuse@trustname.com
Jul 29, 2026

Public Blocklist Status

Stored Capture · 4 sources

Domain Intelligence

Domain
URLScan Verdict Analysis completed score 0 report ↗
Telegram IoCs 1 extracted https://t.me/FolksfinanceOfficial
Server / ASN Apache/2.4.58 (Ubuntu) · AS198550 NODE HOST LIMITED
IP Reputation abuse score 0/100 0 reports checked Aug 28, 2026
IP Address 144.31.215.70 DE
GeoDE Frankfurt am Main, DE
NetworkAS198550 · Intezio Worldwide Limited
RegistrationCreated Jun 20, 2026 (88d · New) Expires Jun 20, 2027
Elapsed Since First Report 6 days
What we count Raw elapsed time since the first stored abuse report. It is not a registrar response-time measurement. Latest observed status: Last known active.
What each report contains Stored outgoing-report records may reference evidence available at the time, such as vendor verdicts, registration data, hosting details, classifications, or screenshots. This page does not infer the exact payload delivered, receipt, acknowledgement, or action by a recipient.
HTTP Status200
Technical detailsDNS, SSL SANs, timestamps
First DetectedJul 29, 2026
DOM Analysisanalyzed Jul 29, 2026score 95/10014 brand signals
IoC Extractionscanned Aug 1, 20260 wallet · 1 Telegram IoC
Submitted URLhttp://folksfinances.com/
Nameserversa.dnspod.comb.dnspod.comc.dnspod.com
TLS Fingerprint
TLS Observationvalid from Jul 3, 2026scanned Jul 30, 2026
TLS SAN Domainswww.folksfinances.com
Favicon Hash
Case ID
Page Title
Folks Finance — Supply, Borrow & Grow Across Chains
Impersonates
Across Arbitrum Avalanche Base Chainlink Coinbase Coinbase Wallet Ethereum +6
TLS Certificate
Valid transport encryption · Issued by Let's Encrypt · valid for 63 days
Technologies · 2 identified
Detected via Cloudflare Radar · Wappalyzer engine
Report This Domain Submit evidence & help protect others

VirusTotal Analysis

21 / 89 security vendors flagged this domain
View on VT
Last analyzed Previous stored snapshot: 16 detections
ChainPatrol
alphaMountain.ai
BitDefender
Chong Lua Dao
CRDF
CyRadar
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
LevelBlue
Lionic
Netcraft
Seclookup
SOCRadar
Sophos
VIPRE
Webroot

Archived Evidence

Wayback Machine Snapshot
A historical snapshot is available for evidence review
View Archive
Site Performance Analysis

Google PageSpeed Insights — mobile performance audit of folksfinances.com · checked Jul 29, 2026

100
Good
Performance
FCP
0.76s
First Contentful Paint
LCP
0.76s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
1.79s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://folksfinances.com/
Final URL: https://folksfinances.com/
Response
HTTP 200
HTML body
2.0 KB
Compressed
1.0 KB
Links
0 internal · 0 external
Detected technologies
apache
Selected response headers
Server: Apache/2.4.58 (Ubuntu)
Cache-Control: no-store
Content-Encoding: gzip
Content-Type: text/html; charset=UTF-8
HSTS: not observed DNSSEC: not observed WAF / firewall: not observed Cloaking flag: not observed
All stored response-header names (9)
DateServerCache-ControlVaryContent-EncodingContent-LengthKeep-AliveConnectionContent-Type

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-20260729-9C3F83 Recipient: abuse@intezio.net
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 38.3 KB

Were You Affected by This Site?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

If credentials, payment data, or files were exposed, report the incident immediately. Change affected passwords, revoke active sessions, and scan the device.

Europol
Find the official reporting channel for your EU country
National police directory
Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

97-country directory
Template-based draft • optional AI wording assistance requires separate consent Review and submit it yourself

Check Any Domain

Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence

Scan Now

Report Phishing

Submit suspicious domains to our threat database — protect the community

Report

Live Threat Feed

Recent phishing reports and observed availability changes

Monitor

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Live Threat Feed Appeal This Listing
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/folksfinances.com"
  title="PhishDestroy threat report for folksfinances.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>