Spamhaus DBL
phishing domain
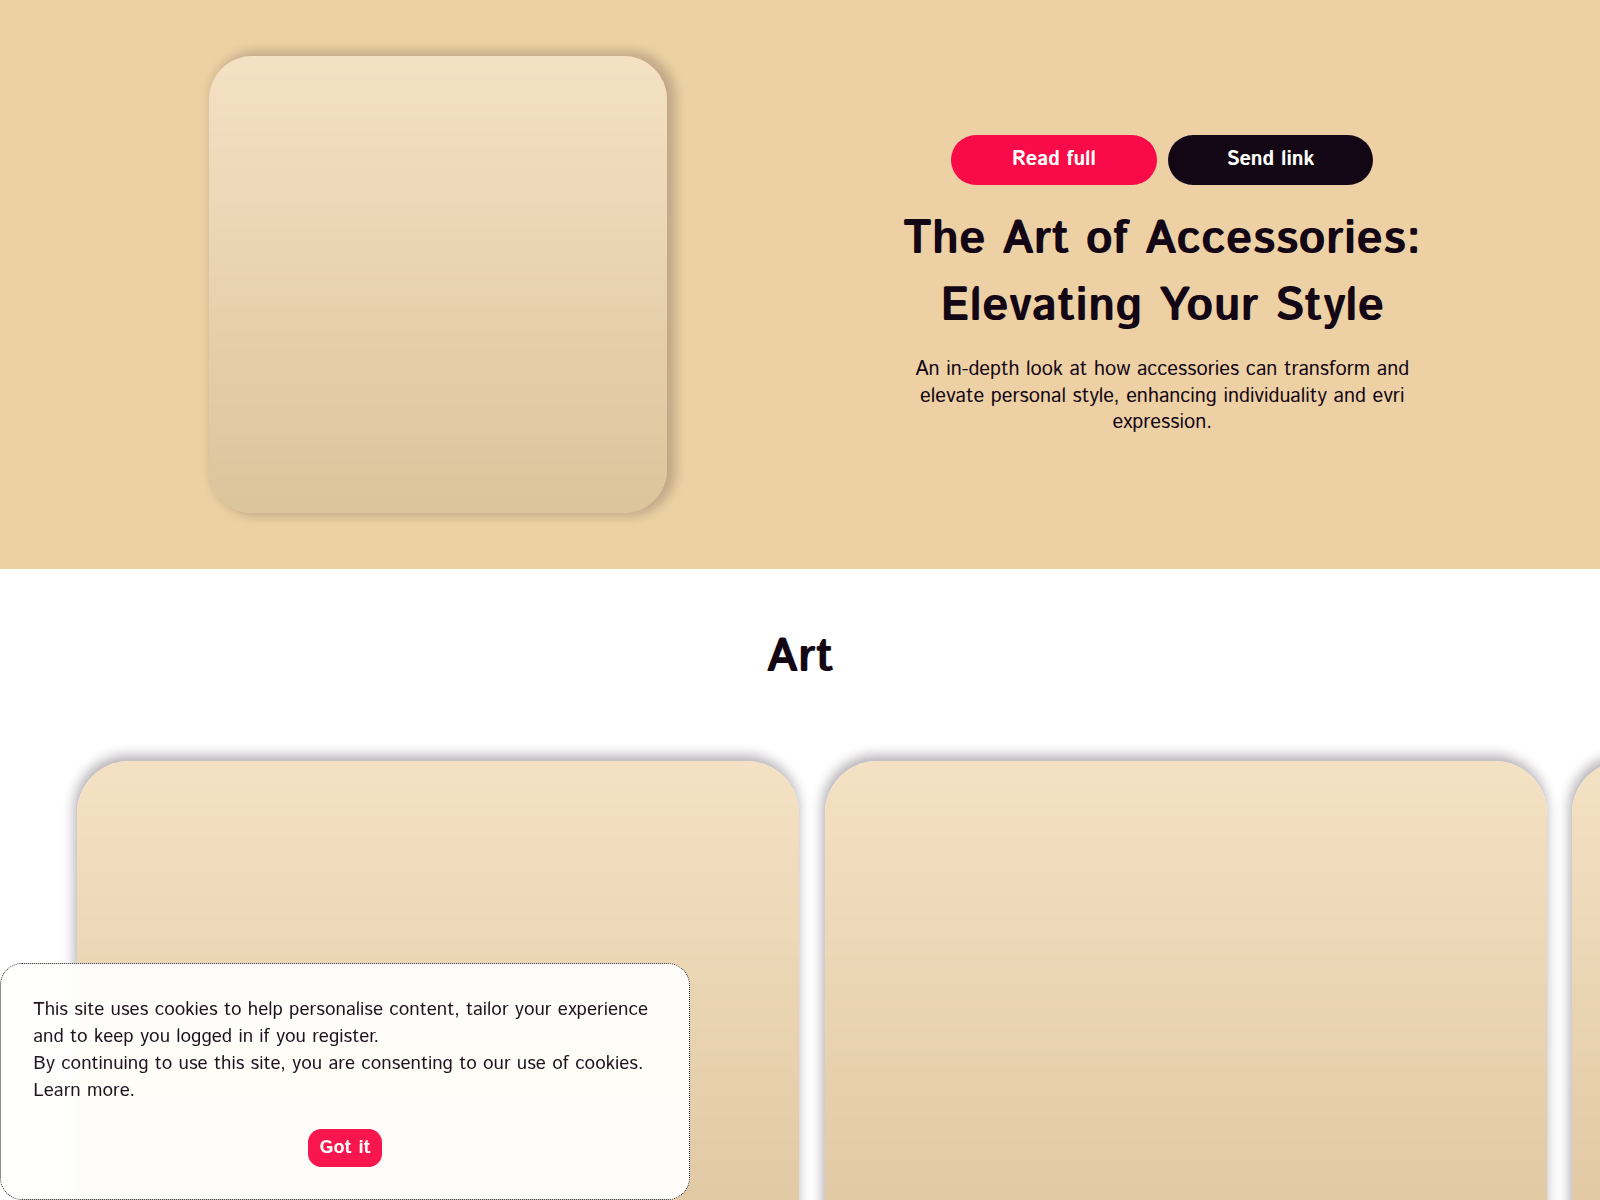
On 2026-11-09, barclaysiportalpayments.com displayed a page focused on fashion accessories rather than banking or payments. The visible content features a prominent article titled "The Art of Accessories: Elevating Your Style," described as an in-depth look at how accessories can transform and elevate personal style, alongside a section heading labeled "Art" with content cards below.
 Dominet (HK)
 179.43.140.168Private Layer INC
PhishDestroy first recorded barclaysiportalpayments.com on 2026-11-09. Stored VirusTotal result: 0/92 engines flagged. Analysis time (as stored): 2026-11-09 09:47 UTC. Retrieved (as stored): 2026-11-09 19:05 UTC. Risk: medium (25/100). Registrar: Dominet (HK). Status: Last known active. Hosting: Private Layer INC. Do not enter credentials or connect a wallet.
179.43.140.168Private Layer INCDominet (HK) Capture recorded with this analysis · URLScan · 2026-11-09T13:45:29Z
SHA-256: 9611c5c9d85238295723bb77aae2a07a82379e8ab951bd1efe930650dcbc8d0e
PhishDestroy analysis, reviewed version
On 2026-11-09, barclaysiportalpayments.com displayed a page focused on fashion accessories rather than banking or payments. The visible content features a prominent article titled "The Art of Accessories: Elevating Your Style," described as an in-depth look at how accessories can transform and elevate personal style, alongside a section heading labeled "Art" with content cards below.
The page offers two visible actions: a "Read full" button to open the complete article and a "Send link" button to share it. A cookie notice at the bottom left states that the site uses cookies to personalise content and keep users logged in, with a "Got it" button to acknowledge it. The layout uses a warm beige and white color scheme with rounded content cards.
phishing domain
Malicious · engine verdict · score 98
SHA-256 bba680d7637168bcc687b64f6840a6c2110144f730a168164d7f6cd601d2dde4
Observed: · Retrieved:
| Uuid | 01a1c08e-6ec5-7000-aa2e-6f6d0e846a53 |
|---|---|
| Final url | https://barclaysiportalpayments.com/ |
| Status | 200 |
| Redirected | https-only |
| Redirects | [
{
"to": "https://barclaysiportalpayments.com/",
"from": "http://barclaysiportalpayments.com/",
"status": 307
}
] |
| Ip | 179.43.140.188 |
| Ptr | hostedby.privatelayer.com |
| Contacted domains | [
"fonts.gstatic.com",
"fonts.googleapis.com"
] |
| Contacted IP addresses | [
"142.251.211.67",
"142.251.179.95",
"179.43.140.188"
] |
| Asns | [
"15169",
"51852"
] |
| Countries | [
"US",
"CH"
] |
| Document hash | 9133c2a6293122ee46b749147da853c831ae77d6071d6341cb12cb5c02310893 |
| Script hashes | [
"5ac297ed85ea3322fb4dd77abb9cd59b1ab4ed3d66a4ace6f251b620487b9649"
] |
| Tls | {
"san": [
"barclaysiportalpayments.com"
],
"cipher": "AES_128_GCM",
"issuer": "YE1",
"subject": "barclaysiportalpayments.com",
"protocol": "TLS 1.3",
"valid_to": "2027-02-07T09:11:11Z",
"valid_from": "2026-11-09T09:11:12Z"
} |
| Domain age days | 0 |
| Apex age days | 0 |
| Tls age days | 0 |
| Tls valid days | 89 |
| Requests | 27 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-2aab354"
],
"score": 98,
"malicious": true
},
"overall": {
"score": 0,
"malicious": false
}
} |
| HTTP headers | {
"server": "Apache/2.4.52 (Ubuntu)",
"content-type": "text/html; charset=utf-8",
"via": "1.1 Caddy\n1.1 Caddy"
} |
Separate stored monitor snapshot; does not replace the primary report record or establish current availability.
0 / 92 engine detections
Observed: · Retrieved:
| Vendor result counts | {
"timeout": 0,
"harmless": 0,
"malicious": 0,
"suspicious": 0,
"undetected": 92
} |
|---|---|
| Reputation | 0 |
| Registrar | Dominet (HK) Limited |
| Created | 2026-11-08T21:17:40Z |
| Expires | 2027-11-08T21:17:40Z |
| Updated | 2026-11-08T21:17:41Z |
| First seen | 2026-11-09T09:47:36Z |
| DNS records | [
{
"ttl": 60,
"type": "A",
"value": "179.43.140.178"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.170"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.171"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.174"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.184"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.180"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.172"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.162"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.186"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.164"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.177"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.189"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.175"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.166"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.185"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.173"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.182"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.168"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.188"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.165"
},
{
"ttl": 2410,
"type": "NS",
"value": "ns2.nsgriddns.com"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.179"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.183"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.181"
},
{
"ttl": 2410,
"type": "NS",
"value": "ns1.nsgriddns.com"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.187"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.176"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.167"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.163"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.190"
}
] |
| Dns at | 2026-11-09T09:47:36Z |
| Registration record | {
"registrar": "Dominet (HK) Limited",
"registrar_iana_id": "3775",
"registrar_url": "http://www.alibabacloud.com",
"created": "2026-11-08T21:17:40Z",
"updated": "2026-11-08T21:17:41Z",
"expires": "2027-11-08T21:17:40Z",
"status": [
"clientTransferProhibited"
],
"nameservers": [
"ns1.nsgriddns.com",
"ns2.nsgriddns.com"
],
"dnssec": "unsigned"
} |
| Registry data | {
"status": [
"client transfer prohibited"
],
"events": {
"expiration": "2027-11-08T21:17:40Z",
"registration": "2026-11-08T21:17:40Z",
"registrar expiration": "2027-11-08T21:17:40Z",
"last update of RDAP database": "2026-11-08T21:17:41Z"
}
} |
This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.
2 community references
Open reportScan report
Open reportNo threat flag
Open report0 / 100 · heuristic score · 0 brand references · 0 classifications
Open reportThis dated monitor analysis is separate from the primary PhishDestroy analysis above. A heuristic score is not a measured probability.
Narrative generation metadata
Open reportThe narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.
Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
Stored page, network and scanner observations, grouped by source and observation time.
| Mail configuration | {
"spf_lookups": 0
} |
|---|---|
| Protective DNS results | {
"resolvers": 12,
"blocked_by": [
"CloudFlare Family"
],
"blocked_count": 1
} |
| Web archive observations | {
"last": "2026-11-09T19:02:27Z",
"first": "2026-11-09T19:02:27Z",
"changes": 0,
"days_archived": 1,
"avg_page_bytes": 6658
} |
| Trackers | {
"requests": 24,
"trackers": [
{
"name": "Google Fonts",
"company": "Google",
"country": "US",
"category": "Hosting",
"requests": 1
}
]
} |
| Forms and mixed content | {
"third_party_scripts": 0
} |
| Status | {
"up": true,
"code": 200,
"timings": {
"dns": 117,
"tls": 42,
"wait": 94,
"connect": 37,
"download": 1
},
"response_ms": 291
} |
| TLS connection | {
"alpn": "h2",
"cipher": "TLS_AES_128_GCM_SHA256",
"protocol": "TLSv1.3",
"versions": [
"TLSv1.2",
"TLSv1.3"
],
"authorized": true,
"forward_secrecy": true
} |
| Ports | {
"open": [
22,
53,
80,
443
]
} |
| Carbon | {
"bytes": 13545,
"co2_grams": 0.0005,
"cleaner_than": 65
} |
| Dns server | {
"ns": [
{
"ip": "179.43.140.162",
"host": "ns1.nsgriddns.com"
},
{
"ip": "179.43.140.163",
"host": "ns2.nsgriddns.com"
}
],
"zone": "barclaysiportalpayments.com"
} |
| Location | {
"ip": "179.43.140.165",
"asn": "51852",
"org": "Private Layer INC",
"city": "Rümlang",
"country": "CH"
} |
| Ssl | {
"issuer": "Let's Encrypt / YE1",
"subject": "barclaysiportalpayments.com"
} |
| DNS records | {
"A": [
"179.43.140.179",
"179.43.140.176",
"179.43.140.165",
"179.43.140.181",
"179.43.140.182",
"179.43.140.190",
"179.43.140.167",
"179.43.140.188"
],
"NS": [
"ns2.nsgriddns.com",
"ns1.nsgriddns.com"
],
"SOA": "{\"nsname\": \"ns1.nsgriddns.com\", \"hostmaster\": \"hostmaster.nsgriddns.com\", \"serial\": 2026110902, \"refresh\": 10800, \"retry\": 3600, \"expire\": 604800, \"minttl\": 60}"
} |
| Dnssec | {
"ds": false,
"rrsig": false,
"dnskey": false
} |
| Hsts | {
"message": "Site does not serve any HSTS headers."
} |
| HTTP security policies | {
"xFrameOptions": false,
"referrerPolicy": false,
"xXSSProtection": false,
"permissionsPolicy": false,
"xContentTypeOptions": false,
"contentSecurityPolicy": false,
"strictTransportPolicy": false,
"crossOriginOpenerPolicy": false,
"crossOriginEmbedderPolicy": false,
"crossOriginResourcePolicy": false
} |
| Get ip | {
"ip": "179.43.140.190",
"family": 4
} |
| Redirects | {
"chain": [
"https://barclaysiportalpayments.com"
]
} |
| Tech stack | {
"technologies": [
"Ubuntu",
"Apache HTTP Server",
"HTTP/3"
]
} |
| Page links | {
"internal_count": 14
} |
| Registration record | {
"registrar": "Dominet (HK) Limited",
"created": "2026-11-08T21:17:40Z",
"updated": "2026-11-08T21:17:41Z",
"expires": "2027-11-08T21:17:40Z",
"status": [
"clientTransferProhibited https://icann.org/epp"
],
"nameservers": [
"ns1.nsgriddns.com",
"ns2.nsgriddns.com"
]
} |
| HTTP headers | {
"headers": {
"server": "Apache/2.4.52 (Ubuntu)",
"content-type": "text/html; charset=utf-8",
"via": "1.1 Caddy, 1.1 Caddy"
}
} |
PhishDestroy rates barclaysiportalpayments.com as medium risk (25/100) from the recorded evidence; it was first recorded on 2026-11-09. Stored VirusTotal result: 0/92 engines flagged. Analysis time (as stored): 2026-11-09 09:47 UTC. Retrieved (as stored): 2026-11-09 19:05 UTC. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.
This report does not record which wallet requests barclaysiportalpayments.com makes. Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions there. A confirmed blockchain transaction cannot be reversed.
It depends on what you did. If you entered a password, change it, and also on every other site where you used the same password; turn on two-factor authentication where it is offered. If you paid or gave card or bank details, contact your bank or payment service through the contacts on your card or its official website. If you only connected a wallet, disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds. If you signed a token approval or permit, revoke it with a token-approval checker. If you shared a seed phrase or private key, treat the wallet as compromised and move the remaining funds to a new wallet with a new seed phrase. If you downloaded a file, do not open it and scan the device with security software. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority; a report does not guarantee that money is returned. Step-by-step help: emergency guide.
Checked, no match
Last checked
9611c5c9d85238295723bb77aae2a07a82379e8ab951bd1efe930650dcbc8d0e SHA-256 of the prepared copy given to the model: 953fc17d0499f3803476a6744713d8ccf732637005959b63fb52af7ea52a58d6 9611c5c9d85238295723bb77aae2a07a82379e8ab951bd1efe930650dcbc8d0e · 34260 bytes 9611c5c9d85238295723bb77aae2a07a82379e8ab951bd1efe930650dcbc8d0e · 34260 bytes d9572dba08d5f12347e28ff026be3c36e63aa45219f655c3f3088f6212e6b171 · 34196 bytes 179.43.140.168 abuse score 0/100 0 reports checked Nov 9, 2026 last reported (HK) 179.43.140.168Rümlang, CHns2.nsgriddns.comns1.nsgriddns.comnsname: ns1.nsgriddns.comhostmaster: hostmaster.nsgriddns.comserial: 2026110902refresh: 10800retry: 3600expire: 604800minttl: 60Location describes the IP network.
barclaysiportalpayments.comSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
{
    "v": 1,
    "ip": "179.43.140.188",
    "asn": "AS51852",
    "ips": [
        "142.251.211.67",
        "142.251.179.95",
        "179.43.140.188"
    ],
    "ptr": "hostedby.privatelayer.com",
    "tls": {
        "san": [
            "barclaysiportalpayments.com"
        ],
        "cipher": "AES_128_GCM",
        "issuer": "YE1",
        "subject": "barclaysiportalpayments.com",
        "protocol": "TLS 1.3",
        "valid_to": "2027-02-07T09:11:11Z",
        "valid_from": "2026-11-09T09:11:12Z"
    },
    "asns": [
        "15169",
        "51852"
    ],
    "city": "Rümlang",
    "uuid": "01a1c08e-6ec5-7000-aa2e-6f6d0e846a53",
    "score": 0,
    "server": "Apache/2.4.52 (Ubuntu)",
    "status": 200,
    "country": "CH",
    "domains": [
        "fonts.gstatic.com",
        "fonts.googleapis.com"
    ],
    "headers": {
        "via": "1.1 Caddy\n1.1 Caddy",
        "server": "Apache/2.4.52 (Ubuntu)",
        "content-type": "text/html; charset=utf-8"
    },
    "asn_name": "PLI-AS Private Layer INC, PA",
    "doc_hash": "9133c2a6293122ee46b749147da853c831ae77d6071d6341cb12cb5c02310893",
    "requests": 27,
    "task_url": "http://barclaysiportalpayments.com/",
    "verdicts": {
        "engines": {
            "tags": [
                "urlscan-ml",
                "urlscan-ml-2aab354"
            ],
            "score": 98,
            "malicious": true
        },
        "overall": {
            "score": 0,
            "malicious": false
        }
    },
    "countries": [
        "US",
        "CH"
    ],
    "final_url": "https://barclaysiportalpayments.com/",
    "malicious": false,
    "redirects": [
        {
            "to": "https://barclaysiportalpayments.com/",
            "from": "http://barclaysiportalpayments.com/",
            "status": 307
        }
    ],
    "fetched_at": "2026-11-09T19:03:33Z",
    "redirected": "https-only",
    "scanned_at": "2026-11-09T13:45:29Z",
    "tls_issuer": "YE1",
    "captured_at": "2026-11-09 13:45:29.971000",
    "task_domain": "barclaysiportalpayments.com",
    "payload_hash": "bba680d7637168bcc687b64f6840a6c2110144f730a168164d7f6cd601d2dde4",
    "tls_age_days": 0,
    "apex_age_days": 0,
    "script_hashes": [
        "5ac297ed85ea3322fb4dd77abb9cd59b1ab4ed3d66a4ace6f251b620487b9649"
    ],
    "tls_valid_days": 89,
    "domain_age_days": 0
}{
"observed_at": null,
"dns_evidence_stale": true,
"http_evidence_stale": true
}{
"vt": {
"v": 1,
"dns": [
{
"ttl": 60,
"type": "A",
"value": "179.43.140.178"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.170"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.171"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.174"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.184"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.180"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.172"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.162"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.186"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.164"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.177"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.189"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.175"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.166"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.185"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.173"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.182"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.168"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.188"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.165"
},
{
"ttl": 2410,
"type": "NS",
"value": "ns2.nsgriddns.com"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.179"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.183"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.181"
},
{
"ttl": 2410,
"type": "NS",
"value": "ns1.nsgriddns.com"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.187"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.176"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.167"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.163"
},
{
"ttl": 60,
"type": "A",
"value": "179.43.140.190"
}
],
"rdap": {
"events": {
"expiration": "2027-11-08T21:17:40Z",
"registration": "2026-11-08T21:17:40Z",
"registrar expiration": "2027-11-08T21:17:40Z",
"last update of RDAP database": "2026-11-08T21:17:41Z"
},
"status": [
"client transfer prohibited"
]
},
"stats": {
"timeout": 0,
"harmless": 0,
"malicious": 0,
"suspicious": 0,
"undetected": 92
},
"whois": {
"dnssec": "unsigned",
"status": [
"clientTransferProhibited"
],
"created": "2026-11-08T21:17:40Z",
"expires": "2027-11-08T21:17:40Z",
"updated": "2026-11-08T21:17:41Z",
"registrar": "Dominet (HK) Limited",
"abuse_email": "domainabuse@service.aliyun.com",
"abuse_phone": "+86.95187",
"nameservers": [
"ns1.nsgriddns.com",
"ns2.nsgriddns.com"
],
"registrar_url": "http://www.alibabacloud.com",
"registrant_email": "6aacf85c31f44448s@",
"registrant_state": "facd29379a9a2b83",
"registrar_iana_id": "3775",
"registrant_country": "US"
},
"dns_at": "2026-11-09T09:47:36Z",
"created": "2026-11-08T21:17:40Z",
"expires": "2027-11-08T21:17:40Z",
"updated": "2026-11-08T21:17:41Z",
"registrar": "Dominet (HK) Limited",
"fetched_at": "2026-11-09T19:05:03Z",
"first_seen": "2026-11-09T09:47:36Z",
"reputation": 0,
"analysis_at": "2026-11-09T09:47:06Z"
},
"shots": {
"v": 1,
"urlscan": {
"url": "https://screenshots.phishdestroy.io/us/01a1c08e-6ec5-7000-aa2e-6f6d0e846a53.png",
"uuid": "01a1c08e-6ec5-7000-aa2e-6f6d0e846a53",
"bytes": 34260,
"sha256": "9611c5c9d85238295723bb77aae2a07a82379e8ab951bd1efe930650dcbc8d0e"
},
"fetched_at": "2026-11-10T00:26:41Z",
"urlscan_history": {
"scans": [
{
"at": "2026-11-09T09:14:37Z",
"uuid": "01a1bf96-17cb-757a-854c-c56cd0c7d7de",
"missing": 404,
"page_url": "https://barclaysiportalpayments.com/",
"task_domain": "barclaysiportalpayments.com"
},
{
"at": "2026-11-09T10:10:14Z",
"uuid": "01a1bfc9-5795-70a6-9938-8a309719b23c",
"missing": 404,
"page_url": "http://barclaysiportalpayments.com/",
"task_domain": "barclaysiportalpayments.com"
},
{
"at": "2026-11-09T12:20:14Z",
"url": "https://screenshots.phishdestroy.io/us/01a1c040-67d6-7148-b355-022e68564e89.png",
"uuid": "01a1c040-67d6-7148-b355-022e68564e89",
"bytes": 34260,
"sha256": "9611c5c9d85238295723bb77aae2a07a82379e8ab951bd1efe930650dcbc8d0e",
"status": 200,
"country": "CH",
"page_url": "https://barclaysiportalpayments.com/",
"task_domain": "barclaysiportalpayments.com"
},
{
"at": "2026-11-09T12:20:39Z",
"uuid": "01a1c040-c41e-75df-8e68-9090b4c29c1a",
"status": 404,
"country": "CH",
"missing": 404,
"page_url": "https://barclaysiportalpayments.com/home/index.php",
"task_domain": "barclaysiportalpayments.com"
},
{
"at": "2026-11-09T13:00:51Z",
"uuid": "01a1c065-954c-76e6-8c5f-f8f1ee872cde",
"status": 404,
"country": "CH",
"missing": 404,
"page_url": "https://barclaysiportalpayments.com/home/index.php",
"task_domain": "barclaysiportalpayments.com"
},
{
"at": "2026-11-09T19:07:59Z",
"url": "https://screenshots.phishdestroy.io/us/01a1c1b5-b5c0-70c6-95a4-1b734bef87bb.png",
"uuid": "01a1c1b5-b5c0-70c6-95a4-1b734bef87bb",
"bytes": 34196,
"sha256": "d9572dba08d5f12347e28ff026be3c36e63aa45219f655c3f3088f6212e6b171",
"status": 200,
"country": "CH",
"page_url": "https://barclaysiportalpayments.com/",
"task_domain": "barclaysiportalpayments.com"
}
],
"total": 10
}
},
"urlscan": {
"v": 1,
"ip": "179.43.140.188",
"ips": [
"142.251.211.67",
"142.251.179.95",
"179.43.140.188"
],
"ptr": "hostedby.privatelayer.com",
"tls": {
"san": [
"barclaysiportalpayments.com"
],
"cipher": "AES_128_GCM",
"issuer": "YE1",
"subject": "barclaysiportalpayments.com",
"protocol": "TLS 1.3",
"valid_to": "2027-02-07T09:11:11Z",
"valid_from": "2026-11-09T09:11:12Z"
},
"asns": [
"15169",
"51852"
],
"uuid": "01a1c08e-6ec5-7000-aa2e-6f6d0e846a53",
"status": 200,
"domains": [
"fonts.gstatic.com",
"fonts.googleapis.com"
],
"headers": {
"via": "1.1 Caddy\n1.1 Caddy",
"server": "Apache/2.4.52 (Ubuntu)",
"content-type": "text/html; charset=utf-8"
},
"doc_hash": "9133c2a6293122ee46b749147da853c831ae77d6071d6341cb12cb5c02310893",
"requests": 27,
"task_url": "http://barclaysiportalpayments.com/",
"verdicts": {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-2aab354"
],
"score": 98,
"malicious": true
},
"overall": {
"score": 0,
"malicious": false
}
},
"countries": [
"US",
"CH"
],
"final_url": "https://barclaysiportalpayments.com/",
"redirects": [
{
"to": "https://barclaysiportalpayments.com/",
"from": "http://barclaysiportalpayments.com/",
"status": 307
}
],
"fetched_at": "2026-11-09T19:03:33Z",
"redirected": "https-only",
"scanned_at": "2026-11-09T13:45:29Z",
"task_domain": "barclaysiportalpayments.com",
"tls_age_days": 0,
"apex_age_days": 0,
"script_hashes": [
"5ac297ed85ea3322fb4dd77abb9cd59b1ab4ed3d66a4ace6f251b620487b9649"
],
"tls_valid_days": 89,
"domain_age_days": 0
},
"webcheck": {
"v": 1,
"dns": {
"A": [
"179.43.140.179",
"179.43.140.176",
"179.43.140.165",
"179.43.140.181",
"179.43.140.182",
"179.43.140.190",
"179.43.140.167",
"179.43.140.188"
],
"NS": [
"ns2.nsgriddns.com",
"ns1.nsgriddns.com"
],
"SOA": "{\"nsname\": \"ns1.nsgriddns.com\", \"hostmaster\": \"hostmaster.nsgriddns.com\", \"serial\": 2026110902, \"refresh\": 10800, \"retry\": 3600, \"expire\": 604800, \"minttl\": 60}"
},
"ssl": {
"issuer": "Let's Encrypt / YE1",
"subject": "barclaysiportalpayments.com"
},
"hsts": {
"message": "Site does not serve any HSTS headers."
},
"ports": {
"open": [
22,
53,
80,
443
]
},
"whois": {
"status": [
"clientTransferProhibited https://icann.org/epp#clientTransferProhibited"
],
"created": "2026-11-08T21:17:40Z",
"expires": "2027-11-08T21:17:40Z",
"updated": "2026-11-08T21:17:41Z",
"registrar": "Dominet (HK) Limited",
"nameservers": [
"ns1.nsgriddns.com",
"ns2.nsgriddns.com"
]
},
"carbon": {
"bytes": 13545,
"co2_grams": 0.0005,
"cleaner_than": 65
},
"dnssec": {
"ds": false,
"rrsig": false,
"dnskey": false
},
"get_ip": {
"ip": "179.43.140.190",
"family": 4
},
"status": {
"up": true,
"code": 200,
"timings": {
"dns": 117,
"tls": 42,
"wait": 94,
"connect": 37,
"download": 1
},
"response_ms": 291
},
"headers": {
"headers": {
"via": "1.1 Caddy, 1.1 Caddy",
"server": "Apache/2.4.52 (Ubuntu)",
"content-type": "text/html; charset=utf-8"
}
},
"archives": {
"last": "2026-11-09T19:02:27Z",
"first": "2026-11-09T19:02:27Z",
"changes": 0,
"days_archived": 1,
"avg_page_bytes": 6658
},
"location": {
"ip": "179.43.140.165",
"asn": "51852",
"org": "Private Layer INC",
"city": "Rümlang",
"country": "CH"
},
"trackers": {
"requests": 24,
"trackers": [
{
"name": "Google Fonts",
"company": "Google",
"country": "US",
"category": "Hosting",
"requests": 1
}
]
},
"redirects": {
"chain": [
"https://barclaysiportalpayments.com"
]
},
"dns_server": {
"ns": [
{
"ip": "179.43.140.162",
"host": "ns1.nsgriddns.com"
},
{
"ip": "179.43.140.163",
"host": "ns2.nsgriddns.com"
}
],
"zone": "barclaysiportalpayments.com"
},
"fetched_at": "2026-11-09T19:03:49Z",
"tech_stack": {
"technologies": [
"Ubuntu",
"Apache HTTP Server",
"HTTP/3"
]
},
"block_lists": {
"resolvers": 12,
"blocked_by": [
"CloudFlare Family"
],
"blocked_count": 1
},
"mail_config": {
"spf_lookups": 0
},
"linked_pages": {
"internal_count": 14
},
"http_security": {
"xFrameOptions": false,
"referrerPolicy": false,
"xXSSProtection": false,
"permissionsPolicy": false,
"xContentTypeOptions": false,
"contentSecurityPolicy": false,
"strictTransportPolicy": false,
"crossOriginOpenerPolicy": false,
"crossOriginEmbedderPolicy": false,
"crossOriginResourcePolicy": false
},
"mixed_content": {
"third_party_scripts": 0
},
"tls_connection": {
"alpn": "h2",
"cipher": "TLS_AES_128_GCM_SHA256",
"protocol": "TLSv1.3",
"versions": [
"TLSv1.2",
"TLSv1.3"
],
"authorized": true,
"forward_secrecy": true
}
}
}Network requests: 27 SHA-256 hashes: 27 URLScan scan:
Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-11-09 19:03 UTC.
Open this scan on URLScan 01a1c08e-6ec5-7000-aa2e-6f6d0e846a53 ↗
| # | Network request | HTTP method · status | Type | Uncompressed size | Response body SHA-256 |
|---|
Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.
Recorded events: 10. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
2 community references
View sourcePage archived
View sourcebarclaysiportalpayments.com
View sourceMalicious · engine verdict · score 98
View source0/92 engine detections
View sourceWe scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL analysis↗
 CloudflareRadar / abuse reporting↗
 YandexSafe Browsing↗
 URLScan.ioPublic scan↗
 ESETSample / URL submission↗
 BitdefenderURL submission↗
 NortonSafe Web↗
 SymantecSiteReview↗
 AviraURL reporting↗
 Avast / AVGURL reporting↗
 KasperskyOpenTIP↗
 Dr.WebOnline scanner↗
 NetcraftAbuse reporting↗
 PhishTankCommunity reporting↗
 APWG eCXPhishing intelligence↗
 PhishStatsPublic feed↗
 Phish.ReportHosting abuse↗
 SpamhausDomain reputation↗
 PolySwarmMulti-engine analysis↗
 CheckPhishURL scan↗
 QutteraMalware scan↗
 URLqueryBrowser analysis↗
 Criminal IPAsset intelligence↗
 CRDFThreat Center↗
 ScamadviserReputation check↗
 MyWOTCommunity reputation↗
Browse this domain’s complete history by source. The download includes every record of the selected source. Dates retain their original field labels.
Download all records as JSON| ID | Stored data |
|---|
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
barclaysiportalpayments.com Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.
IC3 does not accept attachments. Keep original evidence for investigators. IC3 guidance
Federal tips line1-800-CALL-FBI

Current service: Report Fraud. England, Wales and Northern Ireland. Scotland: 101.
Contact centre0300 123 2040


Report scams and fraud to the US Federal Trade Commission. Reports go into a database used by law enforcement.


Report cyber incidents and phishing to the US Cybersecurity and Infrastructure Security Agency.

Forward scam emails and text messages to the National Cyber Security Centre, which takes down the malicious sites it finds.
Emailreport@phishing.gov.uk Text messages7726
Directory of national incident response teams (CSIRTs) in the EU. Find the team for your country.

Forward phishing emails to the Anti-Phishing Working Group.
Emailreportphishing@apwg.org
National Cyber Crime Reporting Portal. For financial fraud, also call the 1930 helpline straight away.
Helpline1930


Select your country to get official cybercrime contacts, or create a complaint draft →.
If you made a payment, contact your bank or payment service through its official contacts as soon as possible. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned.
Scammers are criminals. Filing a report creates a legal record and helps protect others.
Template-based draft • optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
barclaysiportalpayments.com)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.