
Search tracked domains and review stored evidence, detections, and the latest observed availability.
219,828
Total Tracked
213,490
VT Detected
91,921
Last Seen Active
127,907
Unavailable at Last Check
576
VT Pending
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domains
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains

app-hyperliquidl.cam

appethos-invite.network

apptea-fi.com

aragon-vote.com

award-yieldusd.com

bob-sepolia-q8djryial-distributed-crafts.vercel.app
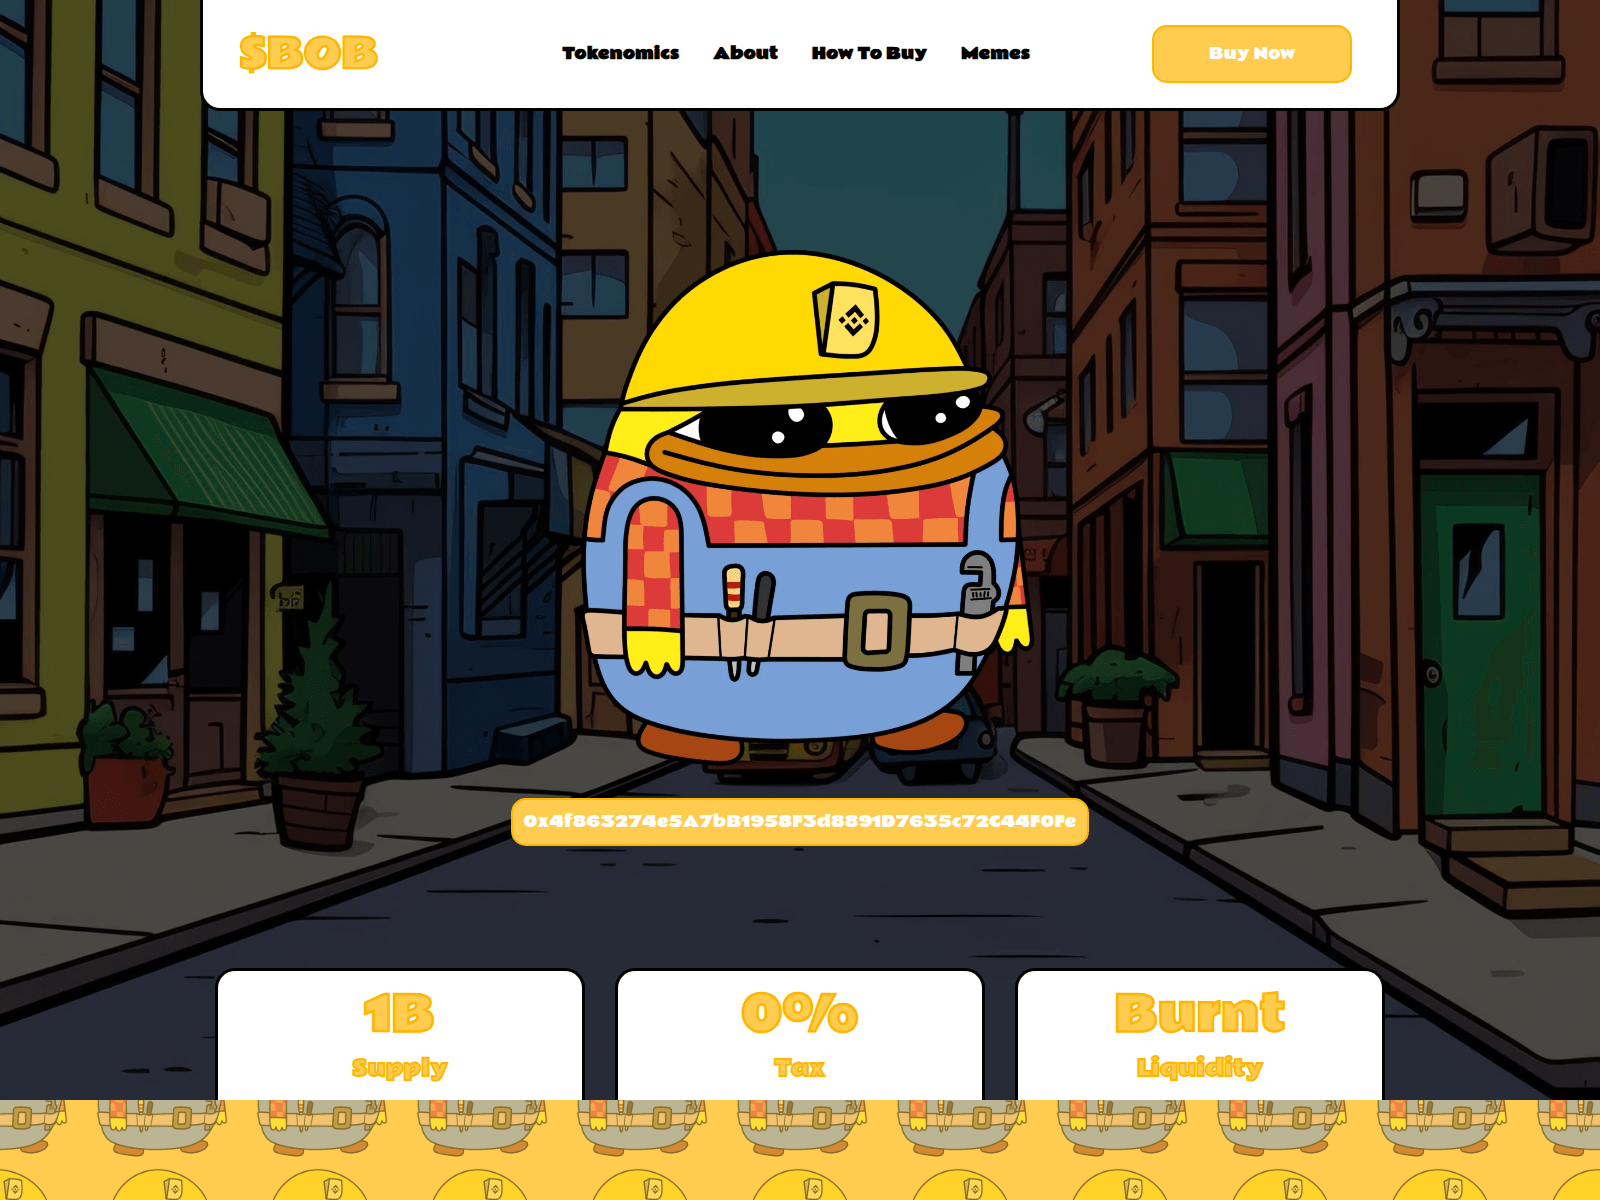
bobonbsc.com

boundless.eligibility.ink

brevis-tge.com

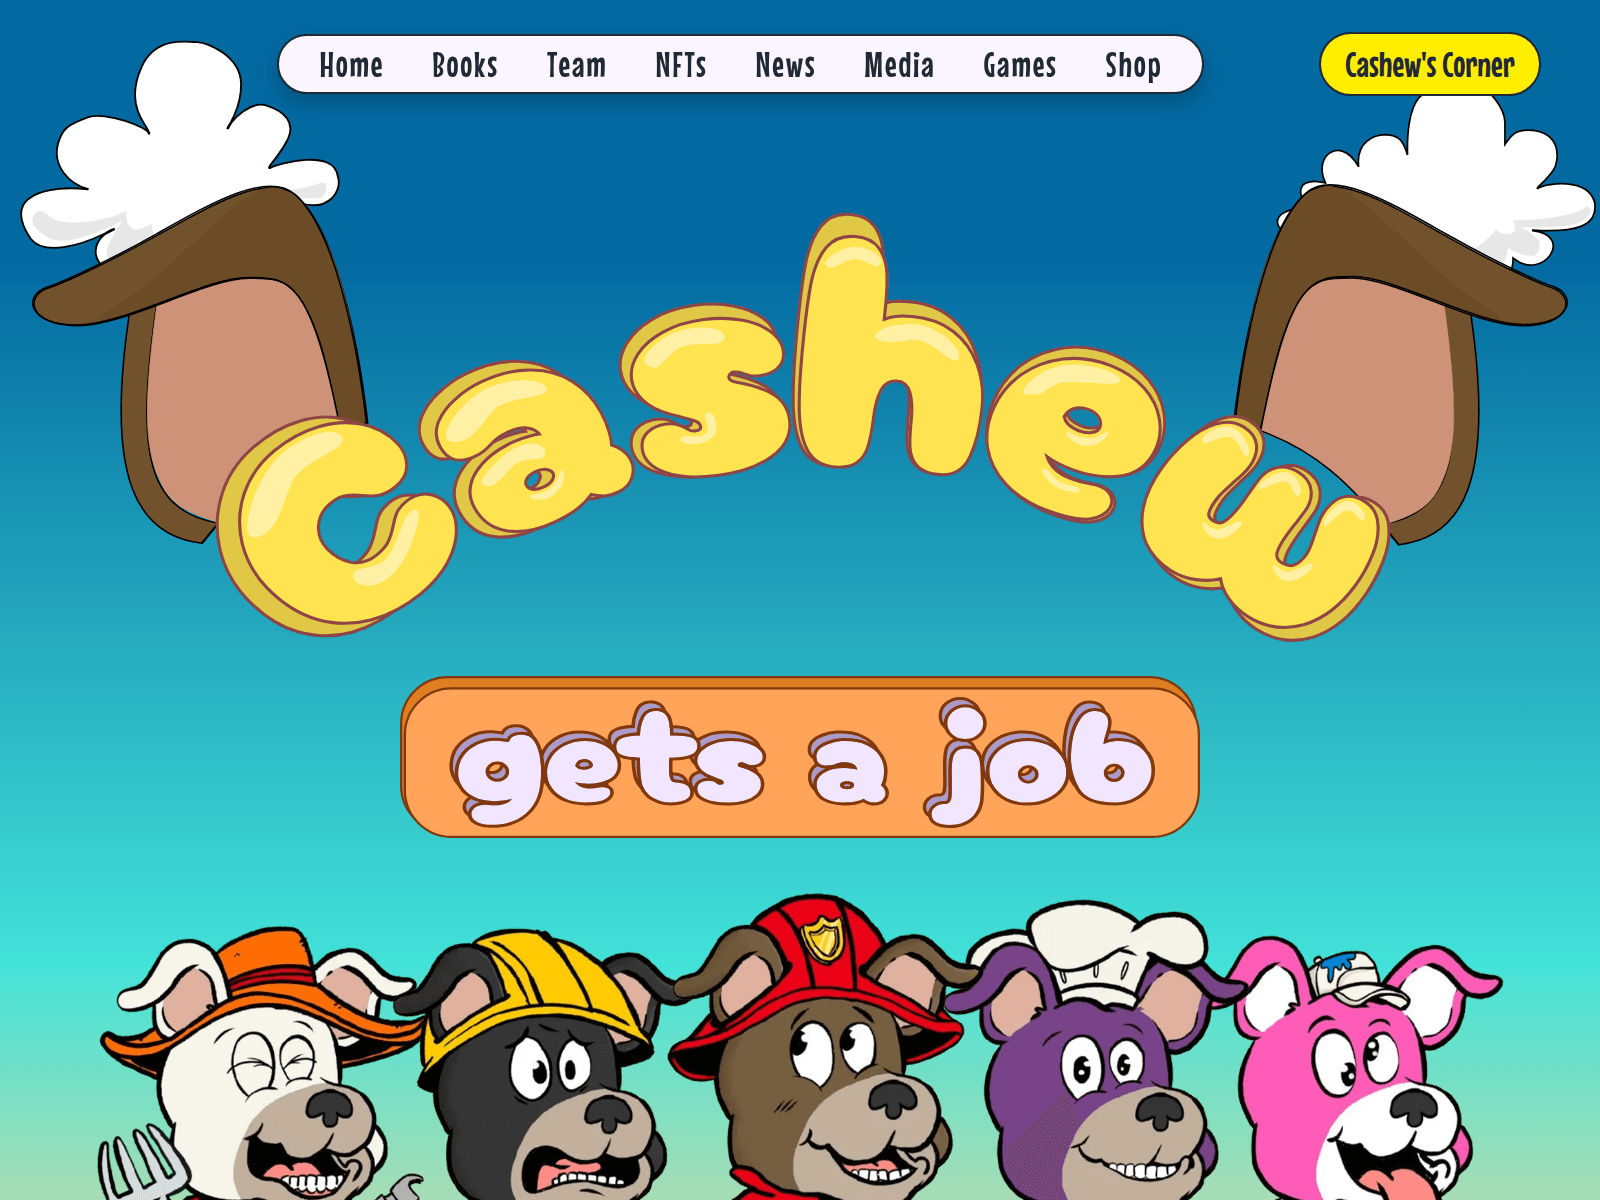
cashewgetsajob.com
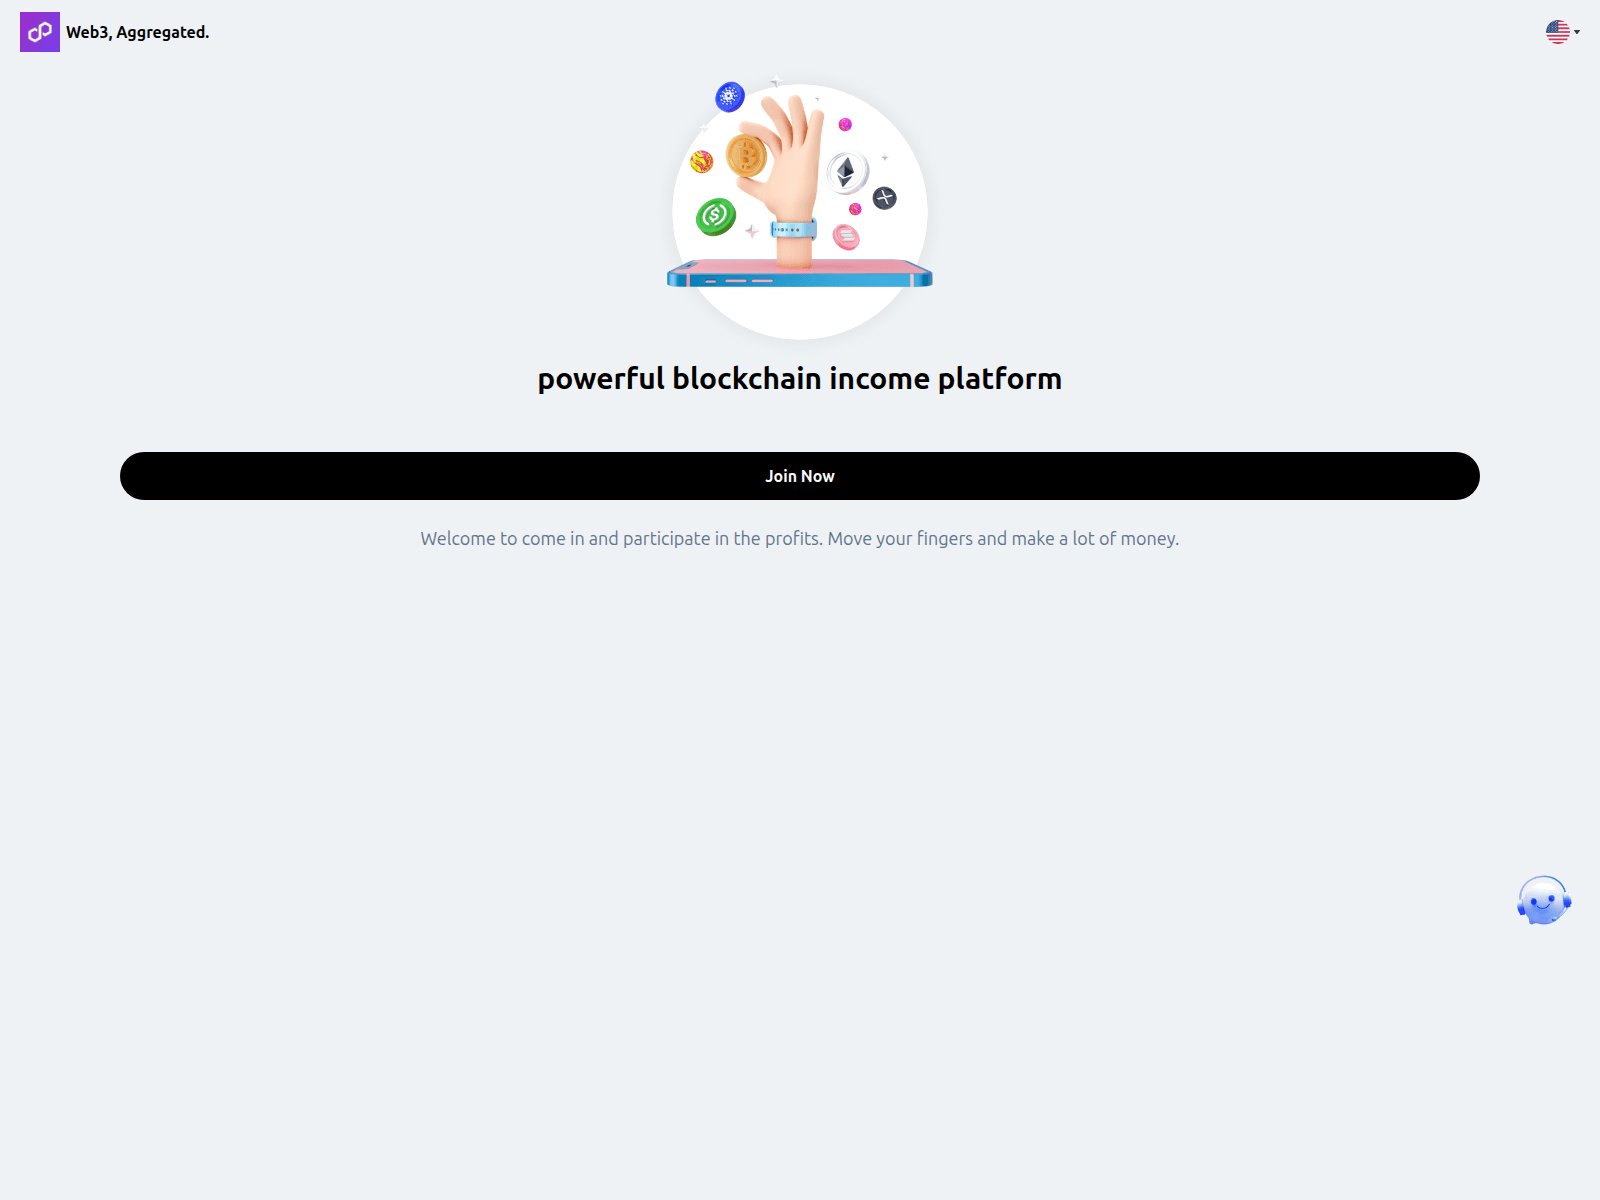
chain6.net
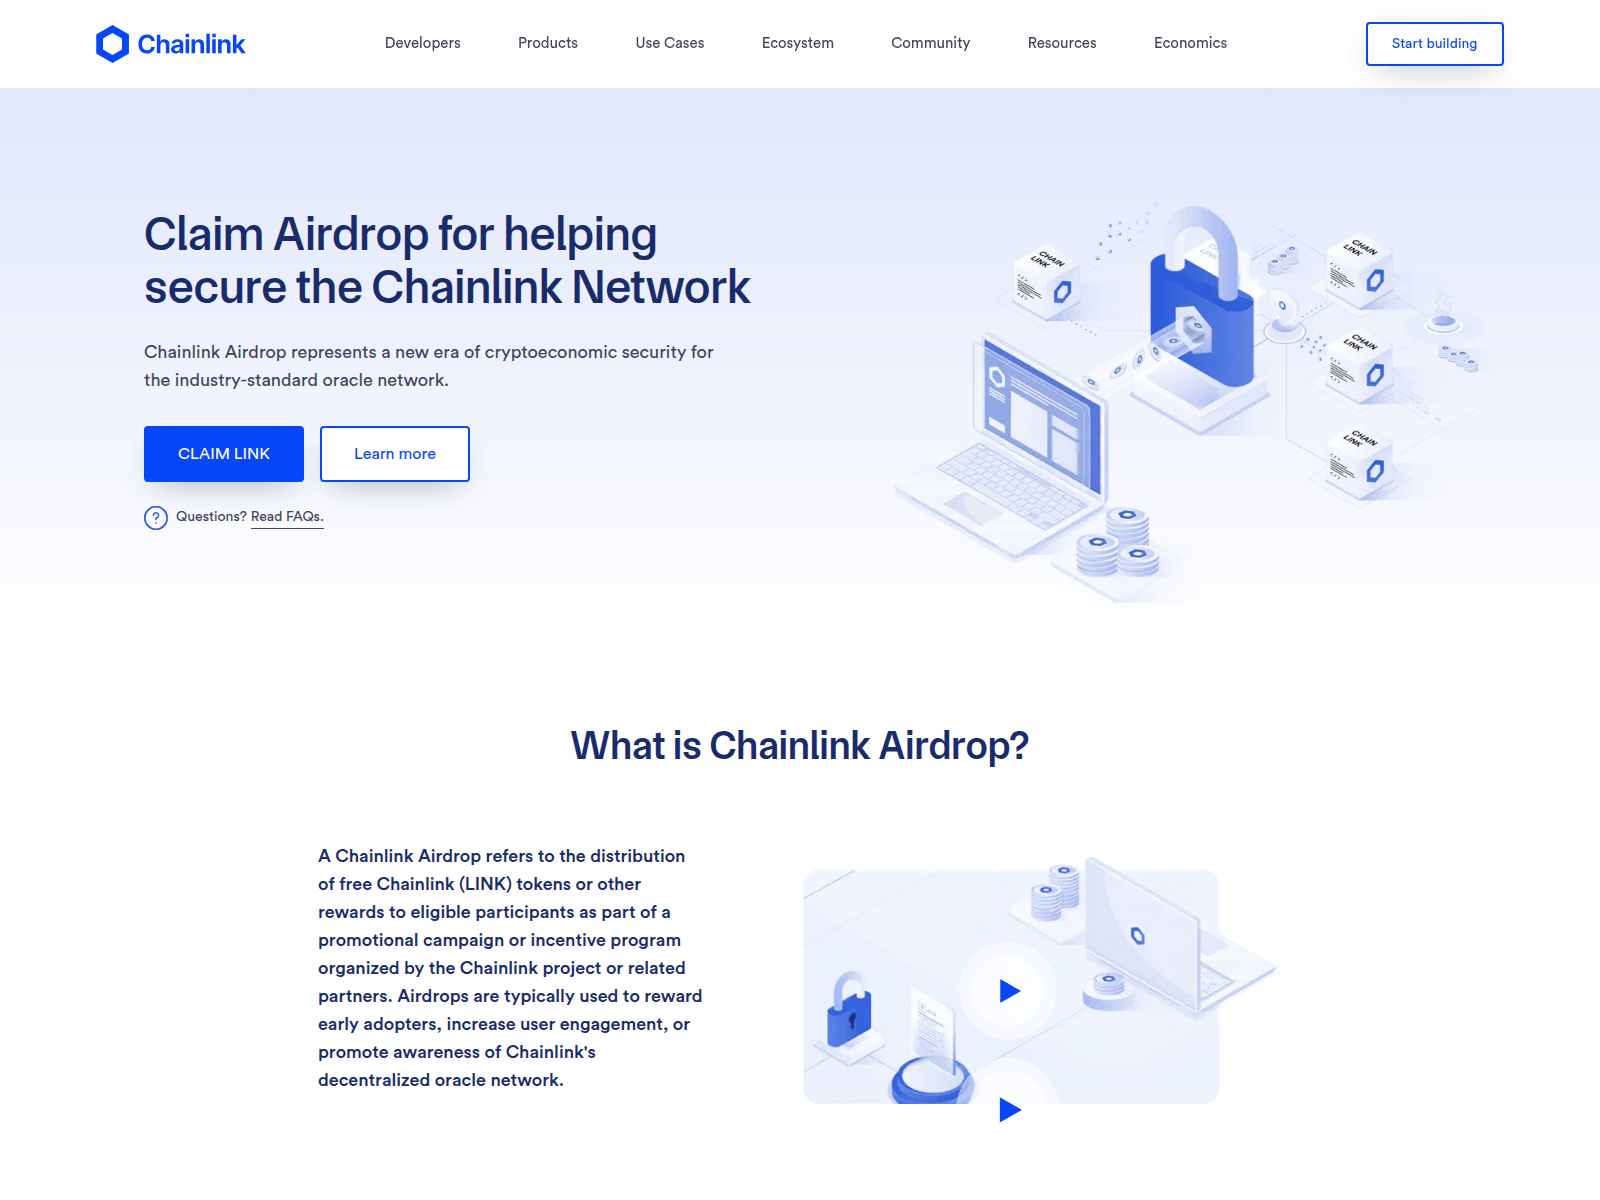
chainlinkairdrop.web.app
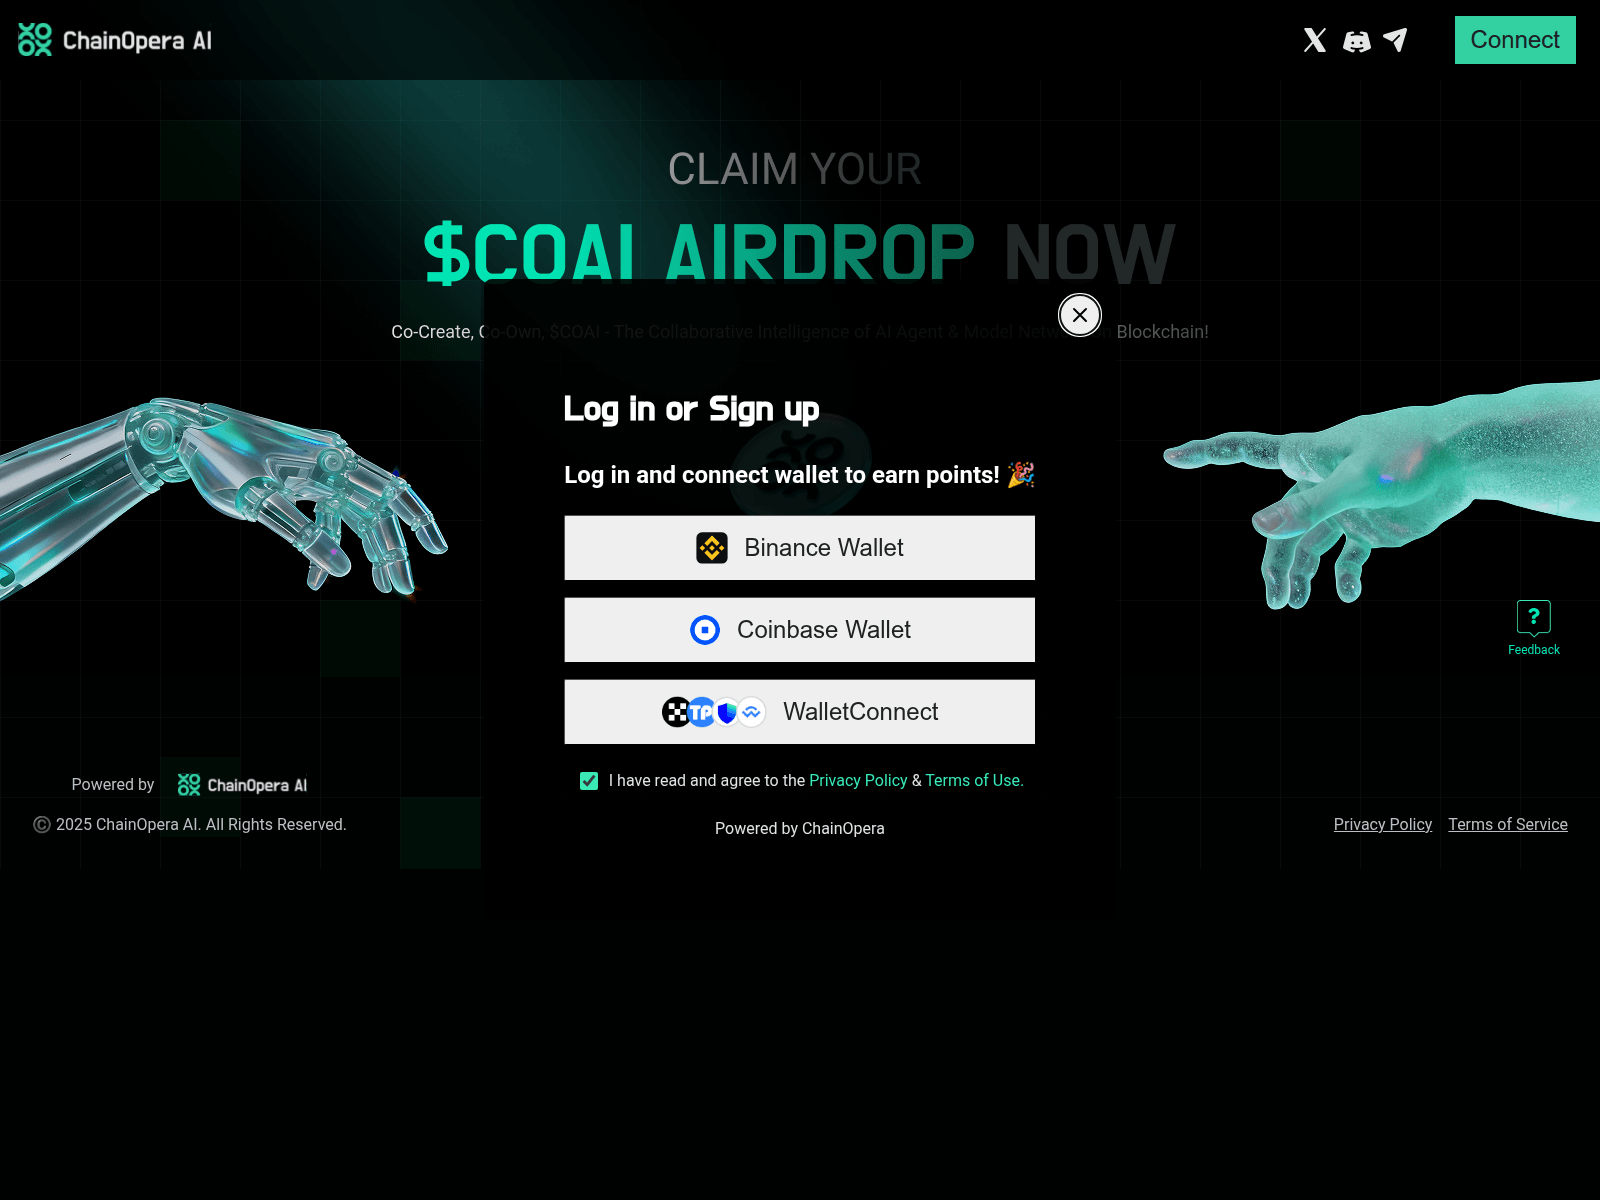
chainopera.foundation
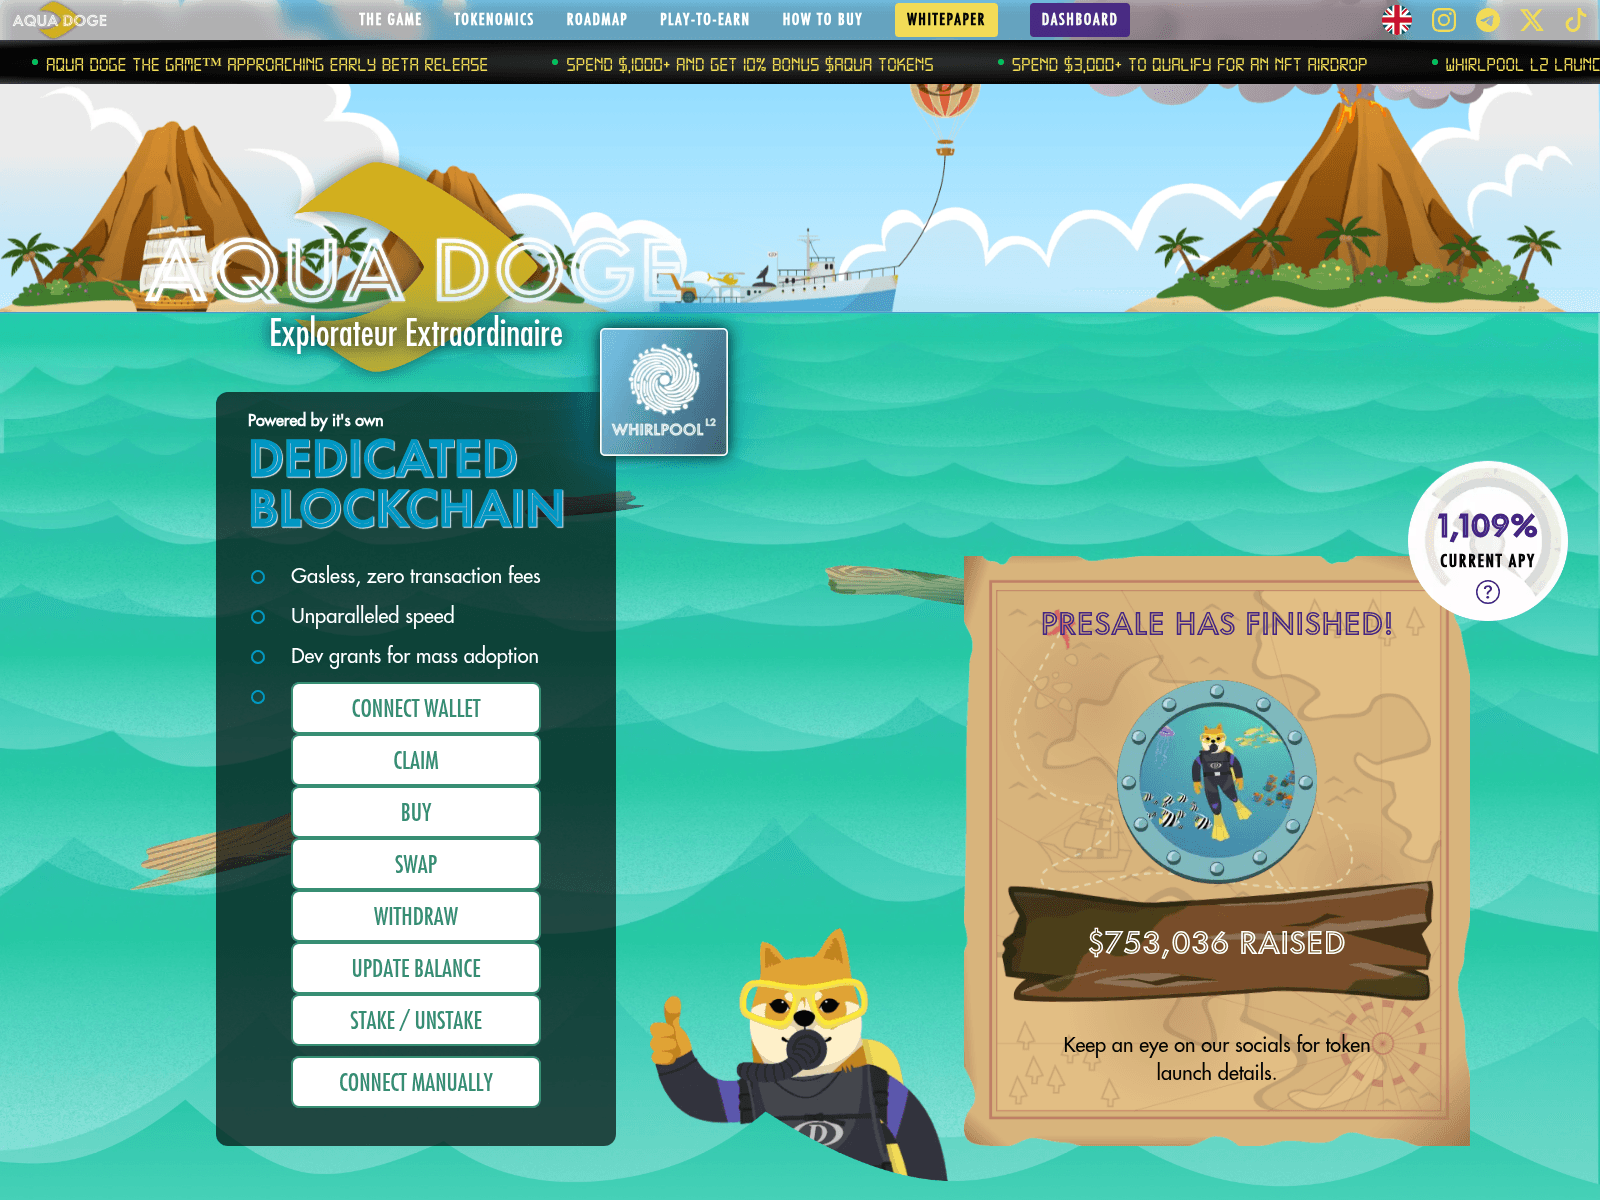
claim-aquadoge.web.app
claim-boundless.app
clear-chat.ai

coinshift.global

cyphq-proposals.com
dappts.depinl.com
dayhub.io
decte-rqaaa-aaaam-advta-cai.icp0.io

duplicate-disabled-2142.invalid
duplicate-disabled-3746.invalid

duplicate-disabled-40909.invalid

duplicate-disabled-4478.invalid

ecoaave.com
egencloud.pages.dev

etherfi-claim.com
ethgas.art
euylk-paaaa-aaaac-a3uya-cai.icp0.io
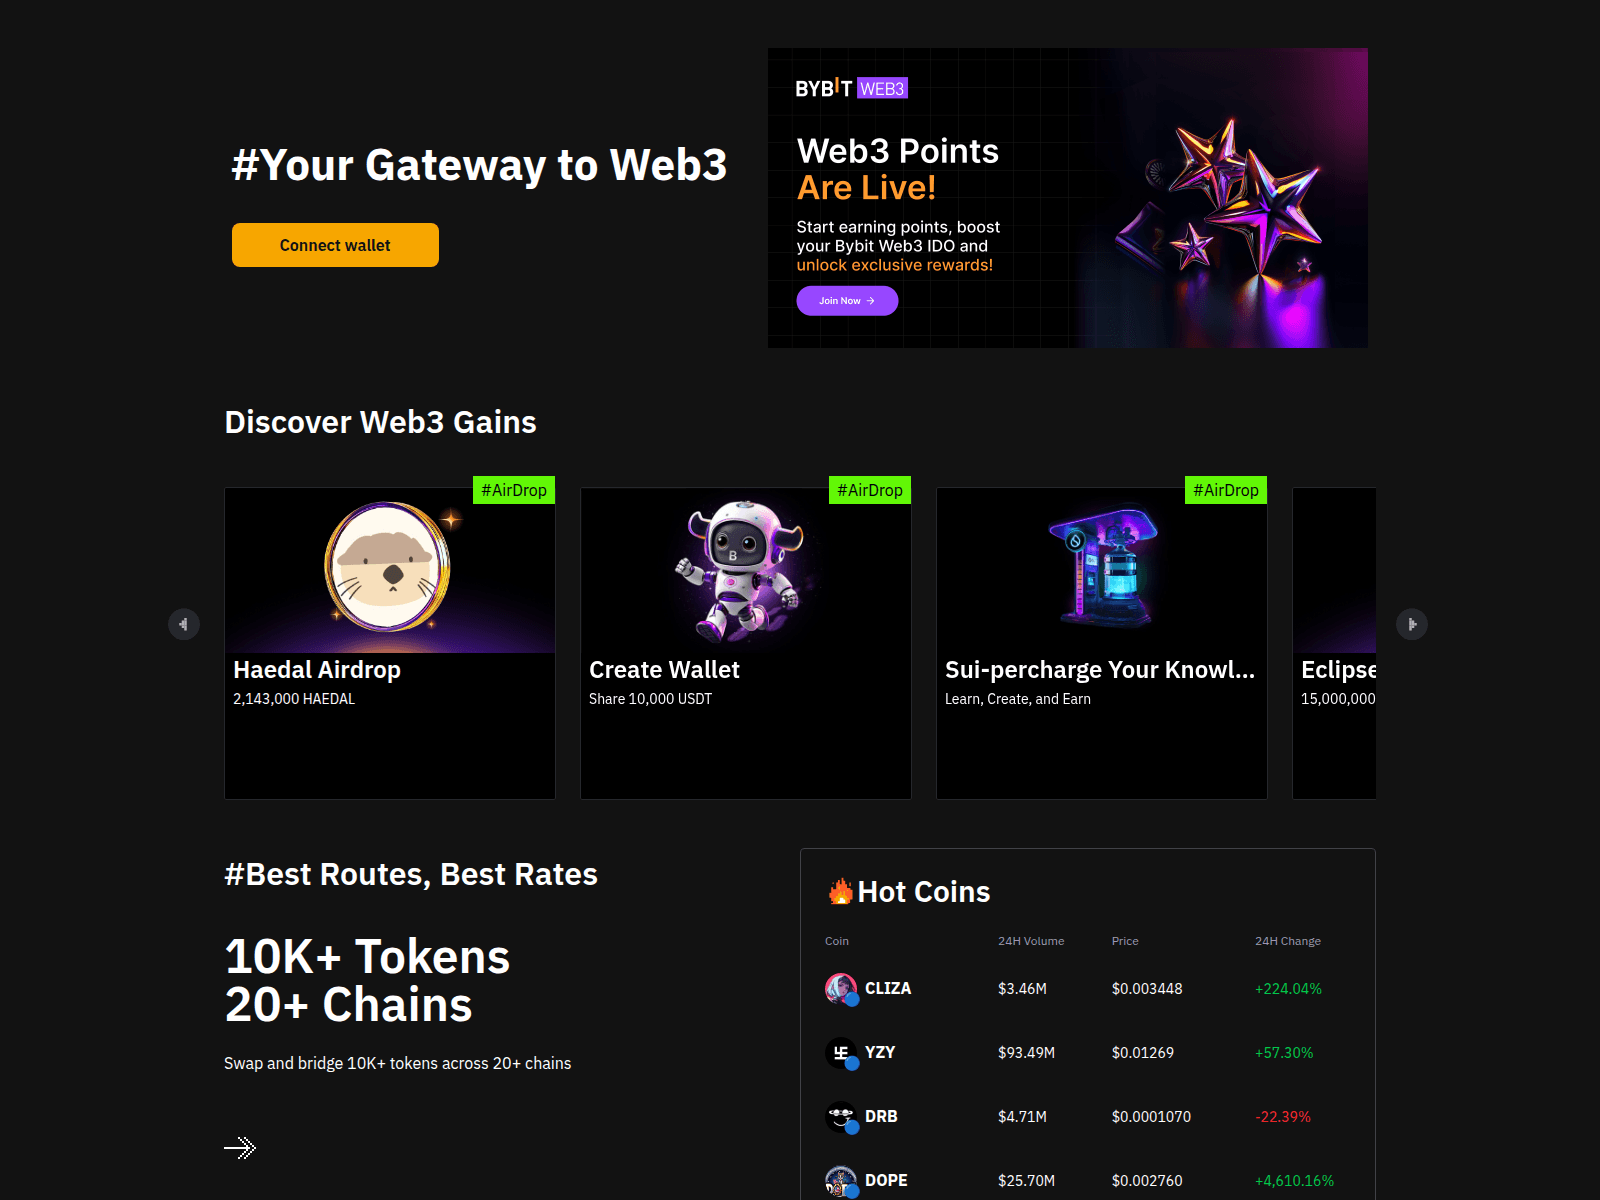
everysteprise.com
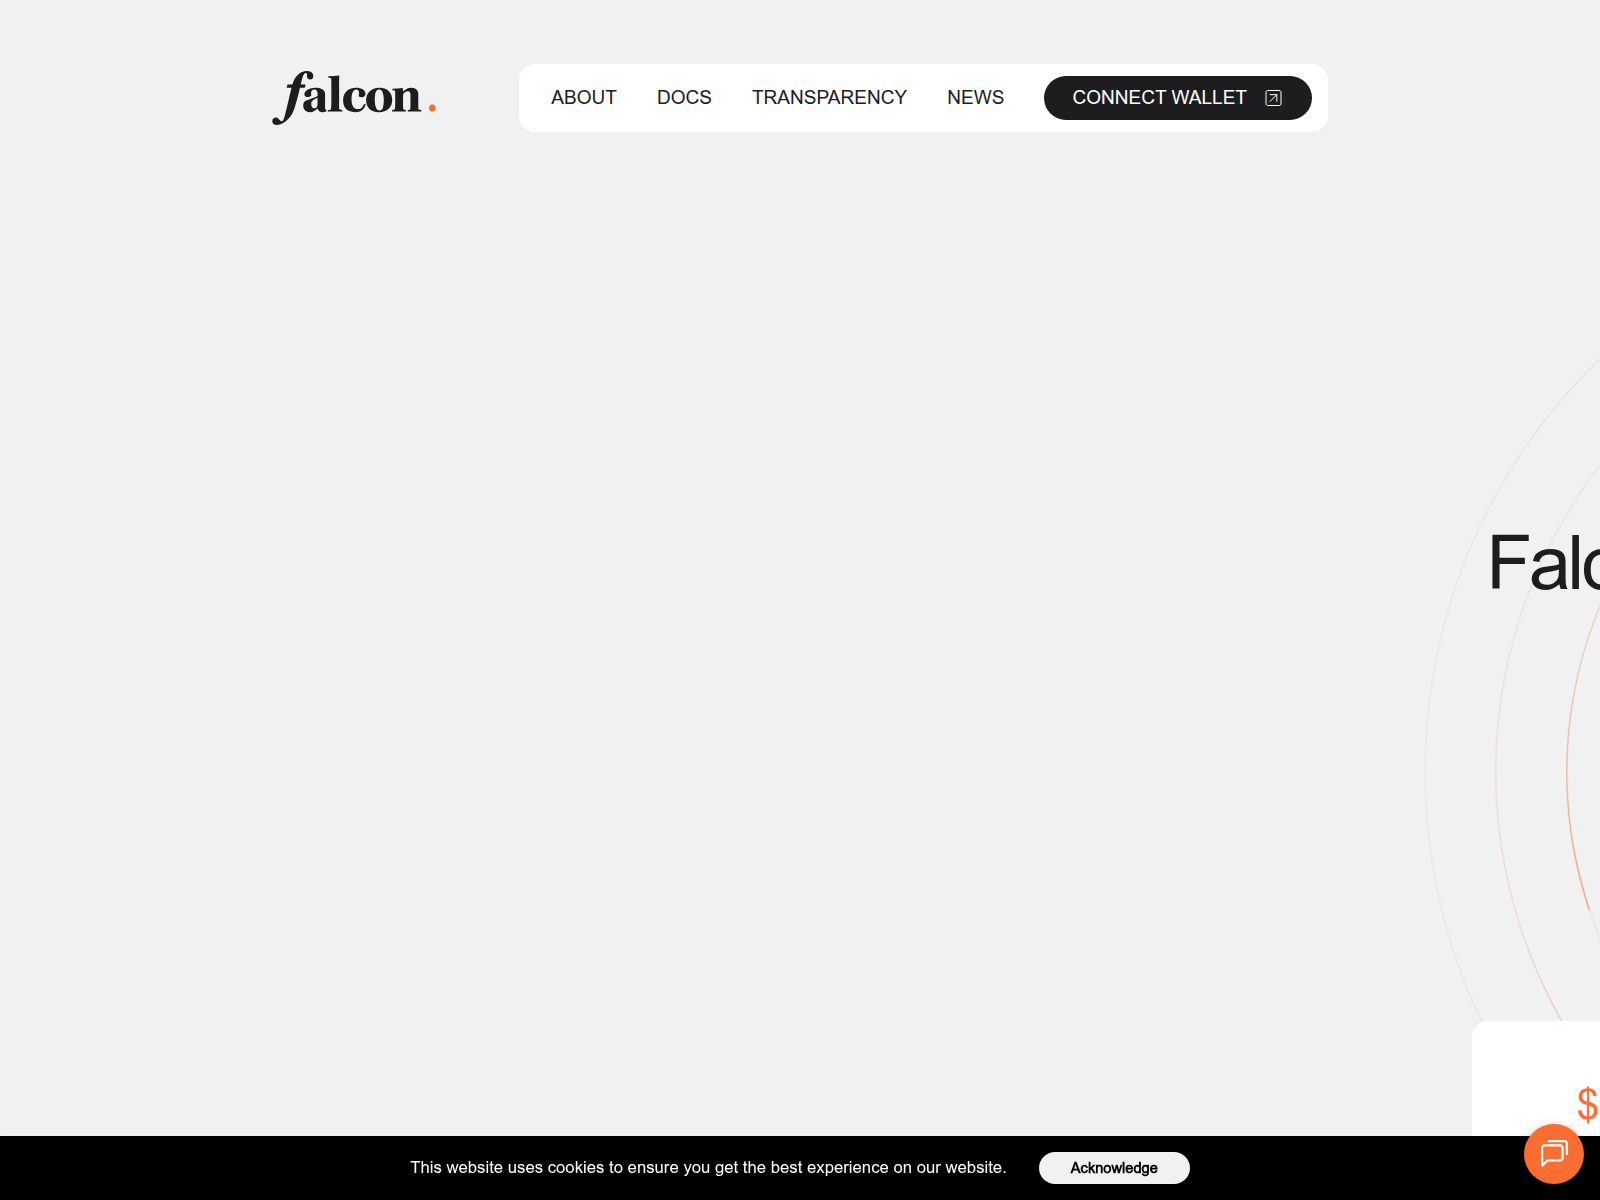
falcon-finance.app
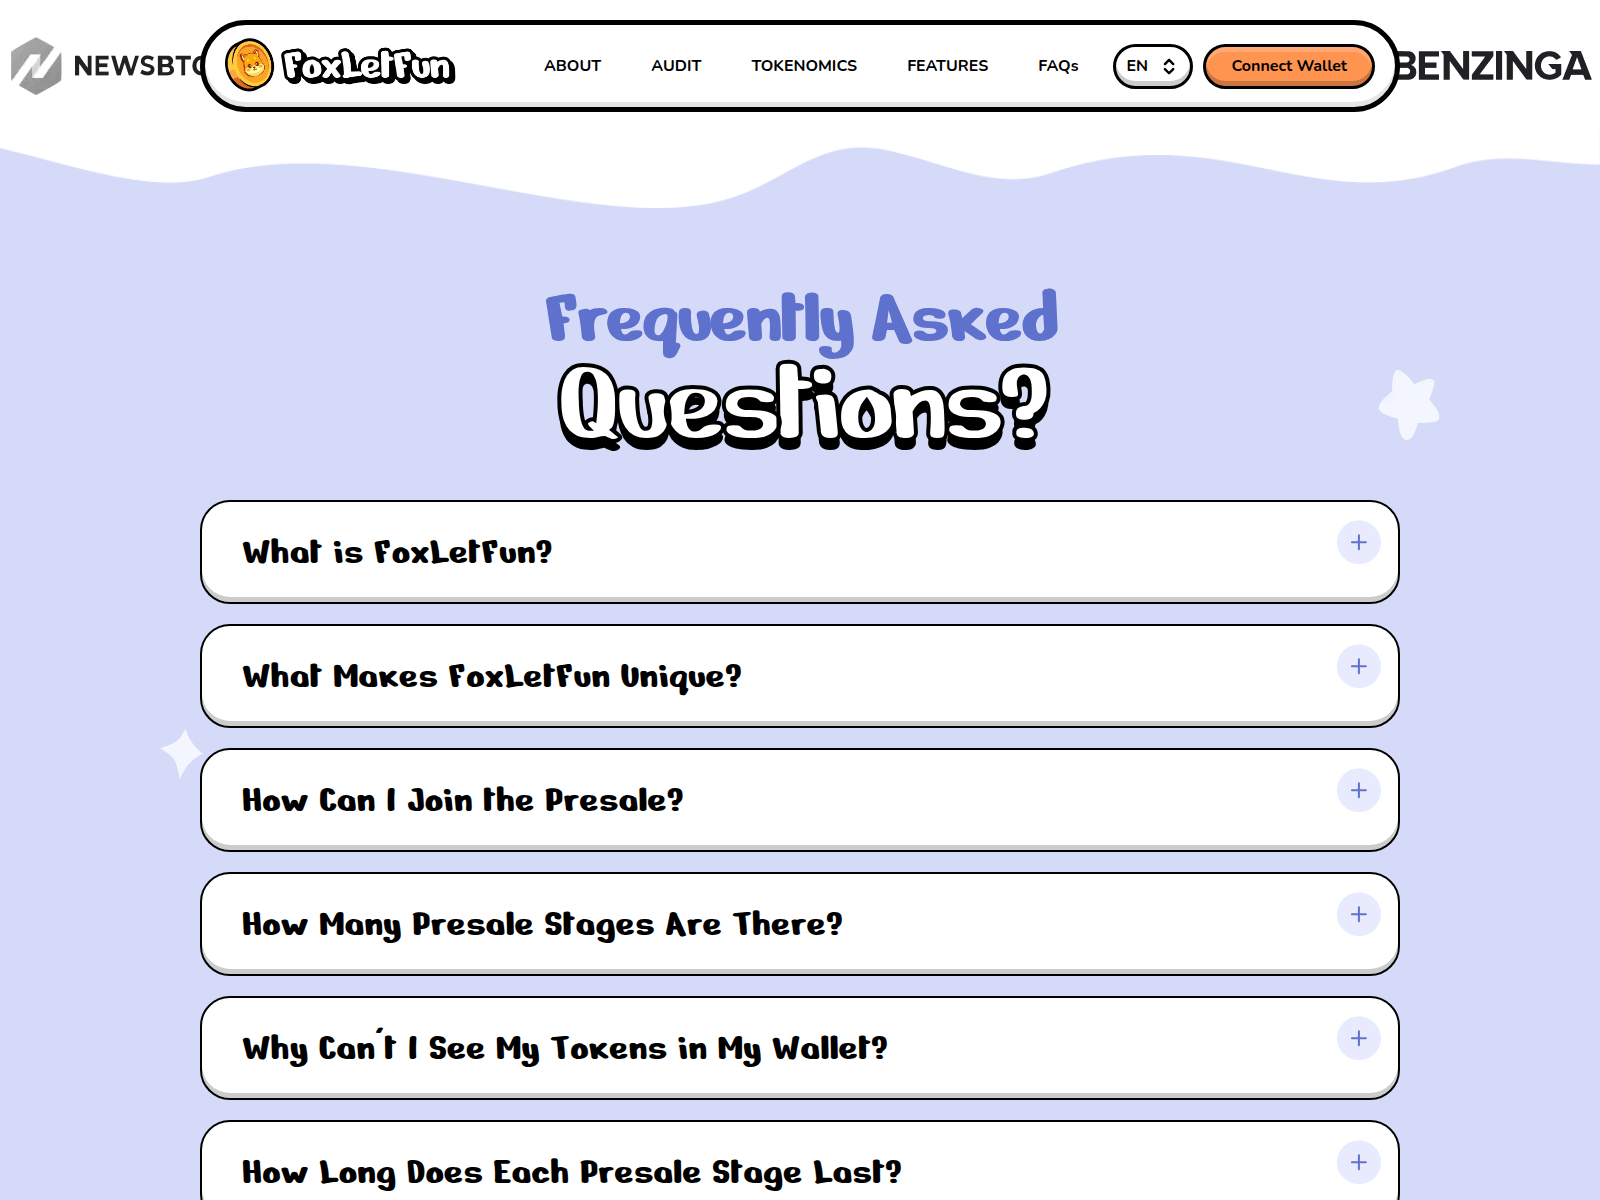
foxletfuntoken-com-purchase-website.pages.dev

get-crypto.online

getyourairdrop.com
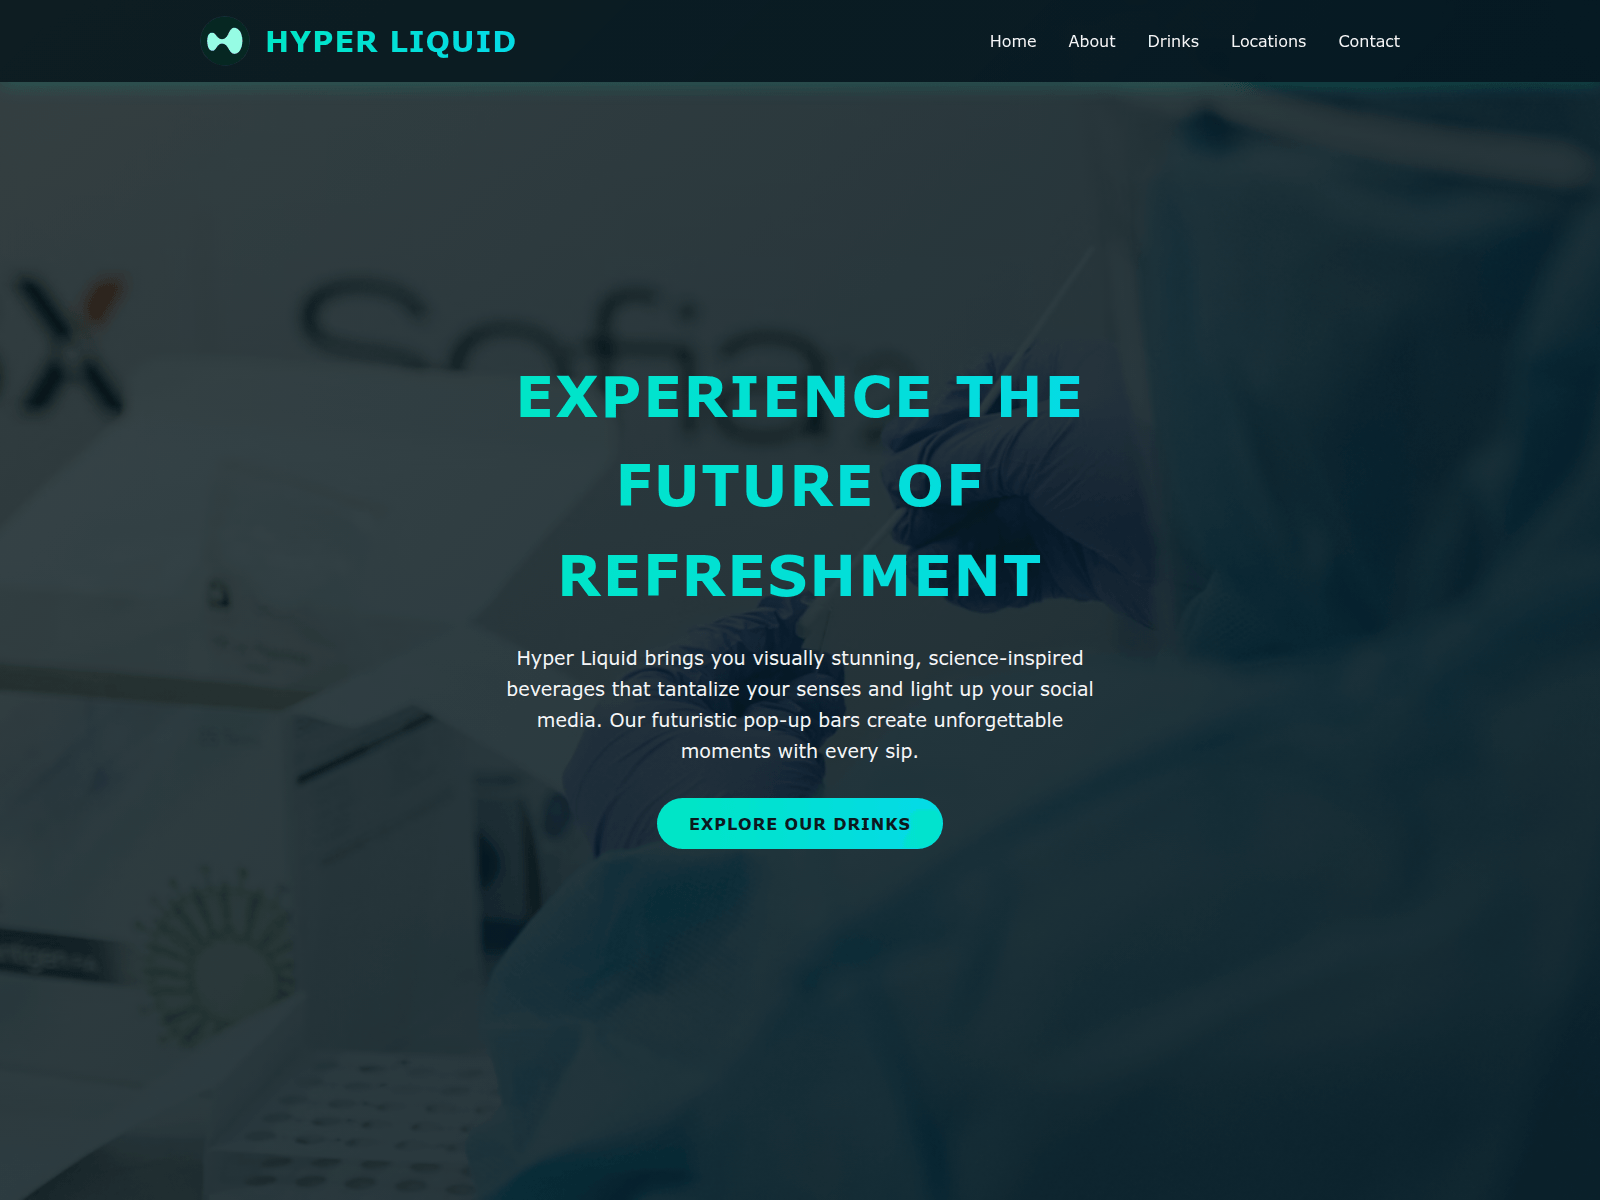
hype.rliquid.co.com
hyper-eligibility.com
hyperfoundation.snapshots.workers.dev

hyperliquid-airdrop.org
hyperliquid-deposit.pages.dev
hyperliquid-tracing.web.app
iassets.org
ico.gaia-blockchain.com
integratedsystemsconnect.com
interac.cakepay.eu

isbankmobilcep.com
islamic-guard.web.app
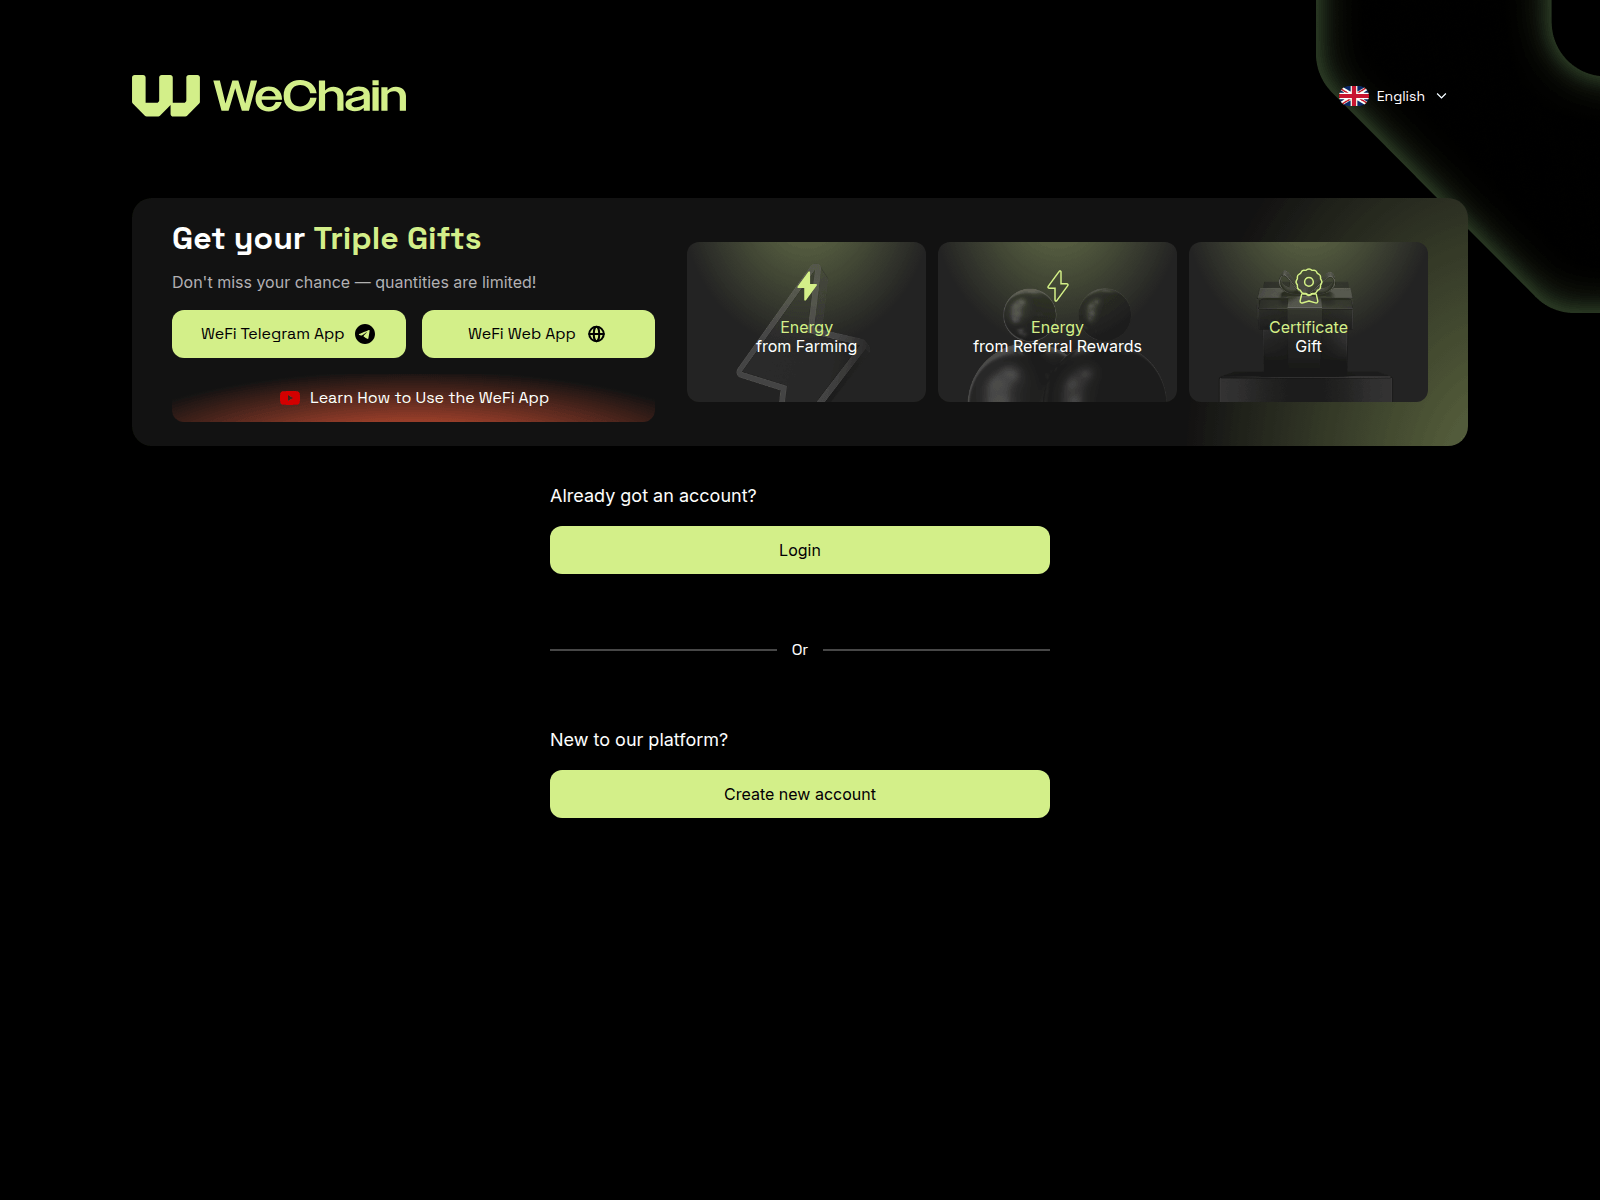
ito.wechain.ai
jitosol.lol

lfg.eco
lineacore.org
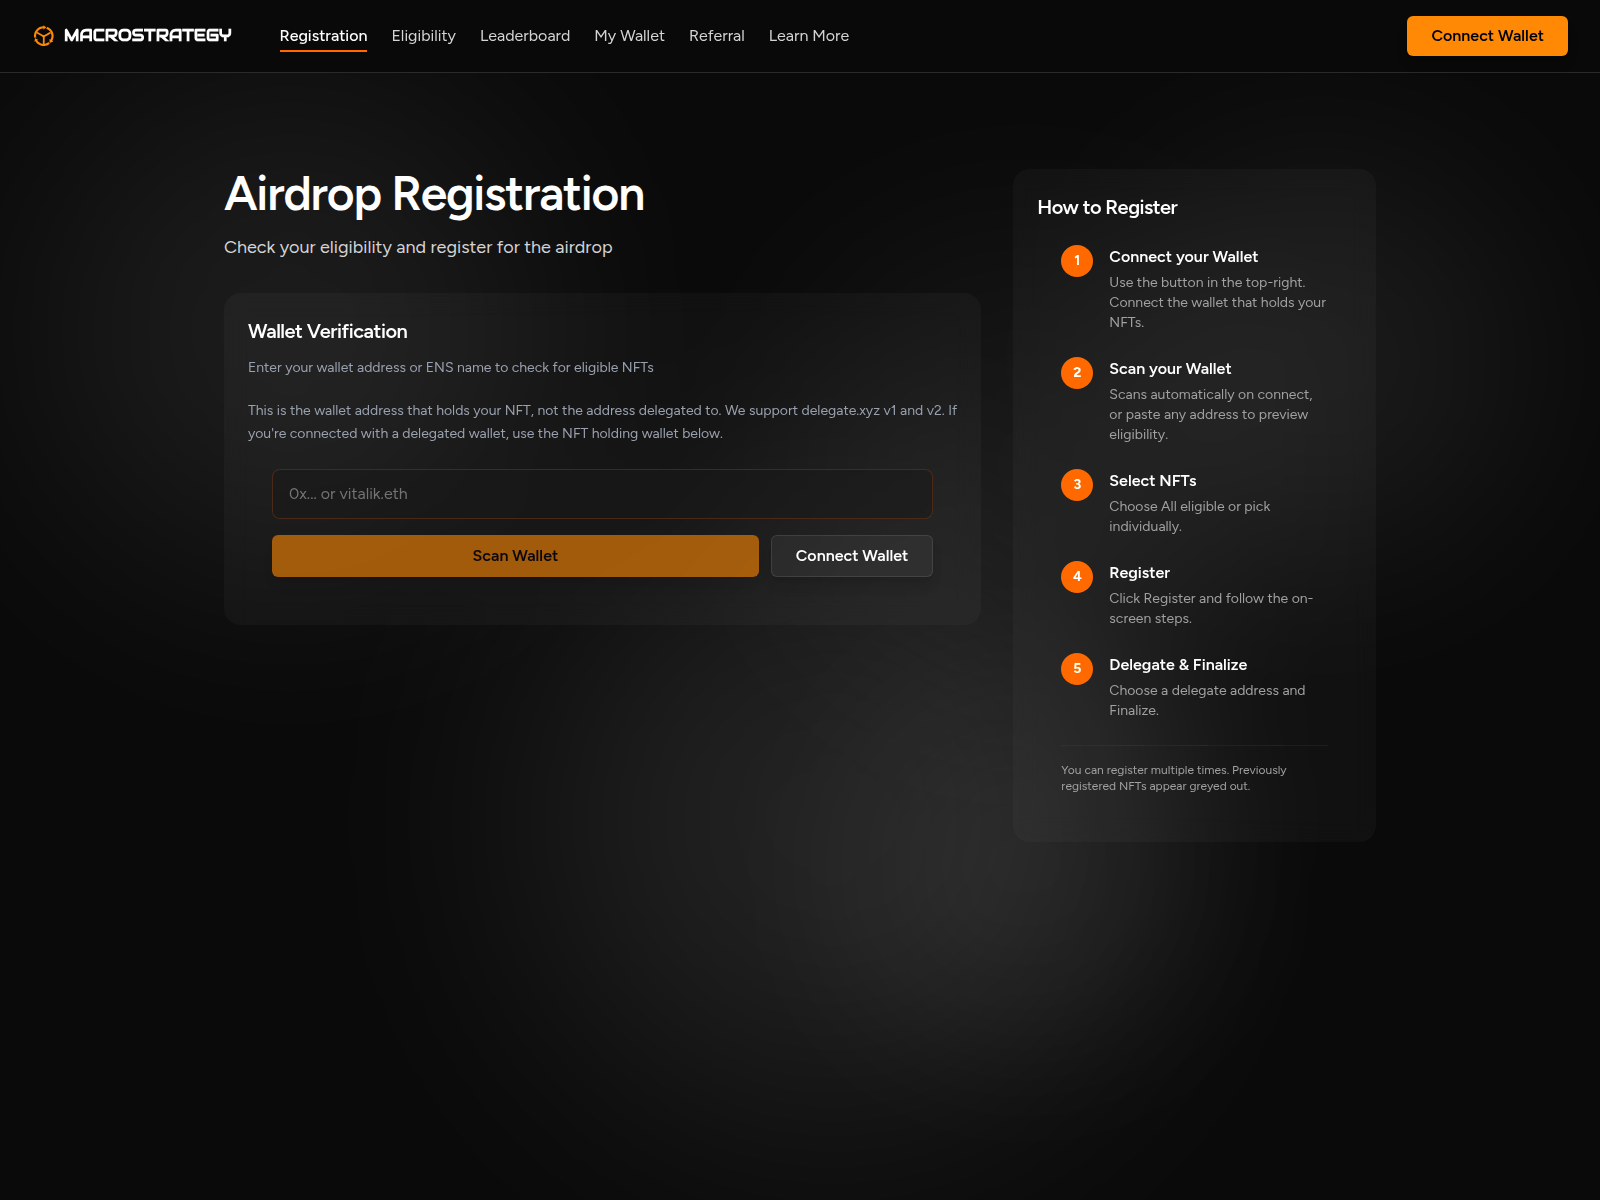
macrostrategy.tech
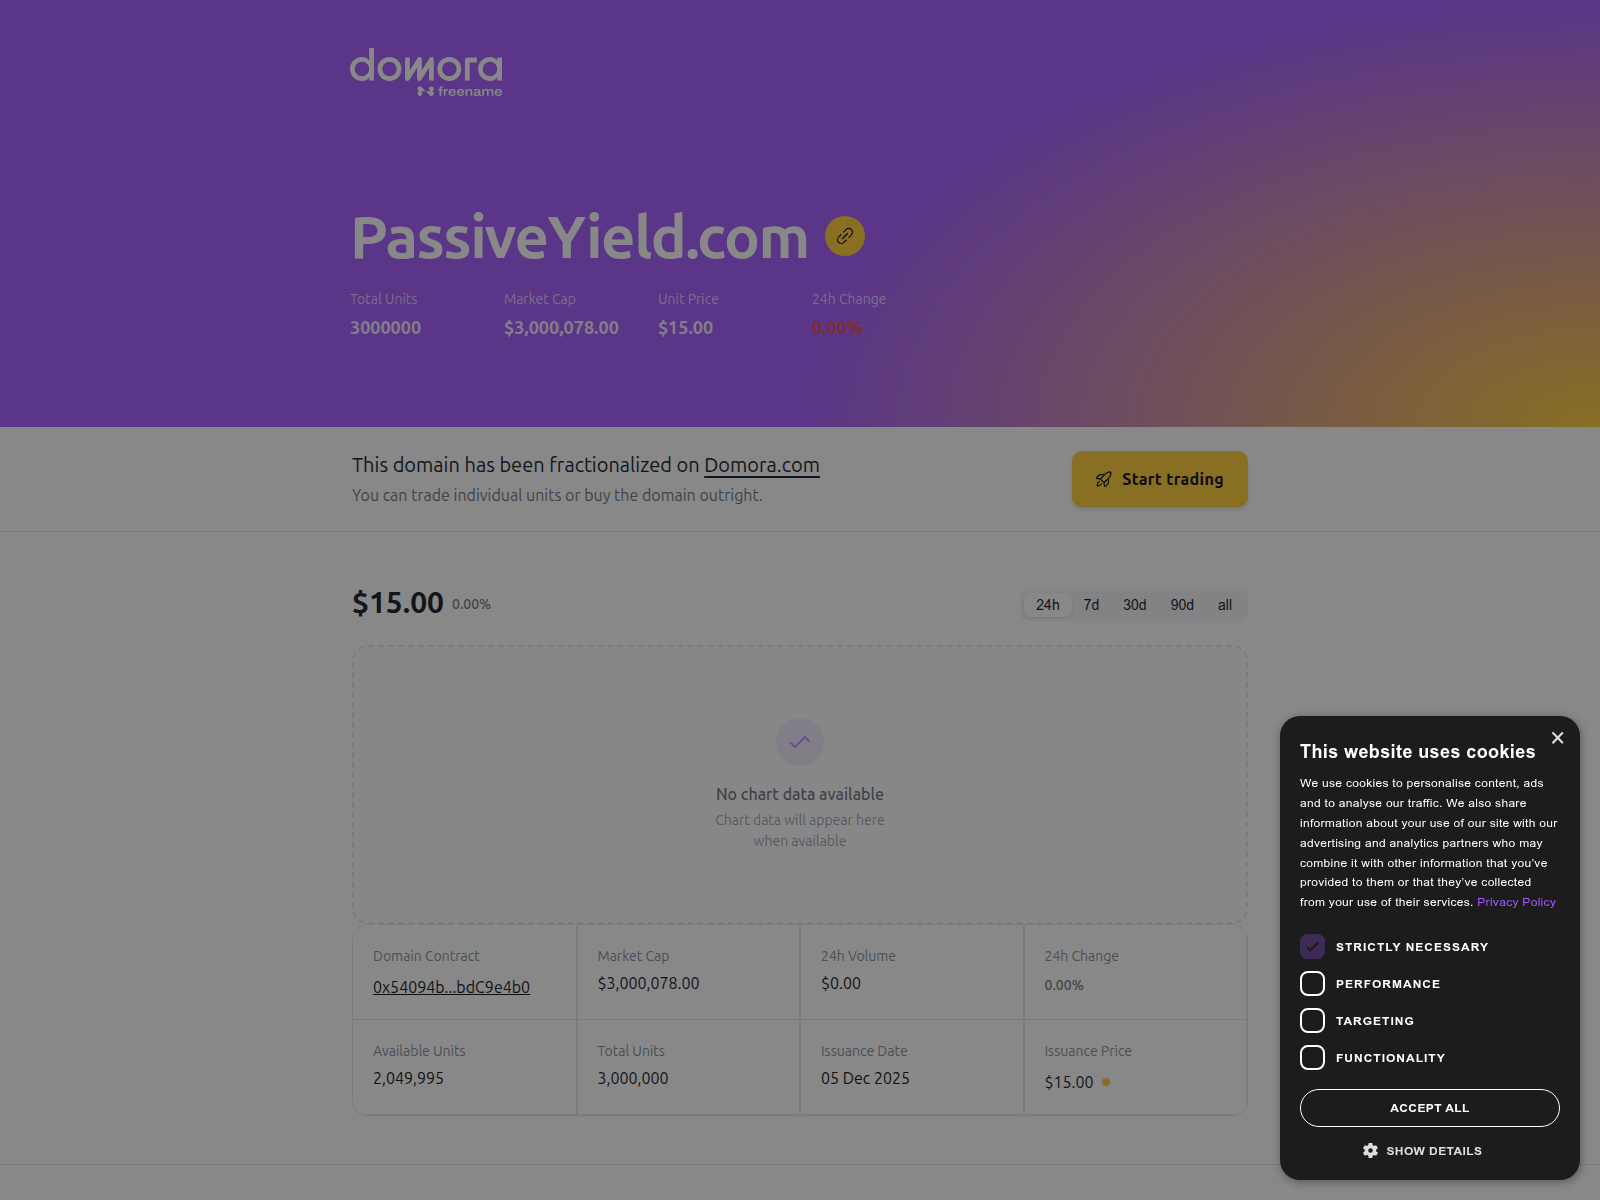
malenerosenberghansen.com
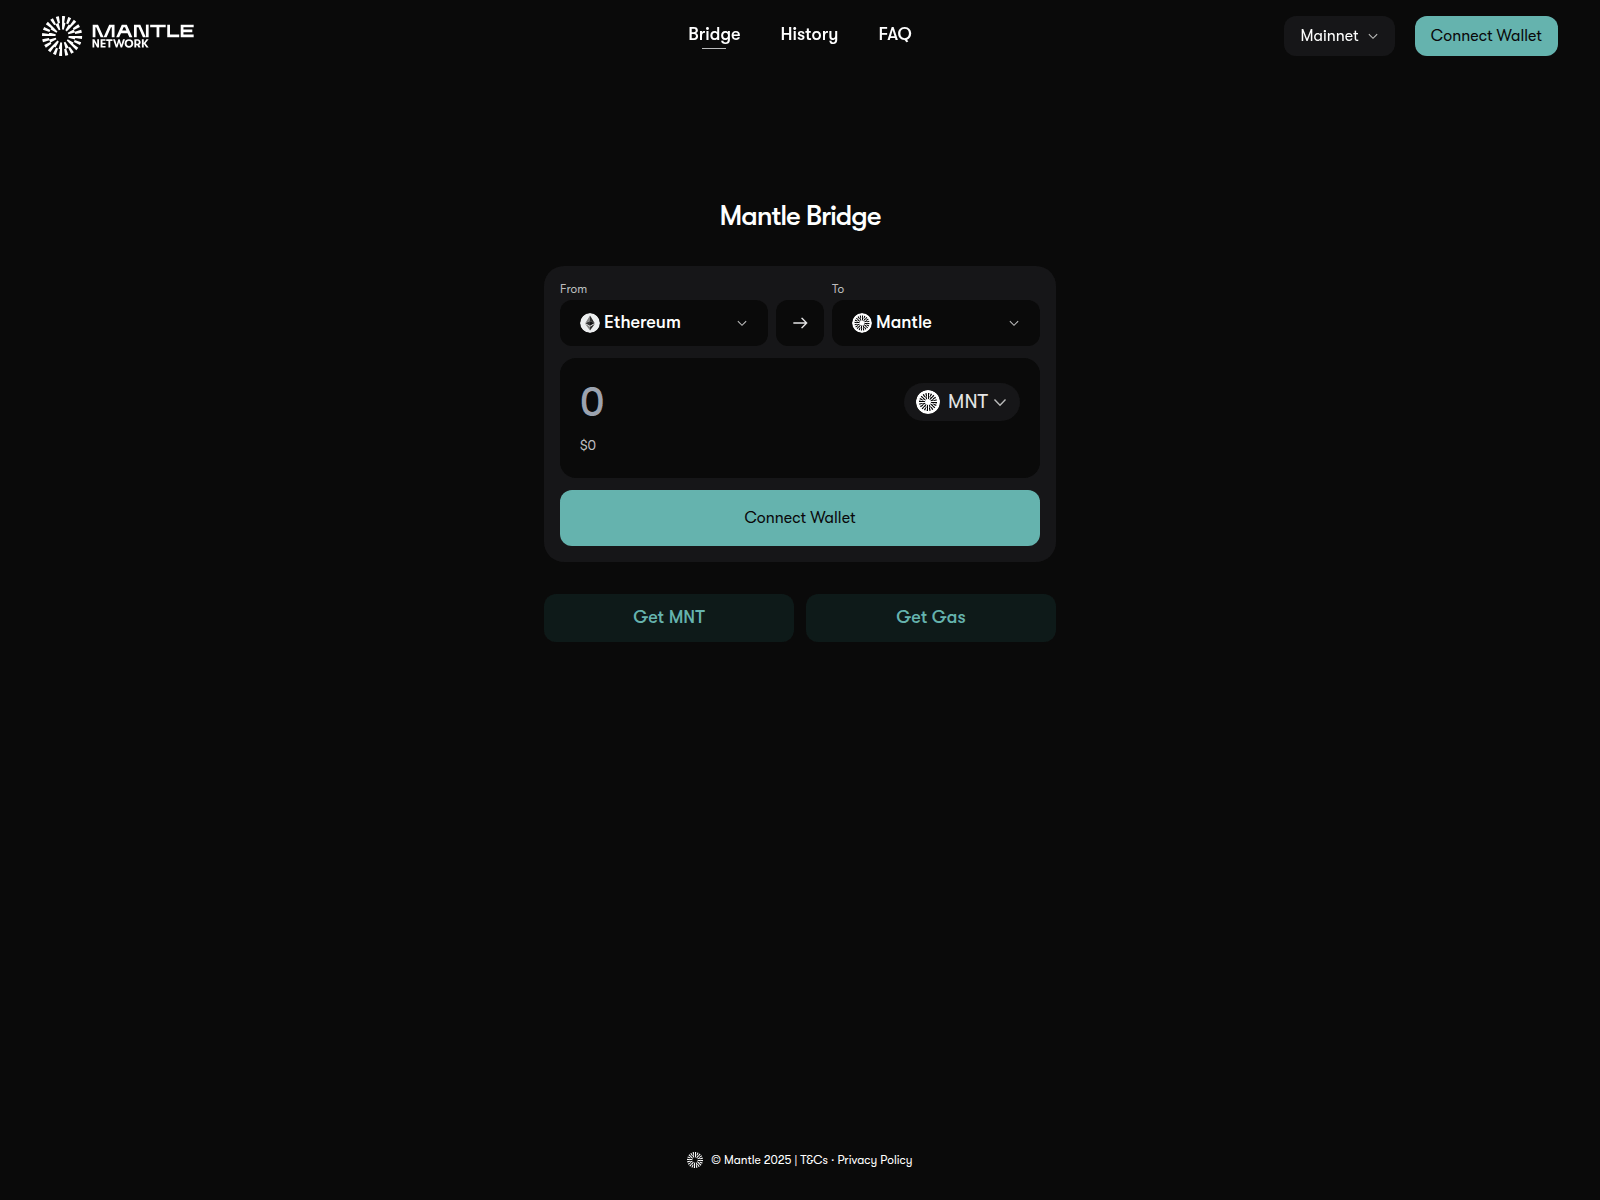
mantlubrodge.org
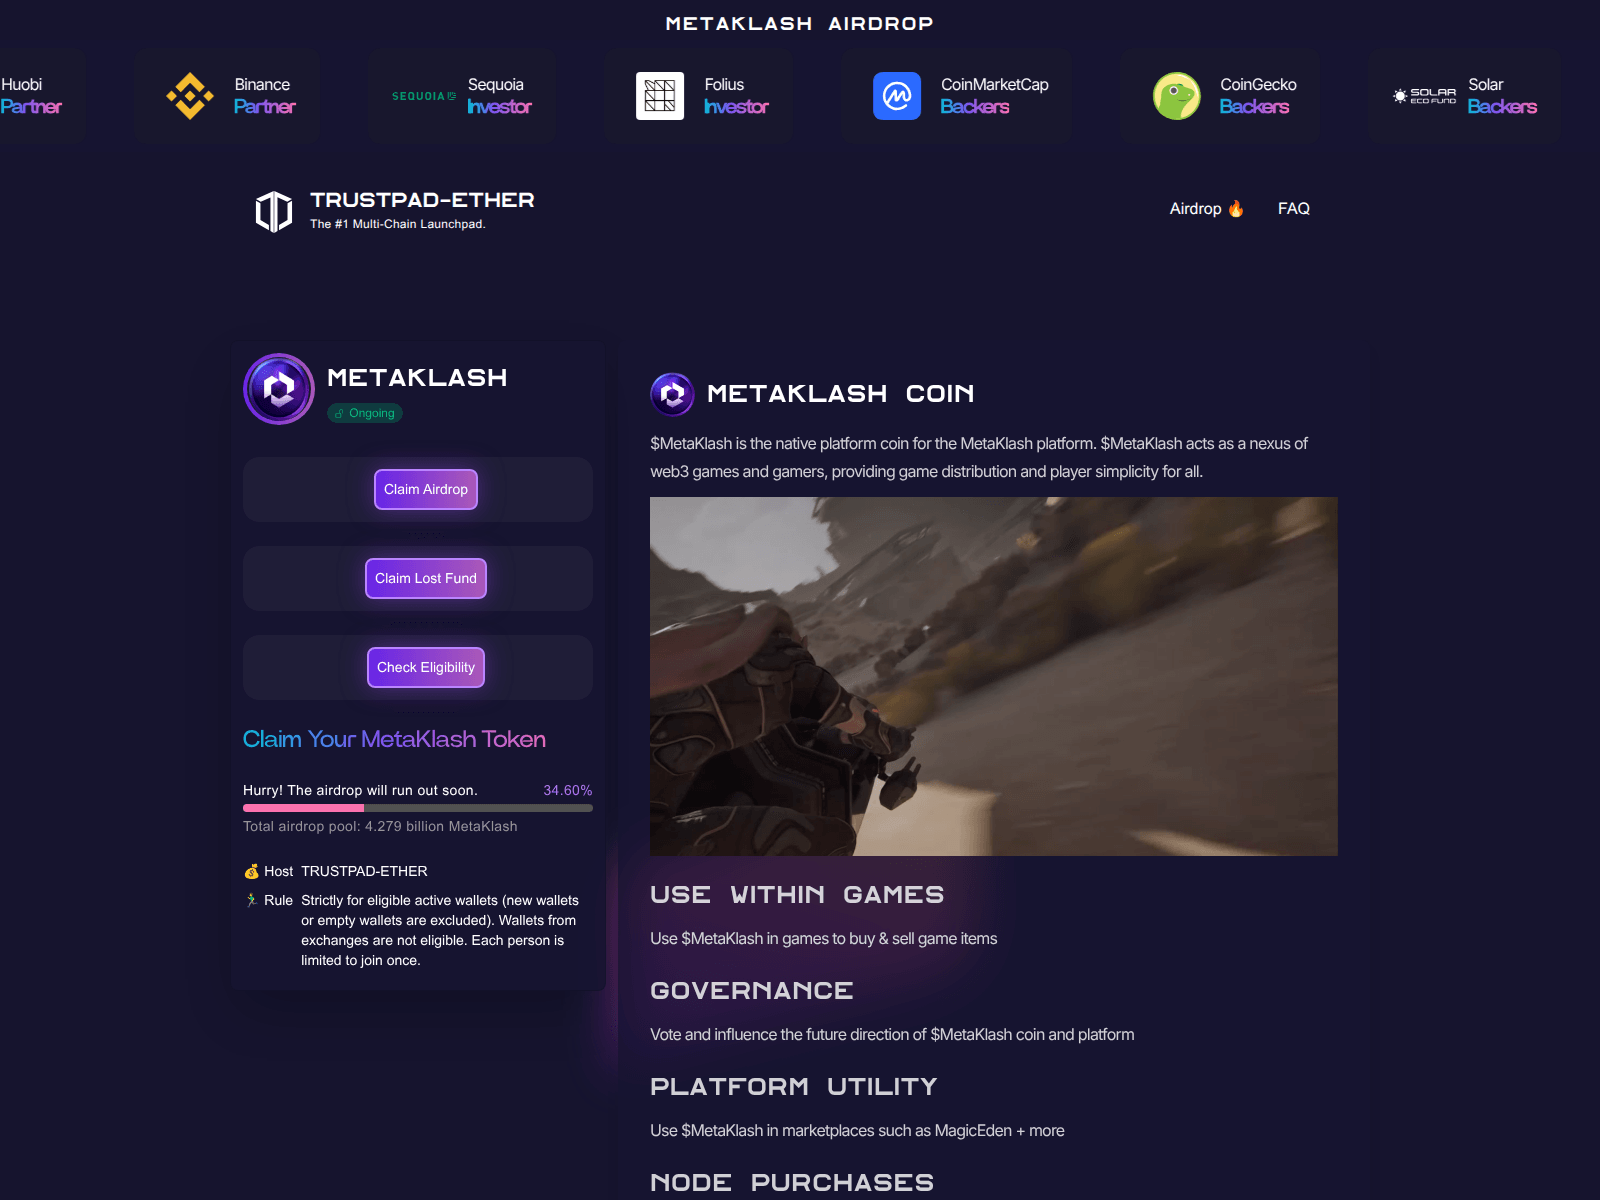
metaklash.com

migratejpeg-jpegd.com
mstblockchain.com
neiropump.org
nkyfp-kyaaa-aaaaj-az62q-cai.icp0.io
nnvtz-uqaaa-aaaah-qpuuq-cai.icp0.io

online650.com

opinion-vote.com
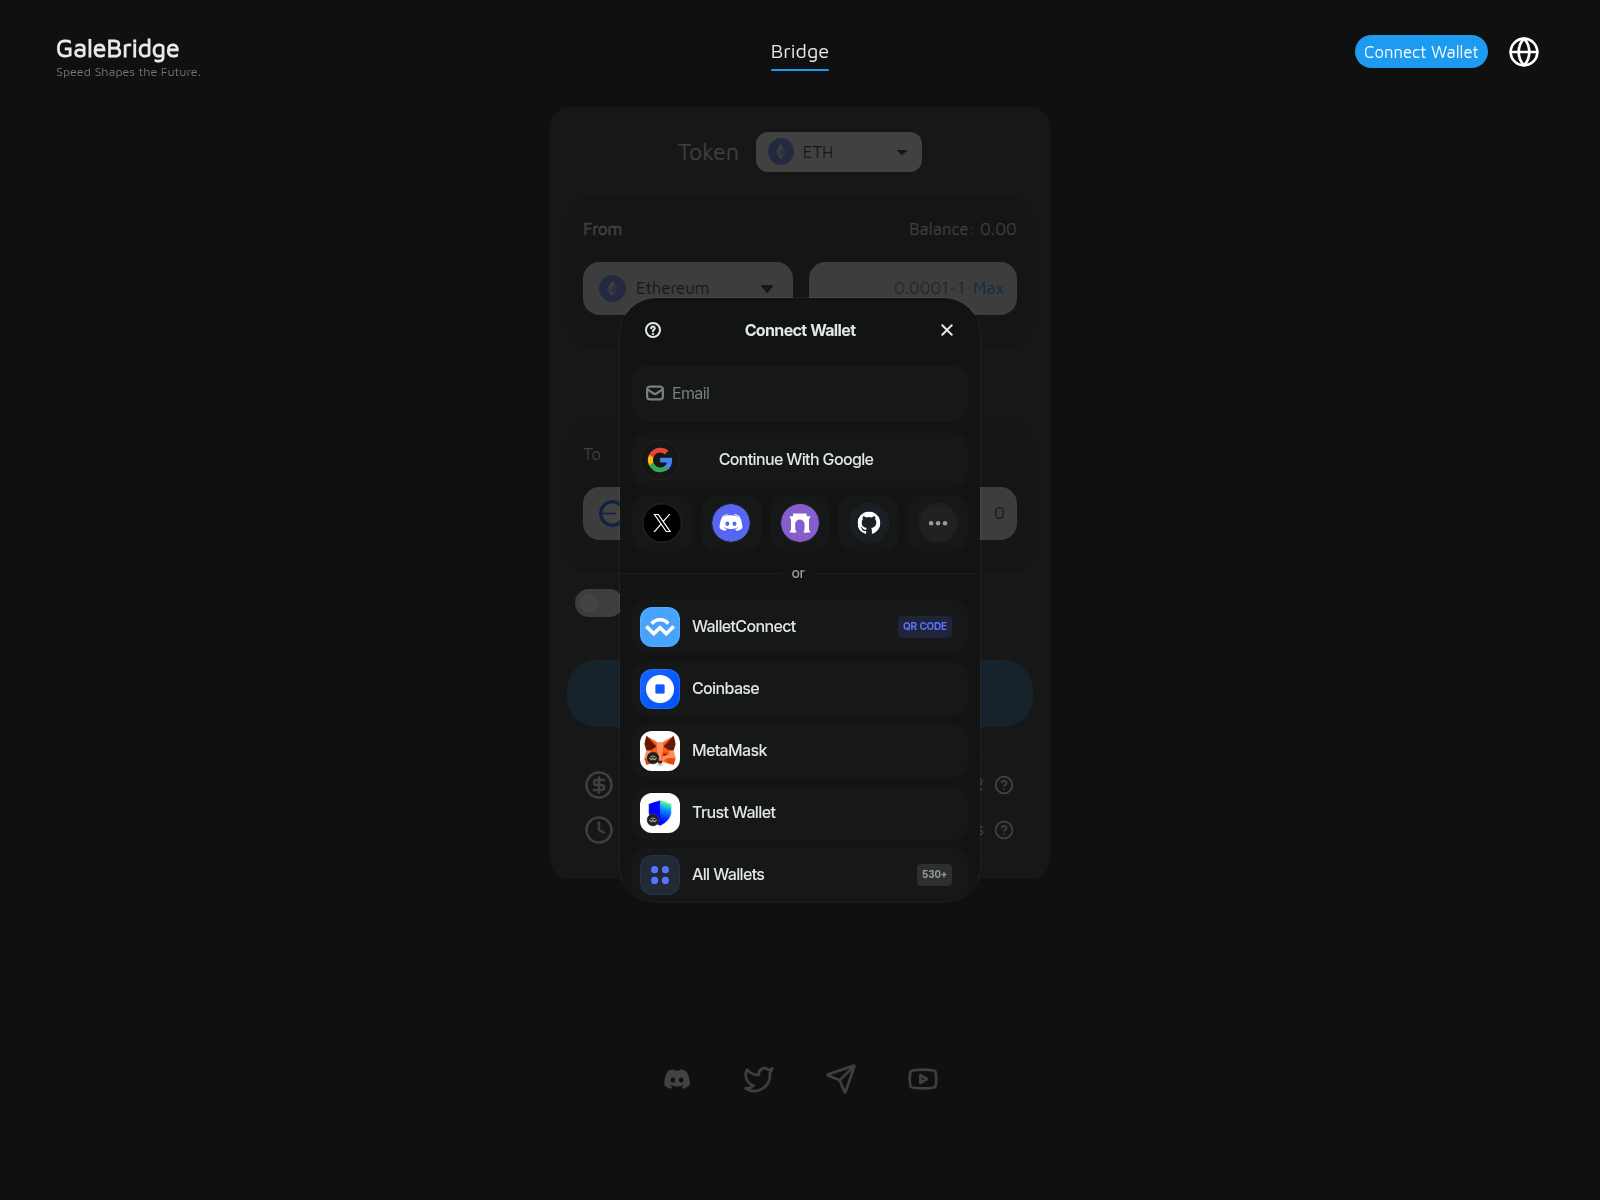
originswap.org

oxygenprotocol.space
oz5wg-liaaa-aaaap-qb43a-cai.icp0.io
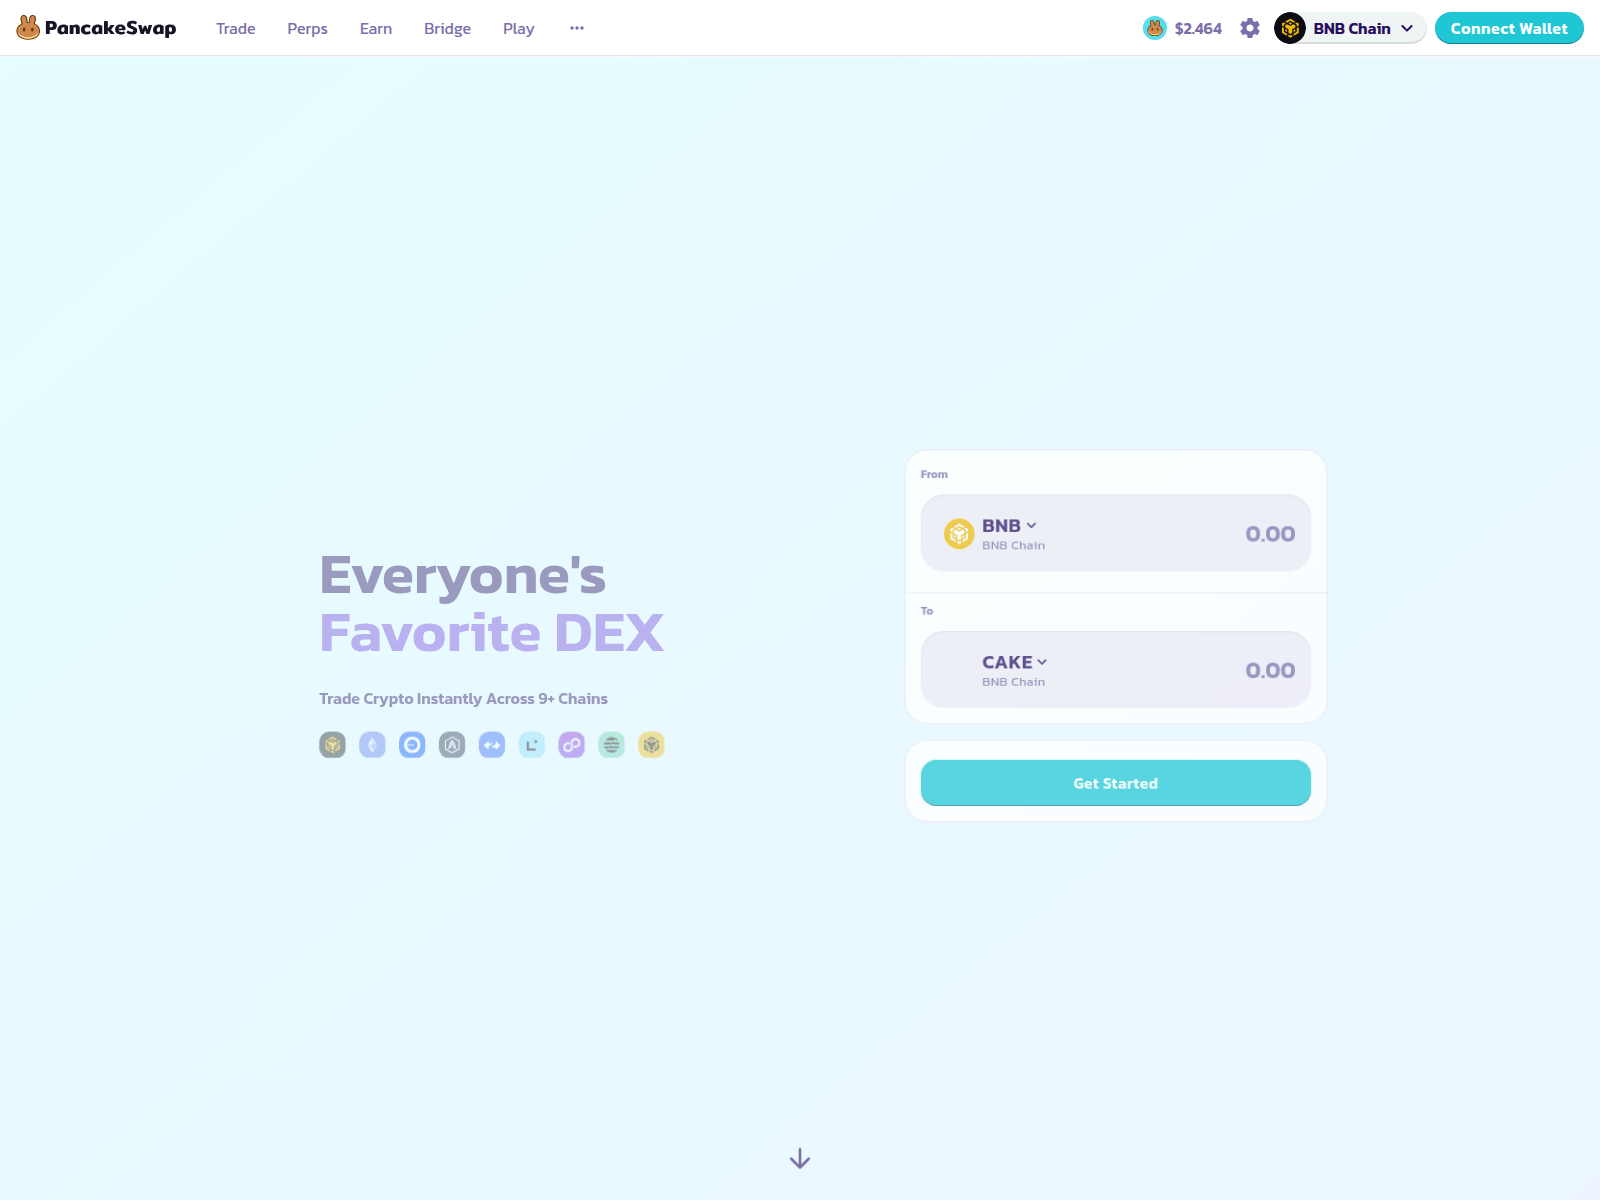
pancakeswap.cam
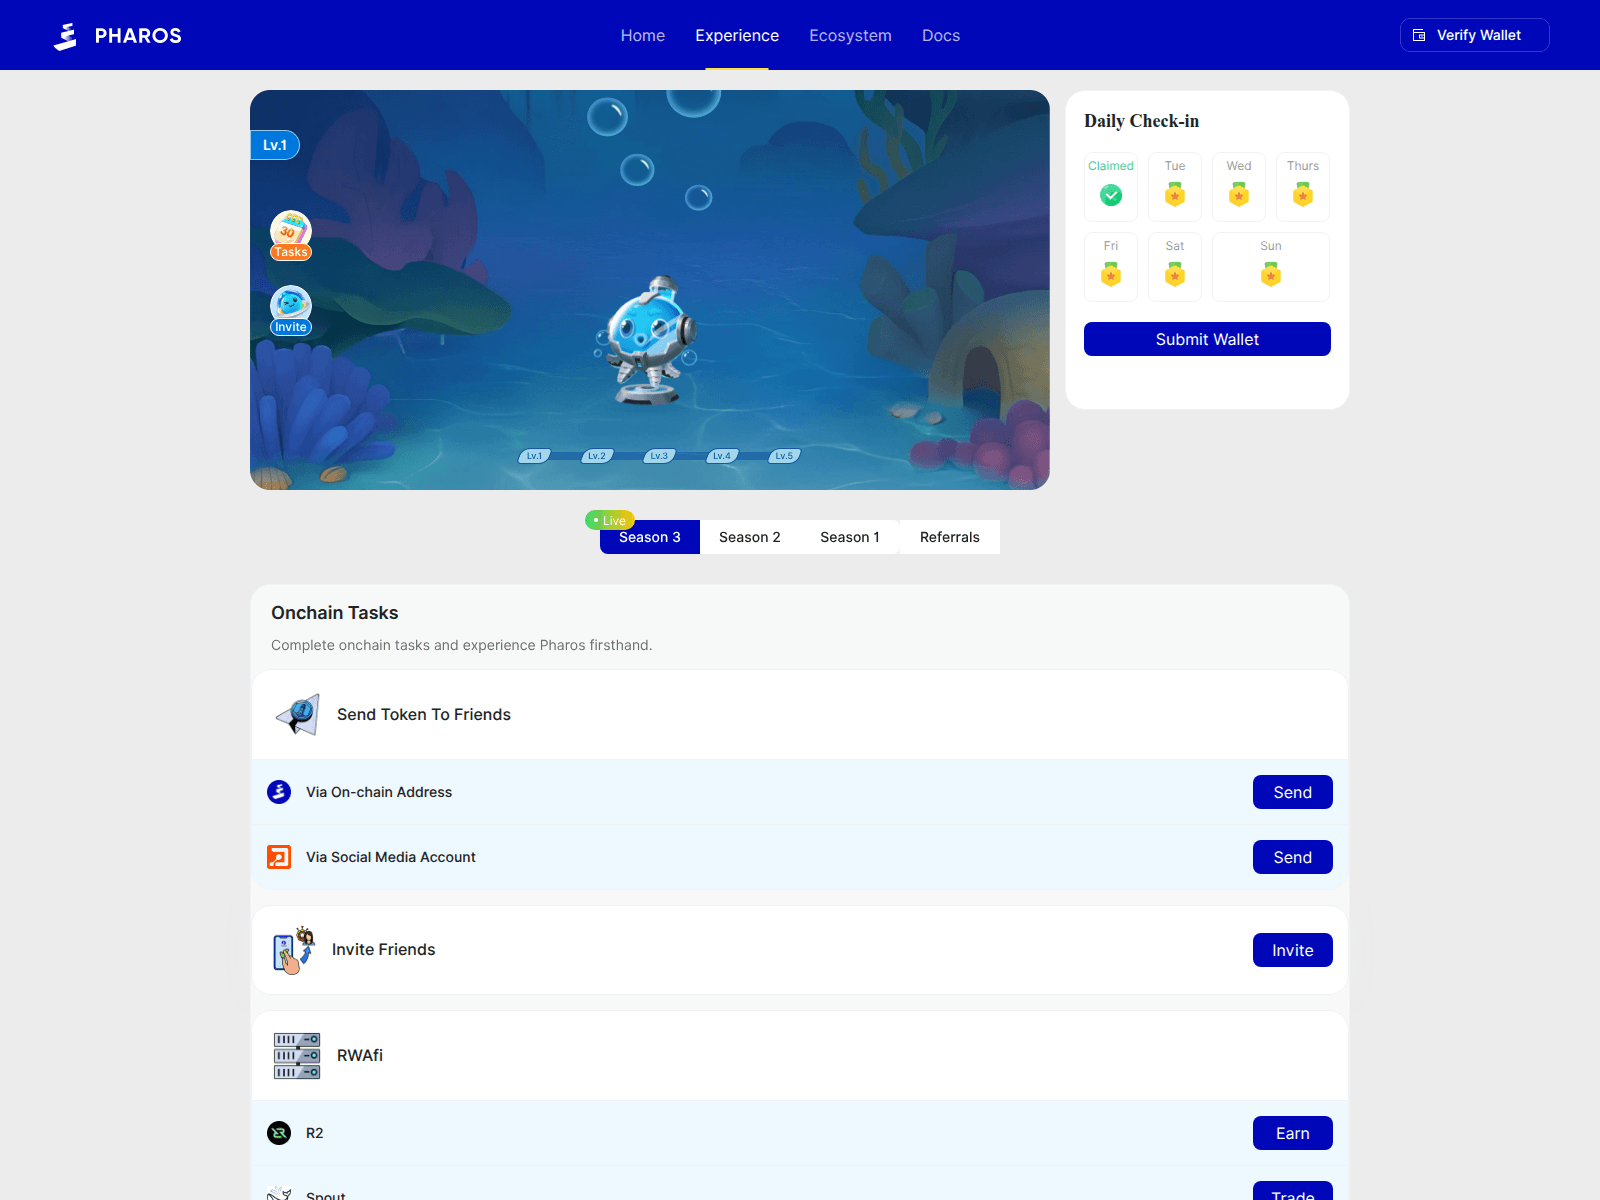
pharoshub.web.app

play.astroc2m.space

polynow.fun

portalbancus.com
pqlzd-baaaa-aaaai-aqfja-cai.icp0.io
presale.digitap.app
pumpcoin.site

pumpfunclaim.online
quantbitverse.com
quickswap.exchange-defi-web-referral.icu
quickswap.exchange-dex-swap-referral.lol
quickswap.exchange-web-defi-referral.life

restoredappnode.com
sanctummm.pages.dev
smartsmoney.io
snipersolbot.com

solsnipers.netlify.app
soneium.pumpevm.net
stake.divewallet.net

sudbbtoken.com
telegrambotgame.pages.dev

tge-momentum.com
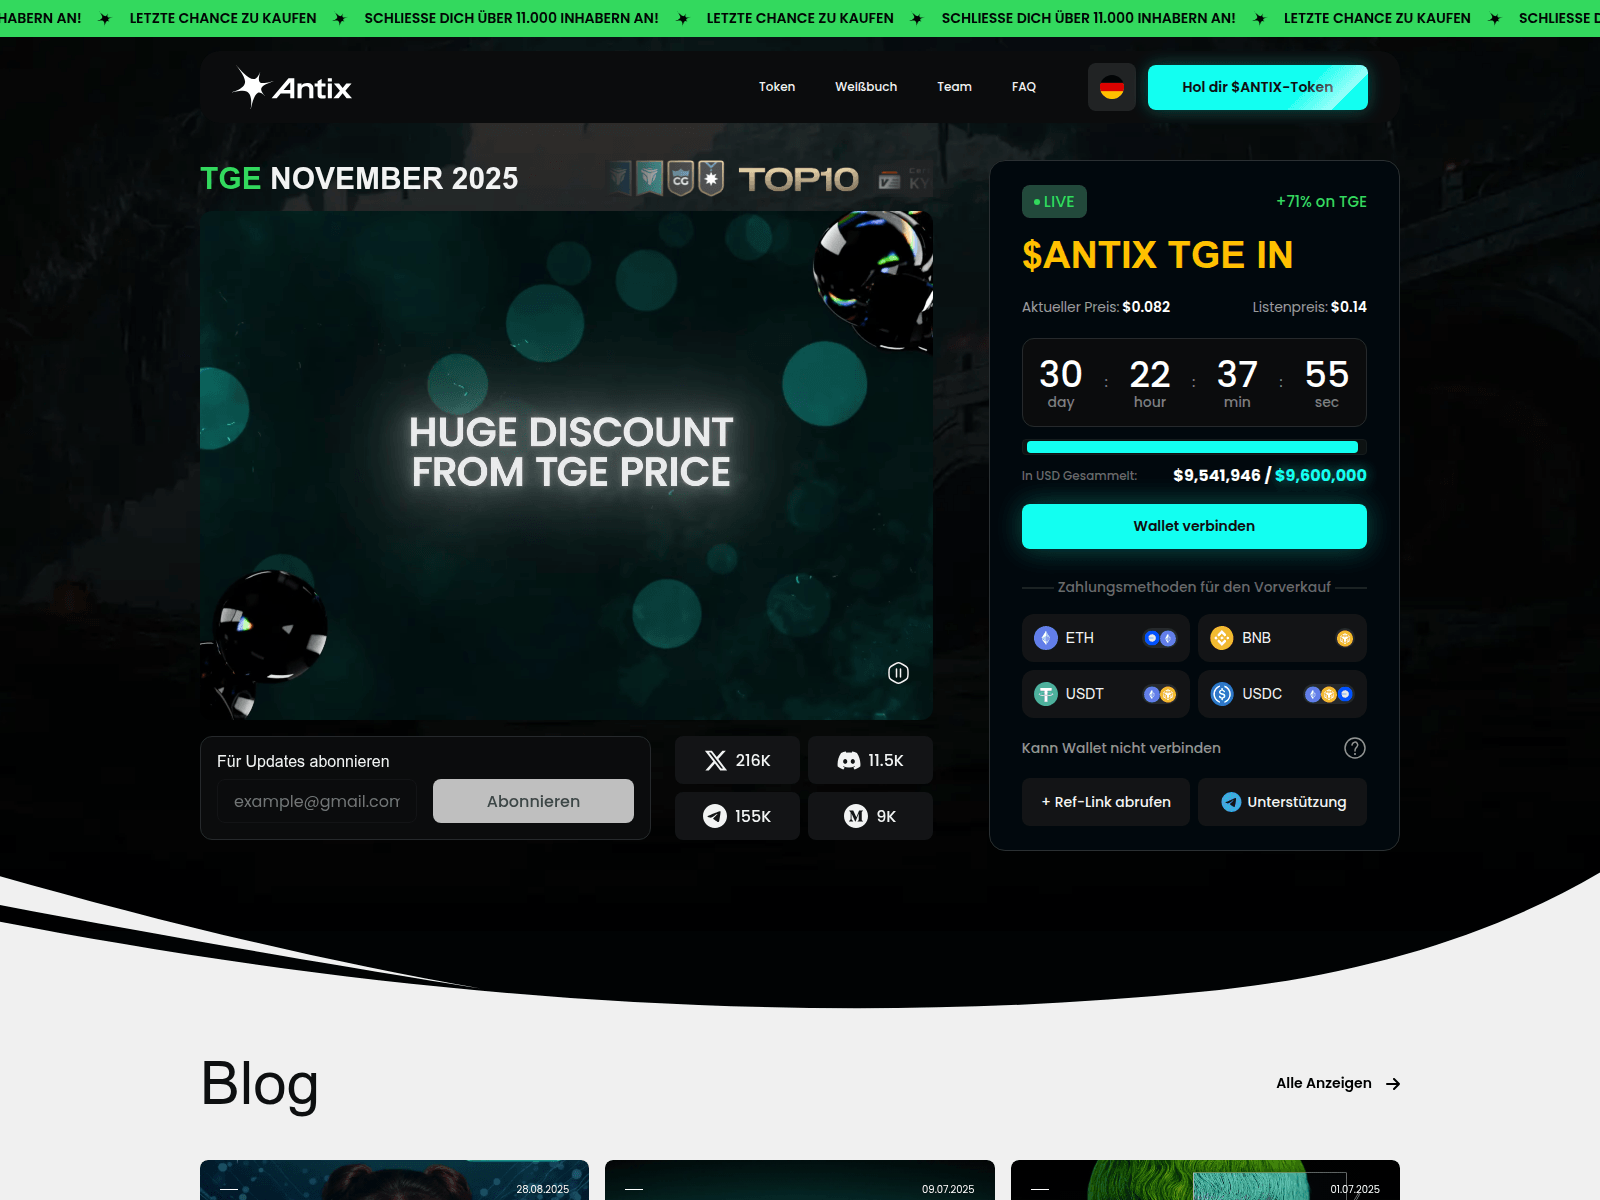
token.antix.in

trackfey.app

tria-vote.com
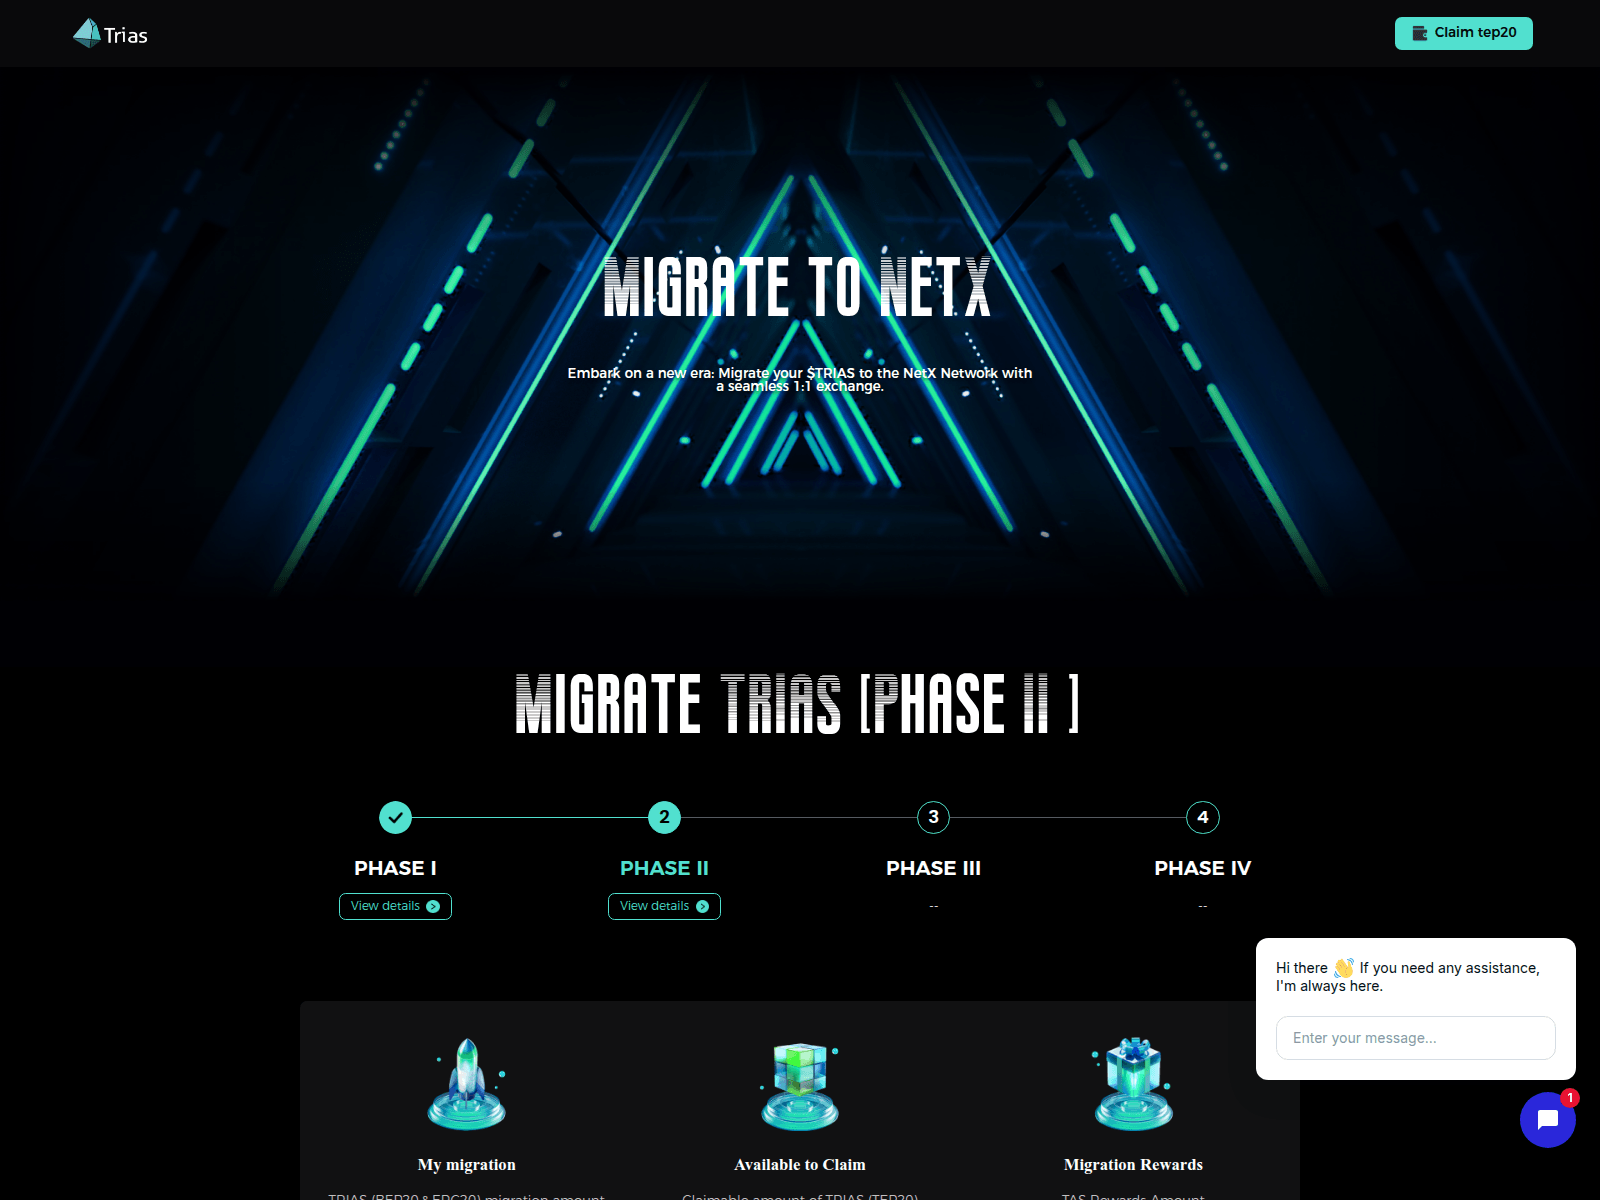
triasnetx-phase2.com

trumpxsol.com

tydro-vote.com
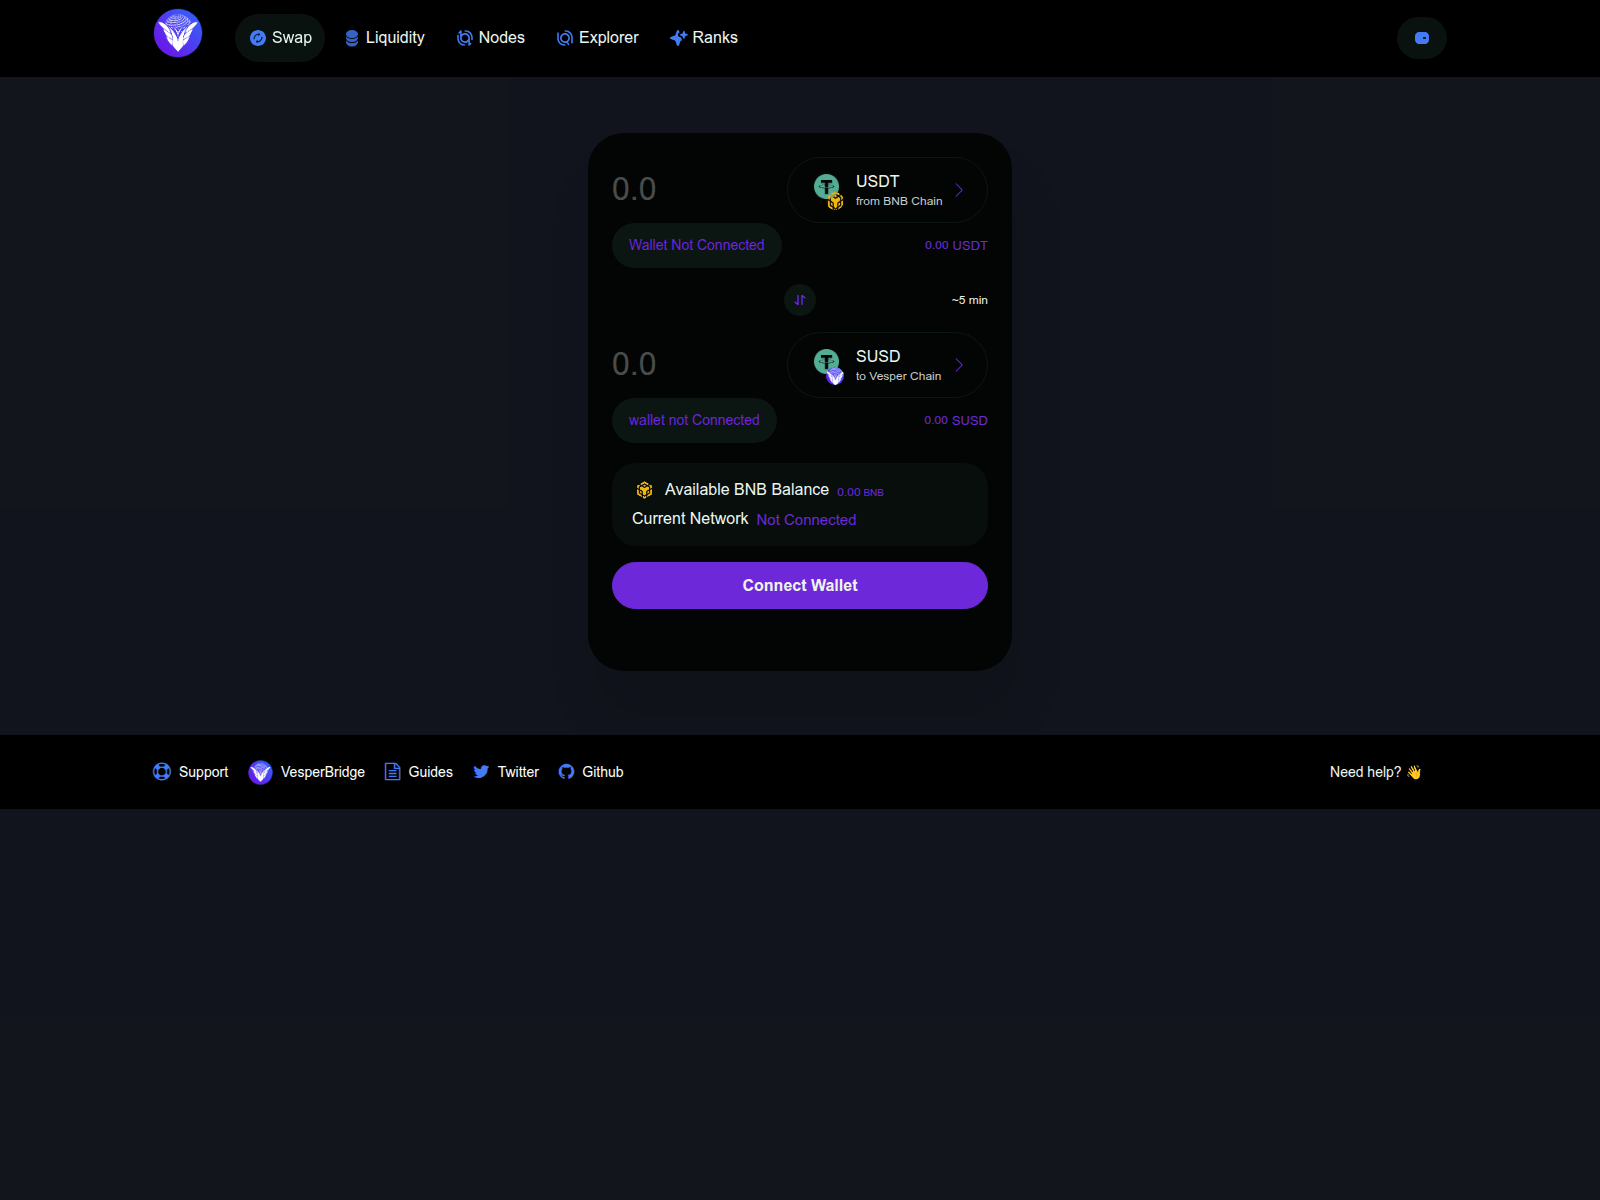
vesperbridge.com
virtual.votings.workers.dev

vote-hyprstr.com

vote-perlelabs.com
Threat Response Pipeline
How every domain in this hub is verified and how confirmed threats are neutralized. Full pipeline visualization →
Threat Intelligence Checks— every domain is scanned & cross-checked against:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ReportCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Security FiltersQuad9 · AdGuard · CleanBrowsingWeb-CheckFull surface scan
 crt.sh
Global Vendor Sync— confirmed detections are pushed to 29 partners:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftTakedown APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ReportHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust