
Search tracked domains and review stored evidence, detections, and the latest observed availability.
219,828
Total Tracked
213,490
VT Detected
91,921
Last Seen Active
127,907
Unavailable at Last Check
576
VT Pending
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domains
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains
lxlwyn.top

manyushiba.xyz
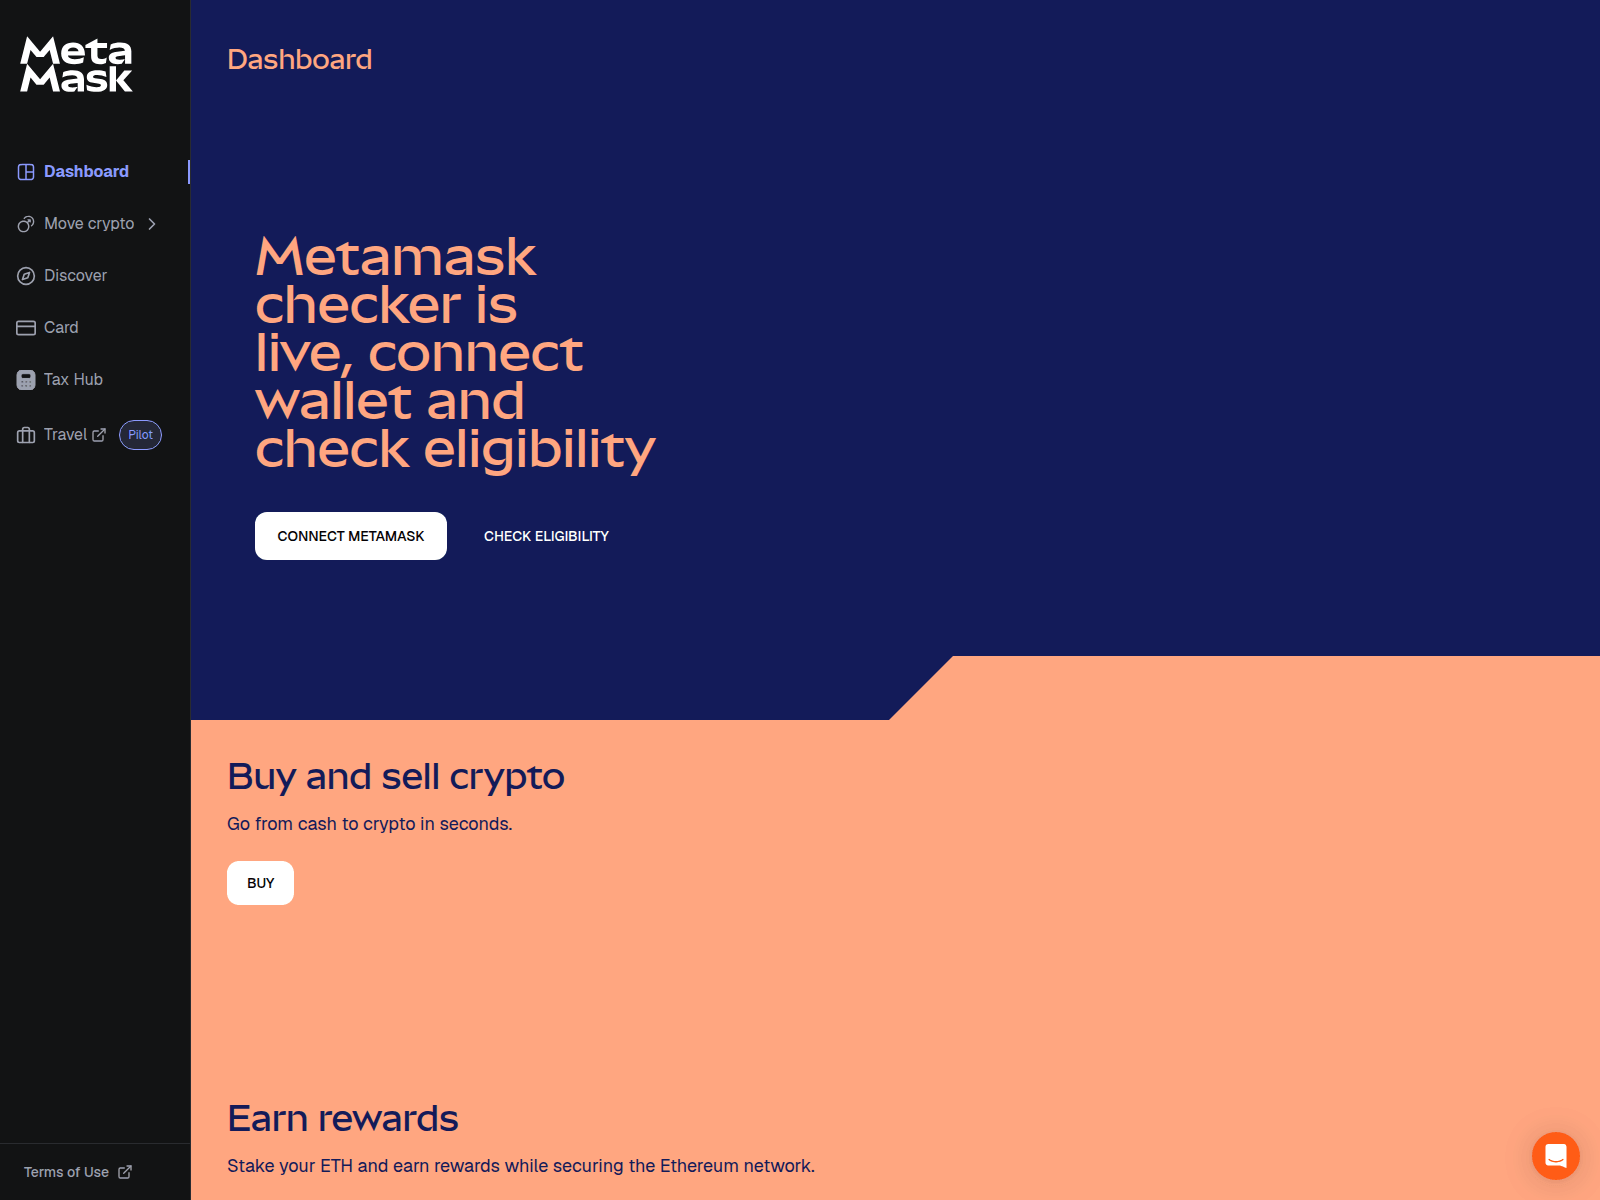
mask-eligibility.app

memepartyoneth.xyz

meteoralp.help
migrate-yield.com

migrate-yieldbasic.com

monovex.com

moon015.szcca.net

moon048.94tp.com

mysterybox.gam3s.claims
nlrwvf.pages.dev

o4xfd-oiaaa-aaaaj-qnsaa-cai.icp0.io

oidc.login.xyz

okxclaim.web.app

online232.com
onyx-token.com

orcamind.ai

originndefi.org

origndefi.org
pad-chain-gpt.org

panther-guard.web.app

pape-drops.netlify.app

paybytelegram.com

paytrustwallet.org

pck-wallet-v1.app

peipeicoins-ai.firebaseapp.com

pepeclaim2.net
perfectwalletconnect.com

phase3-stable.com

polbot55.vip
pro-app.pro

pth997.com


punksauction-votes.com

quickswap-exchange-dapp.com
quickswap.orbs-tt.com
reavers-booty.web.app

registration-neutrlfi-com.pages.dev

remotecontrol.props.app

revoke-veloedrome.com

revoking-aereodrome.com

rewards-mio.com

rewards-shibainu.votings.workers.dev

rewards-soracles.com

scanneraml.com

signup-pepes.com

signup-sends.info
signup-stable.com

snortertoken.com
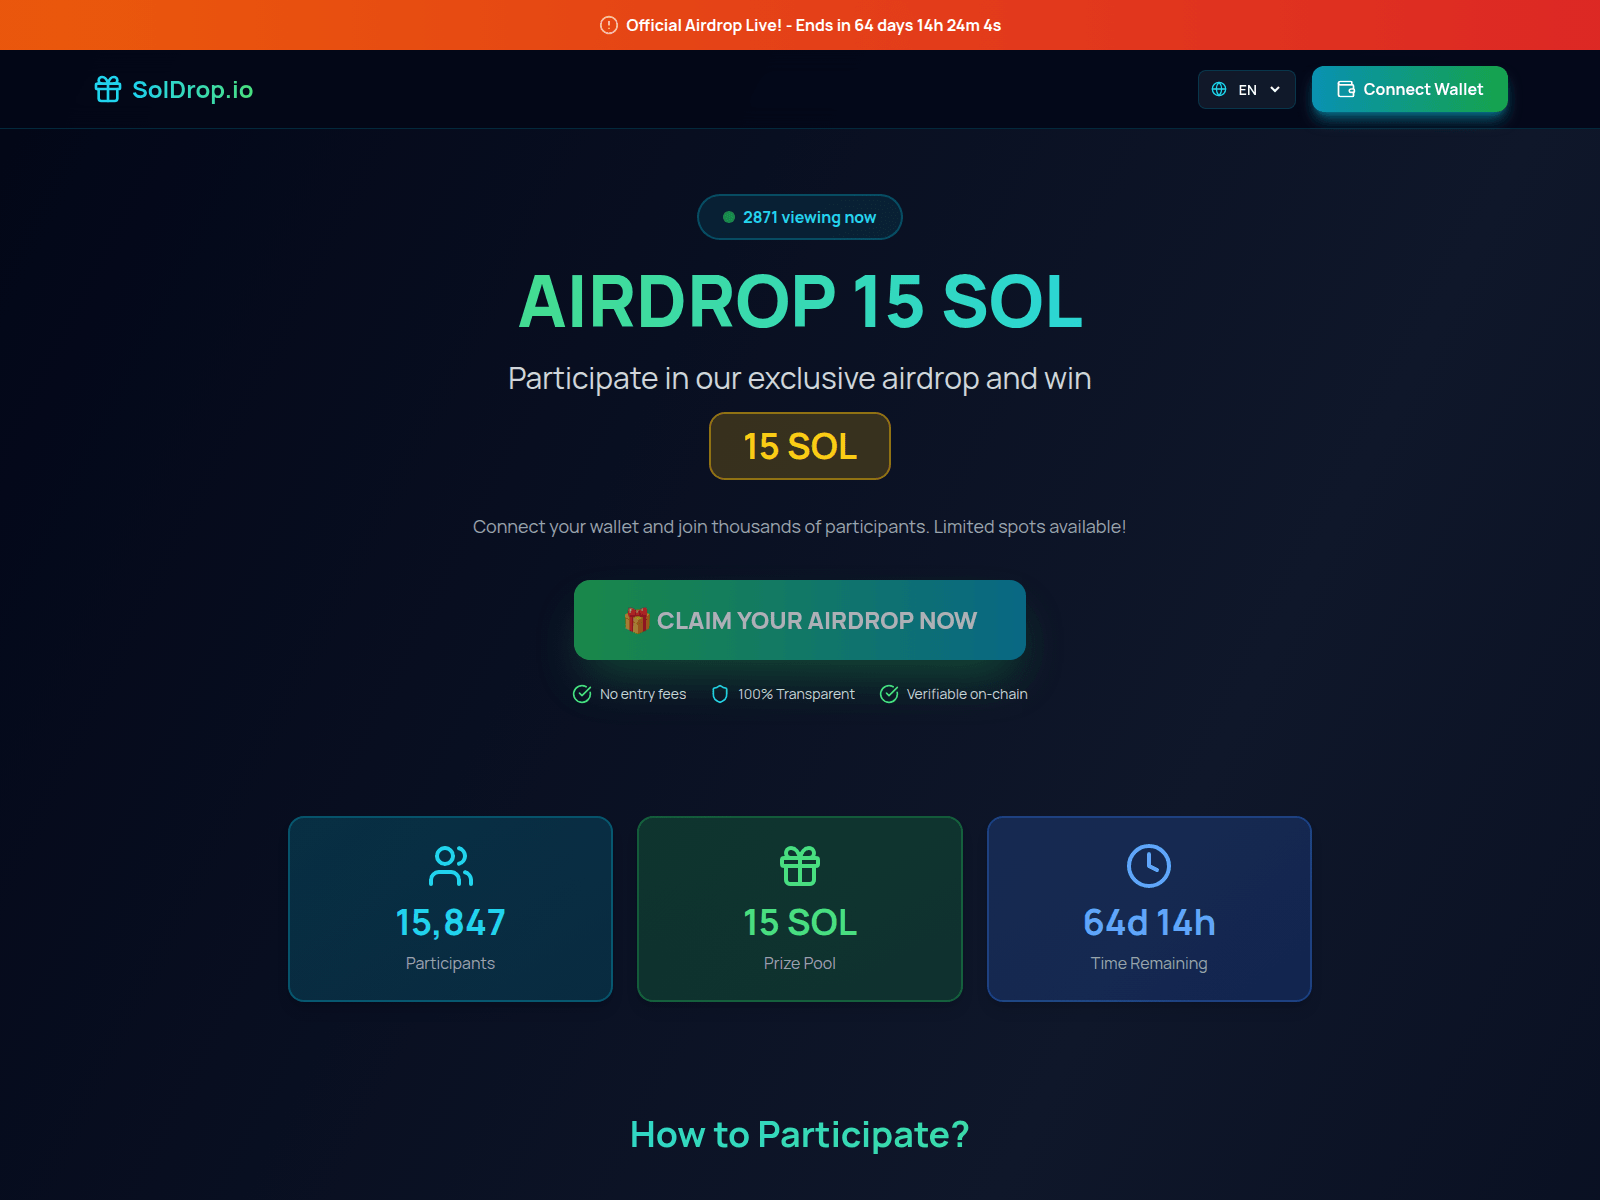
solairdrop.io
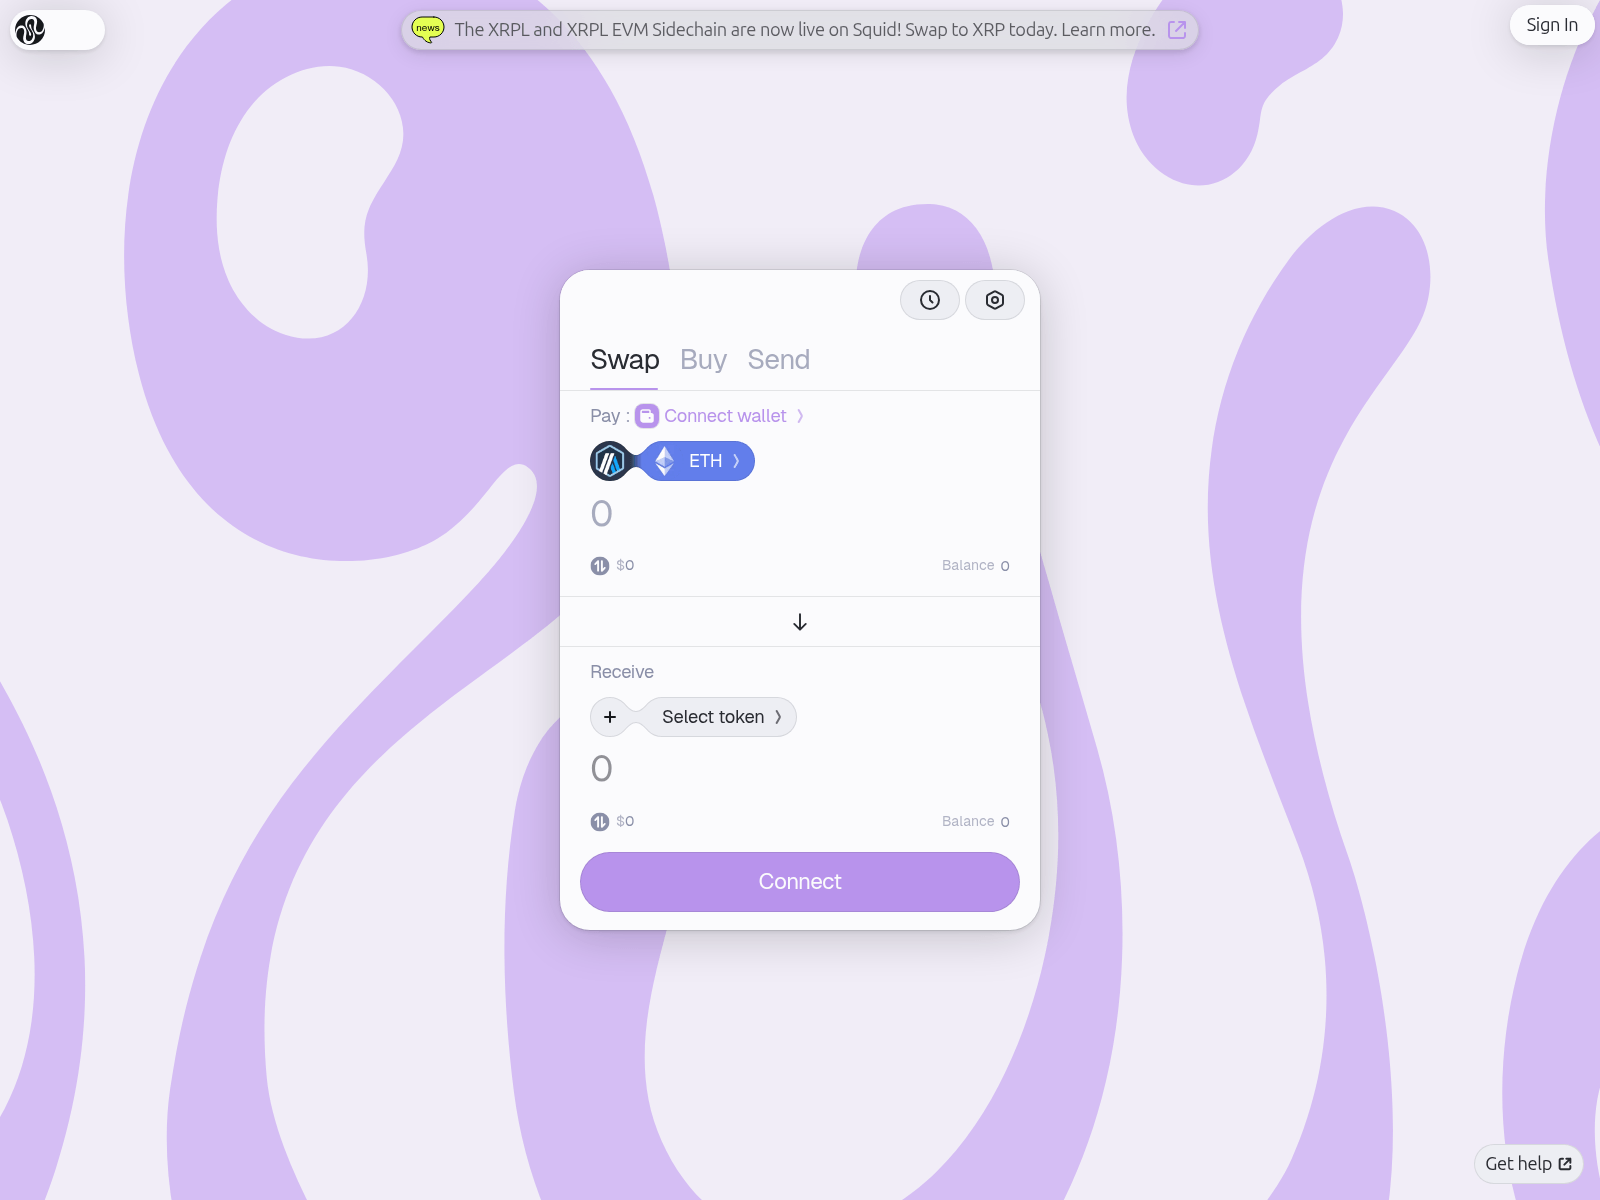
squid-bridge.com

stake.vianxy.online

standx.group

starcheck.help

tapcoin.app
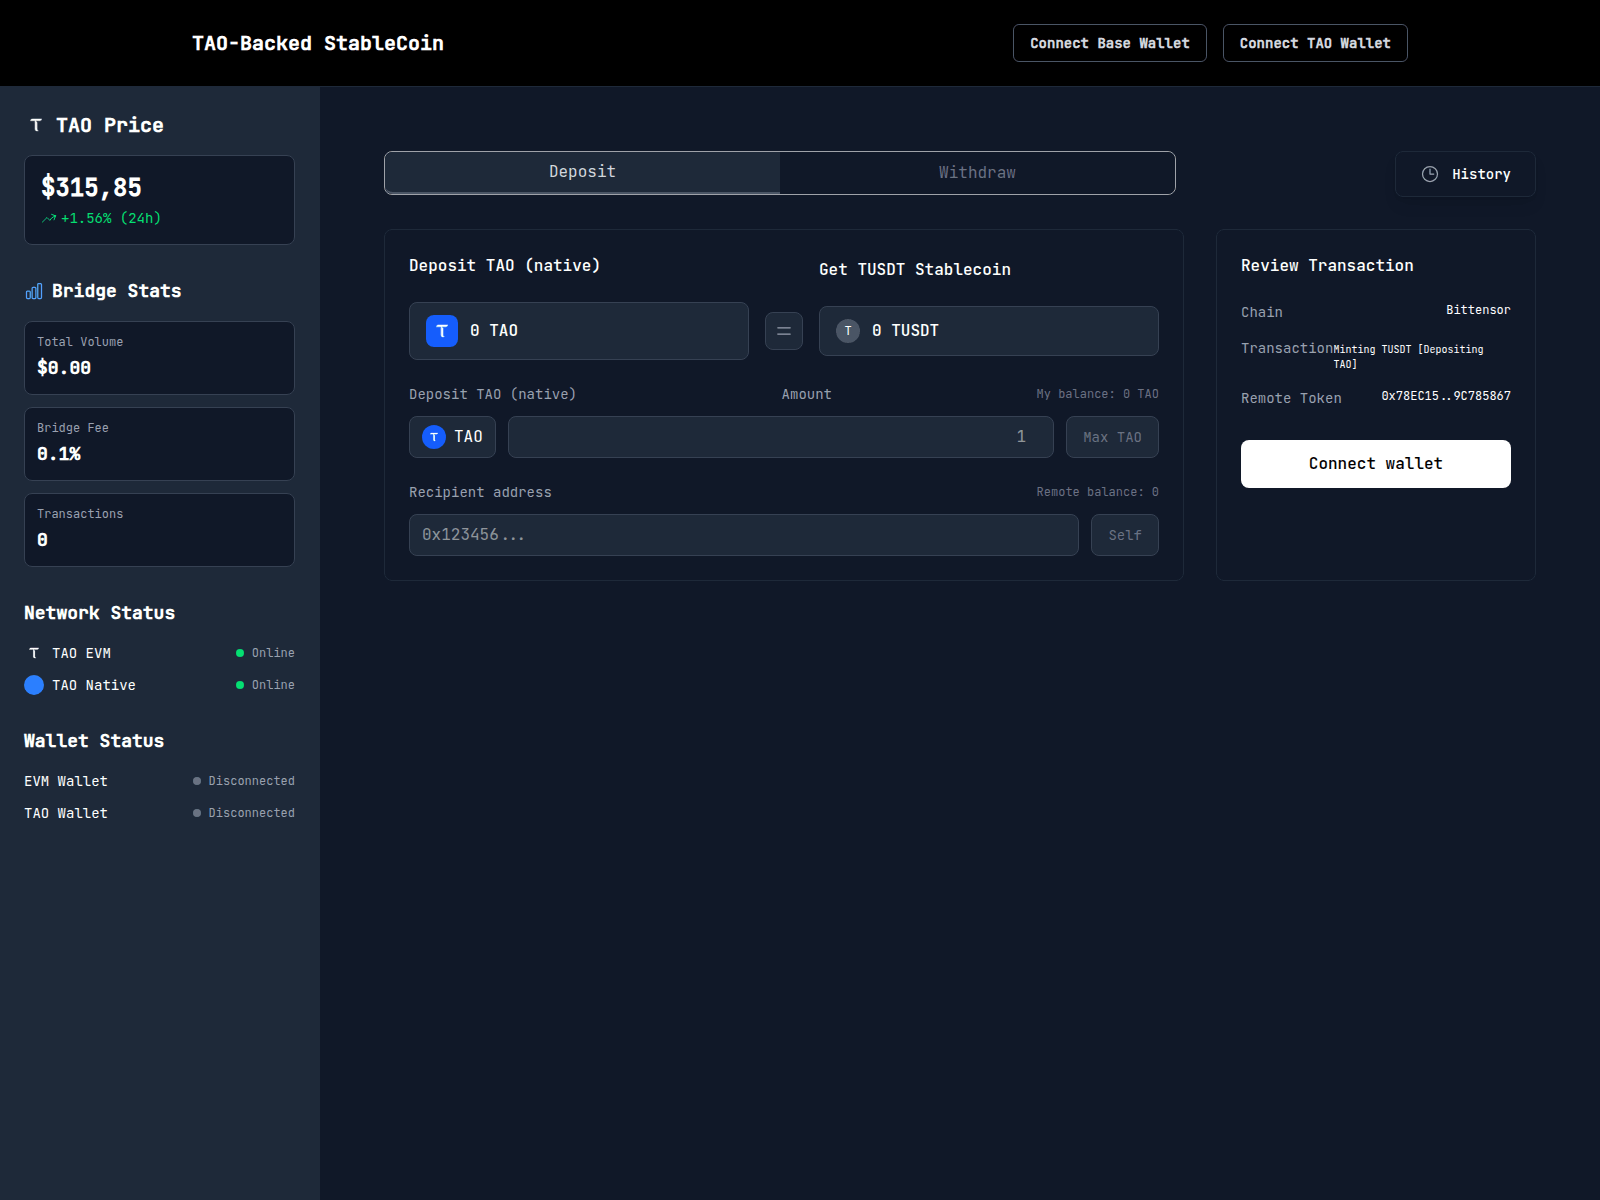
tensorusd.com

trendsfun-git-feature-jupiter-swap-takoprotocol.vercel.app

trust-whitebridge.live

trustwallet-miner.com

twt17.top
u53lc-iaaaa-aaaap-qbnea-cai.icp0.io

ultradex.live

unich-quest.com
uniswap.xmarslive.com

verifusdt.com

vote-gaibai.com

vote-manyushib.com

vote-tokensworks-com.pages.dev

vote-virtual.app

votes-onbeams.com

voting-redstones.com

voting-virtual.app

walletconnectds.network
wallstreetchain.com

web.illuvium.icu
x2h3q-jaaaa-aaaan-qmwdq-cai.icp0.io
xlaunch-pad.firebaseapp.com
xwt.chardness.com
zeno-chain.com

aava.pages.dev

airdrop-boundless.site

airdrop-mmt.com
airdrop.ethena-early-access.claims

airdrop.firachain.com

airdrop.inflora.cloud
airdrop.riftswap.net

airdrop.sheetchain.com

airdrop.sonicsvn.com

airdropnesaratoken.com

almanak-tge.com
aml-tools.com

aml.ink
amlcheckers.org

amlookcheck.com

amlrating.tech

anichess-tge.com

animalfarm3app.com
Threat Response Pipeline
How every domain in this hub is verified and how confirmed threats are neutralized. Full pipeline visualization →
Threat Intelligence Checks— every domain is scanned & cross-checked against:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ReportCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Security FiltersQuad9 · AdGuard · CleanBrowsingWeb-CheckFull surface scan
 crt.sh
Global Vendor Sync— confirmed detections are pushed to 29 partners:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftTakedown APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ReportHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust