
Search tracked domains and review stored evidence, detections, and the latest observed availability.
219,828
Total Tracked
213,490
VT Detected
91,925
Last Seen Active
127,903
Unavailable at Last Check
576
VT Pending
How This Attack Works
Angel Drainer operates by luring victims into interacting with malicious websites that appear legitimate. The attack unfolds in a series of deceptive steps designed to steal cryptocurrency assets.
STEP 1
Baiting with Fake Offers
Attackers create phishing sites mimicking trusted platforms like NFT marketplaces or DeFi protocols, often using domains like opensea.com.offer-proposal.com to appear authentic. Victims are enticed with fake airdrops, giveaways, or urgent account verification prompts.
STEP 2
Wallet Connection Request
Once on the site, users are prompted to connect their crypto wallets (e.g., MetaMask) to 'claim' rewards or 'verify' their accounts. This step often bypasses user suspicion by mimicking standard Web3 interactions.
STEP 3
Malicious Smart Contract Execution
Upon connection, the site triggers a malicious smart contract that requests sweeping permissions, allowing attackers to drain funds or NFTs from the wallet. Victims often don’t realize they’ve approved a transaction that compromises their assets.
STEP 4
Asset Drainage and Laundering
Stolen funds are quickly transferred to attacker-controlled wallets and laundered through mixers like Tornado Cash or cross-chain bridges, making recovery nearly impossible.
Technical Analysis
Angel Drainer is a sophisticated phishing-as-a-service (PhaaS) toolkit that emerged in late 2022, primarily targeting cryptocurrency users. It leverages malicious JavaScript embedded in phishing websites to interact with victims’ wallets. The core mechanism involves tricking users into signing transactions that call functions like 'approve()' or 'transferFrom()' on ERC-20 tokens or NFTs, granting attackers full control over assets. These scripts are often obfuscated to evade detection by antivirus software or browser security extensions. Infrastructure-wise, attackers rely on cheap or compromised domain registrars—PhishDestroy data shows NICENIC INTERNATIONAL GROUP CO., LIMITED (1,173 domains) and Cloudflare, Inc. (434 domains) as top choices for hosting these threats. Common TLDs include .com (1,212 domains), .xyz (712), and .app (290), often paired with free hosting on platforms like Vercel, as seen in examples like mysteryclaims6345-live.vercel.app.
The toolkit also employs advanced evasion techniques, such as IP-based redirects to show benign content to bots or security researchers while serving malicious payloads to real users. Angel Drainer campaigns frequently clone legitimate Web3 interfaces, using typosquatting or subdomain tricks (e.g., opensea.com.offer-proposal.com) to deceive users. On the blockchain side, stolen assets are often routed through intermediary wallets before being mixed, with on-chain analysis revealing connections to known money laundering services. This combination of social engineering and technical exploitation makes Angel Drainer a persistent and evolving threat in the Web3 ecosystem.
Additionally, attackers customize their campaigns based on trending topics in the crypto space, such as new token launches or NFT drops, to maximize victim engagement. The use of decentralized hosting and domain privacy services further complicates takedown efforts, as seen with the 431 active domains still operational in PhishDestroy’s database. This infrastructure resilience, paired with the toolkit’s low barrier to entry for cybercriminals, underscores why Angel Drainer remains a critical risk.
Real Cases
ParaSpace NFT Exploit (2023)
$5 million stolen
In March 2023, attackers used Angel Drainer to target users of the ParaSpace NFT lending platform, tricking them into signing malicious transactions via a fake update prompt, resulting in $5 million in stolen assets.
Fake OpenSea Campaign (2023)
$1.7 million stolen
A widespread phishing campaign in late 2023 mimicked OpenSea’s interface, using domains similar to opensea.com.offer-proposal.com, draining $1.7 million in NFTs and tokens from unsuspecting users.
Blur Marketplace Scam (2024)
$2.3 million stolen
Early 2024 saw Angel Drainer used in a fake Blur marketplace airdrop scam, where users connected wallets to claim 'free tokens,' losing $2.3 million in assets to malicious smart contracts.
How to Detect
Unsolicited offers or urgent prompts for wallet connection on websites mimicking platforms like OpenSea or Vercel, often using domains tracked by PhishDestroy such as mysteryclaims6345-live.vercel.app.
Suspicious domain structures, especially subdomains or unusual TLDs like .xyz or .app, which account for a significant portion of the 4,385 domains in our database.
Transaction requests that ask for broad permissions or unlimited token approvals when connecting a wallet to a site.
Lack of HTTPS or mixed content warnings on supposed Web3 platforms, often a sign of hastily deployed phishing pages.
Unexpected wallet activity or pop-ups prompting signature approvals without clear explanations of the transaction purpose.
How to Protect Yourself
1
Always verify the URL of Web3 platforms before connecting your wallet—avoid clicking links from unsolicited emails or social media, as PhishDestroy has identified 4,385 Angel Drainer-related domains.
2
Use hardware wallets or wallet extensions with transaction simulation features to preview smart contract interactions before signing.
3
Enable two-factor authentication (2FA) and set spending limits on your crypto wallets to minimize potential losses.
4
Regularly monitor your wallet for unauthorized transactions using blockchain explorers and revoke permissions for unused dApps.
5
Leverage PhishDestroy’s threat database to check suspicious domains or report potential Angel Drainer phishing sites for community protection.
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 4,455 domains tracked for this threat type
Angel Drainer 4,455 domains
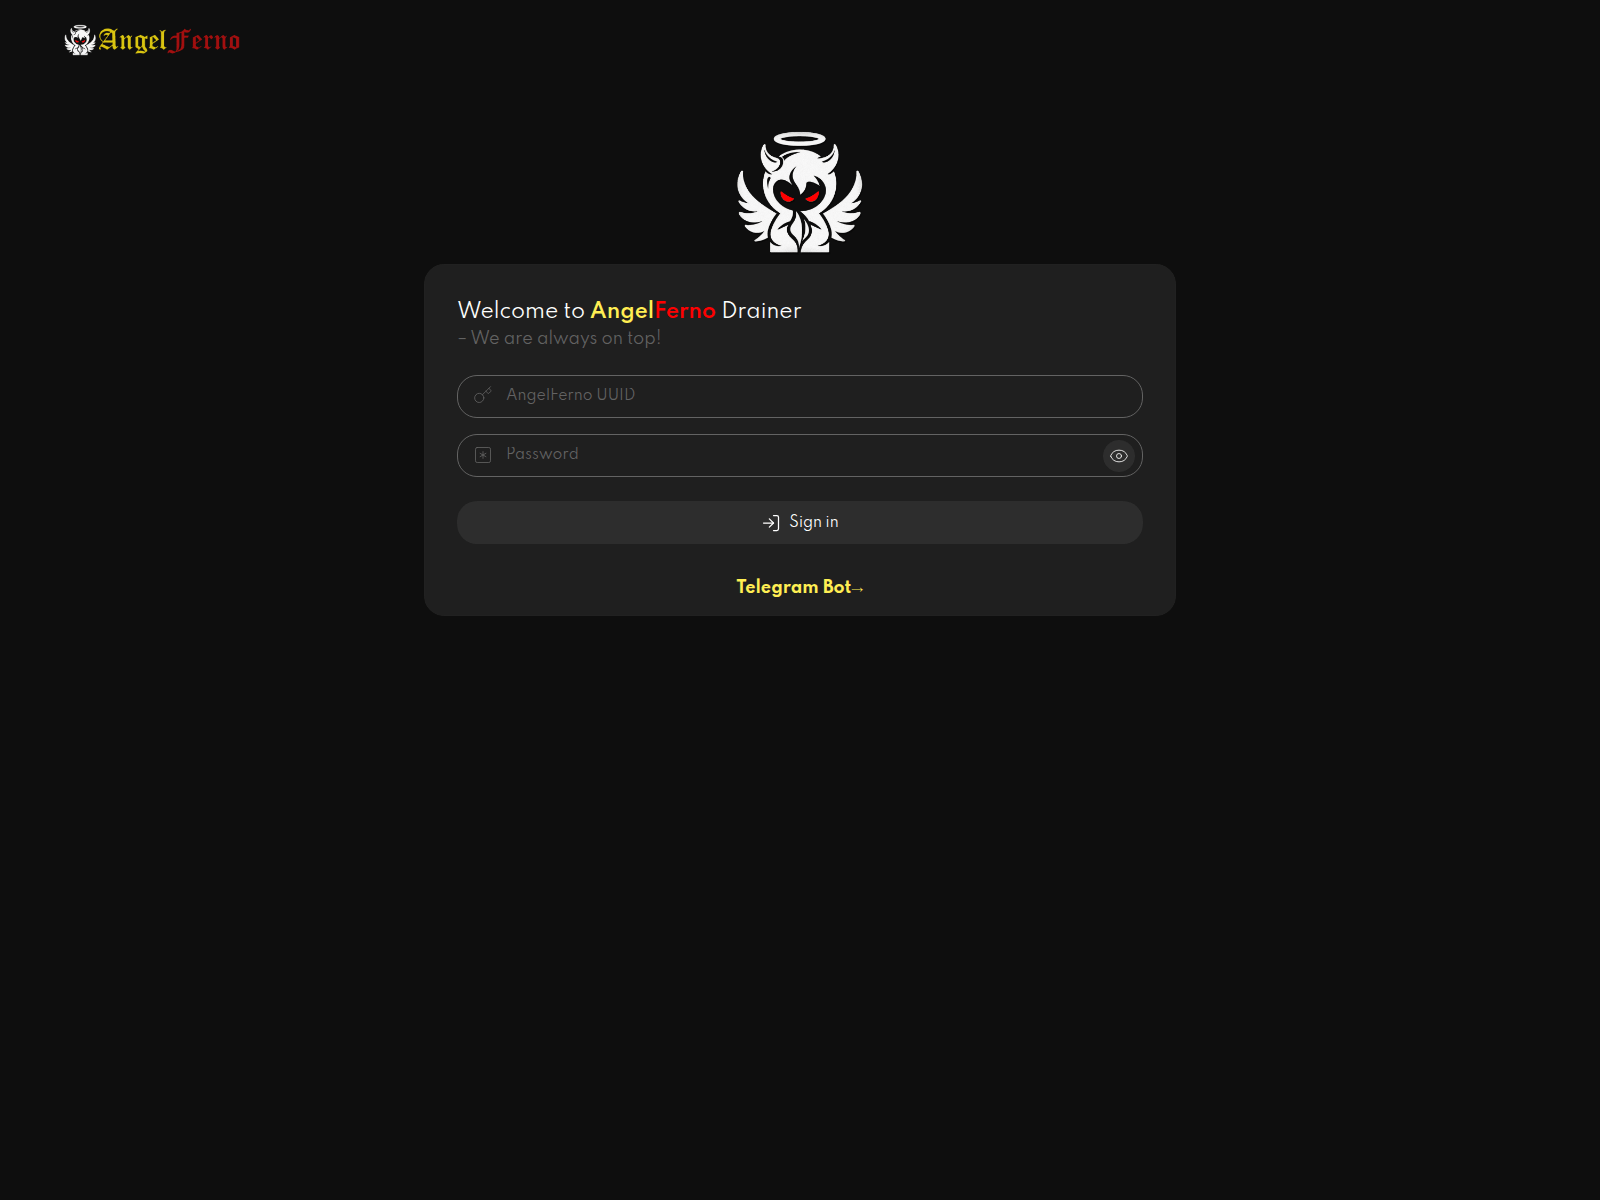

d2e0f982.angelfernotop.pages.dev

dashboard0x0.com

dexthrone.com

dfaifhnasid432bsfhsiofnb.com
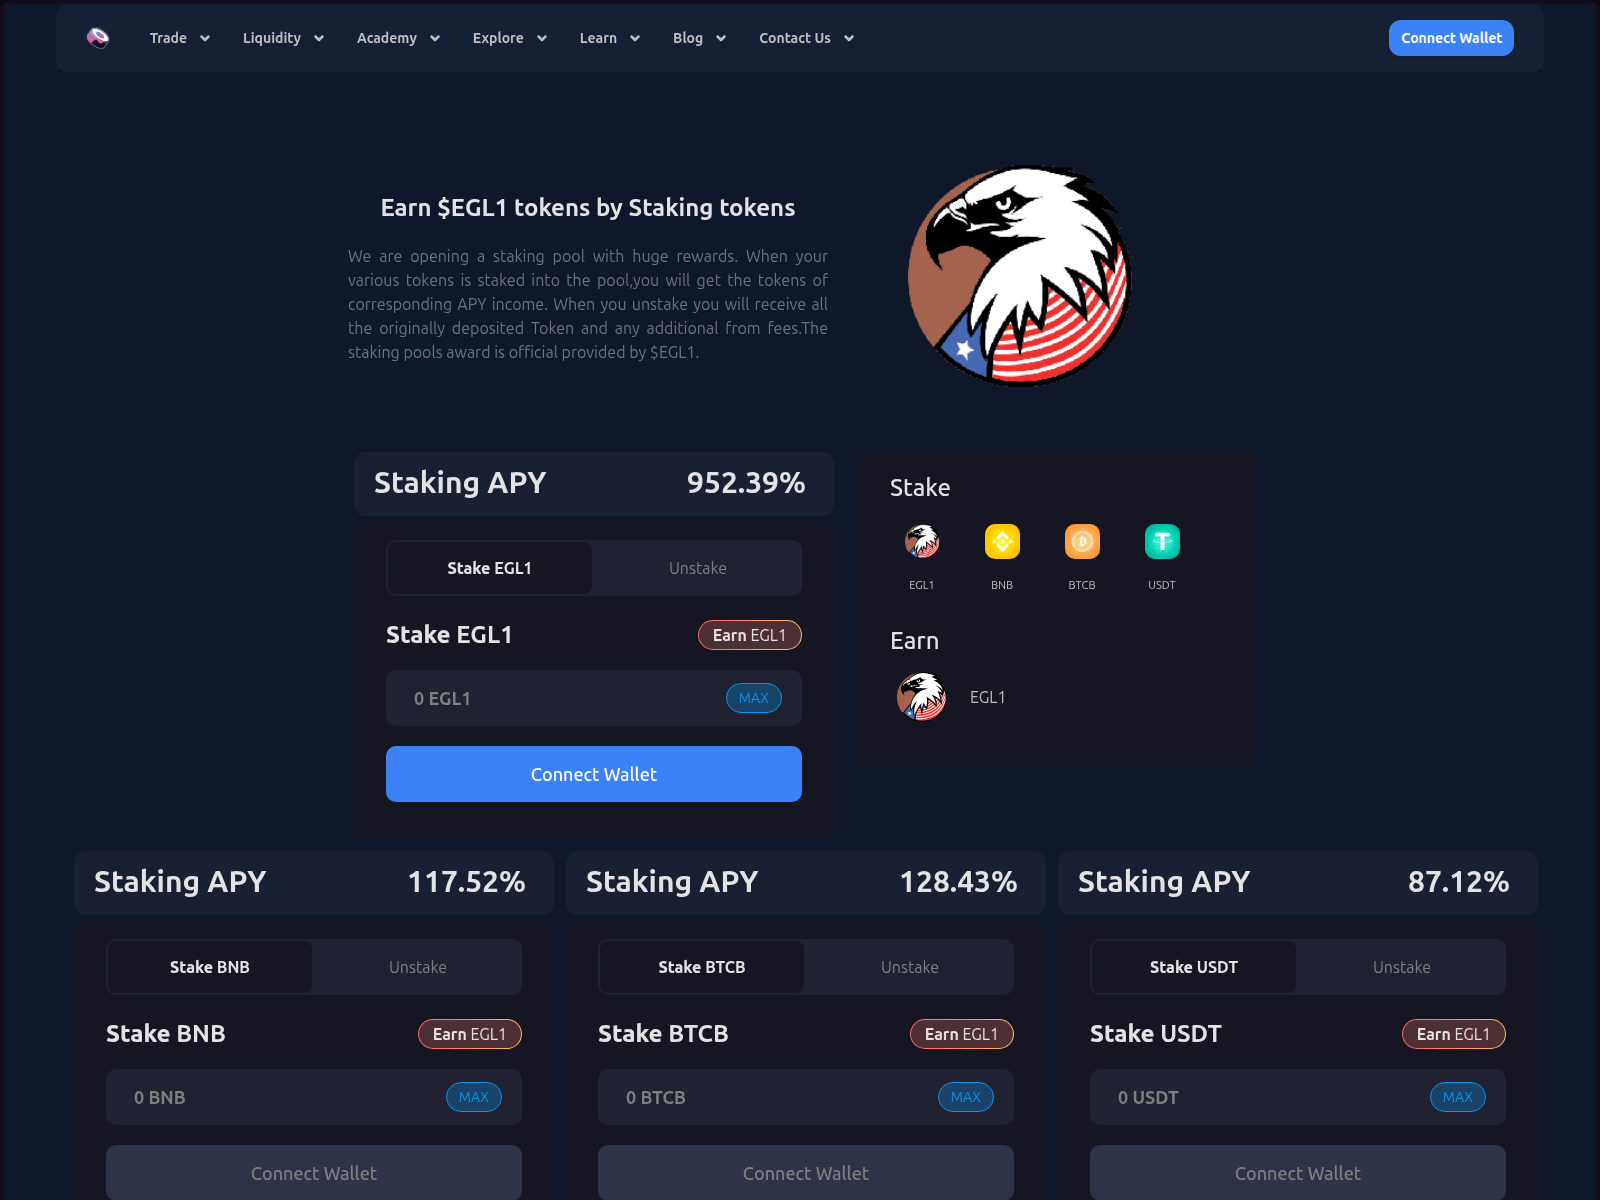
egl1.sushi.us.com
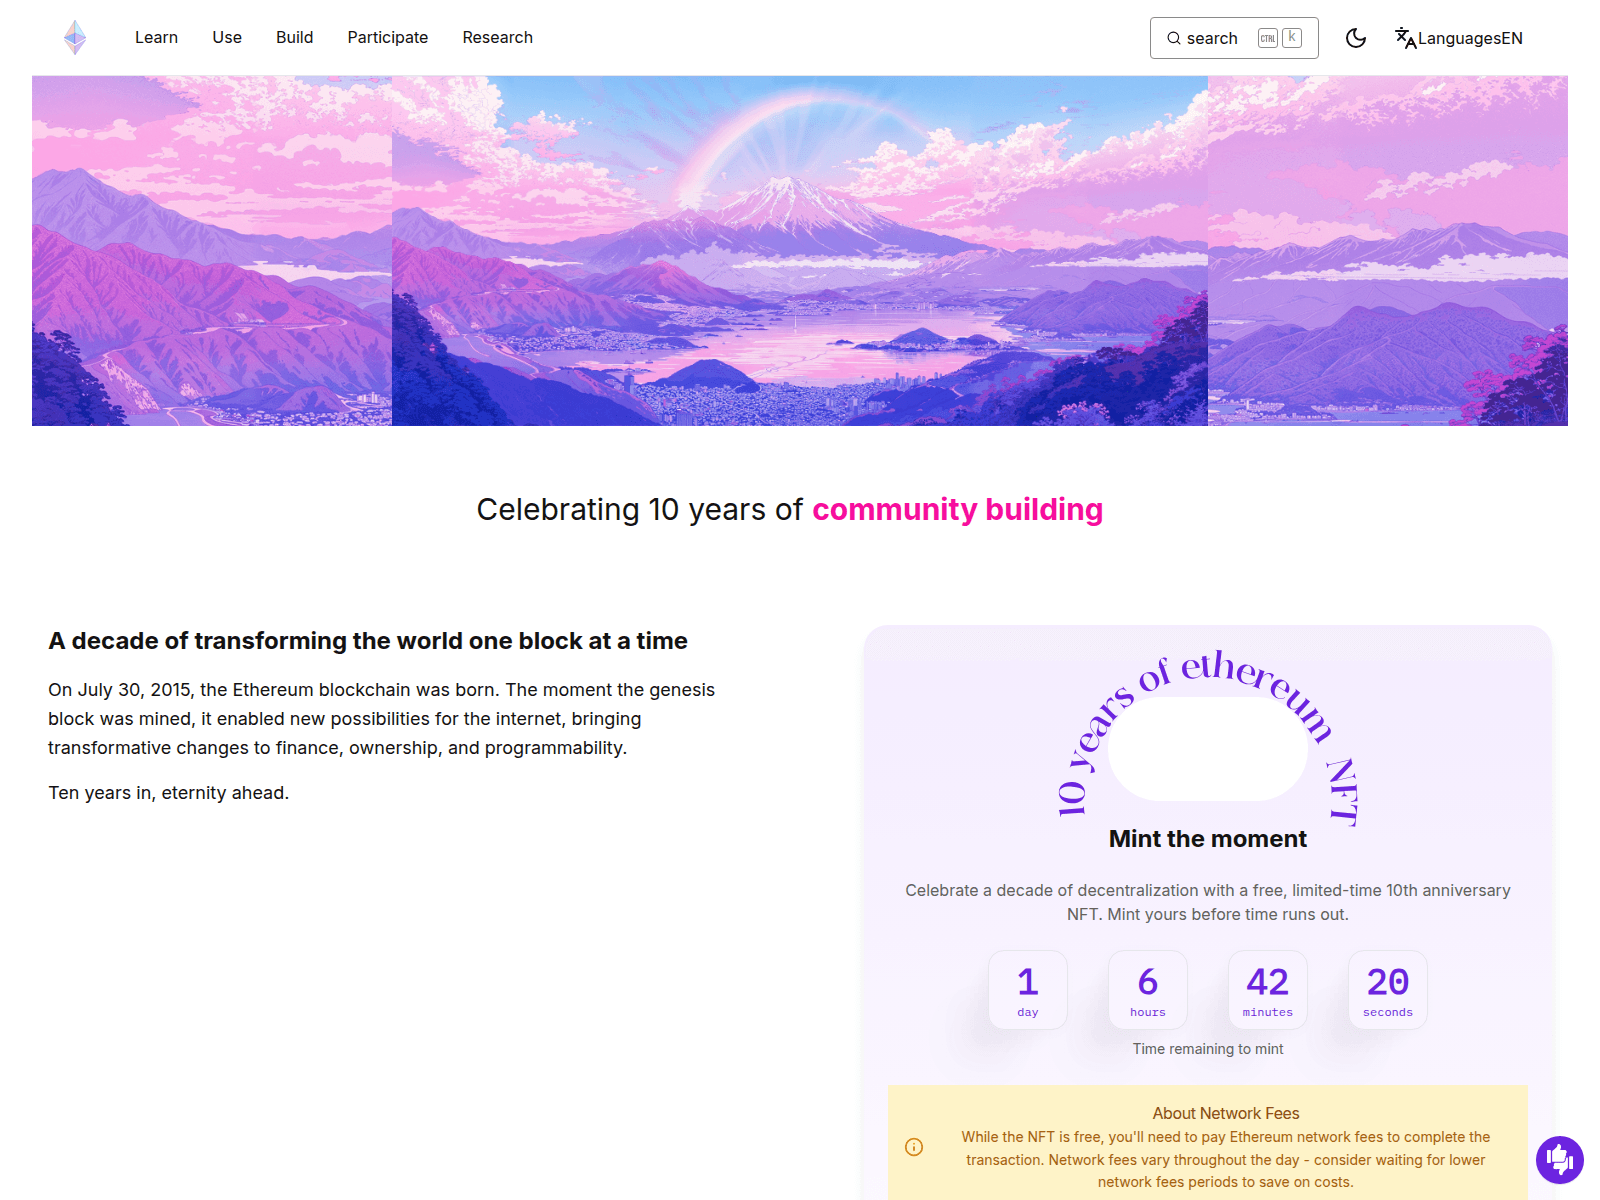
ethereums.life
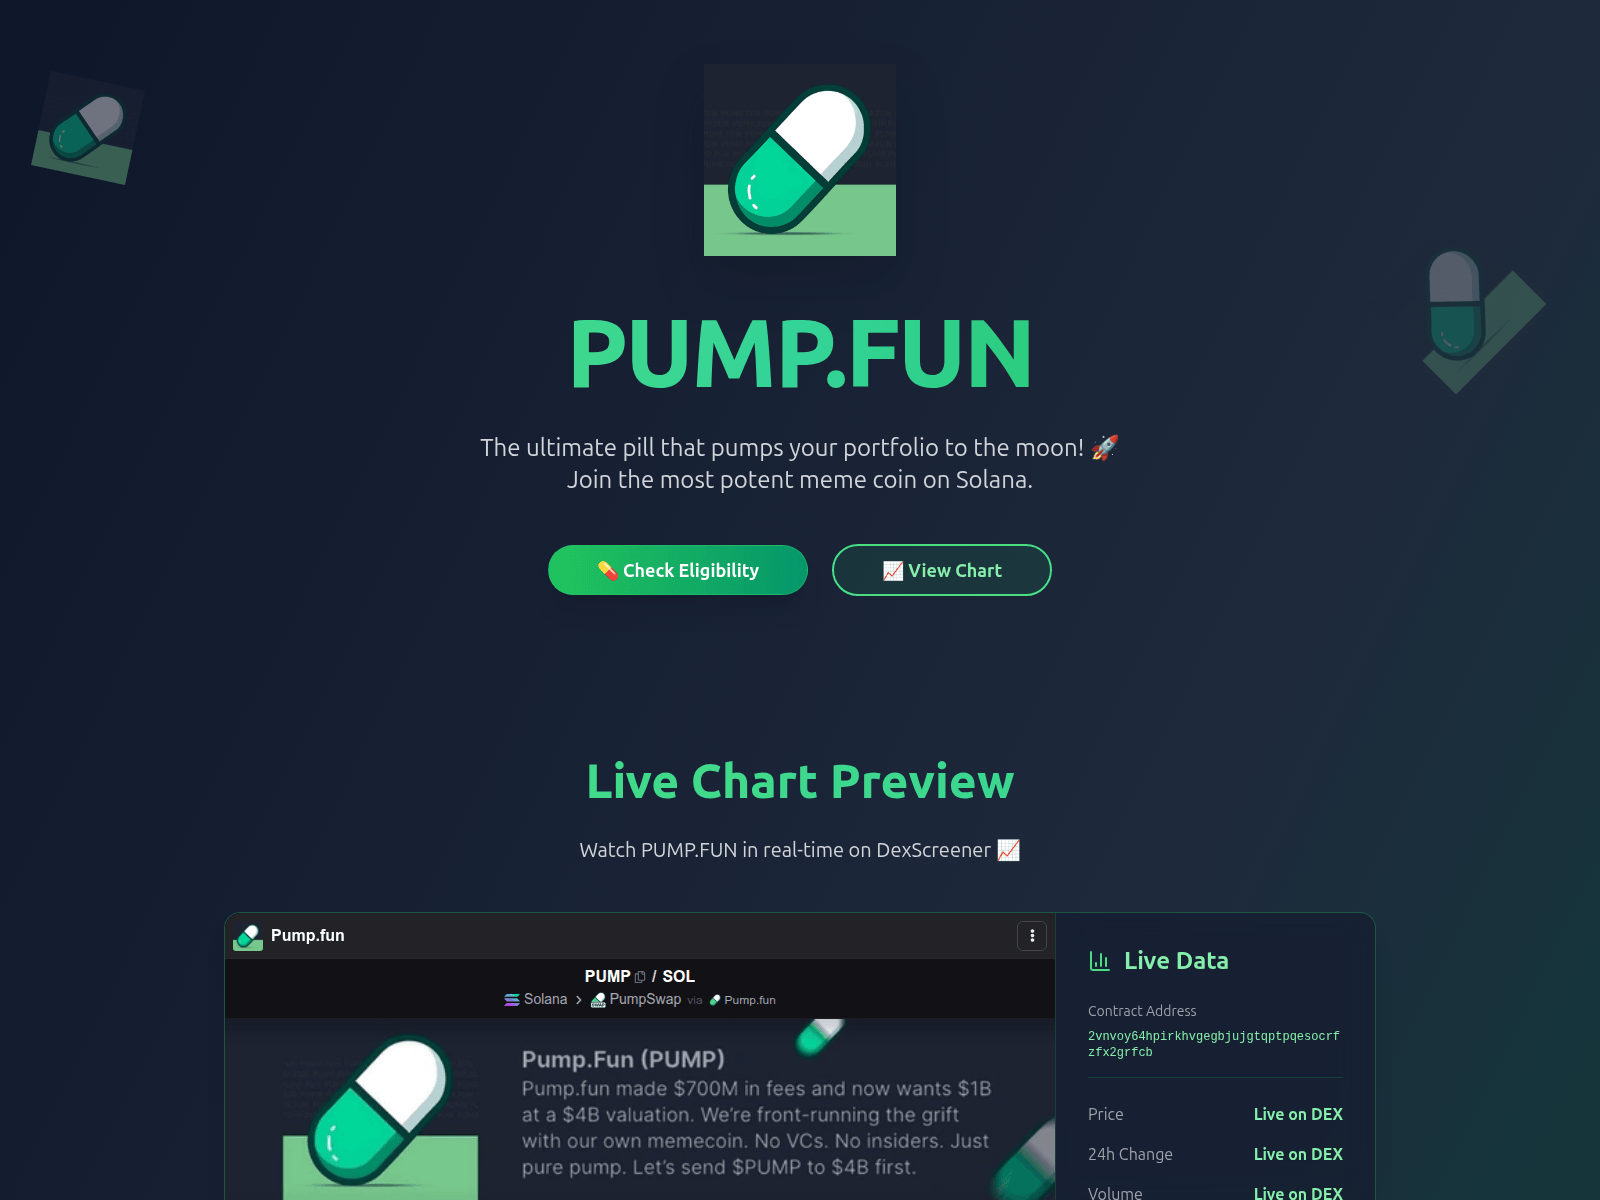
expression.bet
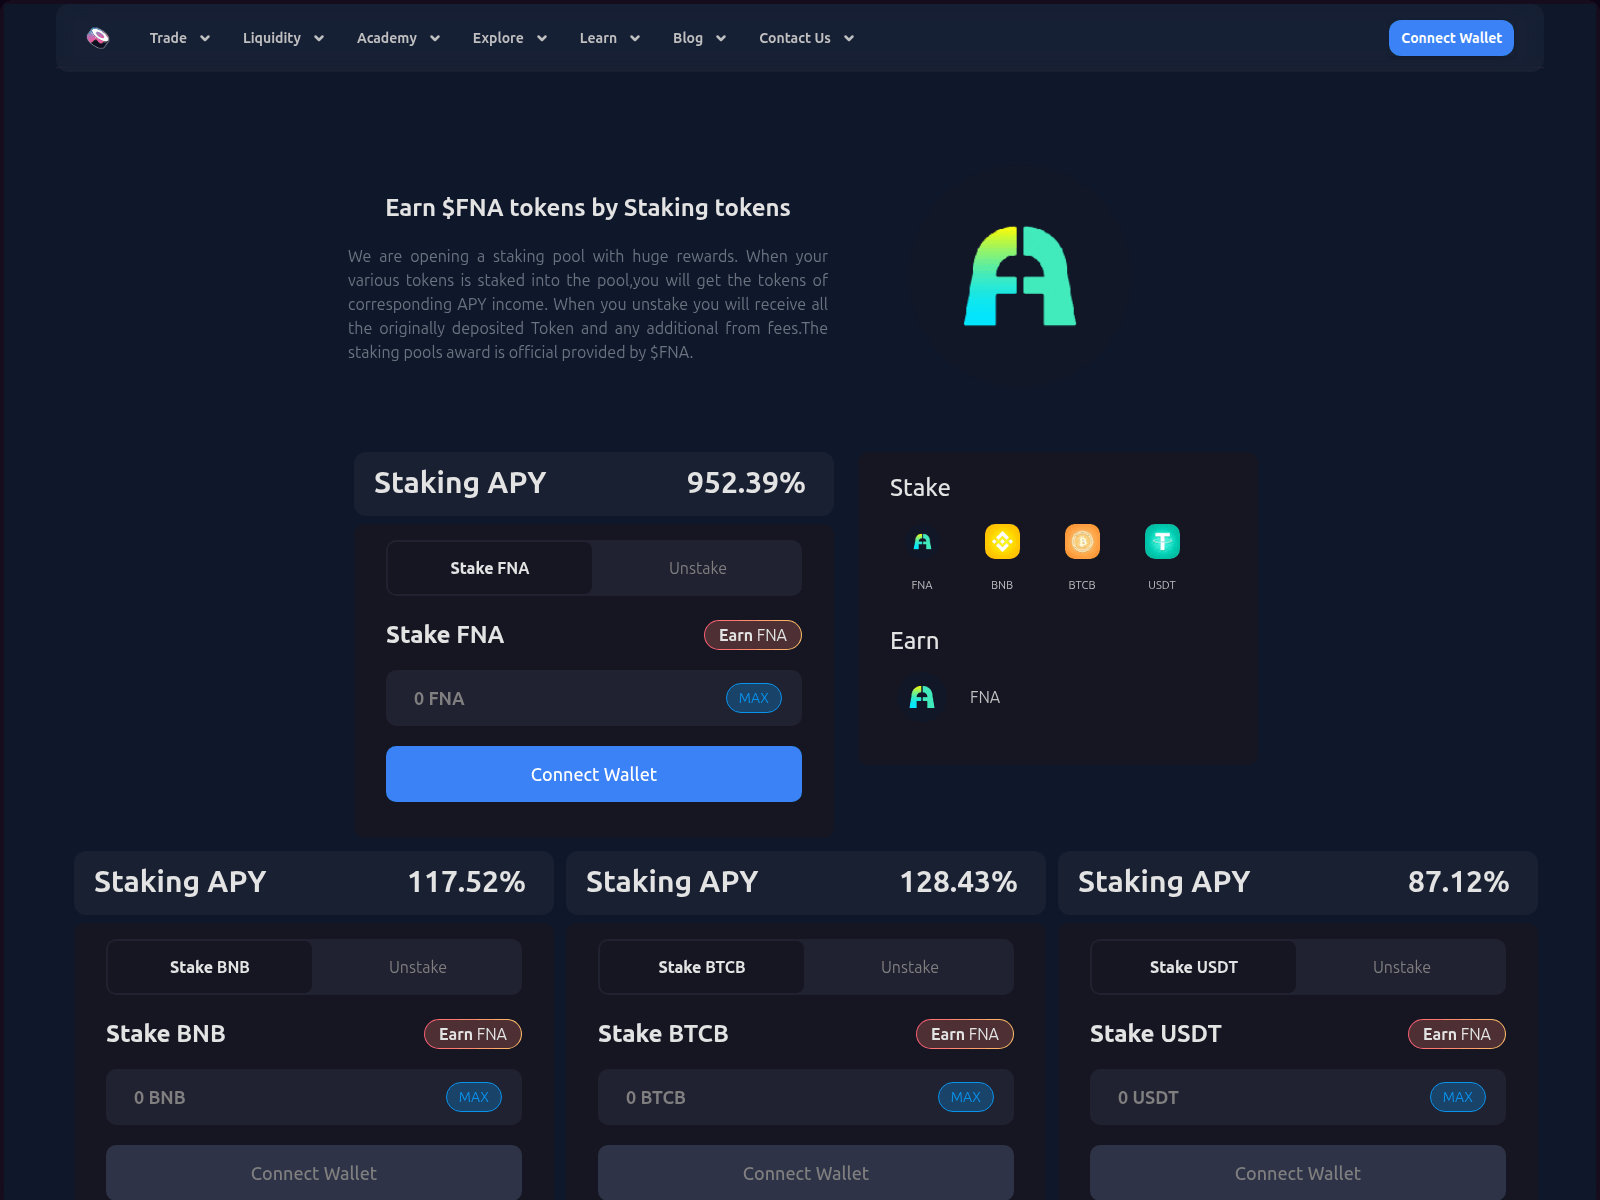
fintech.sushiswap.info
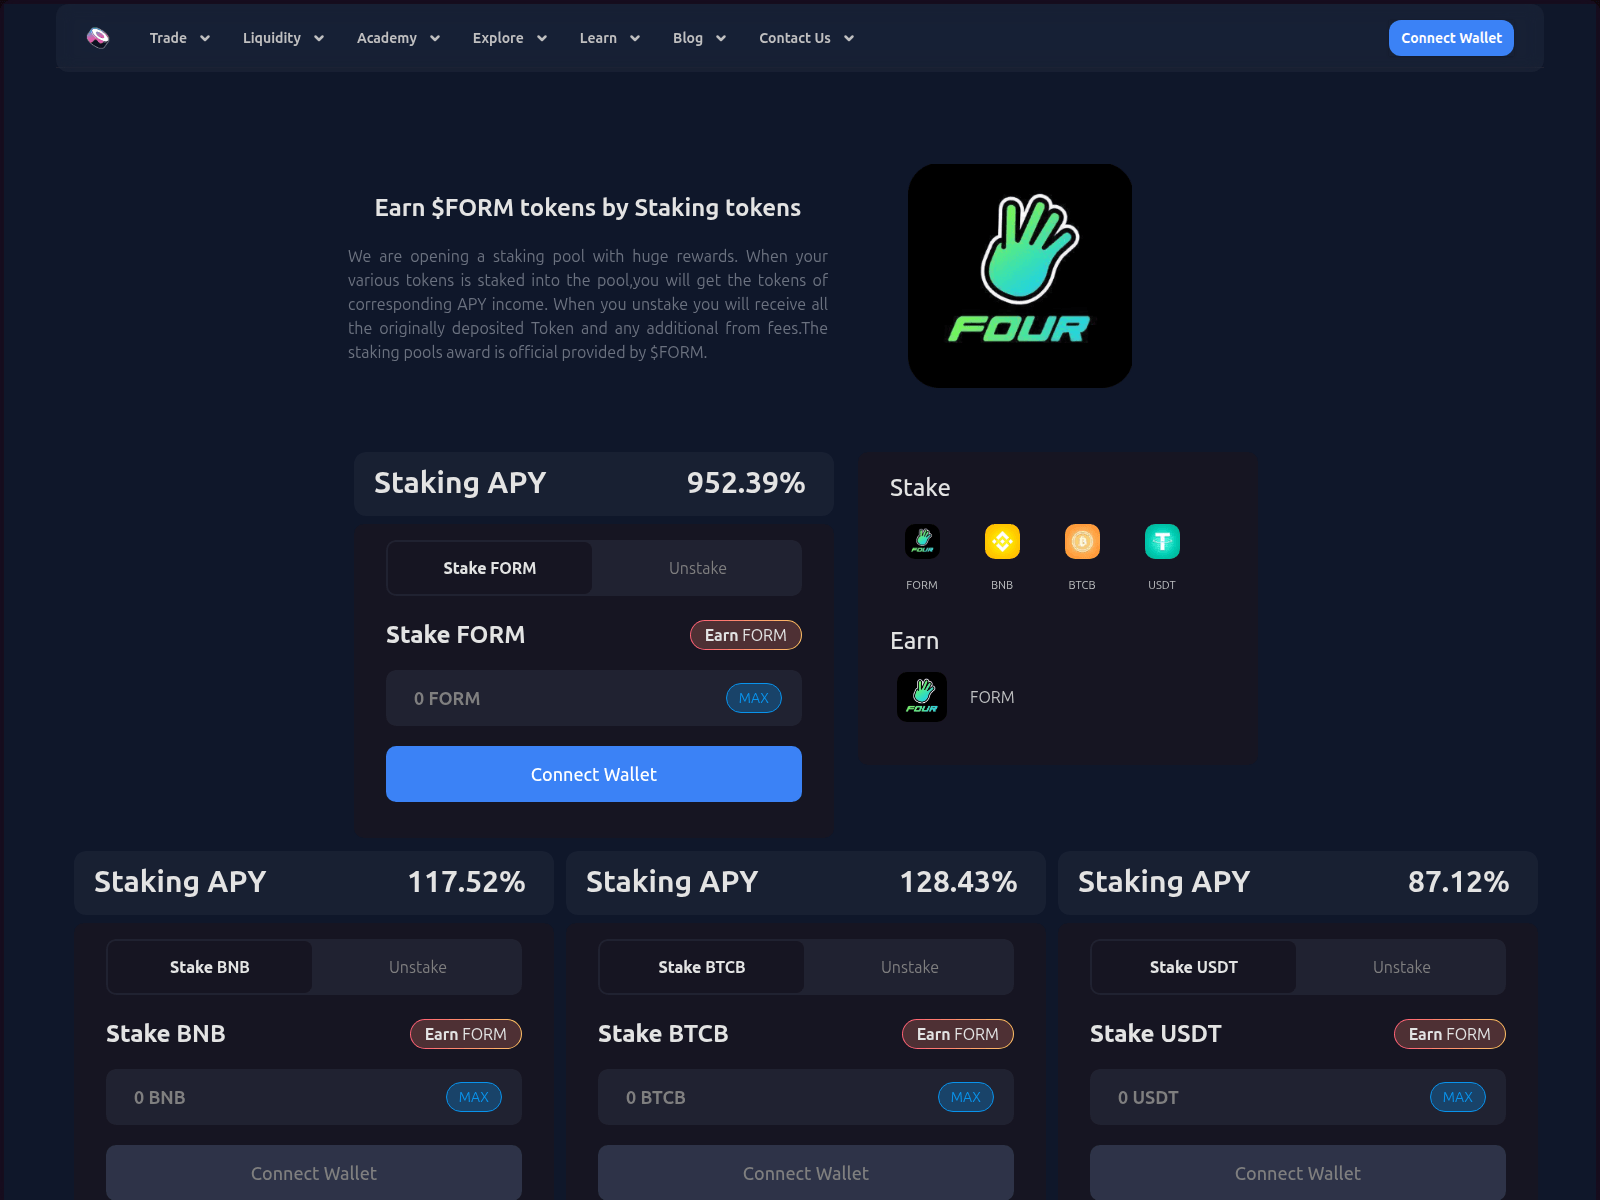
form.sushis.ninja
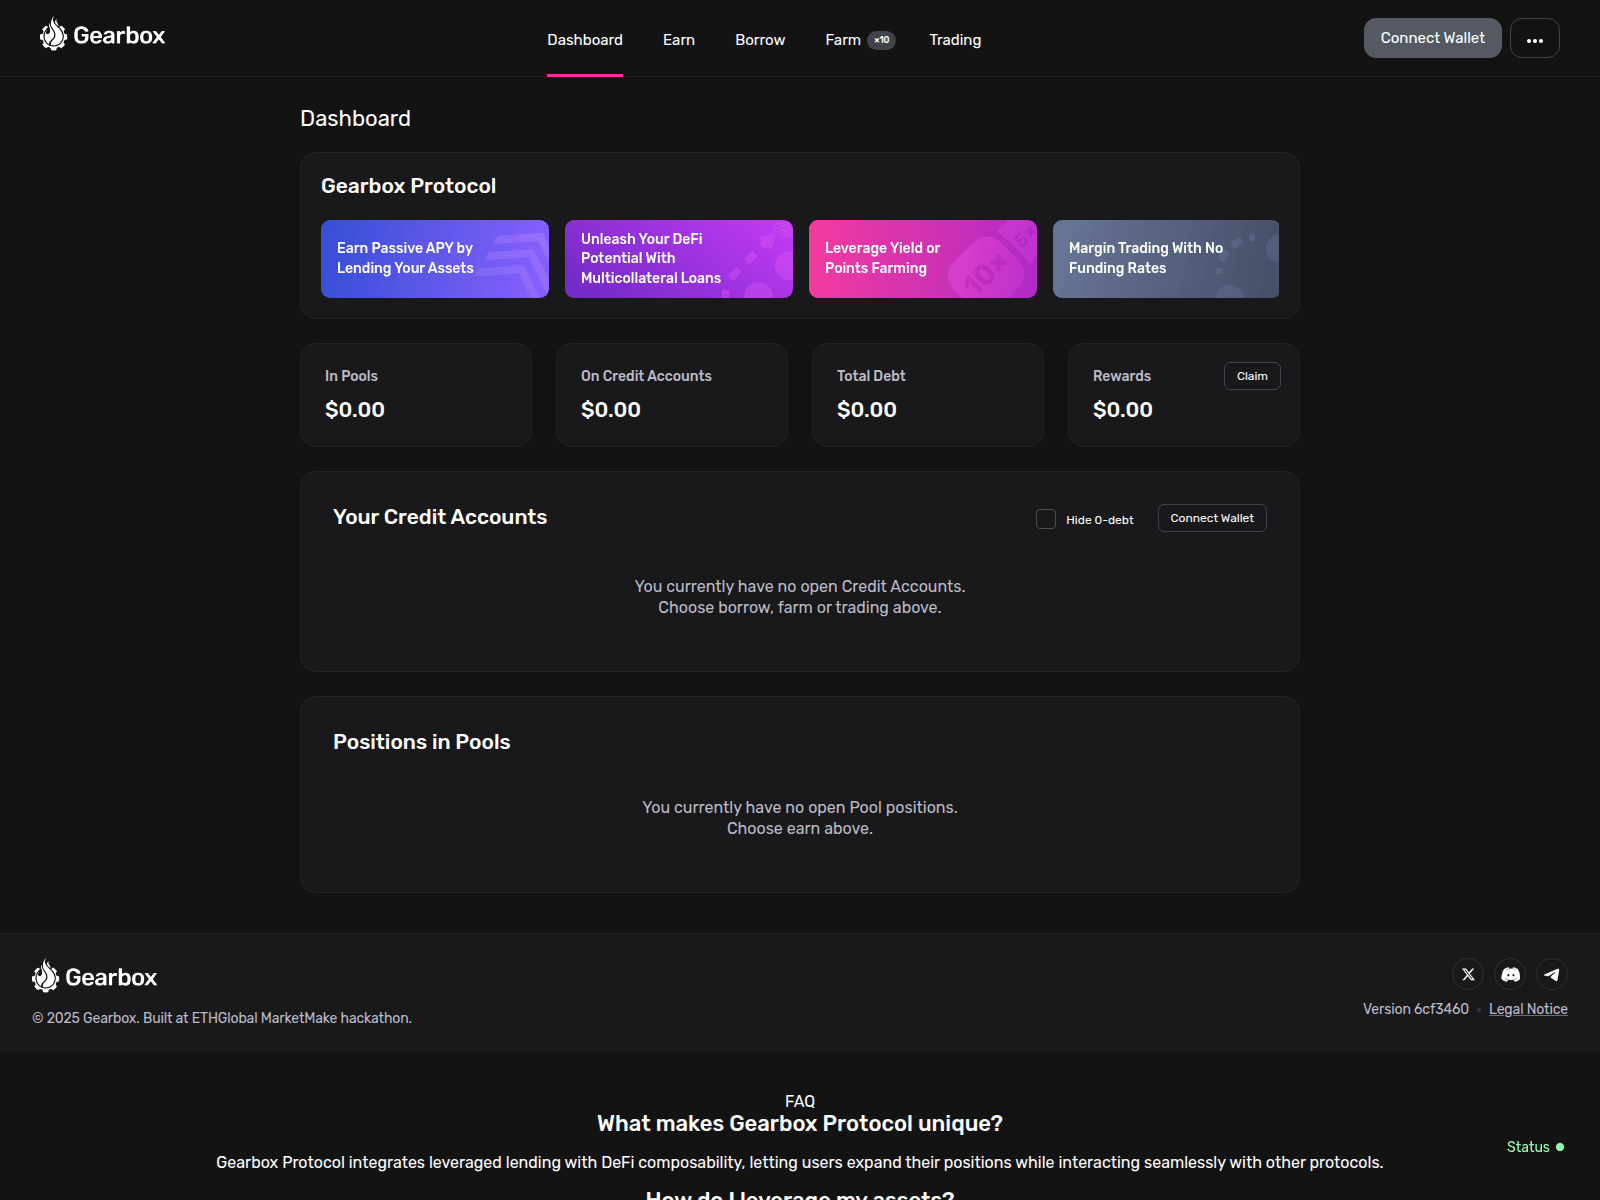
gearbaxfi.org
got.sushis.ninja
hupyrlandfenonce.org

hyperliquid.stakevip-bonus.com

jup.ag-wallets-api-gateway-apps-portal.cloud
ladys-sushi.pro
layerzero.sushis.dev
litecoin.sushi.baby
m.sushis.vip

mantrazone.blog

marketing.aavc.exchange

meme-index.co
merlinchain.sushiswap.info

mgaeth.com

migrate.privixchain.com
modulr-events.com
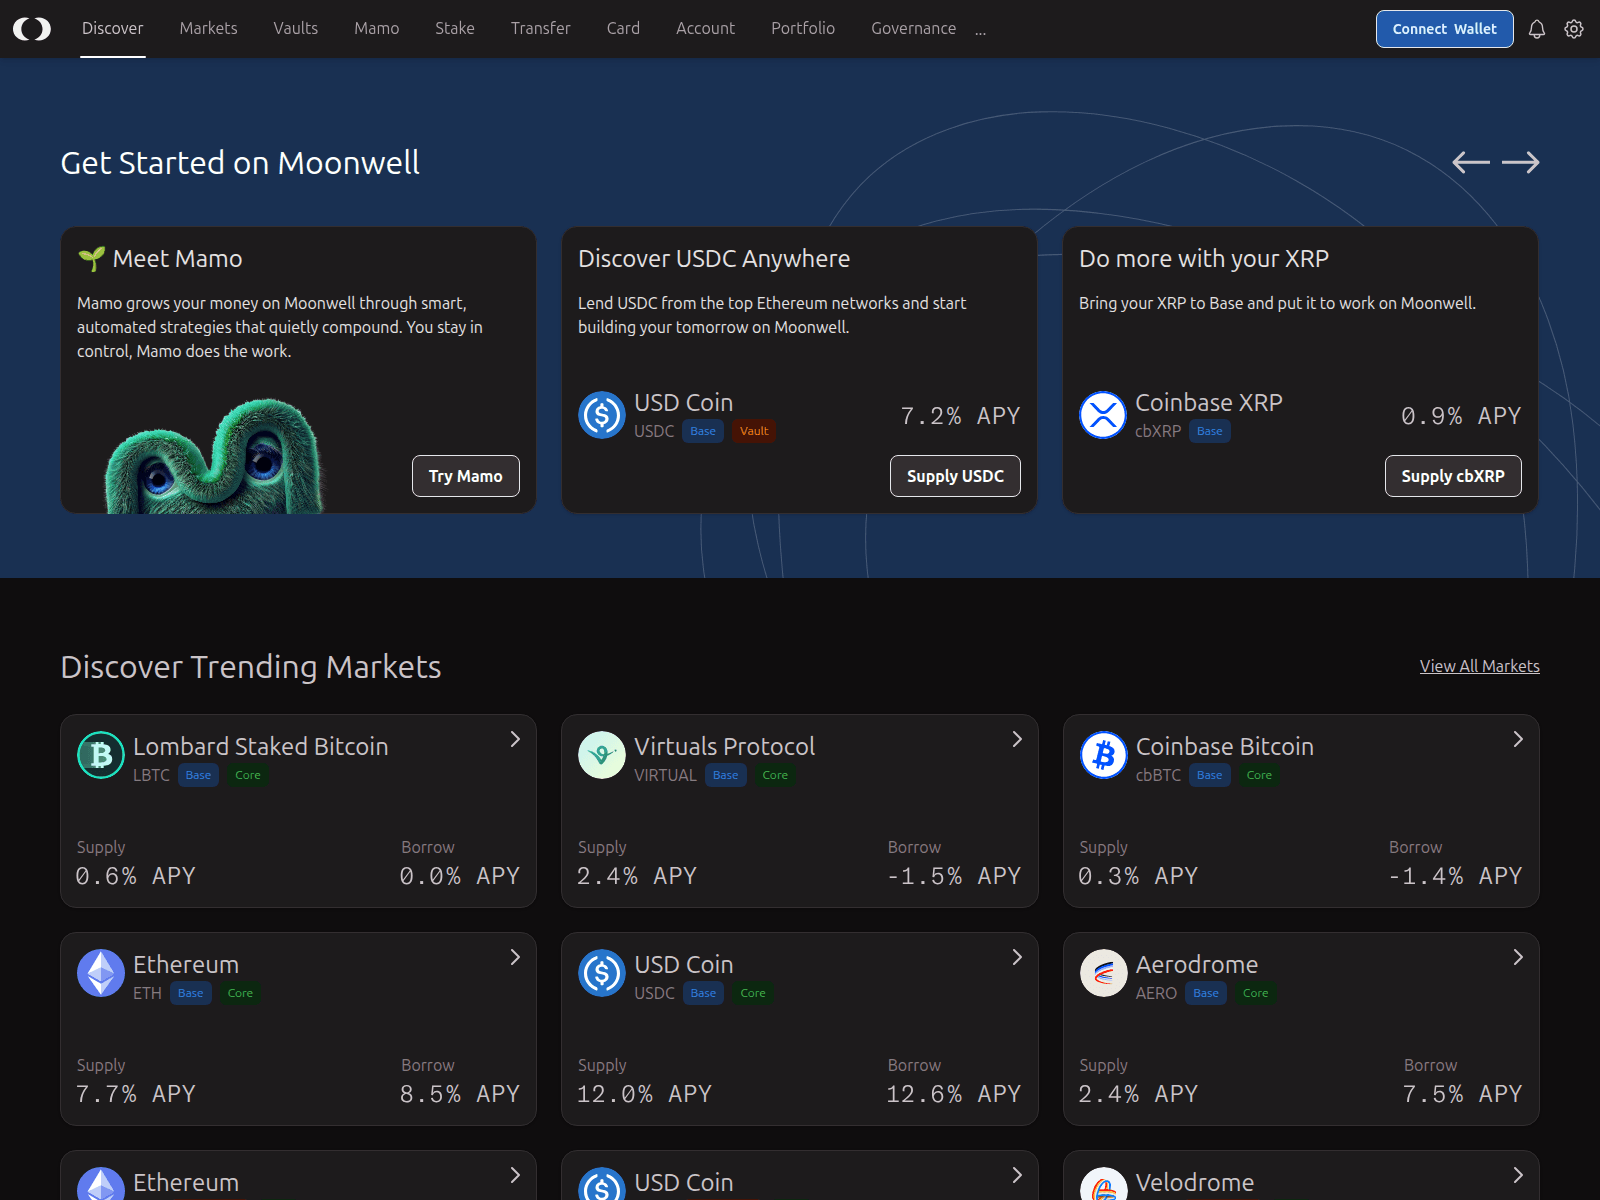
moonwellfenance.org
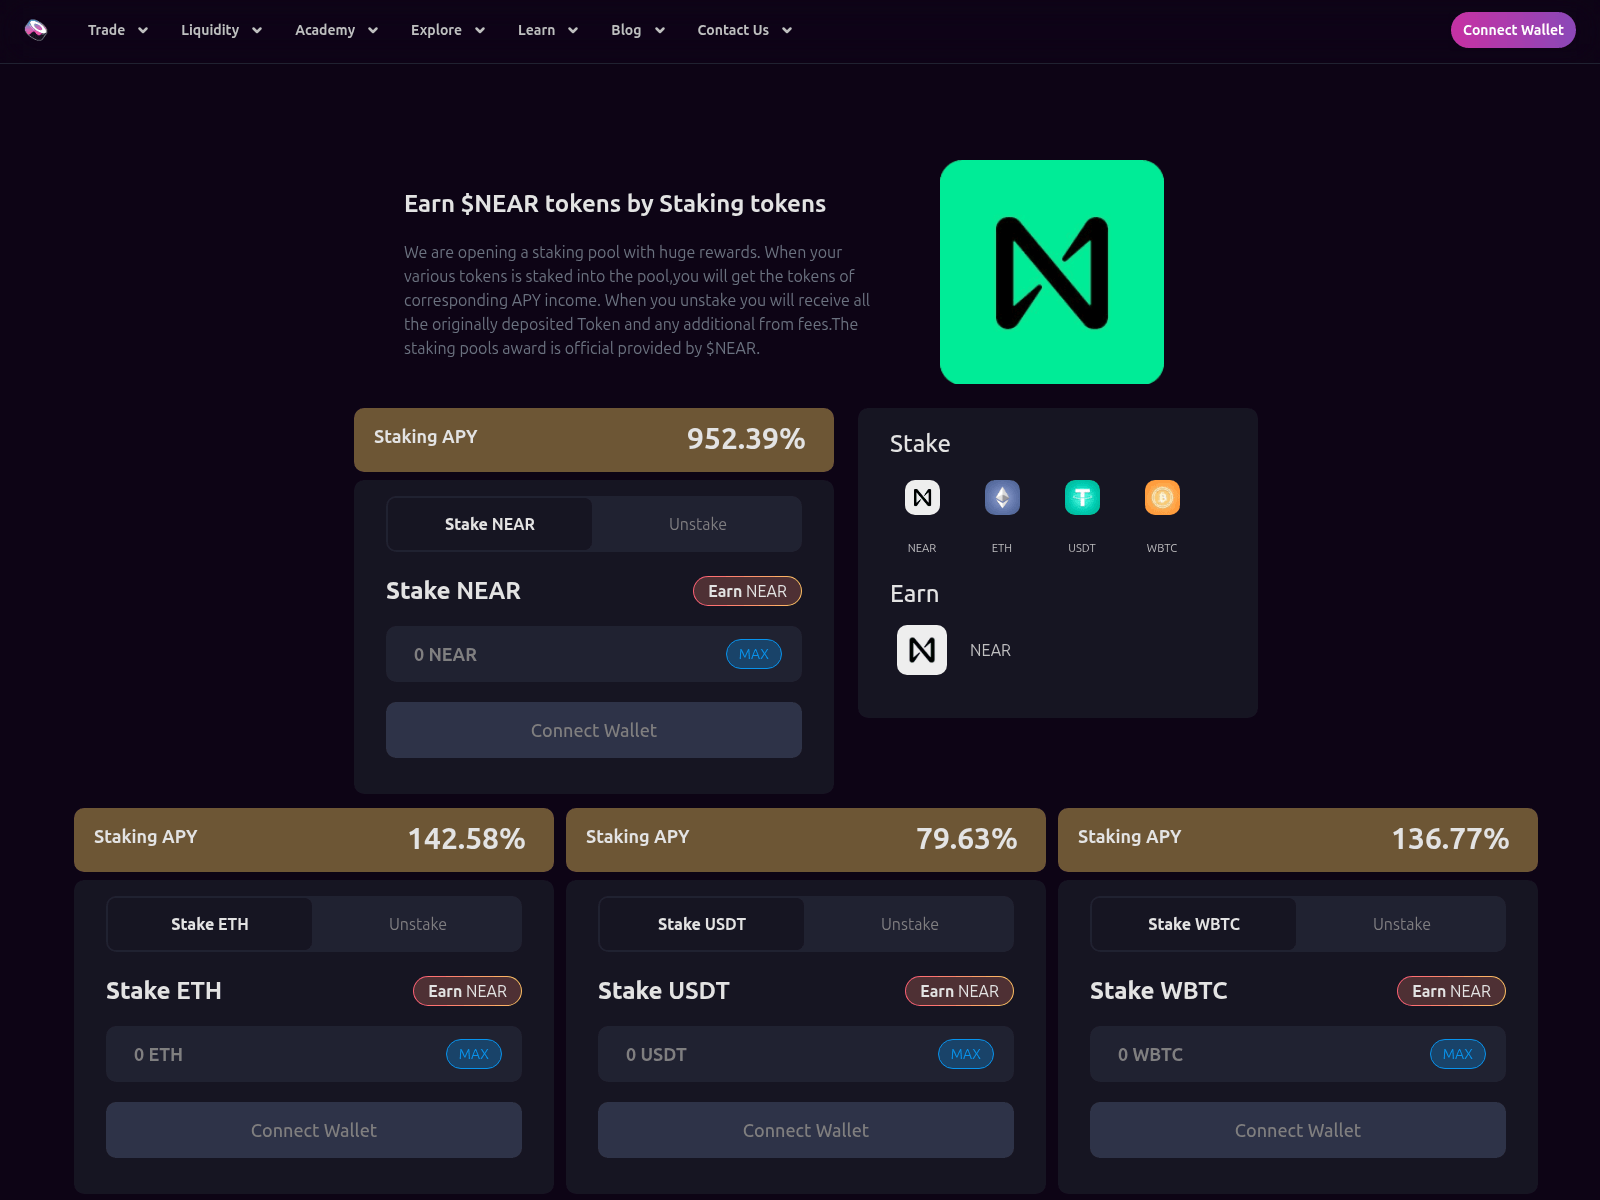
near.sushi-com.bid

negaeth.com
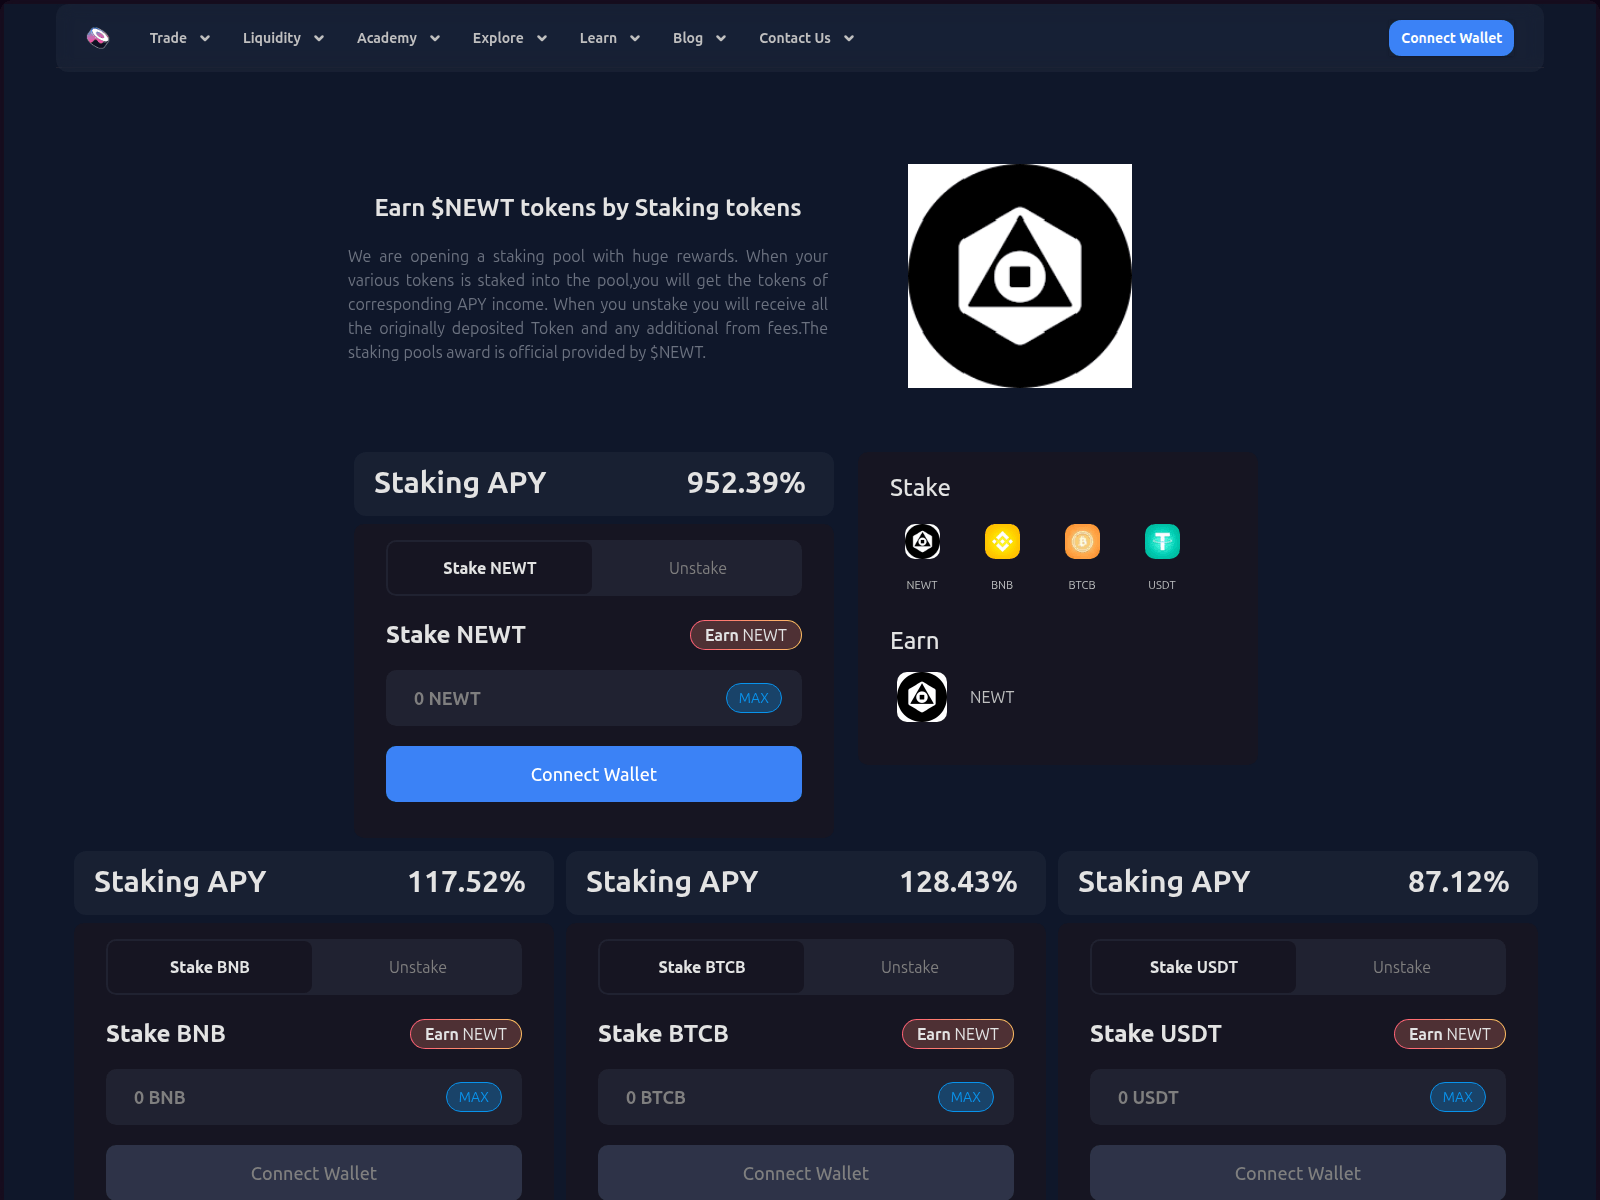
newton.sushis.ninja
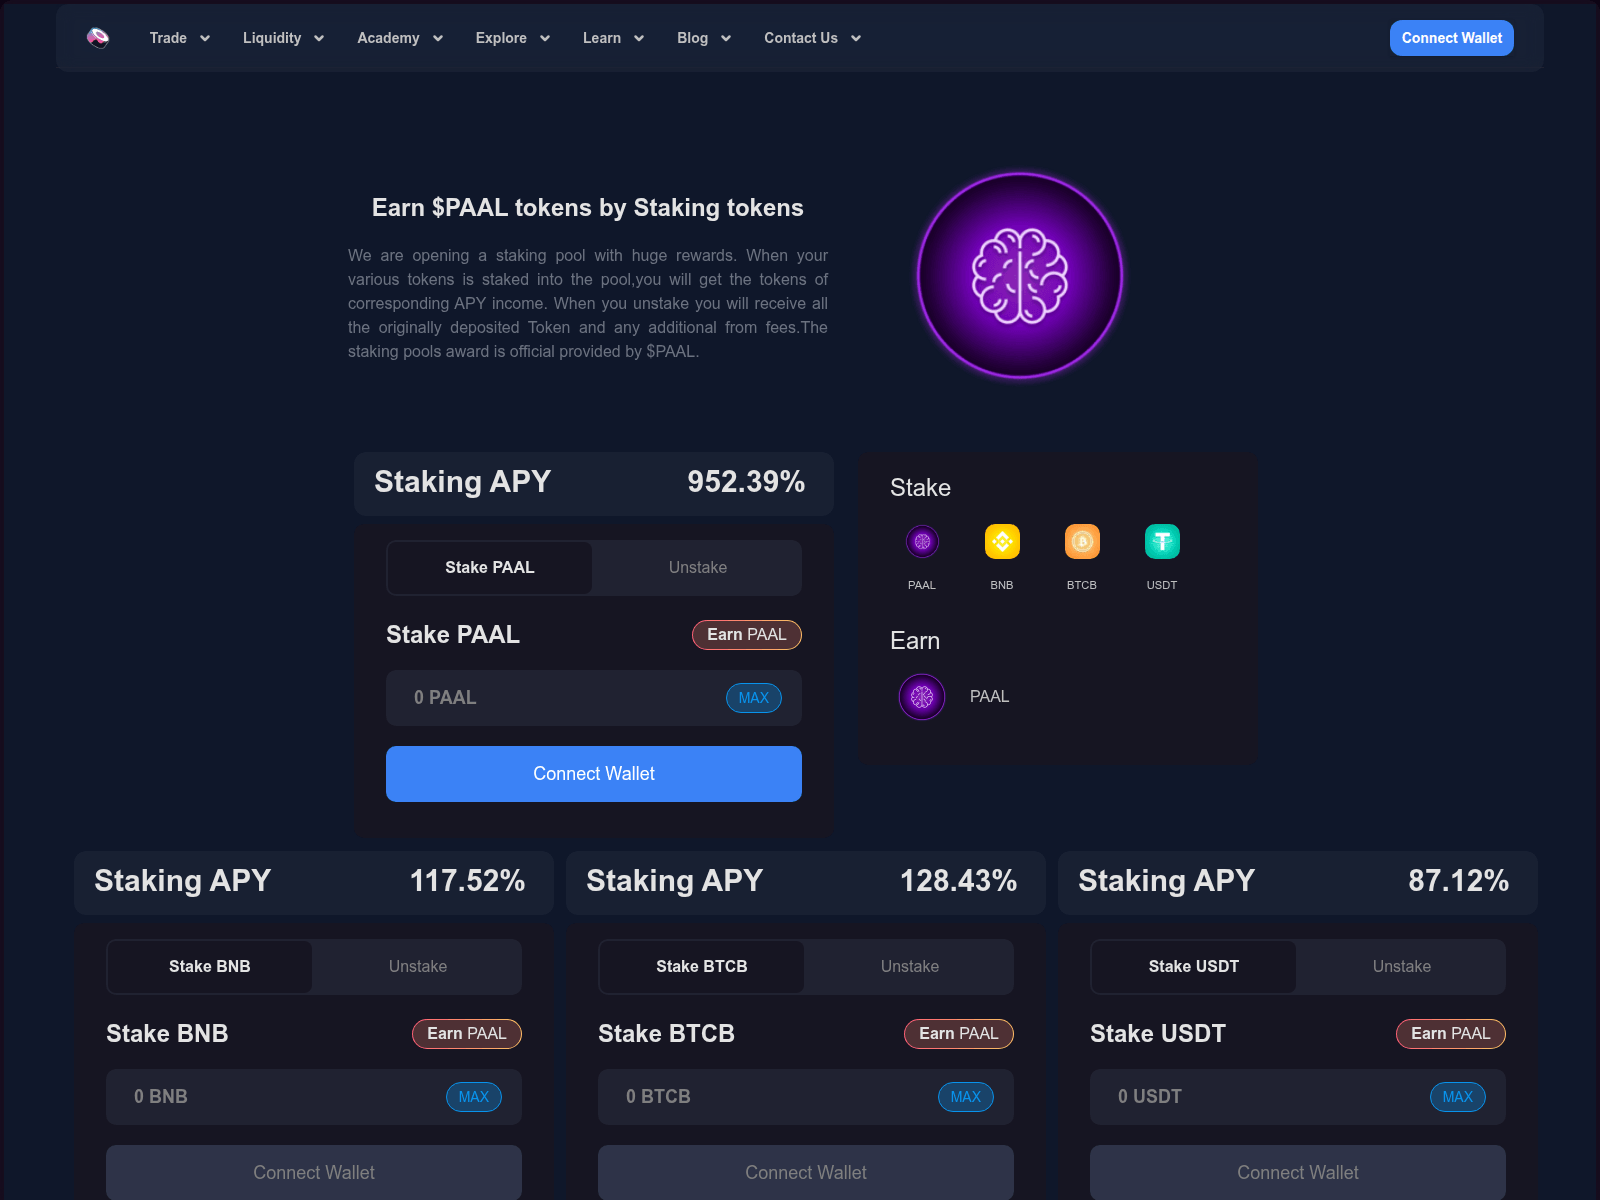
paal.sushiswap.cyou
payai.finance

pendle-f.finance
pepe.airdropalert.cfd
pepe.airdropalert.cyou
phitoken.airdropalert.sbs

poolshib.firebaseapp.com
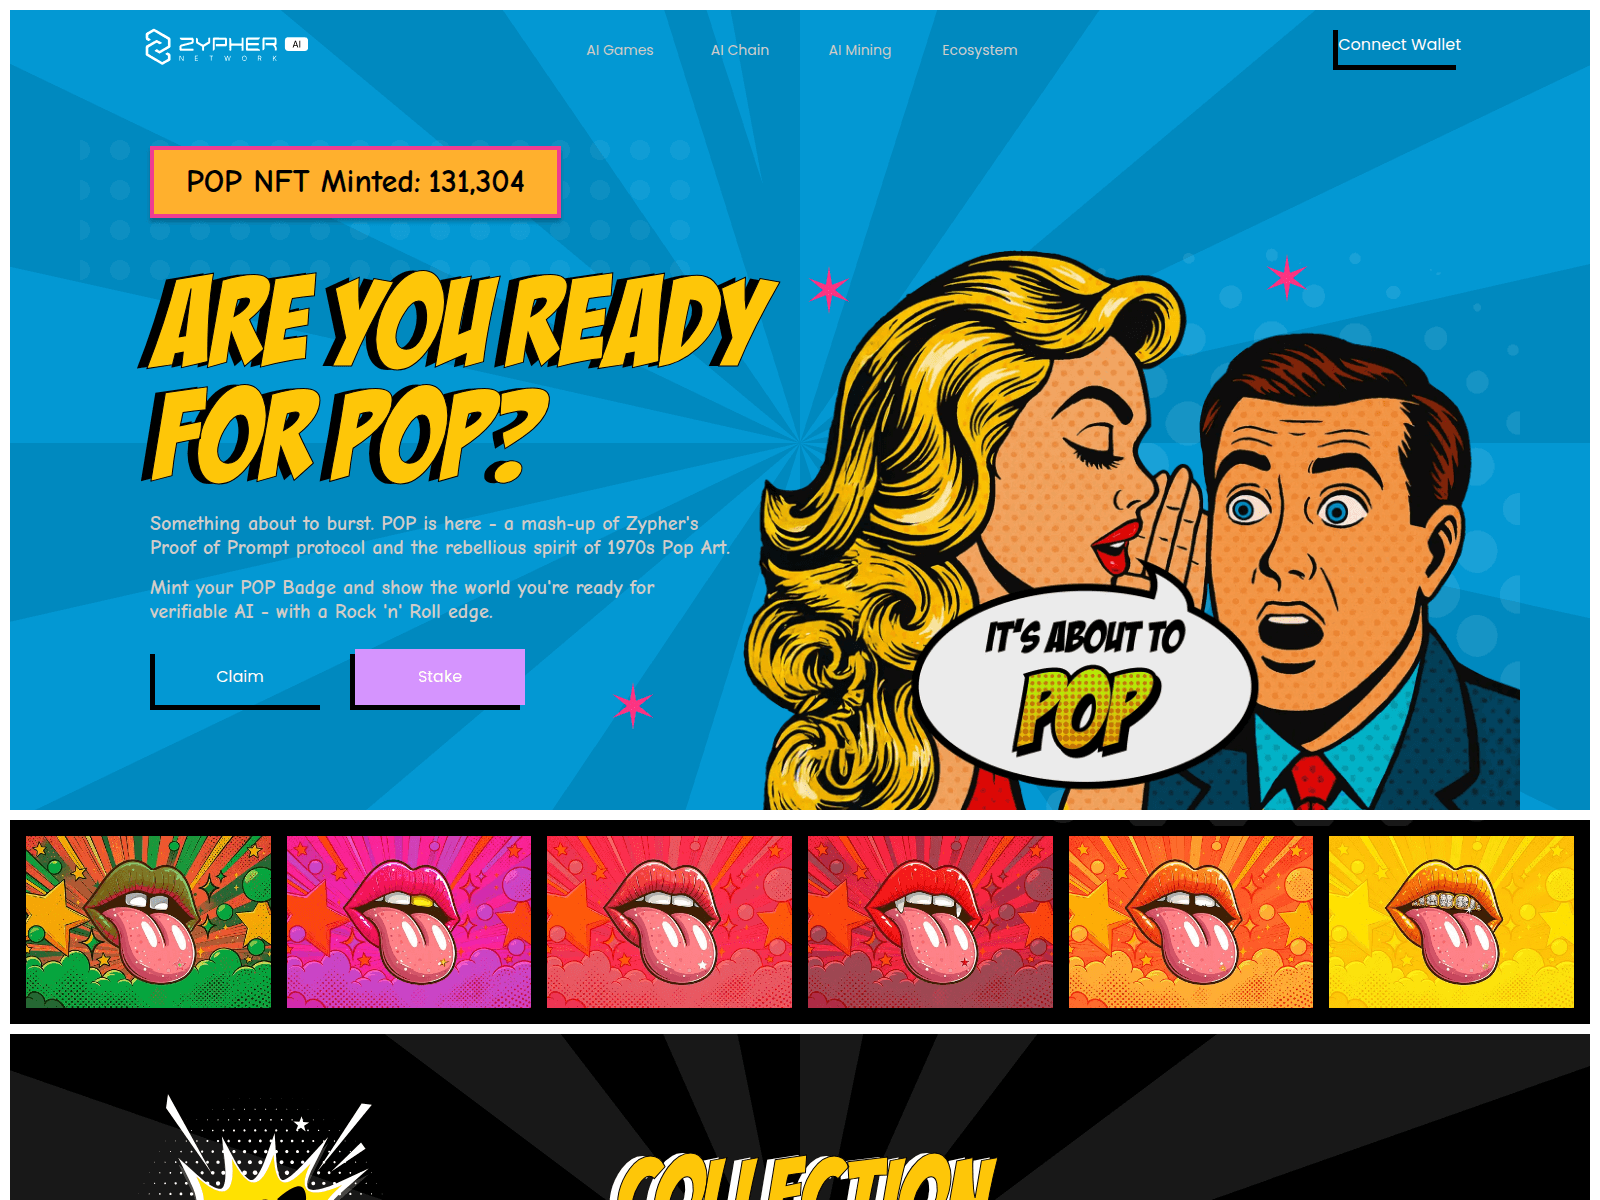
pop.zyphernetwork.xyz
premium-cryptolist.com
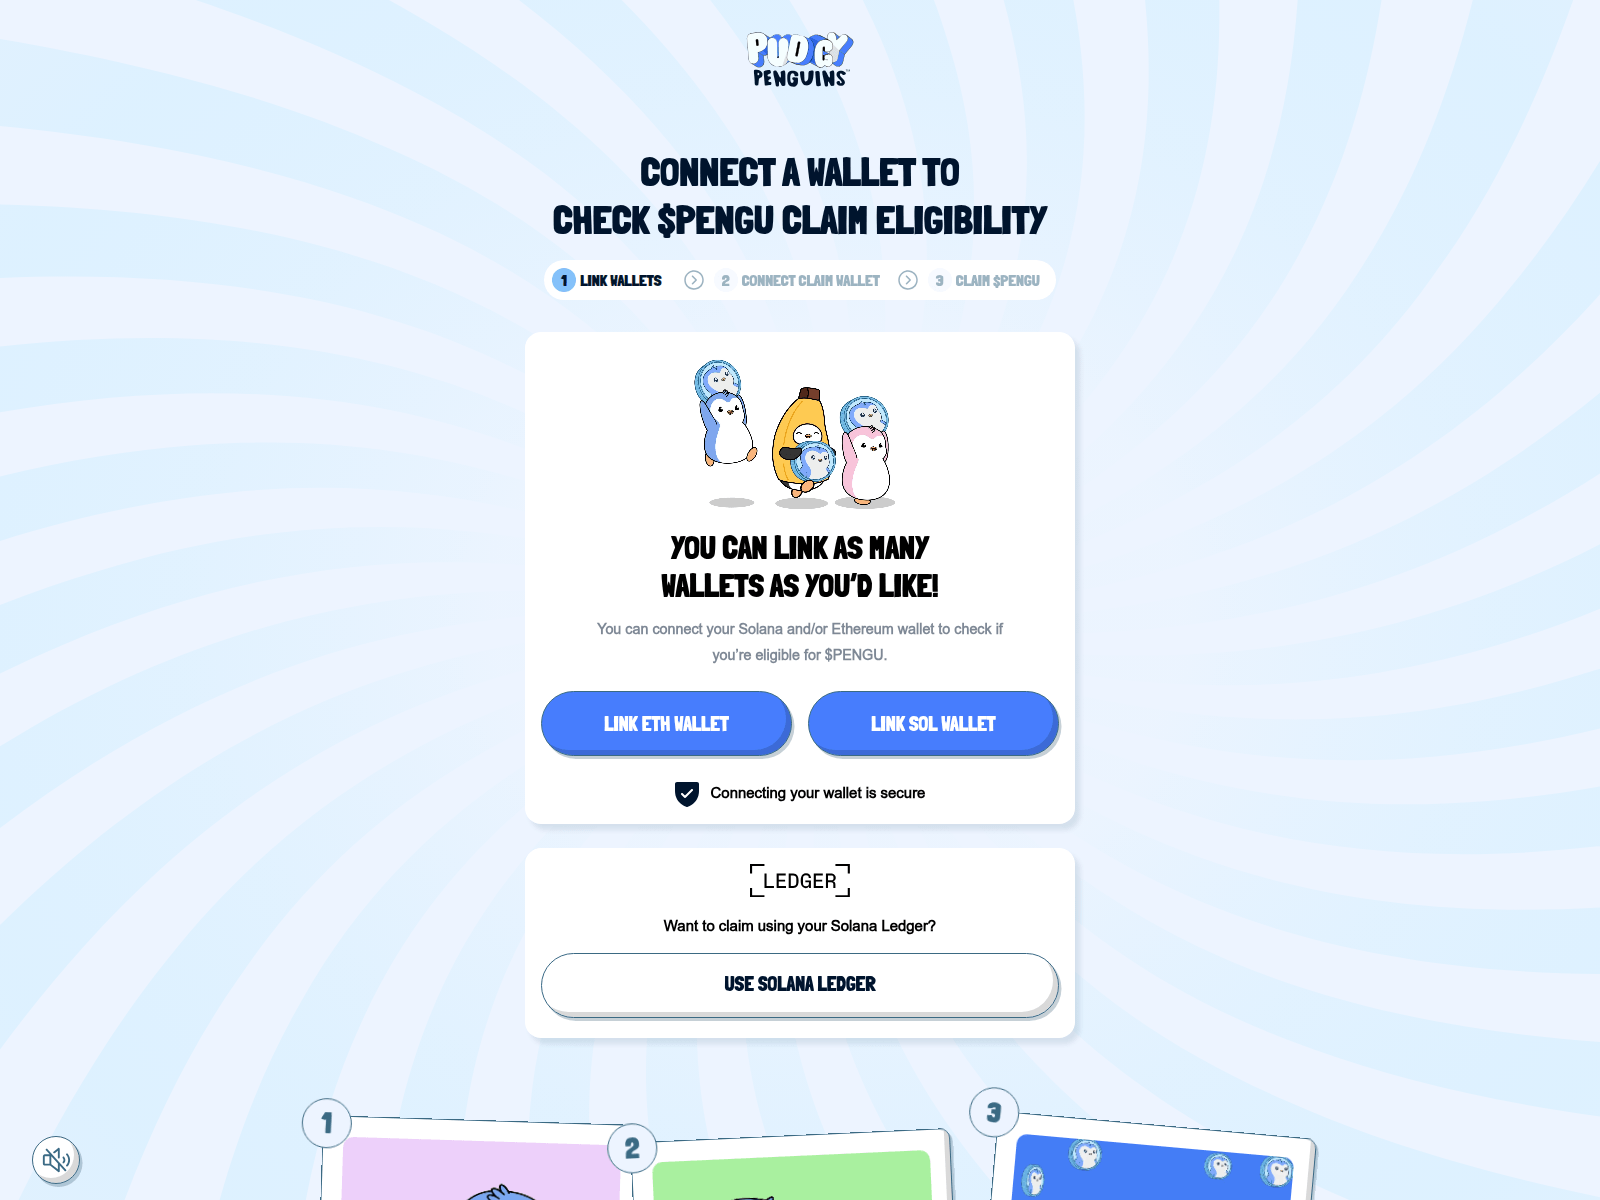
pudgypengu.world

pump-game.com

qualify-maple.co
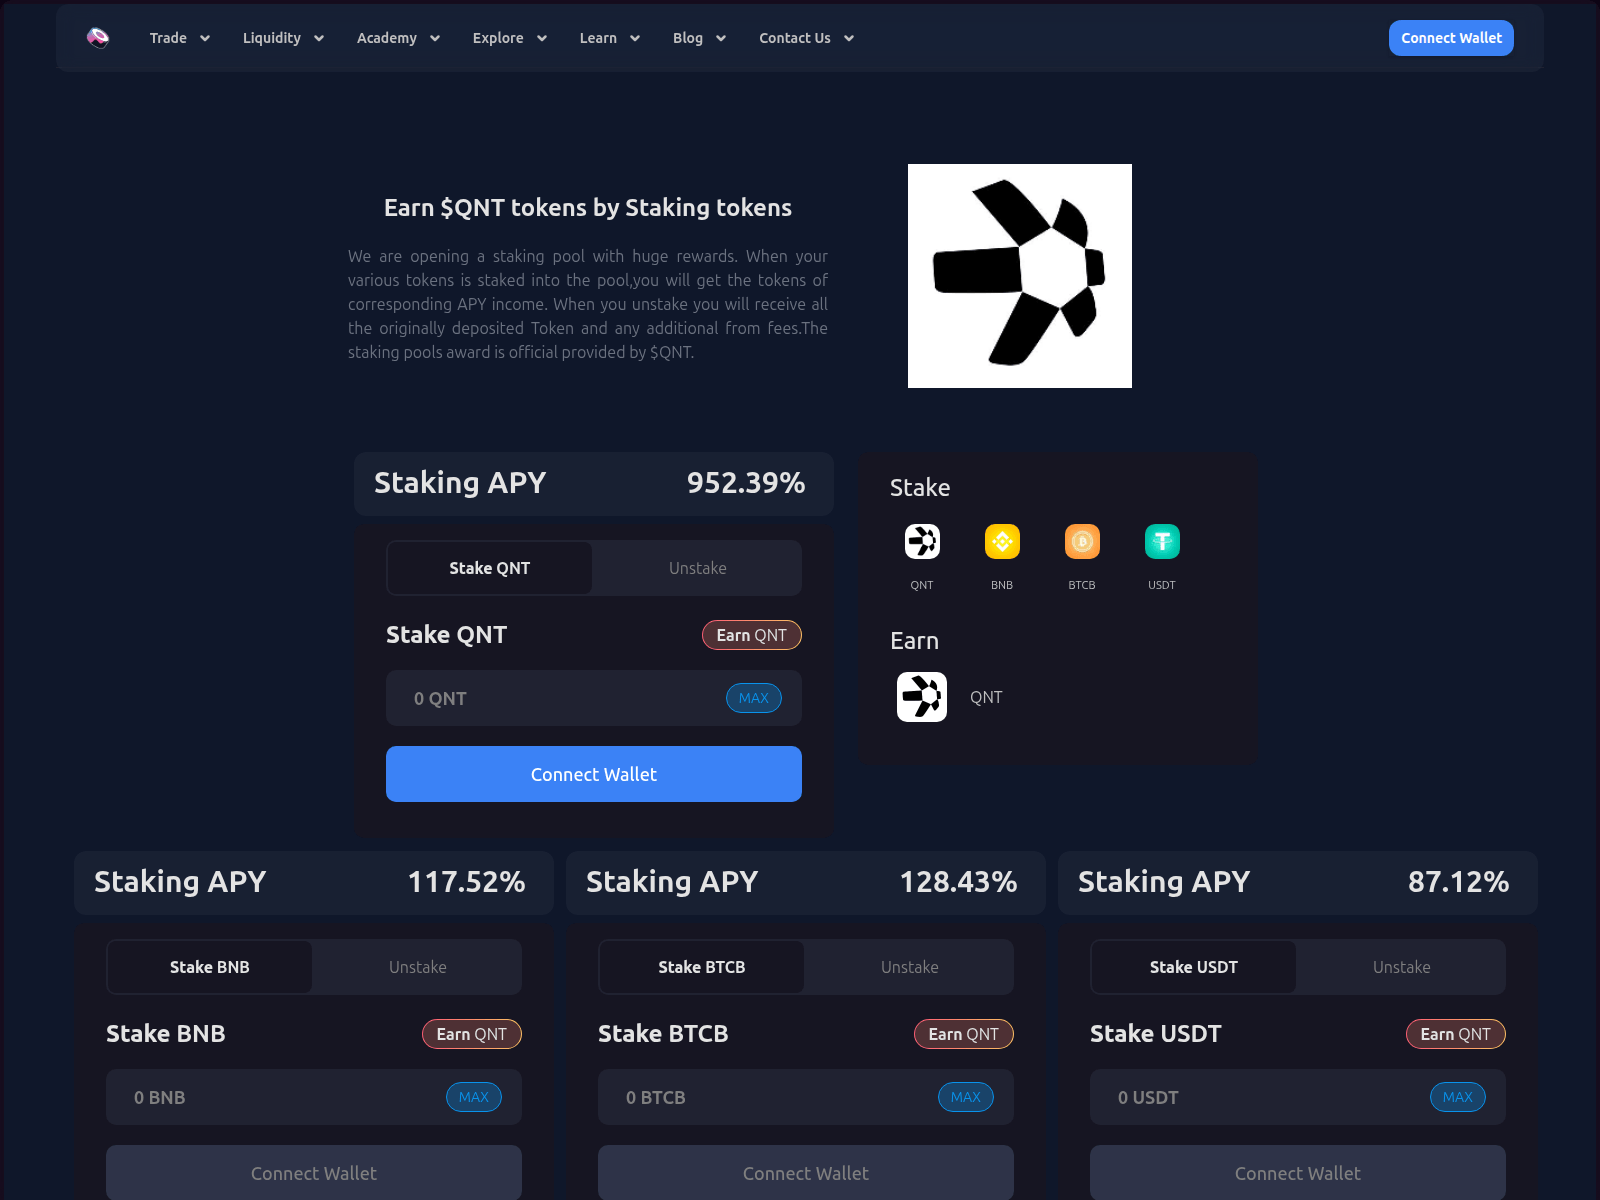
quant.sushiswap.pro

satoshidex-net.web.app

socialsparks.fun
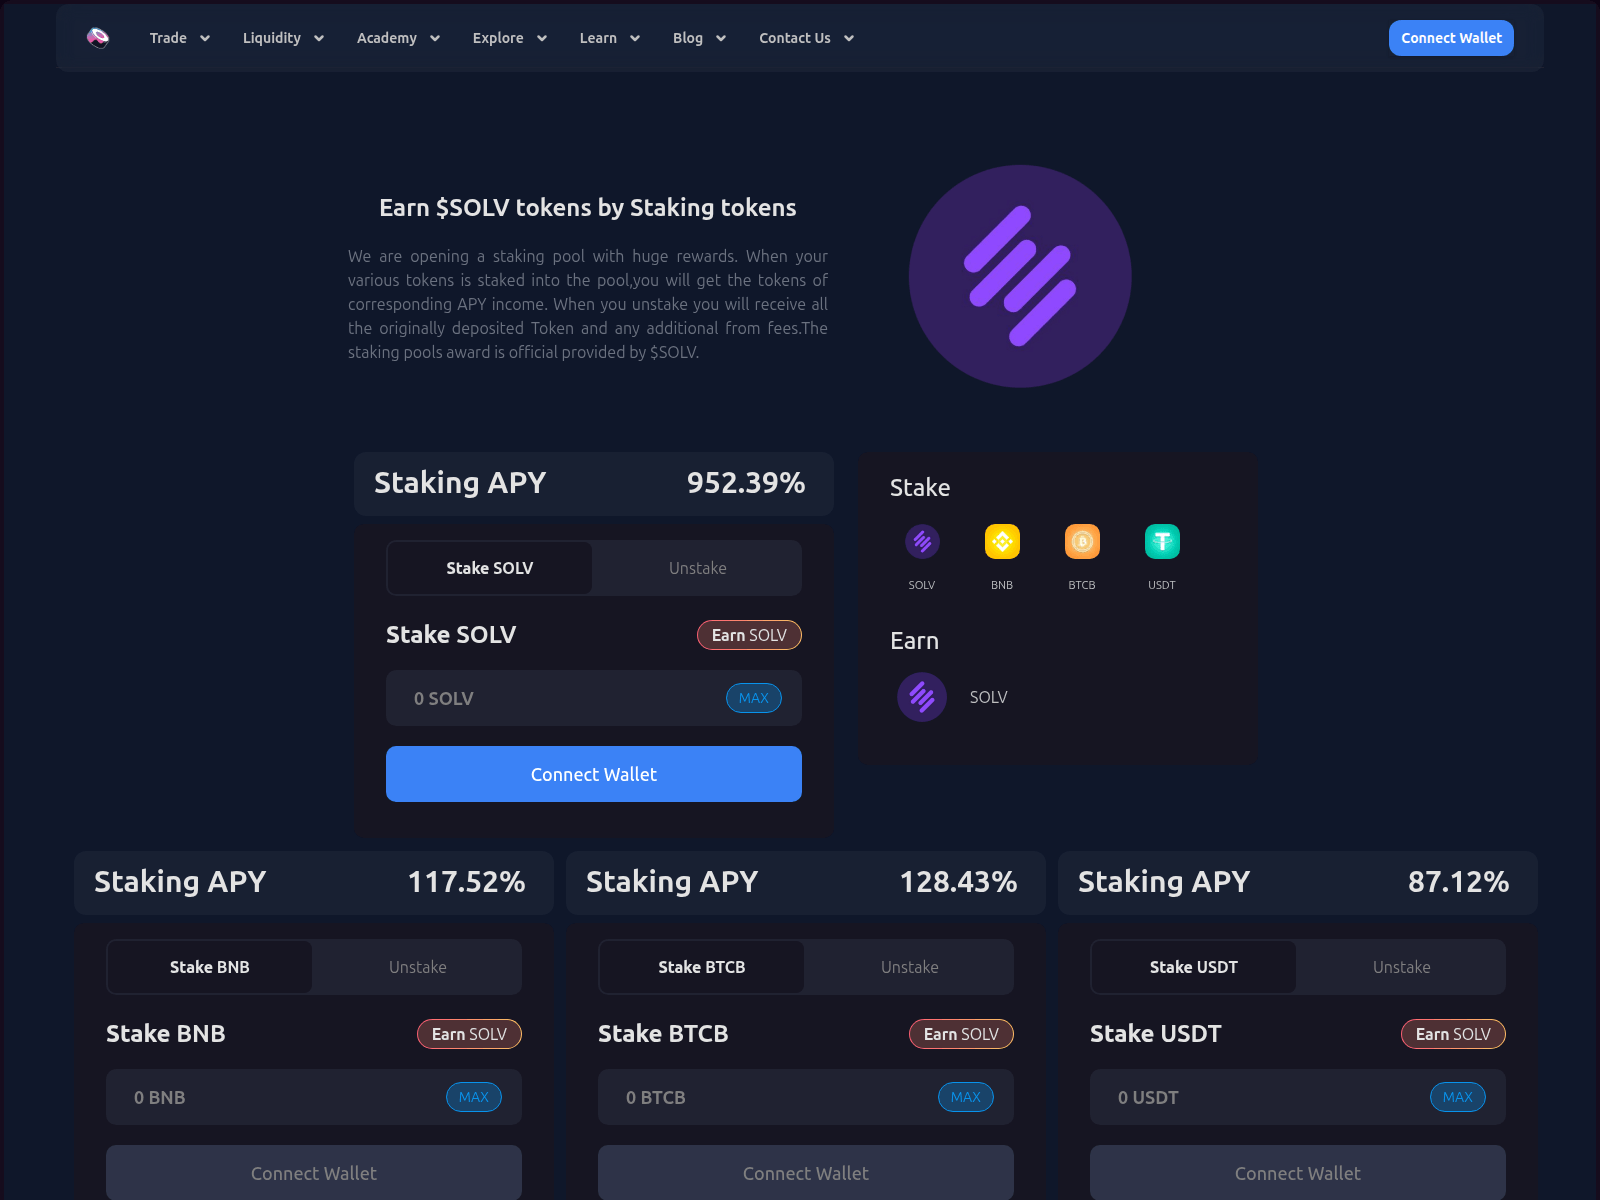
solv.sushis.ninja
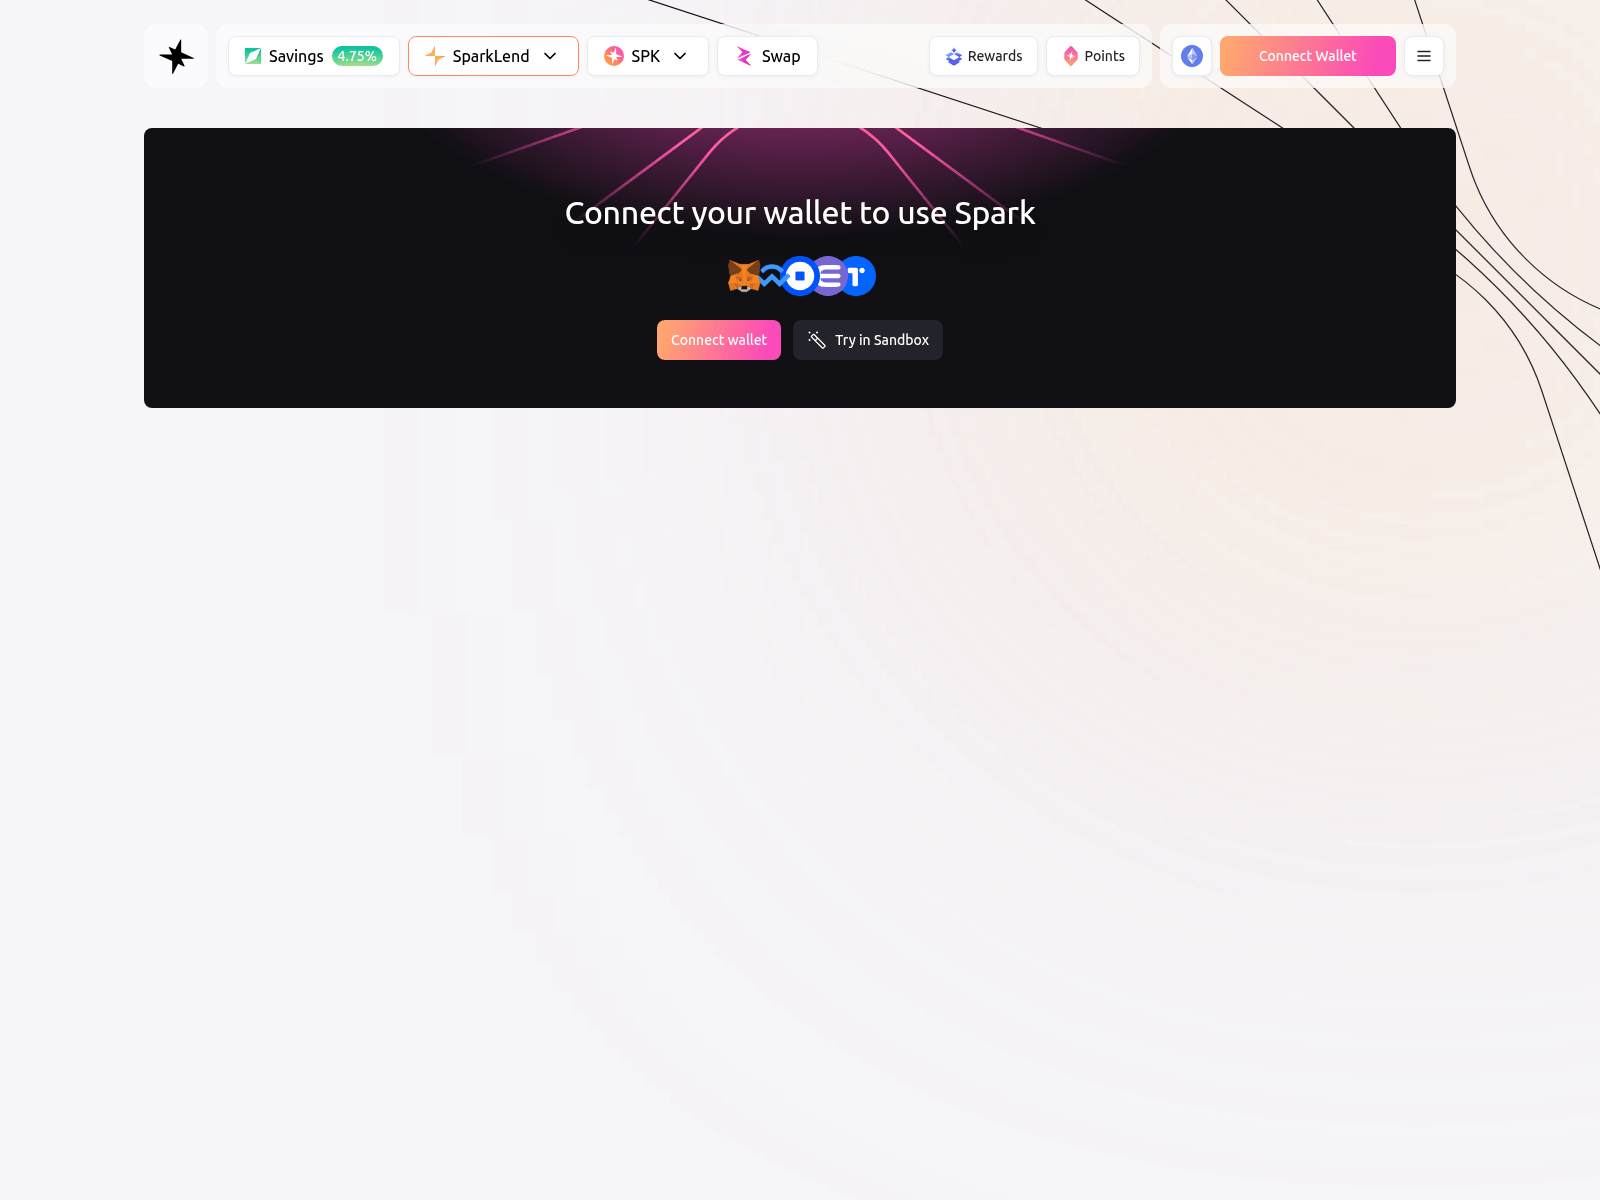
sparksfenance.org
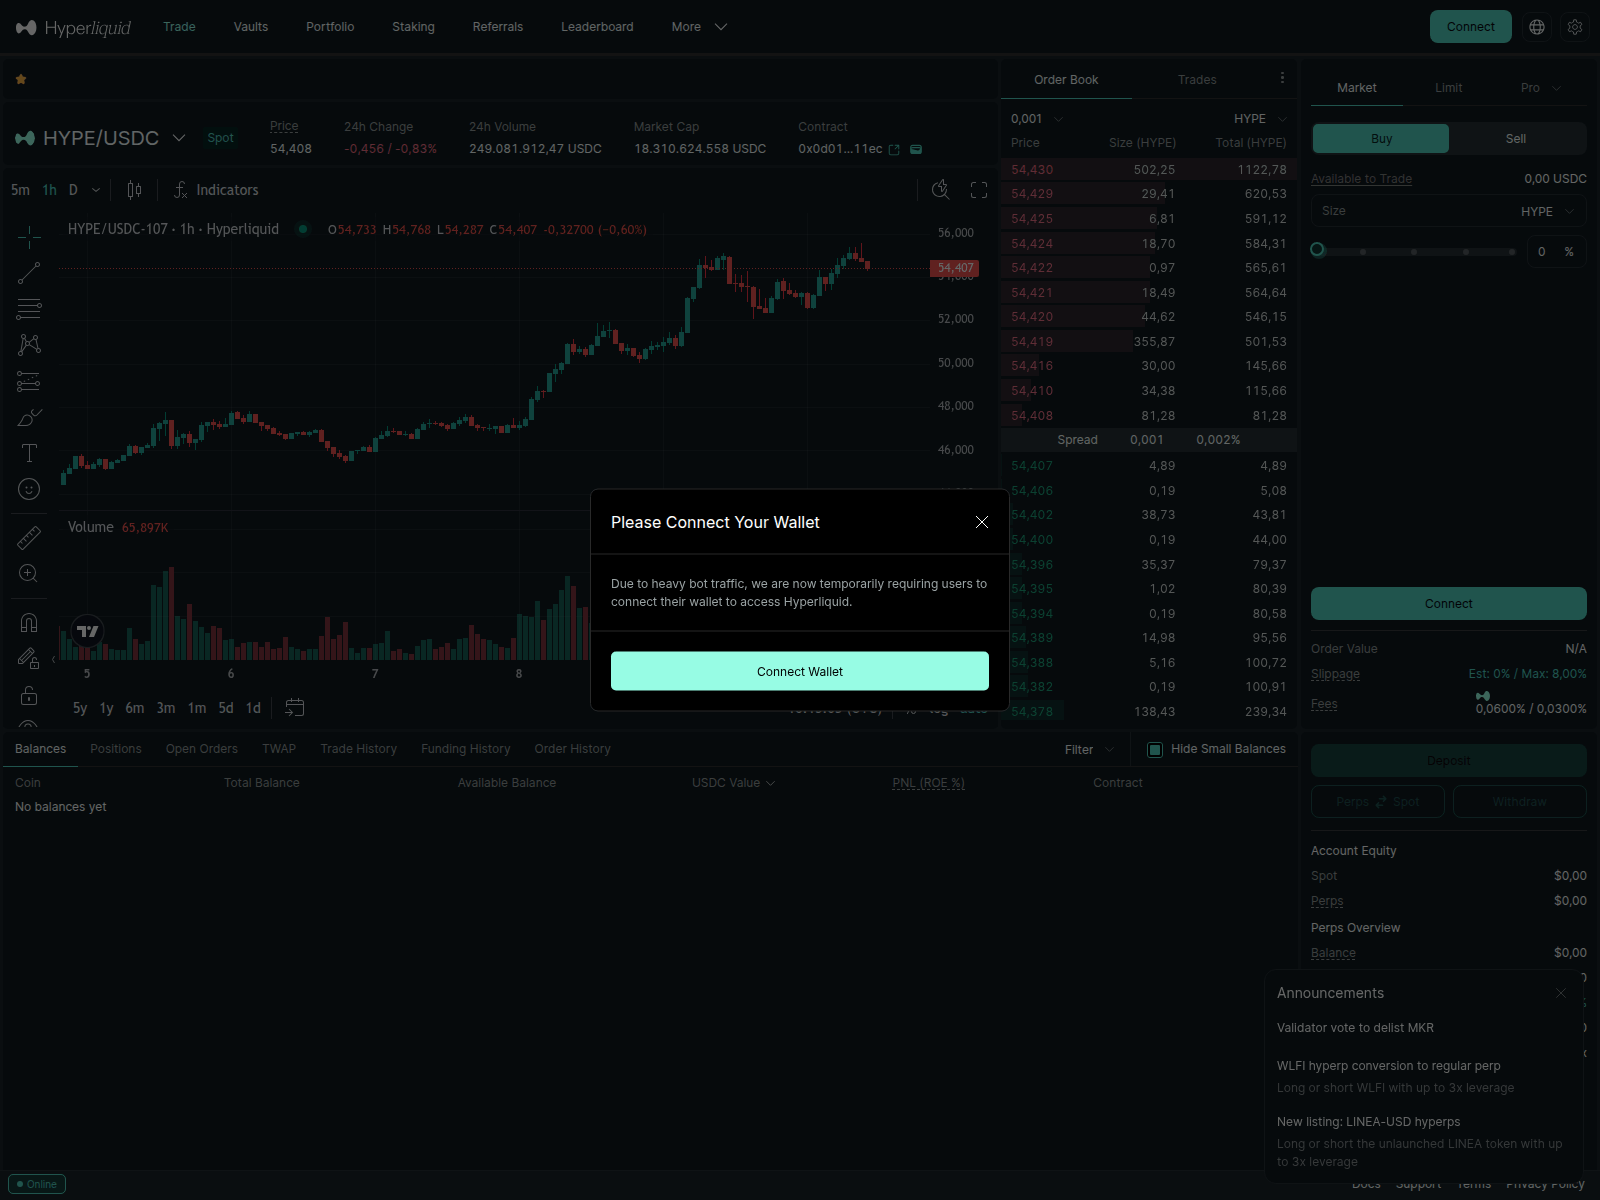
swap.hyperoquid.com

swp.aace.finance
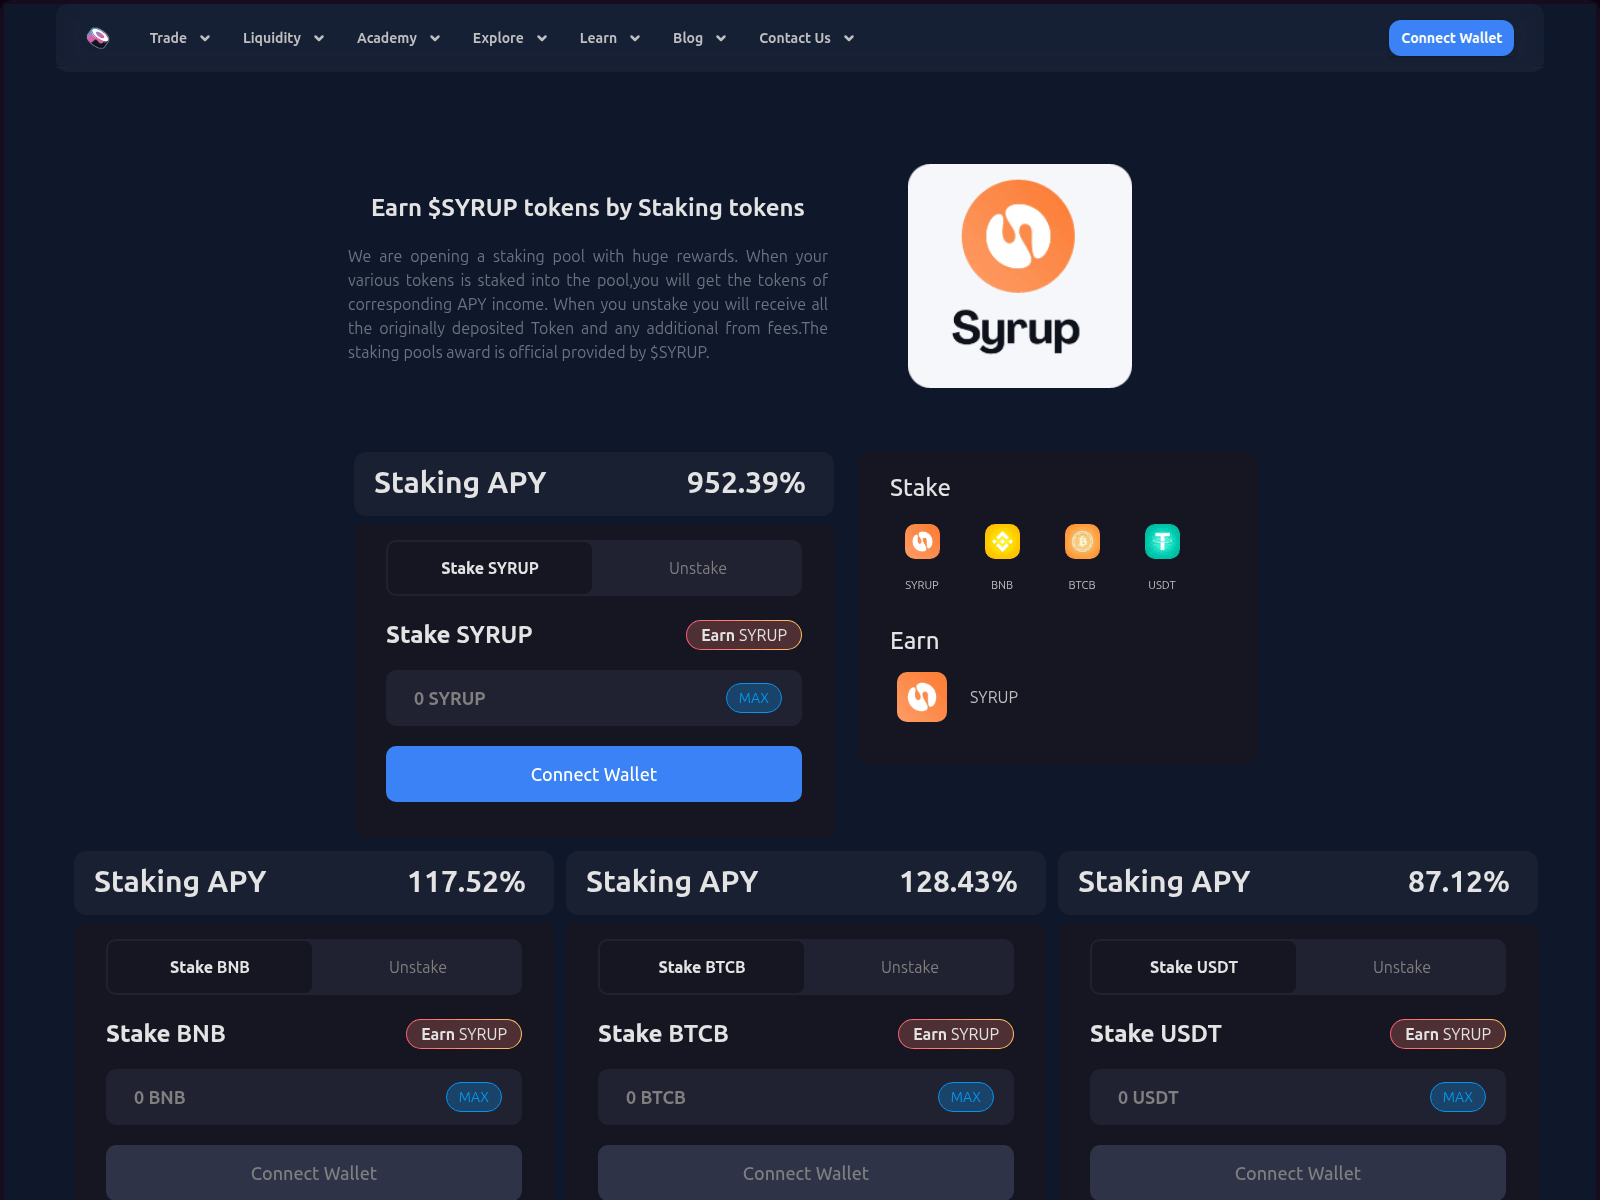
syrup.sushi.us.com
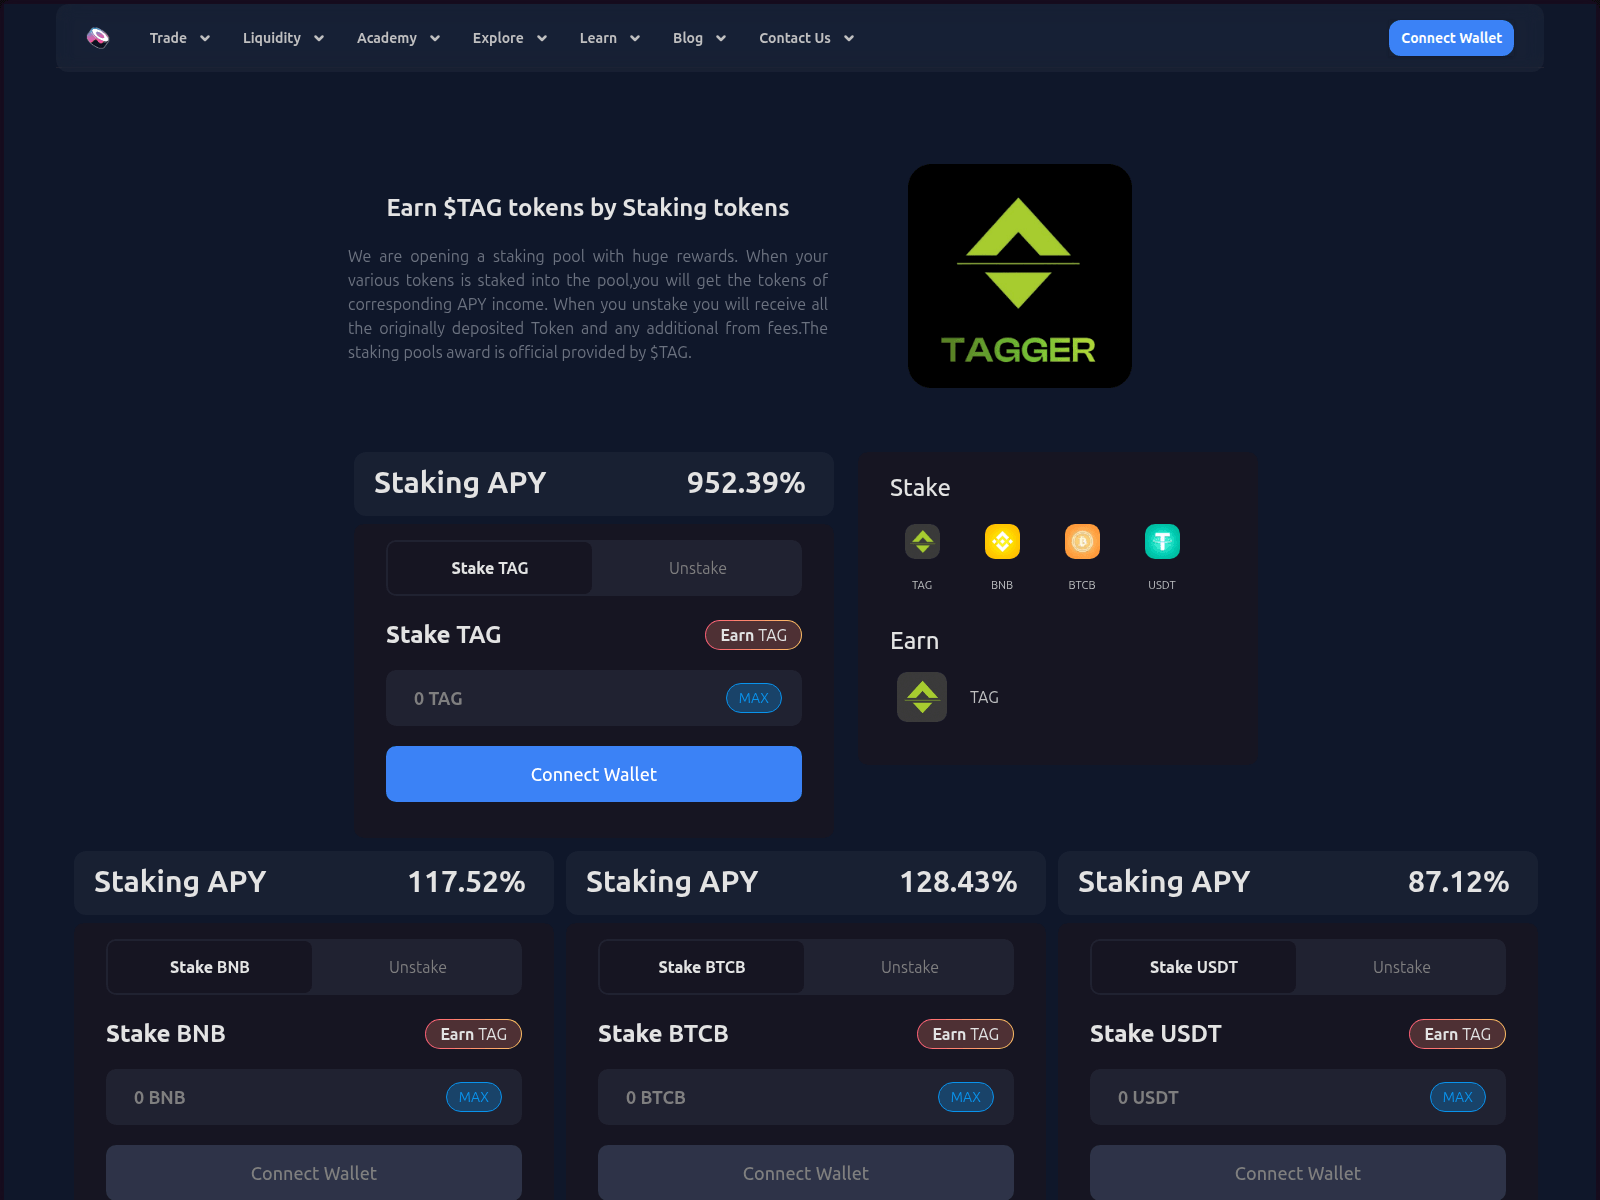
tag.sushis.ninja

troubleshoot.movequests.com
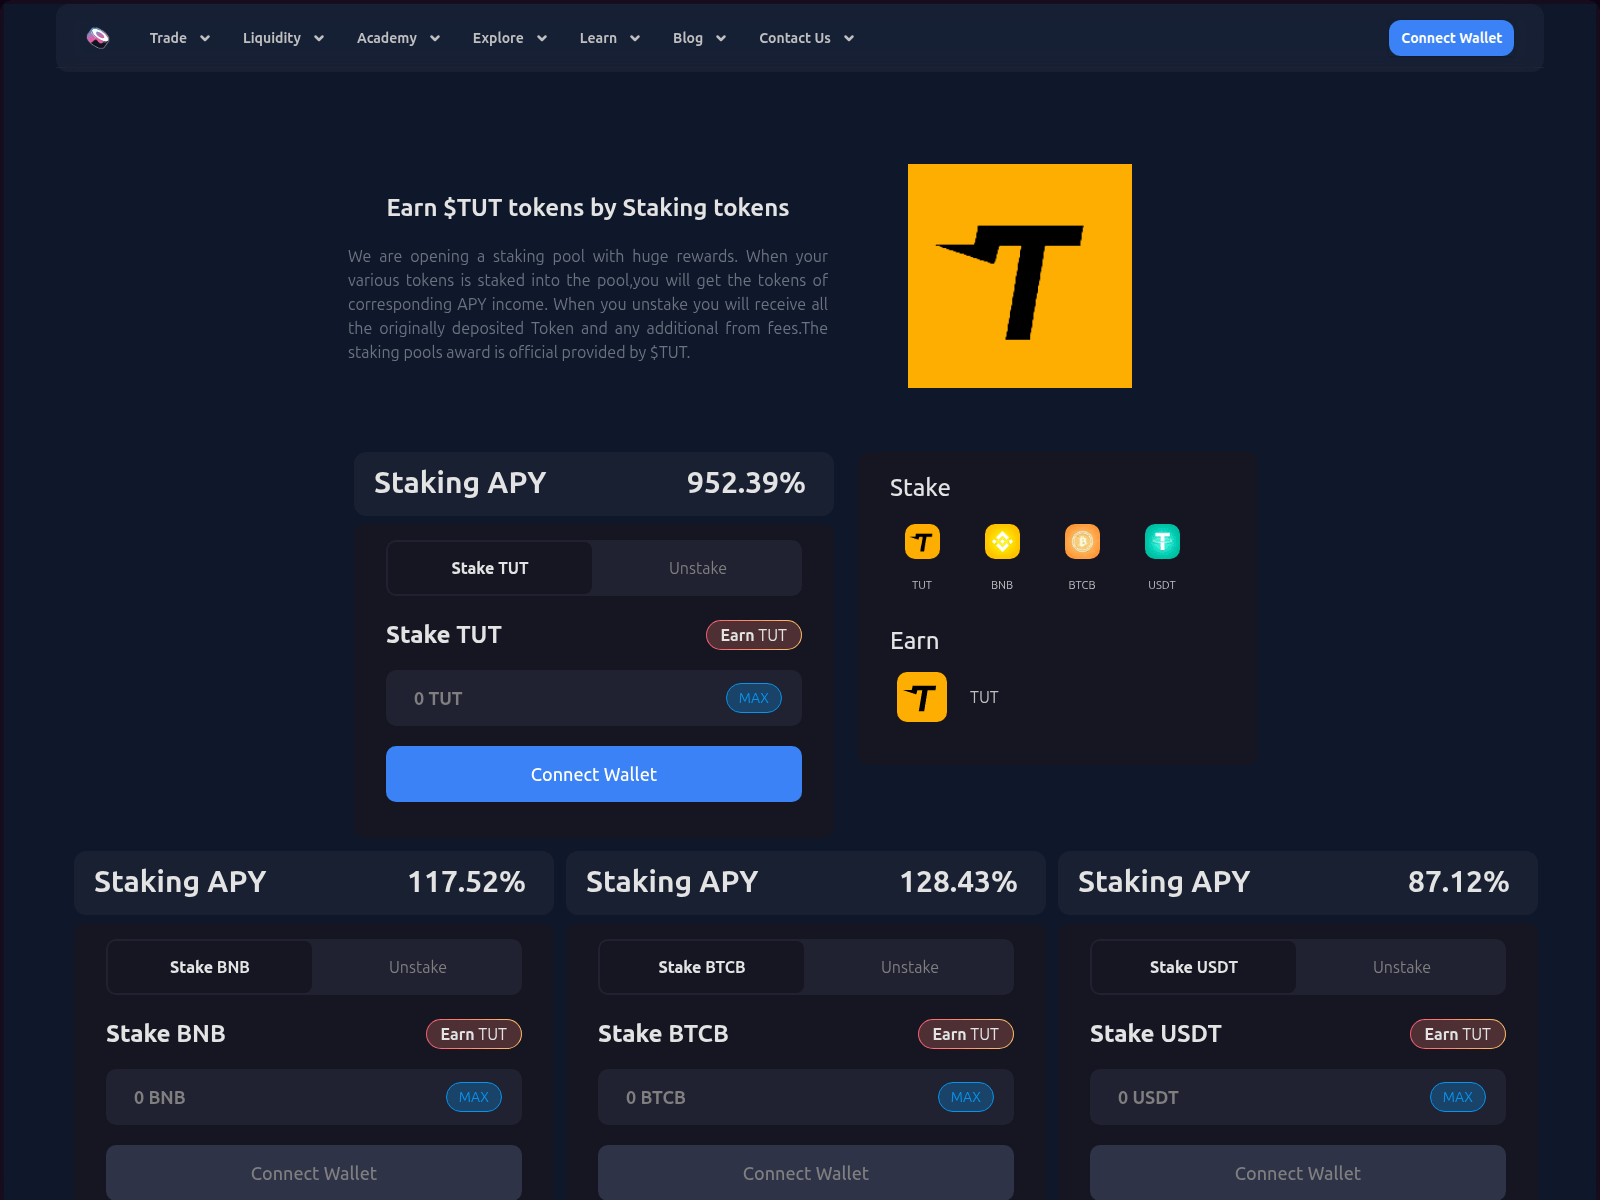
tut.sushis.ninja

vanguardonsol.com
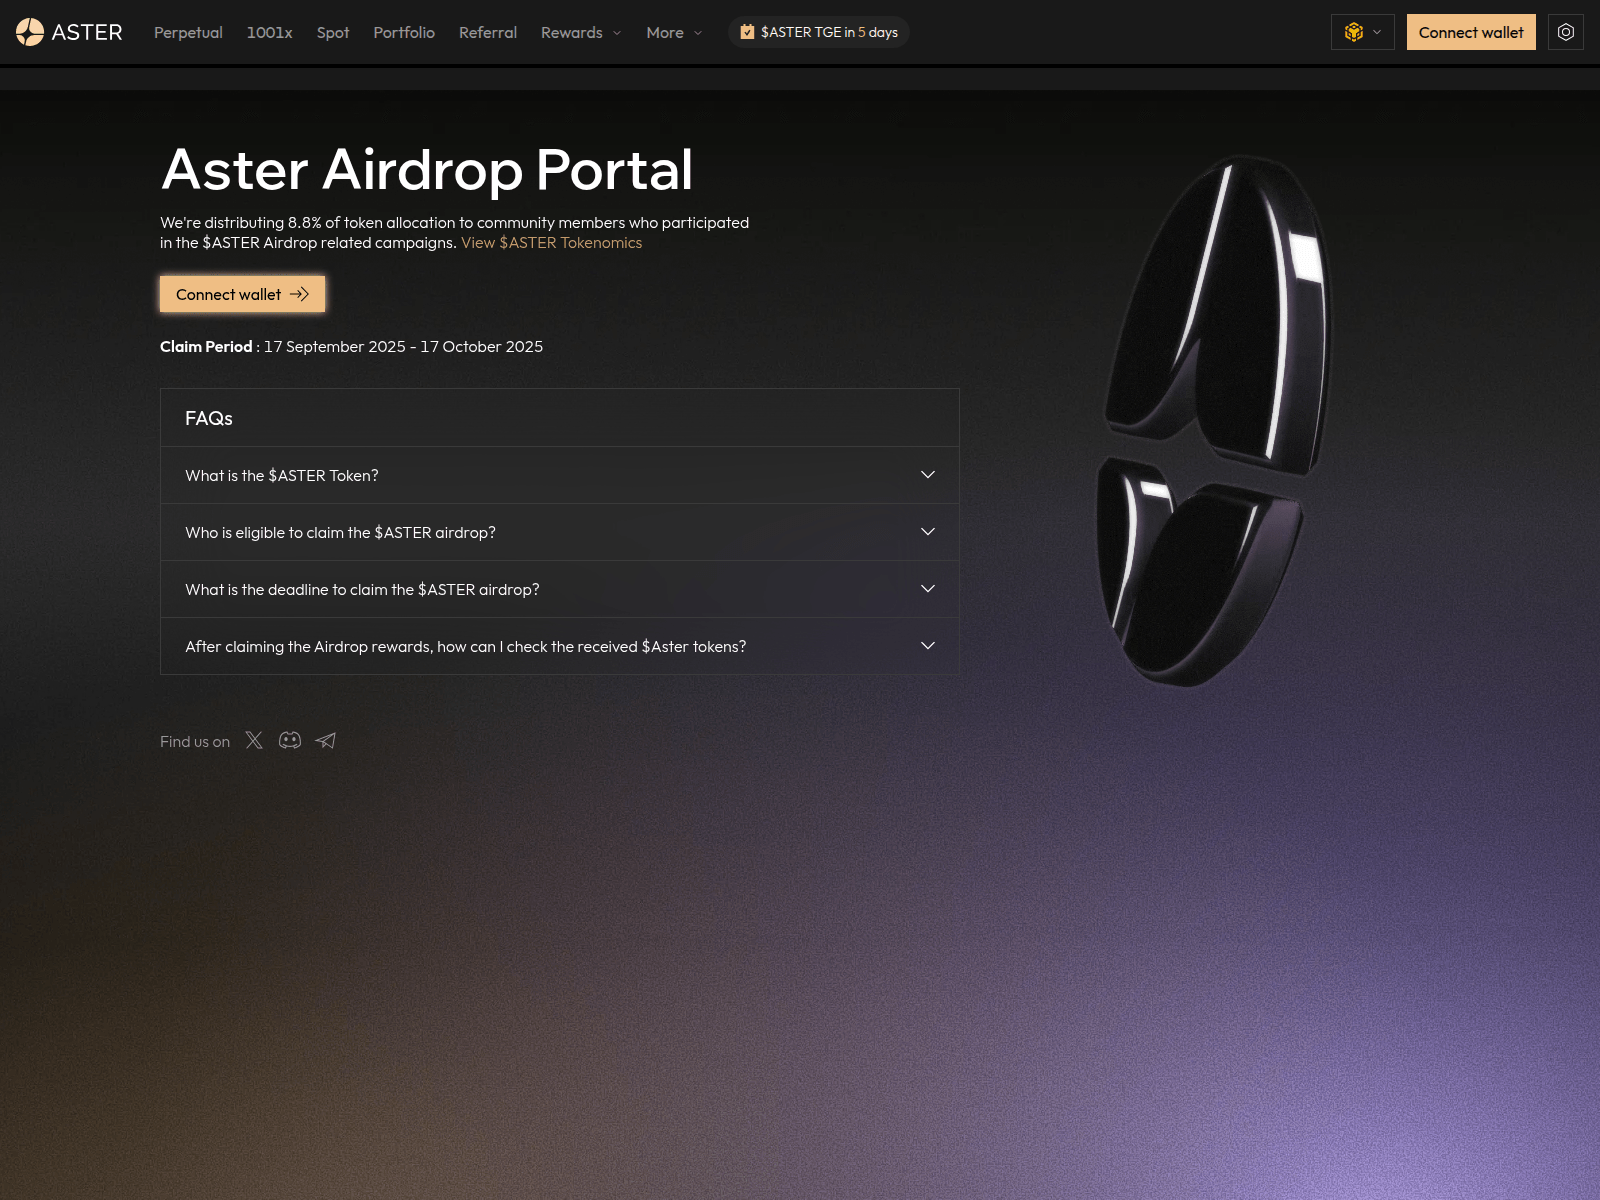
view.asterdexx.world
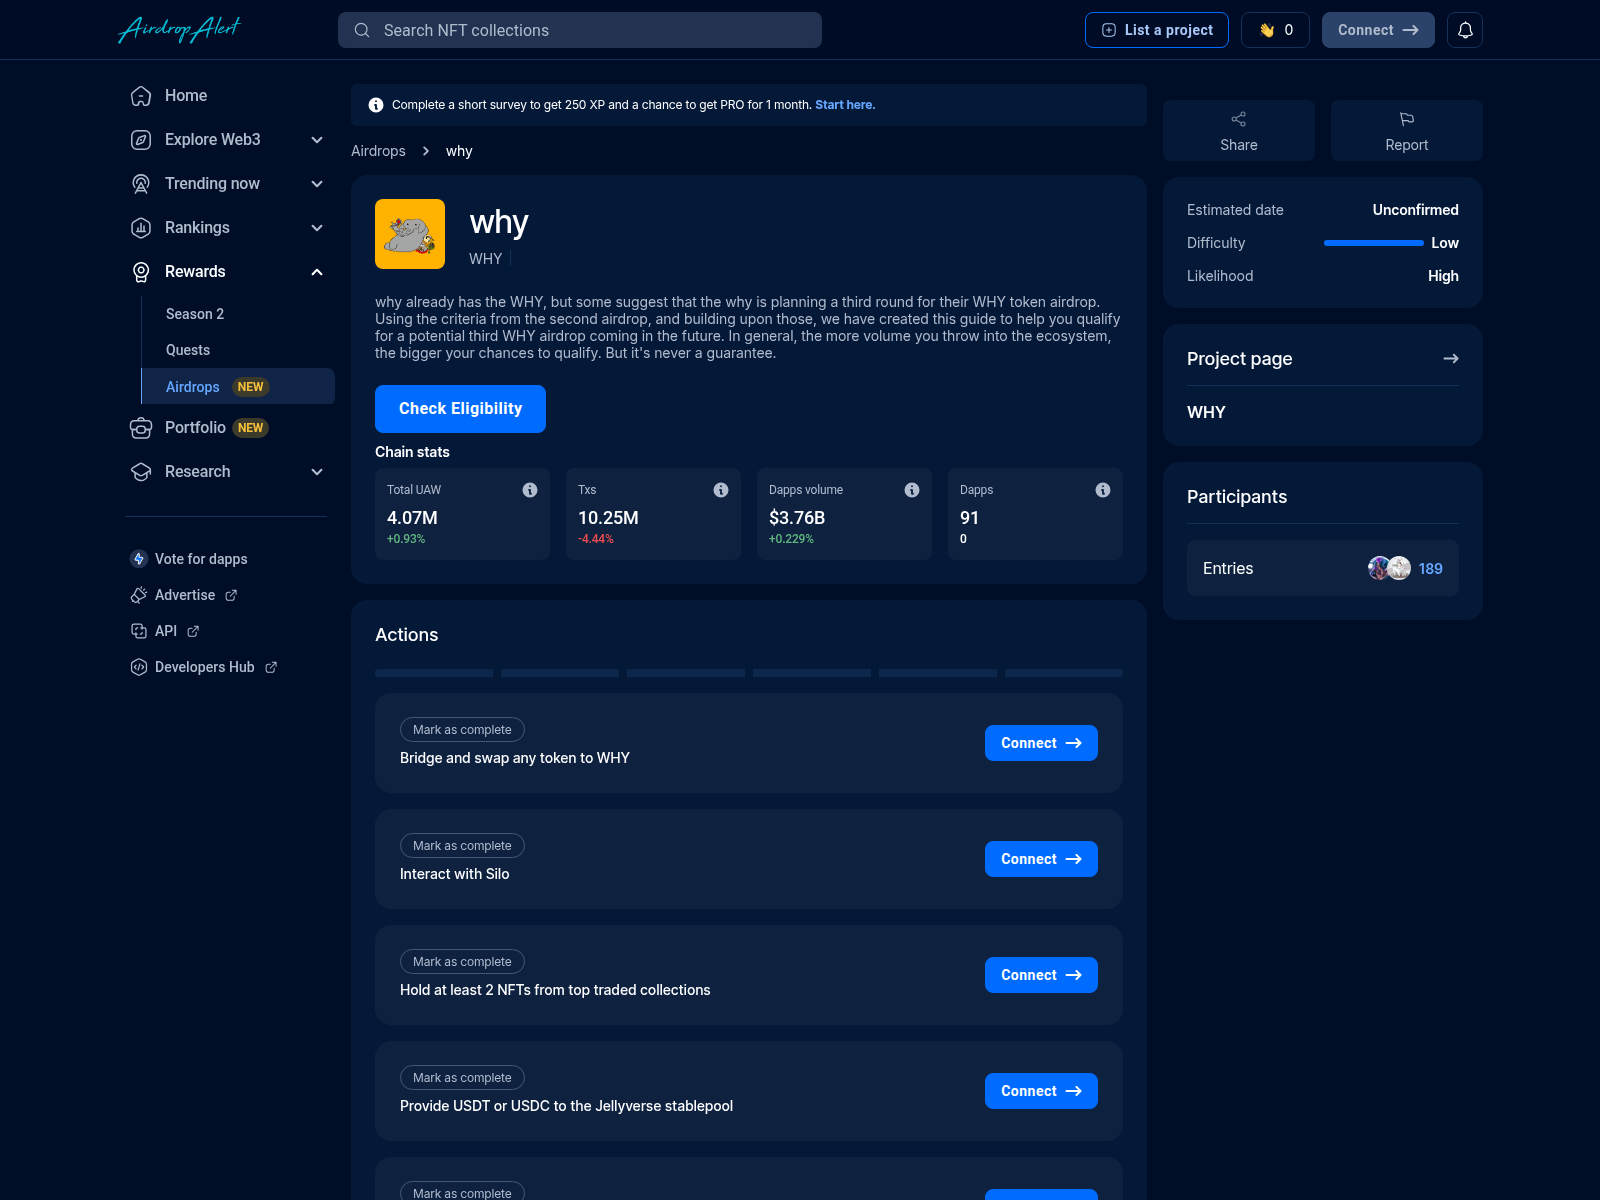
why.airdropalert.cyou
Threat Response Pipeline
How every domain in this hub is verified and how confirmed threats are neutralized. Full pipeline visualization →
Threat Intelligence Checks— every domain is scanned & cross-checked against:
urlscan.ioScreenshot · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ReportCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Security FiltersQuad9 · AdGuard · CleanBrowsingWeb-CheckFull surface scan
 crt.sh
Global Vendor Sync— confirmed detections are pushed to 29 partners:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecSiteReviewAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftTakedown APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ReportHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust