Skip to security report
Recorded security signals
Stored VirusTotal result: 14/92 engines flagged. Analysis time (as stored): 2026-10-28 22:09 UTC. Retrieved (as stored): 2026-11-11 03:54 UTC. Exercise extreme caution — do not enter credentials or personal information.
Were you scammed by this site?Report to authorities
Domain security and threat intelligence
8935qp.com favicon

8935qp.com

In short

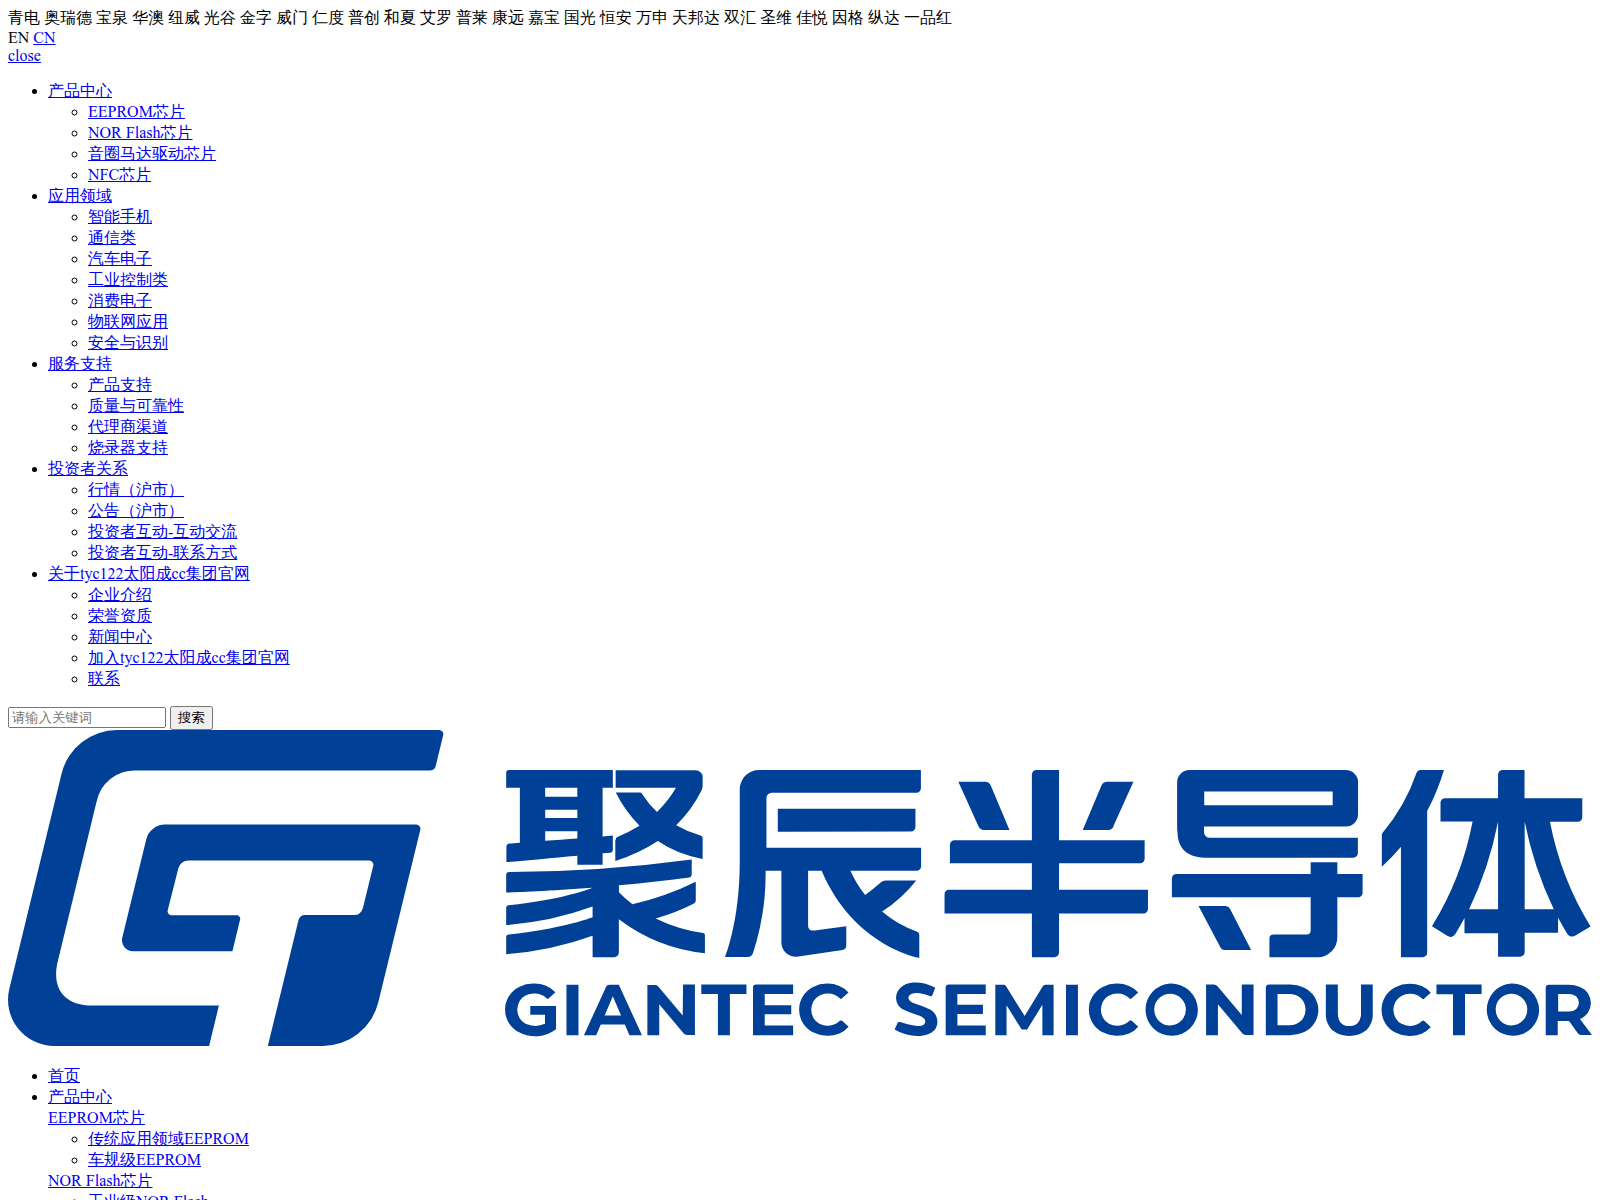
On 2026-11-11, www.8935qp.com displayed a page presenting Giantec Semiconductor branding, with a large blue logo reading "GIANTEC SEMICONDUCTOR" and Chinese characters. The page lists navigation sections in Chinese covering product center items such as EEPROM chips, NOR Flash chips, voice coil motor driver chips and NFC chips, alongside application areas including smartphones, communications, automotive electronics, industrial control, consumer electronics, IoT and security identification.

“中国·44118太阳成城(集团·股份)有限公司-Official”

Registrar
ChinaDominet (HK)
Resolved IP
Hong Kong SAR China82.109.255.179VpsQuan L.L.C.
Registered
Oct 23, 2026
First observed
Nov 11, 2026
PhishDestroy assessment Critical
100/100
Evidence score
Availability Last known active Latest stored reachability observation Observed HTTP probe
VirusTotal detections: 14/92 Young domain: 18 days old Google Safe Browsing: threat flag recorded
VirusTotal
engine detections ·
Google Safe Browsing
URLQuery
detections
OTX
community references
URLScan
engine verdict · score 84
Cloudflare Radar
Page captures
open gallery
Domain age
registered 2026-10-23 according to WHOIS · source data differ
Reports sent
view timeline
OTX: 1 ref Nov 11, 2026 1 Report Sent
X Telegram API

Analysis

Domain summary

PhishDestroy first recorded 8935qp.com on 2026-11-11. Stored VirusTotal result: 14/92 engines flagged. Analysis time (as stored): 2026-10-28 22:09 UTC. Retrieved (as stored): 2026-11-11 03:54 UTC. Google Safe Browsing flags it. Risk: critical (100/100). Registrar: Dominet (HK). Status: Last known active. Hosting: VpsQuan L.L.C. PhishDestroy sent 1 abuse report. Do not enter credentials or connect a wallet.

Critical
Status
Last known active
VirusTotal
14 / 92
Hosting
Hong Kong SAR China82.109.255.179VpsQuan L.L.C.
Registrar
ChinaDominet (HK)
Registered
Oct 23, 2026
OTX
1 community ref
Page captures
5

Capture recorded with this analysis · URLScan · 2026-11-11T03:43:34Z
SHA-256: c4f9777c9d6ba2ec32c81aeb626467f9bf2cdc74de53726b6d1011c144ed8c4a

PhishDestroy analysis, reviewed version

On 2026-11-11, www.8935qp.com displayed a page presenting Giantec Semiconductor branding, with a large blue logo reading "GIANTEC SEMICONDUCTOR" and Chinese characters. The page lists navigation sections in Chinese covering product center items such as EEPROM chips, NOR Flash chips, voice coil motor driver chips and NFC chips, alongside application areas including smartphones, communications, automotive electronics, industrial control, consumer electronics, IoT and security identification.

Further visible sections include service support, investor relations with Shanghai market quotes and announcements, and an about section with company introduction, honors, news and contact links. A keyword search field with a search button appears above the logo, and language options EN and CN are shown at the top of the page.

Source evidenceVirusTotal 14 / 92 · Google Safe Browsing: flagged · OTX 1 references 8 sources

VirusTotal

14 / 92 engine detections

Analysis:
Open report
VirusTotalOriginal source recordObserved: 16 fields

Observed: · Retrieved:

Vendor result counts

Timeout
0
Harmless
46
Malicious
14
Suspicious
0
Undetected
32

Vendor labels

CRDF
malicious
DNS8
phishing
VIPRE
phishing
G-Data
phishing
Lionic
phishing
Sophos
phishing
Webroot
malicious
Fortinet
phishing
SOCRadar
phishing
Seclookup
malicious
BitDefender
phishing
Criminal IP
phishing
alphaMountain.ai
phishing
Google Safe Browsing
phishing

Reputation score

0

Tags

  • dga

Categories

alphaMountain.ai
Phishing, Newly Registered (alphaMountain.ai)

Registrar

Dominet (HK) Limited

Created

Expires

Updated

First seen

DNS records

  • TTL, seconds
    3600
    Type
    NS
    Value
    ns1.domainnamedns.com
  • TTL, seconds
    3600
    Type
    NS
    Value
    ns2.domainnamedns.com
  • TTL, seconds
    600
    Type
    A
    Value
    82.109.255.179
  • TTL, seconds
    3600
    Type
    NS
    Value
    ns3.domainnamedns.com
  • TTL, seconds
    3600
    Type
    NS
    Value
    ns4.domainnamedns.com
  • TTL, seconds
    3600
    Type
    SOA
    Responsible mailbox
    support.namens.net
    Value
    ns1.domainnamedns.com

DNS records observed

JARM fingerprint

3fd3fd0003fd3fd21c42d42d000000bdfc58c9a46434368cf60aa440385763

Certificate

Subject alternative names
  • 12742r.com
  • 210507.com
  • 8269pk.com
  • 8275pk.com
  • 8278pk.com
  • 8305pk.com
  • 8508pk.com
  • 8697qp.com
  • 86eg.com
  • 8760qp.com
Issuer
Let's Encrypt / YR2
Serial
550e0157611ddb9ee7199235a5570b36405
SHA-256
d3266f930cf0dce26835867ad9c1dd3ef61045b4db3021eb5f8999d26f94d40f
Subject
8935qp.com
Valid until
Valid from
Observed at

Registration record

Registrar
Dominet (HK) Limited
Registrar IANA ID
3775
Registrar URL
http://www.alibabacloud.com
Registered
Updated
Expires
Status
  • ok
Nameservers
  • ns1.domainnamedns.com
  • ns2.domainnamedns.com
DNSSEC
unsigned

Registry data (RDAP)

Status
  • active
Registry events
Expiration
Registration
Registrar expiration
Last RDAP database update
Original source fields · JSON
Vendor result counts
{
    "timeout": 0,
    "harmless": 46,
    "malicious": 14,
    "suspicious": 0,
    "undetected": 32
}
Vendor labels
{
    "CRDF": "malicious",
    "DNS8": "phishing",
    "VIPRE": "phishing",
    "G-Data": "phishing",
    "Lionic": "phishing",
    "Sophos": "phishing",
    "Webroot": "malicious",
    "Fortinet": "phishing",
    "SOCRadar": "phishing",
    "Seclookup": "malicious",
    "BitDefender": "phishing",
    "Criminal IP": "phishing",
    "alphaMountain.ai": "phishing",
    "Google Safe Browsing": "phishing"
}
Reputation
0
Tags
[
    "dga"
]
Categories
{
    "alphaMountain.ai": "Phishing, Newly Registered (alphaMountain.ai)"
}
Registrar
Dominet (HK) Limited
Created
2026-10-23T06:53:22Z
Expires
2027-10-23T06:53:22Z
Updated
2026-10-23T06:53:22Z
First seen
2025-08-14T16:04:34Z
DNS records
[
    {
        "ttl": 3600,
        "type": "NS",
        "value": "ns1.domainnamedns.com"
    },
    {
        "ttl": 3600,
        "type": "NS",
        "value": "ns2.domainnamedns.com"
    },
    {
        "ttl": 600,
        "type": "A",
        "value": "82.109.255.179"
    },
    {
        "ttl": 3600,
        "type": "NS",
        "value": "ns3.domainnamedns.com"
    },
    {
        "ttl": 3600,
        "type": "NS",
        "value": "ns4.domainnamedns.com"
    },
    {
        "ttl": 3600,
        "type": "SOA",
        "rname": "support.namens.net",
        "value": "ns1.domainnamedns.com"
    }
]
Dns at
2026-10-28T22:09:52Z
Jarm
3fd3fd0003fd3fd21c42d42d000000bdfc58c9a46434368cf60aa440385763
Certificate
{
    "san": [
        "12742r.com",
        "210507.com",
        "8269pk.com",
        "8275pk.com",
        "8278pk.com",
        "8305pk.com",
        "8508pk.com",
        "8697qp.com",
        "86eg.com",
        "8760qp.com"
    ],
    "issuer": "Let's Encrypt / YR2",
    "serial": "550e0157611ddb9ee7199235a5570b36405",
    "sha256": "d3266f930cf0dce26835867ad9c1dd3ef61045b4db3021eb5f8999d26f94d40f",
    "subject": "8935qp.com",
    "valid_to": "2027-01-23T08:37:01Z",
    "valid_from": "2026-10-25T08:37:02Z",
    "observed_at": "2026-10-28T22:09:52Z"
}
Registration record
{
    "registrar": "Dominet (HK) Limited",
    "registrar_iana_id": "3775",
    "registrar_url": "http://www.alibabacloud.com",
    "created": "2026-10-23T06:53:22Z",
    "updated": "2026-10-23T06:53:22Z",
    "expires": "2027-10-23T06:53:22Z",
    "status": [
        "ok"
    ],
    "nameservers": [
        "ns1.domainnamedns.com",
        "ns2.domainnamedns.com"
    ],
    "dnssec": "unsigned"
}
Registry data
{
    "status": [
        "active"
    ],
    "events": {
        "expiration": "2027-10-23T06:53:22Z",
        "registration": "2026-10-23T06:53:22Z",
        "registrar expiration": "2027-10-23T06:53:22Z",
        "last update of RDAP database": "2026-10-23T06:53:23Z"
    }
}
Separate collector summary

This is a separate stored result. Its counts, vendors and dates do not replace the provider observation above. A retrieval date is not an analysis date.

source
VirusTotal
scope
unknown
result_state
observed
numerator
14
denominator
92
malicious
null
suspicious
null
vendors
["Criminal IP","alphaMountain.ai","BitDefender","CRDF","DNS8","Fortinet","G-Data","Google Safe Browsing","Lionic","Seclookup","SOCRadar","Sophos","VIPRE","Webroot"]
observed_at
2026-10-28 22:09:34
checked_at
2026-11-11 04:54:20
fetched_at
2026-11-11 03:54:20
time_basis
as stored; legacy timezone not established

Cloudflare Radar

Phishing

Open report
Cloudflare RadarOriginal source recordObserved: 15 fields

Observed: · Retrieved:

Report ID

e446db5c-0bd2-4f55-bb7a-74bb1ea14b02

Final URL

https://www.8935qp.com/

HTTP response

200

Redirect type

subdomain

Navigation history

  • URL
    https://8935qp.com/
    Status
    301
  • URL
    http://www.8935qp.com/
    Status
    307
  • URL
    https://www.8935qp.com/
    Status
    200

DOM structure hash

80c943016325a041063ae6b4a5c53787a1c543f8f62847b7eda520dab3c1ee6e

Document hash

6dd24bb72e6bf0b4d93f65efea3ec2268511cce78b7c5e56da95e13dad5ec3b4

Phishing classifier result

  • phishing

Domain risk categories

  • Phishing
  • Security threats
  • CIPA Filter
  • CIPA

Cloudflare Radar rank

Rank range
>200000

DNS records

  • Name
    8935qp.com
    Type
    A
    Value
    82.109.255.179
  • Name
    www.8935qp.com
    Type
    A
    Value
    82.109.255.179

DNSSEC valid

No

IP address

127.0.1.15

127.0.1.15 is not a public internet address. It is the value stored in this source record, not the site's hosting address.

Verdict

Tags
  • phishing
Malicious
Yes
Categories
  • phishing

Registration record

Registrar
Dominet (HK) Limited
Registered
Updated
Expires
Nameservers
  • ns1.domainnamedns.com
  • ns2.domainnamedns.com
Original source fields · JSON
Uuid
e446db5c-0bd2-4f55-bb7a-74bb1ea14b02
Final url
https://www.8935qp.com/
Status
200
Redirected
subdomain
History
[
    {
        "url": "https://8935qp.com/",
        "status": 301
    },
    {
        "url": "http://www.8935qp.com/",
        "status": 307
    },
    {
        "url": "https://www.8935qp.com/",
        "status": 200
    }
]
DOM structure hash
80c943016325a041063ae6b4a5c53787a1c543f8f62847b7eda520dab3c1ee6e
Document hash
6dd24bb72e6bf0b4d93f65efea3ec2268511cce78b7c5e56da95e13dad5ec3b4
Phishing v2
[
    "phishing"
]
Domain risks
[
    "Phishing",
    "Security threats",
    "CIPA Filter",
    "CIPA"
]
Radar rank
{
    "bucket": ">200000"
}
DNS records
[
    {
        "name": "8935qp.com",
        "type": "A",
        "value": "82.109.255.179"
    },
    {
        "name": "www.8935qp.com",
        "type": "A",
        "value": "82.109.255.179"
    }
]
Dnssec valid
false
Ip
127.0.1.15

127.0.1.15 is not a public internet address. It is the value stored in this source record, not the site's hosting address.

Verdict
{
    "tags": [
        "phishing"
    ],
    "malicious": true,
    "categories": [
        "phishing"
    ]
}
Registration record
{
    "registrar": "Dominet (HK) Limited",
    "created": "2026-10-23T06:53:22Z",
    "updated": "2026-10-23T06:53:22Z",
    "expires": "2027-10-23T06:53:22Z",
    "nameservers": [
        "ns1.domainnamedns.com",
        "ns2.domainnamedns.com"
    ]
}
Separate stored summary: Not recorded · observation date not recorded

This summary differs from the dated scan above. It is retained for provenance and does not override the selected source observation.

verdict
null
categories
[]
observed_at
null
source_path
phishdestroy.technologies.cf_radar
scope
Separate stored summary; an absent observation date is not evidence of a clean scan.

Google Safe Browsing

Threat flag recorded

Open report

URLScan

Malicious · engine verdict · score 84

SHA-256 ebefa5e45d837a839b437dc45bf4e711fe7bd65aaf6bfce80cc69606aea029b1

Open report
URLScanOriginal source recordObserved: 22 fields

Observed: · Retrieved:

Report ID

01a1c8b4-0b9a-7318-a522-a1d2ae82930c

Final URL

https://www.8935qp.com/

HTTP response

200

Redirect type

https-only

Redirects

  • To
    https://www.8935qp.com/
    From
    http://www.8935qp.com/
    Status
    307

IP address

82.109.255.179

Contacted domains

  • icon.cnzz.com
  • c.cnzz.com
  • z12.cnzz.com
  • s9.cnzz.com

Contacted IP addresses

  • 220.181.10.16
  • 113.105.138.79
  • 2409:8c20:5c64:2000::5
  • 219.144.78.208
  • 82.109.255.179

Autonomous systems (ASN)

  • 23724
  • 134763
  • 56046
  • 134768
  • 62468

Server countries

  • CN
  • HK

Linked domains

  • www.cnzz.com

Document hash

0427d5cf610e110415874a2bce1d493df6f1d0100c65e44caed633f17d50cfa5

JavaScript globals

  • d
  • _cz_loaded
  • _cz_account
  • _czc
  • _CNZZDbridge_1280670680

Cookies

  • PHPSESSID
  • UM_distinctid
  • CNZZDATA1280670680

TLS session and certificate

Subject alternative names
  • 12742r.com
  • 210507.com
  • 8269pk.com
  • 8275pk.com
  • 8278pk.com
  • 8305pk.com
  • 8508pk.com
  • 8697qp.com
  • 86eg.com
  • 8760qp.com
Cipher
AES_128_GCM
Issuer
YR2
Subject
8935qp.com
Protocol
TLS 1.3
Valid until
Valid from

Domain age, days

2655

Differs from the registration date in WHOIS (2026-10-23), which gives 18 days on the scan date 2026-11-11. The two sources disagree; both values are kept as recorded.

Registered domain age, days

454

Differs from the registration date in WHOIS (2026-10-23), which gives 18 days on the scan date 2026-11-11. The two sources disagree; both values are kept as recorded.

Certificate age, days

16

Certificate validity, days

89

Page requests

67

Provider verdicts

Engine verdict
Tags
  • urlscan-ml
  • urlscan-ml-2aab354
Score
84
Malicious
Yes
Overall verdict
Score
0
Malicious
No

HTTP headers

Server
nginx
Content-type
text/html;charset=utf-8
Strict-transport-security
max-age=31536000
Original source fields · JSON
Uuid
01a1c8b4-0b9a-7318-a522-a1d2ae82930c
Final url
https://www.8935qp.com/
Status
200
Redirected
https-only
Redirects
[
    {
        "to": "https://www.8935qp.com/",
        "from": "http://www.8935qp.com/",
        "status": 307
    }
]
Ip
82.109.255.179
Contacted domains
[
    "icon.cnzz.com",
    "c.cnzz.com",
    "z12.cnzz.com",
    "s9.cnzz.com"
]
Contacted IP addresses
[
    "220.181.10.16",
    "113.105.138.79",
    "2409:8c20:5c64:2000::5",
    "219.144.78.208",
    "82.109.255.179"
]
Asns
[
    "23724",
    "134763",
    "56046",
    "134768",
    "62468"
]
Countries
[
    "CN",
    "HK"
]
Linked domains
[
    "www.cnzz.com"
]
Document hash
0427d5cf610e110415874a2bce1d493df6f1d0100c65e44caed633f17d50cfa5
Globals
[
    "d",
    "_cz_loaded",
    "_cz_account",
    "_czc",
    "_CNZZDbridge_1280670680"
]
Cookies
[
    "PHPSESSID",
    "UM_distinctid",
    "CNZZDATA1280670680"
]
Tls
{
    "san": [
        "12742r.com",
        "210507.com",
        "8269pk.com",
        "8275pk.com",
        "8278pk.com",
        "8305pk.com",
        "8508pk.com",
        "8697qp.com",
        "86eg.com",
        "8760qp.com"
    ],
    "cipher": "AES_128_GCM",
    "issuer": "YR2",
    "subject": "8935qp.com",
    "protocol": "TLS 1.3",
    "valid_to": "2027-01-23T08:37:01Z",
    "valid_from": "2026-10-25T08:37:02Z"
}
Domain age days
2655

Differs from the registration date in WHOIS (2026-10-23), which gives 18 days on the scan date 2026-11-11. The two sources disagree; both values are kept as recorded.

Apex age days
454

Differs from the registration date in WHOIS (2026-10-23), which gives 18 days on the scan date 2026-11-11. The two sources disagree; both values are kept as recorded.

Tls age days
16
Tls valid days
89
Requests
67
Provider verdicts
{
    "engines": {
        "tags": [
            "urlscan-ml",
            "urlscan-ml-2aab354"
        ],
        "score": 84,
        "malicious": true
    },
    "overall": {
        "score": 0,
        "malicious": false
    }
}
HTTP headers
{
    "server": "nginx",
    "content-type": "text/html;charset=utf-8",
    "strict-transport-security": "max-age=31536000"
}
Separate monitor record · date not recorded

Separate stored monitor snapshot; does not replace the primary report record or establish current availability.

record_source
domain_monitor.urlscan
uuid
01a172b8-f9cb-751c-a3c0-a301dd6d2810
score
null
malicious
null
result_at
null
enriched_at
null
source_timestamps
{"urlscan_result_at":null,"urlscan_enriched_at":null}
timestamp_basis
Europe/Berlin, as used by the existing report; source timestamps are retained verbatim

OTX

1 community reference

Open report

PhishDestroy DOM

15 / 100 · heuristic score · 0 brand references · 0 classifications

Open report

PhishDestroy narrative

Narrative generation metadata

Open report
Title, description and generation record

The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.

ai_title
8935qp.com: Recorded Giantec Semiconductor navigation page
ai_description
PhishDestroy records 8935qp.com as showing a Giantec Semiconductor navigation page with product, application, support and investor relations links.
ai_summary
On 2026-11-11, www.8935qp.com displayed a page presenting Giantec Semiconductor branding, with a large blue logo reading "GIANTEC SEMICONDUCTOR" and Chinese characters. The page lists navigation sections in Chinese covering product center items such as EEPROM chips, NOR Flash chips, voice coil motor driver chips and NFC chips, alongside application areas including smartphones, communications, automotive electronics, industrial control, consumer electronics, IoT and security identification. Further visible sections include service support, investor relations with Shanghai market quotes and announcements, and an about section with company introduction, honors, news and contact links. A keyword search field with a search button appears above the logo, and language options EN and CN are shown at the top of the page.
ai_generated_by
threat-v6-mimo
ai_generated_at
2026-11-11 04:48:29
revision
c81408fff9e543c2a2addbd314f3042a16ff58a6a9b3209c1f0f07548b4f22ea
mode
reviewed
interpretation
Selected public package; text generation time is separate from source observation dates.

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Collected source details

Stored page, network and scanner observations, grouped by source and observation time.

Every stored field, with its source and date
Website checksOriginal source recordRetrieved: 19 fields

Mail configuration

SPF lookups
0

Protective DNS results

Resolvers checked
12
Blocked by
  • CloudFlare Family
Blocking resolvers
1

Web archive observations

Last observation
First observation
Recorded changes
1
Archived days
2
Snapshots per day
0.24
Average page size, bytes
8266

Page title and metadata

Page title
中国·44118太阳成城(集团·股份)有限公司-Official
Keywords
tyc122太阳成cc集团官网,太阳122cc官方集团可靠吗,tyc122太阳成cc集团
Description
●官方直营品牌网站●贵宾官方旗舰站:www.8935qp.com tyc122太阳成cc集团官网,太阳122cc官方集团可靠吗,tyc122太阳成cc集团 热门娱乐平台专注打造高品质娱乐服务,支持多端同步体验,操作流畅稳定,首充加赠162元奖励,打造安全稳定的互动娱乐环境,满足不同玩家的娱乐需求。
Canonical URL
https://www.8935qp.com/

Trackers

Requests
66
Observed services
  • Name
    Baidu Ads
    Company
    Baidu
    Country
    CN
    Category
    Advertising
    Requests
    1
  • Name
    Microsoft Clarity
    Company
    Microsoft
    Country
    US
    Category
    Site Analytics
    Requests
    1
  • Name
    Umeng
    Company
    Umeng
    Country
    CN
    Category
    Site Analytics
    Requests
    1

HTTP response

Reachable
Yes
HTTP status
301
Request timings, ms
DNS
432
TLS
188
Waiting
297
Connection
184
Download
0
Response time, ms
1101

TLS connection

ALPN
h2
Cipher
TLS_AES_256_GCM_SHA384
Protocol
TLSv1.3
Supported versions
  • TLSv1.2
  • TLSv1.3
Certificate authorized
Yes
Forward secrecy
Yes

Ports

Open ports
  • 80
  • 443

Carbon estimate

Bytes
71092
CO₂, grams
0.0026
Cleaner than, %
29

DNS servers

Nameservers
  • IP address
    216.106.185.75
    Host
    ns1.domainnamedns.com
  • IP address
    67.220.72.51
    Host
    ns4.domainnamedns.com
  • IP address
    38.114.114.183
    Host
    ns2.domainnamedns.com
  • IP address
    54.151.142.119
    Host
    ns3.domainnamedns.com
DNS zone
8935qp.com

Cookies

Cookies
  • Name
    PHPSESSID
    Session cookie
    Yes
  • Name
    PHPSESSID
    Session cookie
    Yes

Location

IP address
82.109.255.179
ASN
62468
Organization
VpsQuan L.L.C.
City
Hong Kong
Country
HK

TLS certificate

Issuer
Let's Encrypt / YR2
Subject
8935qp.com

DNS records

A
  • 82.109.255.179
NS
  • ns1.domainnamedns.com
  • ns4.domainnamedns.com
  • ns3.domainnamedns.com
  • ns2.domainnamedns.com
SOA
Primary nameserver
ns1.domainnamedns.com
Hostmaster
support.namens.net
Serial
1792911657
Refresh, seconds
3600
Retry, seconds
1800
Expiry, seconds
1209600
Minimum TTL, seconds
180

DNSSEC

DS record
No
RRSIG
No
DNSKEY
No

HSTS

Header value
max-age=31536000
Observation
HSTS header does not include all subdomains.

IP lookup

IP address
82.109.255.179
IP version
4

Technology stack

Technologies
  • PHP
  • jQuery
  • CNZZ
  • Baidu Analytics (百度统计)
  • Microsoft Clarity

Registration record

Registrar
Dominet (HK) Limited
Registered
Updated
Expires
Status
  • ok https://icann.org/epp
Nameservers
  • ns1.domainnamedns.com
  • ns2.domainnamedns.com
Original source fields · JSON
Mail configuration
{
    "spf_lookups": 0
}
Protective DNS results
{
    "resolvers": 12,
    "blocked_by": [
        "CloudFlare Family"
    ],
    "blocked_count": 1
}
Web archive observations
{
    "last": "2026-01-02T16:18:35Z",
    "first": "2025-12-29T11:01:14Z",
    "changes": 1,
    "days_archived": 2,
    "scans_per_day": 0.24,
    "avg_page_bytes": 8266
}
Page title and metadata
{
    "title": "中国·44118太阳成城(集团·股份)有限公司-Official",
    "keywords": "tyc122太阳成cc集团官网,太阳122cc官方集团可靠吗,tyc122太阳成cc集团",
    "description": "●官方直营品牌网站●贵宾官方旗舰站:www.8935qp.com tyc122太阳成cc集团官网,太阳122cc官方集团可靠吗,tyc122太阳成cc集团 热门娱乐平台专注打造高品质娱乐服务,支持多端同步体验,操作流畅稳定,首充加赠162元奖励,打造安全稳定的互动娱乐环境,满足不同玩家的娱乐需求。",
    "canonicalUrl": "https://www.8935qp.com/"
}
Trackers
{
    "requests": 66,
    "trackers": [
        {
            "name": "Baidu Ads",
            "company": "Baidu",
            "country": "CN",
            "category": "Advertising",
            "requests": 1
        },
        {
            "name": "Microsoft Clarity",
            "company": "Microsoft",
            "country": "US",
            "category": "Site Analytics",
            "requests": 1
        },
        {
            "name": "Umeng",
            "company": "Umeng",
            "country": "CN",
            "category": "Site Analytics",
            "requests": 1
        }
    ]
}
Status
{
    "up": true,
    "code": 301,
    "timings": {
        "dns": 432,
        "tls": 188,
        "wait": 297,
        "connect": 184,
        "download": 0
    },
    "response_ms": 1101
}
TLS connection
{
    "alpn": "h2",
    "cipher": "TLS_AES_256_GCM_SHA384",
    "protocol": "TLSv1.3",
    "versions": [
        "TLSv1.2",
        "TLSv1.3"
    ],
    "authorized": true,
    "forward_secrecy": true
}
Ports
{
    "open": [
        80,
        443
    ]
}
Carbon
{
    "bytes": 71092,
    "co2_grams": 0.0026,
    "cleaner_than": 29
}
Dns server
{
    "ns": [
        {
            "ip": "216.106.185.75",
            "host": "ns1.domainnamedns.com"
        },
        {
            "ip": "67.220.72.51",
            "host": "ns4.domainnamedns.com"
        },
        {
            "ip": "38.114.114.183",
            "host": "ns2.domainnamedns.com"
        },
        {
            "ip": "54.151.142.119",
            "host": "ns3.domainnamedns.com"
        }
    ],
    "zone": "8935qp.com"
}
Cookies
{
    "cookies": [
        {
            "name": "PHPSESSID",
            "session": true
        },
        {
            "name": "PHPSESSID",
            "session": true
        }
    ]
}
Location
{
    "ip": "82.109.255.179",
    "asn": "62468",
    "org": "VpsQuan L.L.C.",
    "city": "Hong Kong",
    "country": "HK"
}
Ssl
{
    "issuer": "Let's Encrypt / YR2",
    "subject": "8935qp.com"
}
DNS records
{
    "A": [
        "82.109.255.179"
    ],
    "NS": [
        "ns1.domainnamedns.com",
        "ns4.domainnamedns.com",
        "ns3.domainnamedns.com",
        "ns2.domainnamedns.com"
    ],
    "SOA": "{\"nsname\": \"ns1.domainnamedns.com\", \"hostmaster\": \"support.namens.net\", \"serial\": 1792911657, \"refresh\": 3600, \"retry\": 1800, \"expire\": 1209600, \"minttl\": 180}"
}
Dnssec
{
    "ds": false,
    "rrsig": false,
    "dnskey": false
}
Hsts
{
    "header": "max-age=31536000",
    "message": "HSTS header does not include all subdomains."
}
Get ip
{
    "ip": "82.109.255.179",
    "family": 4
}
Tech stack
{
    "technologies": [
        "PHP",
        "jQuery",
        "CNZZ",
        "Baidu Analytics (百度统计)",
        "Microsoft Clarity"
    ]
}
Registration record
{
    "registrar": "Dominet (HK) Limited",
    "created": "2026-10-23T06:53:22Z",
    "updated": "2026-10-23T06:53:22Z",
    "expires": "2027-10-23T06:53:22Z",
    "status": [
        "ok https://icann.org/epp"
    ],
    "nameservers": [
        "ns1.domainnamedns.com",
        "ns2.domainnamedns.com"
    ]
}

Questions about 8935qp.com

Is 8935qp.com legit?

PhishDestroy rates 8935qp.com as critical risk (100/100) from the recorded evidence; it was first recorded on 2026-11-11. Stored VirusTotal result: 14/92 engines flagged. Analysis time (as stored): 2026-10-28 22:09 UTC. Retrieved (as stored): 2026-11-11 03:54 UTC. Google Safe Browsing flags it. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.

Is 8935qp.com safe to connect a wallet?

This report does not record which wallet requests 8935qp.com makes. Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions there. A confirmed blockchain transaction cannot be reversed.

What should I do if I used 8935qp.com?

It depends on what you did. If you entered a password, change it, and also on every other site where you used the same password; turn on two-factor authentication where it is offered. If you paid or gave card or bank details, contact your bank or payment service through the contacts on your card or its official website. If you only connected a wallet, disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds. If you signed a token approval or permit, revoke it with a token-approval checker. If you shared a seed phrase or private key, treat the wallet as compromised and move the remaining funds to a new wallet with a new seed phrase. If you downloaded a file, do not open it and scan the device with security software. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority; a report does not guarantee that money is returned. Step-by-step help: emergency guide.

Explore

Blocklist matchesPhishDestroy · no match in the other 11 1
PhishDestroy PhishDestroy list View source

Last checked

Stored Capture · 5 captures

All capture links and hashes (5)

Domain details

Domain
URLScan verdict Analysis completed score 0 Engine verdict: malicious · score 84 report ↗
Google Safe Browsing Flagged Social engineering checked Nov 11, 2026
IP Reputation Hong Kong SAR China82.109.255.179 abuse score 0/100 0 reports checked Nov 11, 2026
Registrar Dominet (HK) CN(CN)
RegistrationCreated Oct 23, 2026 (18d · Very New!) — Expires Oct 23, 2027
Registrant countryChina VirusTotal WHOIS
Registrant6aacf85c31f44448s@ VirusTotal WHOIS
WHOIS statusok
HTTP Status301 Moved Permanently
LLM Report Plain-text dossier structured for AI agents
Technical detailsProvenance & timestamps
First DetectedNov 11, 2026
DOM Analysisanalyzed Nov 11, 2026score 15/100
Submitted URLhttp://www.8935qp.com/
Case ID
Observed page title
中国·44118太阳成城(集团·股份)有限公司-Official
TLS Certificate
Issued by YR2 · stored validity ends in 73 days

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
Hong Kong SAR China82.109.255.179
Network ASN
AS62468
Organization
VpsQuan L.L.C.
Observed location
Hong Kong SAR ChinaHong Kong, HK
Server header
nginx

Nameservers 4

  • ns1.domainnamedns.com
  • ns2.domainnamedns.com
  • ns3.domainnamedns.com
  • ns4.domainnamedns.com

SOA

  • nsname: ns1.domainnamedns.com
  • hostmaster: support.namens.net
  • serial: 1792911657
  • refresh: 3600
  • retry: 1800
  • expire: 1209600
  • minttl: 180

Registrar abuse contact VirusTotal WHOIS

Location describes the IP network.

TLS certificate

Issuer
YR2
Valid from
2026-10-25 08:37:02
Valid until
2027-01-23 08:37:01
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection source
PhishDestroy collector
Certificate names · 10 SANs
  • 12742r.com
  • 210507.com
  • 8269pk.com
  • 8275pk.com
  • 8278pk.com
  • 8305pk.com
  • 8508pk.com
  • 8697qp.com
  • 86eg.com
  • 8760qp.com

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Report This Domain Submit evidence & help protect others

VirusTotal Analysis

14 / 92 security vendors flagged this domain
View on VT
Last analyzed First positive detection
CRDF
DNS8
VIPRE
G-Data
Lionic
Sophos
Webroot
Fortinet
SOCRadar
Seclookup
BitDefender
Criminal IP
alphaMountain.ai
Google Safe Browsing

Archived Evidence

Wayback Machine Snapshot
View Archive

Saved snapshots 1

All stored data98

Detections & threat intelligence

VirusTotal detections
14
VirusTotal vendors
Criminal IP, alphaMountain.ai, BitDefender, CRDF, DNS8, Fortinet, G-Data, Google Safe Browsing, Lionic, Seclookup, SOCRadar, Sophos, VIPRE, Webroot
VirusTotal checked at
2026-11-11 04:54:20
Safe Browsing flagged
Yes
Safe Browsing threats
SOCIAL_ENGINEERING
Safe Browsing checked at
2026-11-11 04:36:56
Blocklist hits
PhishDestroy
Blocklist count
1
Blocklist checked at
2026-11-11 04:20:01
Drainer checked at
2026-11-11 04:57:57
URLScan ID
01a1c8b4-0b9a-7318-a522-a1d2ae82930c
Case ID
PD-8781AA3C9F72097473C4
Report count
1
User reports
0
Report status
sent
URLScan checked at
2026-11-11 04:45:27
URLQuery detections
2
URLQuery DOM hash
domhash6c21f228e1268722dc16d1665aa7dc24
OTX pulses
1
OTX malware
0
OTX checked
2026-11-11 04:38:20
DOM risk score
15
VirusTotal total scanners
92
Abuse score
0
Abuse reports
0
Abuse checked at
2026-11-11 06:00:13
Wallet extracted at
2026-11-11 06:00:08
URLScan score
0
URLScan malicious
No
URLScan result at
2026-11-11 05:30:17
VirusTotal result state
observed
VirusTotal fetched at
2026-11-11 03:54:20
VirusTotal observed at
2026-10-28 22:09:34
URLScan captured at
2026-11-11 03:43:35
URLScan result ID
01a1c8b4-0b9a-7318-a522-a1d2ae82930c
URLScan payload hash
ebefa5e45d837a839b437dc45bf4e711fe7bd65aaf6bfce80cc69606aea029b1
URLScan evidence
{ "v": 1, "ip": "82.109.255.179", "asn": "AS62468", "ips": [ "220.181.10.16", "113.105.138…
{
    "v": 1,
    "ip": "82.109.255.179",
    "asn": "AS62468",
    "ips": [
        "220.181.10.16",
        "113.105.138.79",
        "2409:8c20:5c64:2000::5",
        "219.144.78.208",
        "82.109.255.179"
    ],
    "tls": {
        "san": [
            "12742r.com",
            "210507.com",
            "8269pk.com",
            "8275pk.com",
            "8278pk.com",
            "8305pk.com",
            "8508pk.com",
            "8697qp.com",
            "86eg.com",
            "8760qp.com"
        ],
        "cipher": "AES_128_GCM",
        "issuer": "YR2",
        "subject": "8935qp.com",
        "protocol": "TLS 1.3",
        "valid_to": "2027-01-23T08:37:01Z",
        "valid_from": "2026-10-25T08:37:02Z"
    },
    "asns": [
        "23724",
        "134763",
        "56046",
        "134768",
        "62468"
    ],
    "city": "Hong Kong",
    "uuid": "01a1c8b4-0b9a-7318-a522-a1d2ae82930c",
    "score": 0,
    "title": "中国·44118太阳成城(集团·股份)有限公司-Official",
    "server": "nginx",
    "status": 200,
    "cookies": [
        "PHPSESSID",
        "UM_distinctid",
        "CNZZDATA1280670680"
    ],
    "country": "HK",
    "domains": [
        "icon.cnzz.com",
        "c.cnzz.com",
        "z12.cnzz.com",
        "s9.cnzz.com"
    ],
    "globals": [
        "d",
        "_cz_loaded",
        "_cz_account",
        "_czc",
        "_CNZZDbridge_1280670680"
    ],
    "headers": {
        "server": "nginx",
        "content-type": "text/html;charset=utf-8",
        "strict-transport-security": "max-age=31536000"
    },
    "asn_name": "HKCLOUDX - VpsQuan L.L.C., US",
    "doc_hash": "0427d5cf610e110415874a2bce1d493df6f1d0100c65e44caed633f17d50cfa5",
    "requests": 67,
    "task_url": "http://www.8935qp.com/",
    "verdicts": {
        "engines": {
            "tags": [
                "urlscan-ml",
                "urlscan-ml-2aab354"
            ],
            "score": 84,
            "malicious": true
        },
        "overall": {
            "score": 0,
            "malicious": false
        }
    },
    "countries": [
        "CN",
        "HK"
    ],
    "final_url": "https://www.8935qp.com/",
    "malicious": false,
    "redirects": [
        {
            "to": "https://www.8935qp.com/",
            "from": "http://www.8935qp.com/",
            "status": 307
        }
    ],
    "fetched_at": "2026-11-11T03:46:16Z",
    "redirected": "https-only",
    "scanned_at": "2026-11-11T03:43:34Z",
    "tls_issuer": "YR2",
    "captured_at": "2026-11-11 03:43:34.532000",
    "task_domain": "www.8935qp.com",
    "link_domains": [
        "www.cnzz.com"
    ],
    "payload_hash": "ebefa5e45d837a839b437dc45bf4e711fe7bd65aaf6bfce80cc69606aea029b1",
    "technologies": [
        "CNZZ",
        "jQuery",
        "Mixitup"
    ],
    "tls_age_days": 16,
    "apex_age_days": 454,
    "tls_valid_days": 89,
    "domain_age_days": 2655
}
Last reported at
2026-11-11 03:57:07
Last report receipt ID
84668

Network, hosting & TLS

IP address
82.109.255.179
Nameservers
ns1.domainnamedns.com ns2.domainnamedns.com ns3.domainnamedns.com ns4.domainnamedns.com
DNS resolves
Yes
HTTP status
301
IP country
HK
IP city
Hong Kong
IP org
VpsQuan L.L.C.
TLS issuer
YR2
TLS SANs
12742r.com, 210507.com, 8269pk.com, 8275pk.com, 8278pk.com, 8305pk.com, 8508pk.com, 8697qp.com, 86eg.com, 8760qp.com
TLS valid from
2026-10-25 08:37:02
TLS valid to
2027-01-23 08:37:01
ASN
62468
ASN name
VpsQuan L.L.C.
Server header
nginx
CDN
No
DNS state
stale

Registration

Registrar
Dominet (HK) Limited
Registrar country
CN
WHOIS emails
report@abuseradar.com, domainabuse@service.aliyun.com
Creation date
2026-10-23 06:53:22
Expiration date
2027-10-23 06:53:22
Registrar action verified
No
Registrar action linked to report
No
Registration state
unknown

Status, takedown & timeline

Detected at
2026-11-11 04:33:52
Reported at
2026-11-11 03:57:07
Status
enriched
Site status
alive
Last alive
2026-11-11 04:45:27
Last checked
2026-11-11 04:45:27
Created at
2026-11-11 04:35:22
Updated at
2026-11-11 06:02:47
Outcome state
unknown
Outcome cause
stale_current_evidence
Outcome actor type
unknown
Outcome confidence
0
Outcome evidence source
current_state_backfill
Outcome evidence at
2026-11-11 04:38:17.727998
Outcome evidence
{ "observed_at": null, "dns_evidence_stale": true, "http_evidence_stale": true }…
{
    "observed_at": null,
    "dns_evidence_stale": true,
    "http_evidence_stale": true
}
Outcome evidence at (UTC)
2026-11-11 03:38:17.727998
Availability state
unknown
Content state
unknown
Shutdown time basis
inconclusive
Shutdown time precision
open

Page & captures

Source URL
http://www.8935qp.com/
Page title
中国·44118太阳成城(集团·股份)有限公司-Official
Technologies
{ "cf": { "v": 1, "ip": "127.0.1.15", "dns": [ { "name": "8935qp.com", "type": "A", "value…
{
    "cf": {
        "v": 1,
        "ip": "127.0.1.15",
        "dns": [
            {
                "name": "8935qp.com",
                "type": "A",
                "value": "82.109.255.179"
            },
            {
                "name": "www.8935qp.com",
                "type": "A",
                "value": "82.109.255.179"
            }
        ],
        "uuid": "e446db5c-0bd2-4f55-bb7a-74bb1ea14b02",
        "whois": {
            "created": "2026-10-23T06:53:22Z",
            "expires": "2027-10-23T06:53:22Z",
            "updated": "2026-10-23T06:53:22Z",
            "registrar": "Dominet (HK) Limited",
            "nameservers": [
                "ns1.domainnamedns.com",
                "ns2.domainnamedns.com"
            ]
        },
        "status": 200,
        "history": [
            {
                "url": "https://8935qp.com/",
                "status": 301
            },
            {
                "url": "http://www.8935qp.com/",
                "status": 307
            },
            {
                "url": "https://www.8935qp.com/",
                "status": 200
            }
        ],
        "verdict": {
            "tags": [
                "phishing"
            ],
            "malicious": true,
            "categories": [
                "phishing"
            ]
        },
        "doc_hash": "6dd24bb72e6bf0b4d93f65efea3ec2268511cce78b7c5e56da95e13dad5ec3b4",
        "dom_hash": "80c943016325a041063ae6b4a5c53787a1c543f8f62847b7eda520dab3c1ee6e",
        "task_url": "https://8935qp.com/",
        "final_url": "https://www.8935qp.com/",
        "fetched_at": "2026-11-11T03:46:22Z",
        "radar_rank": {
            "bucket": ">200000"
        },
        "redirected": "subdomain",
        "scanned_at": "2026-11-11T03:38:16Z",
        "phishing_v2": [
            "phishing"
        ],
        "task_domain": "8935qp.com",
        "dnssec_valid": false,
        "domain_risks": [
            "Phishing",
            "Security threats",
            "CIPA Filter",
            "CIPA"
        ]
    },
    "vt": {
        "v": 1,
        "dns": [
            {
                "ttl": 3600,
                "type": "NS",
                "value": "ns1.domainnamedns.com"
            },
            {
                "ttl": 3600,
                "type": "NS",
                "value": "ns2.domainnamedns.com"
            },
            {
                "ttl": 600,
                "type": "A",
                "value": "82.109.255.179"
            },
            {
                "ttl": 3600,
                "type": "NS",
                "value": "ns3.domainnamedns.com"
            },
            {
                "ttl": 3600,
                "type": "NS",
                "value": "ns4.domainnamedns.com"
            },
            {
                "ttl": 3600,
                "type": "SOA",
                "rname": "support.namens.net",
                "value": "ns1.domainnamedns.com"
            }
        ],
        "cert": {
            "san": [
                "12742r.com",
                "210507.com",
                "8269pk.com",
                "8275pk.com",
                "8278pk.com",
                "8305pk.com",
                "8508pk.com",
                "8697qp.com",
                "86eg.com",
                "8760qp.com"
            ],
            "issuer": "Let's Encrypt / YR2",
            "serial": "550e0157611ddb9ee7199235a5570b36405",
            "sha256": "d3266f930cf0dce26835867ad9c1dd3ef61045b4db3021eb5f8999d26f94d40f",
            "subject": "8935qp.com",
            "valid_to": "2027-01-23T08:37:01Z",
            "valid_from": "2026-10-25T08:37:02Z",
            "observed_at": "2026-10-28T22:09:52Z"
        },
        "jarm": "3fd3fd0003fd3fd21c42d42d000000bdfc58c9a46434368cf60aa440385763",
        "rdap": {
            "events": {
                "expiration": "2027-10-23T06:53:22Z",
                "registration": "2026-10-23T06:53:22Z",
                "registrar expiration": "2027-10-23T06:53:22Z",
                "last update of RDAP database": "2026-10-23T06:53:23Z"
            },
            "status": [
                "active"
            ]
        },
        "tags": [
            "dga"
        ],
        "stats": {
            "timeout": 0,
            "harmless": 46,
            "malicious": 14,
            "suspicious": 0,
            "undetected": 32
        },
        "whois": {
            "dnssec": "unsigned",
            "status": [
                "ok"
            ],
            "created": "2026-10-23T06:53:22Z",
            "expires": "2027-10-23T06:53:22Z",
            "updated": "2026-10-23T06:53:22Z",
            "registrar": "Dominet (HK) Limited",
            "abuse_email": "domainabuse@service.aliyun.com",
            "abuse_phone": "+86.95187",
            "nameservers": [
                "ns1.domainnamedns.com",
                "ns2.domainnamedns.com"
            ],
            "registrar_url": "http://www.alibabacloud.com",
            "registrant_email": "6aacf85c31f44448s@",
            "registrant_state": "c2f0b1ae781a52ab",
            "registrar_iana_id": "3775",
            "registrant_country": "CN"
        },
        "dns_at": "2026-10-28T22:09:52Z",
        "created": "2026-10-23T06:53:22Z",
        "expires": "2027-10-23T06:53:22Z",
        "updated": "2026-10-23T06:53:22Z",
        "registrar": "Dominet (HK) Limited",
        "categories": {
            "alphaMountain.ai": "Phishing, Newly Registered (alphaMountain.ai)"
        },
        "detections": {
            "CRDF": "malicious",
            "DNS8": "phishing",
            "VIPRE": "phishing",
            "G-Data": "phishing",
            "Lionic": "phishing",
            "Sophos": "phishing",
            "Webroot": "malicious",
            "Fortinet": "phishing",
            "SOCRadar": "phishing",
            "Seclookup": "malicious",
            "BitDefender": "phishing",
            "Criminal IP": "phishing",
            "alphaMountain.ai": "phishing",
            "Google Safe Browsing": "phishing"
        },
        "fetched_at": "2026-11-11T03:54:19Z",
        "first_seen": "2025-08-14T16:04:34Z",
        "reputation": 0,
        "analysis_at": "2026-10-28T22:09:34Z"
    },
    "shots": {
        "v": 1,
        "cf": {
            "url": "https://screenshots.phishdestroy.io/cf/e446db5c-0bd2-4f55-bb7a-74bb1ea14b02.png",
            "scan": "e446db5c-0bd2-4f55-bb7a-74bb1ea14b02",
            "bytes": 318595,
            "sha256": "8a21972ec6d977a3035e13a0e087e7b480589783c43e8f7a9e82fde16c549072"
        },
        "urlscan": {
            "url": "https://screenshots.phishdestroy.io/us/01a1c8b4-0b9a-7318-a522-a1d2ae82930c.png",
            "uuid": "01a1c8b4-0b9a-7318-a522-a1d2ae82930c",
            "bytes": 59882,
            "sha256": "c4f9777c9d6ba2ec32c81aeb626467f9bf2cdc74de53726b6d1011c144ed8c4a"
        },
        "urlquery": {
            "url": "https://screenshots.phishdestroy.io/uq/c6282b6d-2154-4563-8a92-558002fcbd30.png",
            "bytes": 49879,
            "report": "c6282b6d-2154-4563-8a92-558002fcbd30",
            "sha256": "40c3d74a7055026f7b4a587162f578ec98f4b03720aecd0efd93a678130b51e0"
        },
        "fetched_at": "2026-11-11T04:42:24Z",
        "urlscan_history": {
            "scans": [
                {
                    "at": "2026-08-08T00:00:16Z",
                    "url": "https://screenshots.phishdestroy.io/us/019fdeab-7ce3-7782-af52-27adcbb3ed95.png",
                    "uuid": "019fdeab-7ce3-7782-af52-27adcbb3ed95",
                    "bytes": 19547,
                    "sha256": "d8dd53b53ad61438e6f1d8249fed1720644fbd69e20dc69166b1501e6d729a60",
                    "status": 403,
                    "page_url": "https://www.8935qp.com/login",
                    "task_domain": "www.8935qp.com"
                },
                {
                    "at": "2026-08-08T04:17:22Z",
                    "url": "https://screenshots.phishdestroy.io/us/019fdf96-d783-76bf-a5eb-fb2214ff5f63.png",
                    "uuid": "019fdf96-d783-76bf-a5eb-fb2214ff5f63",
                    "bytes": 14584,
                    "sha256": "f8d0b106410344da45f6d2b47a15f0e5ba577cd253eb25847ff7c7eaf6133982",
                    "status": 403,
                    "page_url": "https://www.8935qp.com/login",
                    "task_domain": "www.8935qp.com"
                },
                {
                    "at": "2026-10-25T11:03:21Z",
                    "uuid": "01a172b8-f9cb-751c-a3c0-a301dd6d2810",
                    "status": 200,
                    "country": "HK",
                    "missing": 404,
                    "page_url": "https://www.8935qp.com/",
                    "task_domain": "www.8935qp.com"
                }
            ],
            "total": 4
        }
    },
    "urlscan": {
        "v": 1,
        "ip": "82.109.255.179",
        "ips": [
            "220.181.10.16",
            "113.105.138.79",
            "2409:8c20:5c64:2000::5",
            "219.144.78.208",
            "82.109.255.179"
        ],
        "tls": {
            "san": [
                "12742r.com",
                "210507.com",
                "8269pk.com",
                "8275pk.com",
                "8278pk.com",
                "8305pk.com",
                "8508pk.com",
                "8697qp.com",
                "86eg.com",
                "8760qp.com"
            ],
            "cipher": "AES_128_GCM",
            "issuer": "YR2",
            "subject": "8935qp.com",
            "protocol": "TLS 1.3",
            "valid_to": "2027-01-23T08:37:01Z",
            "valid_from": "2026-10-25T08:37:02Z"
        },
        "asns": [
            "23724",
            "134763",
            "56046",
            "134768",
            "62468"
        ],
        "uuid": "01a1c8b4-0b9a-7318-a522-a1d2ae82930c",
        "status": 200,
        "cookies": [
            "PHPSESSID",
            "UM_distinctid",
            "CNZZDATA1280670680"
        ],
        "domains": [
            "icon.cnzz.com",
            "c.cnzz.com",
            "z12.cnzz.com",
            "s9.cnzz.com"
        ],
        "globals": [
            "d",
            "_cz_loaded",
            "_cz_account",
            "_czc",
            "_CNZZDbridge_1280670680"
        ],
        "headers": {
            "server": "nginx",
            "content-type": "text/html;charset=utf-8",
            "strict-transport-security": "max-age=31536000"
        },
        "doc_hash": "0427d5cf610e110415874a2bce1d493df6f1d0100c65e44caed633f17d50cfa5",
        "requests": 67,
        "task_url": "http://www.8935qp.com/",
        "verdicts": {
            "engines": {
                "tags": [
                    "urlscan-ml",
                    "urlscan-ml-2aab354"
                ],
                "score": 84,
                "malicious": true
            },
            "overall": {
                "score": 0,
                "malicious": false
            }
        },
        "countries": [
            "CN",
            "HK"
        ],
        "final_url": "https://www.8935qp.com/",
        "redirects": [
            {
                "to": "https://www.8935qp.com/",
                "from": "http://www.8935qp.com/",
                "status": 307
            }
        ],
        "fetched_at": "2026-11-11T03:46:16Z",
        "redirected": "https-only",
        "scanned_at": "2026-11-11T03:43:34Z",
        "task_domain": "www.8935qp.com",
        "link_domains": [
            "www.cnzz.com"
        ],
        "tls_age_days": 16,
        "apex_age_days": 454,
        "tls_valid_days": 89,
        "domain_age_days": 2655
    },
    "webcheck": {
        "v": 1,
        "dns": {
            "A": [
                "82.109.255.179"
            ],
            "NS": [
                "ns1.domainnamedns.com",
                "ns4.domainnamedns.com",
                "ns3.domainnamedns.com",
                "ns2.domainnamedns.com"
            ],
            "SOA": "{\"nsname\": \"ns1.domainnamedns.com\", \"hostmaster\": \"support.namens.net\", \"serial\": 1792911657, \"refresh\": 3600, \"retry\": 1800, \"expire\": 1209600, \"minttl\": 180}"
        },
        "ssl": {
            "issuer": "Let's Encrypt / YR2",
            "subject": "8935qp.com"
        },
        "hsts": {
            "header": "max-age=31536000",
            "message": "HSTS header does not include all subdomains."
        },
        "ports": {
            "open": [
                80,
                443
            ]
        },
        "whois": {
            "status": [
                "ok https://icann.org/epp#ok"
            ],
            "created": "2026-10-23T06:53:22Z",
            "expires": "2027-10-23T06:53:22Z",
            "updated": "2026-10-23T06:53:22Z",
            "registrar": "Dominet (HK) Limited",
            "nameservers": [
                "ns1.domainnamedns.com",
                "ns2.domainnamedns.com"
            ]
        },
        "carbon": {
            "bytes": 71092,
            "co2_grams": 0.0026,
            "cleaner_than": 29
        },
        "dnssec": {
            "ds": false,
            "rrsig": false,
            "dnskey": false
        },
        "get_ip": {
            "ip": "82.109.255.179",
            "family": 4
        },
        "status": {
            "up": true,
            "code": 301,
            "timings": {
                "dns": 432,
                "tls": 188,
                "wait": 297,
                "connect": 184,
                "download": 0
            },
            "response_ms": 1101
        },
        "cookies": {
            "cookies": [
                {
                    "name": "PHPSESSID",
                    "session": true
                },
                {
                    "name": "PHPSESSID",
                    "session": true
                }
            ]
        },
        "archives": {
            "last": "2026-01-02T16:18:35Z",
            "first": "2025-12-29T11:01:14Z",
            "changes": 1,
            "days_archived": 2,
            "scans_per_day": 0.24,
            "avg_page_bytes": 8266
        },
        "location": {
            "ip": "82.109.255.179",
            "asn": "62468",
            "org": "VpsQuan L.L.C.",
            "city": "Hong Kong",
            "country": "HK"
        },
        "trackers": {
            "requests": 66,
            "trackers": [
                {
                    "name": "Baidu Ads",
                    "company": "Baidu",
                    "country": "CN",
                    "category": "Advertising",
                    "requests": 1
                },
                {
                    "name": "Microsoft Clarity",
                    "company": "Microsoft",
                    "country": "US",
                    "category": "Site Analytics",
                    "requests": 1
                },
                {
                    "name": "Umeng",
                    "company": "Umeng",
                    "country": "CN",
                    "category": "Site Analytics",
                    "requests": 1
                }
            ]
        },
        "dns_server": {
            "ns": [
                {
                    "ip": "216.106.185.75",
                    "host": "ns1.domainnamedns.com"
                },
                {
                    "ip": "67.220.72.51",
                    "host": "ns4.domainnamedns.com"
                },
                {
                    "ip": "38.114.114.183",
                    "host": "ns2.domainnamedns.com"
                },
                {
                    "ip": "54.151.142.119",
                    "host": "ns3.domainnamedns.com"
                }
            ],
            "zone": "8935qp.com"
        },
        "fetched_at": "2026-11-11T03:47:58Z",
        "tech_stack": {
            "technologies": [
                "PHP",
                "jQuery",
                "CNZZ",
                "Baidu Analytics (百度统计)",
                "Microsoft Clarity"
            ]
        },
        "block_lists": {
            "resolvers": 12,
            "blocked_by": [
                "CloudFlare Family"
            ],
            "blocked_count": 1
        },
        "mail_config": {
            "spf_lookups": 0
        },
        "social_tags": {
            "title": "中国·44118太阳成城(集团·股份)有限公司-Official",
            "keywords": "tyc122太阳成cc集团官网,太阳122cc官方集团可靠吗,tyc122太阳成cc集团",
            "description": "●官方直营品牌网站●贵宾官方旗舰站:www.8935qp.com tyc122太阳成cc集团官网,太阳122cc官方集团可靠吗,tyc122太阳成cc集团 热门娱乐平台专注打造高品质娱乐服务,支持多端同步体验,操作流畅稳定,首充加赠162元奖励,打造安全稳定的互动娱乐环境,满足不同玩家的娱乐需求。",
            "canonicalUrl": "https://www.8935qp.com/"
        },
        "tls_connection": {
            "alpn": "h2",
            "cipher": "TLS_AES_256_GCM_SHA384",
            "protocol": "TLSv1.3",
            "versions": [
                "TLSv1.2",
                "TLSv1.3"
            ],
            "authorized": true,
            "forward_secrecy": true
        }
    },
    "capture_archive": {
        "8516f444c53f76e81b3199b1daf79b4911ab6d9fbfd10aabdd9440705ede8eb4": {
            "at": "2026-10-25T11:03:21Z",
            "url": "https://urlscan.io/screenshots/01a172b8-f9cb-751c-a3c0-a301dd6d2810.png",
            "uuid": "01a172b8-f9cb-751c-a3c0-a301dd6d2810",
            "page_url": "https://www.8935qp.com/",
            "task_domain": "www.8935qp.com"
        }
    }
}
Wayback saved at
2026-11-11 06:00:09

Other

Source ID
418601
AI generated at
2026-11-11 04:48:29
AI queued
2
Indexnow sent at
2026-11-11 05:00:05
AI generated by
threat-v6-mimo
DOM analyzed at
2026-11-11 04:57:57

Captured network requests

Network requests: 67 SHA-256 hashes: 56 URLScan scan:

Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-11-11 03:46 UTC.

Open this scan on URLScan 01a1c8b4-0b9a-7318-a522-a1d2ae82930c ↗

Stored observation history1

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Google Safe Browsing · Threat flag

    No flag recorded→Flag recorded

All retained availability observations1

Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.

  1. current_state_backfillunknown
    Observation source
    current_state_backfill
    Cause
    stale_current_evidence
    Availability state
    unknown
    Content state
    unknown
    DNS state
    stale
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    0
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-11-11 04:38:17.727998
    Evidence SHA-256
    f3049ef8aa957a0c75d1f37b703ae6008630522768f5aca88bbd9915c9e1400b
    DNS evidence marked stale
    true
    HTTP evidence marked stale
    true

Threat Response Pipeline

  1. Discovery · recorded
  2. Analysis · recorded
  3. Notifications · recorded
  4. Monitoring · in progress

Recorded events: 12. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Pre-emptive Discovery & IngestionThreat Ingested Recorded: 1 of 1
  • Threat Ingested
    8935qp.com detected and queued for full analysis
Threat Intelligence ChecksURLScan.io Capture · URLScan Verdict · Cloudflare Radar Report · Web Archive · VirusTotal · Google Safe Browsing · OTX Community References · Forensic Evidence Collected · Technical Analysis Recorded Recorded: 9 of 9
  • URLScan.io Capture
    Stored URLScan report with capture artifacts
  • URLScan Verdict
    URLScan machine-learning engines classified the page as malicious · Score: 84
  • Cloudflare Radar Report
    A stored Cloudflare Radar report is available. The report link alone does not mean that the domain was classified as malicious, and it does not prove that every network field was captured.
  • Web Archive
    Preserved in the Wayback Machine: historical evidence archived
  • VirusTotal
    Detections recorded on VirusTotal: 14/92
  • Google Safe Browsing
    Listed as unsafe by Google Safe Browsing (Google Transparency Report)
  • OTX Community References
    Community publication references on AlienVault OTX: 1. References are not vendor verdicts and are excluded from the evidence score.
  • Forensic Evidence Collected
    Stored evidence from URLScan.io, URLQuery, stored screenshot
  • Technical Analysis Recorded
    The report contains stored results of technology detection or forensic analysis.
Notification RecordsSent Report Recorded Recorded: 1 of 1
  • Sent Report Recorded
    Stored record of an abuse report about this domain; registrar at the time: Dominet (HK) Limited. Abuse contacts: 1.
    • domainabuse@service.aliyun.com
Publication & AvailabilityDestroyList Published · Monitoring Continues Recorded: 1 of 2
  • DestroyList Published
    Listed in the public repository PhishDestroy/DestroyList
  • Monitoring Continues
    The domain remains reachable or access-restricted; future checks may update this observation.

Recorded activity

8 entries
  1. Abuse report sent

    PD-8781AA3C9F72097473C4 · Receipt 84668

    domainabuse@service.aliyun.com
  2. URLScan

    Page captured

    View source
  3. AlienVault OTX

    1 community references

    View source
  4. Cloudflare Radar

    Phishing

    View source
  5. Google Safe Browsing

    Threat flag recorded

    View source
  6. Added to PhishDestroy

    8935qp.com

    View source
  7. VirusTotal

    14/92 engine detections

    View source
  8. Wayback Machine

    Page archived

    View source
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

All stored records by source

Browse this domain’s complete history by source. The download includes every record of the selected source. Dates retain their original field labels.

Download all records as JSON

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

8935qp.com

Evidence & External Reports

Submitted Evidence Snapshot
Sent: Ledger records: 1 Case ID: PD-8781AA3C9F72097473C4 Recipient: domainabuse@service.aliyun.com
Page title stored with report: Warning: Security Risk
PDF notice generated
Deep Analysis
Help & reporting

Were You Affected by This Site?

6 evidence signal groups linked 1 stored notification records Last known active
You are not alone and there is nothing to be ashamed of. Scammers are sophisticated criminals who exploit trust. Reporting your experience is the most powerful weapon against fraud — your report can prevent others from becoming victims and help law enforcement take action. Silence is the scammer’s greatest advantage. Break it.
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.

Official reporting routes

More official reporting routes
FTC ReportFraud United States

Report scams and fraud to the US Federal Trade Commission. Reports go into a database used by law enforcement.

IdentityTheft.gov United States

Official identity theft report with a step-by-step recovery plan.

CISA United States

Report cyber incidents and phishing to the US Cybersecurity and Infrastructure Security Agency.

CSIRTs Network European Union

Directory of national incident response teams (CSIRTs) in the EU. Find the team for your country.

FIRST Worldwide

Worldwide directory of incident response teams, searchable by country and sector.

ReportCyber Australia

Report cybercrime to the Australian Cyber Security Centre and police.

Scamwatch Australia

Report scams to the National Anti-Scam Centre run by the ACCC.

Report to Your Local Authorities

Select your country to get official cybercrime contacts, or create a complaint draft →.

If you made a payment, contact your bank or payment service through its official contacts as soon as possible. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned.

Scammers are criminals. Filing a report creates a legal record and helps protect others.

97-country directory

Template-based draft • optional AI wording assistance requires separate consent

Review and submit it yourself
After a phishing incident

Recommendations & Advice for Victims

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

What should I do immediately?

Urgent

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Entered a password — change it on that service and on every other site where you used the same password
  • Turn on two-factor authentication — where the service offers it; an authenticator app is stronger than SMS codes
  • Paid or entered card or bank details — contact your bank or payment service through the contacts on your card or its official website

What information should I collect for my report?

FBI guidelines

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Exact dates & times — of each transaction and first contact with scammer
  • Screenshots — scam website, chat messages, emails, wallet transactions, social media
  • All URLs & domains used by the scammer (including 8935qp.com)
  • Communications — emails, texts, phone numbers, usernames the scammer used

Even if you don't have all details — file a report anyway. Partial information still helps investigations.

Where should I report the scam?

  • FBI IC3 — Internet Crime Complaint Center (US federal reporting)
  • Europol — European cybercrime reporting (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Local police — creates an official record, even if they can't act immediately

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Fake websites — pixel-perfect clones of legitimate sites with slightly altered domains
  • Pig butchering — trust built over weeks via Telegram/WhatsApp/dating apps, then money stolen
  • Recovery scams — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • AI-powered scams — deepfakes, automated phishing, and AI-generated sites making fraud harder to detect

How can I protect myself in the future?

  • Bookmark official sites — never click links from emails, DMs, or ads
  • Verify domains — check on PhishDestroy before interacting. Check HTTPS, spelling, domain age
  • "Too good to be true" = scam — guaranteed returns, celebrity endorsements, urgent deadlines

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Stay Informed, Stay Safe

Monitor live threats or contest this listing if you believe it's a false positive

Beware of recovery scammers! Recovery scammers may pose as investigators, lawyers, or tracing services. Do not pay upfront fees or disclose credentials. Learn more about recovery fraud →
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Embed This Report

Share this threat intelligence on your website or blog

embed.html
<iframe
  src="https://phishdestroy.io/embed/domain/8935qp.com"
  title="PhishDestroy threat report for 8935qp.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>