VirusTotal
3 / 91 engine detections
Retrieved / checked:
Open report 
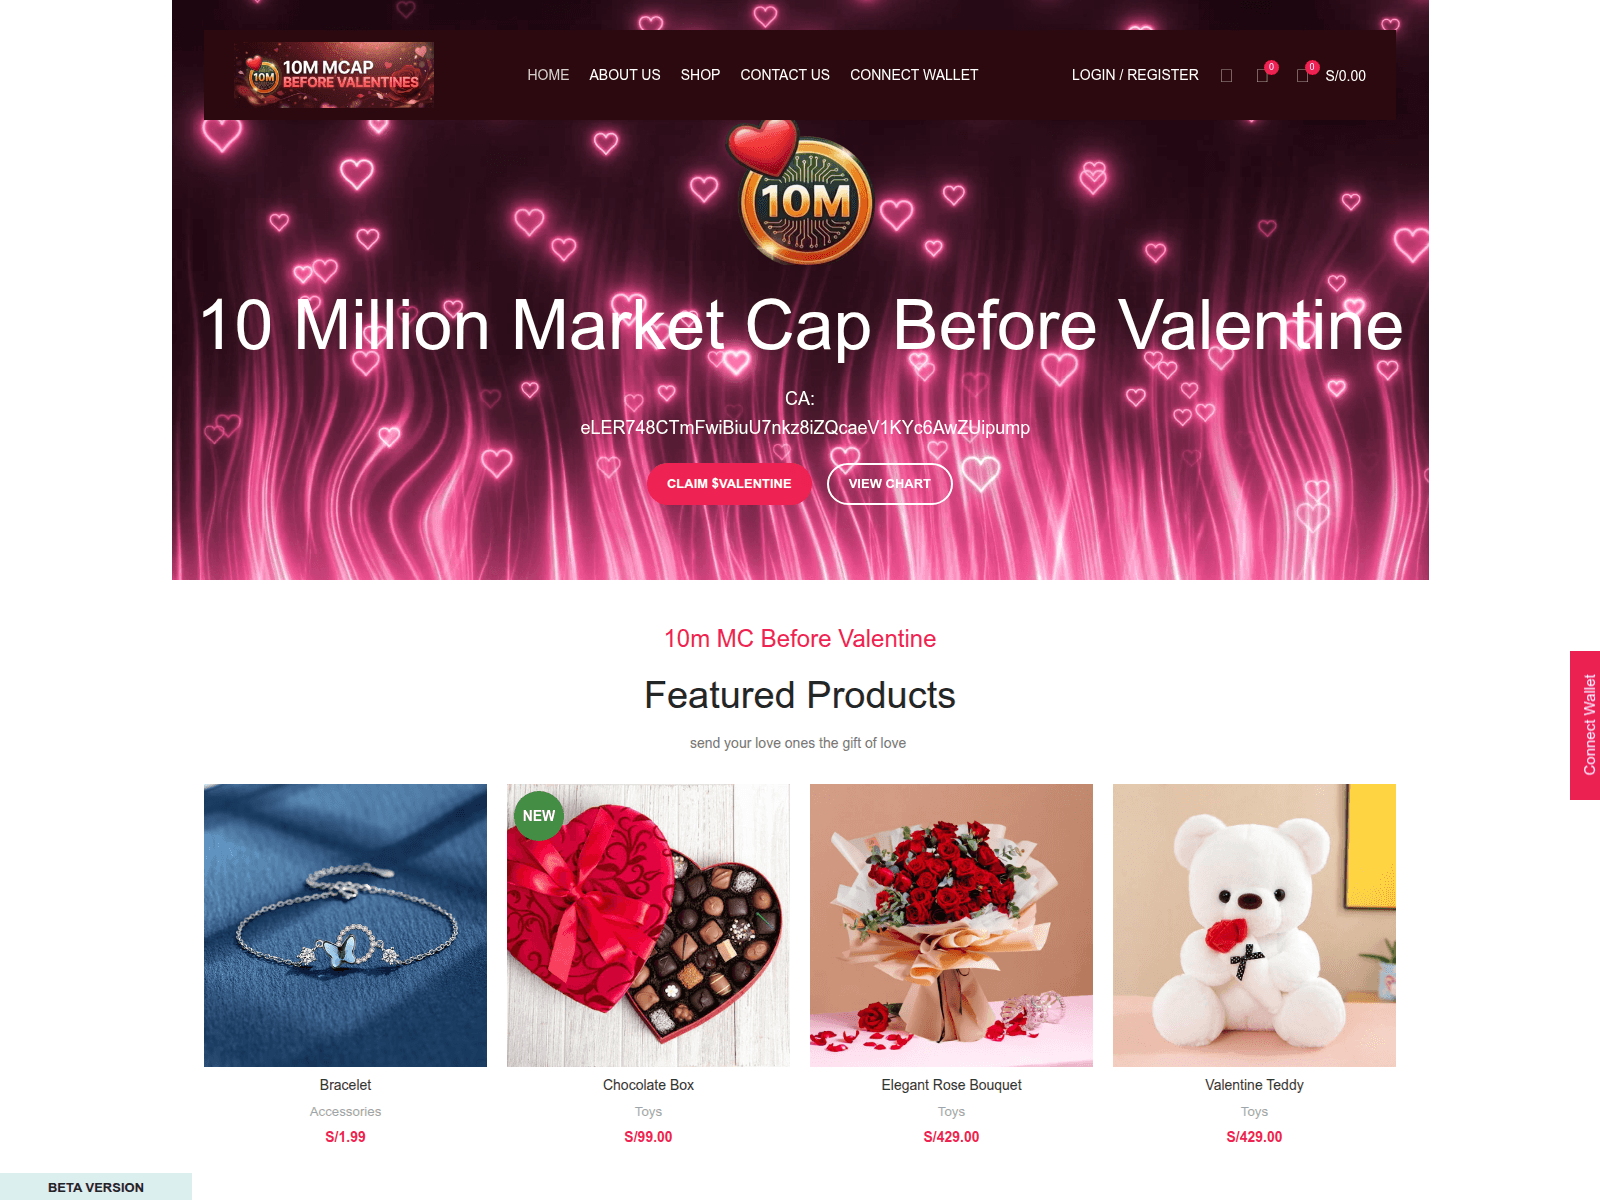
The captured page for 10mbeforevaientine.online presents a Valentine's-themed token promotion alongside a small gift shop. Its main interaction centers on a "CLAIM $VALENTINE" button and a "VIEW CHART" button, with a contract address displayed beneath the headline "10 Million Market Cap Before Valentine." Below that, a "Featured Products" section lists four gift items with prices, and a "Connect Wallet" tab sits at the right edge of the screen.
“10M MCAP BEFORE VALENTINES”
 NiceNIC
 188.114.97.3Cloudflare, Inc. · CDN
The sent-report ledger records the first outgoing report at . The recorded recipient is http://whois.nicenic.com/?page=whoisform. The latest stored availability evidence still shows the domain reachable; 8 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
PhishDestroy first recorded 10mbeforevaientine.online on 2026-02-12. Stored VirusTotal result: 3/91 engines flagged. Listed by external blocklists: ScamSniffer. Risk: critical (81/100). Registrar: NiceNIC. Status: Last known active. Hosting: Cloudflare, Inc. PhishDestroy sent 1 abuse report. Do not enter credentials or connect a wallet.
188.114.97.3Cloudflare, Inc. · CDNNiceNIC Capture recorded with this analysis · Stored capture · Exact capture time not retained
SHA-256: b90b117022f06f73569c389a765a6928231c46a2f53b36b02fbc1195a89305dc
PhishDestroy analysis, reviewed version
The captured page for 10mbeforevaientine.online presents a Valentine's-themed token promotion alongside a small gift shop. Its main interaction centers on a "CLAIM $VALENTINE" button and a "VIEW CHART" button, with a contract address displayed beneath the headline "10 Million Market Cap Before Valentine." Below that, a "Featured Products" section lists four gift items with prices, and a "Connect Wallet" tab sits at the right edge of the screen.
PhishDestroy's VirusTotal record shows 3 out of 91 engines flagging this domain. The flagging vendors include alphaMountain.ai, which labeled it phishing, and Forcepoint ThreatSeeker, which marked it as a malicious site. The scope of this VirusTotal result was not preserved in the record, so it cannot be confirmed as a domain-level scan.
3 / 91 engine detections
1 threat-system alert
Open reportSuspicious
Open reportObserved: · Retrieved:
| Uuid | 91c3f707-51ac-4554-a239-694dacb7c839 |
|---|---|
| Final url | https://10mbeforevaientine.online/ |
| Status | 200 |
| History | [
{
"url": "https://10mbeforevaientine.online/",
"status": 200
}
] |
| DOM structure hash | 81ee6df30f9780b05b64ec04ce77ff5f4d896edb271dab1f5edad899cee6d7f2 |
| Document hash | 695ac83f571a4da4dfe5e47f8bf47e51472045ce97032912f6b633c802922bf5 |
| Domain risks | [
"Newly Seen Domains",
"Security Risks"
] |
| DNS records | [
{
"name": "10mbeforevaientine.online",
"type": "A",
"value": "188.114.97.0"
},
{
"name": "10mbeforevaientine.online",
"type": "A",
"value": "188.114.96.0"
},
{
"name": "10mbeforevaientine.online",
"type": "AAAA",
"value": "2a06:98c1:3120::"
},
{
"name": "10mbeforevaientine.online",
"type": "AAAA",
"value": "2a06:98c1:3121::"
}
] |
| Dnssec valid | false |
| Ip | 188.114.97.0 |
| Registration record | {
"registrar": "NICENIC INTERNATIONAL GROUP CO., LIMITED",
"created": "2026-02-04T20:36:54Z",
"updated": "2026-02-09T20:37:19Z",
"expires": "2027-02-04T23:59:59Z",
"nameservers": [
"chloe.ns.cloudflare.com",
"tadeo.ns.cloudflare.com"
]
} |
29/100
Open report24 community references
Open reportNo threat flag
Open reportNo malicious flag
Open reportObserved: · Retrieved:
| Uuid | 019c5191-54a8-7498-b596-c975681dea33 |
|---|---|
| Final url | https://10mbeforevaientine.online/ |
| Status | 200 |
| Redirected | https-only |
| Redirects | [
{
"to": "https://10mbeforevaientine.online/",
"from": "http://10mbeforevaientine.online/",
"status": 307
}
] |
| Ip | 172.67.193.64 |
| Contacted domains | [
"10mbeforevalentine.online",
"static.cloudflareinsights.com"
] |
| Contacted IP addresses | [
"104.16.79.73",
"38.242.134.33",
"172.67.193.64"
] |
| Asns | [
"13335",
"51167"
] |
| Countries | [
"FR"
] |
| Linked domains | [
"10mbeforevalentine.online",
"dexscreener.com",
"x.com",
"telegram.me"
] |
| Social | [
"https://x.com/share",
"https://telegram.me/share/url"
] |
| Document hash | 695ac83f571a4da4dfe5e47f8bf47e51472045ce97032912f6b633c802922bf5 |
| Script hashes | [
"099e2f986610b279a13fac206df140fc2895c89e9c691235d08ae3774ffdeea1",
"cb6f2d32c49d1c2b25e9ffc9aaafa3f83075346c01bcd4ae6eb187392a4292cf",
"5274f11e6fb32ae0cf2dfb9f8043272865c397a7c4223b4cfa7d50ea52fbde89",
"d151f8c0b2659cfb63704d68654ad8d9437ae9da4410536f63ddec21689a0620",
"fca8dd4ee9c93f33dc3149e2c78aec8a28c54036faaf19c7b0ac9ca32293c070",
"8b083f64f2e9e8ac445c730dfce7013cc6449ce155fd1c2f42b60edba4ecb4b1",
"a41ecabfaa5a628b26a98234caa818e4d68e3edf6c48cee40b2a6f4c4fcafaba",
"988cc08b4210c0b61d47639033efd0eca9e2ea5ca3d09780d9d3b99f7fc04f97",
"711283e412042fac8106151681ed99b6712de6b666fe773f77ea6e05d15237f0",
"c50a0b33030ba0ec063be642c297f48af94359e2222ff140817248d591faf837"
] |
| Globals | [
"setup",
"wc_add_to_cart_params",
"woocommerce_params",
"wd_cart_fragments_params",
"wc_order_attribution",
"elementorFrontendConfig",
"woodmart_settings",
"woodmart_page_css",
"_wpUtilSettings",
"wc_add_to_cart_variation_params",
"wc_cart_fragments_params",
"__cfBeacon",
"__p_KuhP_cache",
"__p_LCZx_array",
"__globalObject",
"__TextDecoder",
"__Uint8Array",
"__String",
"__Array",
"utf8ArrayToStr",
"__p_Pv3U_MAIN_STR_decode",
"__p_Pv3U_MAIN_STR",
"__p_toIP_getGlobal",
"__p_3nBo_bufferToString",
"__p_vDRD_calc",
"__p_yLbX_dummyFunction",
"__p_1c38_d_fnLength",
"__p_2OYj_ast",
"startConnect",
"onPressWallet",
"multi",
"lazyloadRunObserver",
"events",
"__p_s5ve_dlrArray"
] |
| Tls | {
"san": [
"10mbeforevaientine.online",
"*.10mbeforevaientine.online"
],
"cipher": "AES_128_GCM",
"issuer": "WE1",
"subject": "10mbeforevaientine.online",
"protocol": "QUIC",
"valid_to": "2026-05-05T20:59:36Z",
"valid_from": "2026-02-04T20:00:56Z"
} |
| Domain age days | 7 |
| Apex age days | 7 |
| Tls age days | 7 |
| Tls valid days | 90 |
| Requests | 143 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-0.1.0-1-d9114fd"
],
"score": -79,
"malicious": false
},
"overall": {
"score": 0,
"malicious": false
}
} |
| HTTP headers | {
"server": "cloudflare",
"content-type": "text/html",
"strict-transport-security": "max-age=63072000; includeSubDomains; preload",
"content-security-policy": "frame-ancestors http: https:",
"x-content-type-options": "nosniff",
"priority": "u=0,i"
} |
Separate stored monitor snapshot; does not replace the primary report record or establish current availability.
Check recorded; verdict not retained
Open reportNo report found
Open reportA missing report is not a trust verdict. Legacy zeroes remain in the stored record; the measured trust score is unavailable.
81 / 100 · heuristic score · 0 brand references · 1 classification
Open reportThis dated monitor analysis is separate from the primary PhishDestroy analysis above. A heuristic score is not a measured probability.
Narrative generation metadata
Open reportThe narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.
Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
Stored page, network and scanner observations, grouped by source and observation time.
 Scamadviser Warnings 29/100
| Detection System | Indicator | Verdict | Alert |
|---|---|---|---|
| Hagezi Threat Feed | 10mbeforevaientine.online | malicious | Sinkholed |
PhishDestroy rates 10mbeforevaientine.online as critical risk (81/100) from the recorded evidence; it was first recorded on 2026-02-12. Stored VirusTotal result: 3/91 engines flagged. Listed by external blocklists: ScamSniffer. The local score and a listing do not prove fraud. Check each source’s date and the exact URL.
This report does not record which wallet requests 10mbeforevaientine.online makes. Because of the risk signals above, do not connect a wallet, sign messages or approve token permissions there. A confirmed blockchain transaction cannot be reversed.
It depends on what you did. If you entered a password, change it, and also on every other site where you used the same password; turn on two-factor authentication where it is offered. If you paid or gave card or bank details, contact your bank or payment service through the contacts on your card or its official website. If you only connected a wallet, disconnect the site in the wallet and reject pending requests; a connection by itself does not move funds. If you signed a token approval or permit, revoke it with a token-approval checker. If you shared a seed phrase or private key, treat the wallet as compromised and move the remaining funds to a new wallet with a new seed phrase. If you downloaded a file, do not open it and scan the device with security software. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority; a report does not guarantee that money is returned. Step-by-step help: emergency guide.
Checked, no match
Last checked
141c2cae70260881fca1c364e56ad84113c6d5bd00d0a5f9a4d91102e7c3e675 · 506516 bytes 426ee919ffbf4e525bfb6d1c5110a312a8c487b328b86cf0fc4b201c2472ae6e · 386672 bytes 77ae4ea74953b7ce09a0d024c05aca650e0b60fb1681c9c1fd605f4ea64afa69 · 347155 bytes 188.114.97.3 Cloudflare shared edge origin IP hidden Edge-IP reputation is not attributed to this domain. (RU) PhishDestroy Investigation For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
188.114.97.3San Francisco, USEdge-IP reputation is not attributed to this domain.
tadeo.ns.cloudflare.comLocation describes the IP network.
e2d408dcae3783f9efa5e92c1d28107a6765bc0b7a3d04fd0a5e254fe14231e210mbeforevaientine.online*.10mbeforevaientine.onlineSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
The site was redirecting visitors elsewhere at the latest check.
Cloudflare is a web-infrastructure and website-security company, providing content-delivery-network services, DDoS mitigation, Internet security, and distributed domain-name-server services.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Network requests: 143 SHA-256 hashes: 137 URLScan scan:
Network requests that the URLScan browser recorded while loading the page. URLScan does not provide a hash for every request. PhishDestroy retrieved this list on 2026-10-29 06:29 UTC.
Open this scan on URLScan 019c5191-54a8-7498-b596-c975681dea33 ↗
| # | Network request | HTTP method · status | Type | Uncompressed size | Response body SHA-256 |
|---|
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
Our scanner could not complete this check.
10mbeforevaientine.online Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
redirected
http_redirect
Unavailable→Reachable
https://radar.cloudflare.com/scan/d1b462fd-5657-4a1b-9f60-2485def6b24a
https://radar.cloudflare.com/scan/105bd2c4-2fb2-499f-962f-3a9ef57788cd
Reachable→Unavailable
Source: domain_monitor. This stored snapshot does not establish current availability.
Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.
Recorded events: 15. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
24 community references
View sourcePD-20260213-E09E2C · Receipt 10337
10mbeforevaientine.online
View sourcePage captured
View sourceWe scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
 GoogleSafe Browsing↗ GoogleWeb Risk↗
 MicrosoftSmartScreen↗
 VirusTotalURL analysis↗
 CloudflareRadar / abuse reporting↗
 YandexSafe Browsing↗
 URLScan.ioPublic scan↗
 ESETSample / URL submission↗
 BitdefenderURL submission↗
 NortonSafe Web↗
 SymantecSiteReview↗
 AviraURL reporting↗
 Avast / AVGURL reporting↗
 KasperskyOpenTIP↗
 Dr.WebOnline scanner↗
 NetcraftAbuse reporting↗
 PhishTankCommunity reporting↗
 APWG eCXPhishing intelligence↗
 PhishStatsPublic feed↗
 Phish.ReportHosting abuse↗
 SpamhausDomain reputation↗
 PolySwarmMulti-engine analysis↗
 CheckPhishURL scan↗
 QutteraMalware scan↗
 URLqueryBrowser analysis↗
 Criminal IPAsset intelligence↗
 CRDFThreat Center↗ ScamadviserReputation check↗
 MyWOTCommunity reputation↗
Browse this domain’s complete history by source. The download includes every record of the selected source. Dates retain their original field labels.
Download all records as JSON| ID | Stored data |
|---|
Unclassified: Unknown Discovery only 8
Registrar: NiceNIC Discovery only 6
Each spoke is one reason a domain is linked to this report. Node size marks VirusTotal detections, dashed nodes are already offline, and the full lists follow below. Full list of related reports
These reports share an unknown kit label. This does not establish a common kit, operator or campaign. View reports with this unclassified label →
Registered through the same registrar. A registrar serves millions of unrelated customers, so this groups reports rather than proving a link.
Recently added threat reports.
Reported by 1 community member, first seen Feb 12, 2026
PD-20260213-E09E2C Recipient: http://whois.nicenic.com/?page=whoisform Registrar: NICENIC International Group Co., Limited (Hong Kong (China)) Policy Violations: “Services may be used only for lawful purposes… fraud, abuse and illegal activity prohibited. Violations may result in immediate suspension.” + dedicated abuse handling and takedown Applicable Laws: Crimes Ordinance Cap.200 (Fraud), Theft Ordinance Cap.210 §16A (fraud by deception), Personal Data (Privacy) Ordinance Cap.486
Act on what you actually did. Entered a password: change it, and wherever you reused it. Paid or gave card details: contact your bank or payment service. Downloaded a file: scan the device. Then report the incident.
IC3 does not accept attachments. Keep original evidence for investigators. IC3 guidance
Federal tips line1-800-CALL-FBI

Current service: Report Fraud. England, Wales and Northern Ireland. Scotland: 101.
Contact centre0300 123 2040


Report scams and fraud to the US Federal Trade Commission. Reports go into a database used by law enforcement.


Report cyber incidents and phishing to the US Cybersecurity and Infrastructure Security Agency.

Forward scam emails and text messages to the National Cyber Security Centre, which takes down the malicious sites it finds.
Emailreport@phishing.gov.uk Text messages7726
Directory of national incident response teams (CSIRTs) in the EU. Find the team for your country.

Forward phishing emails to the Anti-Phishing Working Group.
Emailreportphishing@apwg.org
National Cyber Crime Reporting Portal. For financial fraud, also call the 1930 helpline straight away.
Helpline1930


Select your country to get official cybercrime contacts, or create a complaint draft →.
If you made a payment, contact your bank or payment service through its official contacts as soon as possible. Keep the address, dates, payment or transaction details and messages for a report to the police or another competent authority. A report does not guarantee that money is returned.
Scammers are criminals. Filing a report creates a legal record and helps protect others.
Template-based draft • optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
10mbeforevaientine.online)Even if you don't have all details — file a report anyway. Partial information still helps investigations.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Threat analysis using stored blocklist, WHOIS, DNS, and public scan evidence
Scan NowSubmit suspicious domains to our threat database — protect the community
ReportRecent phishing reports and observed availability changes
MonitorMonitor live threats or contest this listing if you believe it's a false positive
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.