Zum Sicherheitsbericht springen
Domänensicherheit und Bedrohungsinformationen
beyondbyverastore.shop favicon

beyondbyverastore.shop

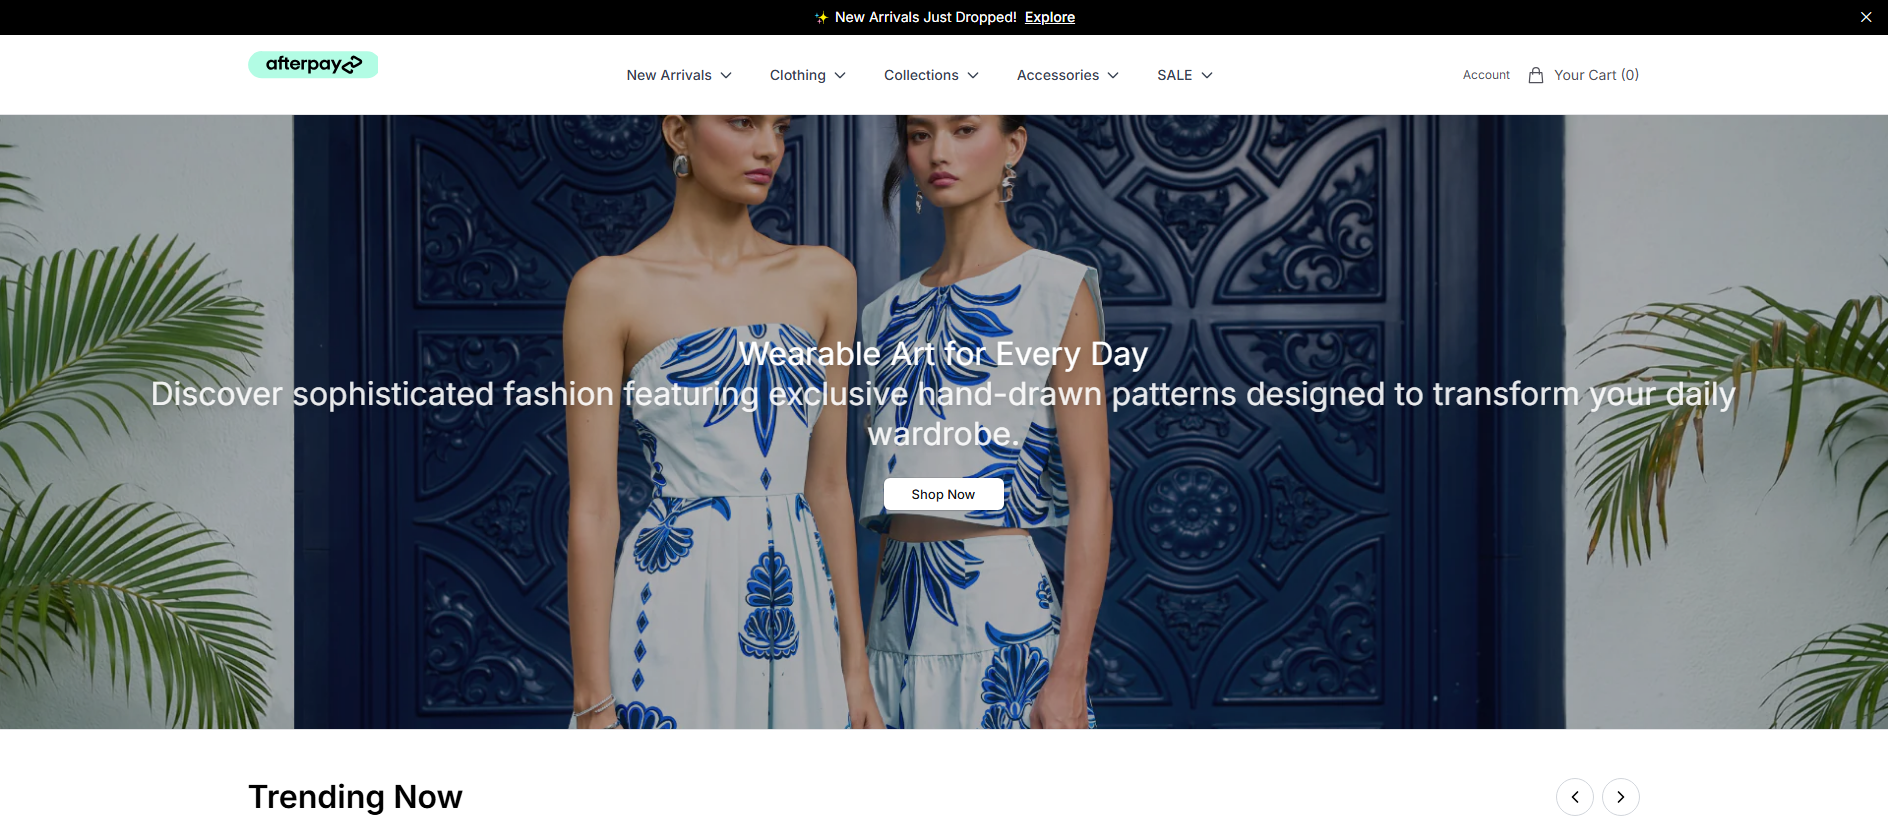
“Modern Women's Clothing Featuring Unique, Hand-drawn Prints | Beyond by Vera”

Registrar
Dynadot
Resolved IP
46.245.239.118
Registered
26.05.2026
PhishDestroy assessment Kritisch
Verfügbarkeit Letzter bekanntermaßen aktiv Letzte gespeicherte Erreichbarkeitsbeobachtung Beobachtet · HTTP probe
VirusTotal-Erkennungen: 7/92 Spamhaus DBL: DBL_SPAM Automatische Markenkennung: Fake shop
OTX: 4 refs 16.10.2026 1 Report Sent
API
Diese Domain wurde als bösartig markiert.
Sicherheits-Engines melden eine Entdeckung: 7. Seien Sie äußerst vorsichtig – Geben Sie keine Anmeldeinformationen oder persönlichen Daten ein.
ABUSE NOTICE · 72H+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is abuse@rashost.com. The latest stored availability evidence still shows the domain reachable; 4 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
4 days
Reports sent
1
Latest case ID
PD-20261016-BE4E56
Current status
HTTP 200 at latest stored check
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
Domain age
Reports sent
view timeline
Berichtsübersicht

Phishing: beyondbyverastore.shop — Letzter bekanntermaßen aktiv (HTTP 200). Zusammenfassung der Beweislage: VirusTotal 7/92 (alphaMountain.ai, CRDF…

Die ausführliche Analyse von PhishDestroy AI bleibt auf Englisch, damit der ursprüngliche forensische Bericht unverändert bleibt.

Source evidenceVirusTotal 7 / 92 · OTX 4 references 7 sources

Spamhaus DBL

DBL_SPAM

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Analysis

Kritisch
VirusTotal
7 / 92
OTX
4 community refs
Page captures
2

PhishDestroy threat report

Overview

beyondbyverastore.shop is a fake online store that uses the name Beyond by Vera and presents itself as a boutique of modern women's clothing with unique, hand-drawn prints. It targets fashion shoppers who find it through ads or search and believe they are buying from a small designer label. PhishDestroy first detected it on 2026-10-16. As of 2026-10-19 the site was still online and serving its shop content.

How the scam works

The storefront is built to look like an independent designer brand, with the page title "Modern Women's Clothing Featuring Unique, Hand-drawn Prints | Beyond by Vera" setting up an artsy, trustworthy image. Shops like this usually draw buyers in with steep discounts and a polished catalogue, then take payment at checkout. The buyer then receives nothing, receives cheap goods unrelated to the listing, or gets a stream of excuses until refund windows close. Victims lose the purchase price and hand over card details, a shipping address and contact information that can be reused for further fraud.

Evidence

urlscan.io rated the site malicious and specifically flagged it as a fake shop, the strongest independent signal here. Spamhaus lists the domain in its DBL under the spam category, and it appears in four AlienVault OTX threat pulses. VirusTotal coverage is thin: on 2026-10-16 only Gridinsoft out of 92 engines flagged it. A low engine count is common for fresh retail scams, so a mostly clean VirusTotal result does not mean the shop is safe.

Infrastructure

The domain was registered on 2026-05-26 through Dynadot Inc., roughly four and a half months before PhishDestroy caught it. That gap suggests the operators kept it ready, or ran it quietly, before pushing traffic to it. It resolves to 46.245.239.118 on the Malakmadze Web LLC network, which is registered in Georgia while the server is located in the US. The free Let's Encrypt certificate only encrypts the connection, so the browser padlock says nothing about whether the shop is honest.

What to do

If you ordered from this site, contact your card issuer or payment provider right away, report the charge as fraud and ask for a chargeback. Keep your order confirmation and any emails as evidence. If you reused a password when you created an account here, change it on your other accounts. Expect phishing aimed at the email address and phone number you entered. Security teams should block the domain and its IP, and watch for lookalike stores that reuse the Beyond by Vera branding.

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list View source

Gespeicherte Aufnahme · 2 captures

Observed page title
Modern Women's Clothing Featuring Unique, Hand-drawn Prints | Beyond by Vera
TLS-Zertifikat
Ausgestellt von Let's Encrypt / YE1 · stored validity ends in 62 days

Domain details

Domain
URLScan verdict Schädlich score 100 Phishing brand: Fakeshop report ↗
IP-Reputation abuse score 0/100 0 reports checked 16.10.2026
OTX tags 2026-10activeall-domainsblocklistcontentcryptoDomainsdrainerfraudlivemonthlyphishdestroyphishingscam
Registrar Dynadot US(US)
Abuse-Kontaktabuse@rashost.com
ICANN-RegistrierungsstelleICANN Lookup (RDAP) →
RegistrierungErstellt 26.05.2026 (147d) — Expires 26.05.2027
HTTP-Status200
Technische DetailsProvenance & timestamps
Erstmals entdeckt16.10.2026
DOM Analysisanalyzed 16.10.2026score 81/100
Submitted URLhttp://beyondbyverastore.shop/
Favicon Hash
Fall-ID
ICANN OVERSIGHT

Akkreditierung und RAA-Kontext

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft Nichts wird automatisch gesendet.

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
46.245.239.118
Network ASN
AS199242
Organization
Malakmadze Web LLC
Observed location
Los Angeles, US

Nameserver 2

  • hasslo.ns.cloudflare.com
  • mckinley.ns.cloudflare.com

Location describes the IP network.

TLS-Zertifikat

Issuer
Let's Encrypt / YE1
Valid from
2026-09-23 07:52:53
Valid until
2026-12-22 07:52:52
Validity
Within stored validity dates
Collection time
2026-10-16 01:02:04 UTC
Collection source
PhishDestroy collector
Certificate fingerprint1d06460bf4ca6e6773d5f54c6cda7727b24967d666008d4f84a6143836aecada

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-19 22:45:46 UTC

Primary outcome Aktive Inhalte reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Aktive Inhalte Ordinary HTTP content served 90% 2026-10-19 22:45:46 UTC
RDAP registration Unbekannt
Observed timeline last reachable: 2026-10-19 22:45:46 UTC last content: 2026-10-19 22:45:46 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Technologien · 1 identified
Detected via Cloudflare Radar · Wappalyzer engine
Diese Domain melden Reichen Sie Beweismaterial ein und helfen Sie mit, andere zu schützen

VirusTotal-Analyse

7 / 92 Sicherheitsanbieter haben diese Domain markiert
View on VT
Last analyzed First positive detection Previous stored snapshot: 1 detection
alphaMountain.ai
CRDF
Forcepoint ThreatSeeker
Fortinet
Gridinsoft
LevelBlue
Netcraft

Archivierte Beweise

Wayback Machine Snapshot
Zur Beweisüberprüfung steht ein historischer Schnappschuss zur Verfügung
View Archive
Website-Performanceanalyse

Google PageSpeed Insights — mobile performance audit of beyondbyverastore.shop · checked Oct 16, 2026

70
Needs Work
Performance
FCP
2.99s
First Contentful Paint
LCP
6.28s
Largest Contentful Paint
CLS
0.005
Cumulative Layout Shift
TBT
114ms
Total Blocking Time
SI
3.96s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://beyondbyverastore.shop/
Final URL: https://beyondbyverastore.shop/
Modern Women's Clothing Featuring Unique, Hand-drawn Prints | Beyond by Vera
Beyond by Vera, created by designer Vera Fritsch, provides sophisticated daily fashion with exclusive, hand-drawn patterns that transform clothing into wearable art.
Reaktion
HTTP 200
HTML body
325.0 KB
Compressed
52.9 KB
Links
35 internal · 0 external
Detected technologies
react
Selected response headers
Cache-Control: private, no-cache, no-store, max-age=0, must-revalidate
Content-Encoding: gzip
Content-Type: text/html; charset=utf-8
Security headers present
X-Frame-OptionsX-Content-Type-OptionsX-XSS-ProtectionReferrer-Policy
HSTS: not observed DNSSEC: not observed WAF / firewall: not observed Cloaking flag: not observed
Open Graph title: Modern Women's Clothing Featuring Unique, Hand-drawn Prints
Open Graph description: Beyond by Vera, created by designer Vera Fritsch, provides sophisticated daily fashion with exclusive, hand-drawn patterns that transform clothing into wearable art.
Twitter card: summary_large_image
Saved response-header values · 13
Alt-Svc
h3=":443"; ma=2592000
Cache-Control
private, no-cache, no-store, max-age=0, must-revalidate
Content-Encoding
gzip
Content-Type
text/html; charset=utf-8
Date
Thu, 15 Oct 2026 23:58:47 GMT
Link
; rel=preload; as="style"
Referrer-Policy
strict-origin-when-cross-origin
Transfer-Encoding
chunked
Vary
RSC, Next-Router-State-Tree, Next-Router-Prefetch, Next-Router-Segment-Prefetch, Accept-Encoding
Via
1.1 Caddy
X-Content-Type-Options
nosniff
X-Frame-Options
SAMEORIGIN
X-XSS-Protection
1; mode=block

Values retained by the collector; long values may be shortened during collection.

Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Stored observation history11

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    Nicht verfügbar→Erreichbar

  2. Availability monitor · Recorded state

    Erreichbar→Nicht verfügbar

  3. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  4. Availability monitor · Recorded state

    Nicht verfügbar→Erreichbar

  5. Availability monitor · Recorded state

    Erreichbar→Nicht verfügbar

Earlier observations 6
  1. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  2. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  3. Availability monitor · Recorded state

    Nicht verfügbar→Erreichbar

  4. Availability monitor · Recorded state

    Erreichbar→Nicht verfügbar

  5. Availability monitor · Recorded state

    Unbekannt→live_content

    content_served

  6. Availability monitor · First collection record

    Erreichbar

Recorded activity

6 entries
  1. VirusTotal

    7/92 engine detections

    View source
  2. Google Safe Browsing

    No threat flag

    View source
  3. AlienVault OTX

    4 community references

    View source
  4. Abuse report sent

    PD-20261016-BE4E56

    abuse@rashost.com
  5. Added to PhishDestroy

    beyondbyverastore.shop

    View source
  6. URLScan

    Page captured

    View source

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

beyondbyverastore.shop

Nachweise und externe Berichte

Momentaufnahme der übermittelten Beweise
Sent: Ledger records: 1 Case ID: PD-20261016-BE4E56 Recipient: abuse@rashost.com
PDF notice generated
Eingehende Analyse
Help & reporting

Wurden Sie von dieser Website betroffen?

6 evidence signal groups linked 1 stored notification records Letzter bekanntermaßen aktiv
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Wenn Sie Kontoanmeldeinformationen, persönliche oder Zahlungsinformationen eingegeben oder eine Datei von dieser Domain heruntergeladen haben, ergreifen Sie sofort Maßnahmen. Nachfolgend finden Sie Ressourcen, die Ihnen helfen, den Vorfall zu melden und sich zu schützen.

Official reporting routes

Vorsicht vor Betrügern, die mit der Rückforderung von Geldern locken! Kriminelle nehmen unter Umständen erneut Kontakt zu Opfern auf und geben dabei vor, Ermittler, Anwälte oder Beitreibungsbeamte zu sein. Zahlen Sie keine Vorabgebühren und geben Sie keine Anmeldeinformationen weiter. Erfahren Sie mehr über Betrug im Zusammenhang mit Wiederaufbaumaßnahmen →

Melden Sie sich bei Ihren örtlichen Behörden

Wählen Sie Ihr Land aus, um Offizielle Kontakte im Bereich Cyberkriminalität oder einen Beschwerdeentwurf erstellen → zu erhalten.

97-Länder-Verzeichnis

Template-based draft · optional AI wording assistance requires separate consent

KI-gestützter Entwurf – Vorfalldetails werden vom KI-Anbieter verarbeitet · Überprüfen Sie es und reichen Sie es selbst ein
After a phishing incident

Empfehlungen und Ratschläge für Betroffene

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

Was soll ich sofort tun?

Dringend

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Alle Passwörter ändern — E-Mail, Exchange-Konten, alles, wofür dasselbe Passwort verwendet wird
  • 2FA aktivieren mit einer Authentifizierungs-App (nicht per SMS). Deaktivieren Sie die SMS-basierte Wiederherstellung
  • Karten einfrieren Falls Sie auf der Phishing-Seite Ihre Bankdaten eingegeben haben

Welche Informationen sollte ich für meinen Bericht sammeln?

FBI-Richtlinien

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Genaue Daten und Uhrzeiten — jeder Transaktion und des ersten Kontakts mit dem Betrüger
  • Screenshots — betrügerische Websites, Chat-Nachrichten, E-Mails, Wallet-Transaktionen, soziale Medien
  • Alle URLs und Domains die der Betrüger verwendet (einschließlich beyondbyverastore.shop)
  • Kommunikation — E-Mails, SMS, Telefonnummern, Benutzernamen, die der Betrüger verwendet hat

Auch wenn dir nicht alle Details bekannt sind — trotzdem Anzeige erstatten. Auch unvollständige Informationen sind für die Ermittlungen hilfreich.

Wo soll ich den Betrugsfall melden?

  • FBI IC3 — Internet Crime Complaint Center (Meldestelle der US-Bundesbehörden)
  • Europol — Meldungen zu Cyberkriminalität in Europa (EU)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Ortspolizei — sorgt für eine offizielle Dokumentation, auch wenn sie nicht sofort handeln können

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Gefälschte Websites — pixelgenaue Kopien legitimer Websites mit leicht abgeänderten Domains
  • Schweineschlachtung — über Wochen hinweg über Telegram, WhatsApp und Dating-Apps aufgebautes Vertrauen, dann wurde Geld gestohlen
  • Betrugsmaschen im Zusammenhang mit der Rückforderung von Geldern — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • Durch KI gestützte Betrugsmaschen — Deepfakes, automatisiertes Phishing und KI-generierte Websites, die es erschweren, Betrugsversuche zu erkennen

Wie kann ich mich in Zukunft schützen?

  • Offizielle Websites als Lesezeichen speichern — Klicken Sie niemals auf Links in E-Mails, Direktnachrichten oder Anzeigen
  • Domains überprüfen — nachsehen, ob PhishDestroy Bevor Sie Kontakt aufnehmen: Überprüfen Sie HTTPS, die Rechtschreibung und das Alter der Domain.
  • „Zu schön, um wahr zu sein“ = Betrug — garantierte Renditen, Prominente als Werbeträger, dringende Fristen

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Bleiben Sie auf dem Laufenden, bleiben Sie sicher

Beobachten Sie aktuelle Bedrohungen oder legen Sie Widerspruch gegen diesen Eintrag ein, wenn Sie der Meinung sind, dass es sich um einen Fehlalarm handelt

Echtzeit-Bedrohungsfeed Einspruch gegen diesen Eintrag einlegen
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Diesen Bericht einbetten

Teilen Sie diese Bedrohungsinformationen auf Ihrer Website oder in Ihrem Blog

embed.html
<iframe
  src="https://phishdestroy.io/de/embed/domain/beyondbyverastore.shop"
  title="PhishDestroy threat report for beyondbyverastore.shop"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>