跳转到安全报告
域安全和威胁情报
walletflower.fun favicon

walletflower.fun

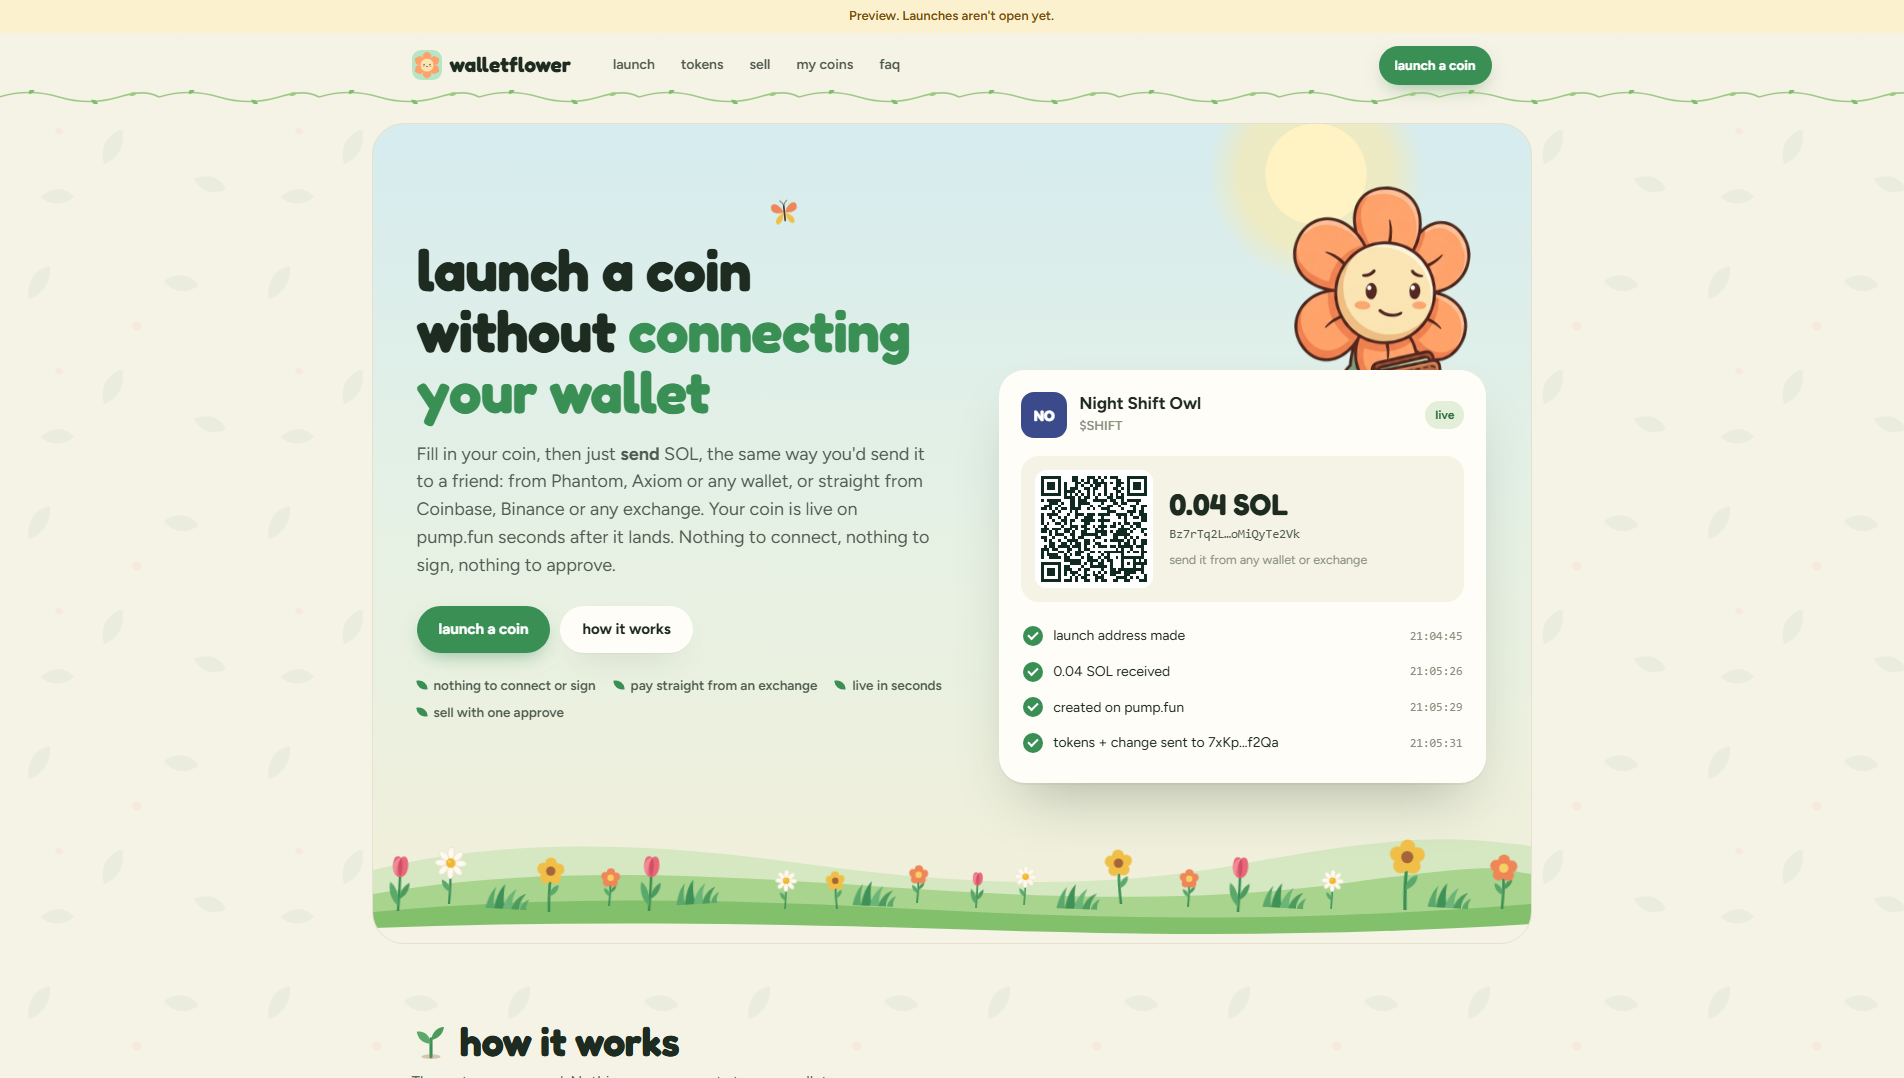
“walletflower · launch on pump.fun without connecting a wallet”

注册商
Cloudflare
Resolved IP
104.21.19.103
PhishDestroy assessment 关键
可用性 最后已知的活跃状态 最新存储的可达性观察 观察到 · HTTP probe
病毒检测总数:7/92 Spamhaus DBL: DBL_PHISH 自动品牌标签:Backpack
OTX: 5 refs 2026年10月17日 CDN
API
该域名已被标记为恶意域名
安全引擎报告检测:7。 请格外小心——不要输入凭据或个人信息。
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
报告概览

冒充 Backpack: walletflower.fun — 最后已知的活跃状态 (HTTP 200). 证据摘要: VirusTotal 7/92 (alphaMountain.ai, CyRadar, DNS8, Forcepoint ThreatSeeker, Fortinet); Spamhaus…

为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。

Source evidenceVirusTotal 7 / 92 · OTX 5 references 6 sources

VirusTotal

7 / 92 engine detections

打开报告

Spamhaus DBL

DBL_PHISH

Google Safe Browsing

No threat flag

打开报告

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

网络安全情报
CF Cloudflare Radar Verdict 恶意
Phishing Security Risks New Domains Security threats Phishing

Analysis

关键
VirusTotal
7 / 92
OTX
5 community refs
Page captures
3

PhishDestroy threat report

Overview

walletflower.fun poses as a tool that lets users launch tokens on pump.fun without connecting a wallet, a pitch designed to lower the guard of DeFi users who are wary of wallet-connection risks. The site targets crypto users active on pump.fun, a popular Solana-based token launchpad. PhishDestroy first identified it on 2026-10-17, one day after the domain was registered, and as of 2026-10-18 the site remains fully live and serving active content.

How the scam works

The page title — "walletflower · launch on pump.fun without connecting a wallet" — is the lure: it promises a friction-free token launch that supposedly requires no wallet connection, which is exactly what a cautious user wants to hear. In practice, drainer sites of this type do the opposite: at some point in the flow they prompt the victim to sign a transaction or approve a contract, and that interaction hands the attacker permission to sweep tokens and NFTs from the connected wallet. The victim loses assets directly from their wallet without any further action on their part, and the transfer is irreversible on-chain.

Evidence

VirusTotal returned 7 detections from 92 engines as of 2026-10-18, with flagging vendors including Kaspersky, Fortinet, Forcepoint ThreatSeeker, OpenPhish, CyRadar, DNS8, and alphaMountain.ai. Spamhaus DBL classifies the domain as DBL_PHISH, an independent confirmation of phishing intent. The domain has also generated 5 OTX threat-intelligence pulses and appears on the PhishDestroy blocklist. Seven detections out of 92 engines is a moderate signal; the Spamhaus and OTX corroboration strengthens the case significantly.

Infrastructure

The domain was registered on 2026-10-16 through Cloudflare, Inc. and is hosted on the same company's network, AS13335, on a US-based IP. The TLS certificate is issued by Google Trust Services under the WE1 intermediate, giving the site a padlock that lends it false legitimacy. The one-day gap between registration and first detection is consistent with a purpose-built scam domain.

What to do

If you visited the site but did not connect a wallet or sign anything, no immediate action is required beyond avoiding the site. If you connected a wallet, immediately revoke all token approvals granted to any contract associated with this site using a trusted approval-revocation tool, then transfer remaining assets to a fresh wallet address. If you signed a transaction, assume your assets are at risk and act without delay. Security teams and wallet providers should add walletflower.fun to blocklists and alert users who may have interacted with pump.fun-adjacent tooling.

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list View source

已保存的截图 · 3 captures

Observed page title
walletflower · launch on pump.fun without connecting a wallet
Automated brand references
Backpack Binance Coinbase Kraken Phantom Solflare Ups
TLS 证书
颁发者 Google Trust Services / WE1 · stored validity ends in 85 days

Domain details

域名
URLScan verdict 分析完成 score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP 声誉不属于此域。
OTX tags 2026-10activeall-domainsblocklistcontentcrypto域名drainerfraudlivemonthlyphishdestroyphishingscam
注册商 Cloudflare US(US)
注册信息Expires 2027年10月16日
HTTP 状态码200
技术详情Provenance & timestamps
首次发现2026年10月17日
DOM Analysisanalyzed 2026年10月17日score 98/1007 brand signals
Submitted URLhttp://walletflower.fun/
Favicon Hash
ICANN OVERSIGHT

认证和 RAA 背景

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft 不会自动发送任何内容。

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
104.21.19.103
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

Edge-IP 声誉不属于此域。

域名服务器 2

  • randy.ns.cloudflare.com
  • vivienne.ns.cloudflare.com

Location describes the IP network.

TLS 证书

Issuer
Google Trust Services / WE1
Valid from
2026-10-16 21:01:08
Valid until
2027-01-14 22:01:05
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-10-17 19:02:07 UTC
Collection source
PhishDestroy collector
Certificate fingerprint5b266368d5f18c7472a40aed02c0c7ce6d103319a24d1cdfb077f7a20236eac4
Certificate names · 1 SANs
  • www.walletflower.fun

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-19 22:48:31 UTC

Primary outcome 内容在线 reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation 内容在线 Ordinary HTTP content served 90% 2026-10-19 22:48:31 UTC
RDAP registration 未知
Observed timeline last reachable: 2026-10-19 22:48:31 UTC last content: 2026-10-19 22:48:31 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
威胁情报交叉核验 · source references
ScamAdviser Public lookup
A public ScamAdviser lookup is available. Review its current score and warnings at the source; the existence of a lookup page is not itself a malicious verdict.
View on ScamAdviser
Live-fetched via CF worker proxy pool · cached 24h
Recorded subdomains1

Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.

  • www.walletflower.funDomain record

The original observation time is not recorded for these hostnames.

技术 · 3 identified
Detected via Cloudflare Radar · Wappalyzer engine
举报此域名 提交证据,帮助保护他人

VirusTotal 分析

7 / 92 安全供应商标记了该域
View on VT
Last analyzed Previous stored snapshot: 7 detections
alphaMountain.ai
CyRadar
DNS8
Forcepoint ThreatSeeker
Fortinet
卡巴斯基
OpenPhish

存档证据

Wayback Machine Snapshot
历史快照可供证据审查
View Archive
网站性能分析

Google PageSpeed Insights — mobile performance audit of walletflower.fun · checked Oct 17, 2026

72
Needs Work
Performance
FCP
2.59s
First Contentful Paint
LCP
7.96s
Largest Contentful Paint
CLS
0.034
Cumulative Layout Shift
TBT
18ms
Total Blocking Time
SI
2.95s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://walletflower.fun/
walletflower · launch on pump.fun without connecting a wallet
Launch a pump.fun coin without connecting your wallet. Just send SOL from Phantom, Axiom or any wallet, or straight from Coinbase, Binance or any exchange, and your coin goes live in seconds.
响应
HTTP 200
HTML body
12.7 KB
Compressed
3.8 KB
Links
17 internal · 0 external
Detected technologies
cloudflare
Selected response headers
Content-Type: text/html; charset=utf-8
Cache-Control: no-cache
Content-Encoding: gzip
Server: cloudflare
HSTS: not observed DNSSEC: not observed WAF / firewall: observed Cloaking flag: not observed
Favicon fingerprint: 4df9b4057332d32747a68167900086971450fae152fbccba75fca59889f010fd
Open Graph title: launch a coin without connecting your wallet
Open Graph description: Nothing to connect, nothing to sign. Fill in your coin, send SOL from any wallet or straight from an exchange, and it's live on pump.fun in seconds.
Twitter card: summary_large_image
Saved response-header values · 11
alt-svc
h2=":443"; ma=60
Cache-Control
no-cache
CF-RAY
a4c1057e8bb823fb-FRA
Connection
keep-alive
Content-Encoding
gzip
Content-Type
text/html; charset=utf-8
Date
Sat, 17 Oct 2026 17:28:44 GMT
Nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
Report-To
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=0rjBgEIASiPTPOgDff7FkHlK8ZrKKvqg2KjuzSfqKWZoZVJi1%2F1%2Fv9eg2UkDk%2BgYIx26o9CdkaJ2pazUVIJ3ntJxeEXPLT%2FxLK3WweToWsmMVI5b7%2BflDPQU4a3k4%2B2tzu8
Server
cloudflare
Transfer-Encoding
chunked

Values retained by the collector; long values may be shortened during collection.

Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Stored observation history8

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    未知→live_content

    content_served

  2. Availability monitor · Recorded state

    未知→live_content

    content_served

  3. VirusTotal · Detection count

    6→7

  4. VirusTotal · Detection count

    5→6

  5. VirusTotal · Detection count

    4→5

Earlier observations 3
  1. Availability monitor · Recorded state

    未知→live_content

    content_served

  2. VirusTotal · Detection count

    2→4

  3. Availability monitor · First collection record

    可访问

Recorded activity

5 entries
  1. Google Safe Browsing

    No threat flag

    View source
  2. AlienVault OTX

    5 community references

    View source
  3. VirusTotal

    7/92 engine detections

    View source
  4. URLScan

    Page captured

    View source
  5. Added to PhishDestroy

    walletflower.fun

    View source

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

walletflower.fun

证据与外部报告

深度分析
Help & reporting

您是否受到本网站的影响?

4 evidence signal groups linked 0 stored notification records 最后已知的活跃状态

Listed domains receive at least one abuse report; this entry has no retained notification history.

If credentials were compromised, report immediately. Do not engage with recovery scammers.

如果您输入了帐户凭据、个人或付款信息,或者从此域下载了文件,请立即采取措施。以下资源可帮助您报告事件并保护自己。

Official reporting routes

警惕“数据恢复”诈骗! 犯罪分子可能会冒充调查员、律师或追债员再次联系受害者。 请勿支付预付费用或共享凭证。 了解有关康复欺诈的更多信息 →

向当地主管部门报告

选择您所在的国家/地区以获取 官方网络犯罪联系人 或 创建投诉草稿 →。

97个国家目录

Template-based draft · optional AI wording assistance requires separate consent

AI辅助草稿——事件详细信息由AI提供商处理 · 自行审核并提交
After a phishing incident

针对受害者的建议与指导

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

我应该立即采取什么措施?

紧急

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • 更改所有密码 — 电子邮件、Exchange 账户,以及任何使用同一密码的账户
  • 启用双因素认证 使用身份验证器应用(而非短信)。禁用基于短信的恢复功能
  • 冻结卡片 如果您在钓鱼网站上输入了银行信息

我应该为报告收集哪些信息?

联邦调查局(FBI)指南

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • 确切日期和时间 — 每笔交易的详情以及与诈骗者的首次接触
  • 屏幕截图 — 诈骗网站、聊天消息、电子邮件、钱包交易、社交媒体
  • 所有网址和域名 诈骗者使用的(包括 walletflower.fun)
  • 通信 — 诈骗者使用的电子邮件、短信、电话号码、用户名

即使你并不了解所有细节—— 不管怎样都要提交报告. 即使信息不完整,对调查仍有帮助。

我应该向哪里举报这起诈骗?

  • 联邦调查局(FBI)IC3 — 互联网犯罪投诉中心(美国联邦举报渠道)
  • 欧洲刑警组织 — 欧洲网络犯罪报告(欧盟)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • 当地警方 — 即使无法立即采取行动,也能留下正式记录

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • 虚假网站 — 与正规网站完全一致的克隆网站,仅域名略有改动
  • 猪的屠宰 — 通过Telegram/WhatsApp/交友软件花数周时间建立信任,随后钱被骗走
  • 退款诈骗 — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • 利用人工智能实施的诈骗 — 深度伪造、自动化网络钓鱼以及人工智能生成的网站,使得欺诈行为更难被察觉

将来我该如何保护自己?

  • 将官方网站添加到书签 — 切勿点击来自电子邮件、私信或广告中的链接
  • 验证域名 — 查看 PhishDestroy 在进行互动之前,请检查HTTPS、拼写和域名注册时间。
  • “好得令人难以置信”=骗局 — 保证收益、名人代言、紧迫的截止日期

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

随时掌握最新信息,确保安全

请实时监控威胁,或者如果您认为这是误报,请对该条目提出异议

实时威胁动态 对该列表提出异议
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

嵌入此报告

在您的网站或博客上分享此威胁情报

embed.html
<iframe
  src="https://phishdestroy.io/zh/embed/domain/walletflower.fun"
  title="PhishDestroy threat report for walletflower.fun"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>