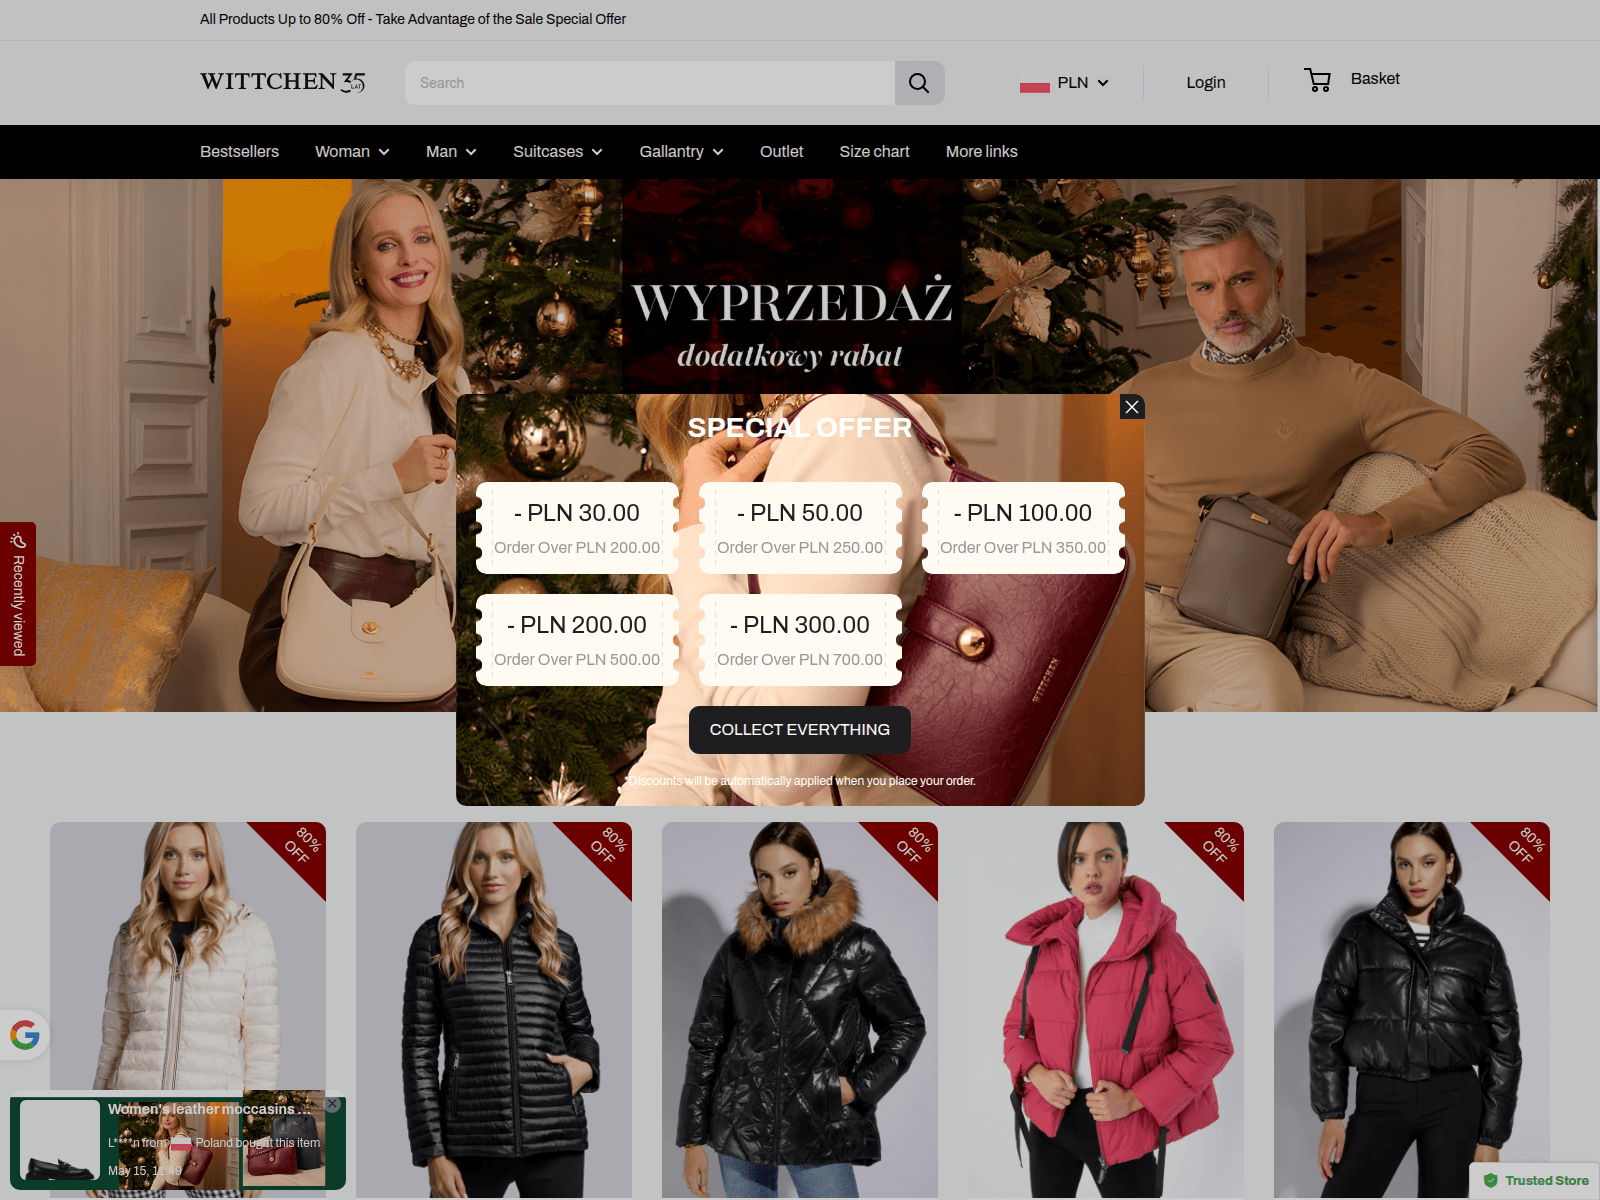
The site clones the Wittchen brand to lure visitors into entering payment card details on a fraudulent checkout form. PhishDestroy's evidence score for it is 75/100 (critical), and Spamhaus DBL lists it as phishing, 16 of 92 engines on VirusTotal flagged it on 11 Nov 2026, and 1 AlienVault OTX community report references it. Contact your bank immediately if you submitted financial information.
URLScan截图 · 2026-05-15 09:07 UTC · SHA-256 cabd4c49…12a169c
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Wittchen fashion clone offering steep discounts
The page opens with the prominent Wittchen 35 brand logo and a top banner stating "All Products Up to 80% Off - Take Advantage of the Sale Special Offer". Navigation links for Bestsellers, Woman, Man, Suitcases, Gallantry, Outlet, and Size chart line the header alongside a search bar and basket icon. A large pop-up overlay titled "SPECIAL OFFER" dominates the centre, displaying various coupon amounts such as "- PLN 30.00" for orders over "PLN 200.00" up to "- PLN 300.00" for orders over "PLN 700.00". Beneath these coupon boxes sits a dark "COLLECT EVERYTHING" button. The background shows models wearing winter jackets and holding leather handbags, with red sale banners in the corners reading "80% OFF". A bottom-left notification popup displays recent purchases with buyer names and locations to manufacture social proof of active sales.
Payment card capture and independent telemetry
The checkout mechanism submits entered payment data through an external form post to translate.googleapis.com, routing card numbers and personal details directly to the operators. Spamhaus DBL lists it as phishing, 16 of 92 engines on VirusTotal flagged it on 11 Nov 2026, and 1 AlienVault OTX community report references it, with security vendors like Kaspersky, ESET and BitDefender flagging the URL as malicious. PhishDestroy's evidence score for it is 75/100 (critical).
Shared infrastructure with related shop clones
4 other domains on PhishDestroy's list share its IP address, pointing to a coordinated network of fraudulent online stores. The server hosts multiple identical shop clones including savingsdeal.shop, savemoredeal.shop and hot-sellingstores.shop.
valuesdeal.shop hosted a fraudulent Wittchen fashion shop asking for payment details, flagged by Spamhaus DBL and 16 VirusTotal engines. Do not enter card data.
AI摘要
Wittchen fashion clone offering steep discounts The page opens with the prominent Wittchen 35 brand logo and a top banner stating "All Products Up to 80% Off - Take Advantage of the Sale Special Offer". Navigation links for Bestsellers, Woman, Man, Suitcases, Gallantry, Outlet, and Size chart line the header alongside a search bar and basket icon. A large pop-up overlay titled "SPECIAL OFFER" dominates the centre, displaying various coupon amounts such as "- PLN 30.00" for orders over "PLN 200.00" up to "- PLN 300.00" for orders over "PLN 700.00". Beneath these coupon boxes sits a dark "COLLECT EVERYTHING" button. The background shows models wearing winter jackets and holding leather handbags, with red sale banners in the corners reading "80% OFF". A bottom-left notification popup displays recent purchases with buyer names and locations to manufacture social proof of active sales. Payment card capture and independent telemetry The checkout mechanism submits entered payment data through an external form post to translate.googleapis.com, routing card numbers and personal details directly to the operators. Spamhaus DBL lists it as phishing, 16 of 92 engines on VirusTotal flagged it on 11 Nov 2026, and 1 AlienVault OTX community report references it, with security vendors like Kaspersky, ESET and BitDefender flagging the URL as malicious. PhishDestroy's evidence score for it is 75/100 (critical). Shared infrastructure with related shop clones 4 other domains on PhishDestroy's list share its IP address, pointing to a coordinated network of fraudulent online stores. The server hosts multiple identical shop clones including savingsdeal.shop, savemoredeal.shop and hot-sellingstores.shop.
According to Tranco this site has a low rank High number of suspicious websites on this server We tried to analyze the content of the site but failed This website has been reported for Phishing by IPQS This website has been reported as Suspicious by IPQS
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:14 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:14 UTClast content: 2026-11-22 11:14 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 47.251.94.120


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 MyWOT