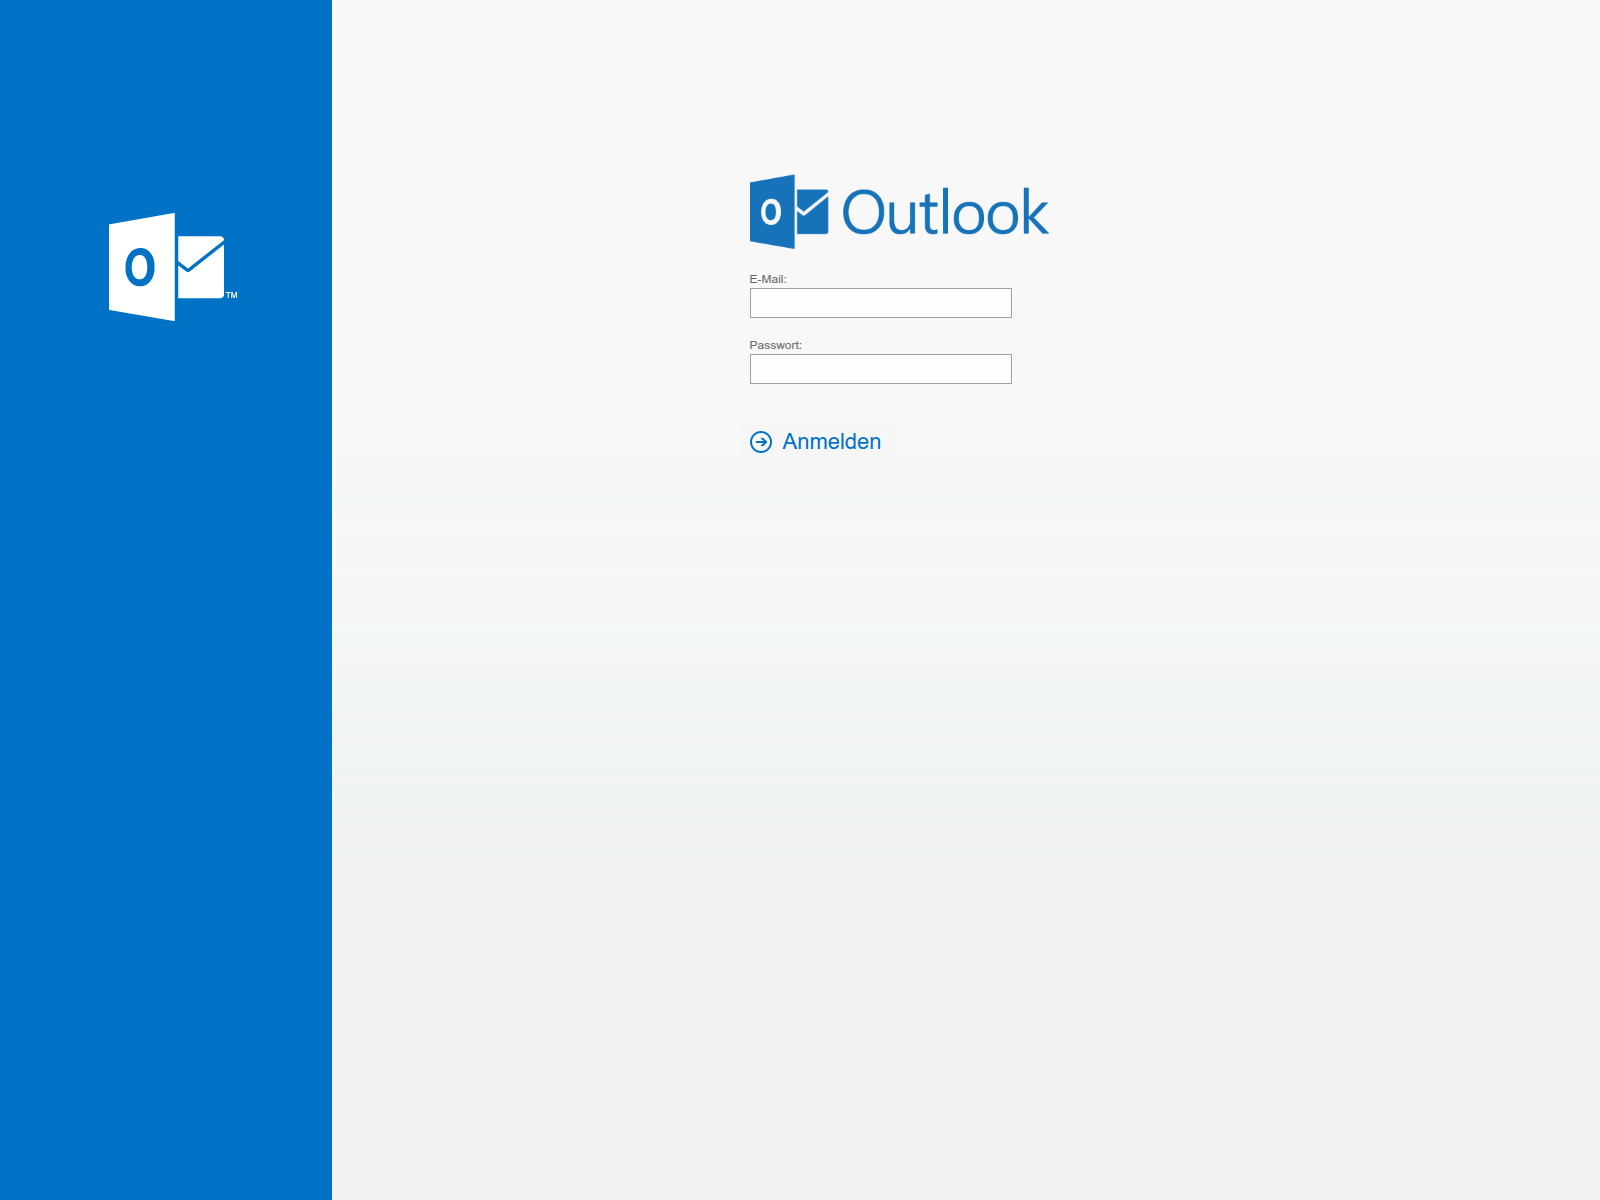
This page mimics Microsoft Outlook to collect user email credentials through a fake sign-in form hosted on a third-party platform. If you entered your password here, change your Microsoft account password immediately and check your account for unauthorized access.
URLScan截图 · 2026-11-07 03:20 UTC · SHA-256 baf4a8f2…9befd1f
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Fake Microsoft Outlook login interface
The page displays a clean, minimalist layout styled to resemble Microsoft Outlook Web Access. A solid blue sidebar occupies the left side featuring the Outlook brand logo. On the main white background, the header shows the Outlook logo alongside the text "Outlook". Below this, two input fields are clearly labelled "E-Mail:" and "Passwort:". At the bottom of the form sits a blue submit button marked with an arrow icon and the German text "Anmelden". The page asks the visitor to type their institutional or personal email address and corresponding password into these fields to proceed.
Credential harvesting mechanism and telemetry
When a visitor types their credentials and clicks the submit button, the entered data is transmitted directly to an external server via an external form post. The domain address uni-bielefeld.vercel.app uses a subdomain hosted on vercel.app, which has no affiliation with Microsoft or any university. Furthermore, PhishDestroy's evidence score for it is 85/100 (critical), and vendors such as Kaspersky, ESET and BitDefender explicitly categorize the URL as a phishing threat because urlscan classified the page as malicious, 20 of 92 VirusTotal engines flagged it on 19 Nov 2026, and Google Safe Browsing flags it.
Recommended actions for affected users
Anyone who submitted their credentials on this page must act quickly to secure their account. Reset your Microsoft account password immediately through official channels at microsoft.com. Review active sessions, connected devices, and inbox forwarding rules to ensure attackers have not established persistent access. If you reused this password on other services, update those credentials as well.
来源证据VirusTotal 20 / 92 · Google Safe Browsing: 被标记6 个来源
uni-bielefeld.vercel.app — Fake Microsoft sign in page
AI 描述
uni-bielefeld.vercel.app presents a fake Microsoft Outlook login page requesting your email and password, flagged by urlscan and 20 VirusTotal engines.
AI摘要
Fake Microsoft Outlook login interface The page displays a clean, minimalist layout styled to resemble Microsoft Outlook Web Access. A solid blue sidebar occupies the left side featuring the Outlook brand logo. On the main white background, the header shows the Outlook logo alongside the text "Outlook". Below this, two input fields are clearly labelled "E-Mail:" and "Passwort:". At the bottom of the form sits a blue submit button marked with an arrow icon and the German text "Anmelden". The page asks the visitor to type their institutional or personal email address and corresponding password into these fields to proceed. Credential harvesting mechanism and telemetry When a visitor types their credentials and clicks the submit button, the entered data is transmitted directly to an external server via an external form post. The domain address uni-bielefeld.vercel.app uses a subdomain hosted on vercel.app, which has no affiliation with Microsoft or any university. Furthermore, PhishDestroy's evidence score for it is 85/100 (critical), and vendors such as Kaspersky, ESET and BitDefender explicitly categorize the URL as a phishing threat because urlscan classified the page as malicious, 20 of 92 VirusTotal engines flagged it on 19 Nov 2026, and Google Safe Browsing flags it. Recommended actions for affected users Anyone who submitted their credentials on this page must act quickly to secure their account. Reset your Microsoft account password immediately through official channels at microsoft.com. Review active sessions, connected devices, and inbox forwarding rules to ensure attackers have not established persistent access. If you reused this password on other services, update those credentials as well.

 64.29.17.195


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT