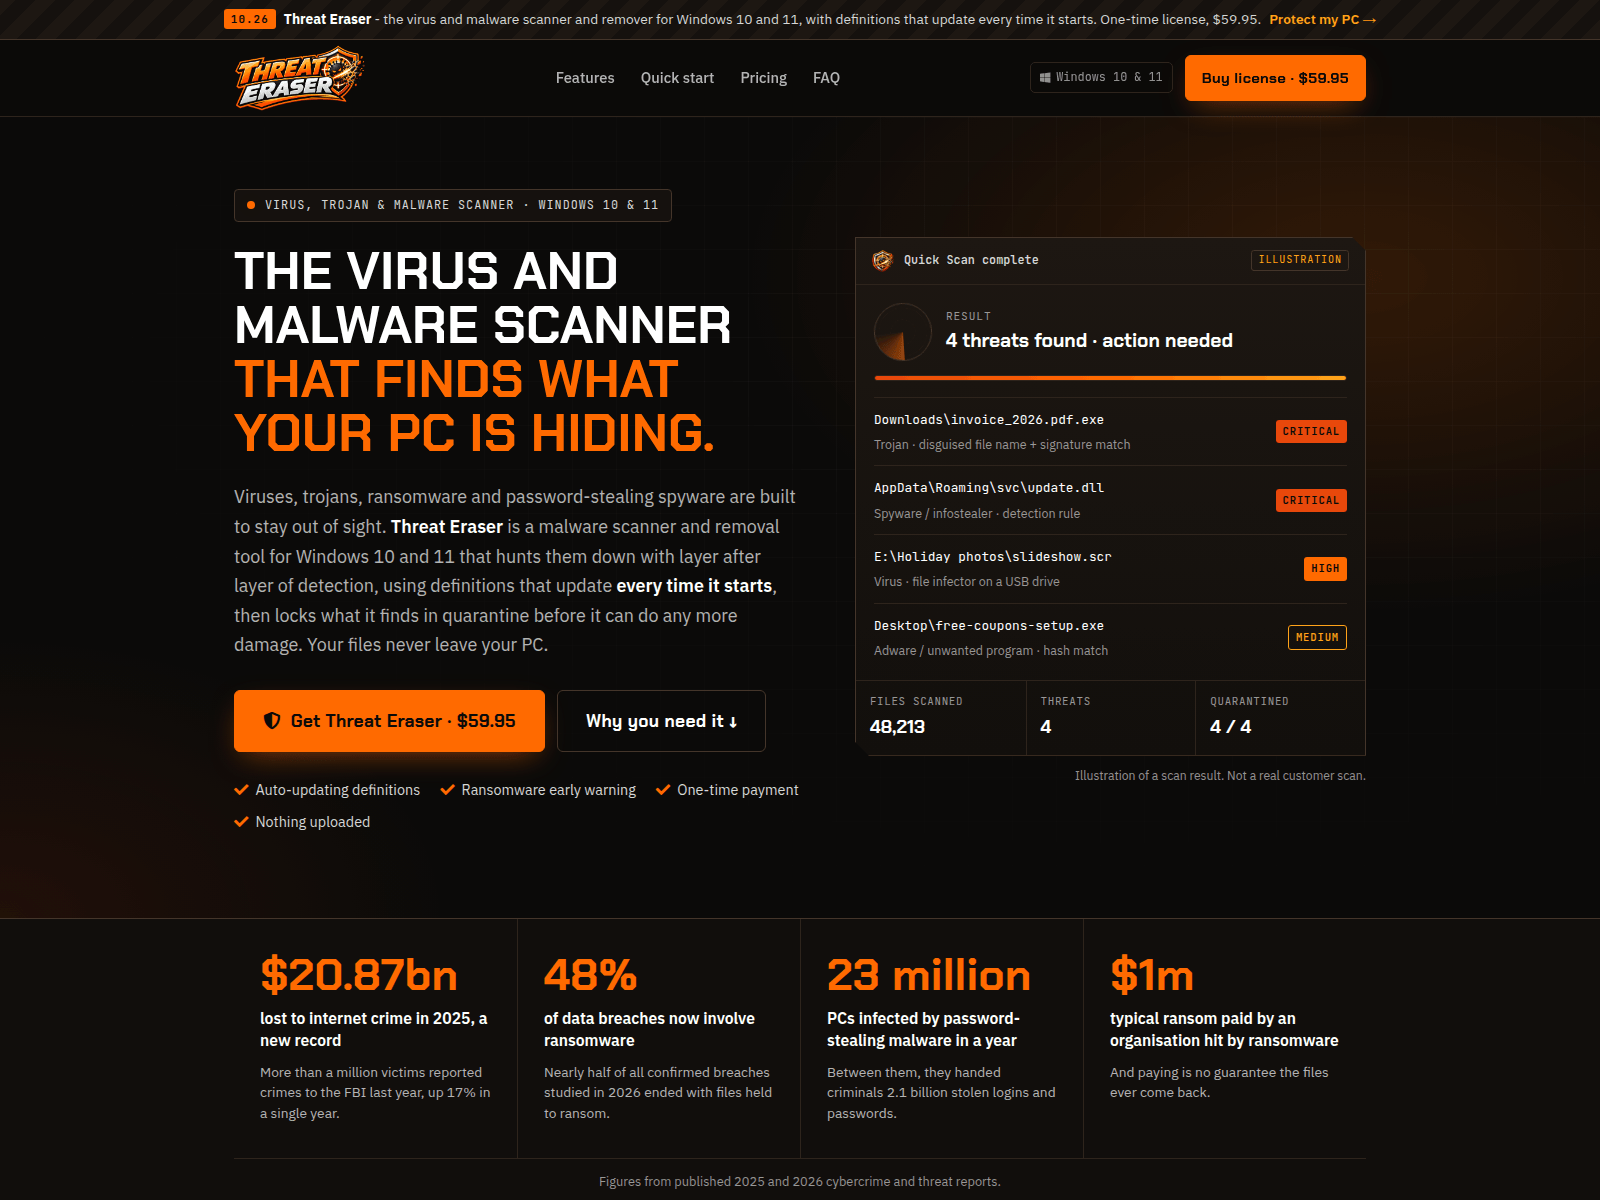
On 2026-11-09, threateraser.com displayed a product landing page for Threat Eraser, described as a virus and malware scanner and remover for Windows 10 and 11. The headline reads "The virus and malware scanner that finds what your PC is hiding," and the page states that definitions update every time it starts, with a one-time license priced at $59.95. A "Get Threat Eraser" button and a "Buy license" button appear as purchase actions, alongside feature notes such as auto-updating definitions, ransomware early warning, and nothing uploaded.
URLScan截图 · 2026-11-09 18:55 UTC · SHA-256 f7ba3495…f1a8019
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-09, threateraser.com displayed a product landing page for Threat Eraser, described as a virus and malware scanner and remover for Windows 10 and 11. The headline reads "The virus and malware scanner that finds what your PC is hiding," and the page states that definitions update every time it starts, with a one-time license priced at $59.95. A "Get Threat Eraser" button and a "Buy license" button appear as purchase actions, alongside feature notes such as auto-updating definitions, ransomware early warning, and nothing uploaded.
The stored VirusTotal domain result reports 8 detections out of 92 engines. CRDF reported "malicious"; Fortinet reported "spam".
PhishDestroy records threateraser.com as a page promoting Threat Eraser, a paid Windows malware scanner and removal tool priced at $59.95.
AI摘要
On 2026-11-09, threateraser.com displayed a product landing page for Threat Eraser, described as a virus and malware scanner and remover for Windows 10 and 11. The headline reads "The virus and malware scanner that finds what your PC is hiding," and the page states that definitions update every time it starts, with a one-time license priced at $59.95. A "Get Threat Eraser" button and a "Buy license" button appear as purchase actions, alongside feature notes such as auto-updating definitions, ransomware early warning, and nothing uploaded. The stored VirusTotal domain result reports 8 detections out of 92 engines. CRDF reported "malicious"; Fortinet reported "spam".
最新的 HTTP 观察结果RedirectingHTTP redirect observed80%2026-11-22 11:19 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:19 UTClast content: 2026-11-13 03:48 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 192.142.10.5


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT