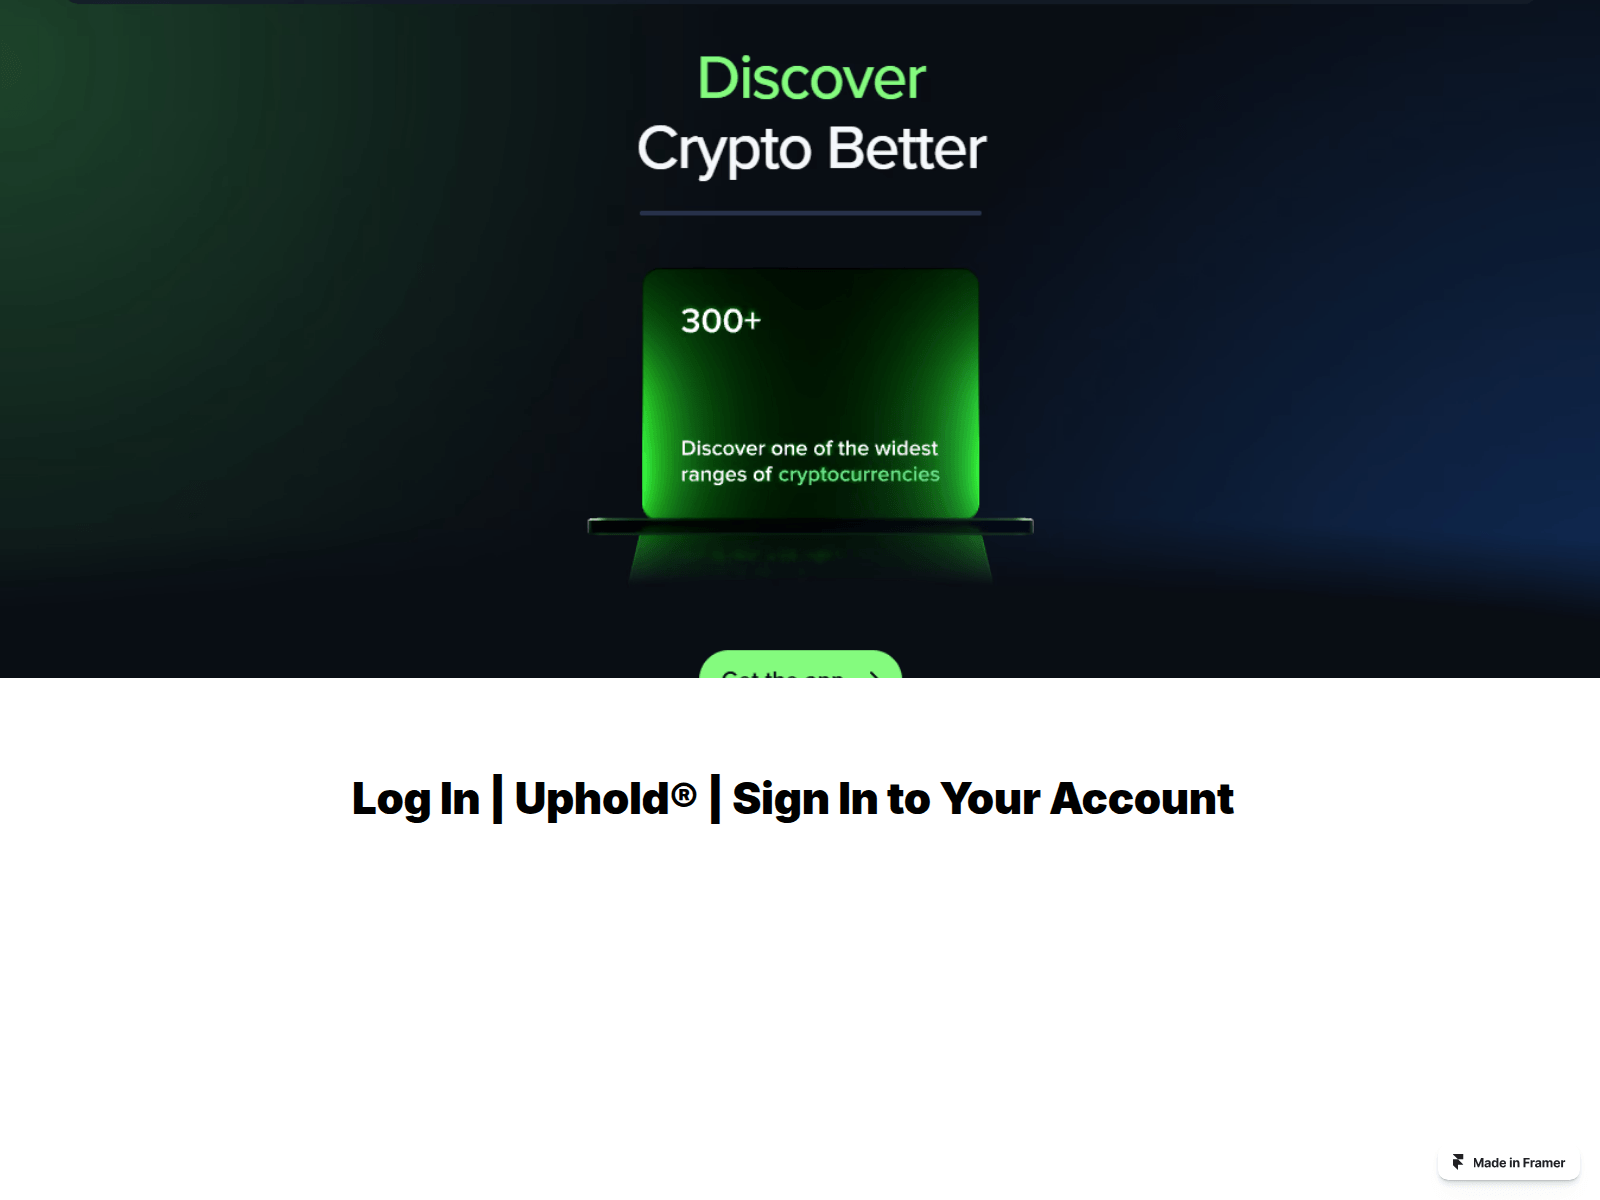
This site is a fake Uphold login page hosted as a subdomain on the Framer website builder. Its long hostname strings together "sso", "uphold-com", "cdn" and a misspelled "autth" to look like a legitimate Uphold single sign-on or authentication address. It targets Uphold customers who hold crypto and fiat balances on the platform. PhishDestroy first flagged it on 2026-08-31. The page has been offline since 2026-09-29 and was still down at the last check on 2026-10-19.
诈骗手法解析
The page carried the title "Log In | Uphold® | Sign In to Your Account", copying the wording a user expects on the real sign-in screen. Victims usually arrive through a link in a fake security alert, support message or ad. They then type their email and password, and often a one-time 2FA code, into a form controlled by the attacker. With those credentials the operator can log into the real Uphold account, move funds out and change recovery settings before the owner notices. urlscan.io also detected Microsoft branding on the page, a sign that the same lure may have been used to collect Microsoft account logins.
证据
On 2026-09-11, 17 of 89 VirusTotal engines flagged the domain, including BitDefender, ESET, Fortinet, Emsisoft, Forcepoint ThreatSeeker, alphaMountain.ai, CyRadar and Chong Lua Dao. That is broad agreement from security vendors that work independently of each other. urlscan.io gave a malicious verdict and identified the Uphold and Microsoft brands on the page. Beyond PhishDestroy, the domain appears on the MetaMask and SEAL blocklists.
基础设施
The operator did not register a domain of their own. They built the page on Framer's hosted site service, so the CSC Corporate Domains registration belongs to Framer's parent domain, not to the attacker. Free builder subdomains let a phishing page go live within minutes and borrow the platform's reputation. Traffic was served from Amazon.com, Inc. infrastructure in the Netherlands. The Let's Encrypt certificate shows that the padlock icon proves nothing about who runs a site.
What to do
If you entered your Uphold login on this page, change your Uphold password right away from the official app or site. Then check active sessions, linked devices, withdrawal addresses and recent transactions for anything you did not do. Reset two-factor authentication, and move to an authenticator app or hardware key if you were using SMS. Contact Uphold support to report a possible account takeover and ask them to freeze withdrawals if anything looks wrong. If you reuse that password, including on a Microsoft account, change it everywhere. Security teams should block the Framer subdomain and search mail and proxy logs for visits or credential submissions after 2026-08-31.
sso-uphold-com-cdn-a-autth.framer.website is a credential phishing page posing as the Uphold sign-in to steal account logins from crypto exchange users.
AI摘要
Overview This site is a fake Uphold login page hosted as a subdomain on the Framer website builder. Its long hostname strings together "sso", "uphold-com", "cdn" and a misspelled "autth" to look like a legitimate Uphold single sign-on or authentication address. It targets Uphold customers who hold crypto and fiat balances on the platform. PhishDestroy first flagged it on 2026-08-31. The page has been offline since 2026-09-29 and was still down at the last check on 2026-10-19. How the scam works The page carried the title "Log In | Uphold® | Sign In to Your Account", copying the wording a user expects on the real sign-in screen. Victims usually arrive through a link in a fake security alert, support message or ad. They then type their email and password, and often a one-time 2FA code, into a form controlled by the attacker. With those credentials the operator can log into the real Uphold account, move funds out and change recovery settings before the owner notices. urlscan.io also detected Microsoft branding on the page, a sign that the same lure may have been used to collect Microsoft account logins. Evidence On 2026-09-11, 17 of 89 VirusTotal engines flagged the domain, including BitDefender, ESET, Fortinet, Emsisoft, Forcepoint ThreatSeeker, alphaMountain.ai, CyRadar and Chong Lua Dao. That is broad agreement from security vendors that work independently of each other. urlscan.io gave a malicious verdict and identified the Uphold and Microsoft brands on the page. Beyond PhishDestroy, the domain appears on the MetaMask and SEAL blocklists. Infrastructure The operator did not register a domain of their own. They built the page on Framer's hosted site service, so the CSC Corporate Domains registration belongs to Framer's parent domain, not to the attacker. Free builder subdomains let a phishing page go live within minutes and borrow the platform's reputation. Traffic was served from Amazon.com, Inc. infrastructure in the Netherlands. The Let's Encrypt certificate shows that the padlock icon proves nothing about who runs a site. What to do If you entered your Uphold login on this page, change your Uphold password right away from the official app or site. Then check active sessions, linked devices, withdrawal addresses and recent transactions for anything you did not do. Reset two-factor authentication, and move to an authenticator app or hardware key if you were using SMS. Contact Uphold support to report a possible account takeover and ask them to freeze withdrawals if anything looks wrong. If you reuse that password, including on a Microsoft account, change it everywhere. Security teams should block the Framer subdomain and search mail and proxy logs for visits or credential submissions after 2026-08-31. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a0a8bc-fb61-72a8-9307-c5b1a105dd68/ VirusTotal report: https://www.virustotal.com/gui/domain/sso-uphold-com-cdn-a-autth.framer.website Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=sso-uphold-com-cdn-a-autth.framer.website Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/


 31.43.161.6


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT