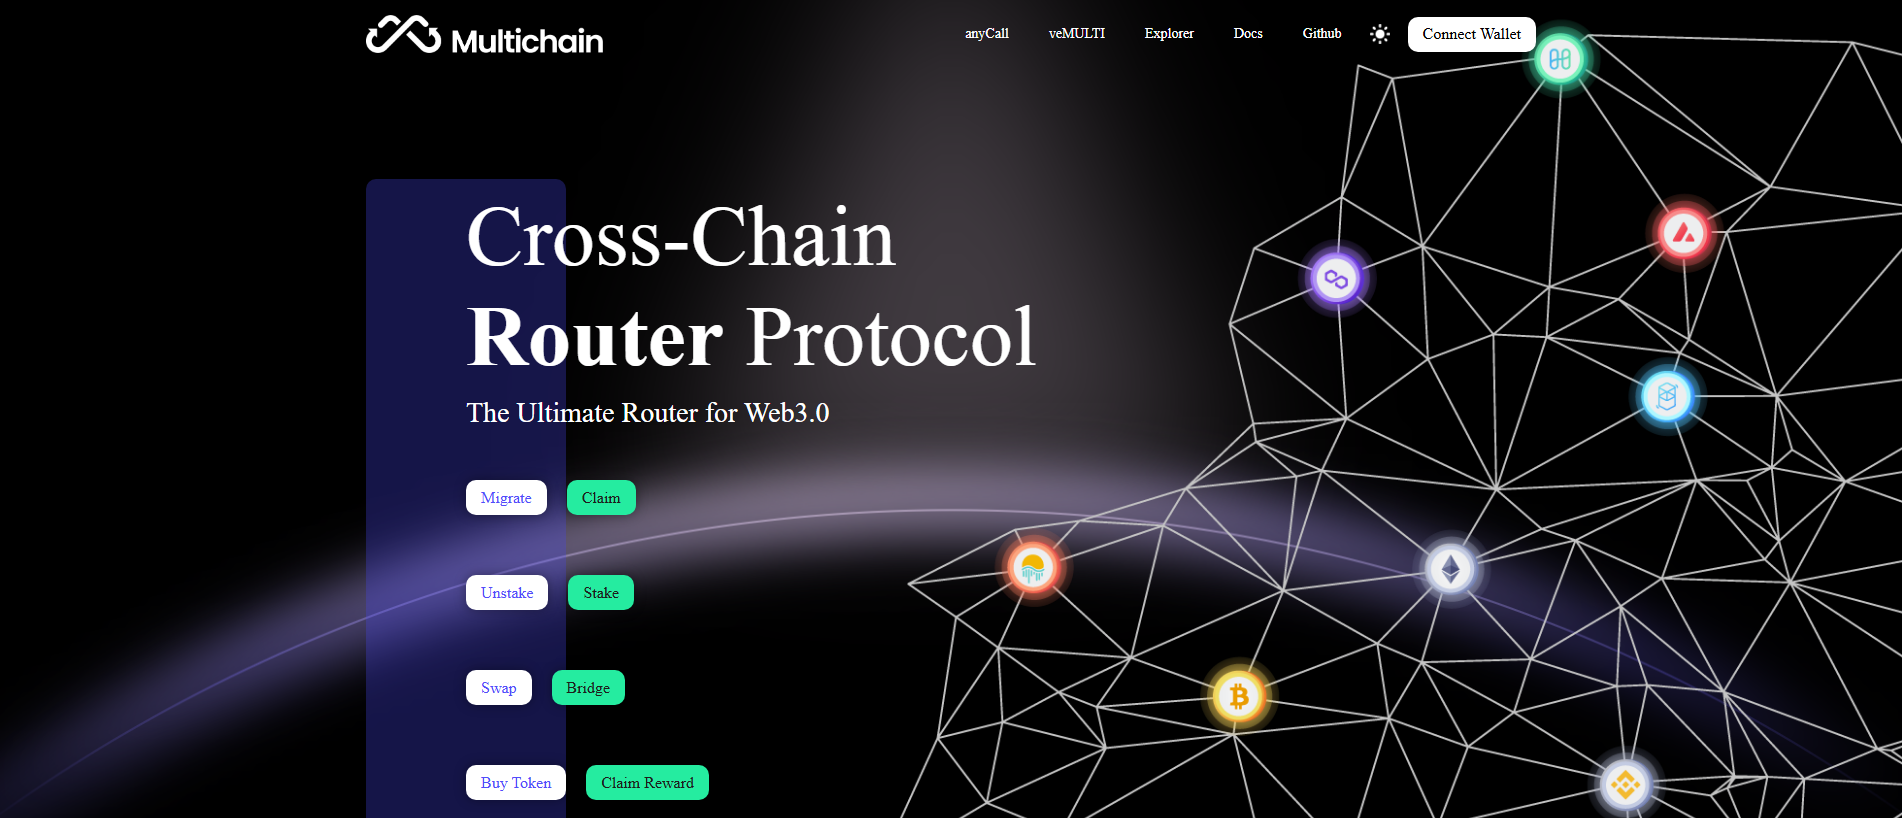
The captured screenshot from 2026-10-26 shows a dark landing page branded Multichain, headlined Cross-Chain Router Protocol and The Ultimate Router for Web3.0, with a Connect Wallet button and a column of action buttons. PhishDestroy listed the domain after its automated assessment classified the page as a crypto wallet drainer, first recording it on 2026-10-26.
诈骗手法解析
The page mimics a cross-chain bridge and pairs troubleshooting-style buttons such as Slippage Error with Rectification and Update Balance with Unable To Buy Coins / Tokens. As a category risk, visitors are steered to connect a wallet and sign transactions or token approvals under the pretense of a migration, claim or fix, which can let draining contract logic take their assets.
证据
The screenshot shows Multichain branding, a Connect Wallet control, and paired lures including Migrate/Claim, Swap/Bridge, Slippage Error/Rectification and Update Balance. urlscan rated the capture malicious with an ML score of 98 and an overall phishing score of 100 on 2026-10-26; Google Safe Browsing showed no flag, Spamhaus listed nothing and OTX recorded 0 pulses. VirusTotal flagged the domain as malicious, with labelling vendors including ESET, Fortinet, Sophos and Netcraft, while the MetaMask and SEAL blocklists and PhishDestroy's own blocklist also listed it, and the sole redirect was an HTTP-to-HTTPS 307. Inspection logged 124 requests, trackers for Cloudflare, Google Fonts, jsDelivr and Cloudflare Insights, a wallet-connect stack alongside Solana transaction libraries and CryptoJS in globals, and 3 distinct script SHA256 hashes for pivoting (one begins 0e75ce1e8b3a).
基础设施
Notable weaknesses lead: no CSP, no HSTS, no X-Frame-Options, no Permissions-Policy and no COOP, COEP or CORP; X-Content-Type-Options and Referrer-Policy present. TLS 1.3 with TLS_AES_256_GCM_SHA384, forward secrecy, ALPN h2; no SPF, DKIM or DMARC email authentication; CAA present; DNSSEC unsigned. The domain ran behind Cloudflare with a Cloudflare WAF and Cloudflare nameservers; no registrar was recorded.
What to do
If you visited smninw-main.pages.dev, connected a wallet or submitted data, stop signing and treat every prompt from it as hostile. Review your recent wallet connections and token approvals, revoke anything unrecognized, and move remaining assets to a fresh wallet you control. Defenders should block smninw-main.pages.dev at proxy, DNS and endpoint layers and share its script hashes and page indicators with peers.
PhishDestroy assesses smninw-main.pages.dev as a crypto wallet drainer impersonating the Multichain cross-chain protocol.
AI摘要
Overview The captured screenshot from 2026-10-26 shows a dark landing page branded Multichain, headlined Cross-Chain Router Protocol and The Ultimate Router for Web3.0, with a Connect Wallet button and a column of action buttons. PhishDestroy listed the domain after its automated assessment classified the page as a crypto wallet drainer, first recording it on 2026-10-26. How the scam works The page mimics a cross-chain bridge and pairs troubleshooting-style buttons such as Slippage Error with Rectification and Update Balance with Unable To Buy Coins / Tokens. As a category risk, visitors are steered to connect a wallet and sign transactions or token approvals under the pretense of a migration, claim or fix, which can let draining contract logic take their assets. Evidence The screenshot shows Multichain branding, a Connect Wallet control, and paired lures including Migrate/Claim, Swap/Bridge, Slippage Error/Rectification and Update Balance. urlscan rated the capture malicious with an ML score of 98 and an overall phishing score of 100 on 2026-10-26; Google Safe Browsing showed no flag, Spamhaus listed nothing and OTX recorded 0 pulses. VirusTotal flagged the domain as malicious, with labelling vendors including ESET, Fortinet, Sophos and Netcraft, while the MetaMask and SEAL blocklists and PhishDestroy's own blocklist also listed it, and the sole redirect was an HTTP-to-HTTPS 307. Inspection logged 124 requests, trackers for Cloudflare, Google Fonts, jsDelivr and Cloudflare Insights, a wallet-connect stack alongside Solana transaction libraries and CryptoJS in globals, and 3 distinct script SHA256 hashes for pivoting (one begins 0e75ce1e8b3a). Infrastructure Notable weaknesses lead: no CSP, no HSTS, no X-Frame-Options, no Permissions-Policy and no COOP, COEP or CORP; X-Content-Type-Options and Referrer-Policy present. TLS 1.3 with TLS_AES_256_GCM_SHA384, forward secrecy, ALPN h2; no SPF, DKIM or DMARC email authentication; CAA present; DNSSEC unsigned. The domain ran behind Cloudflare with a Cloudflare WAF and Cloudflare nameservers; no registrar was recorded. What to do If you visited smninw-main.pages.dev, connected a wallet or submitted data, stop signing and treat every prompt from it as hostile. Review your recent wallet connections and token approvals, revoke anything unrecognized, and move remaining assets to a fresh wallet you control. Defenders should block smninw-main.pages.dev at proxy, DNS and endpoint layers and share its script hashes and page indicators with peers. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1780e-bf76-718e-ab93-3bce04b5715f/ Stored capture screenshot: https://i.ibb.co/JW4JBZHB/eef037f0eeb7.png URLScan screenshot (2026-10-26T09:27:01Z): https://screenshots.phishdestroy.io/us/01a17788-a526-731a-b3f1-58777006effd.png URLScan capture report: https://urlscan.io/result/01a17788-a526-731a-b3f1-58777006effd/ URLScan screenshot (2026-10-26T11:49:22Z): https://screenshots.phishdestroy.io/us/01a1780b-0f88-7075-8806-0b354e4d5d0e.png URLScan capture report: https://urlscan.io/result/01a1780b-0f88-7075-8806-0b354e4d5d0e/ VirusTotal report: https://www.virustotal.com/gui/domain/smninw-main.pages.dev Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=smninw-main.pages.dev Archived copy: https://web.archive.org/web/20261026114320/https://smninw-main.pages.dev/ Revoke token approvals: https://revoke.cash/ Report crypto fraud (Chainabuse): https://www.chainabuse.com/report Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Multichain is a cross-chain router protocol; an infrustructure for multi-chain ecosystem, envisioned to become the ultimate router for Web 3. Non-custodial+MPC, Non Slippage Swap, Multichain Router
Last: 2026-10-26T11:43:20Z; First: 2025-01-21T19:20:31Z; Changes: 3; Days archived: 4; Scans per day: 0; Avg page bytes: 3303
页面标题与元数据
Title: Multichain - Cross-Chain Router Protocol; Keywords: Multichain, Anyswap, cross-chain router, cross chain bridge, cross chain router; Description: Multichain is a cross-chain router protocol; an infrustructure for multi-chain ecosystem, envisioned to become the ultimate router for Web 3. Non-custodial+MPC, Non Slippage Swap, Multichain Router
证据层Availability: Content servingContent: Content served at rootDNS: Stale
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:30 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:30 UTClast content: 2026-11-22 11:30 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Multichain is a cross-chain router protocol; an infrustructure for multi-chain ecosystem, envisioned to become the ultimate router for Web 3. Non-custodial+MPC, Non Slippage Swap, Multichain Router

 188.114.96.3


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT