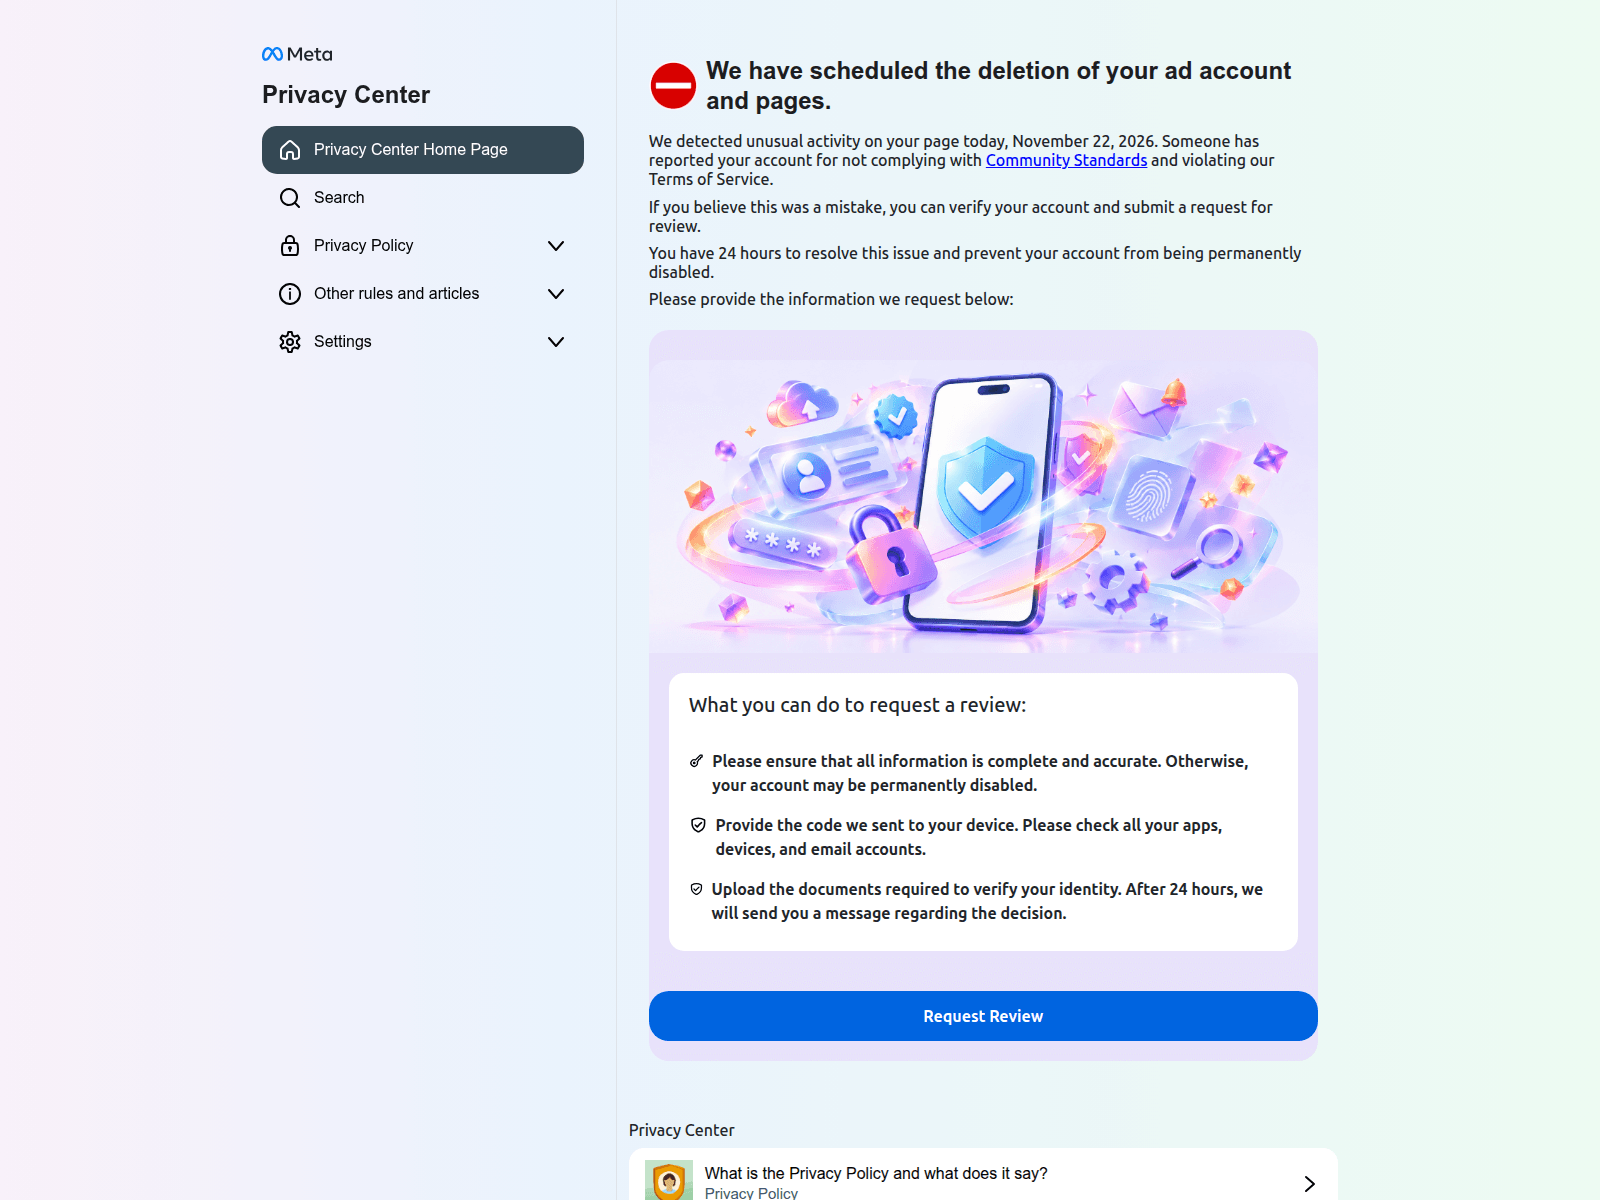
The reconciliation-anemone-3429.s2485121.workers.dev page mimics a Meta Privacy Center notification, falsely claiming that your ad account is scheduled for deletion and requesting your password. If you entered your details, immediately change your password, enable two-factor authentication, and check your real account settings on facebook.com.
URLScan截图 · 2026-11-22 15:27 UTC · SHA-256 c9329e90…2a58954
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
Fake Meta privacy center notice and credential collection
The page mimics a Meta Privacy Center dashboard featuring a sidebar with standard navigation links such as Privacy Center Home Page, Search, Privacy Policy, Other rules and articles, and Settings. The main content area displays a large red warning symbol accompanied by the headline "We have scheduled the deletion of your ad account and pages." The text claims that unusual activity was detected on November 22, 2026, and warns that the account will be permanently disabled within 24 hours unless a review is requested. An illustration shows a smartphone surrounded by security icons, a padlock, and a credit card. Below this, a panel titled "What you can do to request a review" lists requirements to ensure information is complete, provide a verification code sent to your device, and upload identity documents. A prominent blue button at the bottom invites visitors to click "Request Review" to submit their credentials.
Credential harvesting mechanism and security telemetry
The form is designed to capture sensitive user credentials and transmit them directly to an external server controlled by the operators, posing as a legitimate administrative check. urlscan classified the page as malicious, 11 of 92 engines on VirusTotal flagged it on 22 Nov 2026, and OpenPhish blocks it, its PhishDestroy evidence score is 75/100 (critical). Security vendors including ESET, Fortinet and Sophos flag the URL as malicious, confirming that independent security tools recognize the threat.
Recommended actions for affected users
This address is not the official site; legitimate administration takes place exclusively at facebook.com. Anyone who followed the prompts and entered their password must immediately log into their real account to change their credentials, terminate active sessions, and check for unauthorized changes to connected ad accounts or business managers.
reconciliation-anemone-3429.s2485121.workers.dev — Fake Meta
AI 描述
reconciliation-anemone-3429.s2485121.workers.dev mimics a Meta Privacy Center warning to steal Facebook passwords, flagged by urlscan and 11 VirusTotal engines.
AI摘要
Fake Meta privacy center notice and credential collection The page mimics a Meta Privacy Center dashboard featuring a sidebar with standard navigation links such as Privacy Center Home Page, Search, Privacy Policy, Other rules and articles, and Settings. The main content area displays a large red warning symbol accompanied by the headline "We have scheduled the deletion of your ad account and pages." The text claims that unusual activity was detected on November 22, 2026, and warns that the account will be permanently disabled within 24 hours unless a review is requested. An illustration shows a smartphone surrounded by security icons, a padlock, and a credit card. Below this, a panel titled "What you can do to request a review" lists requirements to ensure information is complete, provide a verification code sent to your device, and upload identity documents. A prominent blue button at the bottom invites visitors to click "Request Review" to submit their credentials. Credential harvesting mechanism and security telemetry The form is designed to capture sensitive user credentials and transmit them directly to an external server controlled by the operators, posing as a legitimate administrative check. urlscan classified the page as malicious, 11 of 92 engines on VirusTotal flagged it on 22 Nov 2026, and OpenPhish blocks it, its PhishDestroy evidence score is 75/100 (critical). Security vendors including ESET, Fortinet and Sophos flag the URL as malicious, confirming that independent security tools recognize the threat. Recommended actions for affected users This address is not the official site; legitimate administration takes place exclusively at facebook.com. Anyone who followed the prompts and entered their password must immediately log into their real account to change their credentials, terminate active sessions, and check for unauthorized changes to connected ad accounts or business managers.

 Cloudflare


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT