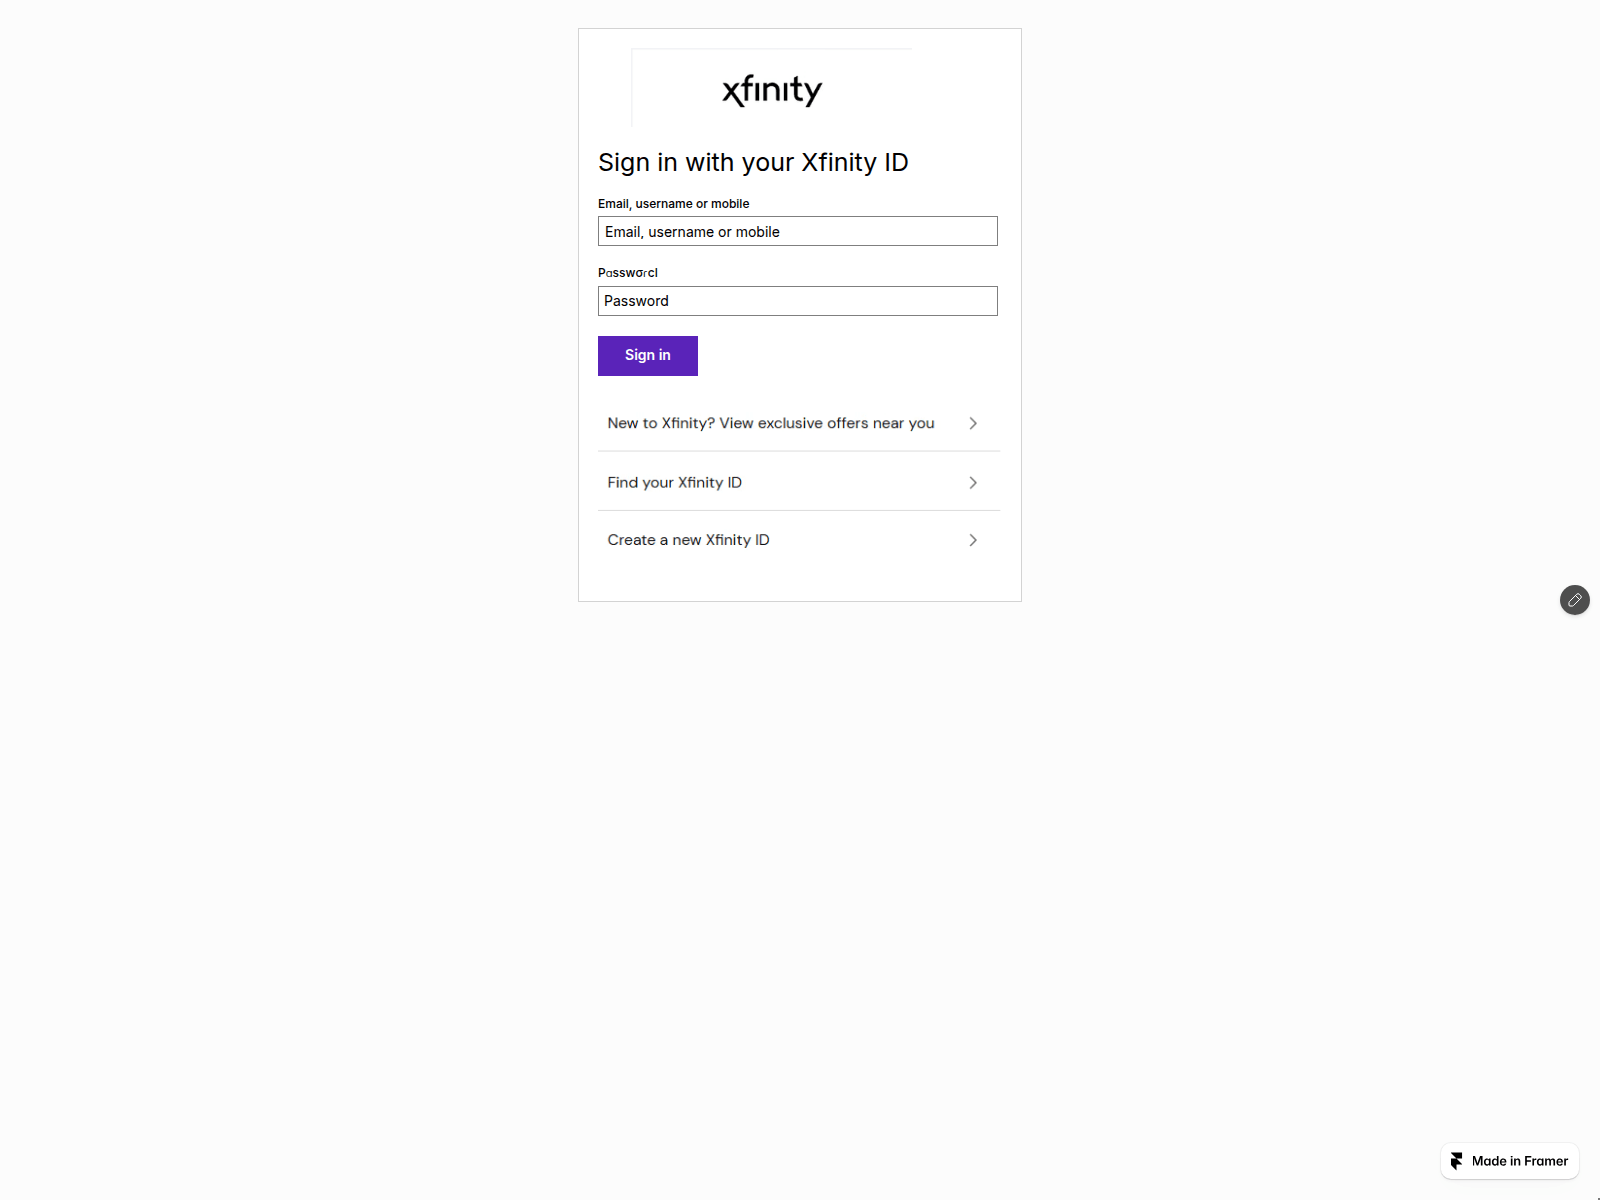
On 2026-11-07, fresh-experiences-537560.framer.app served a page displaying an Xfinity-branded sign-in card. The card shows the Xfinity wordmark above the heading "Sign in with your Xfinity ID," followed by an "Email, username or mobile" field, a "Password" field, and a purple "Sign in" button. Below the button are three links: "New to Xfinity? View exclusive offers near you," "Find your Xfinity ID," and "Create a new Xfinity ID." A "Made in Framer" badge appears in the lower-right corner.
URLScan截图 · 2026-11-07 06:29 UTC · SHA-256 76d4ef5e…d9c6d21
PhishDestroy分析,审阅版
为保留原始取证记录,下方的 PhishDestroy AI 详细分析仍使用英文。
On 2026-11-07, fresh-experiences-537560.framer.app served a page displaying an Xfinity-branded sign-in card. The card shows the Xfinity wordmark above the heading "Sign in with your Xfinity ID," followed by an "Email, username or mobile" field, a "Password" field, and a purple "Sign in" button. Below the button are three links: "New to Xfinity? View exclusive offers near you," "Find your Xfinity ID," and "Create a new Xfinity ID." A "Made in Framer" badge appears in the lower-right corner.
The stored VirusTotal domain result reports 12 detections out of 92 engines. DNS8 reported "phishing"; ESET reported "phishing".
fresh-experiences-537560.framer.app: Recorded Xfinity ID sign-in page
AI 描述
PhishDestroy records fresh-experiences-537560.framer.app as a page showing an Xfinity ID sign-in form with email and password fields.
AI摘要
On 2026-11-07, fresh-experiences-537560.framer.app served a page displaying an Xfinity-branded sign-in card. The card shows the Xfinity wordmark above the heading "Sign in with your Xfinity ID," followed by an "Email, username or mobile" field, a "Password" field, and a purple "Sign in" button. Below the button are three links: "New to Xfinity? View exclusive offers near you," "Find your Xfinity ID," and "Create a new Xfinity ID." A "Made in Framer" badge appears in the lower-right corner. The stored VirusTotal domain result reports 12 detections out of 92 engines. DNS8 reported "phishing"; ESET reported "phishing".