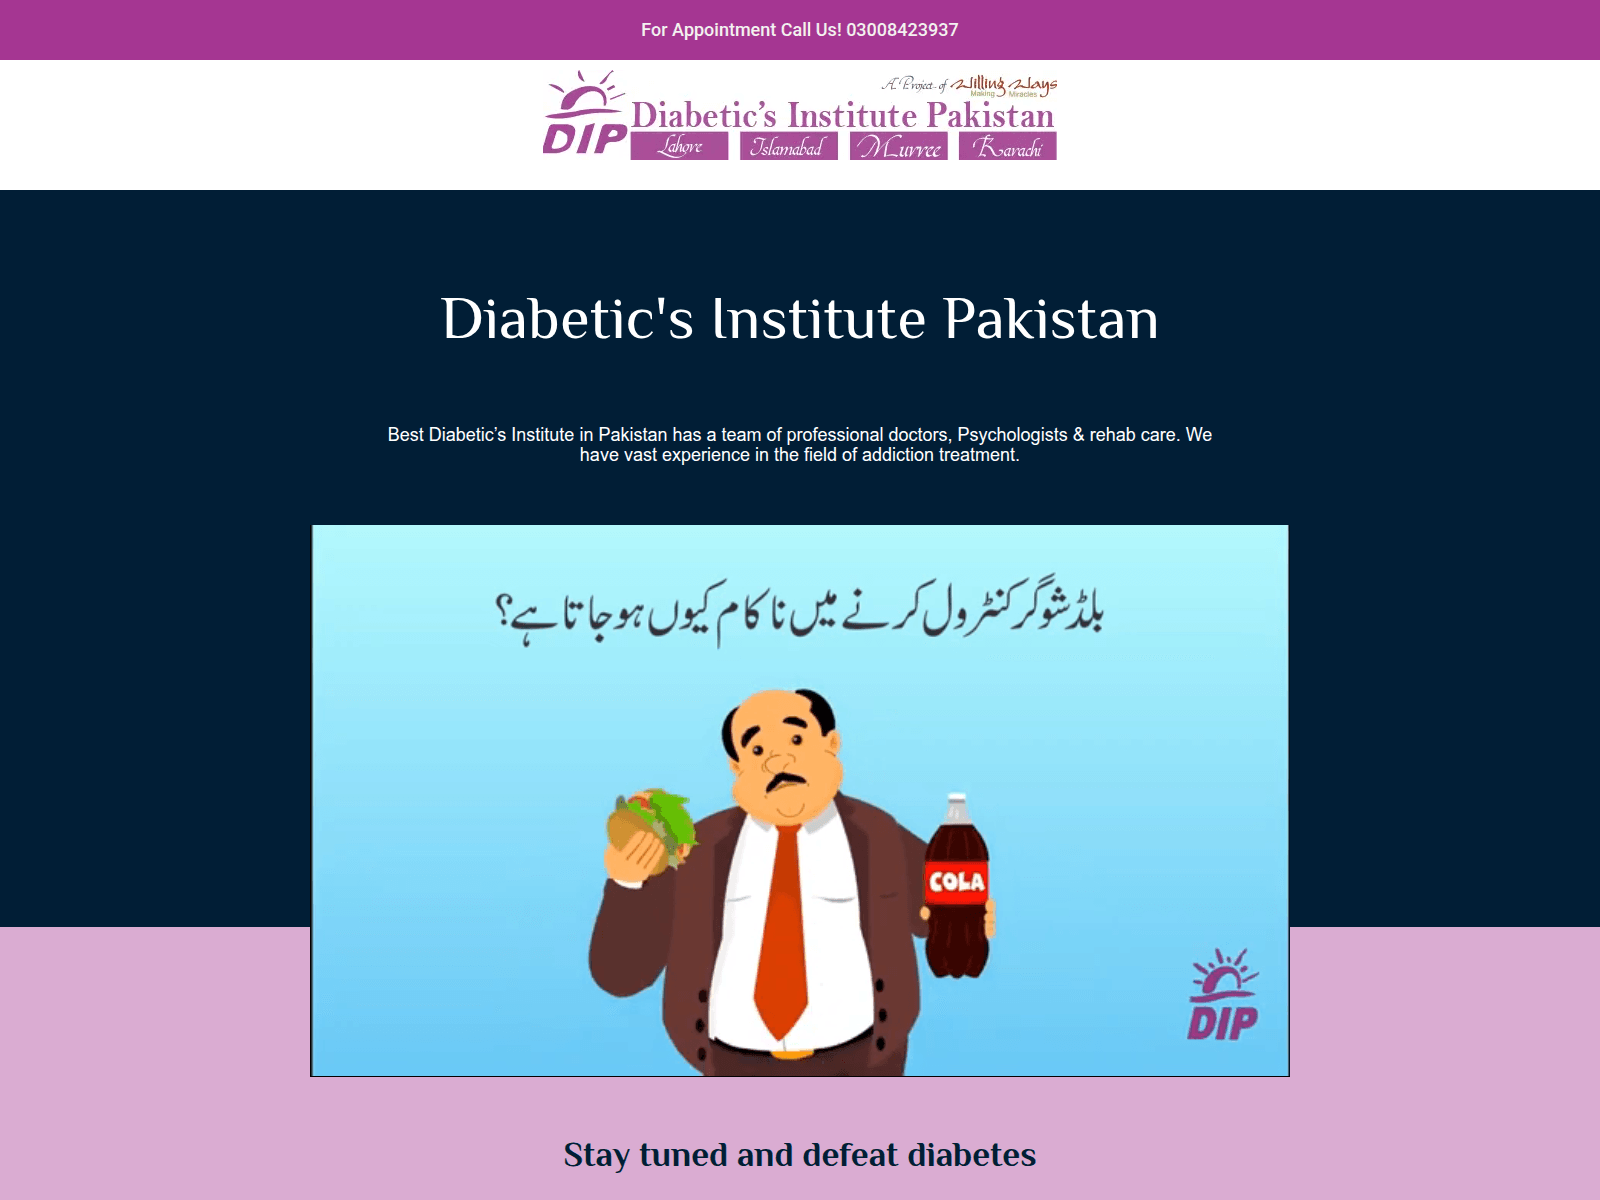
The captured screenshot shows a health page headed Diabetic's Institute Pakistan, topped by a banner reading For Appointment Call Us with a phone number, body copy claiming professional doctors, psychologists and rehab care, and an embedded video player. PhishDestroy listed the domain after VirusTotal flagged it as malicious. The domain was first seen on 2026-10-25.
诈骗手法解析
No form fields appeared in the capture; the page instead pushed visitors toward the appointment phone number shown in the banner, a pattern used to collect personal and health details during an unsolicited call. Paired with promises of treatment and rehab care, it enables social engineering of people seeking diabetes or addiction support.
证据
The screenshot shows the appointment call banner, the institute branding with city names, and the treatment claims described above. urlscan returned a non-malicious overall verdict with an engine ML score of minus 19 on 2026-10-25 and followed a 307 redirect from HTTP to HTTPS. VirusTotal flagged the domain as malicious, with phishing labels from Kaspersky and Sophos, and Cloudflare Radar tagged it malware on 2026-10-25, while Spamhaus listed nothing on 2026-10-25, Google Safe Browsing was not flagged on 2026-10-26, external blocklists showed zero entries with PhishDestroy's internal list matching on 2026-10-26, and OTX recorded 5 pulses on 2026-10-25. Inspection found a WordPress page running jQuery and Elementor with Contact Form 7 alongside Google, Google Marketing Platform and YouTube trackers, and 10 distinct script SHA256 hashes are recorded, for example cb6f2d32c49d, for campaign pivoting.
基础设施
Notable weaknesses first: HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy and COOP, COEP and CORP are all absent, Content-Security-Policy carries only upgrade-insecure-requests, SPF is present with no DKIM or DMARC, and DNSSEC is unsigned. The domain was registered through Dynadot Inc on 2007-12-14 and recorded on Hostinger International Limited infrastructure, with no WAF shown in the capture. TLS 1.3, TLS_AES_256_GCM_SHA384, forward secrecy, ALPN h2; a CAA record is present.
What to do
If you called the number in the banner or shared personal or health information, stop further contact, monitor for follow-up approaches, and report the captured site to your provider. Do not send payments or documents requested during such calls. Defenders should block diabetespakistan.com at the proxy, mail and endpoint layers and keep it on deny lists.
PhishDestroy assesses diabetespakistan.com as a fake clinic appointment lure soliciting appointment calls from visitors.
AI摘要
Overview The captured screenshot shows a health page headed Diabetic's Institute Pakistan, topped by a banner reading For Appointment Call Us with a phone number, body copy claiming professional doctors, psychologists and rehab care, and an embedded video player. PhishDestroy listed the domain after VirusTotal flagged it as malicious. The domain was first seen on 2026-10-25. How the scam works No form fields appeared in the capture; the page instead pushed visitors toward the appointment phone number shown in the banner, a pattern used to collect personal and health details during an unsolicited call. Paired with promises of treatment and rehab care, it enables social engineering of people seeking diabetes or addiction support. Evidence The screenshot shows the appointment call banner, the institute branding with city names, and the treatment claims described above. urlscan returned a non-malicious overall verdict with an engine ML score of minus 19 on 2026-10-25 and followed a 307 redirect from HTTP to HTTPS. VirusTotal flagged the domain as malicious, with phishing labels from Kaspersky and Sophos, and Cloudflare Radar tagged it malware on 2026-10-25, while Spamhaus listed nothing on 2026-10-25, Google Safe Browsing was not flagged on 2026-10-26, external blocklists showed zero entries with PhishDestroy's internal list matching on 2026-10-26, and OTX recorded 5 pulses on 2026-10-25. Inspection found a WordPress page running jQuery and Elementor with Contact Form 7 alongside Google, Google Marketing Platform and YouTube trackers, and 10 distinct script SHA256 hashes are recorded, for example cb6f2d32c49d, for campaign pivoting. Infrastructure Notable weaknesses first: HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy and COOP, COEP and CORP are all absent, Content-Security-Policy carries only upgrade-insecure-requests, SPF is present with no DKIM or DMARC, and DNSSEC is unsigned. The domain was registered through Dynadot Inc on 2007-12-14 and recorded on Hostinger International Limited infrastructure, with no WAF shown in the capture. TLS 1.3, TLS_AES_256_GCM_SHA384, forward secrecy, ALPN h2; a CAA record is present. What to do If you called the number in the banner or shared personal or health information, stop further contact, monitor for follow-up approaches, and report the captured site to your provider. Do not send payments or documents requested during such calls. Defenders should block diabetespakistan.com at the proxy, mail and endpoint layers and keep it on deny lists. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a1723a-fada-735a-ba9b-1b6d0dcaac82/ Cloudflare Radar report: https://radar.cloudflare.com/scan/77fe39cd-a229-4050-9ee4-f66cdf379926 URLQuery report: https://urlquery.net/report/ade85eea-d450-49af-8524-a142fb300229 Stored capture screenshot: https://urlscan.io/screenshots/01a1723a-fada-735a-ba9b-1b6d0dcaac82.png Cloudflare Radar screenshot (2026-10-25T08:36:22Z): https://screenshots.phishdestroy.io/cf/77fe39cd-a229-4050-9ee4-f66cdf379926.png URLQuery screenshot: https://screenshots.phishdestroy.io/uq/ade85eea-d450-49af-8524-a142fb300229.png URLScan screenshot (2026-09-05T08:45:28Z): https://screenshots.phishdestroy.io/us/01a070be-5c9b-720e-b0f8-f3c48f3e1010.png URLScan capture report: https://urlscan.io/result/01a070be-5c9b-720e-b0f8-f3c48f3e1010/ URLScan screenshot (2026-09-05T09:09:28Z): https://screenshots.phishdestroy.io/us/01a070d4-5a44-75c2-aaa7-65e451b40f57.png URLScan capture report: https://urlscan.io/result/01a070d4-5a44-75c2-aaa7-65e451b40f57/ URLScan screenshot (2026-09-06T09:30:50Z): https://screenshots.phishdestroy.io/us/01a0760e-35b6-71bd-9b18-cf5f9a5ecf73.png URLScan capture report: https://urlscan.io/result/01a0760e-35b6-71bd-9b18-cf5f9a5ecf73/ URLScan screenshot (2026-10-25T08:28:57Z): https://screenshots.phishdestroy.io/us/01a1722d-398d-711f-b558-b2f3d0d0f0e2.png URLScan capture report: https://urlscan.io/result/01a1722d-398d-711f-b558-b2f3d0d0f0e2/ VirusTotal report: https://www.virustotal.com/gui/domain/diabetespakistan.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=diabetespakistan.com Archived copy: https://web.archive.org/web/20261025082207/https://diabetespakistan.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
证据层Availability: Content servingContent: Content served at rootDNS: Resolved
最新的 HTTP 观察结果内容在线提供普通 HTTP 内容90%2026-11-22 11:33 UTC
RDAP注册
观测时间线last reachable: 2026-11-22 11:33 UTClast content: 2026-11-22 11:33 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
已注册的子域名2
保存在域名记录或证书透明度缓存中的主机名。仅凭主机名本身无法确定当前是否可用或存在恶意活动。
new.diabetespakistan.com域名记录
www.diabetespakistan.com域名记录
赌场/博彩牌照核验
未经核实的博彩牌照
This domain markets casino/gambling services. Scam casinos routinely display fake Curaçao, MGA, or Kahnawake license badges that don’t exist in the real registries. 存款前,请务必通过官方监管机构数据库核对许可证编号。 If the site shows a seal but no clickable registry link — or the linked registry page doesn’t exist — treat it as fraudulent.


 Dynadot
 147.93.22.56


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT