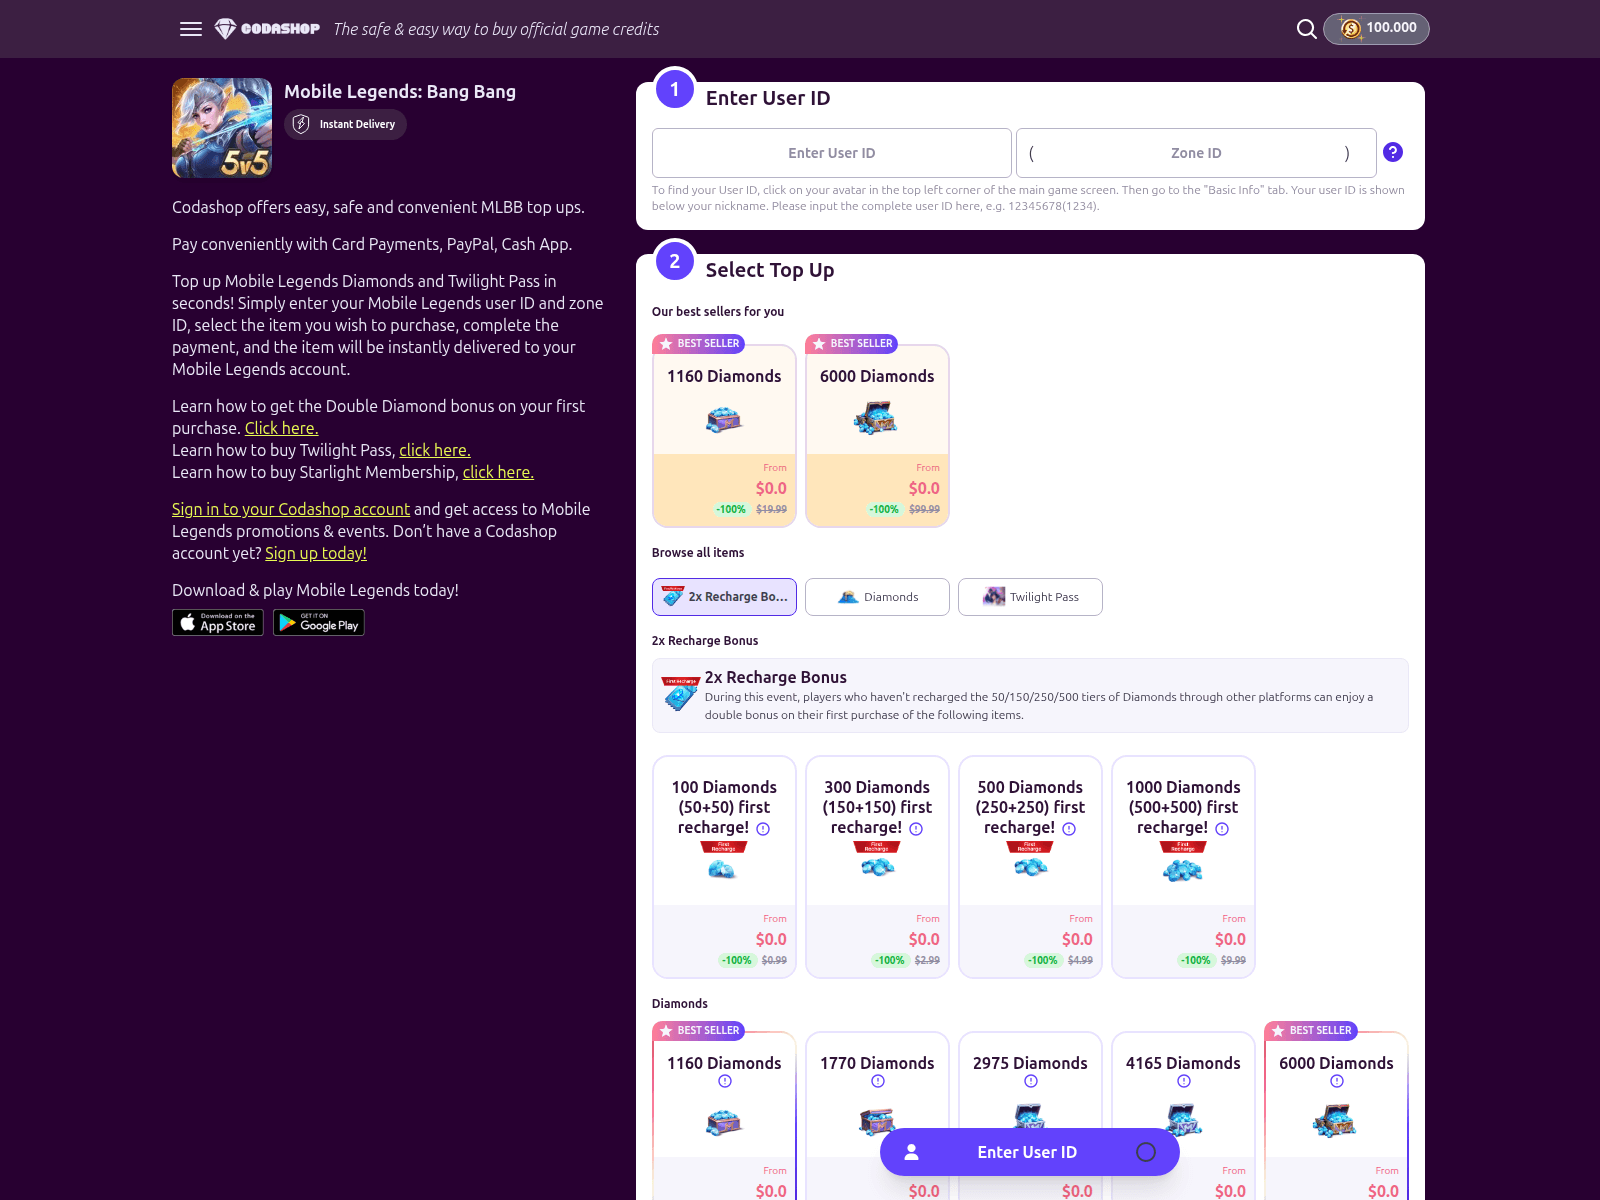
PhishDestroy listed coda-rwx.event-en.de as a suspicious domain after observing a high number of malicious detections on VirusTotal. The recorded page title claims to sell Codashop mobile‑game diamonds, which suggests an attempt to impersonate the Codashop brand. The domain was first seen by PhishDestroy on 2026-10-26 and returned HTTP 200 after a 307 redirect from http to https on that date.
诈骗手法解析
The classification relies on the presence of multiple phishing and malware detections rather than on observed malicious behavior on the page itself. Sites that mimic legitimate brands like Codashop often lure users into entering account credentials or payment information in exchange for promised in‑game items. While the exact mechanism on this page was not captured, the risk profile matches typical credential‑phishing or fraudulent offer schemes.
证据
VirusTotal reported 20 malicious and 3 suspicious detections from 92 engines on 2026-10-26, with vendors such as BitDefender, Emsisoft and Kaspersky labeling the domain as phishing or malicious. Google Safe Browsing checked the domain on 2026-10-26 and did not flag it. OpenPhish, an external blocklist, listed the domain as phishing, and Cloudflare Radar on the same day marked it malicious with a phishing category. URLScan captured the site on 2026-10-26, gave an overall clean verdict but its engine score was 98 and flagged it as malicious, while the overall verdict remained non‑malicious.
基础设施
The recorded IP address was 103.30.194.195; the response included an Apache server header and a Let’s Encrypt TLS certificate valid from 2026-10-23 to 2027-01-21. The domain’s apex is 32 days old and uses nameservers ns2.inwx.com, ns3.inwx.eu and ns.inwx.com. The page loads resources from several third‑party CDNs, including Cloudflare and Amazon CloudFront, but these do not identify the operator.
What to do
Visitors should avoid entering any Codashop credentials, payment details or personal information on this site and, if they have already done so, change associated passwords and monitor accounts for unauthorized activity. Security teams should block the domain at the network perimeter and add it to internal phishing detection lists. Review web proxy and DNS logs for any connections to coda-rwx.event-en.de to assess potential exposure.
coda-rwx.event-en.de is flagged by PhishDestroy as a suspicious domain after multiple security engines reported malicious activity.
AI摘要
Overview PhishDestroy listed coda-rwx.event-en.de as a suspicious domain after observing a high number of malicious detections on VirusTotal. The recorded page title claims to sell Codashop mobile‑game diamonds, which suggests an attempt to impersonate the Codashop brand. The domain was first seen by PhishDestroy on 2026-10-26 and returned HTTP 200 after a 307 redirect from http to https on that date. How the scam works The classification relies on the presence of multiple phishing and malware detections rather than on observed malicious behavior on the page itself. Sites that mimic legitimate brands like Codashop often lure users into entering account credentials or payment information in exchange for promised in‑game items. While the exact mechanism on this page was not captured, the risk profile matches typical credential‑phishing or fraudulent offer schemes. Evidence VirusTotal reported 20 malicious and 3 suspicious detections from 92 engines on 2026-10-26, with vendors such as BitDefender, Emsisoft and Kaspersky labeling the domain as phishing or malicious. Google Safe Browsing checked the domain on 2026-10-26 and did not flag it. OpenPhish, an external blocklist, listed the domain as phishing, and Cloudflare Radar on the same day marked it malicious with a phishing category. URLScan captured the site on 2026-10-26, gave an overall clean verdict but its engine score was 98 and flagged it as malicious, while the overall verdict remained non‑malicious. Infrastructure The recorded IP address was 103.30.194.195; the response included an Apache server header and a Let’s Encrypt TLS certificate valid from 2026-10-23 to 2027-01-21. The domain’s apex is 32 days old and uses nameservers ns2.inwx.com, ns3.inwx.eu and ns.inwx.com. The page loads resources from several third‑party CDNs, including Cloudflare and Amazon CloudFront, but these do not identify the operator. What to do Visitors should avoid entering any Codashop credentials, payment details or personal information on this site and, if they have already done so, change associated passwords and monitor accounts for unauthorized activity. Security teams should block the domain at the network perimeter and add it to internal phishing detection lists. Review web proxy and DNS logs for any connections to coda-rwx.event-en.de to assess potential exposure. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a176fd-cd41-74a9-9e9e-44827187bc87/ Cloudflare Radar report: https://radar.cloudflare.com/scan/f4e2ec8f-6e1f-4f28-a42c-a9b5e581d017 Stored capture screenshot: https://urlscan.io/screenshots/01a176fd-cd41-74a9-9e9e-44827187bc87.png Cloudflare Radar screenshot (2026-10-26T11:42:31Z): https://screenshots.phishdestroy.io/cf/f4e2ec8f-6e1f-4f28-a42c-a9b5e581d017.png URLScan screenshot (2026-10-26T01:02:52Z): https://screenshots.phishdestroy.io/us/01a175bb-1589-7298-8aca-3e7c7141b881.png URLScan capture report: https://urlscan.io/result/01a175bb-1589-7298-8aca-3e7c7141b881/ URLScan screenshot (2026-10-26T04:51:00Z): https://screenshots.phishdestroy.io/us/01a1768a-8be4-75f9-a6a7-e7935b4953c3.png URLScan capture report: https://urlscan.io/result/01a1768a-8be4-75f9-a6a7-e7935b4953c3/ VirusTotal report: https://www.virustotal.com/gui/domain/coda-rwx.event-en.de Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=coda-rwx.event-en.de Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/

 103.30.194.195


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT