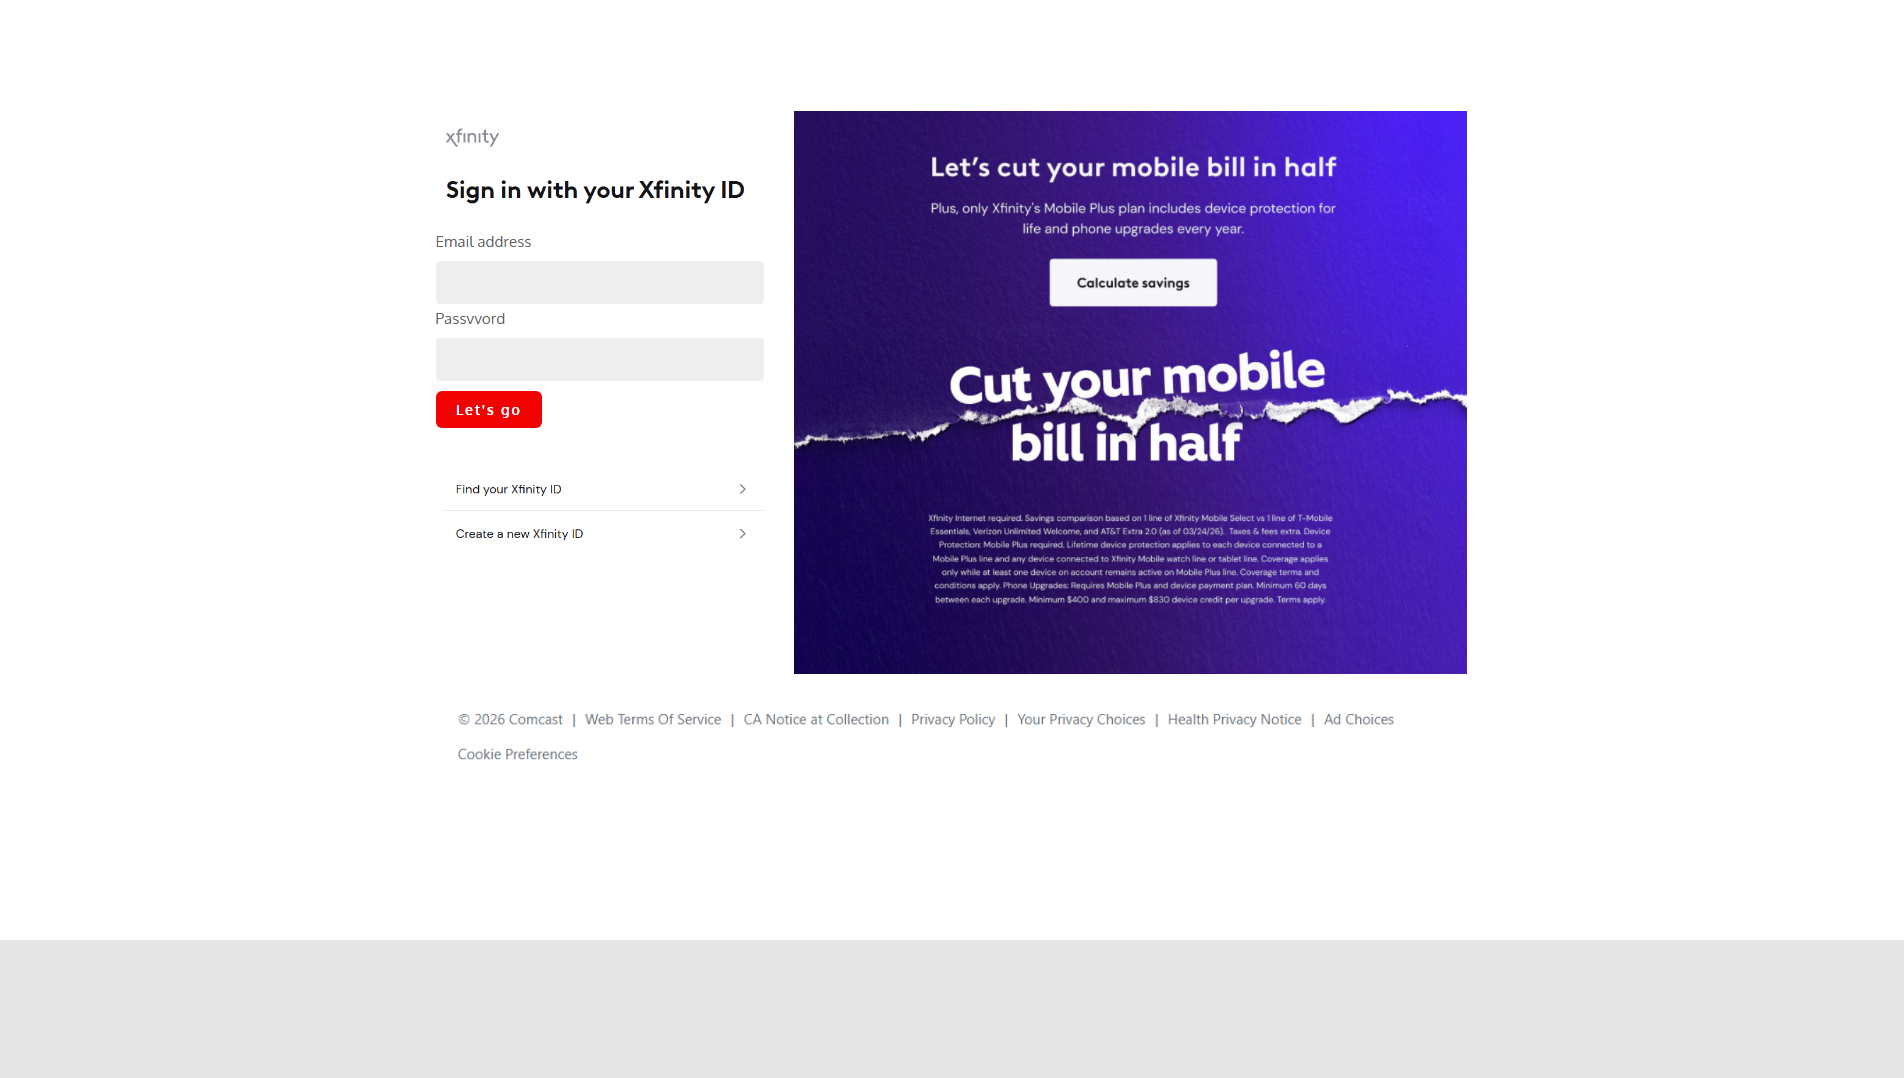
The captured screenshot dated 2026-10-26 shows a page headed Sign in with your Xfinity ID, containing an email address field, a password field and a red button labelled Let's go, with an Xfinity mobile bill savings promotion beside it and Comcast copyright text below. PhishDestroy classified it as an impersonation phishing page, first seen 2026-10-26.
诈骗手法解析
The page replicates a familiar Xfinity account sign-in while pairing it with a mobile savings offer, so a visitor who typed credentials into the captured form would transmit them to whoever controlled the page. As a category risk, such lookalike sign-in forms enable credential phishing and attempted account takeover against the impersonated service.
证据
The screenshot shows the Xfinity-branded credential form and promotional banner described above. On 2026-10-26 urlscan returned a malicious engine verdict with ML score 97 and an overall score of 100, categorising it as phishing with brand label Xfinity. VirusTotal flagged the domain as malicious, with vendors including Kaspersky labelling it phishing, and Google Safe Browsing flagged SOCIAL_ENGINEERING on 2026-10-26. The domain was listed by OpenPhish and on PhishDestroy internal blocklists on 2026-10-26, while Spamhaus DBL showed no listing and OTX recorded 0 pulses; a 307 redirect funneled HTTP to HTTPS. Site inspection found Weebly globals with jQuery, Google reCAPTCHA, Snowplow analytics and Google advertising trackers, plus 4 distinct script SHA256 hashes recorded for pivoting, beginning 5a630b41e7c3.
基础设施
No registrar is recorded for this subdomain; hosting was Weebly, Inc. behind a Cloudflare WAF. Weaknesses first: CSP, HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP all absent; DNSSEC unsigned. TLS 1.3, AES-256-GCM-SHA384, forward secrecy, ALPN h2; CAA records present.
What to do
If you entered credentials on this page, change your password on the genuine Xfinity account, enable two-factor authentication, and review recent account activity for unfamiliar changes. Security teams should block cccomcmaasttxxffintuy.weebly.com and use the recorded script hashes for campaign pivoting, while visitors should avoid the page and report it.
The captured page presents an Xfinity ID sign-in form, and PhishDestroy classifies cccomcmaasttxxffintuy.weebly.com as an impersonation phishing threat.
AI摘要
Overview The captured screenshot dated 2026-10-26 shows a page headed Sign in with your Xfinity ID, containing an email address field, a password field and a red button labelled Let's go, with an Xfinity mobile bill savings promotion beside it and Comcast copyright text below. PhishDestroy classified it as an impersonation phishing page, first seen 2026-10-26. How the scam works The page replicates a familiar Xfinity account sign-in while pairing it with a mobile savings offer, so a visitor who typed credentials into the captured form would transmit them to whoever controlled the page. As a category risk, such lookalike sign-in forms enable credential phishing and attempted account takeover against the impersonated service. Evidence The screenshot shows the Xfinity-branded credential form and promotional banner described above. On 2026-10-26 urlscan returned a malicious engine verdict with ML score 97 and an overall score of 100, categorising it as phishing with brand label Xfinity. VirusTotal flagged the domain as malicious, with vendors including Kaspersky labelling it phishing, and Google Safe Browsing flagged SOCIAL_ENGINEERING on 2026-10-26. The domain was listed by OpenPhish and on PhishDestroy internal blocklists on 2026-10-26, while Spamhaus DBL showed no listing and OTX recorded 0 pulses; a 307 redirect funneled HTTP to HTTPS. Site inspection found Weebly globals with jQuery, Google reCAPTCHA, Snowplow analytics and Google advertising trackers, plus 4 distinct script SHA256 hashes recorded for pivoting, beginning 5a630b41e7c3. Infrastructure No registrar is recorded for this subdomain; hosting was Weebly, Inc. behind a Cloudflare WAF. Weaknesses first: CSP, HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, COOP, COEP and CORP all absent; DNSSEC unsigned. TLS 1.3, AES-256-GCM-SHA384, forward secrecy, ALPN h2; CAA records present. What to do If you entered credentials on this page, change your password on the genuine Xfinity account, enable two-factor authentication, and review recent account activity for unfamiliar changes. Security teams should block cccomcmaasttxxffintuy.weebly.com and use the recorded script hashes for campaign pivoting, while visitors should avoid the page and report it. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a17902-461f-7769-bdde-5487b4e59cef/ Stored capture screenshot: https://i.ibb.co/Psm5whR4/cf1fd601c850.png URLScan screenshot (2026-10-26T13:05:26Z): https://screenshots.phishdestroy.io/us/01a17850-9907-7118-b950-b11983265beb.png URLScan capture report: https://urlscan.io/result/01a17850-9907-7118-b950-b11983265beb/ URLScan screenshot (2026-10-26T16:19:27Z): https://screenshots.phishdestroy.io/us/01a17902-114a-75e2-acce-4afd35a39e6f.png URLScan capture report: https://urlscan.io/result/01a17902-114a-75e2-acce-4afd35a39e6f/ URLScan screenshot (2026-10-26T16:48:19Z): https://screenshots.phishdestroy.io/us/01a1791c-3435-7584-a47b-ae353fb52282.png URLScan capture report: https://urlscan.io/result/01a1791c-3435-7584-a47b-ae353fb52282/ VirusTotal report: https://www.virustotal.com/gui/domain/cccomcmaasttxxffintuy.weebly.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=cccomcmaasttxxffintuy.weebly.com Archived copy: https://web.archive.org/web/20261026161732/https://cccomcmaasttxxffintuy.weebly.com/ Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
Ogurl: https://cccomcmaasttxxffintuy.weebly.com/; Title: Home; Ogimage: https://cccomcmaasttxxffintuy.weebly.com/uploads/1/5/6/5/156501999/screenshot-2025-05-22-191322_orig.png; Ogtitle: My Site
No sri: https://cdn2.editmysite.com/js/lang/en/stl.js, https://cdn11.editmysite.com/js/site/main.js, https://cdn2.editmysite.com/js/site/theme-plugins.js, https://cdn11.editmysite.com/js/site/footerSignup.js, https://cdn2.editmysite.com/js/site/main-customer-accounts-site.js, https://cdn11.editmysite.com/js/jquery-1.8.3.min.js; Third party scripts: 6
证据层Availability: Reachable but protectedDNS: Resolved
最新的 HTTP 观察结果可接触但受保护CaptchaChallenge85%2026-11-21 11:34 UTC
RDAP注册
观测时间线last reachable: 2026-11-21 11:34 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.


 74.115.51.9


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 URLquery
 Criminal IP
 CRDF
 Scamadviser
 MyWOT