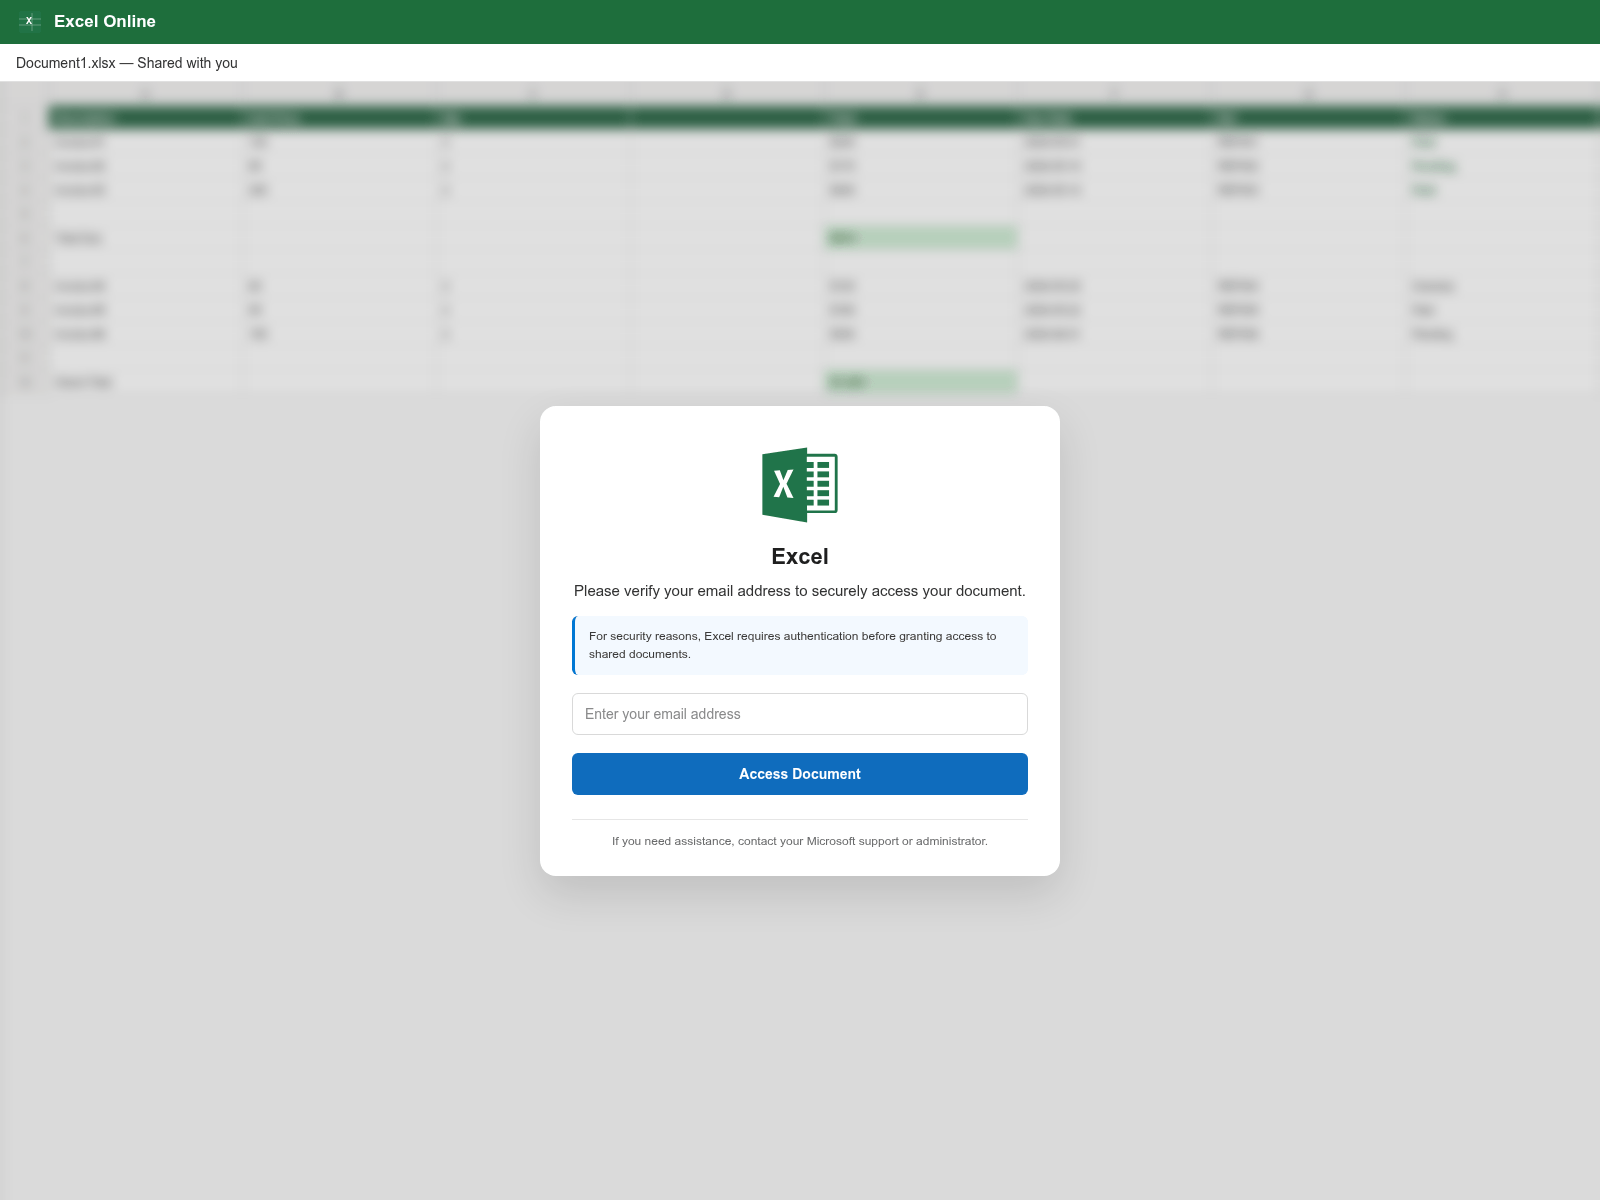
PhishDestroy’s intake AI recorded a malicious assessment for advancedpoultrv.com on 2026-10-23, citing a fresh URLScan analysis that labeled the page as phishing and noting a 95 % confidence that the site impersonates Microsoft Excel Online and asks for email verification. The recorded page title is “Excel Online” and the page excerpt reads “Please verify your email address to securely access your document,” matching the credential‑theft scenario. The domain first appeared in PhishDestroy’s feed on 2026-10-23, fourteen days after its registration on 2026-10-09.
诈骗手法解析
Attackers host a replica of a legitimate service login page—in this case a fake Microsoft Excel Online portal—and prompt visitors to enter or confirm an email address. The collected address can be used to launch further credential‑phishing attacks against the associated Microsoft account.
证据
URLScan captured the site on 2026-10-22 and returned a malicious verdict with a 100 % phishing score, tagging Microsoft as the impersonated brand. VirusTotal scanned the domain on 2026-10-23 and reported two malicious detections out of 92 engines, with CRDF marking it malicious and LevelBlue labeling it phishing. Google Safe Browsing did not flag the URL on 2026-10-23, PhishDestroy’s internal blocklist contains the domain, external blocklists showed no matches, and OTX recorded zero pulses on the same date.
基础设施
The domain was registered on 2026-10-09 through Wild West Domains, LLC. At the time of observation it resolved to IP 4.150.186.111, which belongs to the Microsoft Corporation network (ASN 8075, United States). The TLS handshake presented a Let’s Encrypt certificate for advancedpoultrv.com that was valid until 2027-01-20. The HTTP response header indicated the server software was nginx/1.24.0 on Ubuntu.
What to do
Anyone who entered credentials should change the associated Microsoft account password immediately and enable multi‑factor authentication. Defenders should block the domain, monitor DNS and web traffic for connections to the recorded IP, and add the observed indicators to intrusion‑detection rules.
PhishDestroy flagged advancedpoultrv.com on 2026-10-23 as a malicious site impersonating Microsoft Excel Online and requesting email verification.
AI摘要
Overview PhishDestroy’s intake AI recorded a malicious assessment for advancedpoultrv.com on 2026-10-23, citing a fresh URLScan analysis that labeled the page as phishing and noting a 95 % confidence that the site impersonates Microsoft Excel Online and asks for email verification. The recorded page title is “Excel Online” and the page excerpt reads “Please verify your email address to securely access your document,” matching the credential‑theft scenario. The domain first appeared in PhishDestroy’s feed on 2026-10-23, fourteen days after its registration on 2026-10-09. How the scam works Attackers host a replica of a legitimate service login page—in this case a fake Microsoft Excel Online portal—and prompt visitors to enter or confirm an email address. The collected address can be used to launch further credential‑phishing attacks against the associated Microsoft account. Evidence URLScan captured the site on 2026-10-22 and returned a malicious verdict with a 100 % phishing score, tagging Microsoft as the impersonated brand. VirusTotal scanned the domain on 2026-10-23 and reported two malicious detections out of 92 engines, with CRDF marking it malicious and LevelBlue labeling it phishing. Google Safe Browsing did not flag the URL on 2026-10-23, PhishDestroy’s internal blocklist contains the domain, external blocklists showed no matches, and OTX recorded zero pulses on the same date. Infrastructure The domain was registered on 2026-10-09 through Wild West Domains, LLC. At the time of observation it resolved to IP 4.150.186.111, which belongs to the Microsoft Corporation network (ASN 8075, United States). The TLS handshake presented a Let’s Encrypt certificate for advancedpoultrv.com that was valid until 2027-01-20. The HTTP response header indicated the server software was nginx/1.24.0 on Ubuntu. What to do Anyone who entered credentials should change the associated Microsoft account password immediately and enable multi‑factor authentication. Defenders should block the domain, monitor DNS and web traffic for connections to the recorded IP, and add the observed indicators to intrusion‑detection rules. Useful links urlscan.io scan and screenshot: https://urlscan.io/result/01a164c8-20d3-73ea-b3b3-ec6630f7ceaf/ Cloudflare Radar report: https://radar.cloudflare.com/scan/2d686c26-490c-4ecf-979f-947136668da3 Stored capture screenshot: https://urlscan.io/screenshots/01a164c8-20d3-73ea-b3b3-ec6630f7ceaf.png Cloudflare Radar screenshot (2026-10-23T12:41:50Z): https://screenshots.phishdestroy.io/cf/2d686c26-490c-4ecf-979f-947136668da3.png VirusTotal report: https://www.virustotal.com/gui/domain/advancedpoultrv.com Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=advancedpoultrv.com Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/ Site owner? Request a review: https://phishdestroy.io/appeals/
This website does not have many visitors This website has only been registered recently. IPQS flagged this website for Phishing IPQS has flagged this website as suspicious
According to the SSL check the certificate is valid DNSFilter considers this website safe
网络安全情报
Cloudflare Radar判定结果恶意
Security Risks 网络钓鱼 网络钓鱼 Security threats New Domains
证据层Availability: DNS inactiveContent: UnreachableDNS: NXDOMAIN
RDAP注册
观测时间线last reachable: 2026-11-05 00:03 UTClast content: 2026-11-05 00:03 UTCcurrent episode first observed: 2026-11-06 10:21 UTCobserved RIP window: 2026-11-05 00:03 UTC → 2026-11-06 10:21 UTC · 34.30hmidpoint estimate ≈ 2026-11-05 17:12 UTC · precision medium · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

 4.150.186.111


 Microsoft
 Cloudflare
 Yandex
 ESET
 Bitdefender
 Norton
 Symantec
 Avira
 Avast / AVG
 卡巴斯基
 Dr.Web
 Netcraft
 PhishTank
 APWG eCX
 PhishStats
 Phish.Report
 Spamhaus
 PolySwarm
 CheckPhish
 Quttera
 Criminal IP
 CRDF
 MyWOT