Chuyển đến báo cáo bảo mật
Bảo mật miền và thông tin về mối đe dọa
nestsss.com favicon

nestsss.com

“Problem loading page”

Nhà đăng ký
Amazon
Resolved IP
188.114.97.3
Registered
17/12/2025
Phán quyết đe dọa Quan trọng
sẵn có Hoạt động được biết đến lần cuối Quan sát khả năng tiếp cận được lưu trữ mới nhất
Tổng số phát hiện Virus: 5/92 Mạo danh thương hiệu: Binance
OTX: 4 refs 29/09/2026 Binance 1 Report Sent CDN
API
Tên miền này đã bị đánh dấu là có hại
Công cụ bảo mật báo cáo phát hiện: 5. Hãy hết sức thận trọng — không nhập thông tin xác thực hoặc thông tin cá nhân.
ABUSE NOTICE · 7D+ OPEN Outgoing abuse reports are recorded; the latest stored availability evidence still shows the domain reachable.
Notification and current-status evidence

The sent-report ledger records the first outgoing report at . The recorded recipient is trustandsafety@support.aws.com. The latest stored availability evidence still shows the domain reachable; 12 days has elapsed since the first outgoing report.

ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.

Elapsed since first report
12 days
Reports sent
1
Latest case ID
PD-20260929-453CE4
Current status
HTTP 200 at latest stored check
Tóm tắt báo cáo

nestsss.com — Hoạt động được biết đến lần cuối (HTTP 200). Mạo danh thương hiệu: Binance; Loại lừa đảo: Impersonation. Tóm tắt bằng chứng: VirusTotal 5/92 (CRDF, Forcepoint ThreatSeeker, Gridinsoft, SOCRadar, VIPRE); PhishDestroy score 88/100. Nhà đăng ký: Amazon.

Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.

VirusTotal
VirusTotal
5 det.
OTX references
URLScan
URLScan
Chứng chỉ TLS
Hết hạn hoặc chưa được xác minh
Tuổi
10 mo
Trạng thái ghi nhận
Hoạt động được biết đến lần cuối 200
PhishDestroy
Danh sách hủy bỏ
Có trong danh sách
Reports Sent
1

Source evidence

7 sources

VirusTotal

5 / 92

Báo cáo

URLQuery

Report stored; detailed verdict not recorded

Báo cáo

OTX

4 community references

Báo cáo

URLScan capture

báo cáo được lưu trữ

Stored URLScan capture preview
Báo cáo

URLScan verdict

Phân tích hoàn tất

Báo cáo

Google Safe Browsing

Checked; no threat flag recorded

Báo cáo

Tóm tắt bằng chứng

Quan trọng
VirusTotal
5/92
OTX
4 community refs
URLScan
Stored capture

Assessment

nestsss.com returned HTTP status 200 on 2026-10-01, according to the recorded HTTP check. The same evidence set places first observation of the domain on 2026-09-29, two days earlier.

Recorded Evidence

The HTTP check on 2026-10-01 recorded status 200 for nestsss.com. A PageSpeed check on 2026-09-29 recorded a performance score of 56. VirusTotal recorded 2 detections across 91 scanners on 2026-09-29. OTX recorded 4 pulses on 2026-10-01. The publisher-owned PhishDestroy catalogue listed the domain, and the registration date was 2025-12-17.

Interpretation

The HTTP and OTX observations share the 2026-10-01 date, while the PageSpeed and VirusTotal observations come from 2026-09-29, so those two pairs describe different moments. Because the PhishDestroy listing carries no separate observation date in this set, it cannot be aligned to either pair. The differing dates mean a reader should compare each record within its own snapshot rather than treating them as one simultaneous measurement.

Recommended Actions

Reviewers should retain the dated records for nestsss.com, including the HTTP, PageSpeed, VirusTotal and OTX observations, so later checks can be compared against them. Any subsequent check of nestsss.com should be logged with its own date and source label before conclusions are drawn. During review, avoid submitting sensitive information to the site until the recorded observations have been independently verified.

Phân tích phát hiện và né tránh

Nghi ngờ có hành vi che giấu: tiêu đề của trình quét và người truy cập khác nhau

Chưa được quét Hiện tại vẫn chưa ghi nhận sự khác biệt nào giữa trình thu thập dữ liệu và trình duyệt

Các dữ liệu quan sát đã lưu trữ về sự so sánh giữa trình thu thập dữ liệu và trình duyệt đối với máy chủ này, cùng với việc kiểm tra dấu vân tay thời gian thực dành cho các hệ thống phân phối lưu lượng theo phong cách Keitaro.

Cờ ẩn được lưu trữ
Chưa được quét
Lần quét che giấu gần nhất
Tiêu đề máy chủ được trình quét phát hiện
cloudflare

Ghi chú về máy quét: alive_content: raw=ok; http=200; via=https_proxy; server=cloudflare

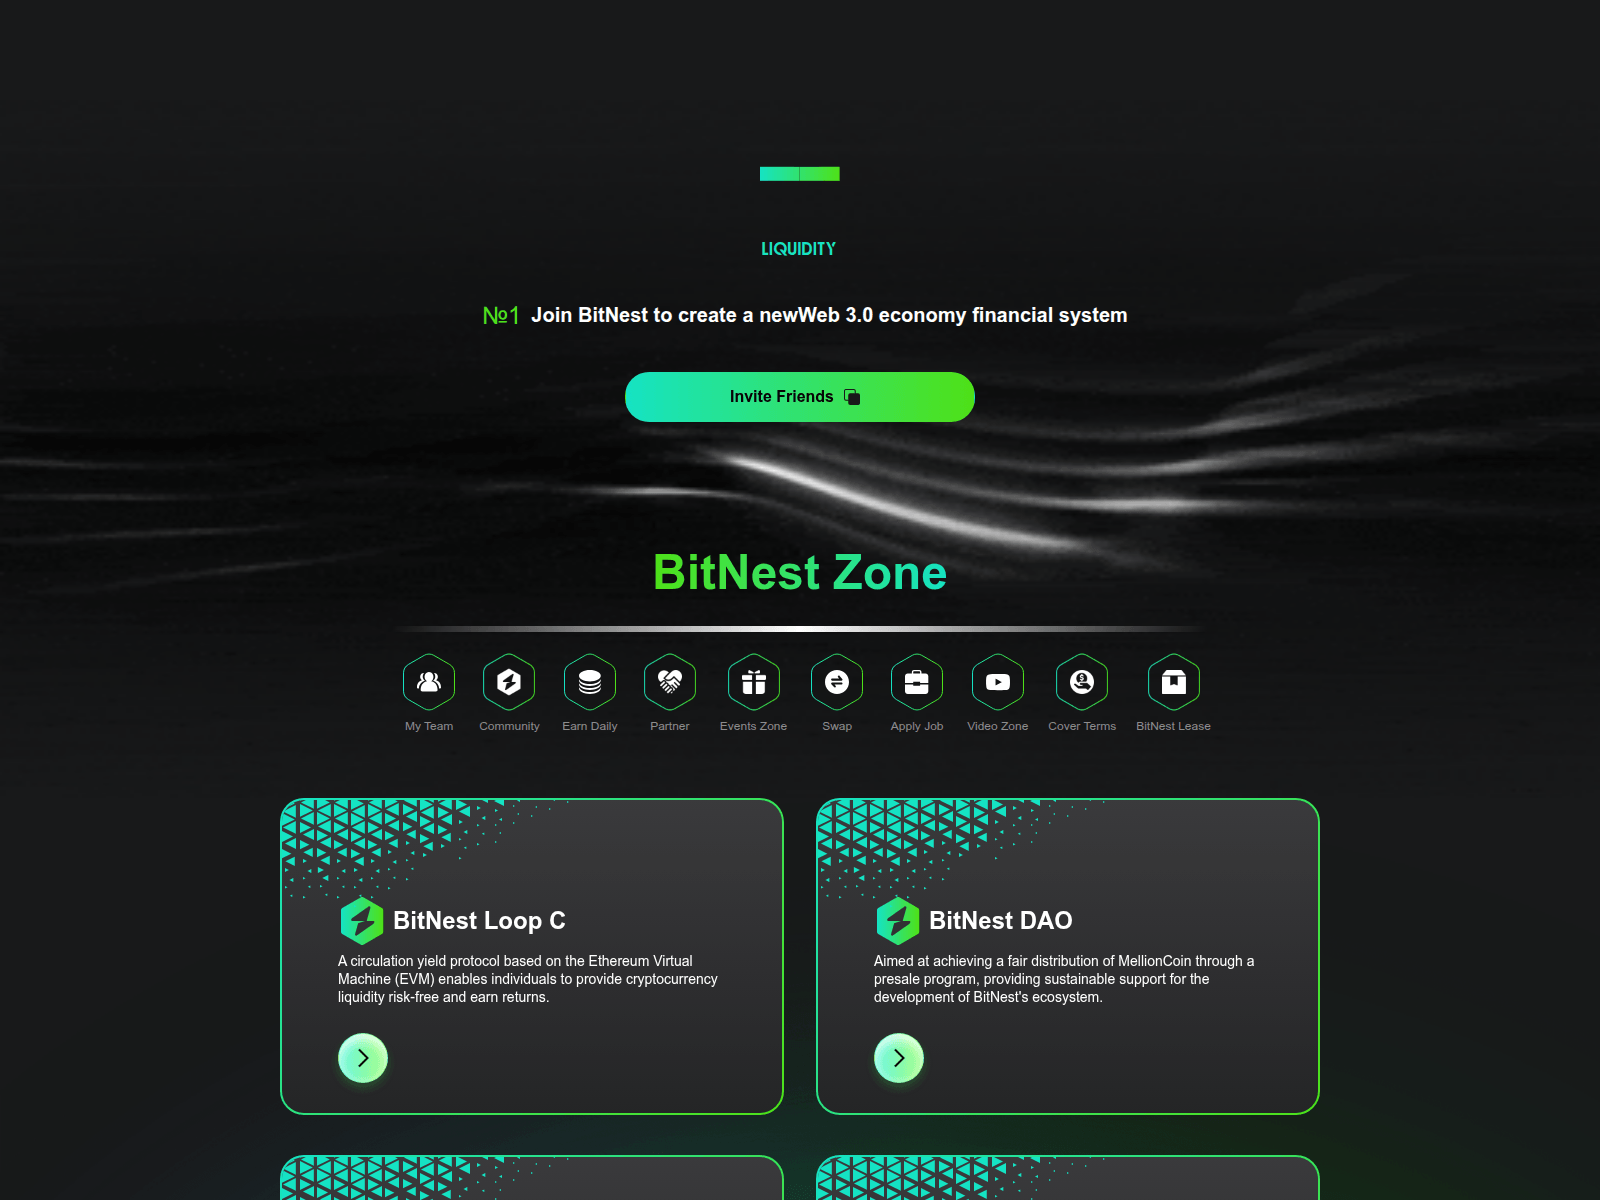
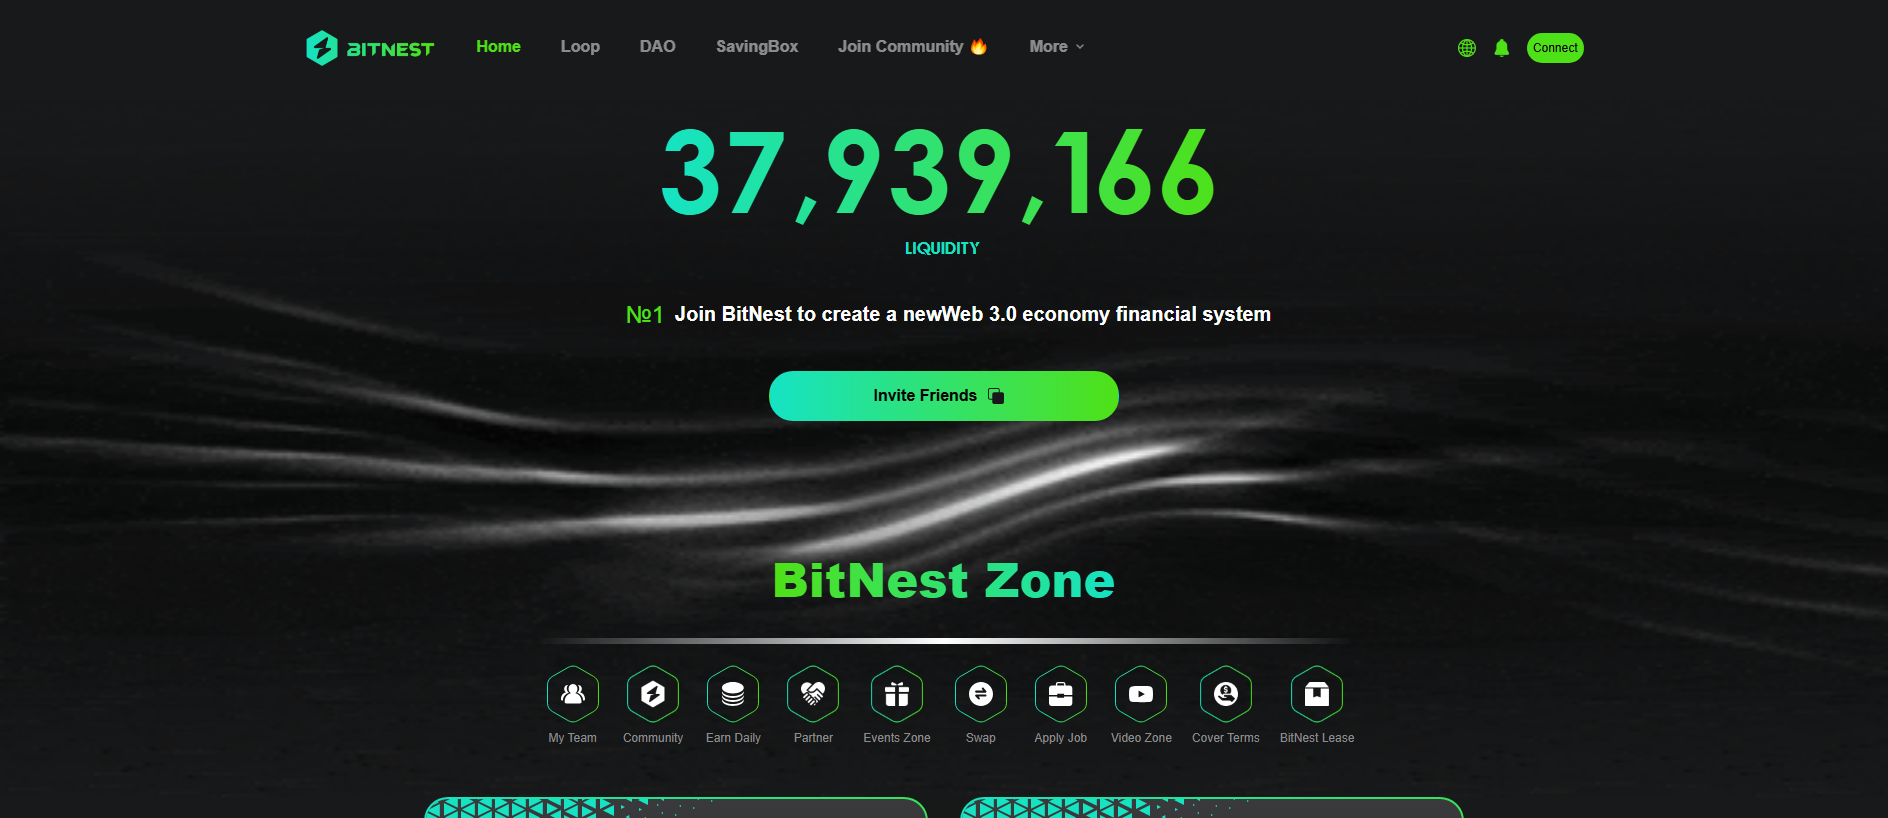
Tiêu đề hiển thị trên máy quét an ninhBITNEST
Tiêu đề hiển thị cho người truy cập trình duyệtProblem loading page
Kiểm tra dấu vân tay trực tiếp trên TDS
Bảy dấu vân tay Keitaro cùng với so sánh giữa trình thu thập dữ liệu và trình duyệt, được thực hiện từ trình quét PhishDestroy khi bảng điều khiển này đang mở.
Chờ đợi

Bản chụp đã lưu · 2 captures

Domain details

Tên miền
URLScan Verdict Phân tích hoàn tất score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Danh tiếng của Edge-IP không được quy cho tên miền này.
OTX Tags 2026-09activeall-domainsblocklistcontentcryptotên miềndrainerfraudlivemonthlyphishdestroyphishingscam
Nhà đăng ký Amazon US(US)
Liên hệ báo cáo lạm dụngtrustandsafety@support.aws.com
Cơ quan đăng ký ICANNICANN Lookup (RDAP) →
Đăng kýĐược tạo 17/12/2025 (297d) — Expires 17/12/2026
Trạng thái HTTP200
Chi tiết kỹ thuậtProvenance & timestamps
Lần đầu tiên được phát hiện29/09/2026
DOM Analysisanalyzed 09/10/2026score 88/1007 brand signals
Submitted URLhttps://nestsss.com/
Favicon Hash
Mã vụ việc
Tiêu đề trang
Problem loading page
Impersonates
Binance Chainlink Coinbase Ethereum MetaMask PancakeSwap Telegram
Chứng chỉ TLS
Hostname coverage not recorded · Được cấp bởi Google Trust Services / WE1 · stored validity ends in 87 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.97.3
Network ASN
AS13335
Organization
CloudFlare, Inc.
Observed location
Toronto, CA
Server header
cloudflare

Danh tiếng của Edge-IP không được quy cho tên miền này.

Máy chủ tên 2

  • coby.ns.cloudflare.com
  • kate.ns.cloudflare.com

Location describes the IP network.

Chứng chỉ TLS

Issuer
Google Trust Services / WE1
Valid from
2026-10-08 15:44:14
Valid until
2027-01-06 16:42:57
Hostname coverage
Hostname coverage not recorded
Validity
Within stored validity dates
Collection time
2026-10-11 07:02:13 UTC
Collection source
PhishDestroy collector
Certificate fingerprint5da95aef498c4cb67907bd7ff067731287c96ad04ef2e2eac1898e248cd2fce3

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 188.114.97.3rapiddns.io

Latest Classified Outcome 2026-10-11 01:41:57 UTC

Primary outcome Nội dung đang hoạt động reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Nội dung đang hoạt động Ordinary HTTP content served 90% 2026-10-11 01:41:57 UTC
RDAP registration Không rõ
Observed timeline last reachable: 2026-10-11 01:41:57 UTC last content: 2026-10-11 01:41:57 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Công nghệ · 8 identified
Detected via Cloudflare Radar · Wappalyzer engine
Báo cáo tên miền này Gửi bằng chứng và góp phần bảo vệ người khác

Phân tích của VirusTotal

5 / Nhà cung cấp bảo mật 92 đã gắn cờ miền này
View on VT
Last analyzed First positive detection Previous stored snapshot: 5 detections
CRDF
Forcepoint ThreatSeeker
Gridinsoft
SOCRadar
VIPRE

Bằng chứng lưu trữ

Wayback Machine Snapshot
Một ảnh chụp nhanh lịch sử có sẵn để xem xét bằng chứng
View Archive
Phân tích hiệu suất trang

Google PageSpeed Insights — mobile performance audit of nestsss.com · checked Sep 29, 2026

56
Needs Work
Performance
FCP
8.85s
First Contentful Paint
LCP
13.18s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
73ms
Total Blocking Time
SI
8.85s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. VirusTotal Detections Update 2026-09-30 02:36:20 UTC
    VirusTotal scanner detections updated from 1 to 2. Added scanner alerts: CRDF.
  2. VirusTotal Detections Update 2026-09-29 12:57:13 UTC
    VirusTotal scanner detections updated from 0 to 1. Added scanner alerts: SOCRadar.
  3. Threat First Observed 2026-09-29 09:42:08 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 188.114.97.3.

Pipeline ứng phó với các mối đe dọa

Khám phá
Analysis
Notifications
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Đã phát hiện mối đe dọa
nestsss.com đã được phát hiện và đưa vào danh sách chờ để phân tích toàn diện
29/09/2026
URLScan.io Capture
Đã lưu URLScan report with capture artifacts
29/09/2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
Web Archive
Preserved in Wayback Machine — historical evidence archived
01/10/2026
VirusTotal
5/92 recorded on VirusTotal
10/10/2026
OTX Community References
4 community publication references on AlienVault OTX. References are not vendor verdicts and are excluded from the evidence score.
01/10/2026
Brand Impersonation
Impersonation of Binance
Forensic Evidence Collected
Stored evidence from URLScan.io, URLQuery, stored screenshot
29/09/2026
Technical Analysis Recorded
Báo cáo chứa công nghệ được lưu trữ hoặc kết quả phân tích pháp y.
11/10/2026
VT Detection +1
+1 new detection (1 → 2): CRDF
30/09/2026
VT Detection +1
+1 new detection (0 → 1): SOCRadar
29/09/2026
Sent Report Recorded
Stored outgoing record associated with registrar Amazon Registrar, Inc., 1 abuse contact
trustandsafety@support.aws.com
29/09/2026
Danh sách tiêu hủy đã được công bố
29/09/2026
Monitoring Continues
Miền vẫn có thể truy cập được hoặc bị hạn chế quyền truy cập; kiểm tra trong tương lai có thể cập nhật quan sát này.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Tên miền tương tự

187 tên miền tương tự đã lưu

Hiển thị tất cả (88)
binabce.com replacement binacne.com transposition binan.ce.com subdomain binancecom.com various binanci.com vowel-swap binanco.com vowel-swap binancr.com replacement binancs.com replacement binancw.com replacement binande.com replacement binanfe.com replacement binanve.com replacement binanxe.com replacement binnace.com transposition binonce.com vowel-swap binsnce.com replacement binunce.com vowel-swap binynce.com replacement binznce.com replacement bniance.com transposition bunance.com replacement ibnance.com transposition ninance.com replacement b-inance.com hyphenation b8inance.com insertion b8nance.com replacement b9nance.com replacement bbinance.com repetition bhinance.com insertion bi-nance.com hyphenation biance.com omission bibance.com replacement bibnance.com insertion bihance.com replacement bihnance.com insertion biinance.com repetition bijnance.com insertion biknance.com insertion bimance.com homoglyph bimnance.com insertion bin-ance.com hyphenation binaance.com repetition binabnce.com insertion binace.com omission binahce.com replacement binamnce.com insertion binan-ce.com hyphenation binanbce.com insertion binanc-e.com hyphenation binanc.com omission binanc3.com replacement binancce.com repetition binancve.com insertion binancxe.com insertion binancz.com replacement binandce.com insertion binane.com omission binanec.com homoglyph binanhce.com insertion binanmce.com insertion binannce.com homoglyph binanvce.com insertion binanxce.com insertion binarnce.com homoglyph binasnce.com insertion binawnce.com insertion binbance.com insertion binhance.com insertion binmance.com insertion binnance.com homoglyph binnce.com omission binqance.com insertion binsance.com insertion binwnce.com replacement binyance.com insertion bionance.com insertion birnance.com homoglyph biunance.com insertion bjnance.com replacement bnance.com omission bninance.com insertion boinance.com insertion bonance.com replacement buinance.com insertion bvinance.com insertion clinance.com homoglyph dinarce.com homoglyph ginance.com replacement

Hiển thị 100 trong tổng số 187

Bằng chứng và các báo cáo bên ngoài

Ảnh chụp bằng chứng đã gửi
Sent: Ledger records: 1 Case ID: PD-20260929-453CE4 Recipient: trustandsafety@support.aws.com
Page title stored with report: Problem loading page
URLScan evidence VirusTotal evidence URLQuery evidence Screenshot 477.9 KB
PDF notice generated Notice text archived (653 chars)
Abuse notice text as sent to the provider
Policy Violations:
Illegal Activities: Active phishing operation targeting victims
Fraud & Deception: Impersonation of legitimate services
Identity Theft: Collection of credentials under false pretenses
Applicable Laws (US):
18 U.S.C. § 1343 - Wire Fraud
18 U.S.C. § 1030 - Computer Fraud and Abuse Act (CFAA)
15 U.S.C. § 45 - FTC Act (Deceptive Practices)
Federal laws prohibit wire fraud, computer fraud, and deceptive business practices.
Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Phân tích sâu

Bạn có bị ảnh hưởng bởi trang web này không?

6 evidence signal groups linked 1 reports recorded Hoạt động được biết đến lần cuối
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.

Europol
Tìm kênh báo cáo chính thức cho quốc gia EU của bạn
National police directory
Hãy cảnh giác với những kẻ lừa đảo lợi dụng việc phục hồi dữ liệu! Tội phạm có thể liên hệ lại với nạn nhân trong khi giả làm điều tra viên, luật sư hoặc nhân viên phục hồi. Không trả phí trả trước hoặc chia sẻ thông tin đăng nhập. Tìm hiểu thêm về gian lận trong quá trình phục hồi →

Hãy báo cáo với chính quyền địa phương

Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.

Danh mục 97 quốc gia

Template-based draft · optional AI wording assistance requires separate consent

Bản nháp có sự hỗ trợ của AI - chi tiết sự cố được nhà cung cấp AI xử lý · Hãy tự mình xem xét và gửi nó

Kiểm tra bất kỳ tên miền nào

Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai

Quét ngay

Báo cáo lừa đảo qua email

Hãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng

Báo cáo

Dòng tin tức về các mối đe dọa thời gian thực

Các báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy

Theo dõi

Luôn cập nhật thông tin, luôn an toàn

Theo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai

Dòng tin tức về các mối đe dọa thời gian thực Khiếu nại về thông tin đăng tải này
HTML · IFRAME

Nhúng báo cáo này

Hãy chia sẻ thông tin tình báo về mối đe dọa này trên trang web hoặc blog của bạn

embed.html
<iframe
  src="https://phishdestroy.io/vi/embed/domain/nestsss.com"
  title="PhishDestroy threat report for nestsss.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>