VirusTotal
5 / 92
Báo cáo


“Access Forbidden”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@loopia.se.
The latest stored availability evidence still shows the domain reachable; 2 days has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
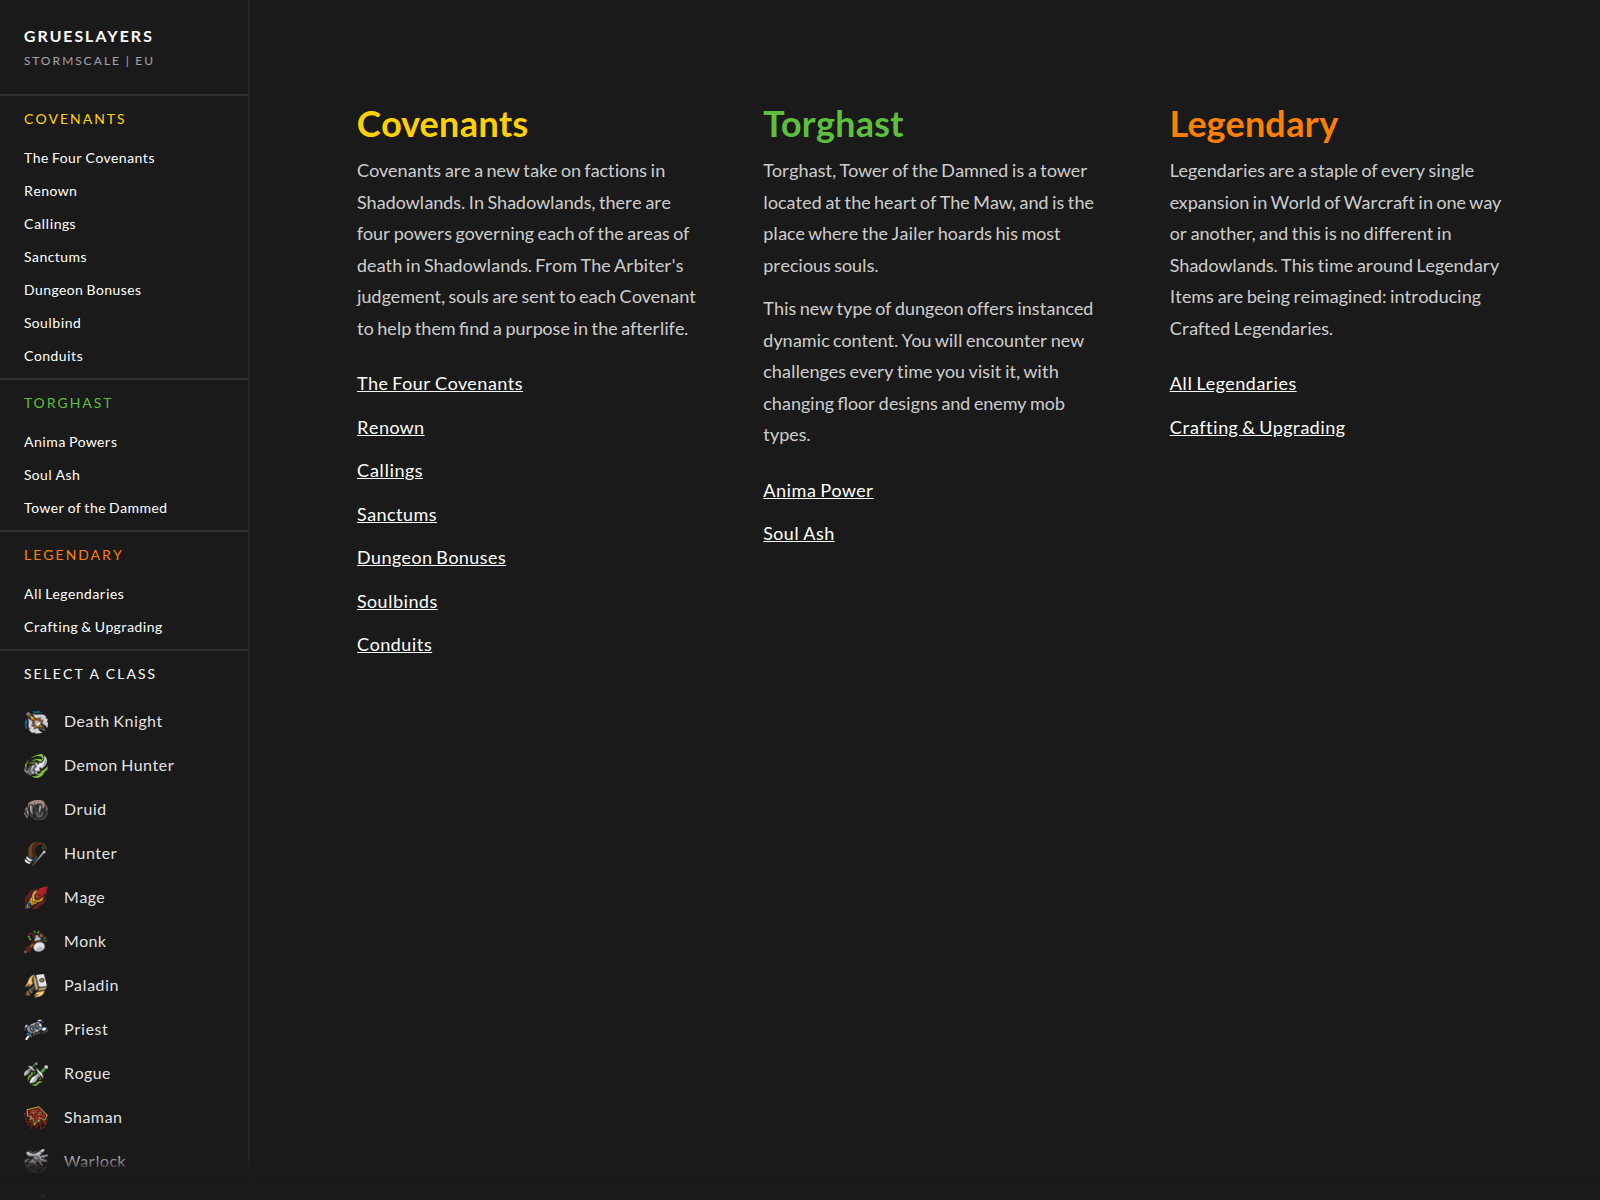
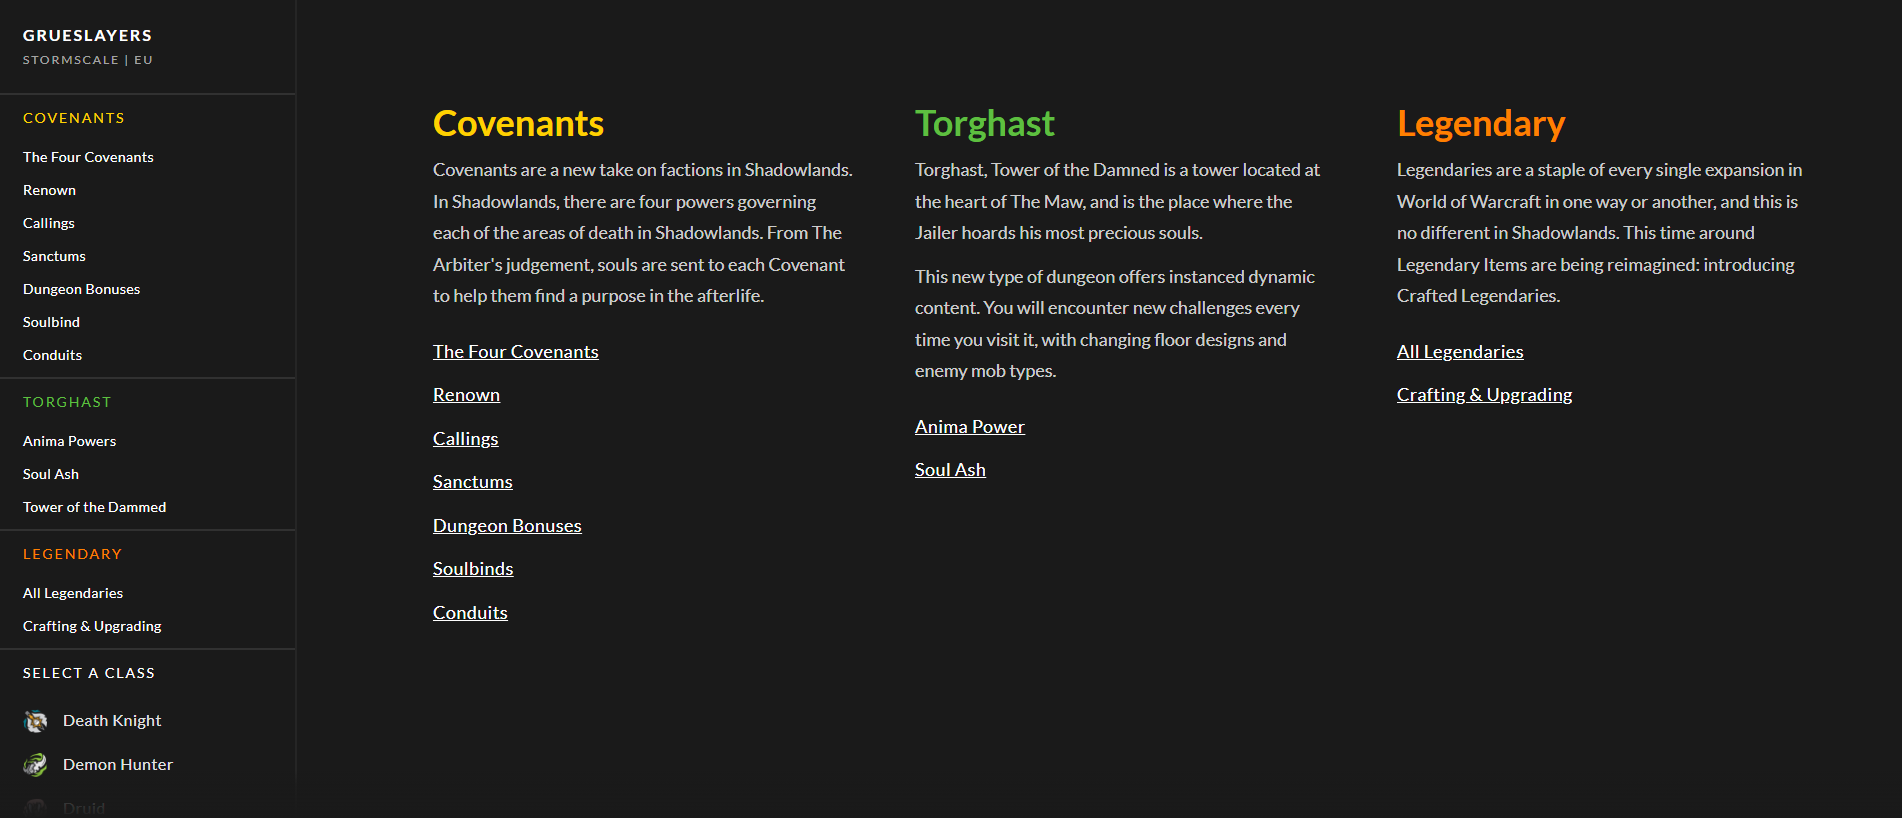
grueslayers.eu — Hoạt động được biết đến lần cuối (HTTP 200). Mạo danh thương hiệu: World of warcraft; Loại lừa đảo: Impersonation. Tóm tắt bằng chứng: VirusTotal 5/92 (alphaMountain.ai, Fortinet, Gridinsoft, Seclookup, SOCRadar); URLQuery 2 det.; PhishDestroy score 80/100. Nhà đăng ký: Loopia Group AB.
Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.

The domain grueslayers.eu returned an HTTP status 200 on 2026-10-11, documenting a successful response at that time. On the same date, the domain was listed in the PhishDestroy internal catalogue, providing an additional recorded observation.
On 2026-10-11, the HTTP status for grueslayers.eu was recorded as 200. The domain was also included in the PhishDestroy internal listing on 2026-10-11. Registration records show the registrar as Loopia Group AB, and the SSL certificate was issued by Let's Encrypt / R3, with the certificate scan also occurring on 2026-10-11.
The PhishDestroy record contains a catalogue listing for grueslayers.eu, which documents its presence in an internal publisher-owned source. The HTTP status source provides a measurement of the domain's ability to return a standard success code on a specific date. These sources together offer a technical snapshot of the domain's response and catalogue presence as of their respective recording times.
For any review of grueslayers.eu, retain the HTTP status and PhishDestroy listing records as key evidence for future comparison. Use the registration and SSL certificate details as reference points to track changes in the domain's technical profile over time.
Các dữ liệu quan sát đã lưu trữ về sự so sánh giữa trình thu thập dữ liệu và trình duyệt đối với máy chủ này, cùng với việc kiểm tra dấu vân tay thời gian thực dành cho các hệ thống phân phối lưu lượng theo phong cách Keitaro.
openrestyGhi chú về máy quét: captcha: raw=captcha; http=200; via=https_proxy; server=openresty
ns1.loopiagroup.comvisitwww.eurid.euformoreinfons2.loopiagroup.commx10.websupport.sepriority 10mx20.websupport.sepriority 100Location describes the IP network.
fd13e0cf92511a39f5edb20920418b28155991d9a12284b2f028f564722c5577www.grueslayers.euSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of grueslayers.eu · checked Oct 12, 2026
109.235.174.3. 10 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261010-FDAB17 Recipient: abuse@loopia.se AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.


Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.
Template-based draft · optional AI wording assistance requires separate consent
Mỗi làn là một lý do khiến một tên miền được liên kết với máy chủ này. Kích thước nút biểu thị các phát hiện từ VirusTotal, còn các nút có đường gạch ngang đã ngừng hoạt động. Danh sách đầy đủ được trình bày dưới đây.
Có cùng mã băm favicon hoặc cùng tiêu đề trang với máy chủ này.
Các báo cáo được thêm gần đây từ cơ sở dữ liệu PhishDestroy. Các liên kết khám phá này không ngụ ý cơ sở hạ tầng hoặc quyền sở hữu chung.
Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai
Quét ngayHãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng
Báo cáoCác báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy
Theo dõiTheo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai