Chuyển đến báo cáo bảo mật

bhd8fa6-4acb-be64-76e26a.xo.je

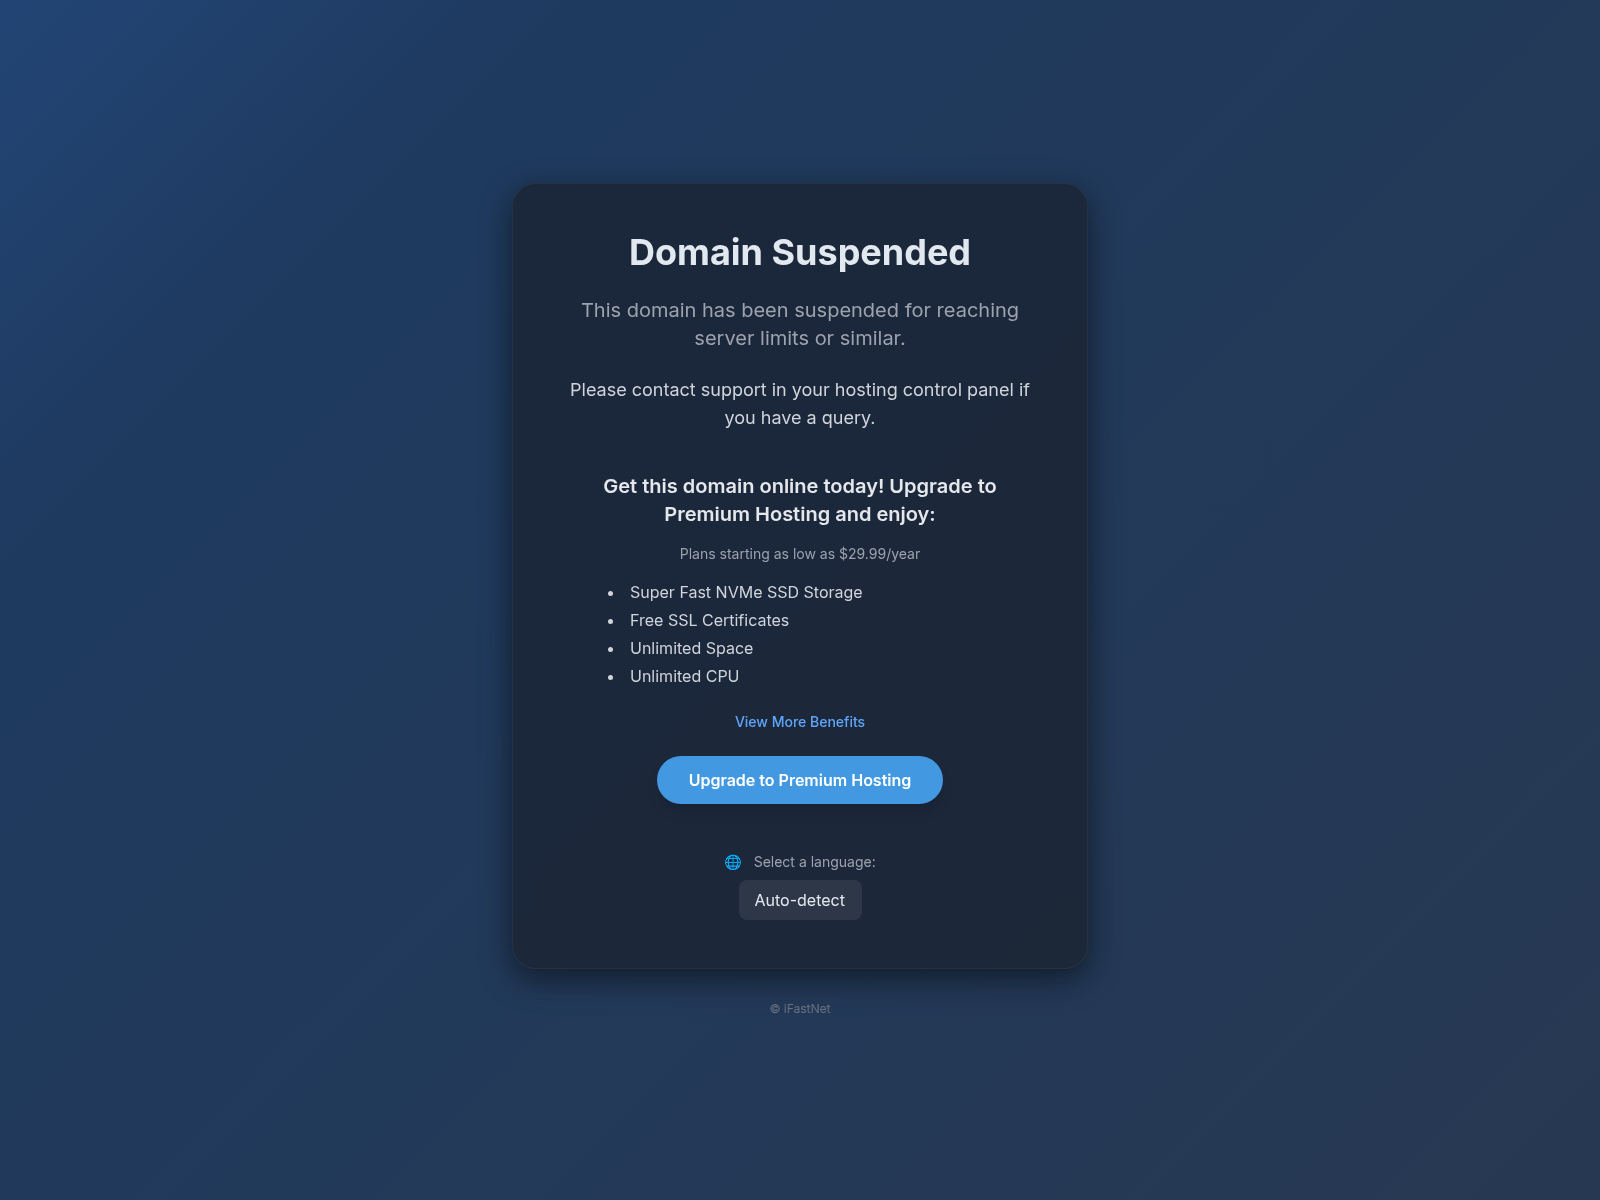
Loại lừa đảo: Account Takeover Page title: “Domain Suspended”

Availability last checked First listed 06/12/2025 VirusTotal analysed Sep 19, 2026 UTC

PhishDestroy verdict Quan trọng 91/100 evidence score

Based on 3 recorded source signals. The score is a heuristic over stored detections, not a probability or confidence level.

View evidence
Availability · last observation Chưa được xác minh

Khả năng tiếp cận hiện tại chưa được xác minh

· Source: HTTP probe

Reachability is not a safety rating.

Key evidence

  • Tổng số phát hiện Virus: 12/89
  • Spamhaus DBL: DBL_PHISH
  • Loại lừa đảo: Account Takeover
IP
77.72.1.44
Stored capture 1 of 2 · Feb 27, 2026 UTC · Primary capture OpenAll capturesWayback

Evidence

Source checks and detection results recorded for this domain, with the time each was observed.

Tóm tắt báo cáo

bhd8fa6-4acb-be64-76e26a.xo.je — Chưa được xác minh. Loại lừa đảo: Account Takeover. Tóm tắt bằng chứng: VirusTotal 12/89 (BitDefender, Chong Lua Dao, CyRadar, ESET, Forcepoint ThreatSeeker); Spamhaus DBL_PHISH; CF Radar malicious; PhishDestroy score 91/100.

Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.

Source evidence

8 sources

VirusTotal

12 / 89

Báo cáo

CF Radar

provider verdict: malicious

Báo cáo

Spamhaus DBL

DBL_PHISH

PhishStats

checked — no match recorded

OTX

no community references

Báo cáo

URLScan capture

báo cáo được lưu trữ

Stored URLScan capture preview
Báo cáo

Google Safe Browsing

Checked; no threat flag recorded

Báo cáo
Detailed resultsVirusTotal vendor list · written summary · threat-intel cross-reference · cloaking analysis
Tín hiệu bảo mật
SA Scamadviser Warnings 1/100
The Tranco rank (how much traffic) is rather low An iframe has been detected within the website The server of the site has several low reviewed other websites This website seems for sale at this time (how to get your money back) The website was reported in the last 30 days as threat by DNSFilter This website was reported by IPQS for phishing. This website has been classified as suspicious by IPQS
We found a valid SSL certificate
Tình báo an ninh mạng
CF Cloudflare Radar Verdict Độc hại
Phishing Security threats Phishing

Evidence summary

Stored written summary, generated Jul 23, 2026. It is not updated when source results change.

This summary quotes VirusTotal 20/95. The current stored result is 12/89 (analysed Sep 19, 2026).

The domain bhd8fa6-4acb-be64-76e26a.xo.je was observed returning the page title "Domain Suspended" and is currently taken offline. DNS resolution points to the IPv4 address 77.72.1.44, which is announced by AS12488 (Krystal Hosting Ltd) located in Great Britain. The domain lacks publicly resolvable nameservers, and no TLS certificate was presented when the host was queried, indicating an absence of encrypted traffic. Reputation services record a Scamadviser trust score of 1 out of 100, reflecting extreme suspicion.

Read full summary

The domain appears on a single security blocklist and has been explicitly flagged by the PhishDestroy feed. VirusTotal analysis shows that 20 out of 95 scanned security vendors flagged the domain as malicious, reinforcing the notion of malicious intent despite the offline state. The intelligence categorizes the activity as an "Account Takeover" scam, though the targeted brand or service is not disclosed in the available data.

The combination of a low trust score, lack of SSL, presence on a blocklist, and multiple vendor detections suggests the domain was deployed to harvest credentials or session tokens before being shut down.

Uncertainty remains regarding the exact victim profile and the infrastructure used to deliver the malicious payload, as the site content was not captured before suspension. Defenders should continue to deny any outbound connections to 77.72.1.44, add the domain to perimeter deny lists, and monitor DNS logs for any resurgence of the hostname or related sub‑domains. Additional investigation of Krystal Hosting Ltd’s IP range may reveal other malicious actors sharing the same hosting environment.

Phân tích của VirusTotal

12 / Nhà cung cấp bảo mật 89 đã gắn cờ miền này
View on VT
Last analyzed Previous stored snapshot: 14 detections
BitDefender
Chong Lua Dao
CyRadar
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Lionic
SOCRadar
Sophos
VIPRE
Phân tích phát hiện và né tránh

Kiểm tra tính năng ẩn trang và phân phối lưu lượng truy cập

Chưa được quét Hiện tại vẫn chưa ghi nhận sự khác biệt nào giữa trình thu thập dữ liệu và trình duyệt

Các dữ liệu quan sát đã lưu trữ về sự so sánh giữa trình thu thập dữ liệu và trình duyệt đối với máy chủ này, cùng với việc kiểm tra dấu vân tay thời gian thực dành cho các hệ thống phân phối lưu lượng theo phong cách Keitaro.

Cờ ẩn được lưu trữ
Chưa được quét
Lần quét che giấu gần nhất

Ghi chú về máy quét: timeout: raw=timeout; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='bhd8fa6-4acb-be64-76e26a.xo.je', port=80): Max retries exceeded with url: / (Caused by Con

Kiểm tra dấu vân tay trực tiếp trên TDS
Bảy dấu vân tay Keitaro cùng với so sánh giữa trình thu thập dữ liệu và trình duyệt, được thực hiện từ trình quét PhishDestroy khi bảng điều khiển này đang mở.
Chờ đợi

Domain & infrastructure

IP 77.72.1.44

Domain details

Tên miền
Uy tín IP abuse score 0/100 0 reports checked 25/09/2026
Registrar (base domain) Không rõ
Liên hệ báo cáo lạm dụngabuse@ifastnet.com
Chi tiết kỹ thuậtProvenance & timestamps
Lần đầu tiên được phát hiện06/12/2025
DOM Analysisanalyzed 27/07/2026score 88/100
Submitted URLhttp://bhd8fa6-4acb-be64-76e26a.xo.je/

Network & certificates

Stored technical evidence

Network & DNS

Resolved IP
77.72.1.44
Network ASN
AS12488
Organization
Krystal Hosting Ltd
Observed location
London, GB
Server header
openresty

Location describes the IP network.

Ảnh chụp

2 stored captures · Wayback archive

Bản chụp đã lưu · 2 captures

Tiêu đề trang
Domain Suspended

Bằng chứng lưu trữ

Wayback Machine Snapshot
Một ảnh chụp nhanh lịch sử có sẵn để xem xét bằng chứng
View Archive

Reports & history

No abuse reports recorded · first listed 06/12/2025 · detection timeline

Latest Classified Outcome 2026-10-14 10:41:21 UTC

Primary outcome Không rõ reason: Probe Inconclusive 20% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unreachable Content: Unknown DNS: Resolved Registration: Unknown
Latest HTTP observation Không rõ Probe Inconclusive 20% 2026-10-14 10:41:21 UTC
RDAP registration Không rõ
Observed timeline last reachable: 2026-09-15 22:17:50 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-07-26 22:23:32 UTC
    Domain state transitioned from dead to alive.
  2. Cloudflare Radar Scan 2026-03-07 11:44:23 UTC
    Cloudflare Radar scan registered: View Radar report.
  3. Domain Status Transition 2026-03-01 04:45:09 UTC
    Domain state transitioned from alive to dead.

Pipeline ứng phó với các mối đe dọa

Khám phá
Analysis
Monitoring

13 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Báo cáo cộng đồng

Được 1 thành viên cộng đồng báo cáo; ghi nhận lần đầu 06/12/2025

Báo cáo đã lưu
1
URL được báo cáo duy nhất
1
Đã chấp nhận1

Get help

Official reporting channels, a complaint draft, and listing review

Bạn có bị ảnh hưởng bởi trang web này không?

If credentials were compromised, report immediately. Do not engage with recovery scammers.

Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.

Europol
Tìm kênh báo cáo chính thức cho quốc gia EU của bạn
National police directory
Hãy cảnh giác với những kẻ lừa đảo lợi dụng việc phục hồi dữ liệu! Tội phạm có thể liên hệ lại với nạn nhân trong khi giả làm điều tra viên, luật sư hoặc nhân viên phục hồi. Không trả phí trả trước hoặc chia sẻ thông tin đăng nhập. Tìm hiểu thêm về gian lận trong quá trình phục hồi →

Hãy báo cáo với chính quyền địa phương

Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.

Danh mục 97 quốc gia
Bản nháp có sự hỗ trợ của AI - chi tiết sự cố được nhà cung cấp AI xử lý · Hãy tự mình xem xét và gửi nó

Tools & export

External lookups, JSON / PDF export, API and embed code
Analyze on destroy.tools Run a fresh external analysis of bhd8fa6-4acb-be64-76e26a.xo.je (opens in a new tab)

Bằng chứng và các báo cáo bên ngoài

Phân tích sâu
HTML · IFRAME

Nhúng báo cáo này

Hãy chia sẻ thông tin tình báo về mối đe dọa này trên trang web hoặc blog của bạn

embed.html
<iframe
  src="https://phishdestroy.io/vi/embed/domain/bhd8fa6-4acb-be64-76e26a.xo.je"
  title="PhishDestroy threat report for bhd8fa6-4acb-be64-76e26a.xo.je"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>

Kiểm tra bất kỳ tên miền nào

Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai

Quét ngay

Báo cáo lừa đảo qua email

Hãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng

Báo cáo

Dòng tin tức về các mối đe dọa thời gian thực

Các báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy

Theo dõi

Luôn cập nhật thông tin, luôn an toàn

Theo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai

Dòng tin tức về các mối đe dọa thời gian thực Khiếu nại về thông tin đăng tải này