URLScan verdict
malicious
Báo cáo
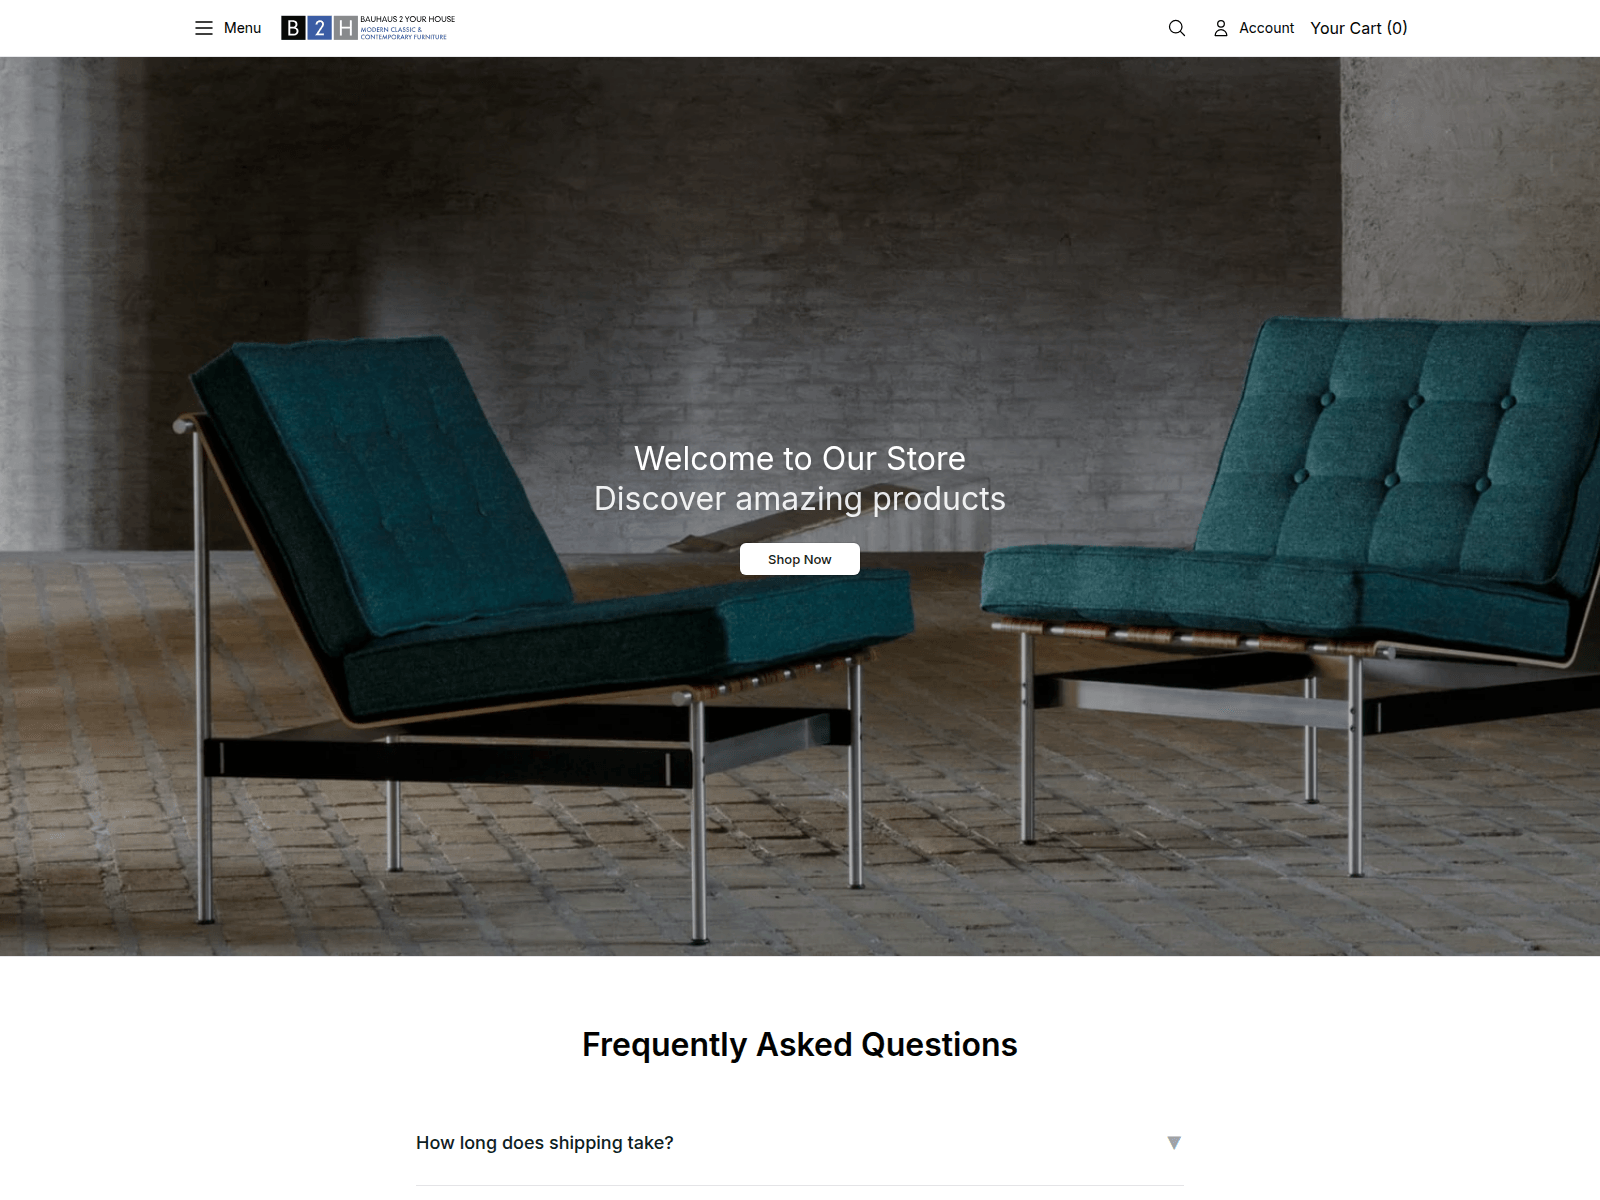
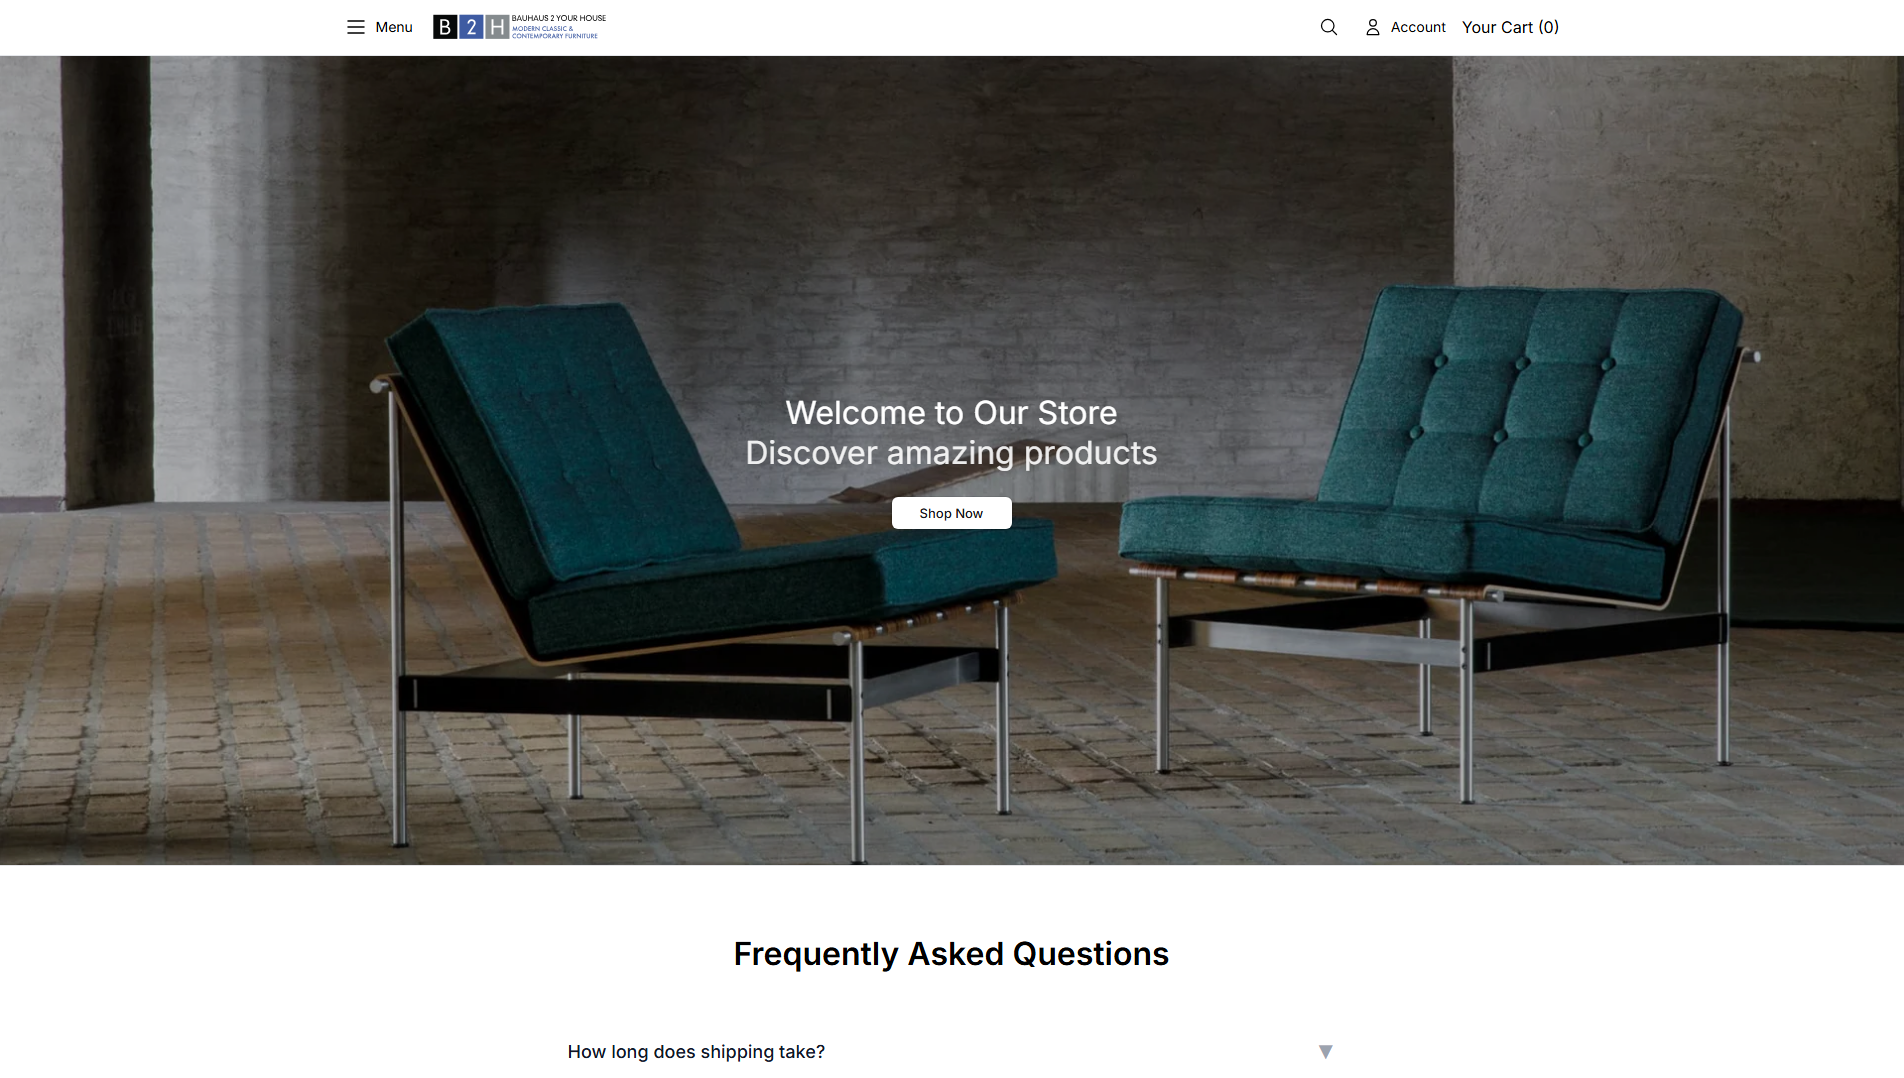
“Bauhaus 2 Your House | Modern Classic Furniture | Bauhaus 2 Your House”
bauhaus2yourhousestore.shop — Hoạt động được biết đến lần cuối (HTTP 200). Mạo danh thương hiệu: Fakeshop; Loại lừa đảo: Impersonation. Tóm tắt bằng chứng: URLScan malicious verdict; PhishDestroy score 65/100. Nhà đăng ký: Dynadot.
Phân tích chi tiết của PhishDestroy AI bên dưới được giữ bằng tiếng Anh để bảo toàn hồ sơ pháp chứng gốc.

The domain bauhaus2yourhousestore.shop returned an HTTP status 200 on 2026-10-11, documenting a successful response at that time. The domain was also observed in a PhishDestroy internal listing, which records its presence in a publisher-owned catalogue.
OTX recorded four pulses related to bauhaus2yourhousestore.shop on 2026-10-11. The domain was first observed on 2026-10-11, and its registration date is documented as 2026-04-14. The SSL certificate for this domain was issued by Let's Encrypt / YE2 and scanned on 2026-10-11. URLScan provided a report for the domain on 2026-10-11, and the page title observed was "Bauhaus 2 Your House | Modern Classic Furniture | Bauhaus 2 Your House."
The PhishDestroy internal listing contains a catalogue record for bauhaus2yourhousestore.shop, documenting its inclusion in a publisher-owned source. OTX provides a measurement of pulses, which are external intelligence entries referencing the domain. These records, along with the HTTP status observation, offer a snapshot of the domain's technical and intelligence context on their respective dates.
For bauhaus2yourhousestore.shop, preserve the PhishDestroy catalogue entry and OTX pulse records for ongoing comparison with future observations. Review the URLScan report and HTTP status record to maintain a reference for technical changes. Use these documented sources to inform any further assessments or monitoring efforts.
Các dữ liệu quan sát đã lưu trữ về sự so sánh giữa trình thu thập dữ liệu và trình duyệt đối với máy chủ này, cùng với việc kiểm tra dấu vân tay thời gian thực dành cho các hệ thống phân phối lưu lượng theo phong cách Keitaro.
Ghi chú về máy quét: alive_content: raw=ok; http=200; via=https_proxy
 (US)
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
bradley.ns.cloudflare.comlana.ns.cloudflare.comLocation describes the IP network.
3d56e91d2209666cea6b77dadb40daed66a63c9644c9a5d0d95ebc093a7bb896Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
212.52.28.161. 9 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20261011-C64B8D Recipient: abuse@rashost.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
Nếu bạn đã nhập thông tin xác thực tài khoản, thông tin cá nhân hoặc thông tin thanh toán hoặc đã tải xuống tệp từ miền này, hãy hành động ngay lập tức. Dưới đây là các nguồn lực giúp bạn báo cáo vụ việc và bảo vệ chính mình.


Chọn quốc gia của bạn để nhận liên hệ tội phạm mạng chính thức hoặc soạn thảo đơn khiếu nại →.
Template-based draft · optional AI wording assistance requires separate consent
Mỗi làn là một lý do khiến một tên miền được liên kết với máy chủ này. Kích thước nút biểu thị các phát hiện từ VirusTotal, còn các nút có đường gạch ngang đã ngừng hoạt động. Danh sách đầy đủ được trình bày dưới đây.
Có cùng mã băm favicon hoặc cùng tiêu đề trang với máy chủ này.
IP gốc này lưu trữ nhiều miền lừa đảo — cơ sở hạ tầng có thể được chia sẻ giữa các chiến dịch.
Các tên miền này cũng nhắm đến người dùng Fakeshop. Xem tất cả các mối đe dọa liên quan đến “Fakeshop” →
Được đăng ký thông qua cùng một nhà đăng ký tên miền. Một nhà đăng ký tên miền phục vụ hàng triệu khách hàng không có mối liên hệ với nhau, do đó việc này chỉ cho thấy sự trùng hợp về số liệu chứ không chứng minh được mối liên hệ nào.
Các báo cáo được thêm gần đây từ cơ sở dữ liệu PhishDestroy. Các liên kết khám phá này không ngụ ý cơ sở hạ tầng hoặc quyền sở hữu chung.
Phân tích mối đe dọa bằng cách sử dụng danh sách chặn được lưu trữ, WHOIS, DNS và bằng chứng quét công khai
Quét ngayHãy gửi các tên miền đáng ngờ đến cơ sở dữ liệu mối đe dọa của chúng tôi — để bảo vệ cộng đồng
Báo cáoCác báo cáo lừa đảo gần đây và những thay đổi về tính khả dụng được quan sát thấy
Theo dõiTheo dõi các mối đe dọa đang diễn ra hoặc phản đối danh sách này nếu bạn cho rằng đây là kết quả báo động sai