
Tìm kiếm các tên miền đang được theo dõi và xem xét các bằng chứng đã lưu trữ, các kết quả phát hiện cũng như tình trạng khả dụng mới nhất được ghi nhận.
221,187
Tổng số được theo dõi
215,382
Phát hiện VT
93,441
Lần cuối được nhìn thấy đang hoạt động
127,746
Không có sẵn tại thời điểm kiểm tra lần cuối
0
VT Đang chờ xử lý
How This Attack Works
Ice Phishing is a sophisticated technique that targets users by manipulating blockchain transactions. Here's how it typically unfolds.
STEP 1
Target Identification
Attackers identify potential victims, often targeting users with significant cryptocurrency holdings.
STEP 2
Setup Spoofed Environment
The attacker creates a fake website or app mimicking a legitimate service to deceive users.
STEP 3
Credential Harvesting
Users are tricked into entering sensitive information, allowing attackers to gain access to their accounts.
STEP 4
Unauthorized Transactions
With access to the victim's account, attackers execute unauthorized transactions, siphoning funds.
Technical Analysis
Ice Phishing attacks often involve the use of malicious smart contracts that exploit users by redirecting transactions to the attacker's wallet. Attackers employ social engineering techniques to lure victims into signing transactions that they believe are legitimate. These transactions often use clever code obfuscation to hide the true nature of the transaction. Attackers also leverage compromised infrastructure, such as DNS servers or hosting services like those registered through arin or Vercel Inc., to create convincing phishing environments. By mimicking legitimate services, these attacks bypass traditional security checks, making detection challenging.
Real Cases
Ethereum Wallet Scam (2023)
$1.2 million stolen
Attackers used a fake wallet service to steal credentials, resulting in a substantial loss of Ethereum funds.
Crypto Exchange Phishing (2024)
$2.5 million stolen
A phishing site mimicking a popular exchange tricked users into entering their login details, leading to significant asset theft.
DeFi Nền tảng Breach (2024)
$3.8 million stolen
A decentralized finance platform was targeted by ice phishers who exploited smart contract vulnerabilities to siphon funds.
How to Detect
Unusual domain names that closely resemble legitimate services
Unexpected requests for private keys or seed phrases
Emails or messages urging immediate action on your crypto assets
Anomalies in transaction requests, such as unexpected gas fees
Lack of HTTPS encryption on websites requiring sensitive input
How to Protect Yourself
1
Always verify the URL before entering sensitive information
2
Enable two-factor authentication on all accounts
3
Regularly monitor transaction logs for unauthorized activities
4
Educate yourself about common phishing tactics
5
Use hardware wallets for enhanced security
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 40 domains tracked for this threat type
Ice Phishing 40 domains
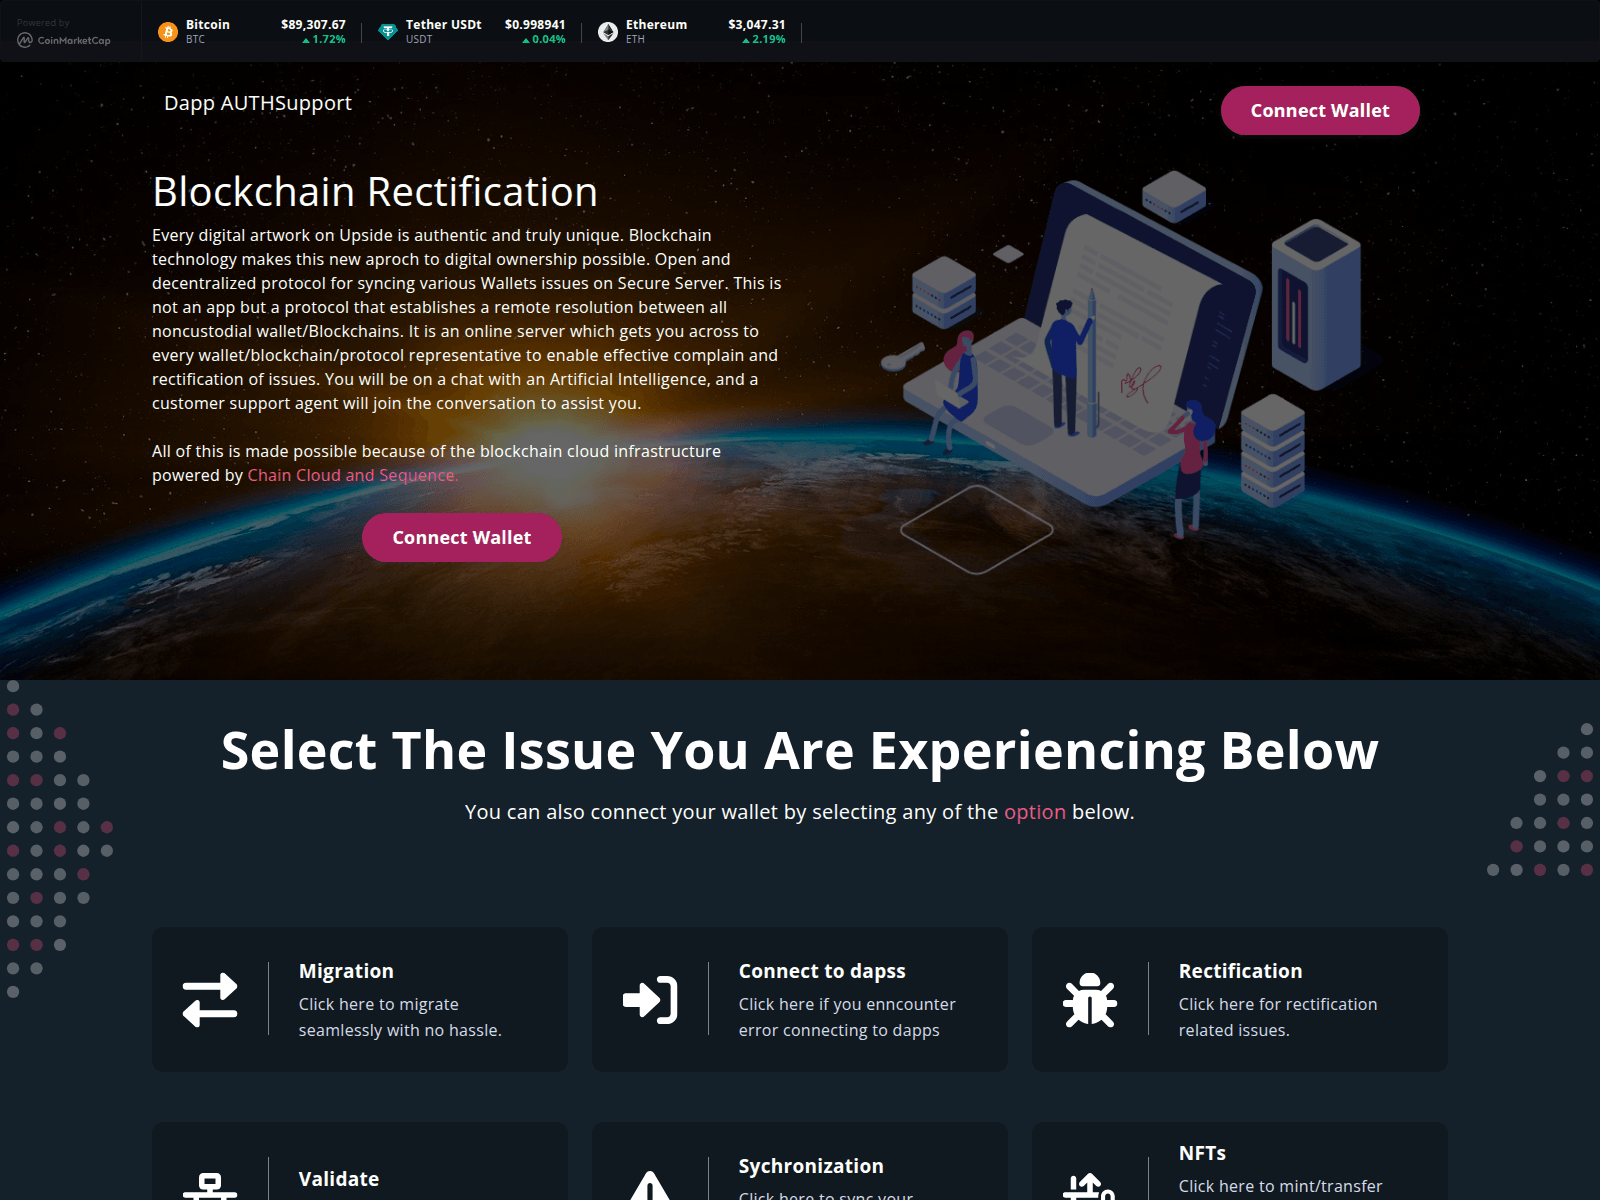
rectification-fixuserauthentication.vercel.app
rectifyissues-now.vercel.app
supports-rectification.vercel.app
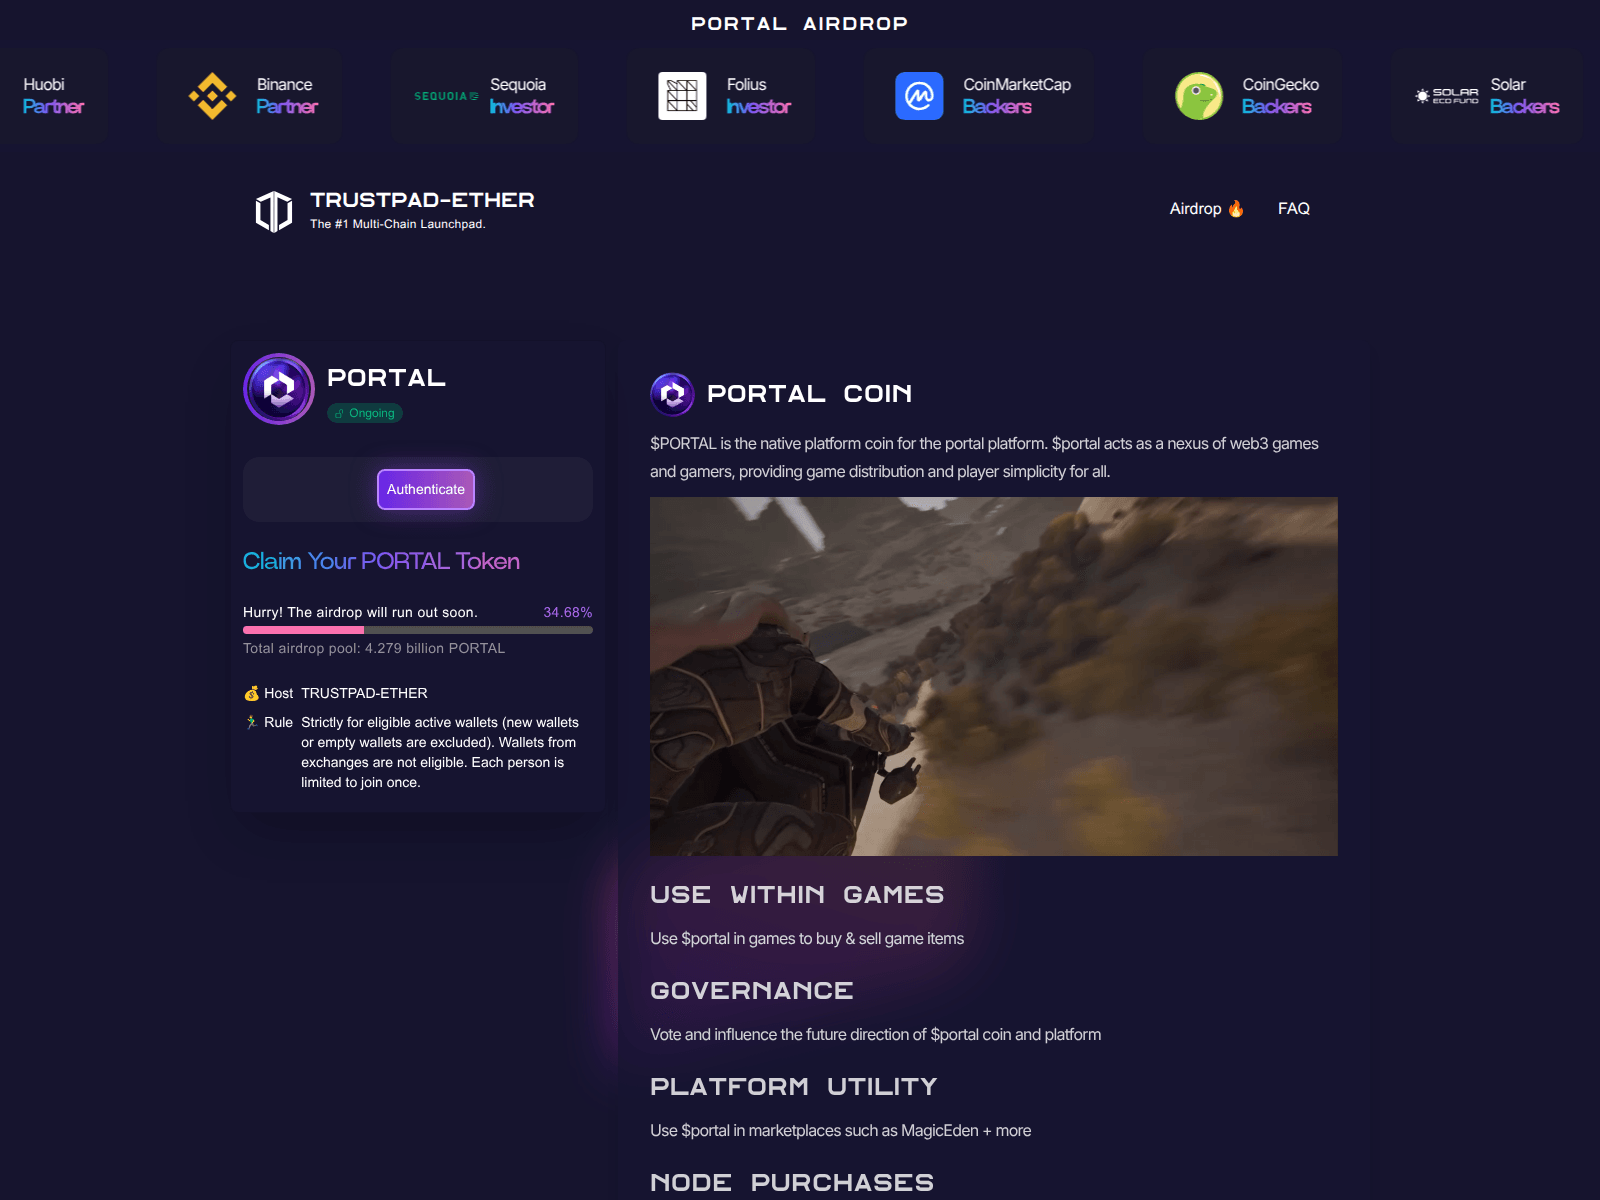
authwalletconnect.com
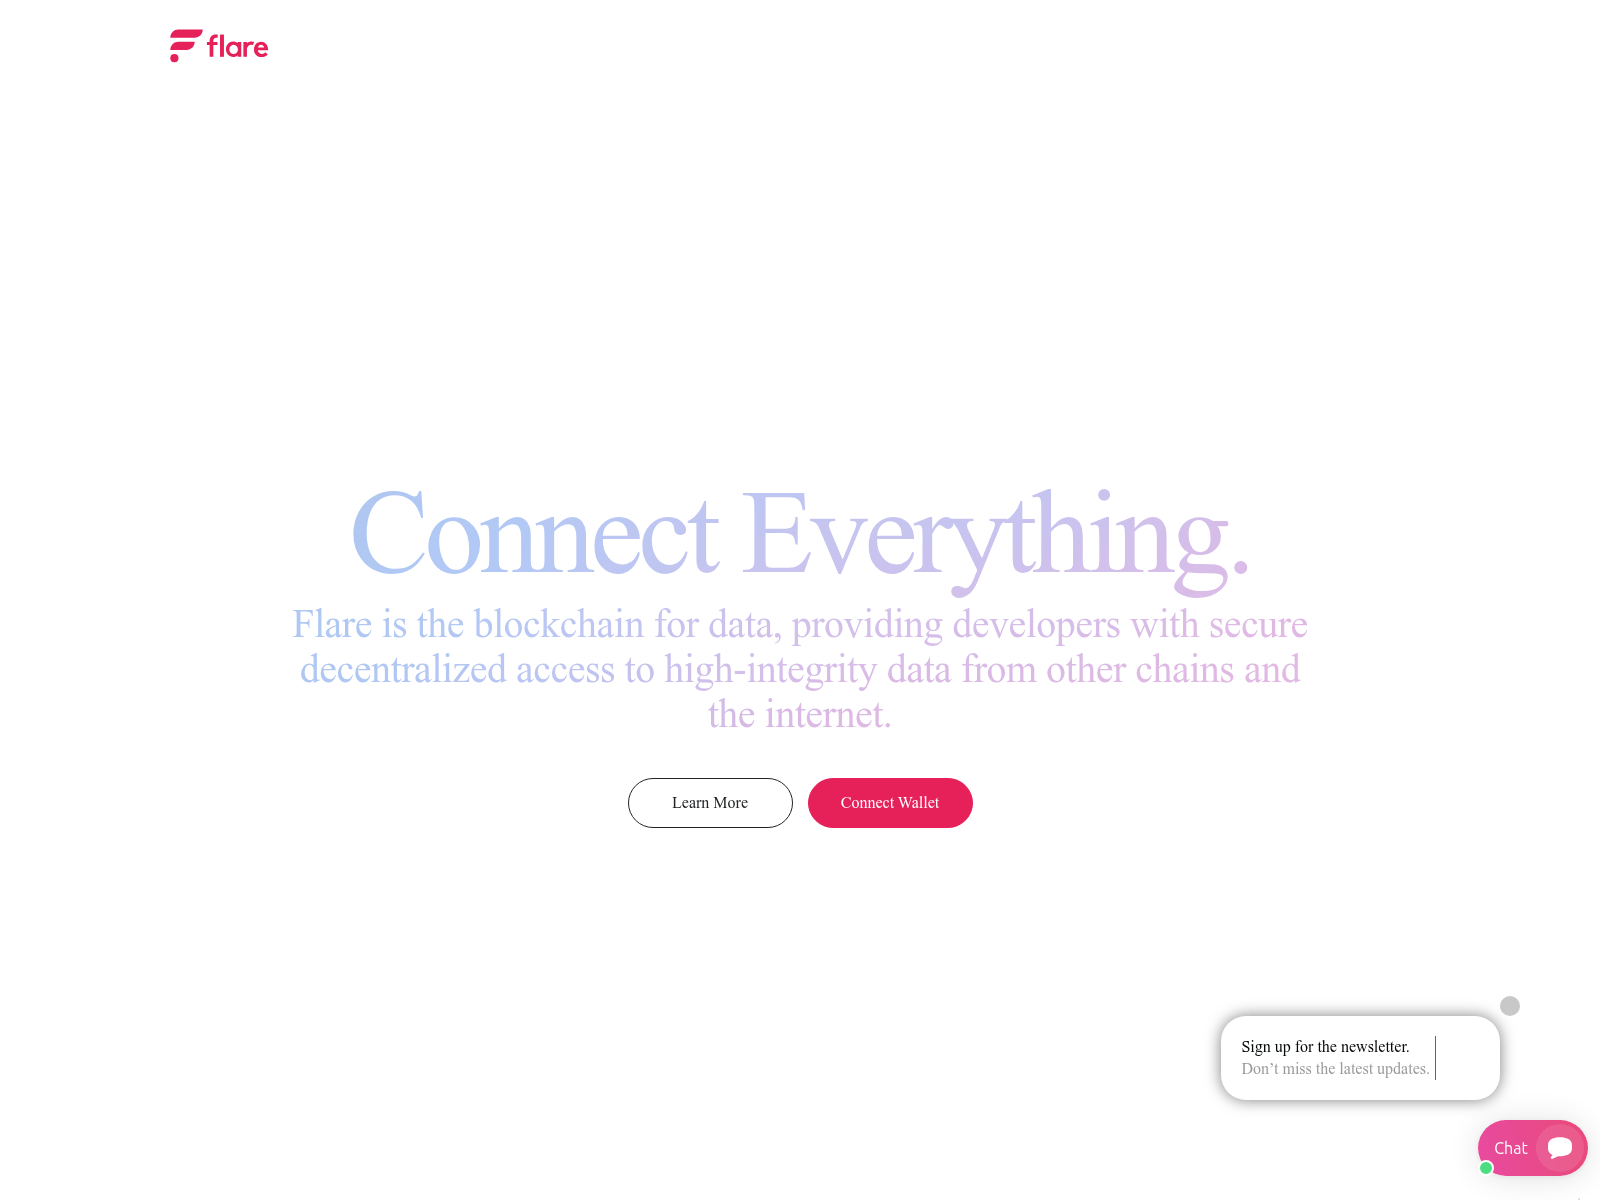
flaretokensdrop.com
seaportal.fo
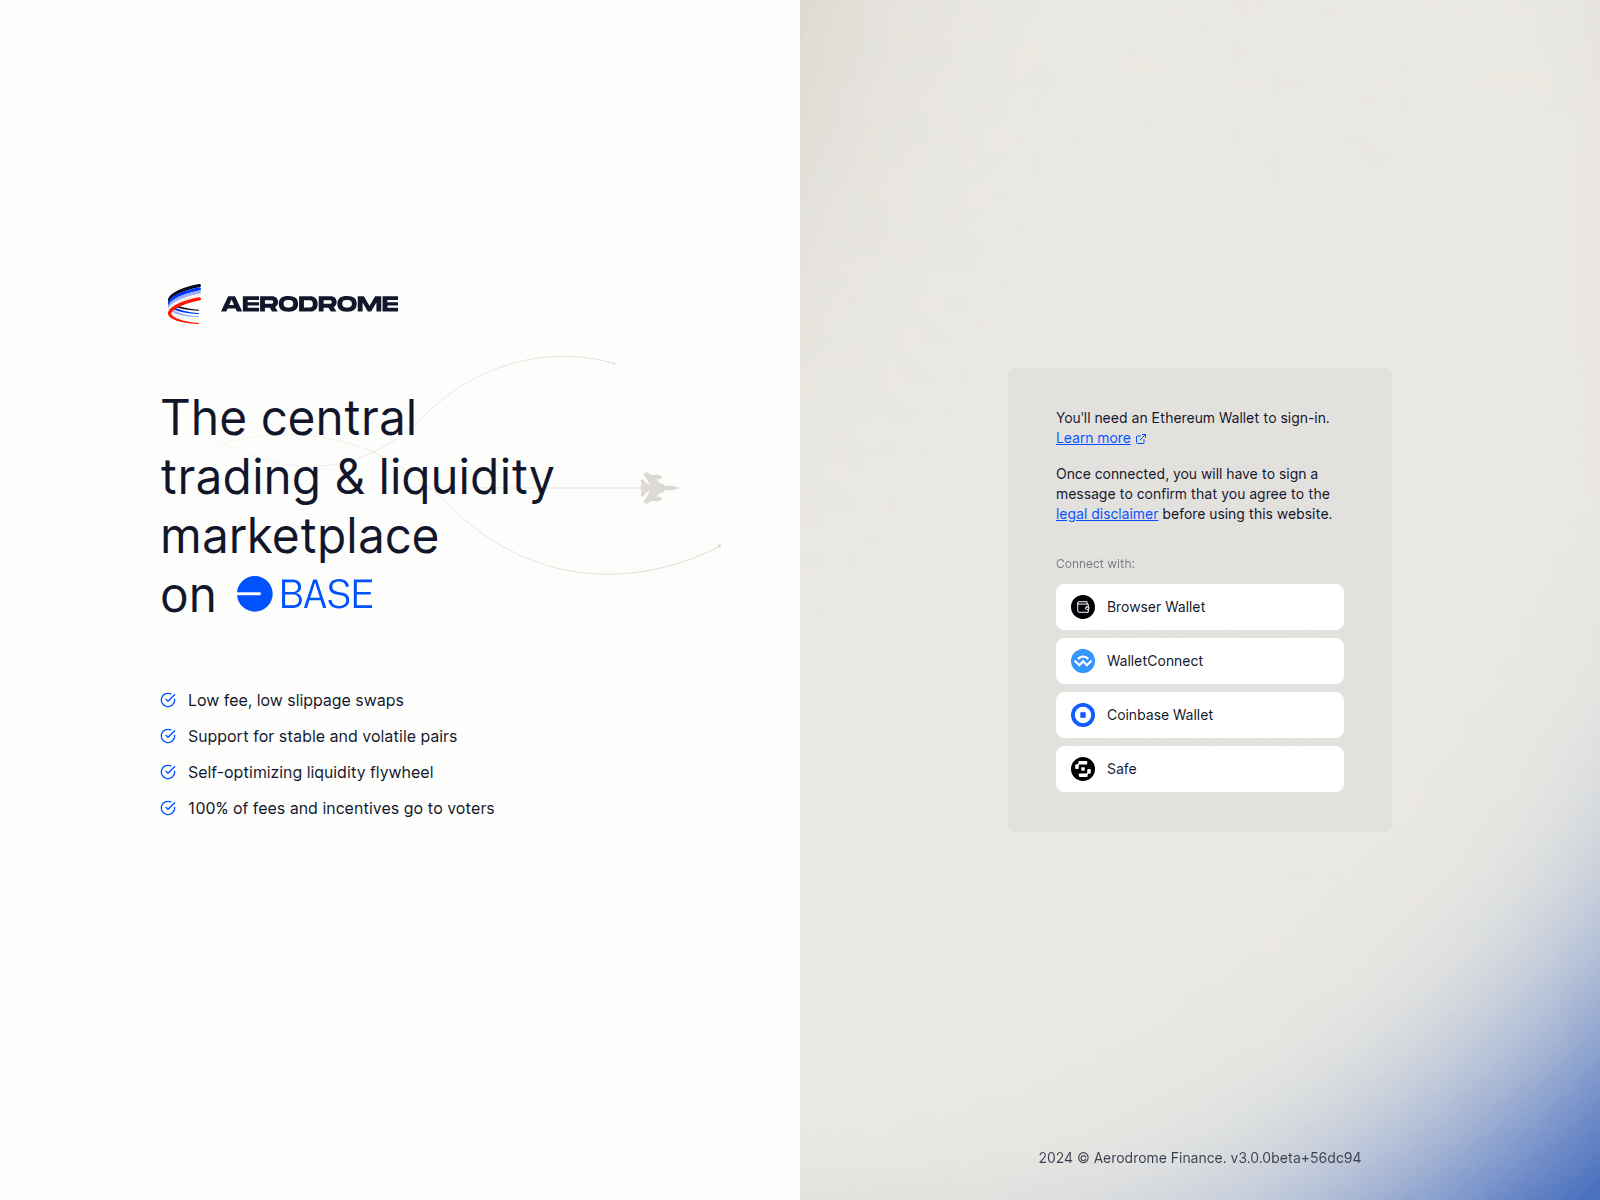
agencyanalyticsframe.us.com
enacoin-newbridge.com
flrconnectportal.live
airdrop.wrlomhole.net
aoerodrome.finance
chainxtrade.com
ethdrawclaimdrop.org
test123.sphere-drainer.cc
arb.claimscrypto.top
eth-drainer.exontra.com
drnr.fiznen.com
h2-finance.web.app
xrpdistributions.firebaseapp.com
ngcrp.com
drainer.bexcapitaltrade.com
flare.linkportalnet.com
trovako.com
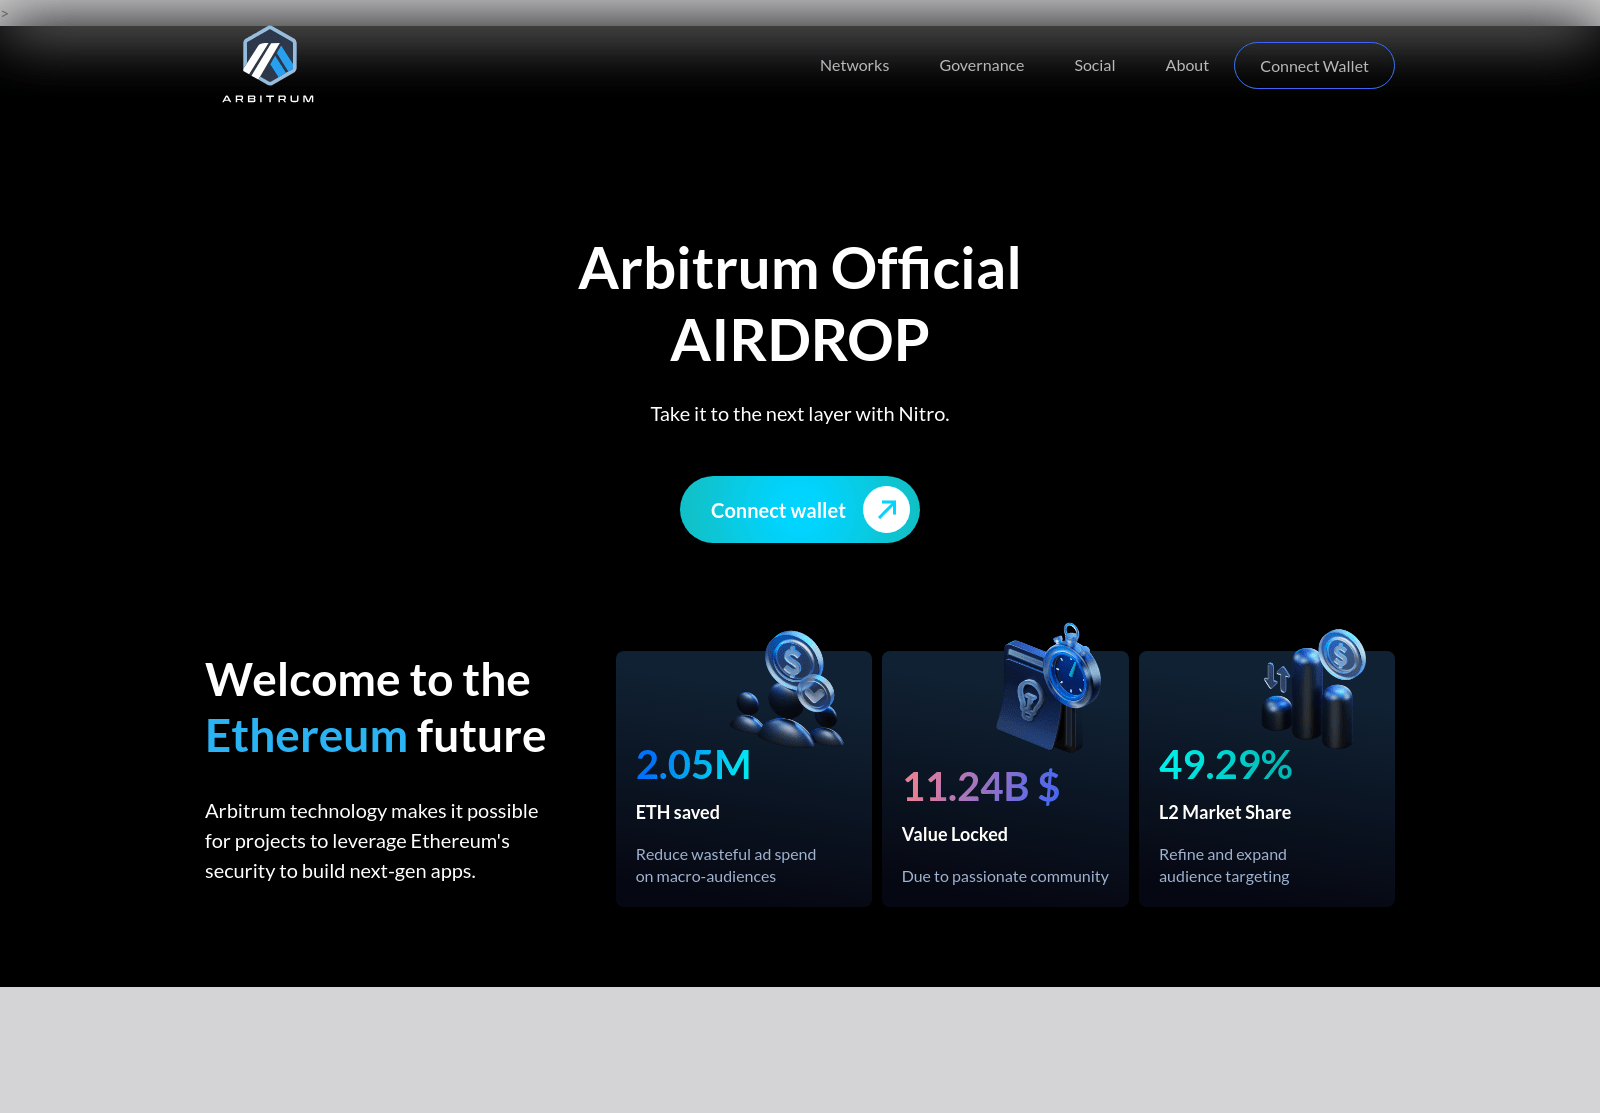
arbitriums.icu
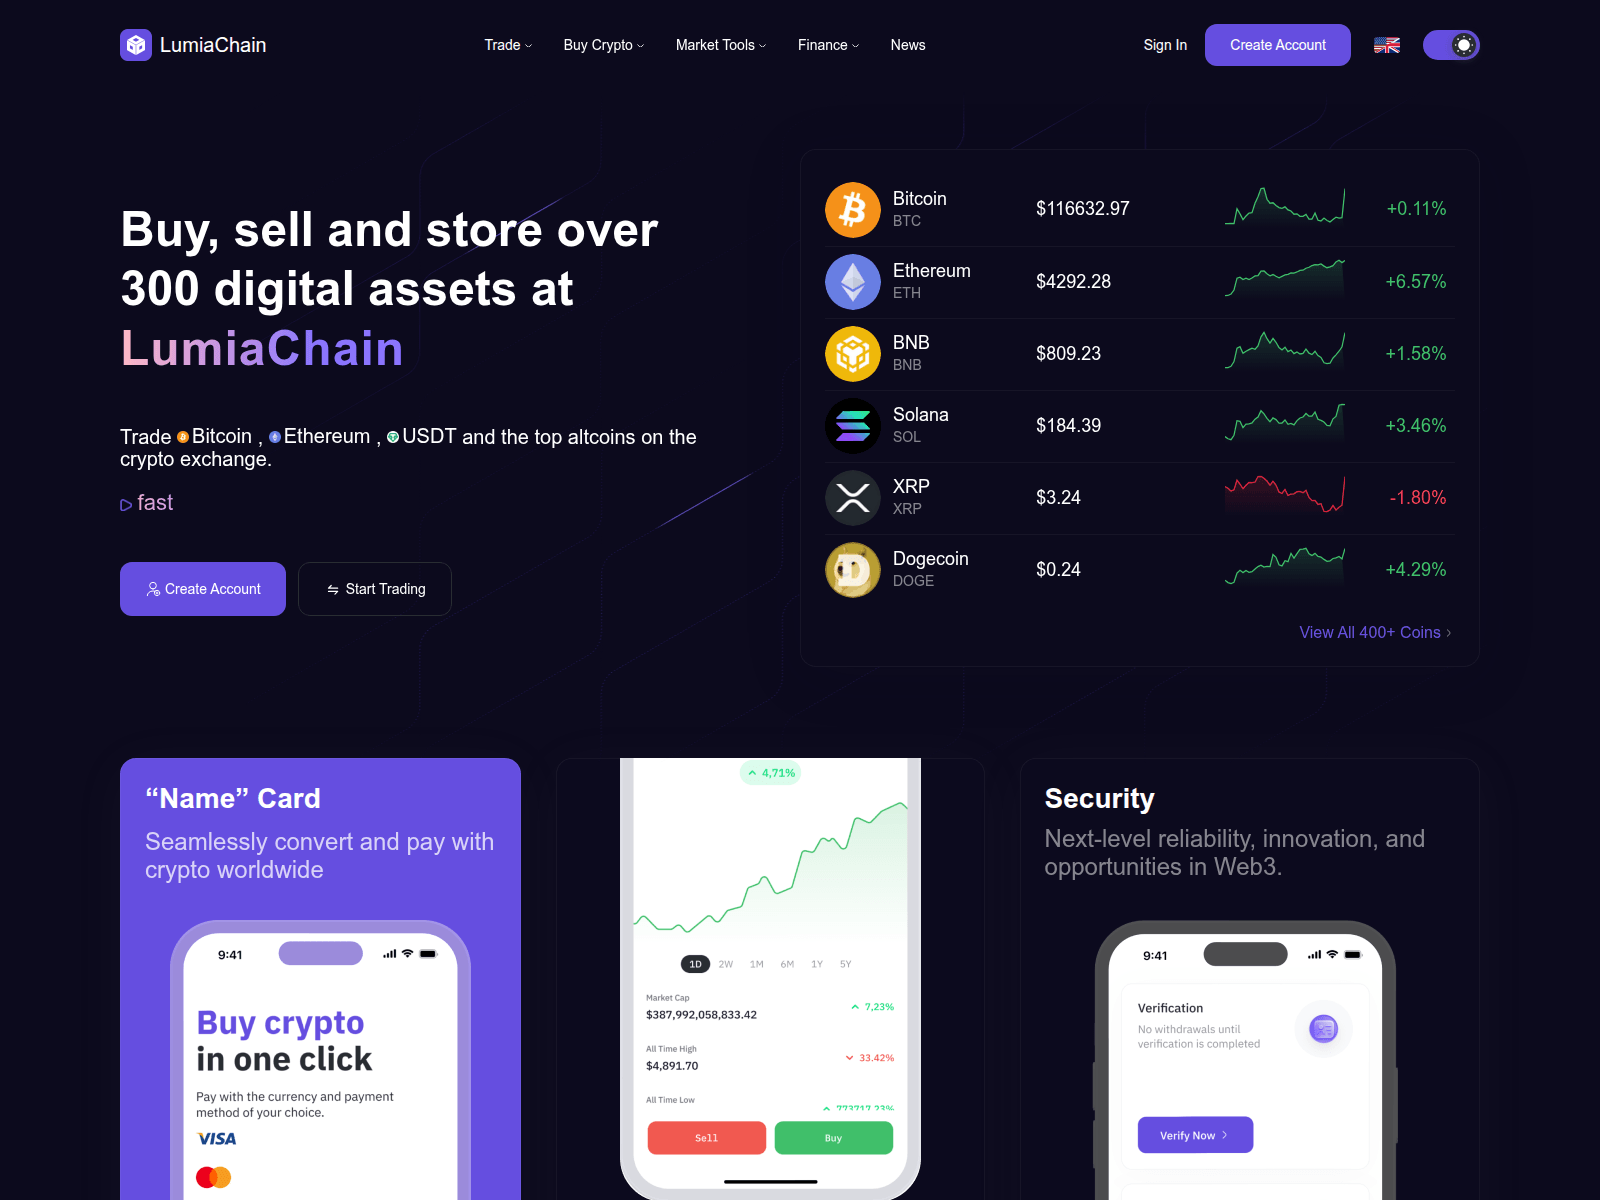
lumiachain.com

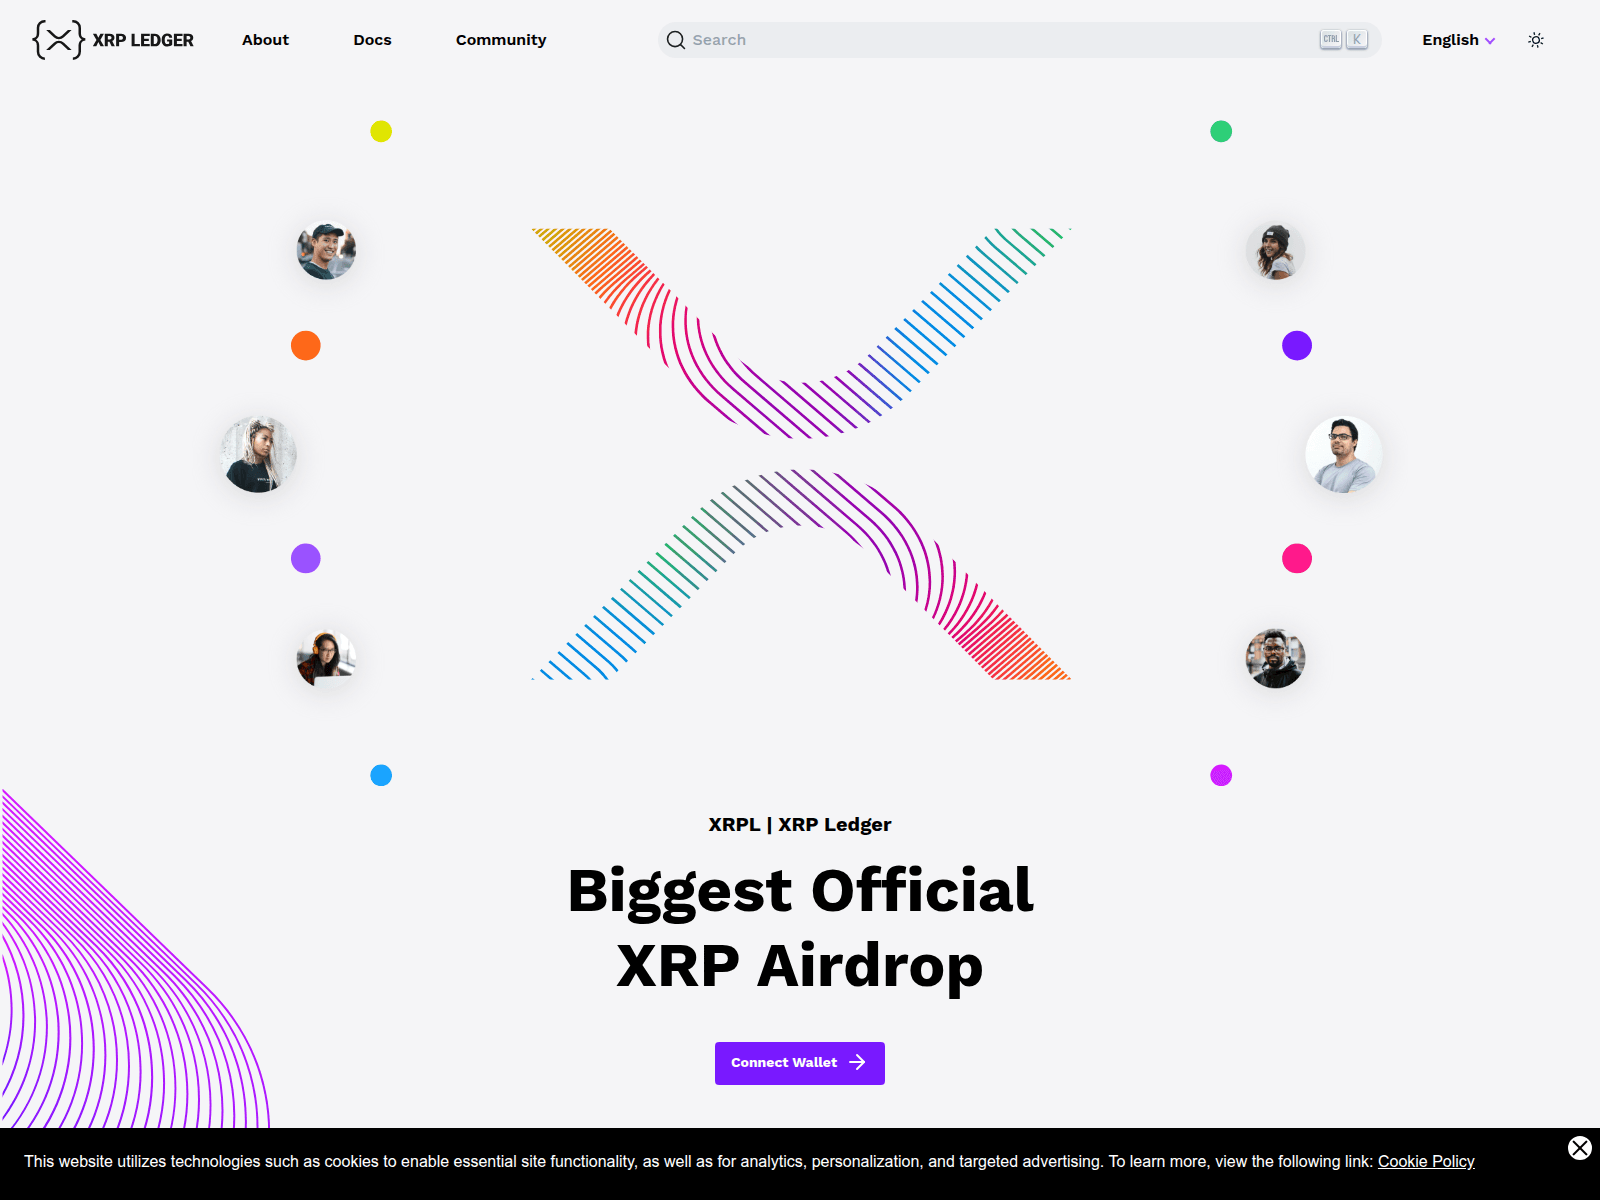
xrpdistributions.web.app
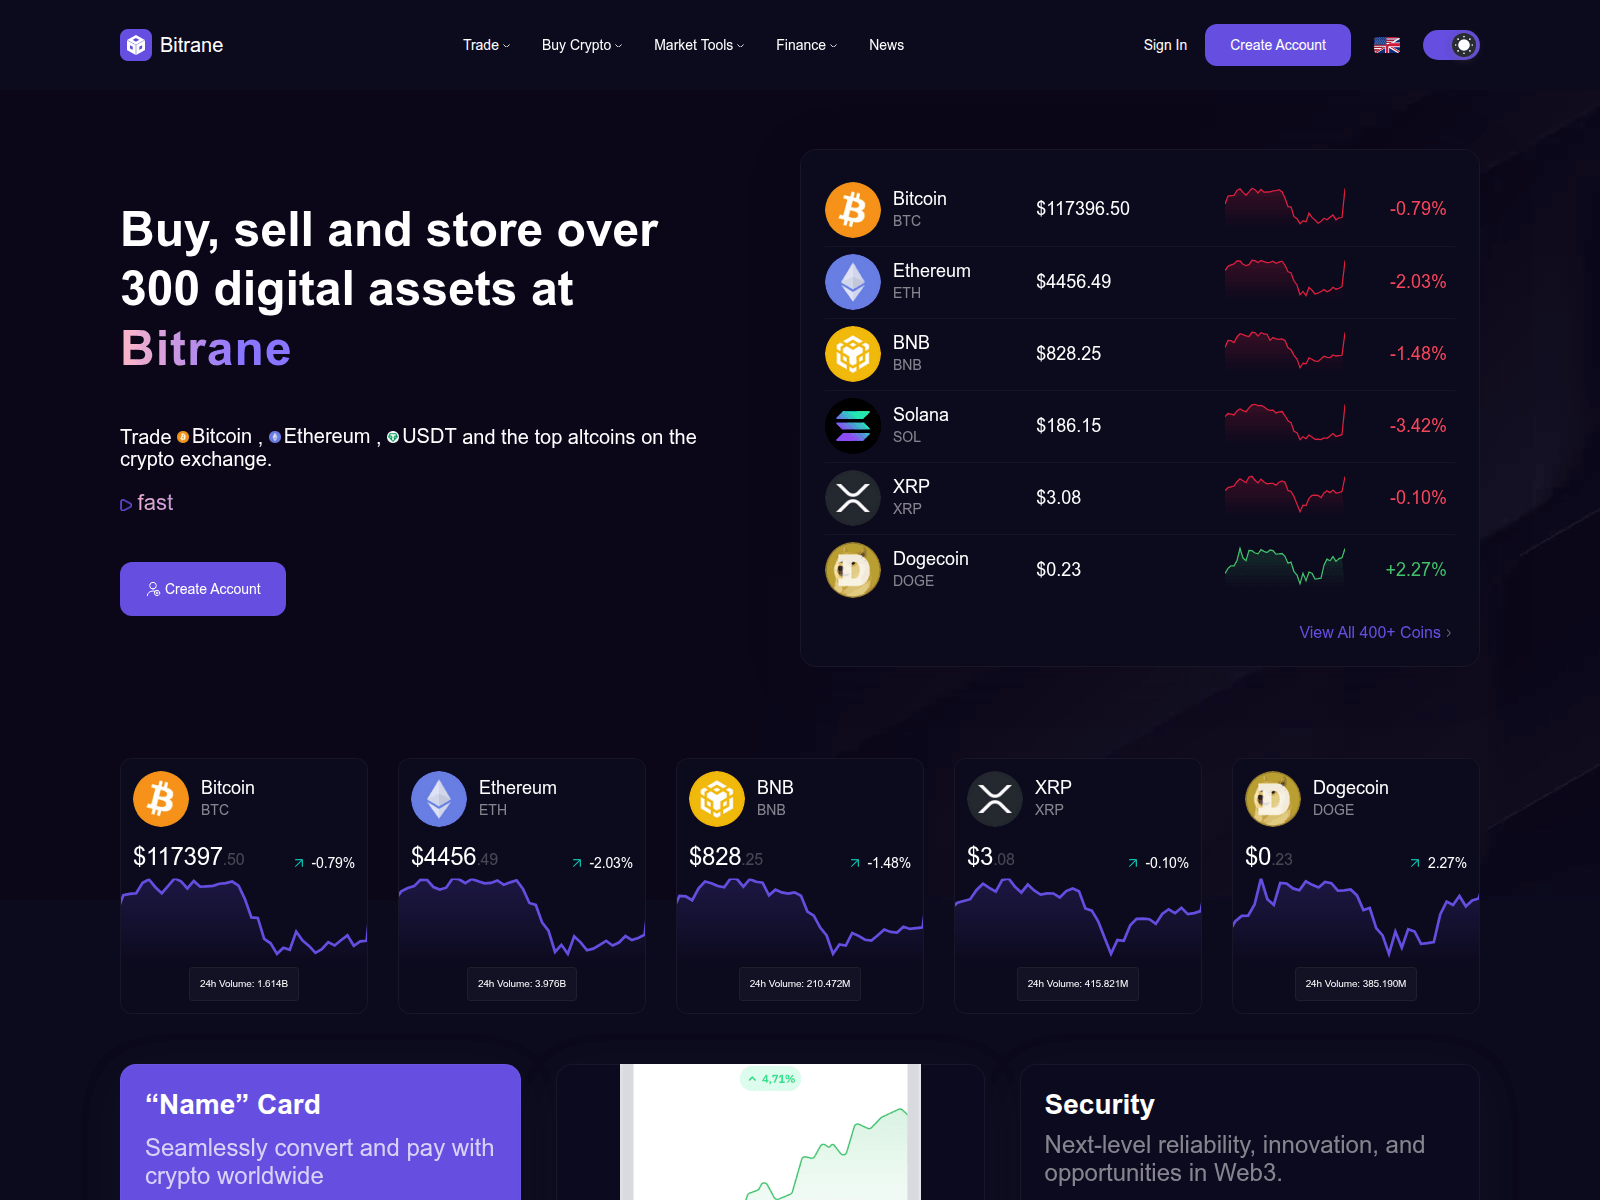
bitrane.com
duplicate-disabled-13104.invalid
ledgerlane.icu
megaethlabs.top
semantic.nexus-innovators.site
claim.mindof-pepe.world
defi-launch.io
metaversentf.com
bridge.maob.site
dymensionrollapps.com
fincaptor.app
publicsale.well3.website
randombitcoins.com
Pipeline ứng phó với các mối đe dọa
Cách thức xác minh từng miền trong trung tâm này và cách thức vô hiệu hóa các mối đe dọa đã được xác nhận. Trực quan hóa toàn bộ quy trình →
Kiểm tra thông tin tình báo về mối đe dọa— Mỗi tên miền đều được quét và đối chiếu với:
urlscan.ioẢnh chụp màn hình · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency Báo cáoCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Bảo mật FiltersQuad9 · AdGuard · CleanBrowsingWeb-Kiểm traFull surface scan
 crt.sh
Đồng bộ hóa nhà cung cấp toàn cầu— Các trường hợp phát hiện đã được xác nhận sẽ được gửi đến 29 đối tác:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecĐánh giá trang webAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftGỡ bỏ APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.Báo cáoHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust