VirusTotal
15 / 89
Повідомити

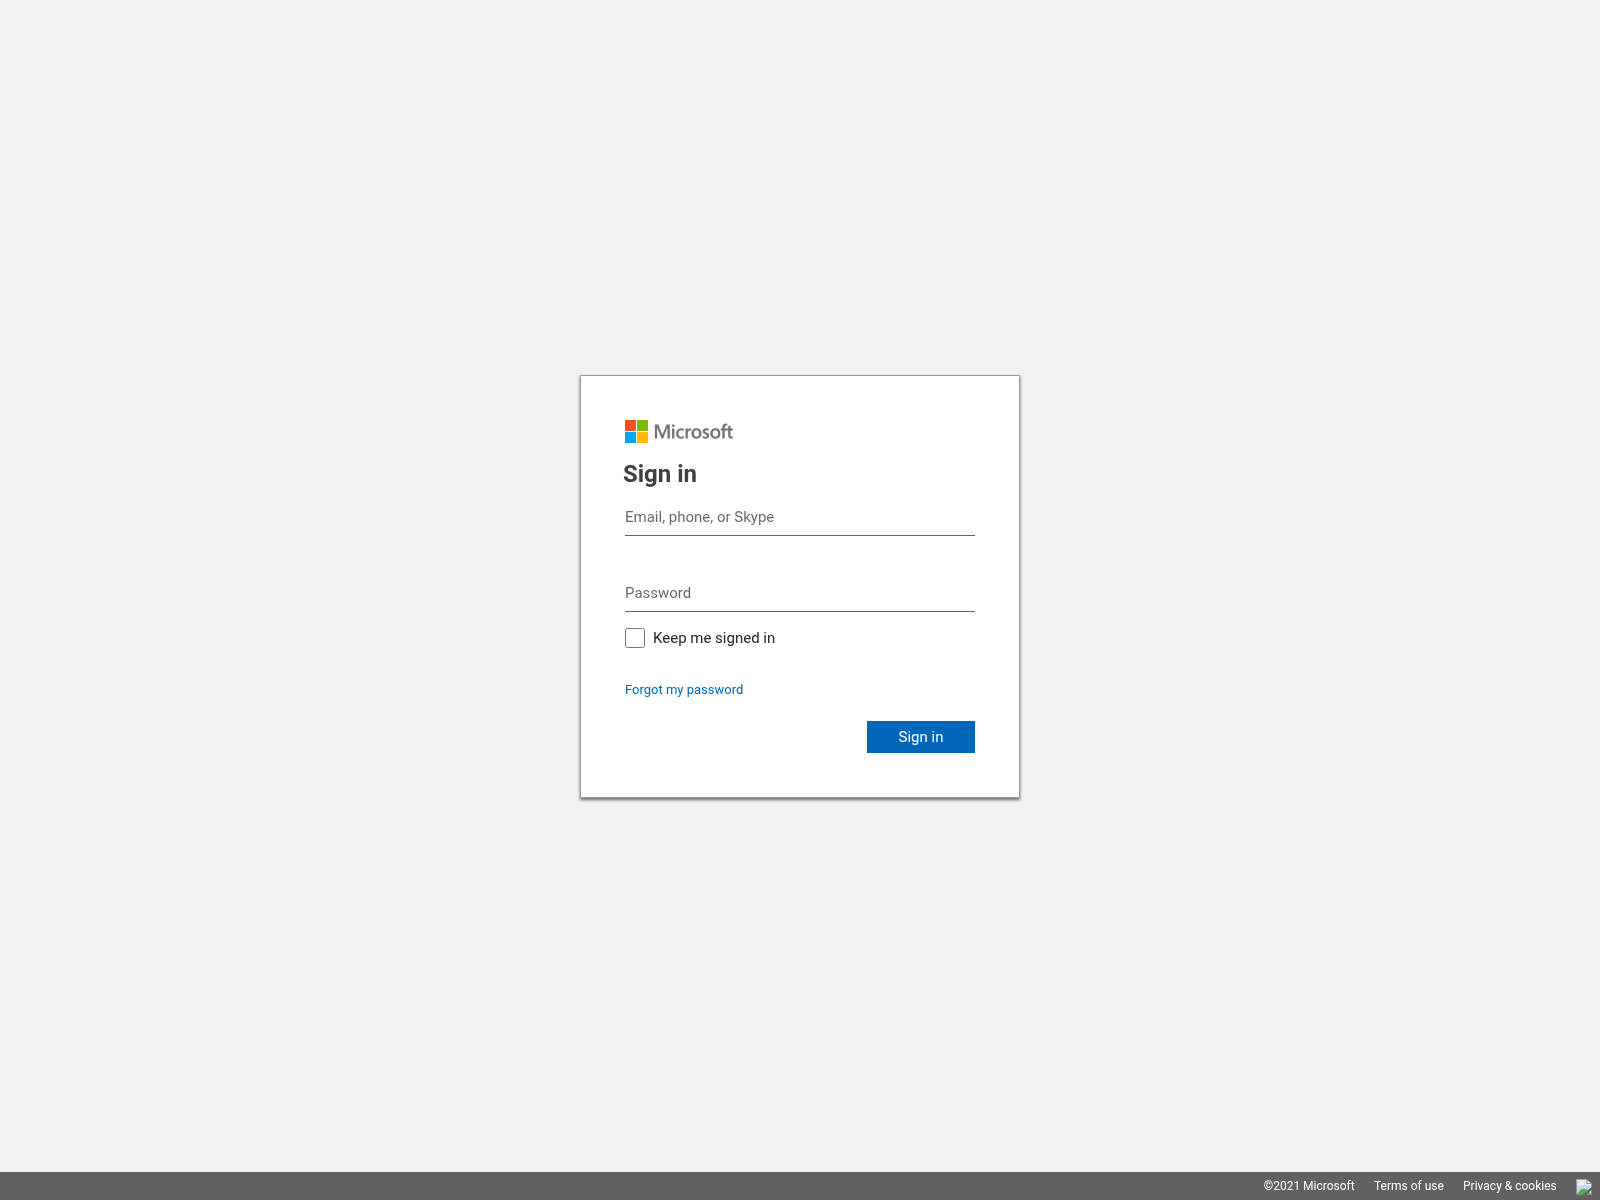
“Sign in to your Microsoft account”
mssecuregateway.de — Контент недоступний (HTTP 410). Уособлення бренду: Microsoft; Тип шахрайства: Tech Support Scam. Зведення доказів: VirusTotal 15/89 (ADMINUSLabs, alphaMountain.ai, BitDefender, Chong Lua Dao, Forcepoint ThreatSeeker); URLScan malicious verdict; Google Safe Browsing flagged; CF Radar malicious; PhishDestroy score 100/100.
Докладний аналіз PhishDestroy AI нижче залишено англійською, щоб зберегти оригінальний криміналістичний запис.

15 / 89
provider verdict: malicious
Повідомитиmalicious
Повідомити5/14
Threat flag recorded
Повідомитиchecked — no match recorded
27 community references
Повідомитизбережений звіт
 Повідомити
This domain, mssecuregateway.de, operates as a credential harvesting site specifically designed to impersonate Microsoft authentication portals. Analysis indicates the page title 'Sign in to your Microsoft account' was used to deceive users into submitting login credentials, which would be captured by threat actors for unauthorized access to accounts or further malicious activities. The infrastructure mimics legitimate Microsoft services, increasing the likelihood of successful phishing attempts against unsuspecting users. Infrastructure analysis reveals multiple high-confidence indicators of compromise. The domain was registered on February 21, 2026, with an SSL certificate issued by Let's Encrypt (R12), resolving to IP address 87.230.86.70 under AS8972 (Host Europe GmbH). Security vendors flagged this domain as malicious, with 25 out of 95 engines on VirusTotal detecting it as a phishing threat. Additionally, the domain appears on one security blocklist, and Google Safe Browsing has explicitly flagged it as a phishing site. The combination of these indicators confirms the domain's malicious intent. Users who visited mssecuregateway.de or entered credentials on this site should immediately take corrective action. First, reset passwords for any accounts accessed through the domain, prioritizing Microsoft and other sensitive services. Enable multi-factor authentication where available to mitigate unauthorized access. Monitor accounts for suspicious activity, such as unrecognized logins or unauthorized transactions. If corporate credentials were exposed, notify internal security teams to assess potential lateral movement risks. Finally, ensure endpoint security tools are updated to detect and block similar threats in the future.
Збережені дані спостережень за взаємодією веб-сканера та браузера для цього хоста, а також перевірка відбитків у режимі реального часу для систем розподілу трафіку типу «Кейтаро».
Apache/2.4.68 (Unix)Примітка щодо сканера: terminal_unconfirmed: candidate_reason=dead_http; raw=http_410; http=410; via=http_proxy; server=Apache/2.4.68 (Unix)
docks01.rzone.deshades12.rzone.demssecuregateway.depriority 20Location describes the IP network.
5844a39cdc39cd526101ee2cf325e752d7585f884ac864237b257e3d9d535decSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of mssecuregateway.de · checked Mar 1, 2026
16 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Повідомив 1 учасник спільноти; уперше помічено 20.01.2026
Якщо ви ввели облікові дані облікового запису, особисту чи платіжну інформацію або завантажили файл із цього домену, негайно вживіть заходів. Нижче наведено ресурси, які допоможуть вам повідомити про інцидент і захистити себе.


Виберіть свою країну, щоб отримати офіційні контакти кіберзлочинців або створити проект скарги →.
Template-based draft · optional AI wording assistance requires separate consent
Кожна смуга позначає одну з причин, через яку домен пов’язаний із цим хостом. Розмір вузла вказує на виявлення VirusTotal, а вузли, позначені пунктирною лінією, вже не працюють. Повний перелік наведено нижче.
Однаковий хеш фавікону або однаковий заголовок сторінки, як у цього хоста.
Ці домени також націлені на користувачів Microsoft. Переглянути всі загрози типу «Microsoft» →
Аналіз загроз за допомогою збереженого списку блокувань, WHOIS, DNS і загальнодоступних доказів сканування
Сканувати заразДодавайте підозрілі домени до нашої бази даних загроз — захищайте спільноту
ПовідомитиОстанні звіти про фішинг і помічені зміни доступності
ВідстежуватиСлідкуйте за актуальними загрозами або оскаржте цей запис, якщо вважаєте, що це помилкова тривога





