VirusTotal
2 / 92
Повідомити


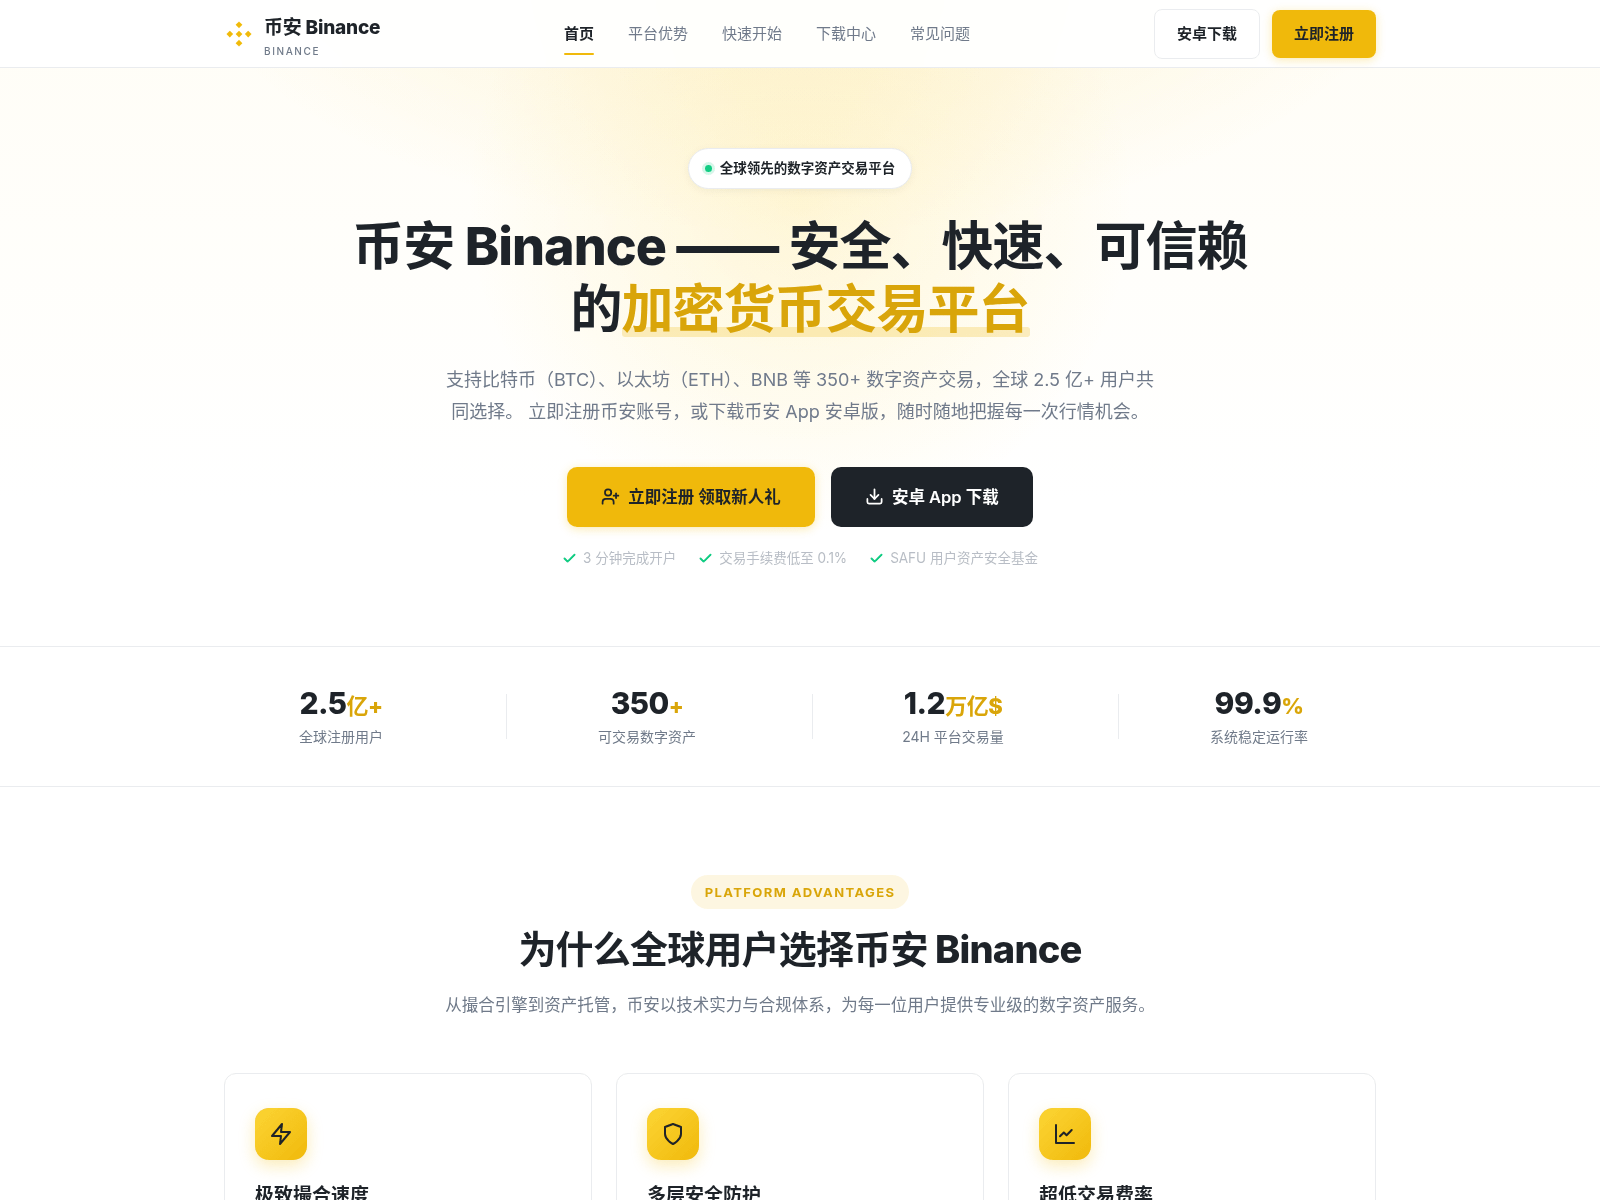
“币安 Binance 官网入口 | 币安App安卓下载与注册教程(2026最新)”
binanv-binance.com.cn — Останній відомий активний (HTTP 200). Уособлення бренду: Binance; Тип шахрайства: Impersonation. Зведення доказів: VirusTotal 2/92 (Gridinsoft, LevelBlue); URLQuery 2 det.; URLScan malicious verdict; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 98/100. Реєстратор: 北京新网数码信息技术有限公司.
Докладний аналіз PhishDestroy AI нижче залишено англійською, щоб зберегти оригінальний криміналістичний запис.

2 / 92
2 det.
Повідомитиmalicious
Повідомити2 community references
Повідомитиprovider verdict: suspicious
Повідомитизбережений звіт
 Повідомити
Checked; no threat flag recorded
ПовідомитиThe domain binanv-binance.com.cn was observed in a security context with a VirusTotal detection count on 2026-10-10. On the same date, the domain was also listed on two external blocklists, providing further context for its profile.
On 2026-10-10, VirusTotal recorded 2 detections out of 92 total scanners for binanv-binance.com.cn. The domain appeared on MetaMask and SEAL blocklists as of that date. OTX referenced the domain in 2 pulses on 2026-10-10. PhishDestroy included an internal listing for the domain. The SSL certificate issuer was recorded as Let's Encrypt / YR1.
VirusTotal provides a measurement of how many security vendors flagged the domain, which helps gauge its visibility in threat intelligence feeds. OTX records document community-driven observations, while the MetaMask and SEAL blocklists represent external security assessments. This combination of sources covers both automated scanner results and curated blocklist entries, offering a broad view of the domain’s recorded security context on the specified date.
For binanv-binance.com.cn, retain the VirusTotal, OTX, and PhishDestroy records for ongoing monitoring and future comparison. Review the external blocklist entries from MetaMask and SEAL alongside these sources to track any changes in security assessments over time.
Full extracted values, their blockchain and collection source. An address found in page content does not establish who controls it.
https://t.me/binanceexchangeStored page referenceIoC extraction recorded 2026-10-11 04:01:28 UTC
Збережені дані спостережень за взаємодією веб-сканера та браузера для цього хоста, а також перевірка відбитків у режимі реального часу для систем розподілу трафіку типу «Кейтаро».
nginxПримітка щодо сканера: alive_content: raw=ok; http=200; via=https_proxy; server=nginx
ns1.myhostadmin.netns2.myhostadmin.netns5.west.cnns6.west.cnLocation describes the IP network.
d1a1ac09790eb33523b37d0532dcc673744aa85d47d8a742d8cd886143da4c91Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of binanv-binance.com.cn · checked Oct 10, 2026
179.61.182.48. 12 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
Збережено 187 схожих доменів
Показано 100 із 187
PD-20261010-A19A10 Recipient: philispotts7284@hotmail.com AUP & Terms of Service Violations: Acceptable Use Policy: Active phishing operations targeting internet users directly violate standard AUP provisions prohibiting fraud and deceptive practices. Terms of Service: Material breach of service terms regarding malicious use, providing contractual justification for immediate suspension. Applicable Legal Framework (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Investigation Notice: We fully respect your internal investigation processes and discretion. Prompt remediation protects innocent users while mitigating regulatory compliance scrutiny, legal liability, and brand reputation risks associated with ongoing malicious infrastructure.
Якщо ви ввели облікові дані облікового запису, особисту чи платіжну інформацію або завантажили файл із цього домену, негайно вживіть заходів. Нижче наведено ресурси, які допоможуть вам повідомити про інцидент і захистити себе.


Виберіть свою країну, щоб отримати офіційні контакти кіберзлочинців або створити проект скарги →.
Template-based draft · optional AI wording assistance requires separate consent
Кожна смуга позначає одну з причин, через яку домен пов’язаний із цим хостом. Розмір вузла вказує на виявлення VirusTotal, а вузли, позначені пунктирною лінією, вже не працюють. Повний перелік наведено нижче.
Однаковий хеш фавікону або однаковий заголовок сторінки, як у цього хоста.
Ця вихідна IP-адреса містить кілька фішингових доменів — інфраструктура може бути спільною для кампаній.
Ці домени також націлені на користувачів Binance. Переглянути всі загрози типу «Binance» →
Зареєстровані через одного й того самого реєстратора. Один реєстратор обслуговує мільйони клієнтів, які не пов’язані між собою, тому це лише об’єднує дані, а не доводить наявність зв’язку.
Нещодавно додані звіти з бази даних PhishDestroy. Ці посилання для виявлення не передбачають спільної інфраструктури чи власності.
Аналіз загроз за допомогою збереженого списку блокувань, WHOIS, DNS і загальнодоступних доказів сканування
Сканувати заразДодавайте підозрілі домени до нашої бази даних загроз — захищайте спільноту
ПовідомитиОстанні звіти про фішинг і помічені зміни доступності
ВідстежуватиСлідкуйте за актуальними загрозами або оскаржте цей запис, якщо вважаєте, що це помилкова тривога





