Перейти до звіту про безпеку
Безпека домену та аналіз загроз
aktivasi-fitur-dana2.hint.my.id favicon

aktivasi-fitur-dana2.hint.my.id

Resolved IP
172.67.159.233
Registered
18.04.2026
Загрозливий вердикт Критичний
Доступність Контент недоступний Вміст був недоступний під час останнього спостереження
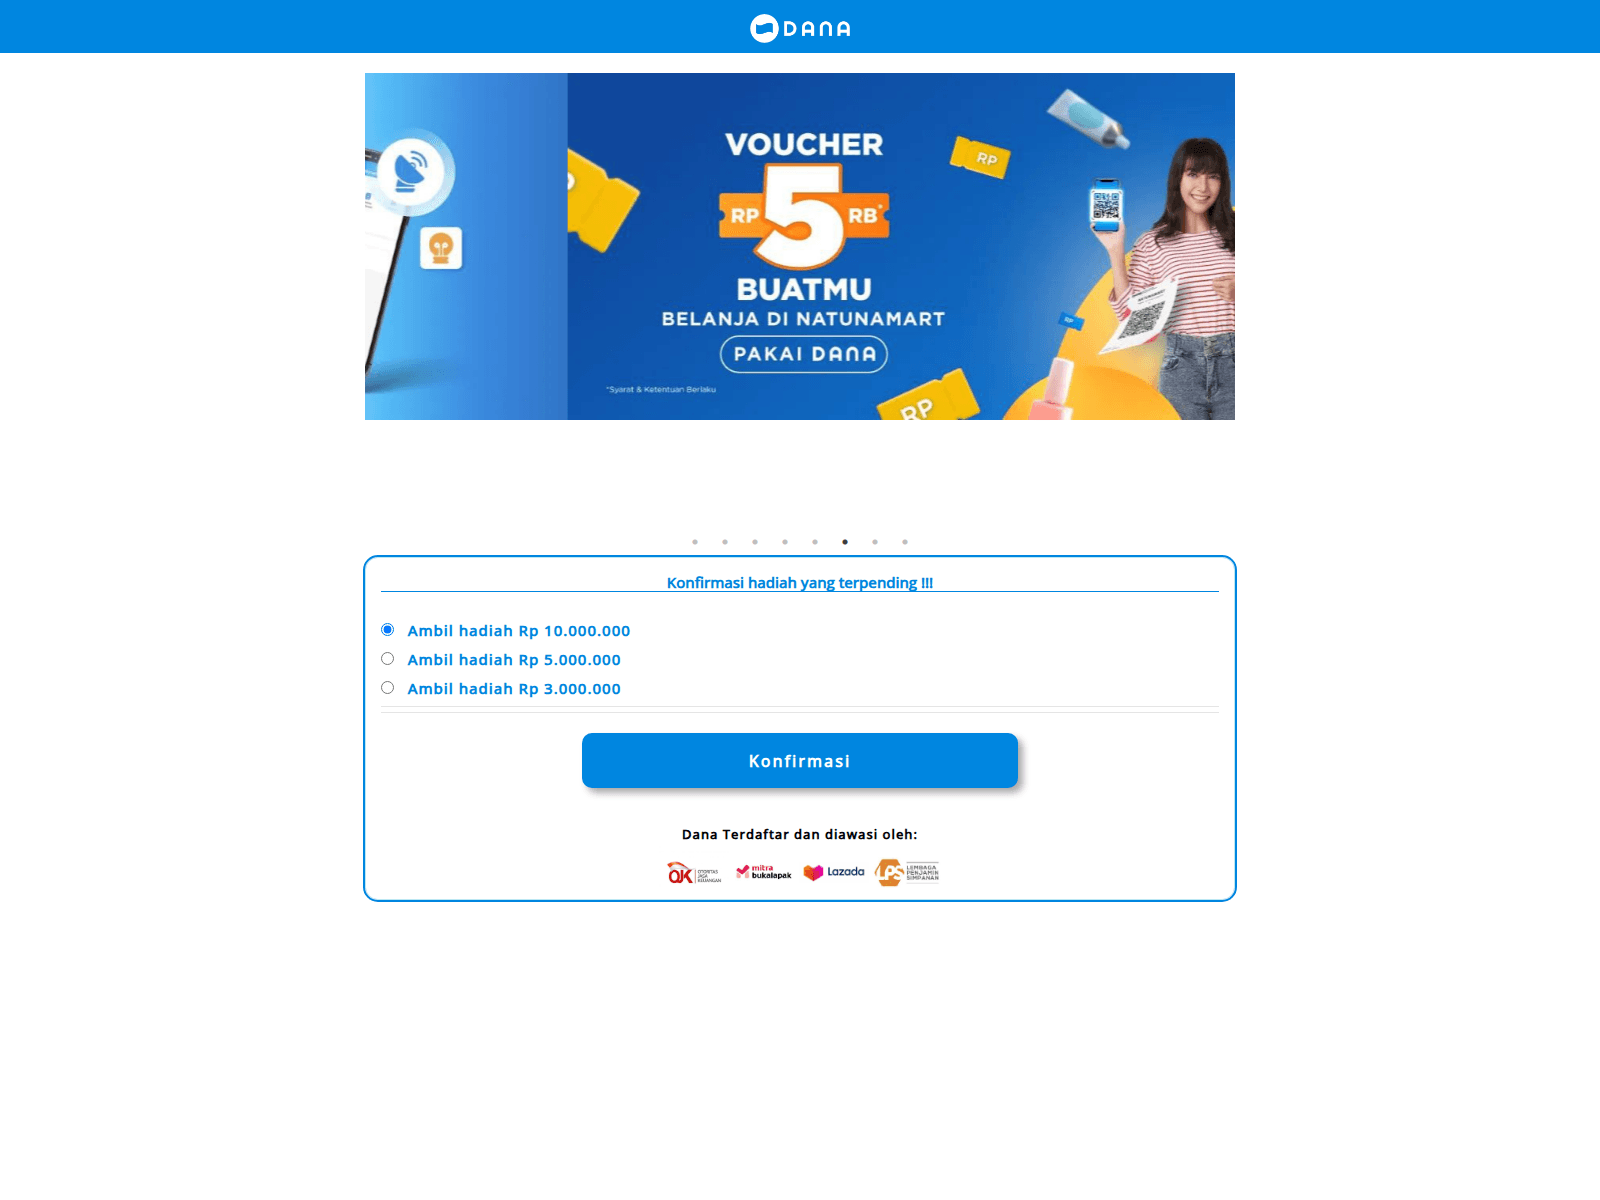
Виявлення VirusTotal: 17/89 Уособлення бренду: Dana
07.09.2026 Dana CDN
API
Цей домен було позначено як шкідливий
Системи безпеки повідомляють про виявлення: 17. Будьте дуже обережні — не вводьте облікові дані чи особисту інформацію.
Огляд звіту

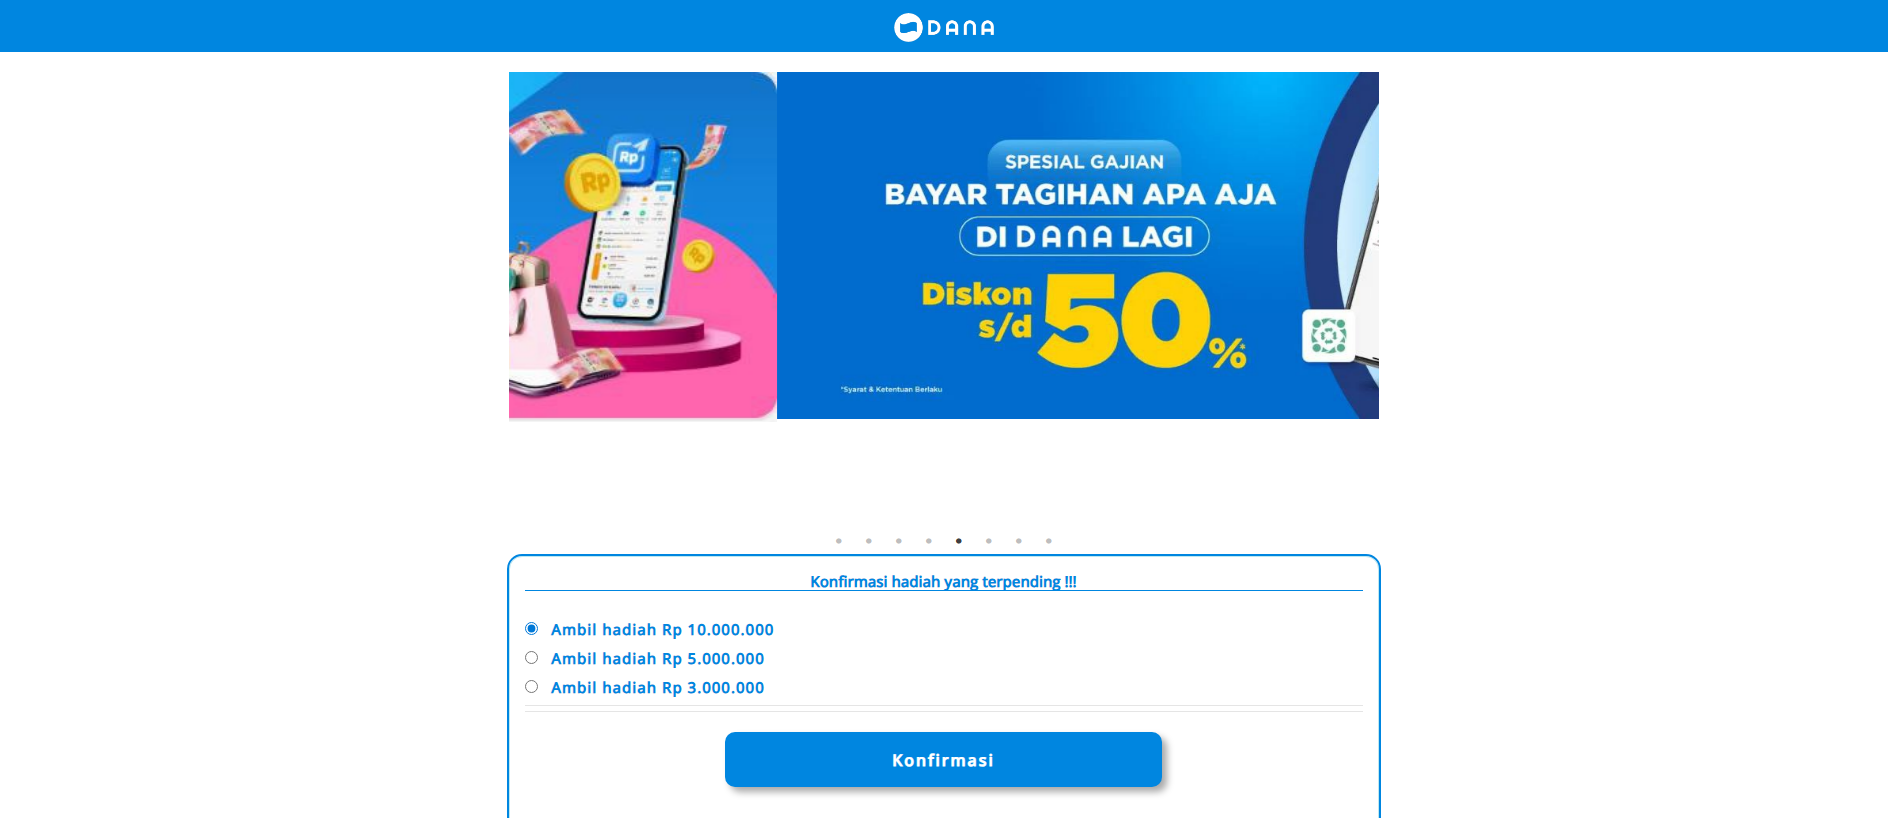
aktivasi-fitur-dana2.hint.my.id — Контент недоступний. Уособлення бренду: Dana; Тип шахрайства: Impersonation. Зведення доказів: VirusTotal 17/89 (alphaMountain.ai, BitDefender, CRDF, ESET, Emsisoft); URLScan malicious verdict; CF Radar malicious; PhishDestroy score 95/100.

Докладний аналіз PhishDestroy AI нижче залишено англійською, щоб зберегти оригінальний криміналістичний запис.

VirusTotal
VirusTotal
17 det.
CF Radar
Шкідливий
URLScan
URLScan
Сертифікат TLS
Прострочений або неперевірений
Вік
6 mo
Зафіксований статус
Контент недоступний
PhishDestroy
DestroyList
У списку

Source evidence

6 sources

Google Safe Browsing

Checked; no threat flag recorded

Повідомити
Розвіддані з мережевої безпеки
CF Cloudflare Radar Verdict Шкідливий
Phishing
SSL Certificate Invalid
SSL certificate is invalid or expired. Issuer:

Зведення доказів

Критичний
VirusTotal
17/89
URLScan
Stored capture

Assessment

On 2026-10-01, aktivasi-fitur-dana2.hint.my.id appeared in a phishdestroy internal listing, giving a dated catalogue record from that source. A PageSpeed performance score of 73 was recorded for this domain on 2026-09-07, a separate technical measurement from that day.

Recorded Evidence

VirusTotal recorded 17 detections across 89 total scanners for aktivasi-fitur-dana2.hint.my.id on 2026-09-11. The domain was first observed on 2026-09-07, and its SSL scan on that same date named Let's Encrypt / YE1 as the issuer. The phishdestroy internal listing was recorded on 2026-10-01, while the PageSpeed score of 73 was measured on 2026-09-07.

Interpretation

The VirusTotal detections and the phishdestroy internal listing are distinct source records, each produced under its own criteria and timing. The PageSpeed score and SSL scan describe technical characteristics rather than catalogue entries, so they address different aspects of the domain. The recorded dates allow a reader to see when each observation was captured, without treating them as a single combined signal.

Recommended Actions

Retain the VirusTotal report and the phishdestroy internal listing for aktivasi-fitur-dana2.hint.my.id as records from separate sources. Compare those two records side by side to understand what each one covers. Preserve the PageSpeed and SSL scan results for technical reference, and recheck the same sources later if updated observations are needed.

Аналіз виявлення та ухилення

Перевірка маскування та розподілу трафіку

Ще не відскановано Наразі не зафіксовано жодних відмінностей між роботами-павуками та браузерами

Збережені дані спостережень за взаємодією веб-сканера та браузера для цього хоста, а також перевірка відбитків у режимі реального часу для систем розподілу трафіку типу «Кейтаро».

Збережений прапор маскування
Ще не відскановано
Останнє сканування маскування

Примітка щодо сканера: timeout: raw=timeout; http=0; via=http_proxy; error=HTTPConnectionPool(host='191.101.26.25', port=5764): Read timed out. (read timeout=7)

Перевірка відбитків пальців у режимі реального часу за адресою TDS
Сім відбитків Keitaro та порівняння «краулер проти браузера», що запускаються зі сканера PhishDestroy, коли ця панель відкрита.
Очікування

Збережений знімок · 2 captures

Domain details

Домен
URLScan Verdict Шкідливий score 100 Phishing brand: Dana report ↗
IP Context Cloudflare shared edge origin IP hidden Репутація Edge-IP не пов’язана з цим доменом.
Registration (base domain)hint.my.id · Створено 18.04.2026 (173d)
Час до першої недоступності 4 days
Що ми враховуємо Час, що минув від першого збереженого звіту про порушення до першого спостереження, що вміст був недоступний. Це не встановлює причину.
Що містить кожен звіт Збережені записи вихідних звітів можуть посилатися на докази, доступні на той час, наприклад вердикти постачальників, реєстраційні дані, деталі хостингу, класифікації або знімки екрана. Ця сторінка не визначає точного доставленого корисного навантаження, квитанції, підтвердження чи дії одержувача.
Технічні подробиціProvenance & timestamps
Вперше виявлено07.09.2026
DOM Analysisanalyzed 07.09.2026score 88/1001 brand signal
Submitted URLhttp://aktivasi-fitur-dana2.hint.my.id/Danaweb
Favicon Hash
Impersonates
Dana
Сертифікат TLS
Certificate hostname mismatch · Виданий Let's Encrypt / YE1

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
172.67.159.233
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

Репутація Edge-IP не пов’язана з цим доменом.

Location describes the IP network.

Сертифікат TLS

Issuer
Let's Encrypt / YE1
Valid from
2026-08-14 07:41:14
Valid until
2026-11-12 07:41:13
Hostname coverage
Certificate hostname mismatch
Validity
Within stored validity dates
Collection time
2026-09-07 01:02:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprint4e3af9c135c3440d43c9c8c865af3171c68786912f2a4cc627f8ff11438db835
Certificate names · 1 SANs
  • hint.my.id

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

viewdns.info · 172.67.159.233rapiddns.io

Latest Classified Outcome 2026-10-07 01:49:49 UTC

Primary outcome Невідомо reason: Stale Current Evidence 0% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Unknown Content: Unknown DNS: Stale Registration: Unknown
Latest HTTP observation Невідомо Probe Inconclusive 20% 2026-10-07 01:49:49 UTC
RDAP registration Невідомо
Observed timeline last reachable: 2026-09-15 22:17:48 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Технології · 8 identified
Detected via Cloudflare Radar · Wappalyzer engine
Поскаржитися на цей домен Надішліть докази та допоможіть захистити інших

Аналіз VirusTotal

17 / 89 постачальників безпеки позначили цей домен
View on VT
Last analyzed First positive detection Previous stored snapshot: 17 detections
alphaMountain.ai
BitDefender
CRDF
ESET
Emsisoft
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
«Касперський»
LevelBlue
Lionic
Netcraft
OpenPhish
SOCRadar
Sophos
Webroot
Аналіз продуктивності сайту

Google PageSpeed Insights — mobile performance audit of aktivasi-fitur-dana2.hint.my.id · checked Sep 7, 2026

73
Needs Work
Performance
FCP
2.99s
First Contentful Paint
LCP
4.22s
Largest Contentful Paint
CLS
0.097
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
6.05s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor

Forensic History & Detection Timeline

ThreatLifecycleTelemetry
This timeline displays historical security and status checkpoints observed by the PhishDestroy automated monitoring network. It records domain lifecycle updates, scanner changes, and threat telemetry over time.
  1. Domain Status Transition 2026-09-10 22:17:32 UTC
    Domain state transitioned from dead to alive.
  2. Domain Status Transition 2026-09-10 22:08:13 UTC
    Domain state transitioned from alive to dead.
  3. VirusTotal Detections Update 2026-09-07 13:06:22 UTC
    VirusTotal scanner detections updated from 16 to 17. Added scanner alerts: OpenPhish.
  4. VirusTotal Detections Update 2026-09-07 12:33:39 UTC
    VirusTotal scanner detections updated from 12 to 16. Added scanner alerts: BitDefender, ESET, Forcepoint ThreatSeeker, Lionic.
  5. VirusTotal Detections Update 2026-09-07 02:08:07 UTC
    VirusTotal scanner detections updated from 10 to 12. Added scanner alerts: CRDF, Gridinsoft.
  6. Threat First Observed 2026-09-07 00:33:54 UTC
    Domain ingestion complete. Initial state is marked as alive pointing to IP 172.67.159.233.

Процес реагування на загрози Pipeline

Відкриття
Analysis
Monitoring

17 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.

Загроза виявлена
aktivasi-fitur-dana2.hint.my.id виявлено та додано до черги для повного аналізу
07.09.2026
URLScan.io Capture
Збережено URLScan report with capture artifacts
07.09.2026
URLScan Verdict
URLScan returned a malicious verdict · score 100
08.09.2026
Cloudflare Radar Report
A stored Cloudflare Radar report is available. The report link alone is not a malicious verdict and does not prove that every network field was captured.
VirusTotal
17/89 recorded on VirusTotal
11.09.2026
CF Radar: Malicious
Cloudflare Radar classified this domain as phishing
Brand Impersonation
Impersonation of Dana
Forensic Evidence Collected
Stored evidence from URLScan.io, stored screenshot
07.09.2026
Technical Analysis Recorded
Звіт містить збережені результати технологічного або криміналістичного аналізу.
08.10.2026
Site Came Back Online
Domain is responding again — monitoring resumed
11.09.2026
Content Observed Unavailable
Моніторинг зафіксував недоступну відповідь; причина не була незалежно встановлена.
11.09.2026
VT Detection +1
+1 new detection (16 → 17): OpenPhish
07.09.2026
VT Detection +4
+4 new detections (12 → 16): BitDefender, ESET, Forcepoint ThreatSeeker, Lionic
07.09.2026
VT Detection +2
+2 new detections (10 → 12): CRDF, Gridinsoft
07.09.2026
Опубліковано список «DestroyList»
07.09.2026
Content Observed Unavailable
Останні збережені перевірки вказують на те, що повідомлений вміст недоступний; це не встановлює, хто або що спричинило зміну.
11.09.2026
Час до першої недоступності
Від виявлення до першого недоступного спостереження минуло 93 годин.
How we investigate & report

Public scans, evidence and abuse channels

We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.

01Public scans & evidence collection10 sources and tool groups
urlscan.io Screenshot · DOM · HTTP

Capture the rendered page, requests and visible infrastructure.

VirusTotal Multi-engine verdicts

Compare the available engine results and retain the analysis timestamp.

Cloudflare Radar DNS · certificates · categories

Inspect a public scan and its recorded network and classification data.

AlienVault OTX Threat-intelligence pulses

Look for indicator references and related community intelligence.

Wayback Machine Historical evidence

Compare archived captures and preserve historical context.

crt.sh Certificate Transparency

Inspect certificate records and related hostnames.

DNS Security Filters Quad9 · AdGuard · CleanBrowsing

Compare security resolver responses and record observed blocking.

Web-Check Surface inspection

Inspect the public DNS, TLS, HTTP and technology surface.

02Abuse reports & follow-upRegistrar, hosting and security channels
  1. Identify the responsible provider. Match registration and hosting records to the relevant abuse contact.
  2. Prepare an evidence package. Include the URL, public scan references, captures and the recorded observations.
  3. Send the report. Keep outgoing report records and recipient information when available.
  4. Recheck and publish updates. Track later scanner verdicts, provider responses and site availability.

Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.

Докази та зовнішні звіти

Глибокий аналіз

Чи вплинув на вас цей сайт?

3 evidence signal groups linked 0 reports recorded Контент недоступний
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Якщо ви ввели облікові дані облікового запису, особисту чи платіжну інформацію або завантажили файл із цього домену, негайно вживіть заходів. Нижче наведено ресурси, які допоможуть вам повідомити про інцидент і захистити себе.

Європол
Знайдіть офіційний канал звітності для вашої країни ЄС
National police directory
Остерігайтеся шахраїв, які обіцяють повернути втрачені кошти! Злочинці можуть знову зв’язатися з жертвами, видаючи себе за слідчих, адвокатів або агентів із відновлення. Не сплачуйте авансових зборів і не діліться обліковими даними. Дізнайтеся більше про шахрайство у сфері відшкодування збитків →

Зверніться до місцевих органів влади

Виберіть свою країну, щоб отримати офіційні контакти кіберзлочинців або створити проект скарги →.

Довідник 97 країн

Template-based draft · optional AI wording assistance requires separate consent

Чернетка за допомогою штучного інтелекту — деталі інциденту обробляються постачальником штучного інтелекту · Перегляньте та подайте його самостійно

Перевірити будь-який домен

Аналіз загроз за допомогою збереженого списку блокувань, WHOIS, DNS і загальнодоступних доказів сканування

Сканувати зараз

Повідомити про фішинг

Додавайте підозрілі домени до нашої бази даних загроз — захищайте спільноту

Повідомити

Потокова стрічка про загрози

Останні звіти про фішинг і помічені зміни доступності

Відстежувати

Будьте в курсі подій, дбайте про свою безпеку

Слідкуйте за актуальними загрозами або оскаржте цей запис, якщо вважаєте, що це помилкова тривога

Потокова стрічка про загрози Оскаржити це оголошення
HTML · IFRAME

Вбудувати цей звіт

Поділіться цією інформацією про загрози на своєму веб-сайті або в блозі

embed.html
<iframe
  src="https://phishdestroy.io/uk/embed/domain/aktivasi-fitur-dana2.hint.my.id"
  title="PhishDestroy threat report for aktivasi-fitur-dana2.hint.my.id"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>