
Здійснюйте пошук серед відстежуваних доменів та переглядайте збережені докази, виявлені випадки та останні дані щодо доступності.
219,813
Загальна кількість відстежених
213,488
Виявлено VT
91,906
Останнє підключення: активний
127,907
Недоступний під час останньої перевірки
563
VT — у процесі розгляду
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Домени
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains

live-morpho.xyz

logixa.ae

luxedrop.pro

mainnetmonad.io

mantra-dex.ink
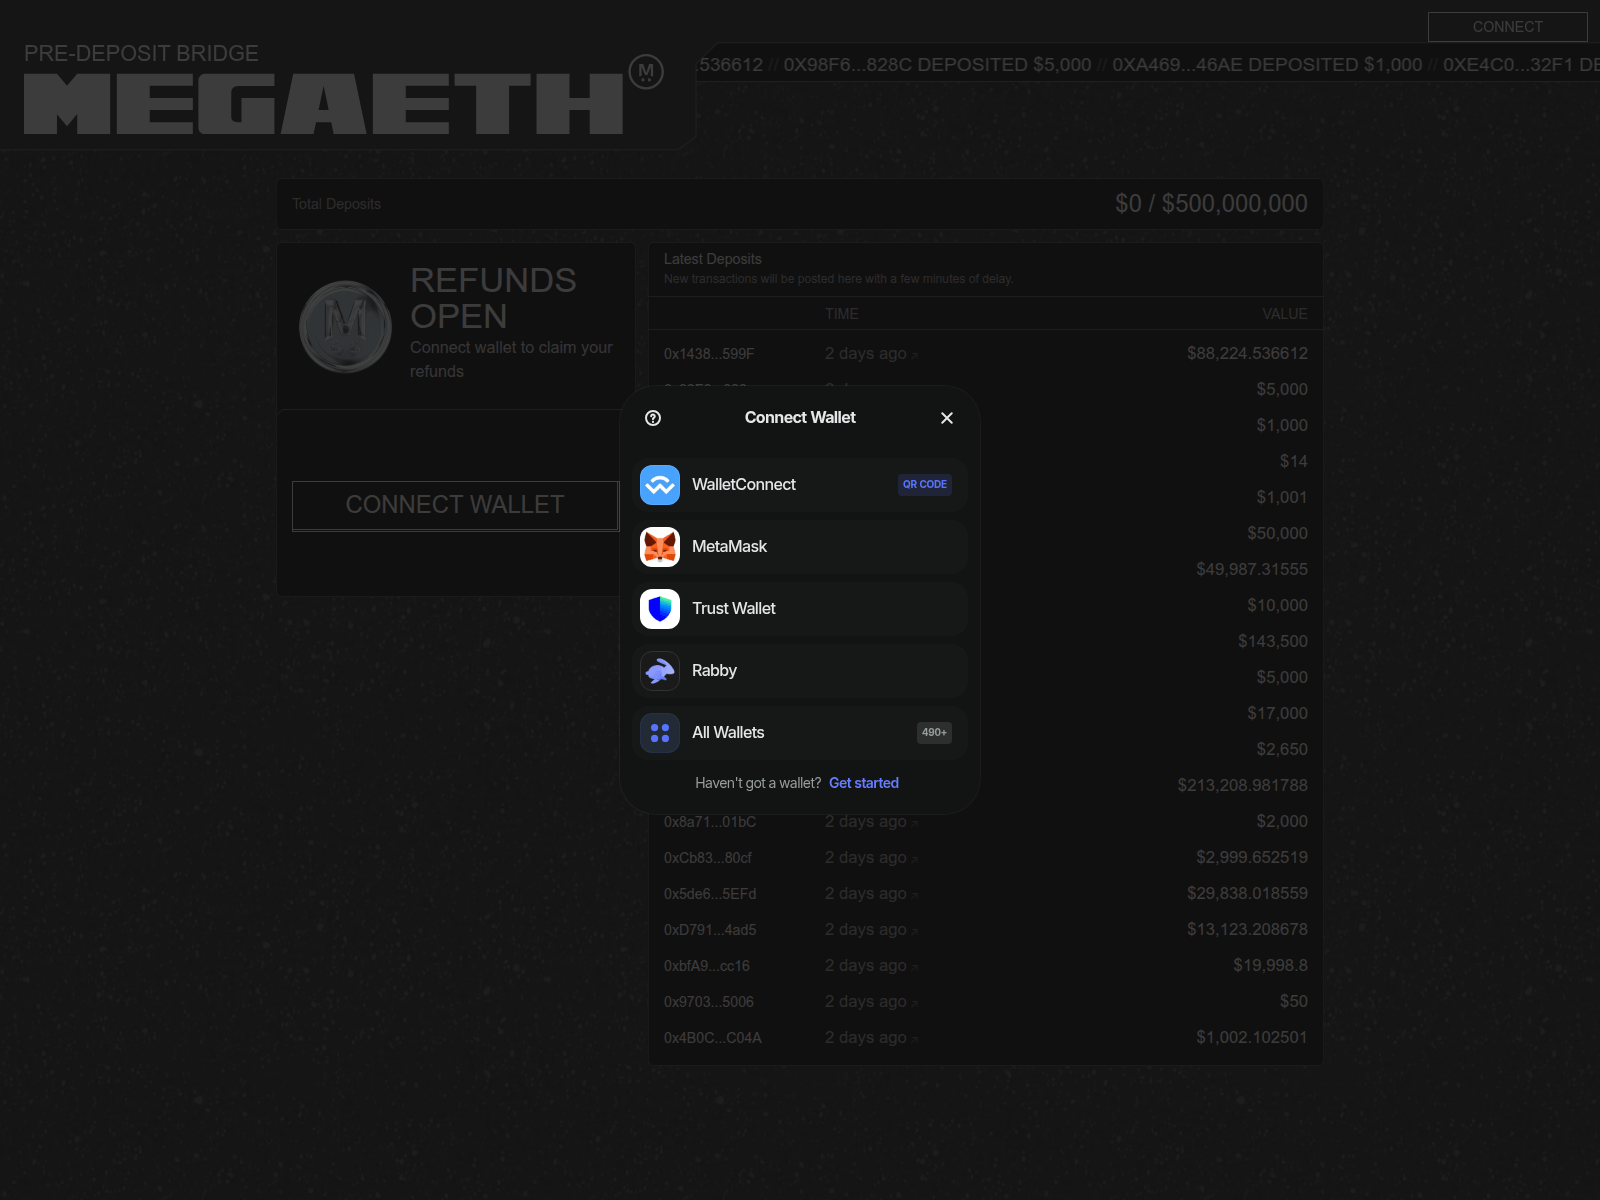
megaeth-refund.xyz

metamask-supported.pages.dev

micdrop-market.io

monad-testnet.icu

monadic-app.xyz

monadplus.xyz

multicoinprotoco.app

noox.global

nooxdao.net

nooxdao.pro

nooxlabs.net

oracle-eligibility.com

pan-swaps.pro

pancakeswap.xn--financeswap-0t4j.0x4e15361fd6b4bb609fa63c81a2be19d873717870.link
paralogixy.com

paxosgift.com

perceptron-network.xyz

peth.top

plasmachecks.com

polysniper.fun
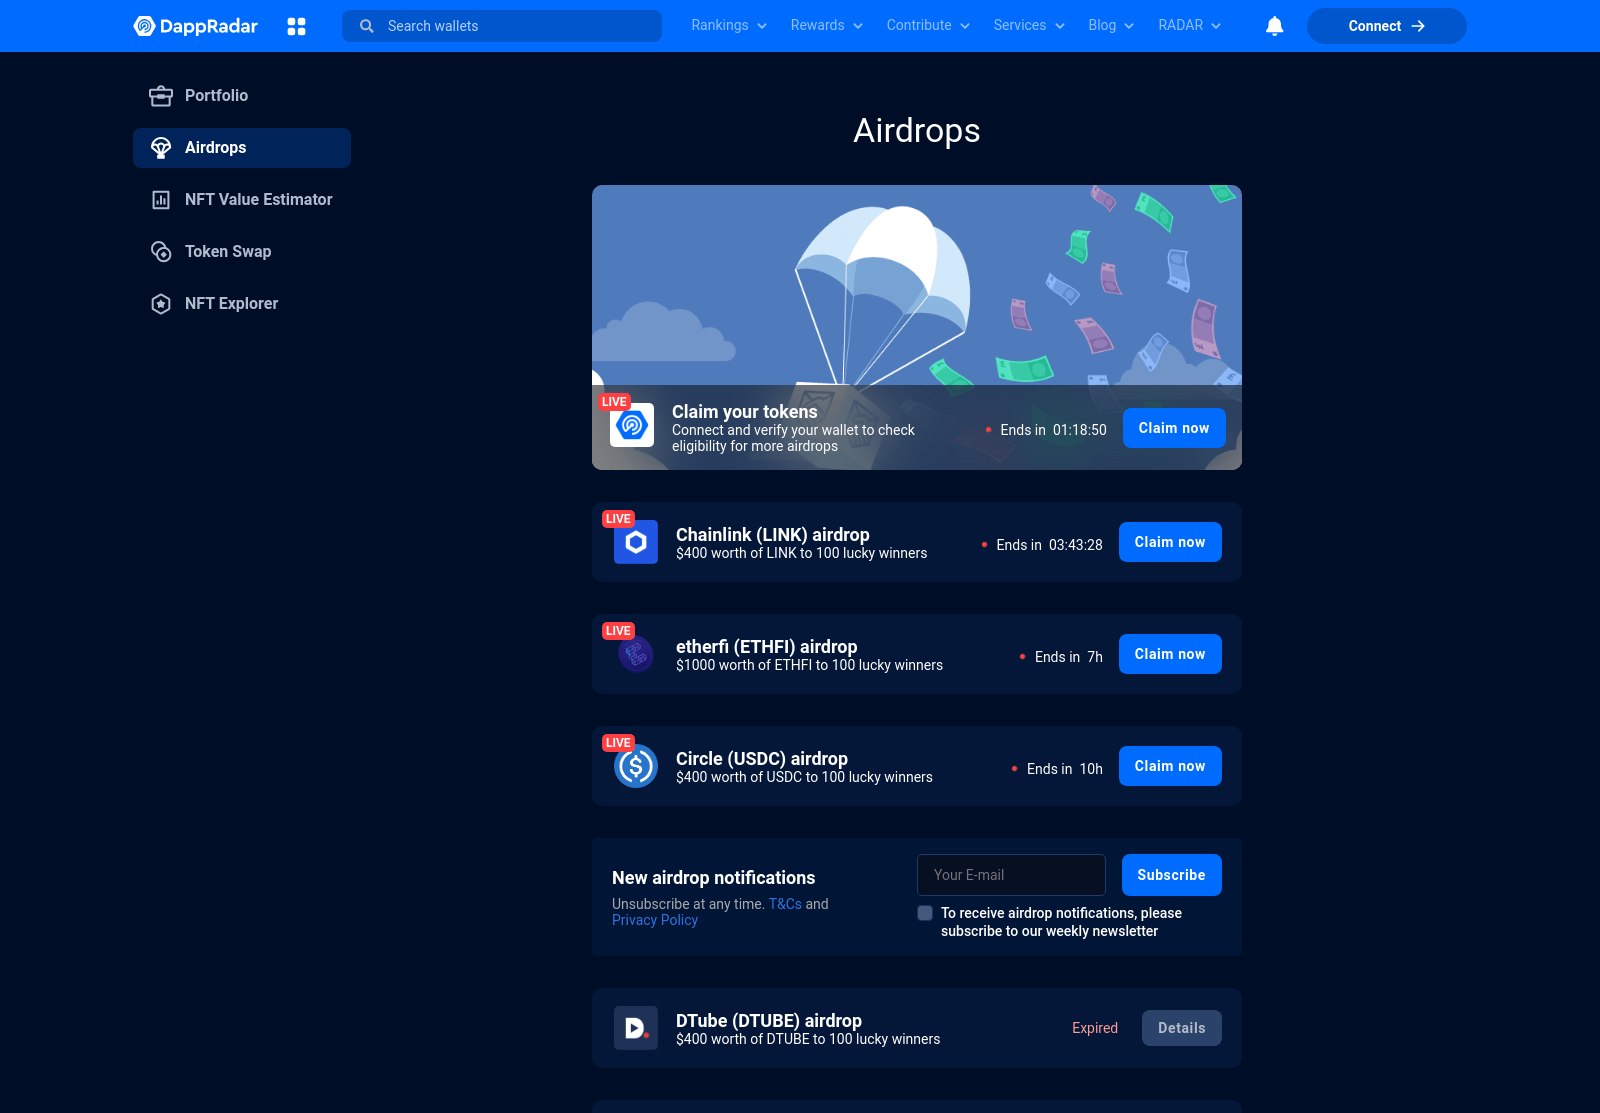
pub-d2815d99eef1471eb19512b2562cb1f8.r2.dev

radar-dapp.dev
raiydum.cfd
remittix.foundation

retikclaim.web.app

reward-lidoxp.org

safeearn.app
sol-claims.com
soniclabs-network.web.app

sundaeswap.org
sw-ae.com


tokens-alloca.org

tornado-cash.co

trendsfun-git-feature-new-12-api-takoprotocol.vercel.app

u103.ucdc2233.xyz

uk099.top

uniswap-airdrop.pages.dev

walletconnect-final-test-airdrop.web3-openhub.com

walletconnector.cc
web-git-develop.pancake.run

web.bp-nxbd.com

web.im.token-app.ac

wlfecoclaim.com

worldlibertyficlaim.xyz
wormhole.today

xplclaimlive.xyz

yields-basis.com

yieldusd-app.com

yqiiai.pages.dev

zcoinlab.com

aboreon.finance
access-asterdex.com

address-analyse.com

aml-verification.cfd

aml.lat

app-etc.net

asterdex-s2.com

bimodal-oxeliteoriginator.firebaseapp.com

blockchaindapp.site

bnb-4.vip

bnb6844.com
bnb6888.com

bob-mainnet-5i9u3edtb-distributed-crafts.vercel.app

centralchain-elitebridge.firebaseapp.com

chain-validation.pages.dev

claim-airdrop-5mm.pages.dev

claim-humidifi.org

claim-met.site

claimairdropfree.biz
claims-tradetomato.pages.dev

croc.finance

dasdas.elysium-drainer.world

duplicate-disabled-3213.invalid

duplicate-disabled-7462.invalid

eligibility-cysic.org

eligibility-humidifi.org
eligibility-ofc.app

eligibility-stable.org

eth-mining-global.top
everythinghere.co.za

fcgffd.cc
fkbtff.cc

fpmifp.cc

fprcfo.cc
fukzfb.cc
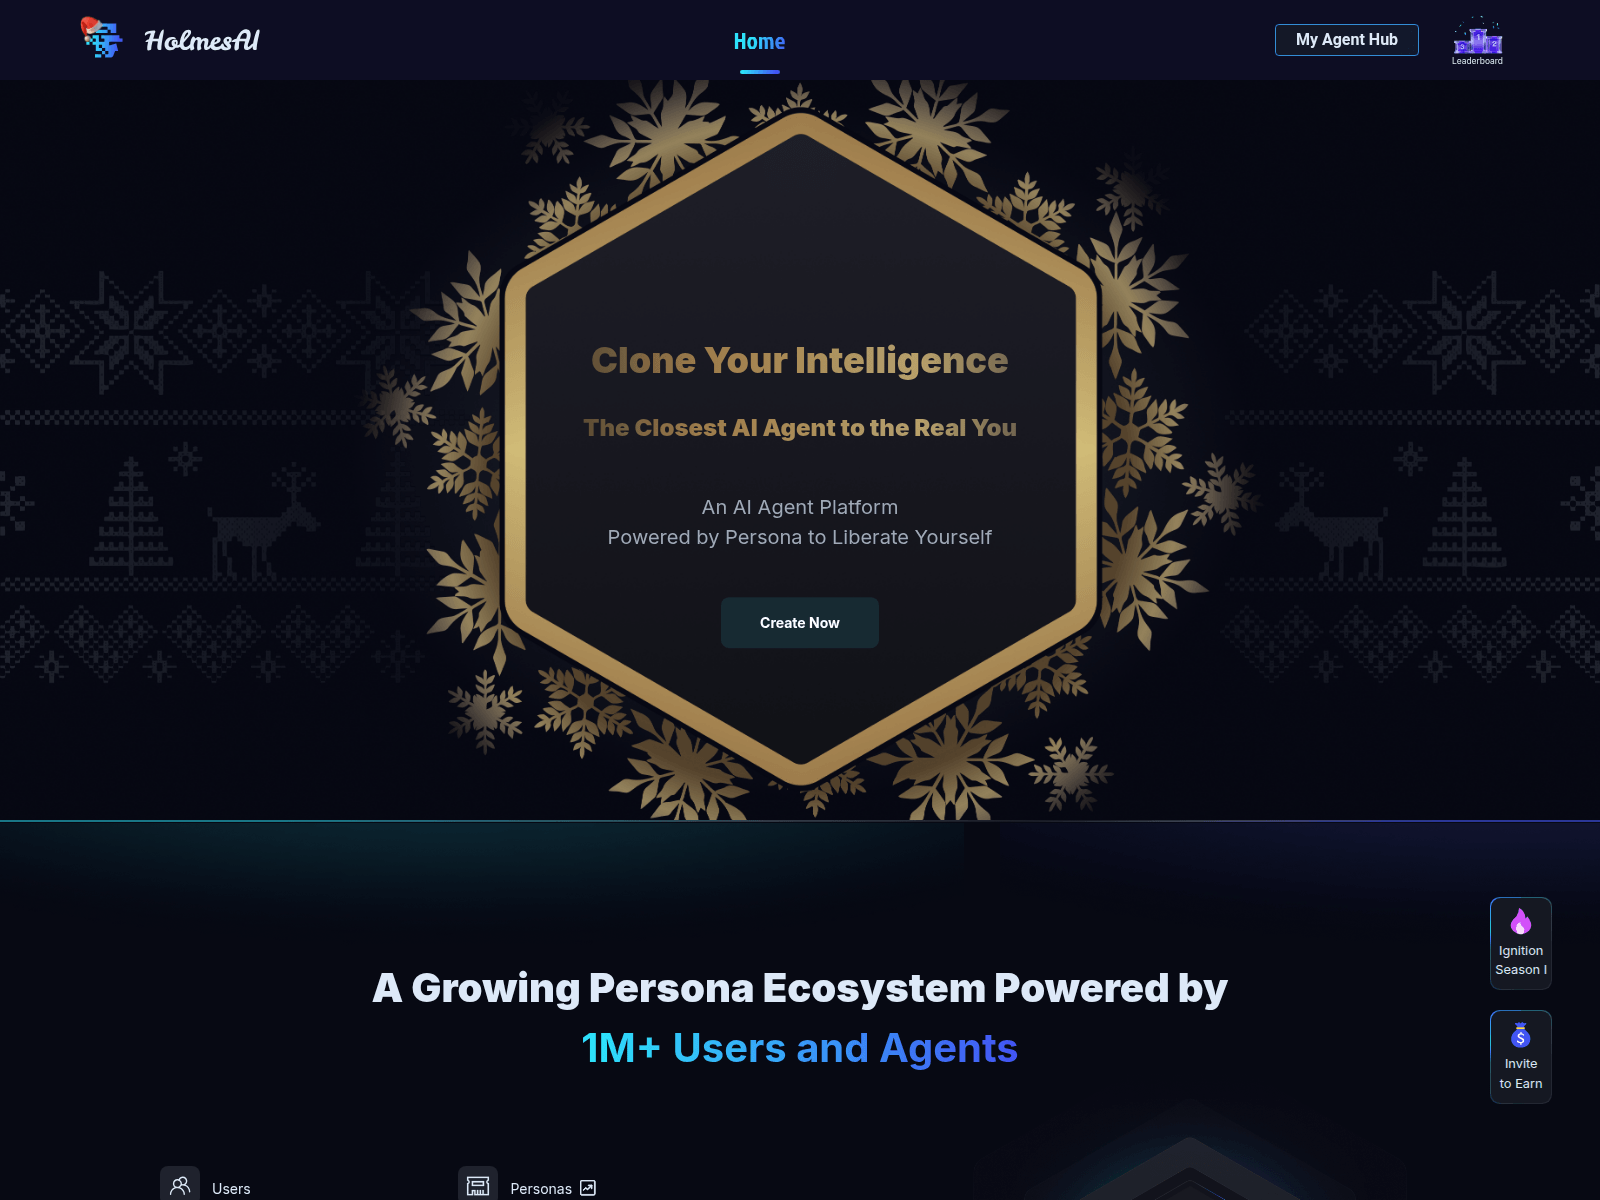
hoimesai.xyz

houdiniswsp.com

hyperappy.com

hypertliquid.com

kinetiqs-market.xyz

lab-airdrop.xyz

layer3-app.com

layer3-dapp.com
Процес реагування на загрози Pipeline
Як перевіряється кожен домен у цьому хабі та як нейтралізуються підтверджені загрози. Повна візуалізація технологічного процесу →
Перевірки даних про загрози— кожен домен проходить сканування та перехресну перевірку щодо:
urlscan.ioЗнімок екрана · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency ЗвітCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Безпека FiltersQuad9 · AdGuard · CleanBrowsingWeb-ПеревіритиFull surface scan
 crt.sh
Глобальна синхронізація постачальників— підтверджені випадки передаються 29 партнерам:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecОгляд сайтуAviraCloud detectionAvast / AVGWeb Shield«Касперський»OpenTIPDr.WebOnline scannerNetcraftЛіквідація APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.ЗвітHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust