VirusTotal
0 / 92 engine detections
Raporu aç

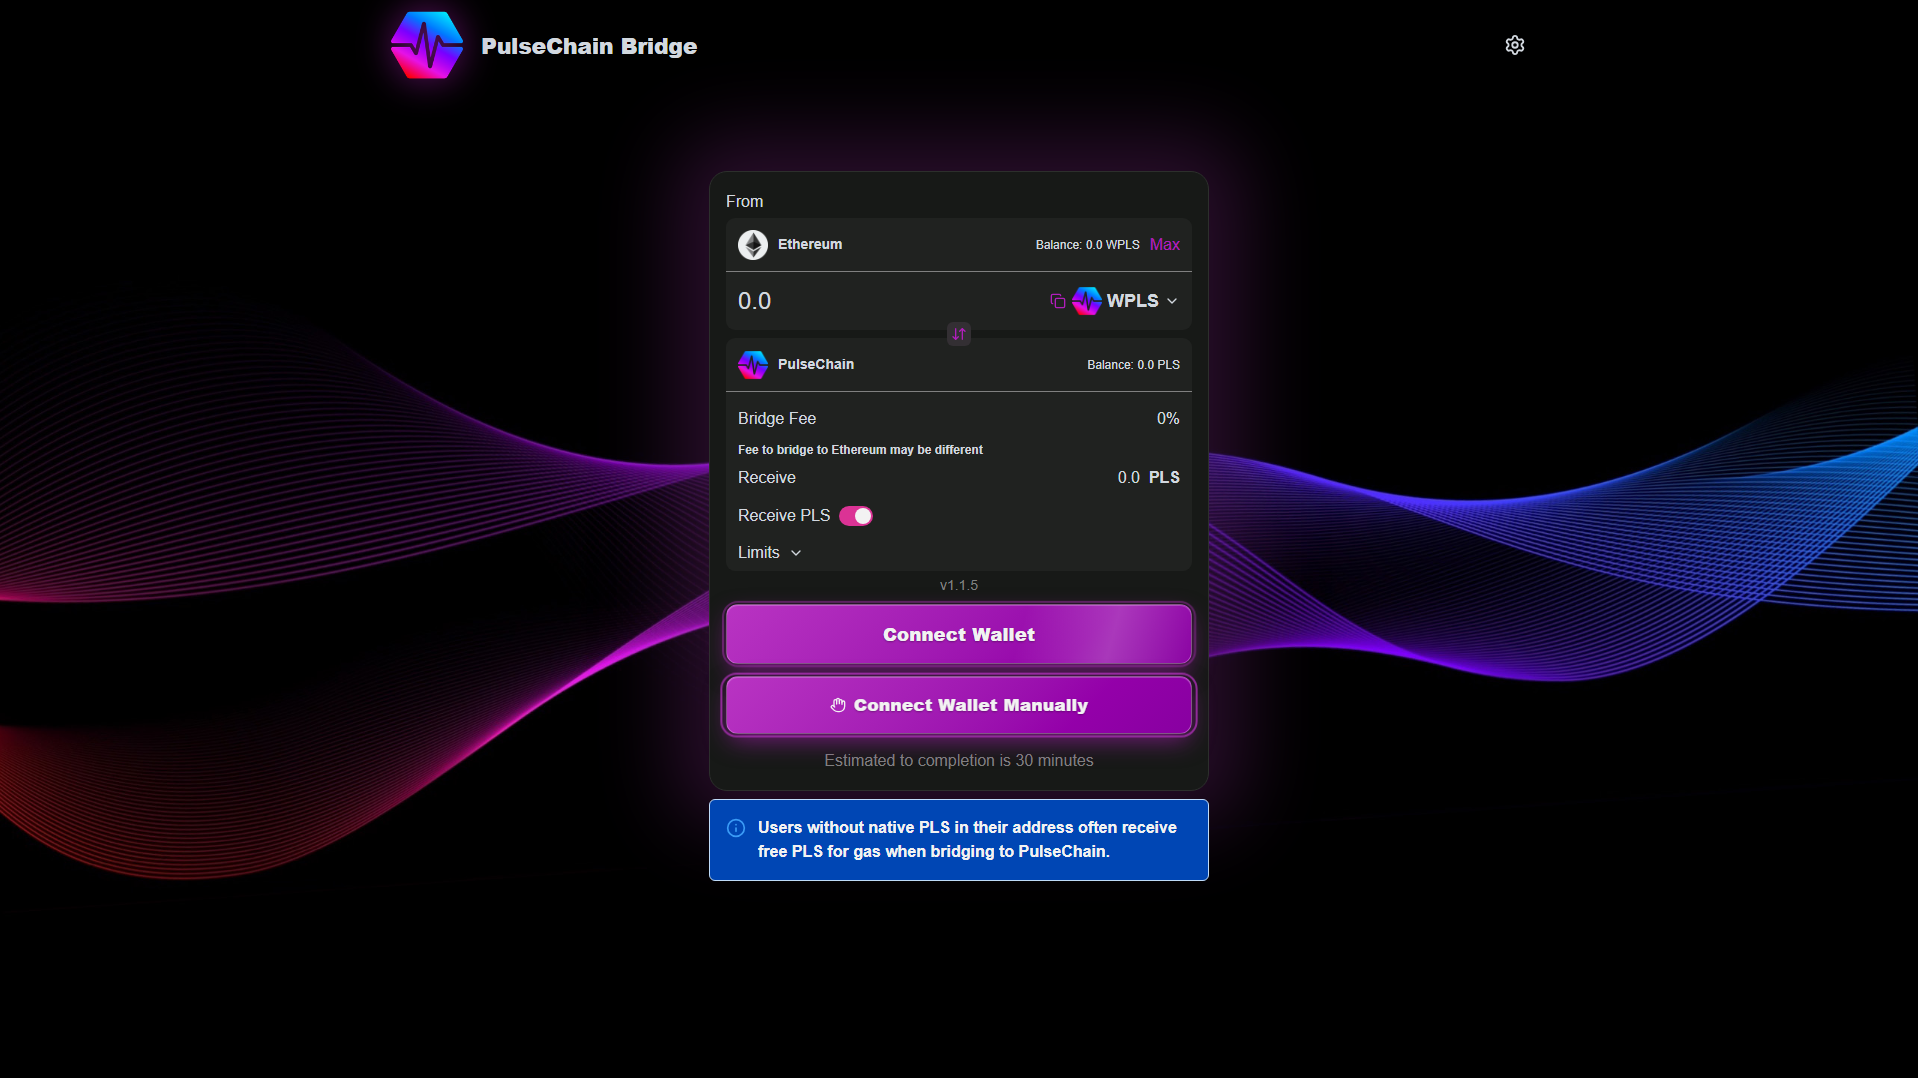
“PulseChain Bridge”
Ethereum taklidi: bridge-pulsechains.com — Doğrulanmamış. Kanıt özeti: VirusTotal 0/92; URLScan capture; PhishDestroy score 45/100. Kayıt kuruluşu: NiceNIC.
Özgün adli kaydı korumak için aşağıdaki ayrıntılı PhishDestroy AI analizi İngilizce bırakılmıştır.
0 / 92 engine detections
Raporu aç3 community references
Raporu açScan report
Raporu açNo threat flag
Raporu açPage capture
Raporu açResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
PhishDestroy has added bridge-pulsechains.com to its internal blocklist as a suspicious domain. The site’s recorded title is “PulseChain Bridge.” The domain was first seen by PhishDestroy on 2026-10-20.
Because the domain is flagged without a concrete scheme, there is no evidence of a particular fraud technique such as phishing, wallet draining, or a fake exchange. Suspicious domains may attempt to trick users into providing credentials, approving transactions, or downloading malicious content, but none of those behaviors were observed on this page.
VirusTotal scanned the URL on 2026-10-15 and reported 0 detections from 92 engines; the result was retrieved on 2026-10-20. Google Safe Browsing checked on 2026-10-20 and did not flag the site. No external blocklists listed the domain as of 2026-10-20, while PhishDestroy’s internal list marked it as suspicious on that same date. Open Threat Exchange recorded three pulses referencing the domain on 2026-10-20.
The domain was registered on 2026-10-15 through NICENIC INTERNATIONAL GROUP CO., LIMITED. DNS resolution at the time of capture pointed to 104.21.71.29, which belongs to Cloudflare’s AS13335 network in the United States.
Visitors should not enter any credentials, private keys or approve blockchain transactions on this site; if they have already done so, they should treat any associated accounts as compromised and follow standard recovery procedures. Organizations should add bridge-pulsechains.com to their deny lists, review access logs for requests to the recorded IP, and monitor for related activity.
 (RU)
PhishDestroy Investigation
Edge-IP itibarı bu etki alanıyla ilişkilendirilmez.
anahi.ns.cloudflare.comdarl.ns.cloudflare.comLocation describes the IP network.
Google PageSpeed Insights — mobile performance audit of bridge-pulsechains.com · checked Oct 20, 2026
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Erişilebilir
3 community references
View sourceNo threat flag
View source0/92 engine detections
View sourcebridge-pulsechains.com
View sourcePage captured
View source52 kayıtlı benzer alan adı
Aynı kayıt kuruluşu aracılığıyla kaydedilmiştir. Bir kayıt kuruluşu, birbiriyle hiçbir bağlantısı olmayan milyonlarca müşteriye hizmet verdiğinden, bu durum bir bağlantıyı kanıtlamaktan ziyade raporları bir araya getirmektedir.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
bridge-pulsechains.com
Listed domains receive at least one abuse report; this entry has no retained notification history.
Hesap kimlik bilgilerini, kişisel bilgileri veya ödeme bilgilerini girdiyseniz ya da bu alan adından bir dosya indirdiyseniz hemen harekete geçin. Aşağıda olayı bildirmenize ve kendinizi korumanıza yardımcı olacak kaynaklar bulunmaktadır.


resmi siber suç iletişim bilgileri veya şikayet taslağı oluştur → almak için ülkenizi seçin.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
bridge-pulsechains.com)Tüm ayrıntıları bilmeseniz bile — yine de şikayette bulun. Kısmi bilgiler de soruşturmalara yardımcı olmaktadır.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Saklanan engelleme listesi, WHOIS, DNS ve genel tarama kanıtlarını kullanarak tehdit analizi
Şimdi TaraŞüpheli alan adlarını tehdit veritabanımıza bildirin — topluluğu koruyun
BildirSon kimlik avı raporları ve gözlemlenen kullanılabilirlik değişiklikleri
İzleCanlı tehditleri izleyin veya bunun yanlış bir uyarı olduğunu düşünüyorsanız bu kayda itiraz edin
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.