VirusTotal
14 / 91
Сообщить


“halal-treasured.org”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@pir.org.
The latest stored availability evidence still shows the domain reachable; 2 months has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
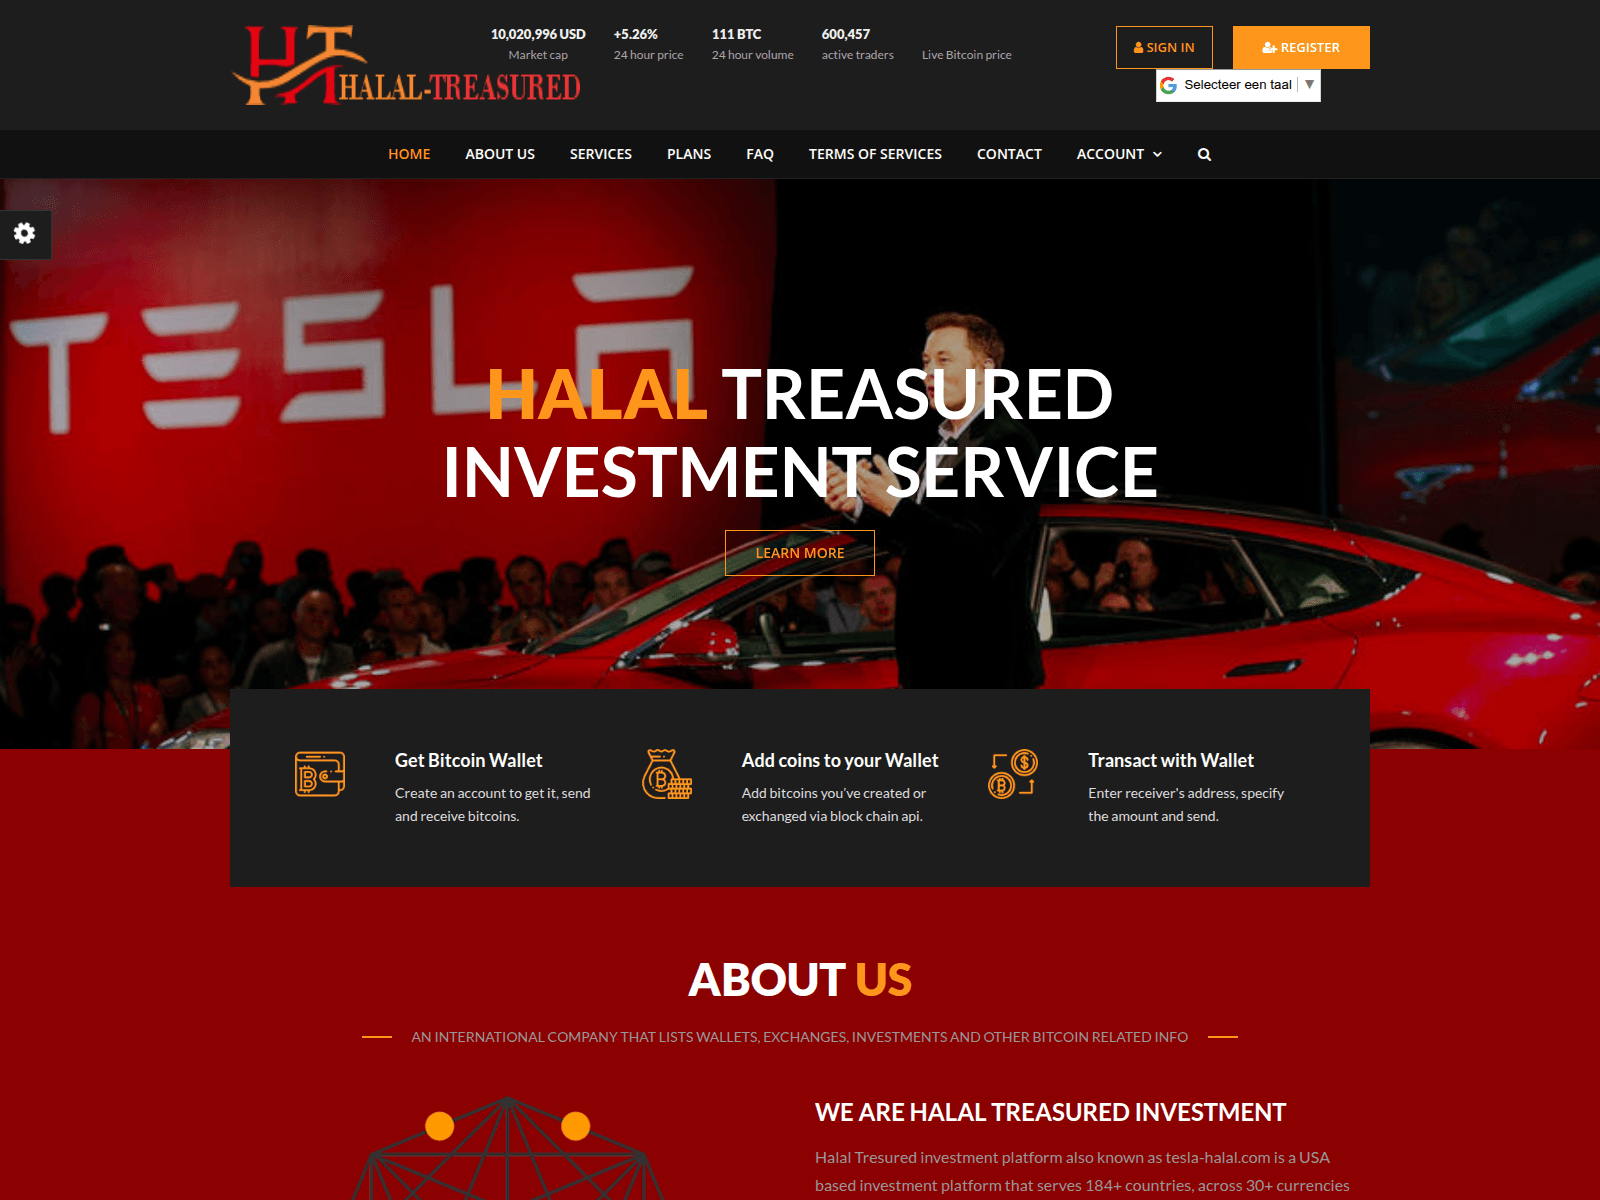
halal-treasured.org — Непроверенный. Олицетворение бренда: Cryptoscam; Тип мошенничества: Impersonation. Сводка доказательств: VirusTotal 14/91 (alphaMountain.ai, BitDefender, CRDF, ESET, Fortinet); URLScan malicious verdict; Spamhaus DBL_SPAM; PhishDestroy score 98/100. Регистратор: NameSilo.
Подробный анализ PhishDestroy AI ниже оставлен на английском, чтобы сохранить исходную криминалистическую запись.

14 / 91
malicious
СообщитьDBL_SPAM
Report stored; detailed verdict not recorded
Сообщить5 community references
Сообщитьprovider verdict: suspicious
Сообщитьсохраненный отчет
 Сообщить
Checked; no threat flag recorded
СообщитьAnalysis of the domain halal-treasured.org, created on August 21, 2025 and registered through NameSilo, LLC, shows it is currently active and resolves to the IPv4 address 5.196.175.67. The domain is listed on a single security blocklist and has been explicitly blocked by the PhishDestroy service, indicating that at least one anti‑phishing platform has identified malicious activity associated with this host. VirusTotal has recorded 15 detections out of 91 scanned security vendors, reinforcing the suspicion that the domain is being used for abusive purposes.
The authoritative name servers are ns3.ddoscure.com, ns4.ddoscure.com, ns5.ddoscure.com, and ns6.ddoscure.com, which are not typical of reputable hosting providers and may be part of a shared malicious infrastructure. No public evidence has been released regarding SSL certificate details, HTTP response codes, Safe Browsing status, Open Threat Exchange (OTX) mentions, or page title content, so the surface‑web characteristics of the site remain unverified. Given the combination of registrar information, recent creation date, blocklist presence, multiple vendor detections, and the fact that PhishDestroy has taken active mitigation steps, defenders should treat halal-treasured.org as a high‑risk phishing indicator.
Recommended actions include adding the domain to internal blocklists, monitoring DNS queries for the associated IP address, and employing URL filtering to prevent user access. Continuous re‑evaluation is advised, as additional threat‑intel feeds may provide further context on the hosting environment or payloads delivered by the domain.
Сохраненные данные сравнения данных сканера и браузера для данного хоста, а также проверка отпечатков в режиме реального времени для систем распределения трафика типа «Кейтаро».
Примечание к сканированию: unavailable: raw=connection_error; http=0; via=http_proxy; error=SOCKSHTTPConnectionPool(host='halal-treasured.org', port=80): Max retries exceeded with url: / (Caused by NewConnectionE
ns3.ddoscure.comns4.ddoscure.comns5.ddoscure.comns6.ddoscure.commail.halal-treasured.orgpriority 10Location describes the IP network.
4b5c1b0962608e82cd24b77aee59a62361893491a8a4aa91667bf80695b07b6bftp.halal-treasured.orgmail.halal-treasured.orgpop.halal-treasured.orgsmtp.halal-treasured.orgwww.halal-treasured.orgSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of halal-treasured.org · checked Jul 27, 2026
5.196.175.67. 14 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
5 сообщений сообщества
КатегорияOTHER_INVESTMENT_SCAM
Data submited by Intelligence for good
PD-20260727-0B1AEE Recipient: abuse@pir.org Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Если вы ввели учетные данные, личную или платежную информацию или загрузили файл с этого домена, примите немедленные меры. Ниже приведены ресурсы, которые помогут вам сообщить об инциденте и защитить себя.


Выберите свою страну, чтобы получить официальные контакты по киберпреступности или создать проект жалобы →.
Template-based draft · optional AI wording assistance requires separate consent
Каждая полоса — это одна из причин, по которой домен связан с этим хостом. Размер узла обозначает обнаружения VirusTotal, а пунктирные узлы уже находятся в автономном режиме. Полные списки приведены ниже.
На этом исходном IP-адресе размещено несколько фишинговых доменов — инфраструктура может использоваться в разных кампаниях.
Эти домены также нацелены на пользователей сайта Cryptoscam. Просмотреть все угрозы, связанные с «Cryptoscam» →
Зарегистрированы через одного и того же регистратора. Регистратор обслуживает миллионы клиентов, не связанных друг с другом, поэтому данный факт скорее свидетельствует о сходстве данных, чем доказывает наличие связи.
Недавно добавленные отчёты об угрозах. Эти ссылки не означают общую инфраструктуру или одного владельца.
Анализ угроз с использованием сохраненного черного списка, WHOIS, DNS и общедоступных доказательств сканирования.
Сканировать сейчасДобавляйте подозрительные домены в нашу базу данных угроз — защищайте сообщество
СообщитьНедавние сообщения о фишинге и наблюдаемые изменения доступности
ОтслеживатьОтслеживайте актуальные угрозы или оспорьте эту запись, если считаете, что это ложное срабатывание







