Cloudflare Radar
Suspicious
Abrir relatório
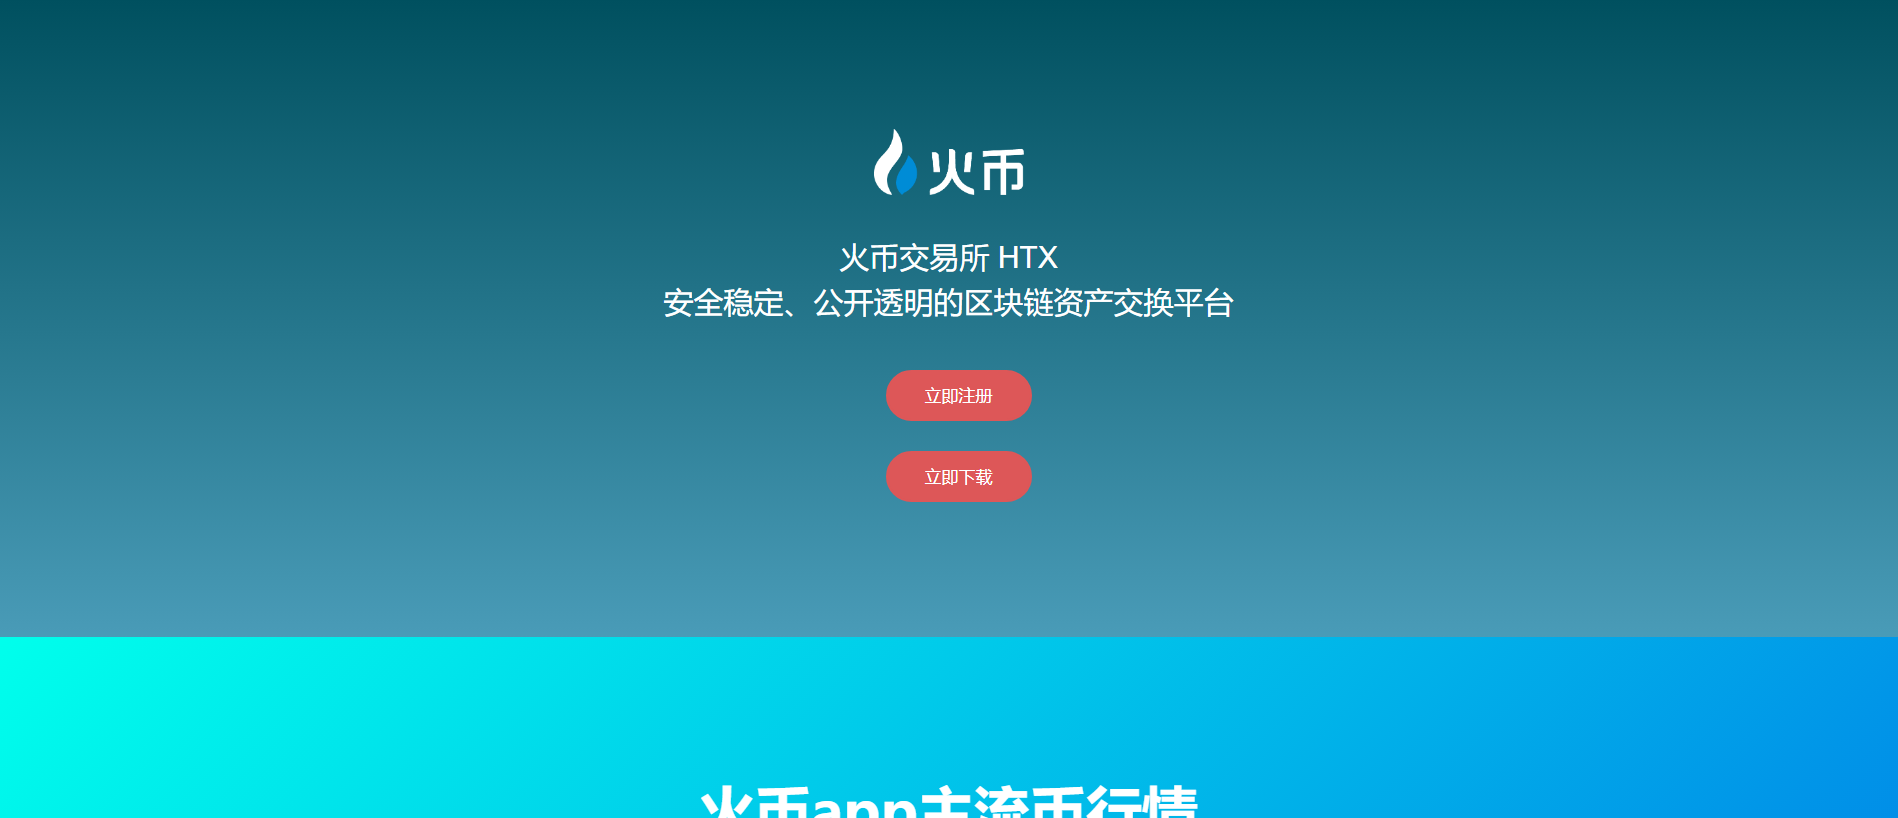
“火币 | HTX官网 | 火币官网下载 | 火币HTX官方下载”
guanwang-huobi.com.cn — Não verificado. Representação da marca: Htx; Tipo de golpe: Impersonation. Resumo das evidências: VirusTotal 0/92; 2 external blocklist matches (MetaMask, SEAL); PhishDestroy score 85/100. Registrador: 北京新网数码信息技术有限公司.
A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.
Suspicious
Abrir relatório0 / 92 engine detections
Abrir relatórioScan report
Abrir relatório4 community references
Abrir relatórioNo threat flag
Abrir relatórioNo malicious flag
Abrir relatórioResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
AI-assisted evidence review
This domain presents itself as the official HTX (Huobi) website, using the Chinese title '火币 | HTX官网 | 火币官网下载 | 火币HTX官方下载' to appear legitimate. PhishDestroy first observed guanwang-huobi.com.cn on 2026-10-19. The site is currently marked as unreachable, yet remains hosted and registered. The page title suggests an HTX impersonation, which conflicts with the suspicious classification from independent sources.
The site uses HTX branding to deceive visitors into believing it is the genuine exchange or its official download portal. Victims risk entering login credentials, downloading malicious software, or connecting wallets to a fake interface. Once credentials are captured or wallet connections approved, attackers can drain funds or take over accounts. Even if the page is unreachable now, prior availability could have enabled theft.
VirusTotal flagged the domain with 0 detections out of 92 engines on 2026-10-19. It is listed on PhishDestroy, MetaMask, and SEAL blocklists, and referenced in 4 OTX pulses. The low detection rate suggests the site may employ evasion tactics or is newly active, but multiple reputable blocklists independently classify it as suspicious.
The domain was registered on 2026-09-20 via 北京新网数码信息技术有限公司. It resolves to IP 154.216.69.157, hosted on a network associated with this address.
Anyone who visited guanwang-huobi.com.cn should assume credentials or wallet connections may have been compromised. Revoke any HTX-related API keys or wallet approvals immediately and change passwords elsewhere using a separate device. Defenders should block the domain and IP at the network level and alert users to avoid interacting with it. Report the domain to HTX support and relevant blocklist teams if not already listed.
urlscan.io scan and screenshot: https://urlscan.io/result/01a151ce-1086-713c-8c62-b374b0f47e27/
VirusTotal report: https://www.virustotal.com/gui/domain/guanwang-huobi.com.cn
Google Safe Browsing status: https://transparencyreport.google.com/safe-browsing/search?url=guanwang-huobi.com.cn
Report phishing to Google: https://safebrowsing.google.com/safebrowsing/report_phish/
Site owner? Request a review: https://phishdestroy.io/appeals/
Last checked
ns1.myhostadmin.netns2.myhostadmin.netns5.west.cnns6.west.cnLocation describes the IP network.
b35f747890fbcbf8d7f5165ab5ce3cc39b0d22a3d4bb5d7693181128cb39b247Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of guanwang-huobi.com.cn · checked Oct 19, 2026
Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.
http://guanwang-huobi.com.cn/Server: nginxContent-Type: text/html; charset=UTF-8Content-Encoding: gzip0374eaa25e3bb6d3bb07d8ad736a2a7b919cf991923c47c645a604104cc42286quic=":443"; h3=":443"; h3-29=":443"; h3-27=":443";h3-25=":443"; h3-T050=":443"; h3-Q050=":443";h3-Q049=":443";h3-Q048=":443"; h3-Q046=":443"; h3-Q043=":443"keep-alivegziptext/html; charset=UTF-8Mon, 19 Oct 2026 01:45:44 GMTnginxmax-age=31536000chunkedAccept-EncodingValues retained by the collector; long values may be shortened during collection.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Acessível
4 community references
View sourceNo threat flag
View source0/92 engine detections
View sourcePD-20261019-FDBA94
guanwang-huobi.com.cn
View sourcePage captured
View sourceRegistrados pelo mesmo registrador. Um registrador atende a milhões de clientes sem qualquer relação entre si; portanto, isso apenas agrupa os registros, em vez de comprovar uma ligação.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
guanwang-huobi.com.cn
PD-20261019-FDBA94 Recipient: 609042020@qq.com Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.


Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
guanwang-huobi.com.cn)Mesmo que você não tenha todos os detalhes — registre uma ocorrência mesmo assim. Mesmo informações parciais ainda ajudam nas investigações.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análise de ameaças usando lista de bloqueio armazenada, WHOIS, DNS e evidências de verificação pública
Digitalize agoraEnvie domínios suspeitos para nosso banco de dados de ameaças — proteja a comunidade
DenunciarRelatórios recentes de phishing e alterações de disponibilidade observadas
MonitorarMonitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.