VirusTotal
7 / 92 engine detections
Abrir relatório

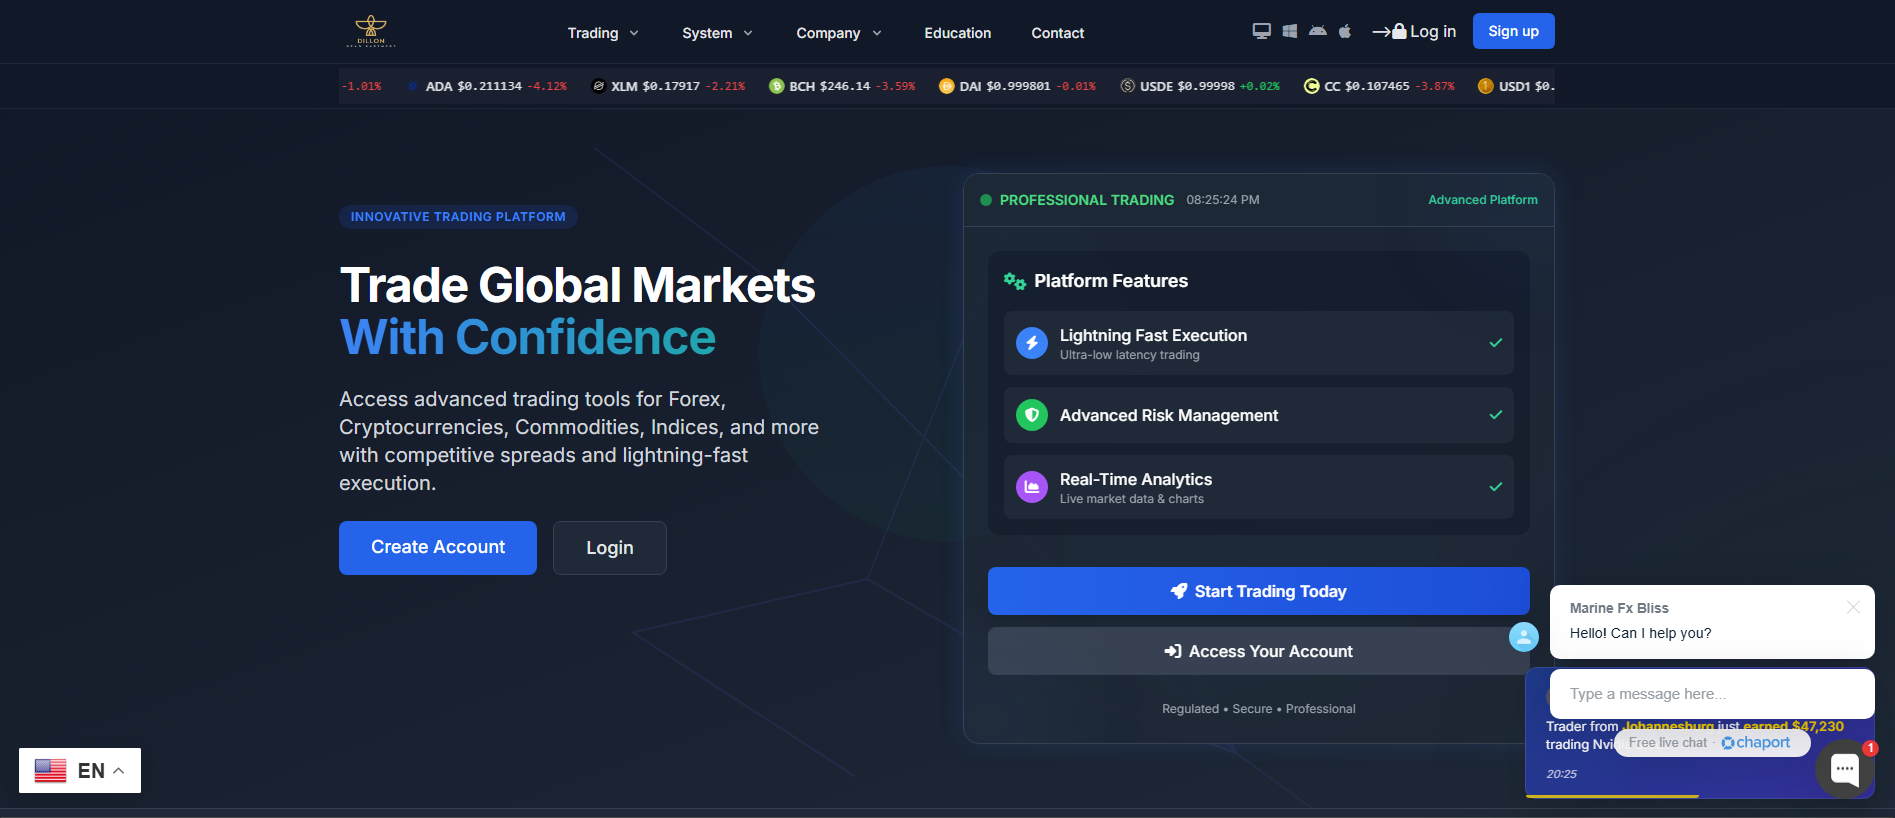
“Dillon Read Partner | CFD Trading — Trading on Stocks, Gold, Oil, Indices”
Phishing: dillonreadpartners.com — Último ativo conhecido (HTTP 200). Resumo das evidências: VirusTotal 7/92 (alphaMountain.ai, CRDF, Forcepoint ThreatSeeker…
A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.
7 / 92 engine detections
Abrir relatórioDBL_SPAM
Malicioso
Abrir relatório7 community references
Abrir relatórioprovider verdict: clean
Abrir relatórioNo threat flag
Abrir relatórioResults reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.
PhishDestroy threat report
dillonreadpartners.com presents itself as "Dillon Read Partner," a CFD trading platform offering stocks, gold, oil and indices. It borrows the Dillon Read name to look like an established financial firm and targets retail investors looking for leveraged trading. PhishDestroy classifies it as an impersonation phishing page and first flagged it on 2026-09-05. As of 2026-10-19 the site was still online and serving its content.
Fake CFD brokers like this one sell an image of credibility: a recognizable firm name, a polished trading dashboard and promises of easy access to commodities and indices. Victims are typically asked to register, hand over identity details and fund an account, and are often steered by a so-called account manager toward larger deposits. The balances shown on screen are not backed by real trades. When a victim tries to withdraw, new taxes, fees or verification charges appear, and the money already sent is lost along with any personal documents uploaded.
Seven of 92 VirusTotal engines flagged the domain: alphaMountain.ai, CRDF, Forcepoint ThreatSeeker, Fortinet, Gridinsoft, Netcraft and SOCRadar. That count is modest, but these vendors include several that specialise in fraud and phishing. urlscan.io returned a malicious verdict and matched the page to a generic scam pattern. Spamhaus lists the domain in its DBL as spam, and it appears in seven AlienVault OTX threat pulses, which shows other researchers have tracked it independently.
The domain was registered on 2026-05-08 through Fewmoretaps OU, which does business as Trustname.com, about four months before PhishDestroy detected it. That gap suggests the site was set up ahead of time and kept running long enough to build a track record before it drew scrutiny. It runs on Contabo GmbH infrastructure in France, a common choice for low-cost virtual servers.
Do not deposit money and do not pay any "withdrawal fee," tax or unlock charge. Paying more will not release a balance. If you already sent funds, contact your bank or card issuer right away to attempt a chargeback or recall, keep every receipt and chat log, and report the loss to your national fraud authority. If you uploaded ID documents, watch for identity misuse, and be wary of "recovery" services that promise to get your money back for an upfront fee. Defenders should block the domain at DNS and proxy level and add it to filters for investment-fraud lures.
 (BY)
PhishDestroy Investigation
lisa.ns.cloudflare.comrick.ns.cloudflare.commail.dillonreadpartners.compriority 10Location describes the IP network.
45a2d95c79bb54ecb9ceb7aecd0dc06b3c914891df905d1d1aad83826a7440fdSaved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.
Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Desconhecido→live_content
content_served
Acessível
7/92 engine detections
View source7 community references
View sourceNo threat flag
View sourcedillonreadpartners.com
View sourcePage captured
View source203 domínios semelhantes armazenados
Exibindo 100 de 203
Cada faixa representa um motivo pelo qual um domínio está vinculado a este host. O tamanho dos nós indica as detecções do VirusTotal, e os nós tracejados já estão offline. As listas completas seguem abaixo.
Este IP de origem hospeda vários domínios de phishing — a infraestrutura pode ser compartilhada entre campanhas.
Registrados pelo mesmo registrador. Um registrador atende a milhões de clientes sem qualquer relação entre si; portanto, isso apenas agrupa os registros, em vez de comprovar uma ligação.
Compare what a browser and a crawler receive, and check for Keitaro traffic routing.
dillonreadpartners.com
Listed domains receive at least one abuse report; this entry has no retained notification history.
Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.


Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.
Template-based draft · optional AI wording assistance requires separate consent
Choose the steps that match what you shared. Keep a copy of this report alongside your own records.
Stop using the suspicious site. Open the real service through its official app or an address you already trust.
Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗
dillonreadpartners.com)Mesmo que você não tenha todos os detalhes — registre uma ocorrência mesmo assim. Mesmo informações parciais ainda ajudam nas investigações.
A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
Análise de ameaças usando lista de bloqueio armazenada, WHOIS, DNS e evidências de verificação pública
Digitalize agoraEnvie domínios suspeitos para nosso banco de dados de ameaças — proteja a comunidade
DenunciarRelatórios recentes de phishing e alterações de disponibilidade observadas
MonitorarMonitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo
This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.
The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.
A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.