VirusTotal
10 / 89
Denunciar


“Adelyn Rae | Adelyn Rae”
The sent-report ledger records the first outgoing report at .
The recorded recipient is abuse@rashost.com.
The latest stored availability evidence still shows the domain reachable; 1 month has elapsed since the first outgoing report.
ICANN RAA §3.18 describes registrar abuse-contact and handling obligations. This section records outgoing timestamps, listed recipients, case identifiers, and later availability. It does not by itself prove receipt, acknowledgement, investigation, remediation, or contractual non-compliance.
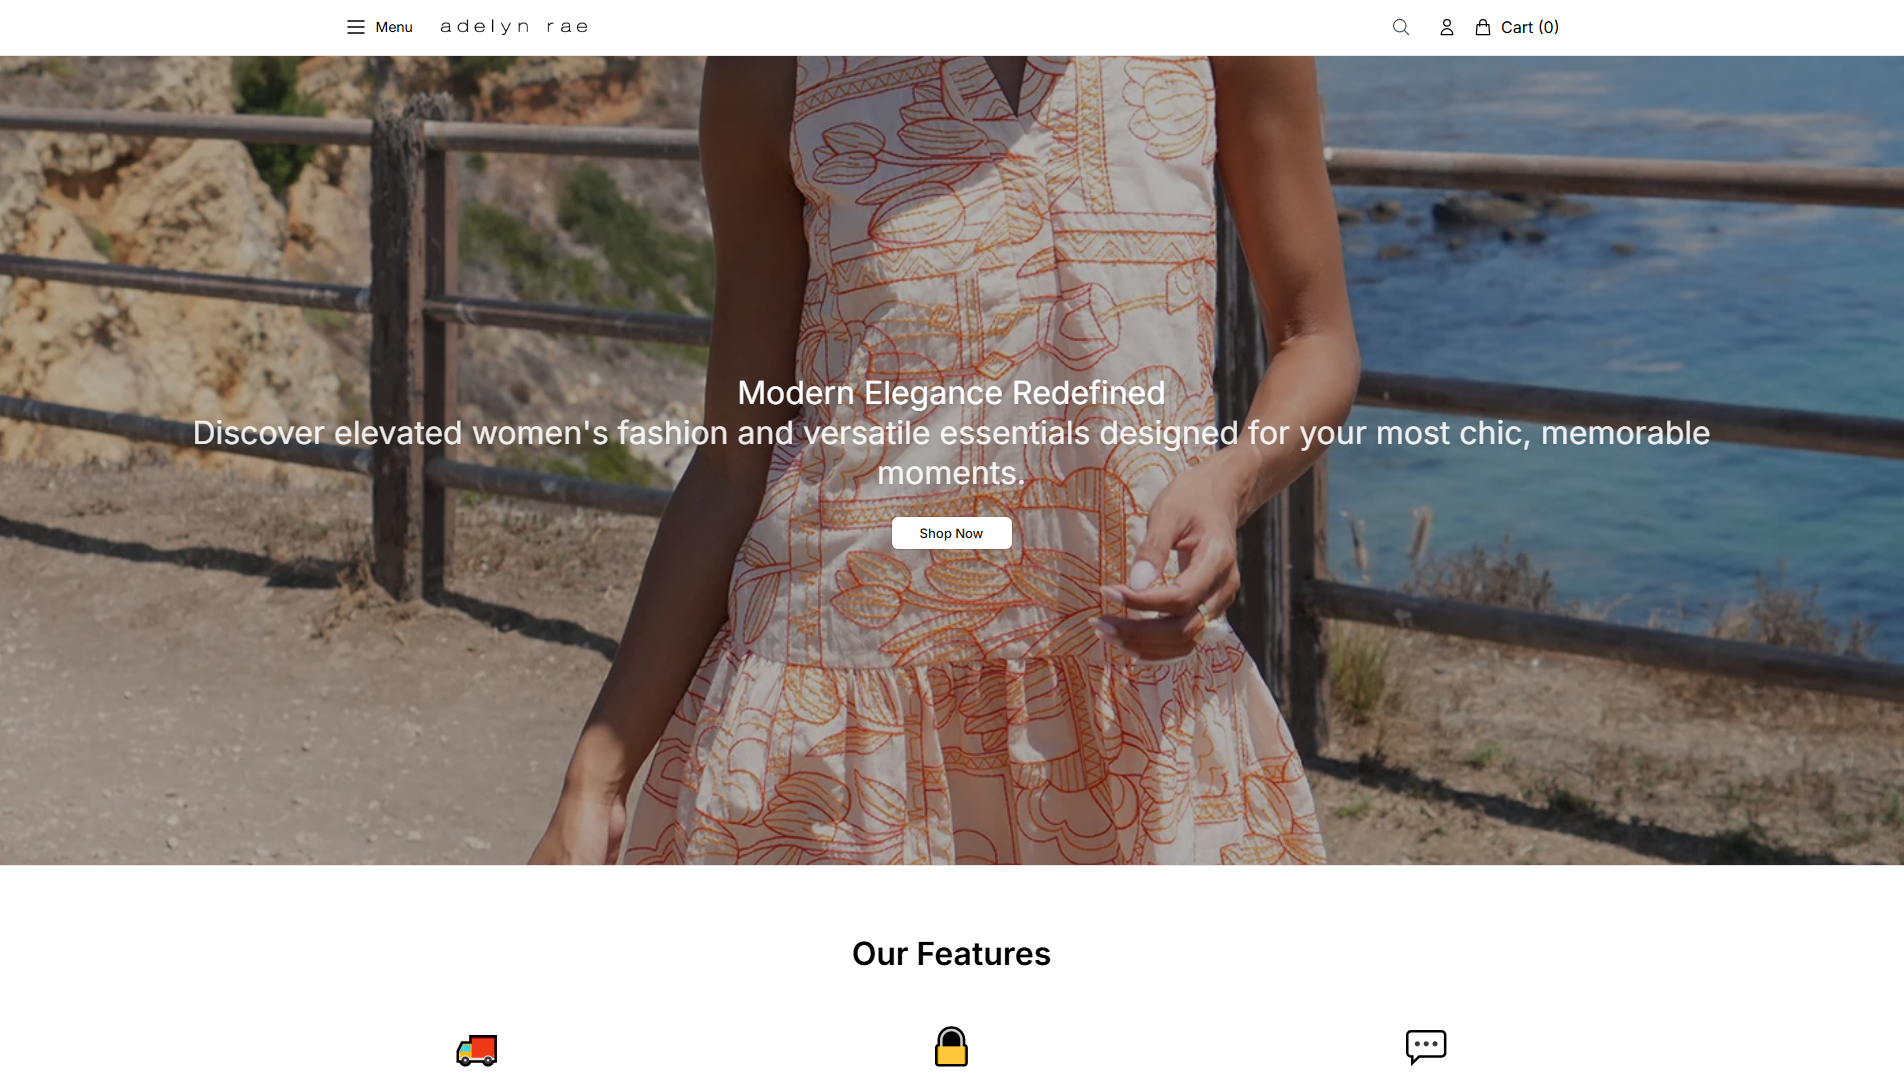
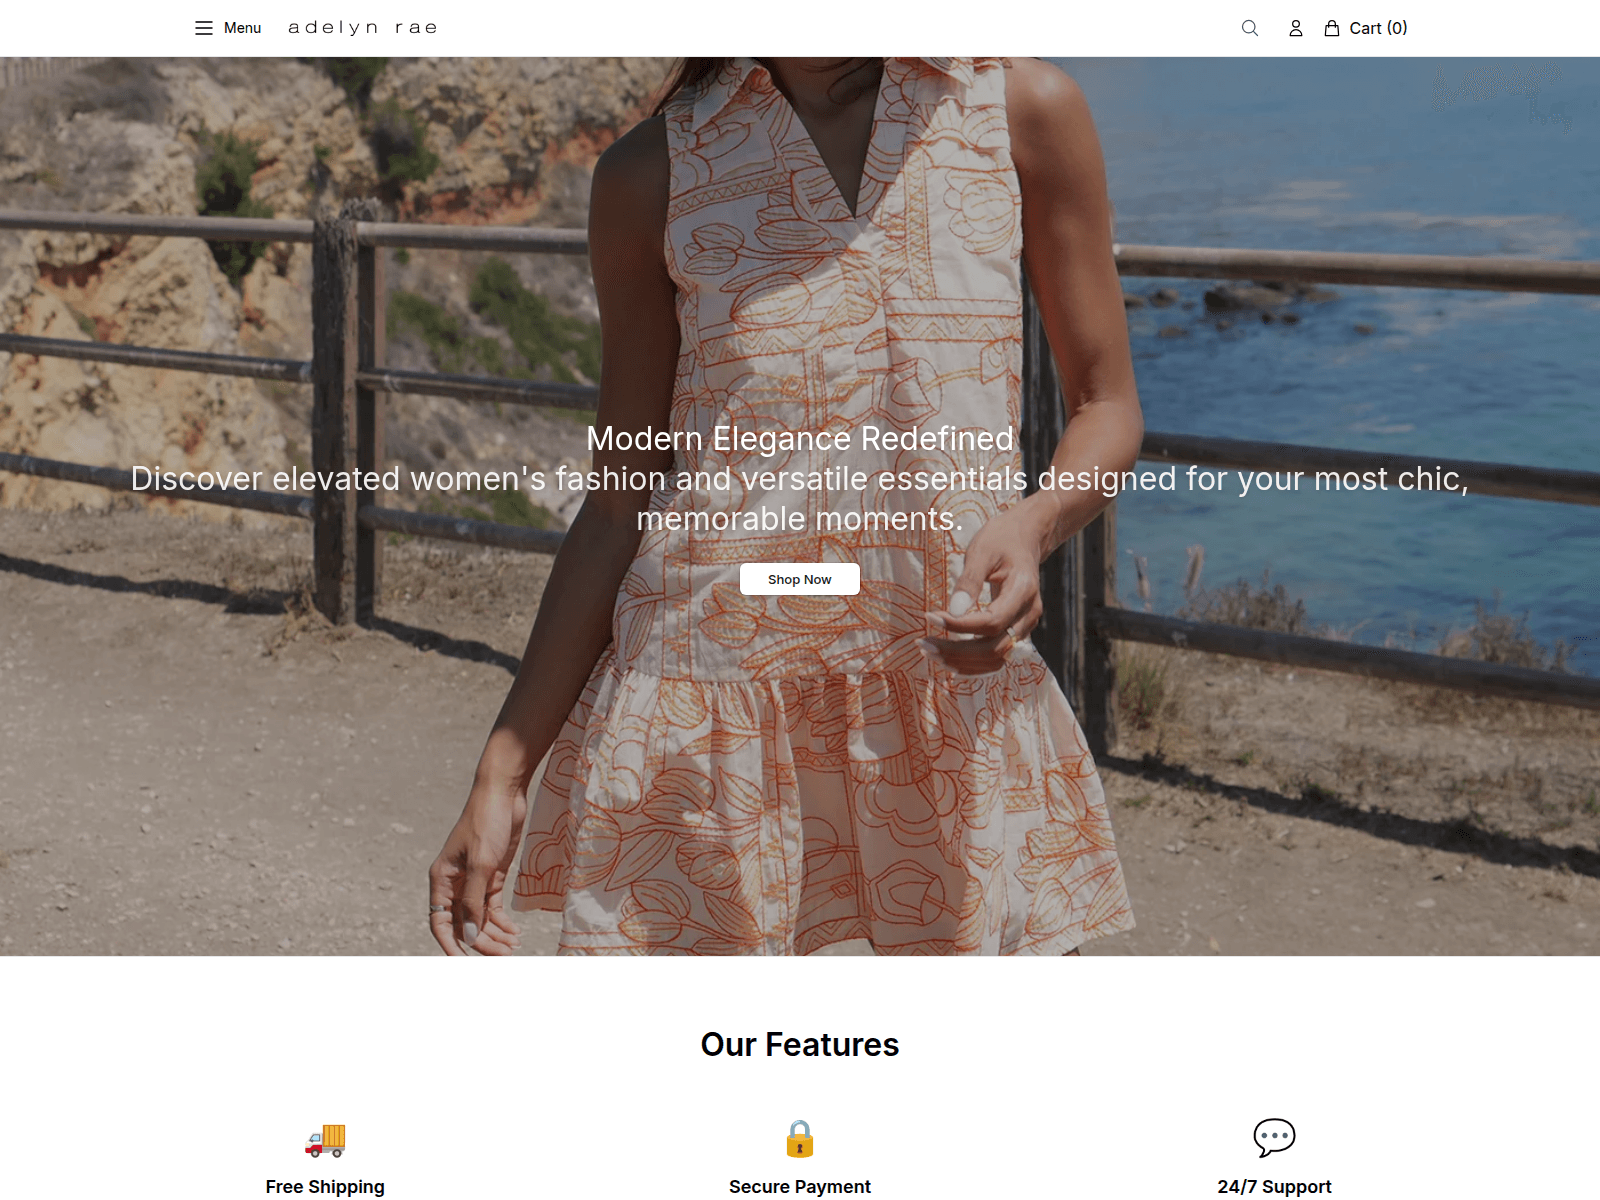
adelynraeshop.shop — Último ativo conhecido (HTTP 200). Representação da marca: Fakeshop; Tipo de golpe: Impersonation. Resumo das evidências: VirusTotal 10/89 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); URLScan malicious verdict; PhishDestroy score 98/100. Registrador: Dynadot.
A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.

10 / 89
malicious
Denunciarchecked — no detections recorded
Denunciar4 community references
Denunciarprovider verdict: clean
Denunciarrelatório armazenado
 Denunciar
Checked; no threat flag recorded
Denunciaradelynraeshop.shop returned an HTTP 200 response on 2026-10-01, according to its recorded HTTP check. The domain was first observed on 2026-09-09, providing a clear starting point for its documented activity.
The HTTP check on 2026-10-01 recorded status 200 for adelynraeshop.shop. VirusTotal recorded 10 detections out of 89 scanners on 2026-09-18. OTX documented 4 pulses on 2026-09-10. The domain was first observed on 2026-09-09, and a PageSpeed check on that date returned a performance score of 63. The registrar was Dynadot Inc., with registration on 2026-04-24. The SSL issuer was YE2, scanned on 2026-09-09. PhishDestroy's internal listing was recorded as true.
Each source observation for adelynraeshop.shop provides a distinct perspective on the domain's recorded status and performance. The HTTP response and PageSpeed score reflect technical checks, while VirusTotal and OTX offer insight into security-related observations. The registration and SSL details supply context for the domain's setup, and the PhishDestroy listing is a publisher-owned record.
For adelynraeshop.shop, retain the HTTP, VirusTotal, OTX, and PhishDestroy records for ongoing reference. Compare future VirusTotal and OTX results with these documented findings. Review the HTTP response and PageSpeed performance in subsequent checks to track any technical changes.
Observações armazenadas comparando o rastreador com o navegador para este host, além de uma verificação em tempo real da assinatura digital para sistemas de distribuição de tráfego do tipo Keitaro.
Nota do digitalizador: alive_content: raw=ok; http=200; via=https_proxy
For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.
RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.
millie.ns.cloudflare.comLocation describes the IP network.
53b1f3be1a232fd1abd09c1578d0ae8ff7159acfe100e847fc7341321b39e500Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.
Google PageSpeed Insights — mobile performance audit of adelynraeshop.shop · checked Sep 9, 2026
37.72.142.130. 20 recorded events. These records describe collected evidence, outgoing notifications and publication; they do not confirm a complete investigation or a takedown.
We scan suspicious URLs, inspect public results and send evidence through the appropriate abuse-reporting channels. The dated events above show what is recorded for this domain. The directory below explains the wider workflow.
Capture the rendered page, requests and visible infrastructure.
Compare the available engine results and retain the analysis timestamp.
Check whether Google currently lists the URL as unsafe.
Inspect a public scan and its recorded network and classification data.
Look for indicator references and related community intelligence.
Compare archived captures and preserve historical context.
Look for matching indicators and associated threat records.
Inspect certificate records and related hostnames.
Compare security resolver responses and record observed blocking.
Inspect the public DNS, TLS, HTTP and technology surface.
Security services used for scanning, reputation checks and reporting are listed below. A service being listed is not evidence that it received, accepted or acted on this particular domain. Recorded submissions appear in the notification history above.
PD-20260909-9A32CA Recipient: abuse@rashost.com Policy Violations: Illegal Activities: Active phishing operation targeting victims Fraud & Deception: Impersonation of legitimate services Identity Theft: Collection of credentials under false pretenses Applicable Laws (Unknown): International Anti-Cybercrime Regulations Budapest Convention on Cybercrime Universal Fraud Prevention Laws Phishing activities violate international cybercrime conventions and Unknown's domestic fraud laws. Action Required: This evidence-backed report demonstrates clear violations requiring suspension per your policies. Continued hosting exposes your organization to regulatory scrutiny and potential legal liability.
Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.


Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.
Template-based draft · optional AI wording assistance requires separate consent
Cada faixa representa um motivo pelo qual um domínio está vinculado a este host. O tamanho dos nós indica as detecções do VirusTotal, e os nós tracejados já estão offline. As listas completas seguem abaixo.
Este IP de origem hospeda vários domínios de phishing — a infraestrutura pode ser compartilhada entre campanhas.
Esses domínios também têm como alvo os usuários do Fakeshop. Ver todas as ameaças do tipo “Fakeshop” →
Registrados pelo mesmo registrador. Um registrador atende a milhões de clientes sem qualquer relação entre si; portanto, isso apenas agrupa os registros, em vez de comprovar uma ligação.
Relatórios adicionados recentemente do banco de dados PhishDestroy. Esses links de descoberta não implicam infraestrutura ou propriedade compartilhada.
Análise de ameaças usando lista de bloqueio armazenada, WHOIS, DNS e evidências de verificação pública
Digitalize agoraEnvie domínios suspeitos para nosso banco de dados de ameaças — proteja a comunidade
DenunciarRelatórios recentes de phishing e alterações de disponibilidade observadas
MonitorarMonitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo