
Pesquise domínios monitorados e analise as evidências armazenadas, as detecções e a disponibilidade mais recente observada.
219,828
Total rastreado
213,490
VT detectado
91,921
Visto pela última vez: Ativo
127,907
Indisponível na última verificação
576
VT Pendente
How This Attack Works
WalletConnect Abuse involves deceptive tactics to exploit users of cryptocurrency platforms. Understanding these steps can help in prevention.
STEP 1
Creation of Fake Domínios
Attackers create fake domains that mimic legitimate cryptocurrency platforms to lure victims.
STEP 2
Deployment of Phishing Pages
Phishing pages are set up on these domains to capture user credentials and wallet information.
STEP 3
Execution of Malicious Code
JavaScript and other scripting languages are used to execute malicious code that intercepts user data.
STEP 4
Unauthorized Transactions
Stolen credentials are used to authorize transactions, draining victims’ wallets.
Technical Analysis
WalletConnect Abuse often involves the creation of phishing sites that mimic popular cryptocurrency service providers. Attackers use sophisticated scripts to manipulate the WalletConnect protocol, intercepting the authentication process. This includes the use of JavaScript to capture private keys and signatures when users attempt to connect their wallets. Infrastructure-wise, attackers frequently utilize content delivery networks like Cloudflare to host phishing sites, taking advantage of high availability and speed. Additionally, smart contracts are sometimes manipulated to automatically approve transactions that transfer funds to the attacker’s address without the victim's explicit consent.
Real Cases
The Opensea Phishing Incident (2024)
$2 million stolen
A phishing campaign targeting Opensea users resulted in significant financial losses and credential theft.
Vercel App Scam (2023)
$1.5 million stolen
Attackers used fake Vercel app domains to trick users into revealing wallet information, leading to unauthorized access.
Marketplace-Art Fraud (2024)
$3 million stolen
Fraudulent marketplace-art domains were used to deceive users into connecting their wallets, resulting in asset theft.
How to Detect
Unfamiliar domain names mimicking legitimate services
Requests for private keys or seed phrases
Unexpected transaction requests
Poor website design or misspellings
Limited or no HTTPS security
How to Protect Yourself
1
Always verify domain authenticity
2
Enable two-factor authentication
3
Use hardware wallets for transactions
4
Regularly update security software
5
Educate yourself on common phishing tactics
Frequently Asked Questions
Data sourced from PhishDestroy threat intelligence database — 1,677 domains tracked for this threat type
WalletConnect Abuse 1,677 domains

infraredfinances.org
irynaconnect.xyz

keo.retaileth.com
koinlytax.app

launch-talusfoundation.com

layerswap.finance

ldketang.com
legacy-aave.com

lhoui.cc

libertryswap.finance
mail.www-berachains.vote


mefai-voting.net
mega-tge.com
memegainerbot.pages.dev

met-meteora.com
mira-network.app

mobile.illuvium.icu

momentum-ten-inky.vercel.app
mspuitt.xrdapp.com

multichainpump.fun

mysterybox-ethereum.vercel.app
mywallet.is

networkdapp.netlify.app

neutrl-incentives.com

newmainprojectpro.netlify.app

nftstrategy-votes.com

notpad.fun
onchainscore.live

onchainscores.site

onefootballclub.website
optionspolymarket.com

originndefi.io

pancake-swap.sa.com
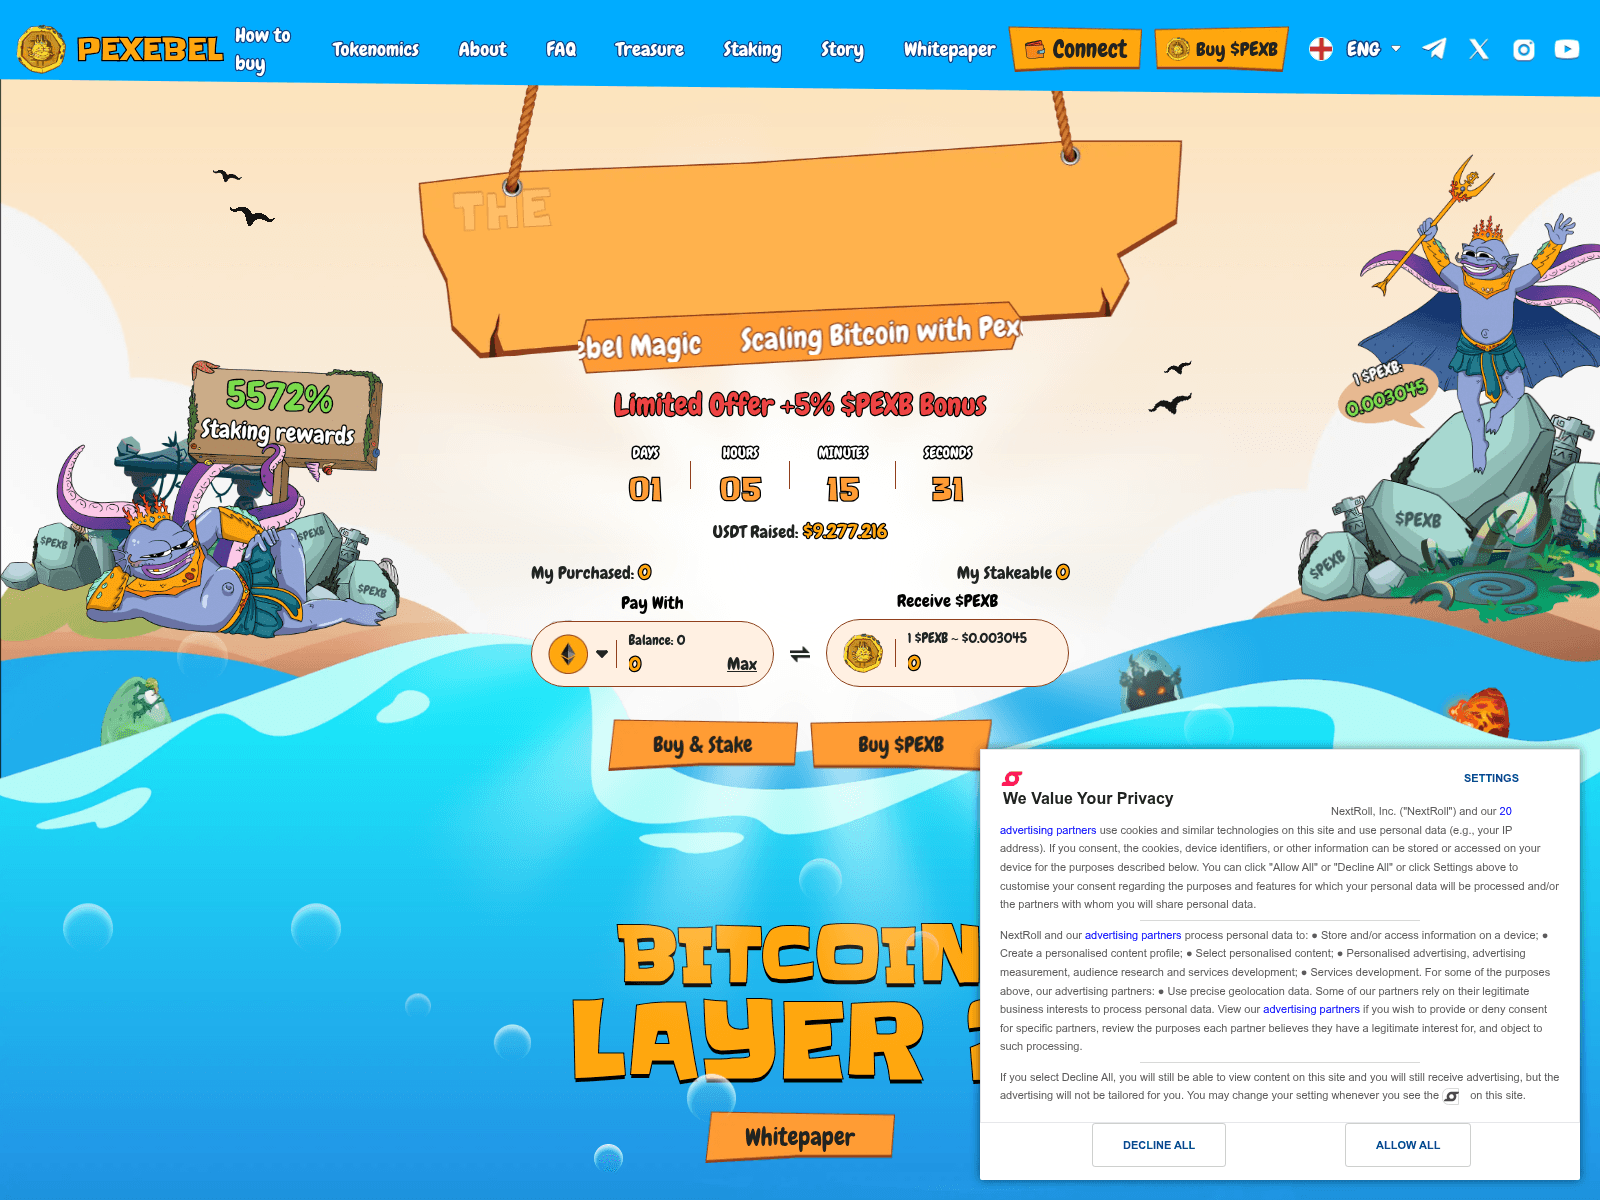
pexebel.com

plasmaswap.to

po555queen.com
pol10.com
polbot77.vip

polygonvip.com
polygonvip.net
portal-campnetwork.web.app
presale.thevault.casa

pro-invite.info
pro700.vip
pub-159584f62dcf45f09d67c8485f215d9a.r2.dev

pumpfun.pump-airdrop.cfd
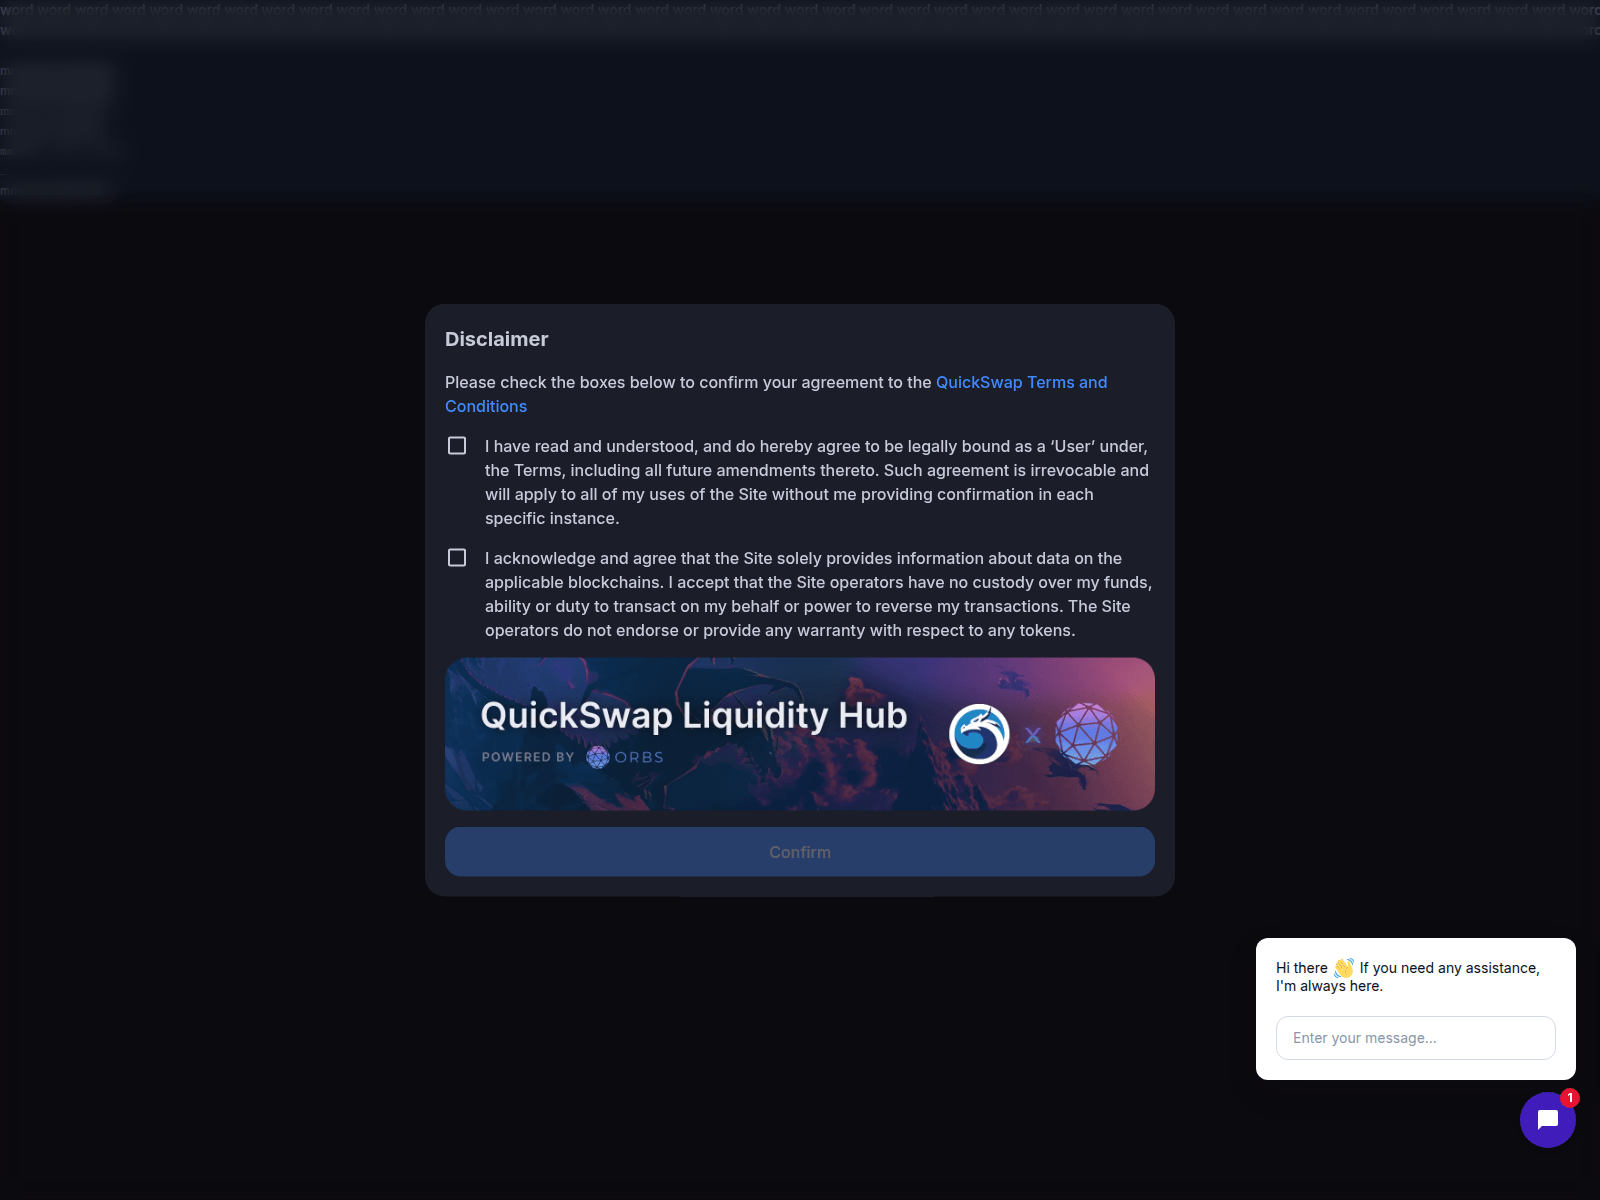
quickswap.exchange-defi-swap-referral.life

rainbow-wallet.pages.dev

raindex.finance

raydium.website

razorvanoeochkto.top

reward-ofc.org

rewards-padresapp.com
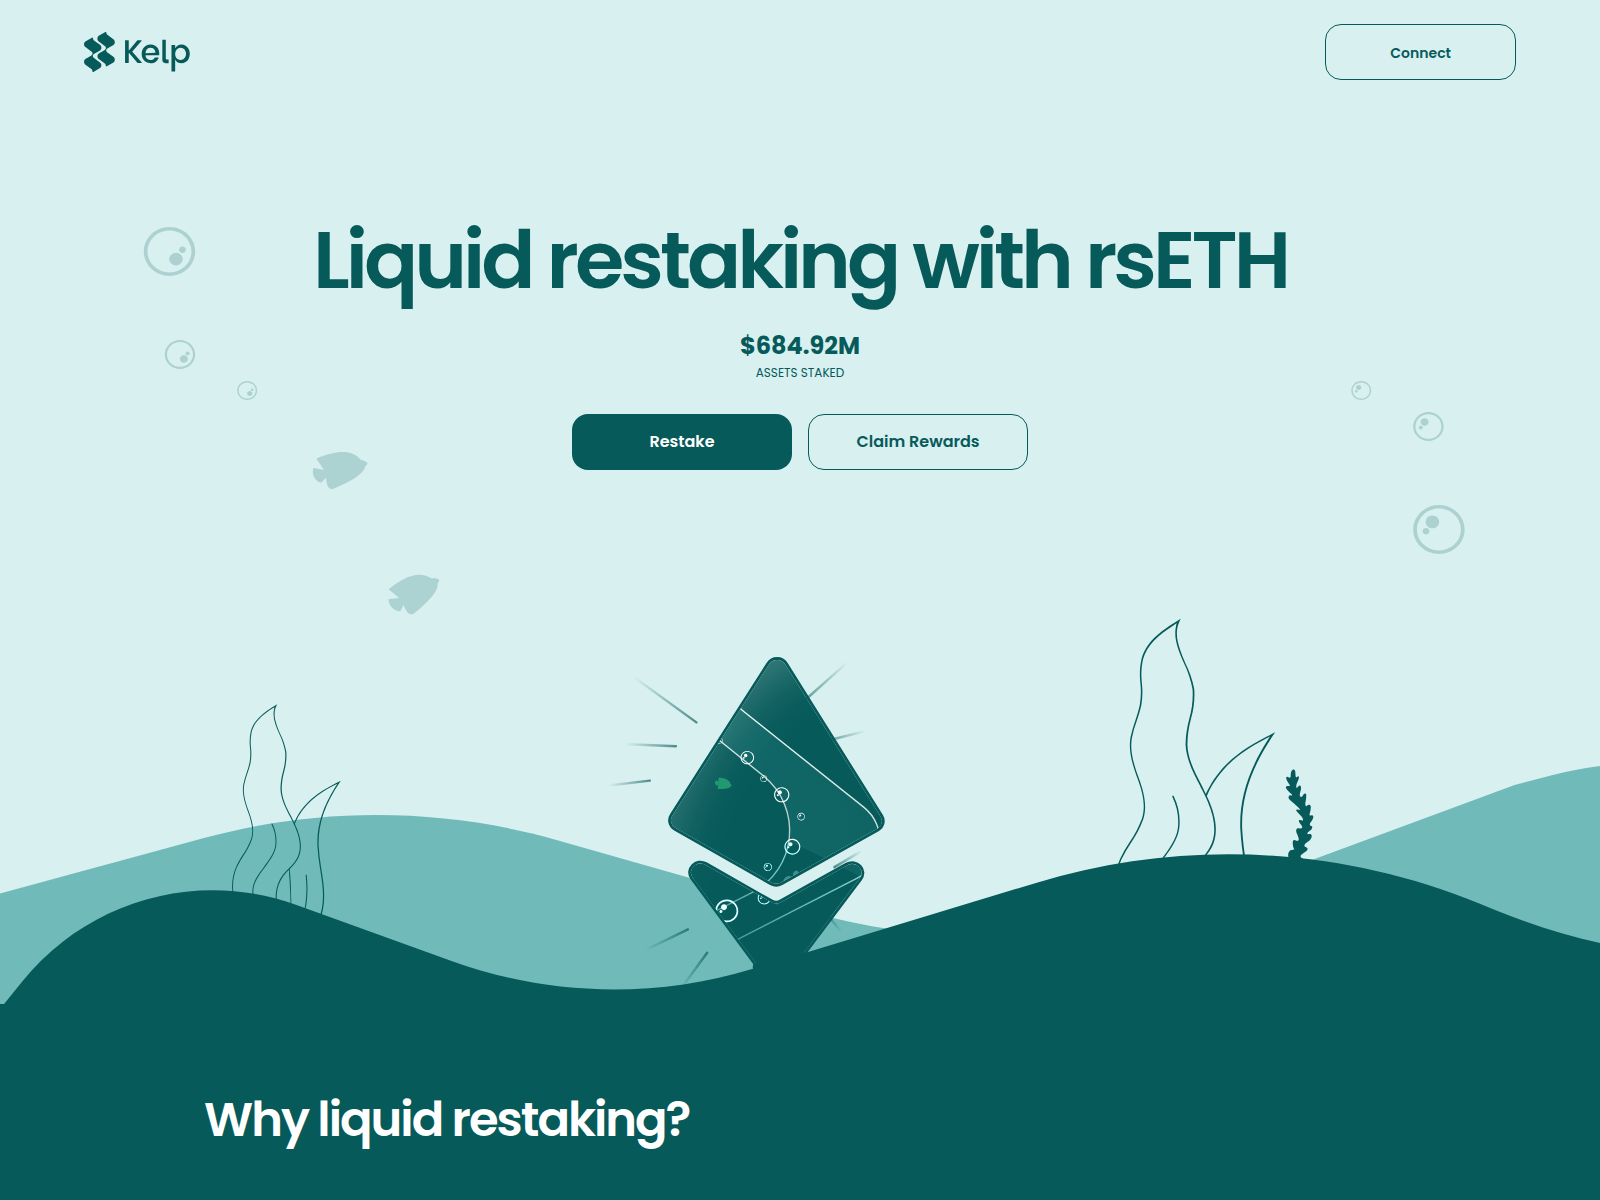
rseth.pro

salute-origindefi.site

scope.rocketlauncher.gg
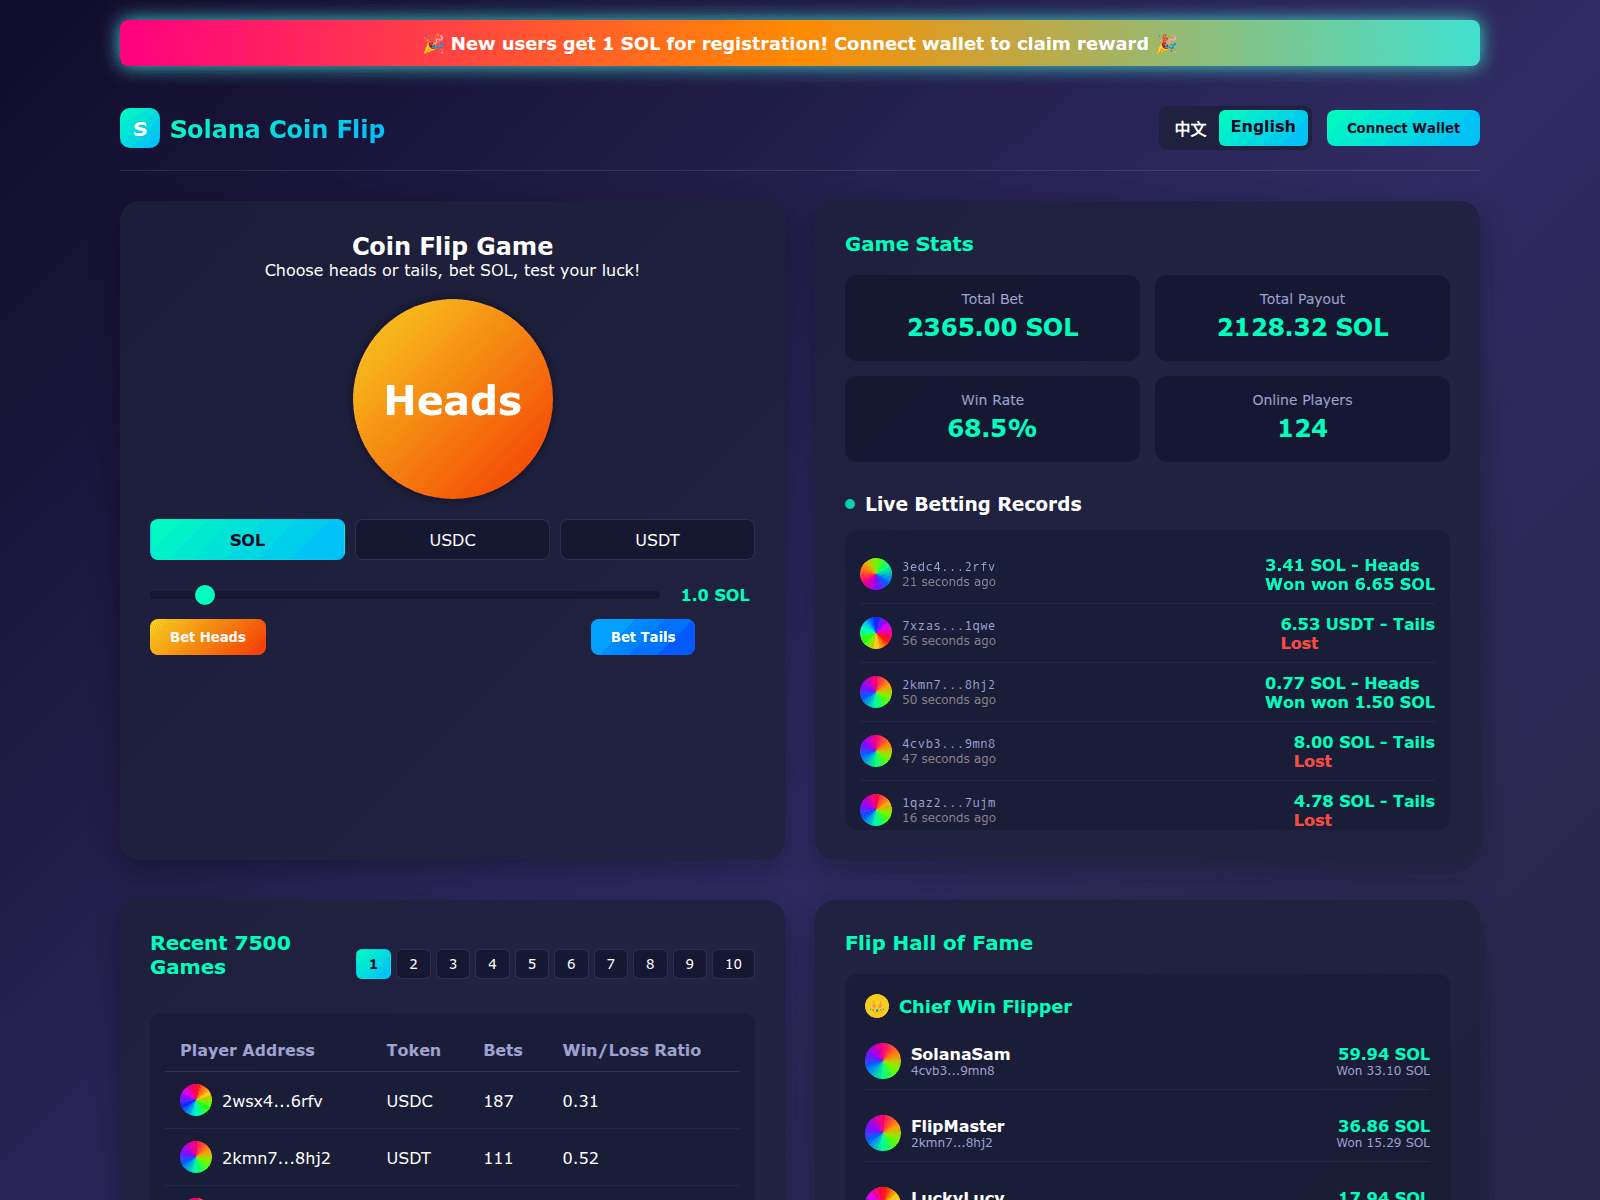
sflip.lol

smartcontract233.com

smartcontract244.com

smartcontract247.online

smartnodesapp.live
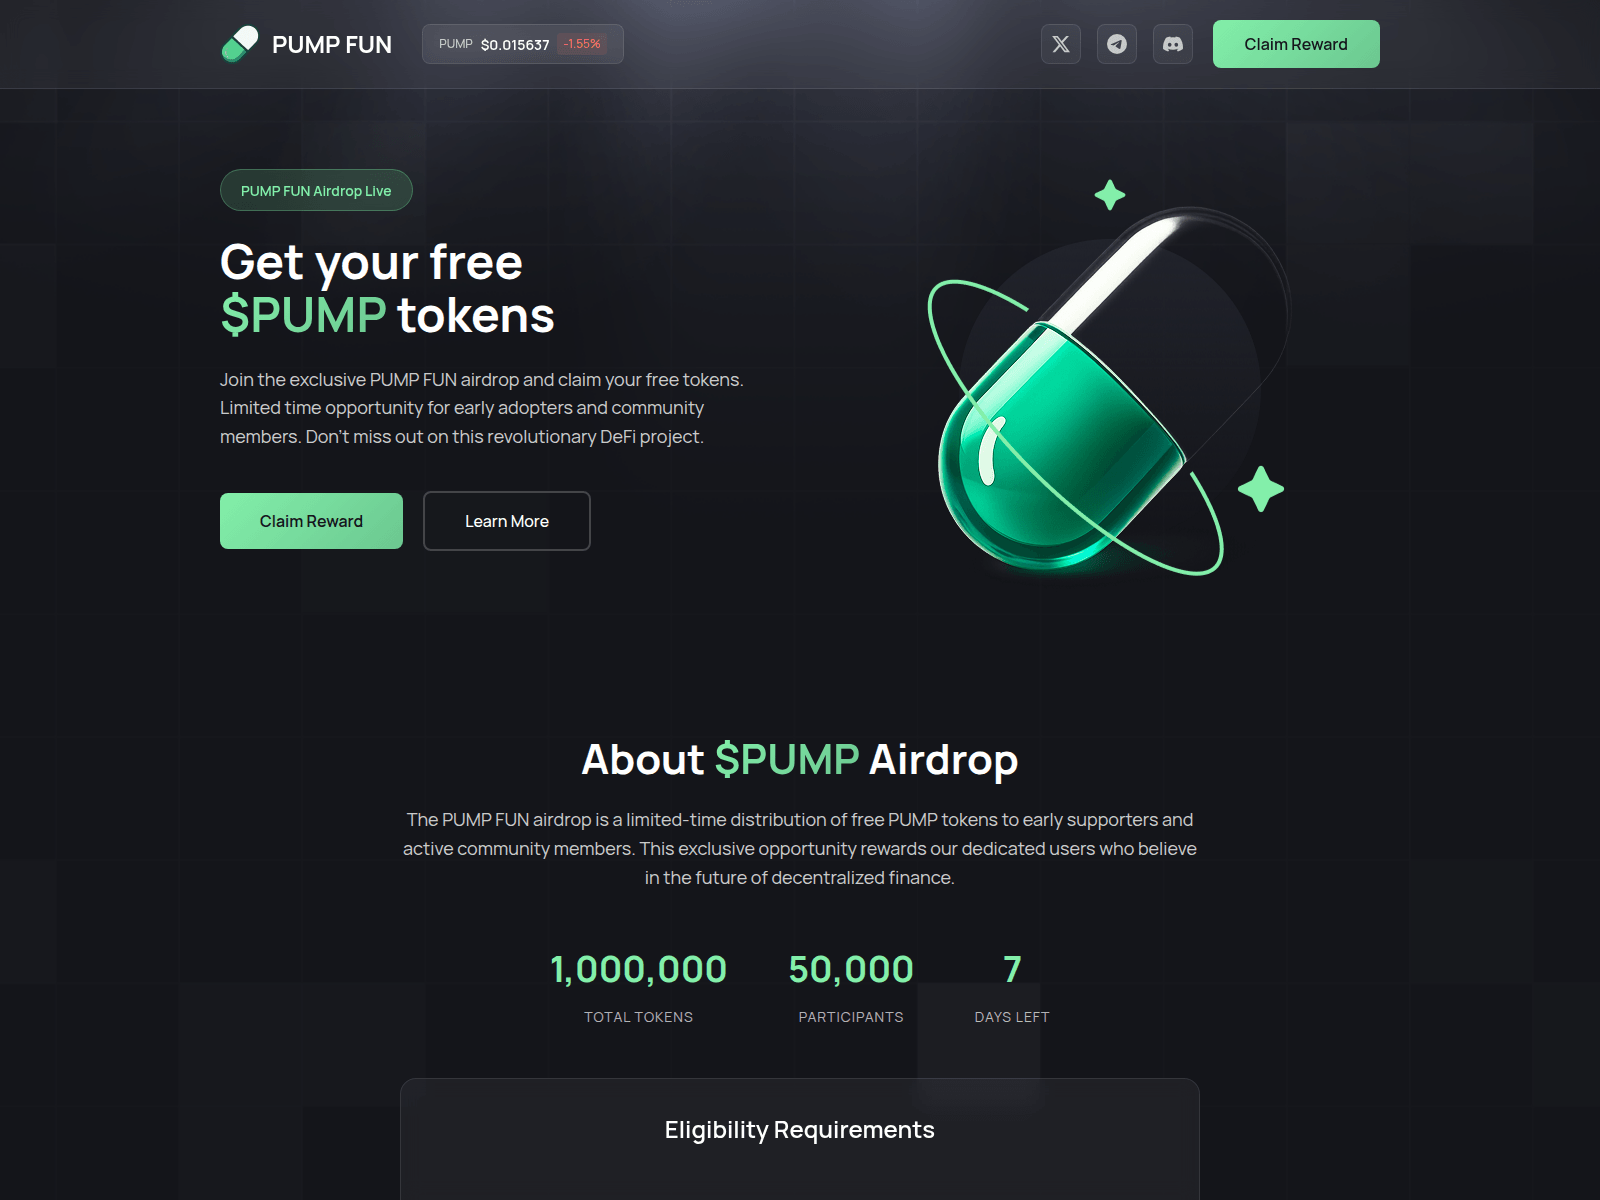
solanafun.org

spacepay.live

sparkdex.exchange

ssv-6kp.pages.dev

stake-validator2025.tech
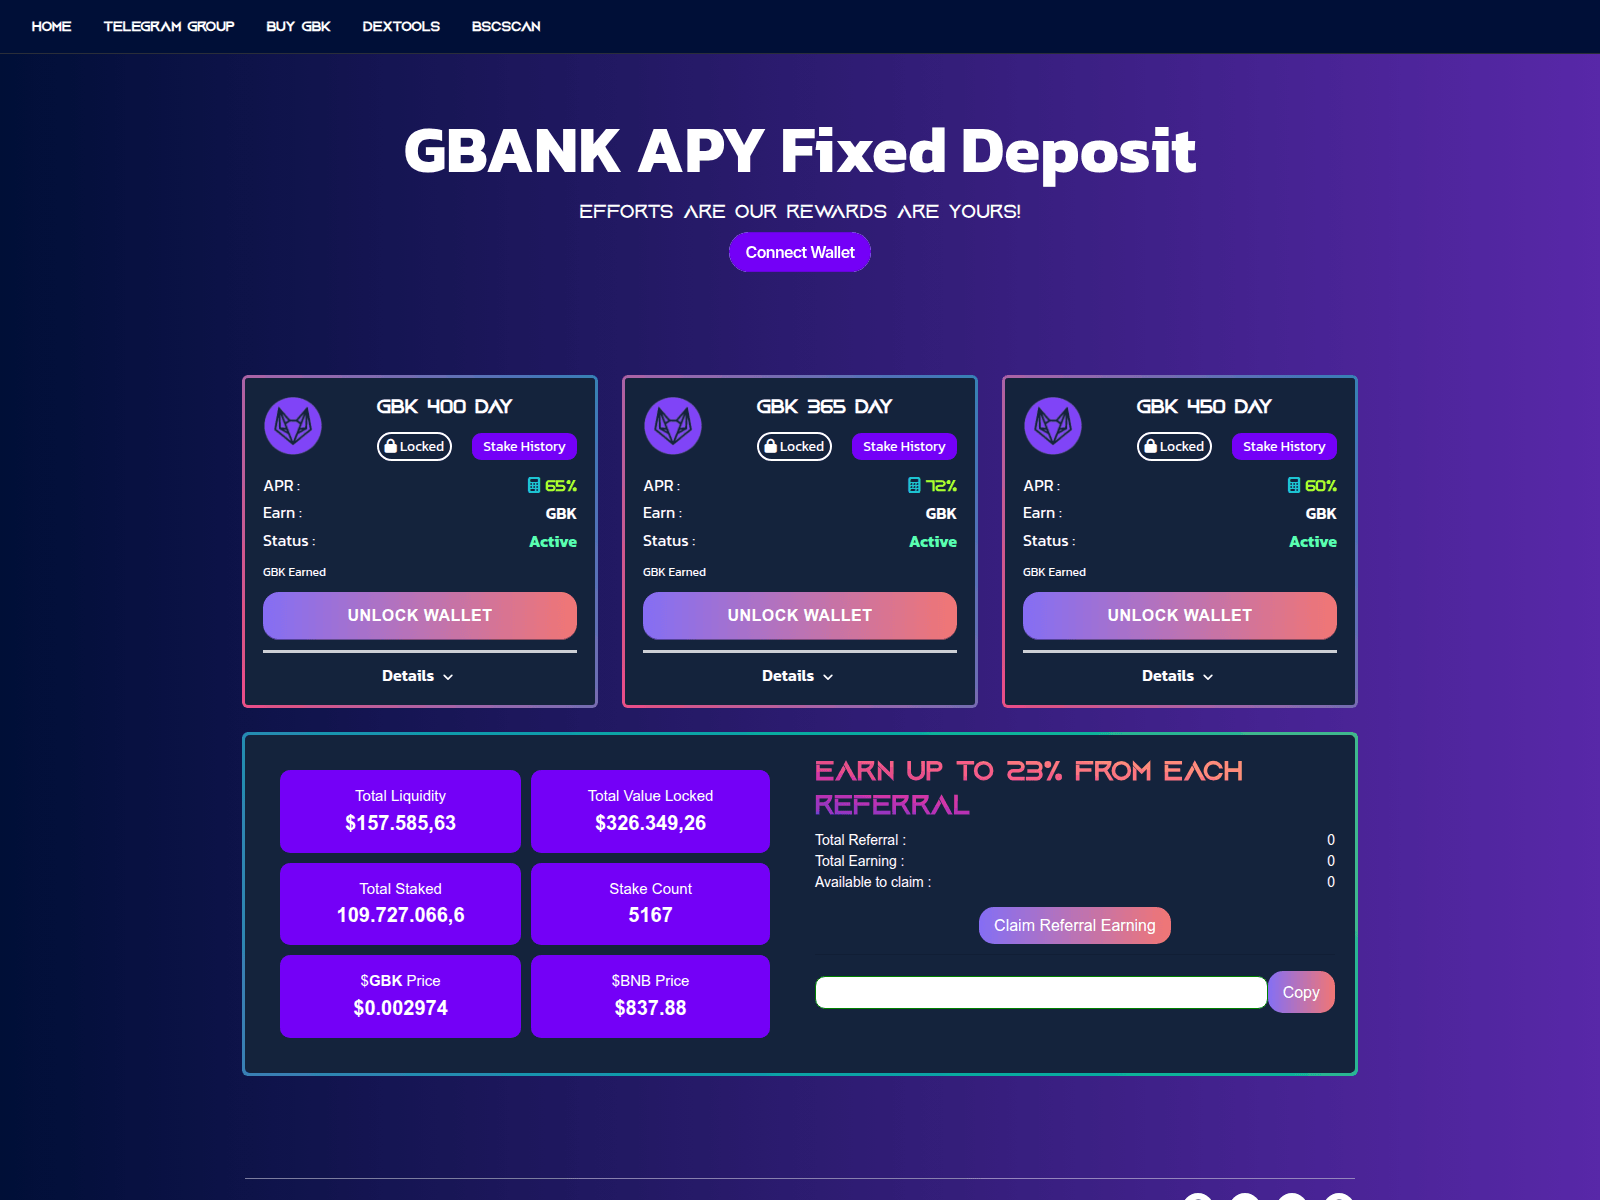
stake.gamebank.fun

stkwise.net
sushiswap.click

swap--x.fi
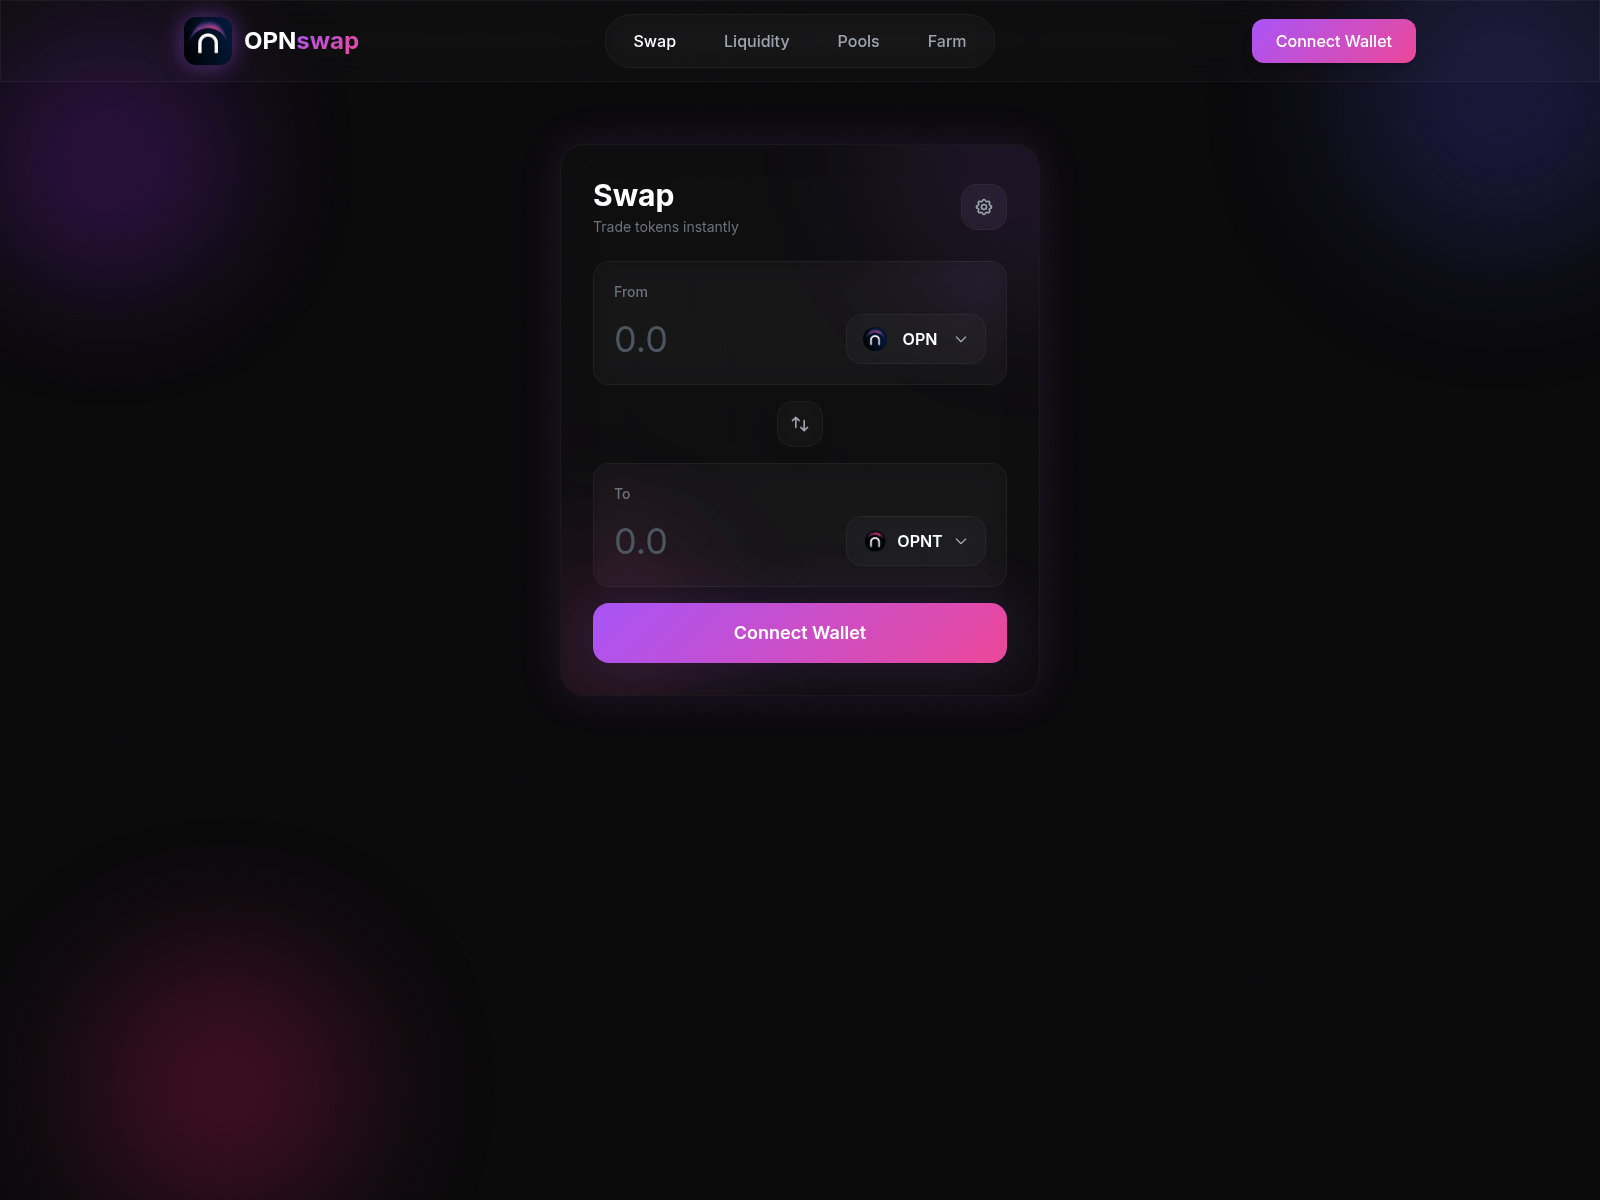
swap.iopn.tech

topstrike.io
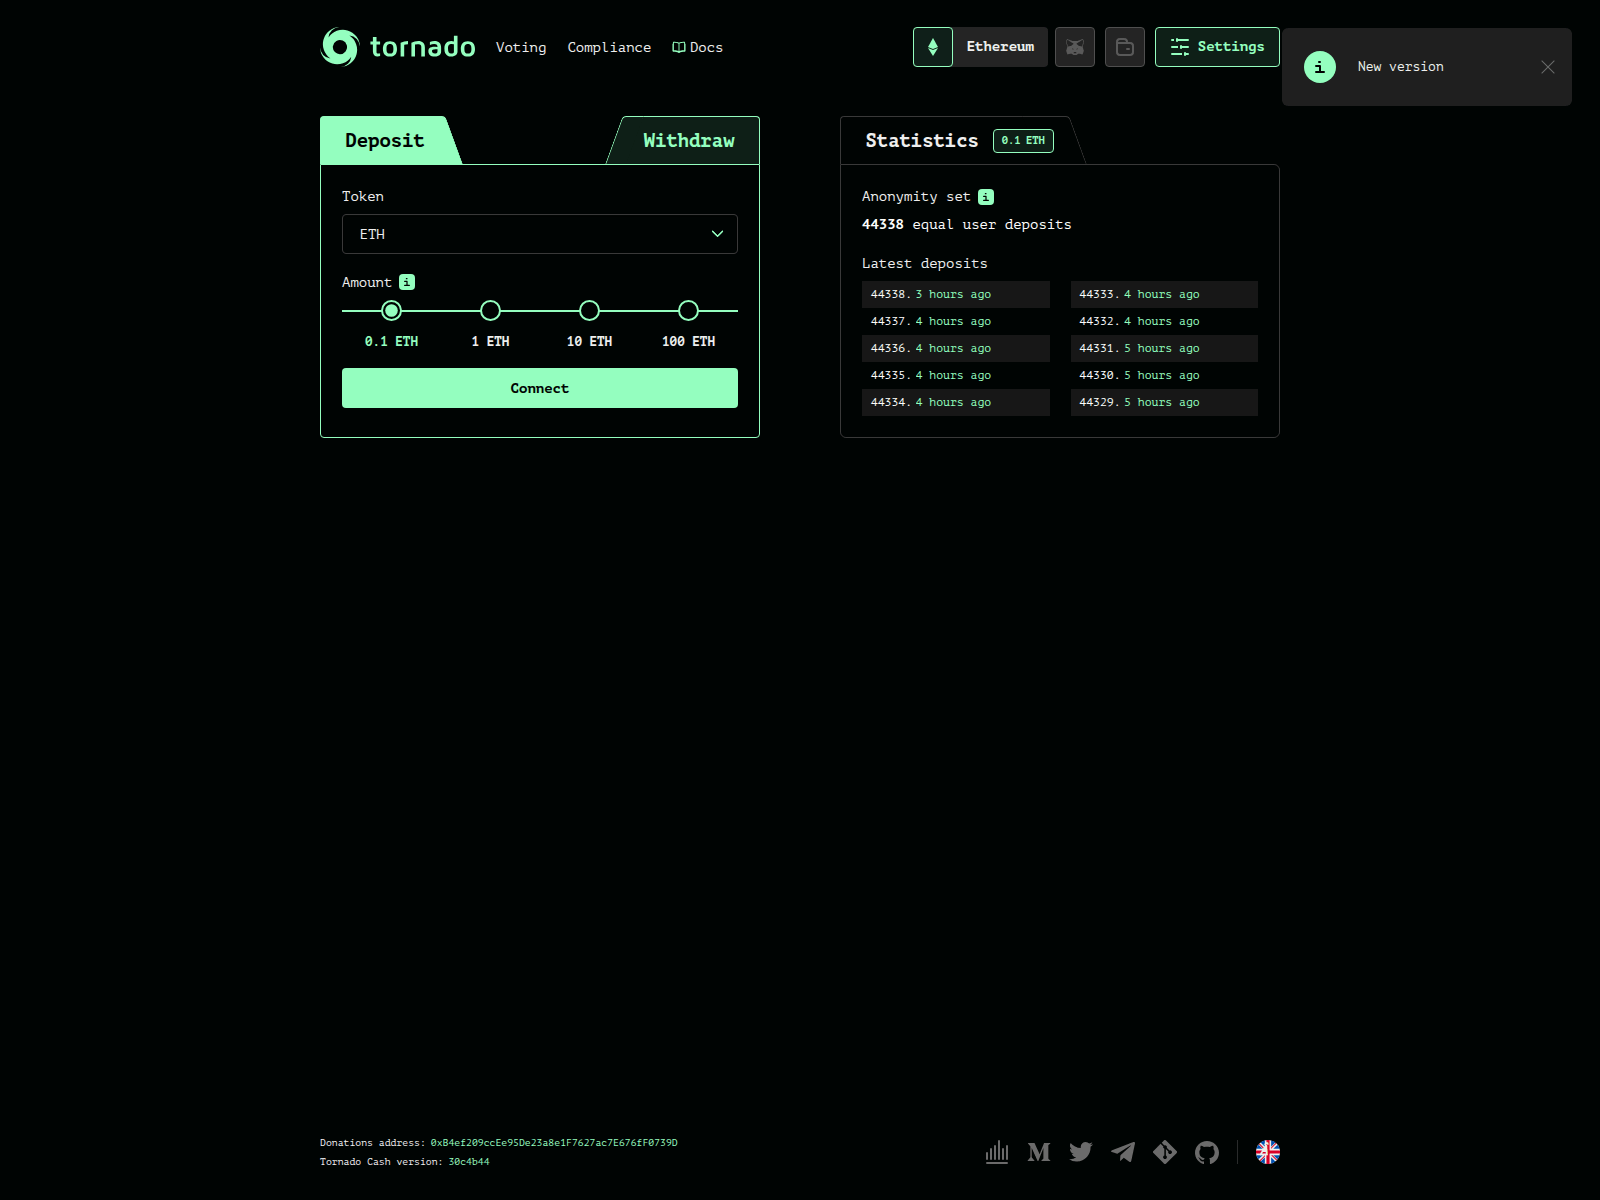
tornedocash-eth.cfd

tradetide.org

trust22.top

trust24.top
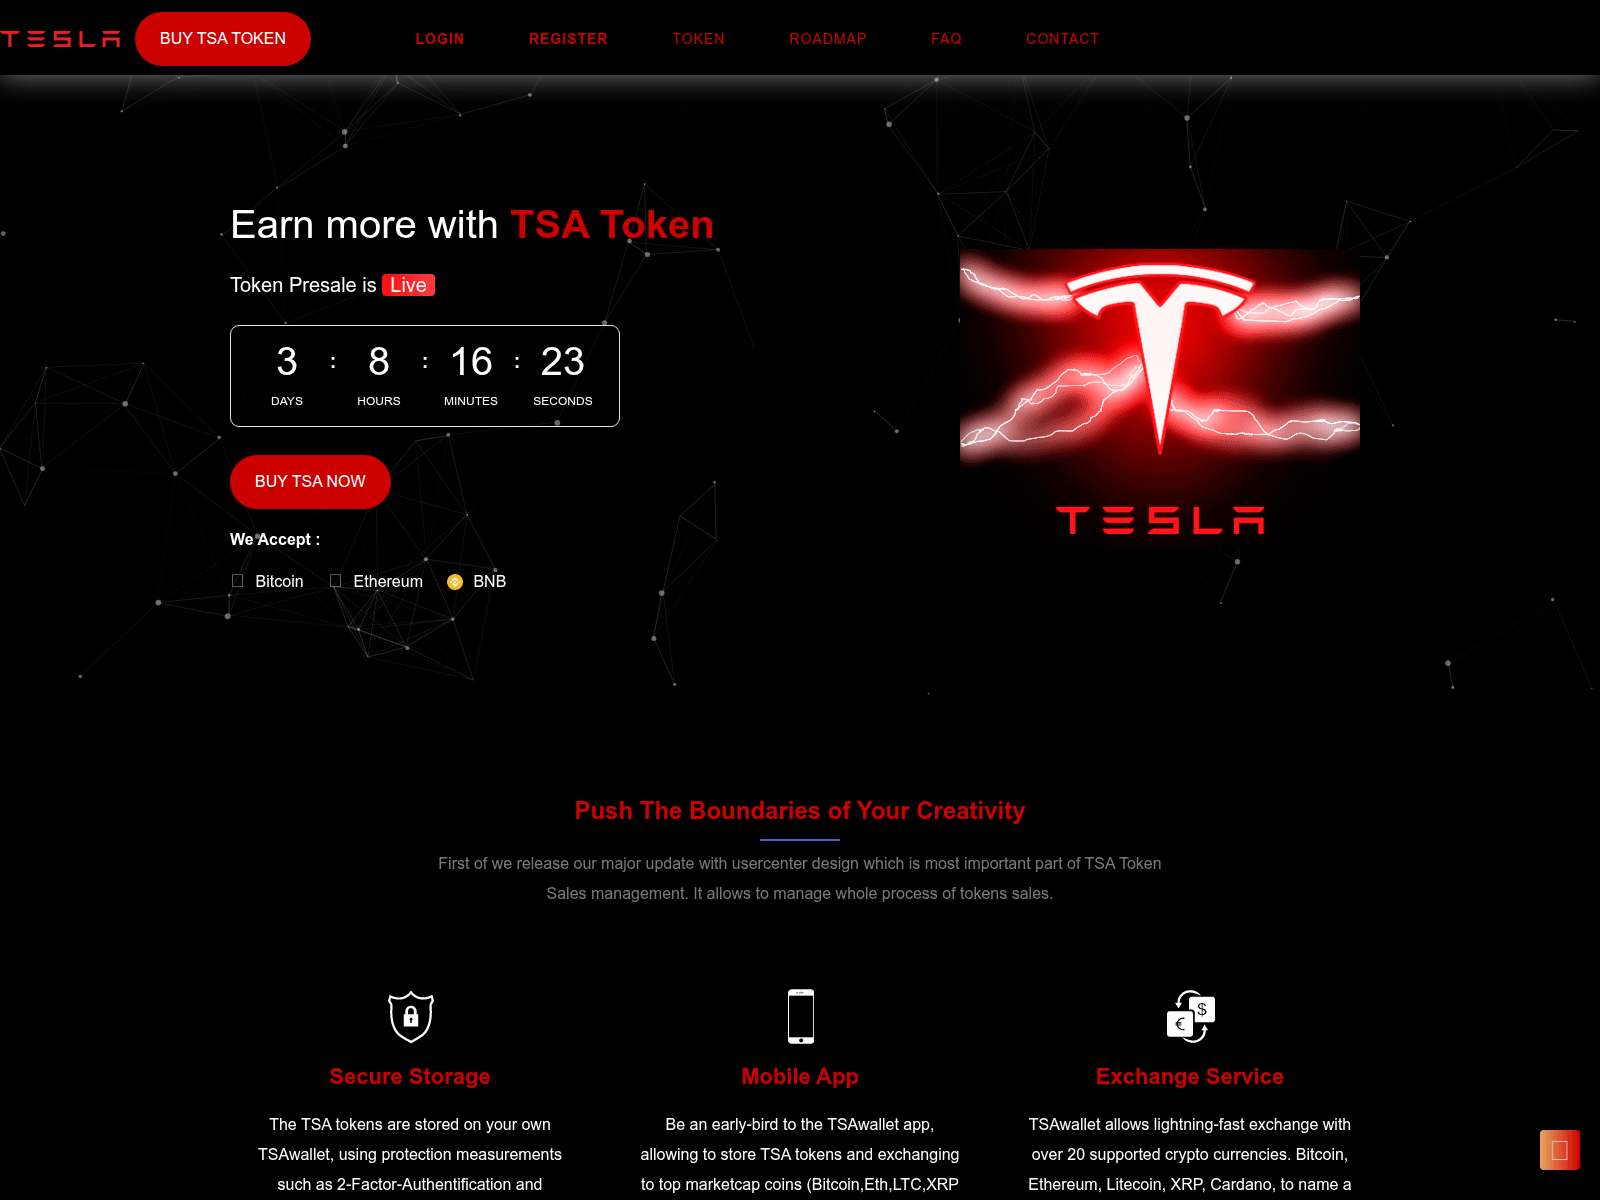
tsa-presale-oppurtunity.web.app

turbotrump.info
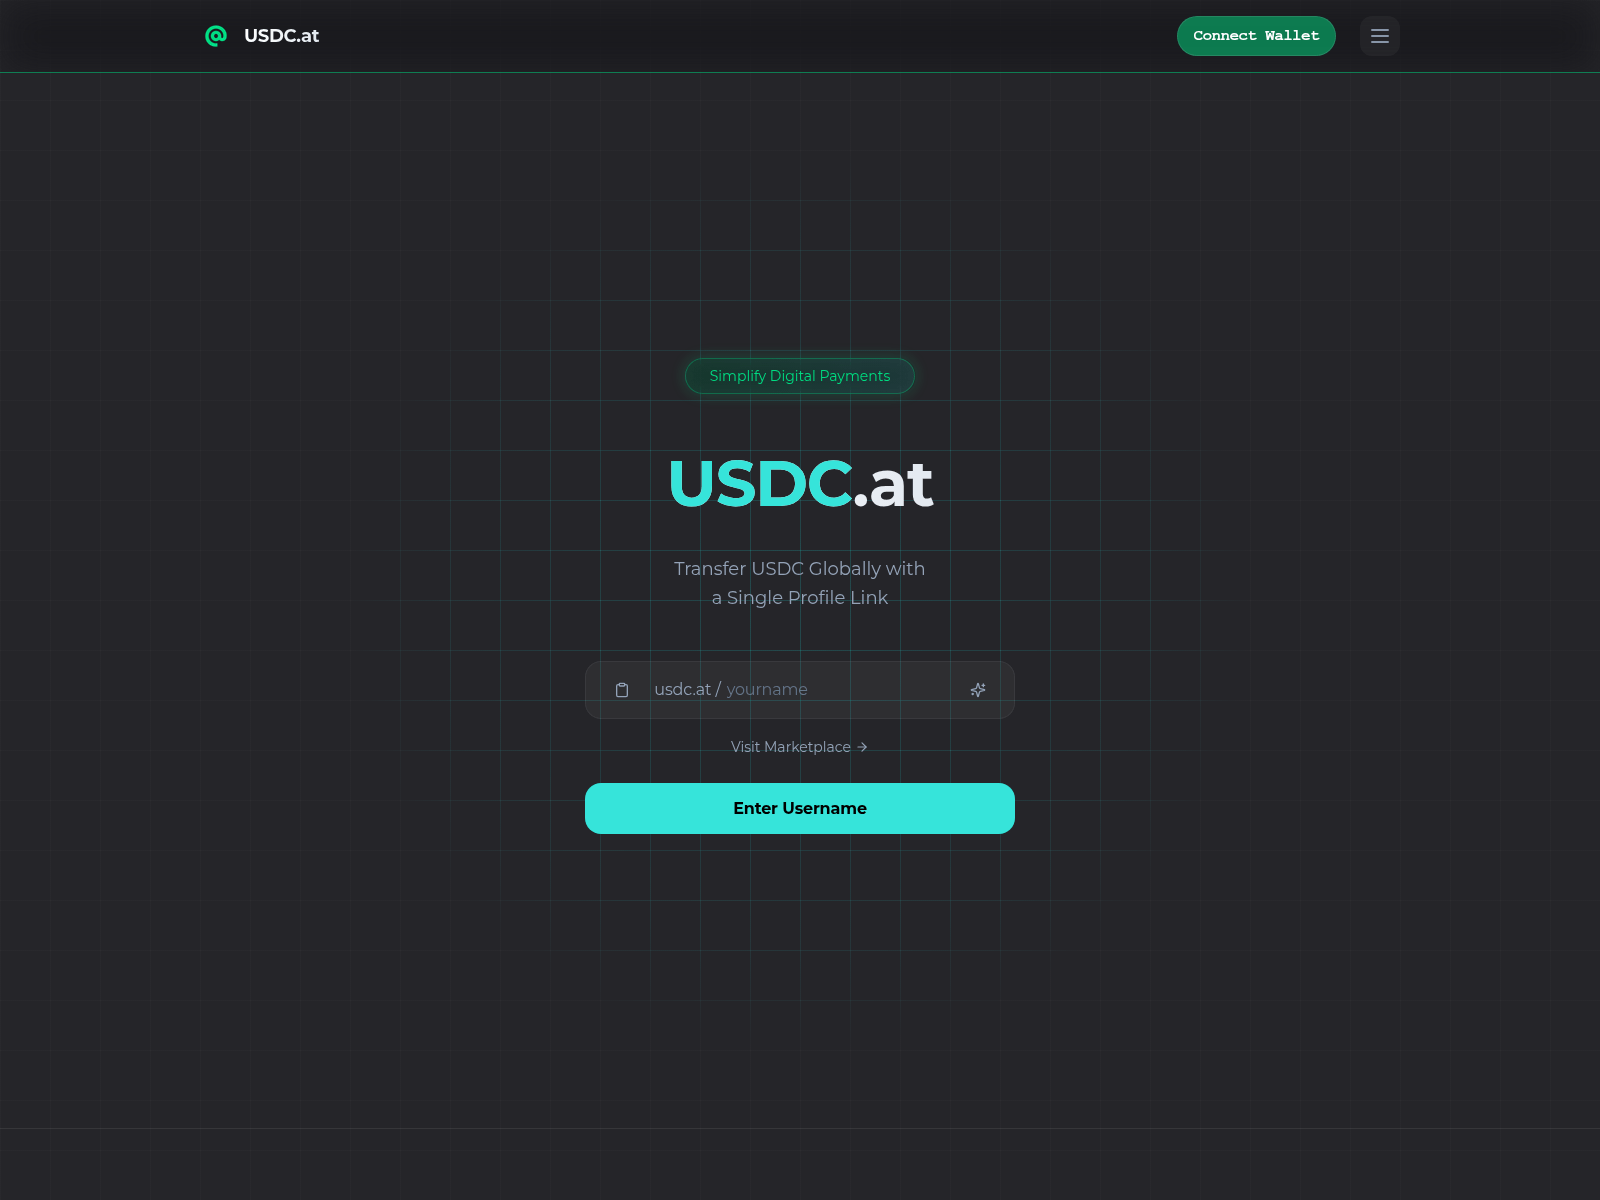
usdc.at

usdc.coupons

velorahr.com
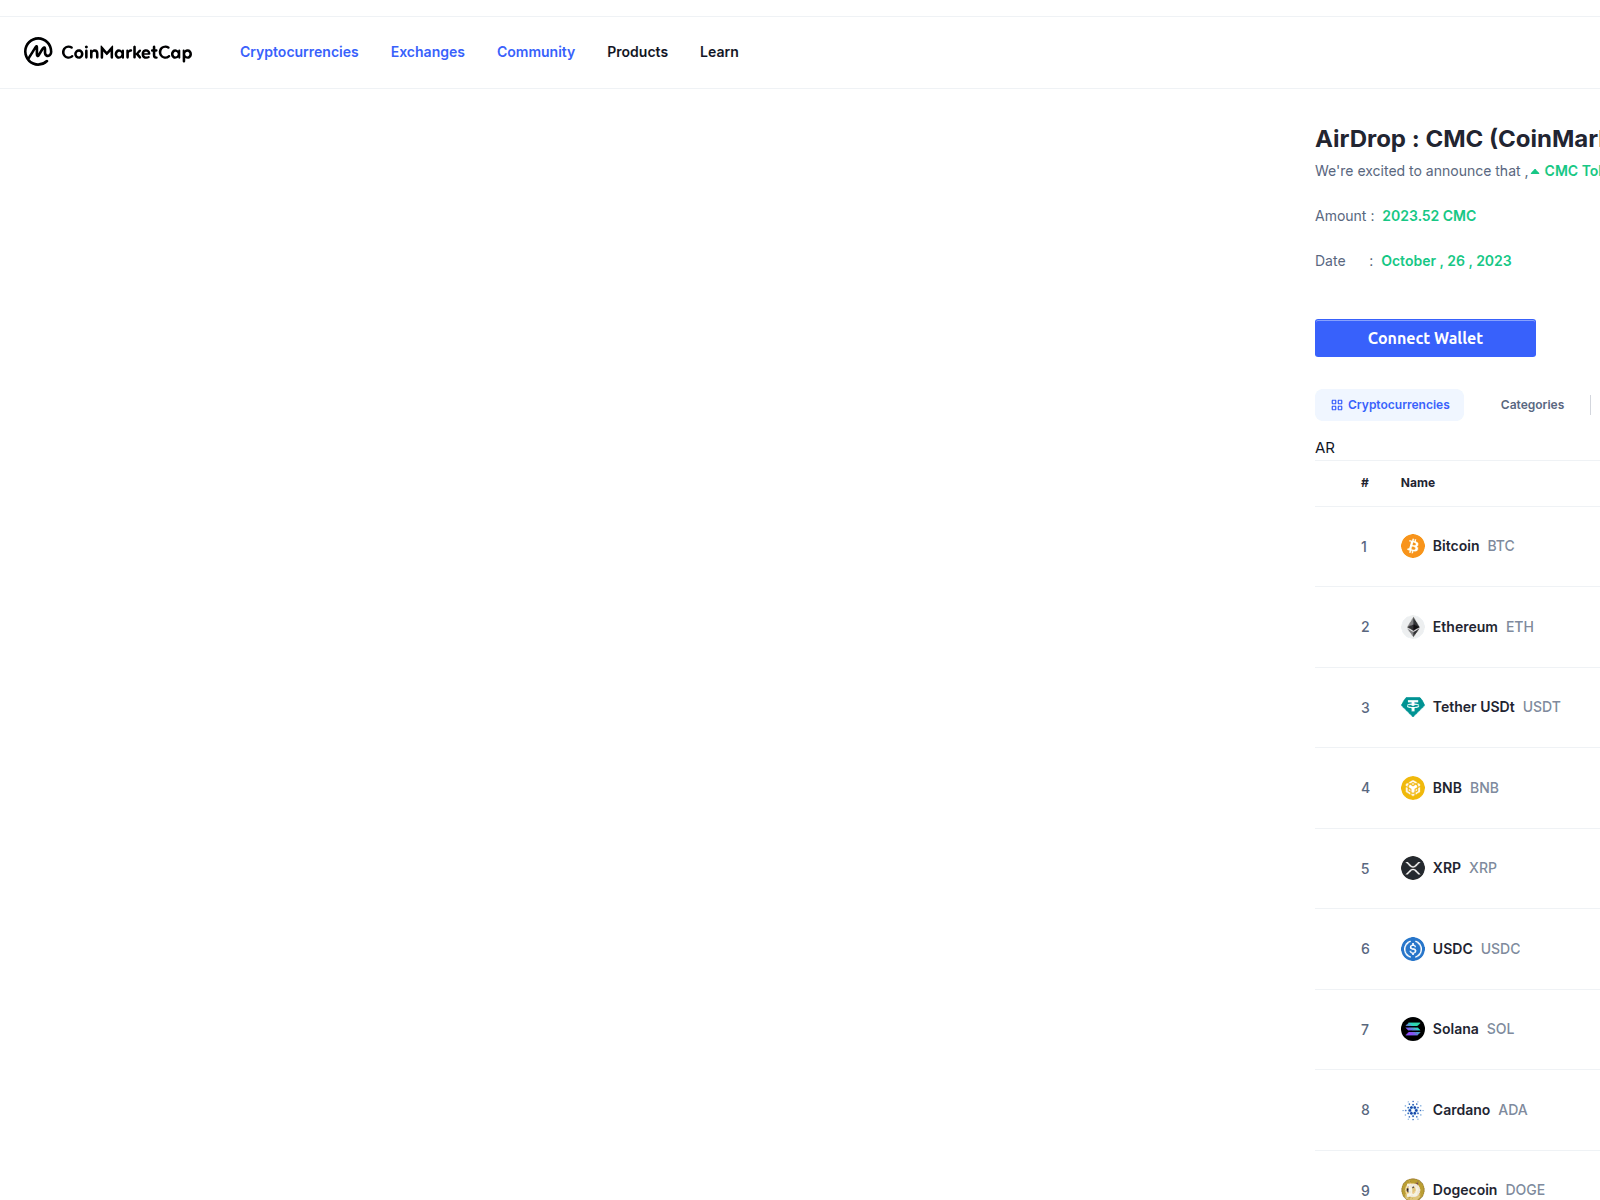
verify-cmc.app
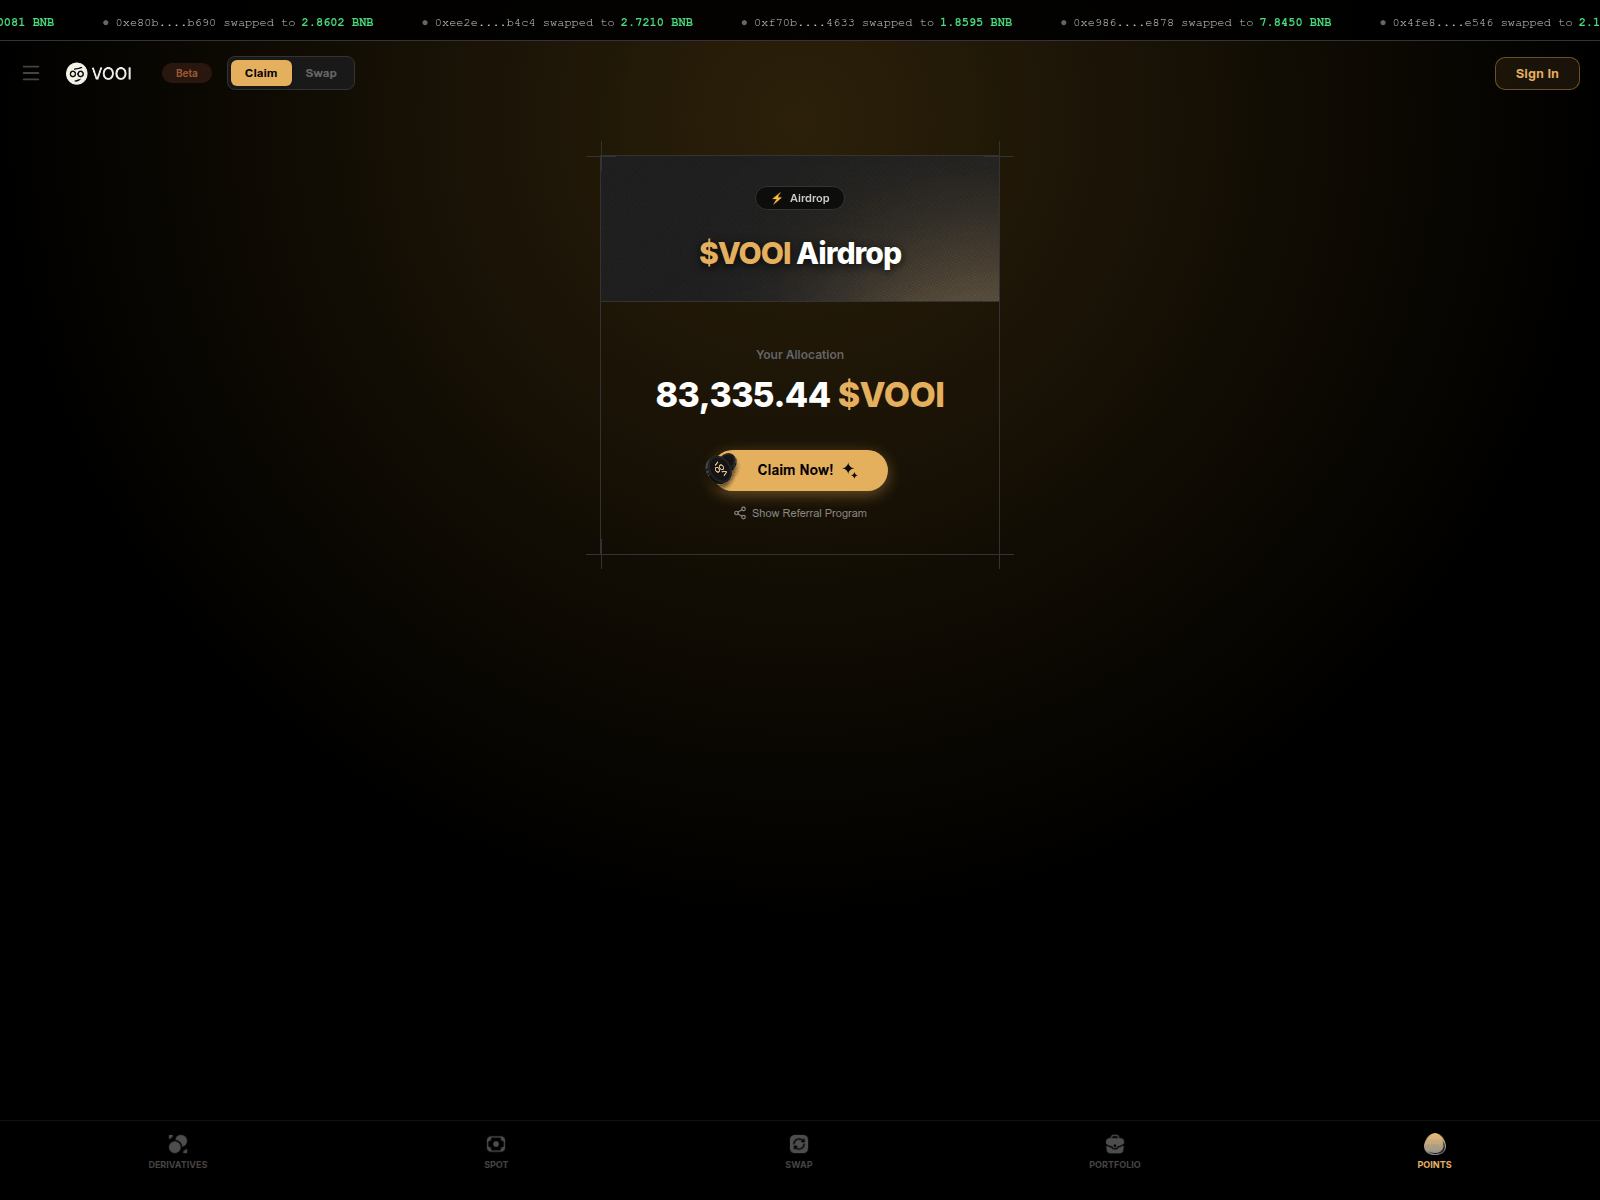
vooi.quest

vote-trillions.info
votes-cypher.com

voting-predi.app
voting-vibestr.com

voting-zoras.xyz

walletanalise.com
walletconnect-demo.sunmoney.net

walletconnect-launchpadprotocol002f.vercel.app

walletconnect.burnghost.com

webauth.com

worldlibertycommunity.com

wr.jcy100.com

www-reya.xyz

zigchain.mom

zoobit-bnb.org
Pipeline de resposta a ameaças
Como cada domínio neste hub é verificado e como as ameaças confirmadas são neutralizadas. Visualização completa do pipeline →
Verificações de inteligência contra ameaças— cada domínio é verificado e comparado com:
urlscan.ioCaptura de tela · DOM · HTTPVirusTotal90+ AV enginesGoogle Safe BrowsingTransparency RelatórioCloudflare RadarDNS · certs · categoriesAlienVault OTXThreat-intel pulsesWayback MachineHistorical evidenceabuse.ch ThreatFoxIOC correlationcrt.shCertificate TransparencyDNS Segurança FiltersQuad9 · AdGuard · CleanBrowsingWeb-VerificarFull surface scan
 crt.sh
Sincronização Global de Fornecedores— as detecções confirmadas são enviadas a 29 parceiros:
GoogleSafe BrowsingGoogleWeb Risk APIMicrosoftSmartScreenVirusTotalDetection feedCloudflareRadar / 1.1.1.1YandexSafe BrowsingURLScan.ioPublic scanESETWebGuardBitdefenderThreat exchangeNortonSafe WebSymantecAvaliação do siteAviraCloud detectionAvast / AVGWeb ShieldKasperskyOpenTIPDr.WebOnline scannerNetcraftRemoção APIPhishTankVerified voteAPWG eCXBulk feedPhishStatsOpen feedPhish.RelatórioHosting abuseSpamhausDBL feedPolySwarmMarketplaceCheckPhishBolster scanQutteraMalware scanURLquerySandboxCriminal IPAsset intelCRDFThreat CenterScamadviserTrust scoreMyWOTWeb of Trust