Ir para o relatório de segurança
Segurança de domínio e inteligência contra ameaças
188betguanfang.com favicon

188betguanfang.com

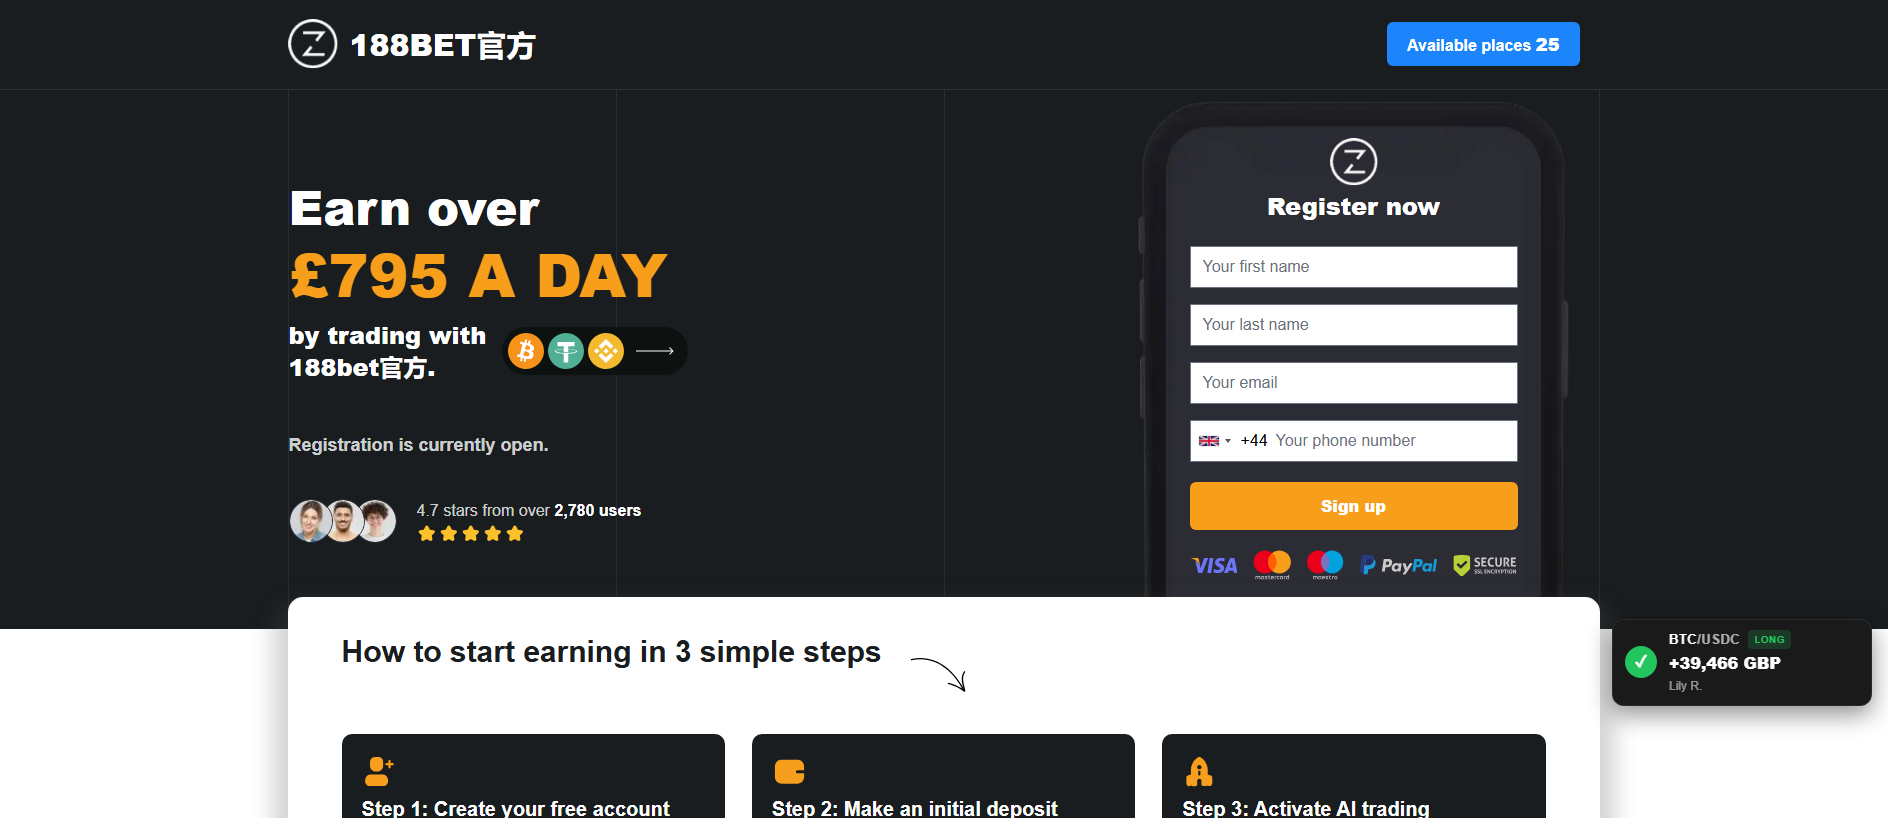
“188bet官方 — 智能AI平台助力自动化定投决策”

Registrador
DYNADOT
Resolved IP
104.21.93.215
Registered
03/10/2026
PhishDestroy assessment Crítico
Disponibilidade Último ativo conhecido Última observação de acessibilidade armazenada Observado · HTTP probe
Detecções do VirusTotal: 15/92 Domínio jovem: 17 dias atrás
OTX: 1 ref 19/10/2026 1 Report Sent CDN
API
Este domínio foi sinalizado como malicioso
Mecanismos de segurança relatando uma detecção: 15. Tenha extremo cuidado – não insira credenciais ou informações pessoais.
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
Domain age
Reports sent
view timeline
Resumo do relatório

Phishing: 188betguanfang.com — Último ativo conhecido (HTTP 200). Resumo das evidências: VirusTotal 15/92 (alphaMountain.ai, BitDefender, CRDF, CyRadar…

A análise detalhada do PhishDestroy AI permanece em inglês para preservar o registro forense original.

Source evidenceVirusTotal 15 / 92 · OTX 1 references 6 sources

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Inteligência de segurança de rede
CF Cloudflare Radar Verdict Malicioso
Security threats Malware Malware

Analysis

Crítico
VirusTotal
15 / 92
OTX
1 community ref
Page captures
3

PhishDestroy threat report

Overview

PhishDestroy has listed 188betguanfang.com as a suspicious domain in its internal blocklist. The domain was first observed by PhishDestroy on 2026-10-19.

How the scam works

No specific malicious scheme has been identified for this domain; the presence on a blocklist and multiple security detections indicate potential risk. Visitors should treat any request for credentials, payments, or personal information from this site as untrusted.

Evidence

VirusTotal reported 15 detections from 92 scanning engines, with vendors such as BitDefender, ESET and Fortinet flagging the site; the results were retrieved on 2026-10-19 and analyzed on 2026-10-14. Google Safe Browsing checked the domain on 2026-10-19 and did not flag it. PhishDestroy’s internal blocklist includes the domain, while external blocklists checked on the same date reported none, and OTX listed one pulse referencing the domain.

Infrastructure

The domain was registered on 2026-10-03 through Dynadot Inc. The recorded IP address associated with the site is 104.21.93.215.

What to do

Do not enter login credentials, payment details, or personal data on this site; if you have already done so, change affected passwords and monitor accounts for unusual activity. Security teams should add 188betguanfang.com to their deny lists and review logs for any connections to the recorded IP address. Continue to monitor reputable threat feeds for any updates on this domain.

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list View source

Captura armazenada · 3 captures

Domain details

Domínio
URLScan verdict Análise concluída score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden A reputação do Edge-IP não é atribuída a este domínio.
Registrador DYNADOT US(US)
Contato para abusosabuse@dynadot.com
Registro da ICANNICANN Lookup (RDAP) →
RegistroCriado 03/10/2026 (17d · Very New!) — Expires 03/10/2027
Status HTTP200
Detalhes técnicosProvenance & timestamps
Detectado pela primeira vez19/10/2026
DOM Analysisanalyzed 20/10/2026score 98/100
Submitted URLhttp://188betguanfang.com/
Favicon Hash
ID do caso
Observed page title
188bet官方 — 智能AI平台助力自动化定投决策
Certificado TLS
Emitido por Let's Encrypt / YE2 · stored validity ends in 72 days

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
104.21.93.215
Network ASN
AS13335
Organization
Cloudflare, Inc.
Observed location
San Francisco, US
Server header
cloudflare

A reputação do Edge-IP não é atribuída a este domínio.

Servidores de nomes 2

  • jaxson.ns.cloudflare.com
  • naya.ns.cloudflare.com

Location describes the IP network.

Certificado TLS

Issuer
Let's Encrypt / YE2
Valid from
2026-10-03 04:26:05
Valid until
2027-01-01 04:26:04
Validity
Within stored validity dates
Collection time
2026-10-19 22:02:04 UTC
Collection source
PhishDestroy collector
Certificate fingerprintdddc0ea70d9f3a9de7d8baee9efcecfa8a73288dae775279831fa16c1dd28ab5

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-19 23:03:05 UTC

Primary outcome Conteúdo ativo reason: Ordinary HTTP content served 90% confidence
Attribution source: Current Http Probe
Evidence layers Availability: Content serving Content: Content served at root DNS: Resolved Registration: Unknown
Latest HTTP observation Conteúdo ativo Ordinary HTTP content served 90% 2026-10-19 23:03:05 UTC
RDAP registration Desconhecido
Observed timeline last reachable: 2026-10-19 23:03:05 UTC last content: 2026-10-19 23:03:05 UTC
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
Casino / Gambling License Verification
Unverified gambling license
This domain markets casino/gambling services. Scam casinos routinely display fake Curaçao, MGA, or Kahnawake license badges that don’t exist in the real registries. Always verify the license number against the official regulator database before depositing. If the site shows a seal but no clickable registry link — or the linked registry page doesn’t exist — treat it as fraudulent.
Curaçao eGaming (official) Malta Gaming Authority UK Gambling Commission PA Gaming Control Kahnawake Gaming Gibraltar Gambling
Tecnologias · 5 identified
Detected via Cloudflare Radar · Wappalyzer engine
Denunciar este domínio Envie evidências e ajude a proteger outras pessoas

Análise do VirusTotal

15 / Os fornecedores de segurança 92 sinalizaram este domínio
View on VT
Last analyzed
alphaMountain.ai
BitDefender
CRDF
CyRadar
DNS8
ESET
Forcepoint ThreatSeeker
Fortinet
G-Data
Gridinsoft
Kaspersky
Netcraft
SOCRadar
Sophos
VIPRE

Evidências arquivadas

Wayback Machine Snapshot
Um instantâneo histórico está disponível para revisão de evidências
View Archive
Análise de desempenho do site

Google PageSpeed Insights — mobile performance audit of 188betguanfang.com · checked Oct 19, 2026

98
Good
Performance
FCP
1.71s
First Contentful Paint
LCP
1.95s
Largest Contentful Paint
CLS
0
Cumulative Layout Shift
TBT
0ms
Total Blocking Time
SI
2.44s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Stored Capture Evidence 1 snapshot

Timestamped response metadata retained by the local collection pipeline. Each value below belongs to the displayed archive time.

Archived HTTP response HTTP 200
Requested URL: http://188betguanfang.com/
Final URL: https://188betguanfang.com/
Resposta
HTTP 200
HTML body
1.2 KB
Compressed
697 B
Links
0 internal · 0 external
Detected technologies
cloudflare
Selected response headers
Content-Type: text/html; charset=utf-8
CF-Cache-Status: DYNAMIC
Cache-Control: no-cache, no-store, must-revalidate
Server: cloudflare
X-Powered-By: Express
Content-Encoding: gzip
Security headers present
X-Content-Type-OptionsReferrer-Policy
HSTS: not observed DNSSEC: not observed WAF / firewall: observed Cloaking flag: not observed
Saved response-header values · 18
alt-svc
h3=":443"; ma=86400
Cache-Control
no-cache, no-store, must-revalidate
CF-Cache-Status
DYNAMIC
CF-Ray
a4d25d9219833749-GRU
Connection
keep-alive
Content-Encoding
gzip
Content-Type
text/html; charset=utf-8
Date
Mon, 19 Oct 2026 19:59:50 GMT
Nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
Referrer-Policy
same-origin
Report-To
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=b8kkLpaGkgFb1z5HhN6Sw0gnRtPYr1OAJSbHxJq654qYCbOvqAKnWfJHjltakBtu%2B6EQAyZYDr91v8Bu%2FLSdnbZu0rOxIwT1n%2BiZUTCD%2BGH6oRHRdHCV4FrNfaRgeAp6kJLyGcW
Server
cloudflare
Server-Timing
cfCacheStatus;desc="DYNAMIC"
Transfer-Encoding
chunked
Vary
Accept-Encoding
Via
1.1 Caddy
X-Content-Type-Options
nosniff
x-powered-by
Express

Values retained by the collector; long values may be shortened during collection.

Registration & observation details3

Availability observations

Last reachable observation
Last content observation
Estimate basis
Currently reachable

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Stored observation history2

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    Desconhecido→live_content

    content_served

  2. Availability monitor · First collection record

    Acessível

Recorded activity

6 entries
  1. Abuse report sent

    PD-20261019-671CCC

    abuse@dynadot.com
  2. URLScan

    Page captured

    View source
  3. AlienVault OTX

    1 community references

    View source
  4. Google Safe Browsing

    No threat flag

    View source
  5. VirusTotal

    15/92 engine detections

    View source
  6. Added to PhishDestroy

    188betguanfang.com

    View source

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

188betguanfang.com

Evidências e relatórios externos

Instantâneo das evidências enviadas
Sent: Ledger records: 1 Case ID: PD-20261019-671CCC Recipient: abuse@dynadot.com
PDF notice generated Notice text archived (291 chars)
Abuse notice text as sent to the provider
Registrar: Dynadot LLC / Dynadot Inc (United States)
Policy Violations: Acceptable Use forbids illegal content; Spam & Abuse Policy prohibits phishing, fraud, malware; Dynadot may disable DNS and suspend domains
Applicable Laws: CFAA 18 U.S.C. §1030, Wire Fraud 18 U.S.C. §1343, CAN-SPAM Act
Análise aprofundada
Help & reporting

Você foi afetado por este site?

6 evidence signal groups linked 1 stored notification records Último ativo conhecido
If credentials were compromised, report immediately. Do not engage with recovery scammers.

Se você inseriu credenciais de conta, informações pessoais ou de pagamento, ou baixou um arquivo deste domínio, tome medidas imediatas. Abaixo estão os recursos para ajudá-lo a relatar o incidente e se proteger.

Official reporting routes

Cuidado com os golpistas que prometem recuperação! Os criminosos podem entrar em contato novamente com as vítimas fingindo ser investigadores, advogados ou agentes de recuperação. Não pague taxas antecipadas nem compartilhe credenciais. Saiba mais sobre fraudes relacionadas à recuperação →

Notifique as autoridades locais

Selecione seu país para obter contactos oficiais do cibercrime ou crie um rascunho de reclamação →.

Diretório de 97 países

Template-based draft · optional AI wording assistance requires separate consent

Rascunho assistido por IA – os detalhes do incidente são processados pelo provedor de IA · Revise e envie você mesmo
After a phishing incident

Recomendações e orientações para as vítimas

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

O que devo fazer agora mesmo?

Urgente

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • Alterar todas as senhas — e-mail, contas do Exchange, qualquer coisa que use a mesma senha
  • Ativar a autenticação de dois fatores usando um aplicativo autenticador (não por SMS). Desative a recuperação por SMS
  • Cartões de congelamento se você inseriu dados bancários no site de phishing

Que informações devo coletar para o meu relatório?

Diretrizes do FBI

Keep original emails, receipts, messages and screenshots in a secure place. A factual timeline helps the receiving authority understand what happened. IC3 evidence guidance ↗

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • Datas e horários exatos — de cada transação e do primeiro contato com o golpista
  • Capturas de tela — sites fraudulentos, mensagens de bate-papo, e-mails, transações em carteiras digitais, redes sociais
  • Todas as URLs e domínios utilizado pelo golpista (incluindo 188betguanfang.com)
  • Comunicações — e-mails, mensagens de texto, números de telefone e nomes de usuário que o golpista utilizou

Mesmo que você não tenha todos os detalhes — registre uma ocorrência mesmo assim. Mesmo informações parciais ainda ajudam nas investigações.

A quem devo denunciar o golpe?

  • FBI IC3 — Centro de Denúncias de Crimes na Internet (sistema federal de denúncias dos EUA)
  • Europol — Relatórios sobre crimes cibernéticos na Europa (UE)
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • Polícia local — cria um registro oficial, mesmo que não possam agir imediatamente

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

How do phishing scams typically work?

  • Sites falsos — clones idênticos, até o último pixel, de sites legítimos, com domínios ligeiramente alterados
  • Abate de suínos — confiança construída ao longo de semanas pelo Telegram, WhatsApp e aplicativos de namoro; em seguida, o dinheiro foi roubado
  • Golpes relacionados à recuperação — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • Golpes baseados em IA — deepfakes, phishing automatizado e sites gerados por IA, o que torna a fraude mais difícil de detectar

Como posso me proteger no futuro?

  • Adicione os sites oficiais aos favoritos — nunca clique em links de e-mails, mensagens diretas ou anúncios
  • Verificar domínios — verificar PhishDestroy antes de interagir. Verifique se o site usa HTTPS, a ortografia e a idade do domínio
  • "Bom demais para ser verdade" = golpe — retornos garantidos, endossos de celebridades, prazos urgentes

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

Mantenha-se informado, mantenha-se seguro

Monitore ameaças em tempo real ou conteste esta listagem caso acredite que se trate de um falso positivo

Feed de ameaças em tempo real Recorrer deste anúncio
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

Incorporar este relatório

Compartilhe essas informações sobre ameaças em seu site ou blog

embed.html
<iframe
  src="https://phishdestroy.io/pt-br/embed/domain/188betguanfang.com"
  title="PhishDestroy threat report for 188betguanfang.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>