VirusTotal
15 / 89 engine detections
보고서 열기

enam.co.za: Adobe 사칭. PhishDestroy가 2026-09-07에 탐지했습니다. 위험도: 심각 (98/100). 등록 대행자: 1-Grid. 상태: 연결 가능 · 액세스가 제한됨. 호스팅: DIMENOC - HostDime.com, Inc., US. VirusTotal: 엔진 15/89개가 탐지. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.
“403 Forbidden”
Adobe 사칭: enam.co.za — 연결 가능 · 액세스가 제한됨 (HTTP 403). 증거 요약: VirusTotal 15/89 (alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker); URLScan…
원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.
15 / 89 engine detections
보고서 열기악성
보고서 열기4 community references
보고서 열기provider verdict: clean
보고서 열기위협 플래그 없음
보고서 열기결과는 각 출처의 수집 시점을 기준으로 합니다. 탐지 0건이 안전을 보장하지는 않습니다. OTX 참조는 커뮤니티 게시물입니다.
PhishDestroy threat report
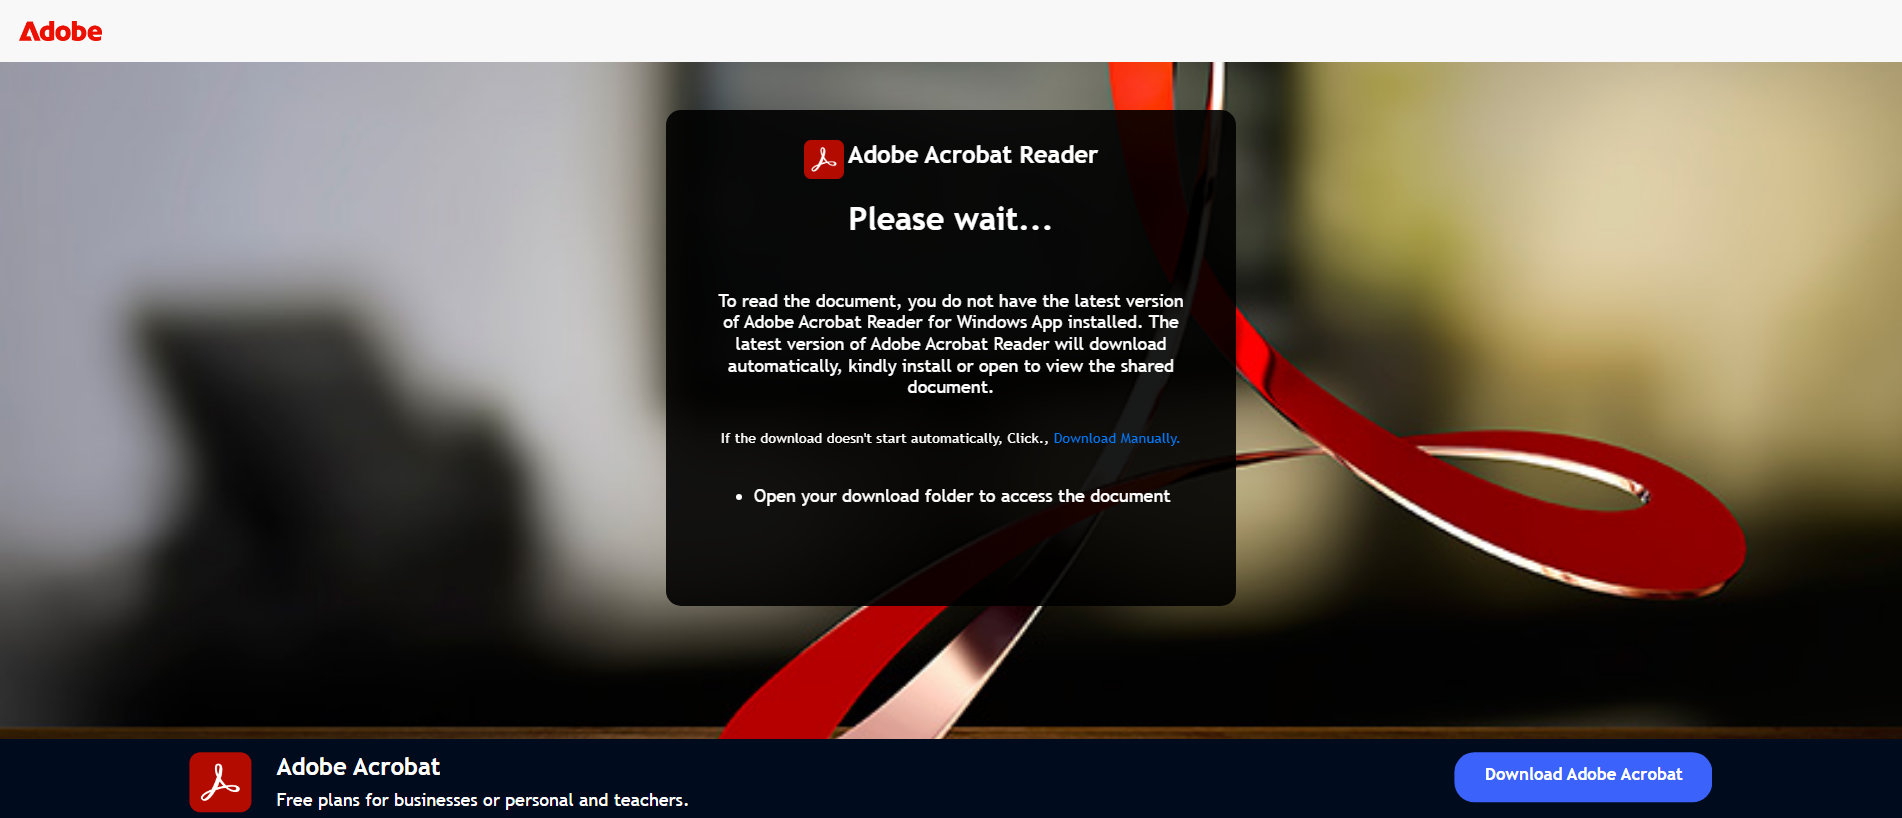
enam.co.za is a South African domain that PhishDestroy classifies as an impersonation phishing page posing as Adobe. It targets people who expect an Adobe sign-in or shared-document prompt and are willing to type in their credentials. PhishDestroy first flagged it on 2026-09-07, and as of 2026-10-19 the site was still online, with its content reachable but access-restricted. The page currently presents the title "403 Forbidden", while our classification and independent scans identify Adobe-branded phishing content on the domain.
Adobe lures typically arrive as an email or message saying a document, invoice or PDF has been shared with you. The link leads to a page styled after Adobe's branding that asks you to log in to view the file. Anything entered there, whether an Adobe ID, a work email password or a Microsoft or Google login offered as an alternative, goes straight to the operators. Stolen mailbox access is then commonly reused for invoice fraud, further phishing from your address, or password resets on other accounts.
On 2026-09-18, 15 of 89 VirusTotal engines flagged the domain. The vendors included alphaMountain.ai, BitDefender, CRDF, ESET, Forcepoint ThreatSeeker, Fortinet, G-Data and Gridinsoft, a spread of independent security vendors that points the same way. urlscan.io returned a malicious verdict and specifically recognised Adobe branding on the page, which supports the impersonation classification. The domain also appears in four AlienVault OTX threat pulses and is listed on the PhishDestroy blocklist.
The domain was registered on 2015-02-04 through 1-Grid, more than eleven years before it surfaced as phishing. That makes it an established name rather than a freshly registered throwaway, so its age alone should not be read as a sign of trust. It resolves to 41.185.8.216 on HostDime's network, with the server located in South Africa. Its Let's Encrypt certificate only means the connection is encrypted and says nothing about who runs the site.
If you entered credentials on this site, change the Adobe password right away, along with the password for any email account you used. Change it on every other service where you reused that password. Turn on two-factor authentication and review your mailbox for forwarding rules or recovery details you did not set up. Also warn colleagues who may have received the same "shared document" message. Defenders should block the domain and its IP at the mail gateway and web proxy, and search mail logs for links to it to identify exposed users.
저장된 페이지, 네트워크, 스캐너 관측 결과를 출처와 관측 시각별로 묶어 보여 줍니다.
관측됨: · Retrieved:
| Uuid | 01a07944-c109-75fb-9d21-00936b8a401a |
|---|---|
| Final url | https://sabcleaningnyc.com/SWG/en/index.html |
| 상태 | 200 |
| 리디렉션됨 | off-domain |
| Redirects | [
{
"to": "https://enam.co.za/",
"from": "http://enam.co.za/",
"status": 307
},
{
"to": "https://sabcleaningnyc.com/SWG/en/index.html",
"from": "https://enam.co.za/",
"status": 301
}
] |
| Ip | 200.7.107.81 |
| Ptr | server.siscomtec.com |
| Contacted domains | [
"pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev",
"maxcdn.bootstrapcdn.com",
"code.jquery.com",
"ajax.googleapis.com",
"enam.co.za"
] |
| Contacted IP addresses | [
"2606:4700:311b::6812:3222",
"104.18.11.207",
"2a04:4e42::411",
"2a00:1450:4001:c17::5f",
"200.7.107.81",
"41.185.8.216"
] |
| Asns | [
"13335",
"54113",
"15169",
"33182",
"36943"
] |
| Countries | [
"US",
"DE",
"CO",
"ZA"
] |
| Linked domains | [
"pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev"
] |
| Document hash | a70069694d95ef852dc20b6f52fcd2f80d36a4b936d89b2b49605a06e4c93360 |
| Globals | [
"$",
"jQuery"
] |
| Tls | {
"san": [
"*.sabcleaningnyc.com",
"sabcleaningnyc.com"
],
"cipher": "AES_128_GCM",
"issuer": "YR2",
"subject": "*.sabcleaningnyc.com",
"protocol": "TLS 1.3",
"valid_to": "2026-10-30T15:30:51Z",
"valid_from": "2026-08-01T15:30:52Z"
} |
| 도메인 연령(일) | 580 |
| Apex age days | 580 |
| Tls age days | 36 |
| TLS 유효 일수 | 89 |
| Requests | 10 |
| Provider verdicts | {
"engines": {
"tags": [
"urlscan-ml",
"urlscan-ml-60c5e22"
],
"score": 95,
"malicious": true
},
"overall": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"adobe"
],
"malicious": true,
"categories": [
"phishing"
]
},
"urlscan": {
"tags": [
"phishing"
],
"score": 100,
"brands": [
"Adobe"
],
"malicious": true,
"categories": [
"phishing"
]
}
} |
| HTTP headers | {
"server": "Apache",
"content-type": "text/html"
} |
관측됨: · Retrieved:
| Uuid | d3d628a0-2f0a-4753-9ef2-0924ac92f116 |
|---|---|
| Final url | https://pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev/ESign_Acrobat_Update.exe |
| 상태 | 200 |
| 리디렉션됨 | off-domain |
| History | [
{
"url": "http://enam.co.za/",
"status": 307
},
{
"url": "https://enam.co.za/",
"status": 301
},
{
"url": "https://sabcleaningnyc.com/SWG/en/index.html",
"status": 307
},
{
"url": "http://enam.co.za/",
"status": 301
},
{
"url": "https://sabcleaningnyc.com/SWG/en/index.html",
"status": 200
},
{
"url": "https://pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev/ESign_Acrobat_Update.exe",
"status": 200
}
] |
| DOM structure hash | 928889293afa7452cc604703e7760fa29d3da555ad52c5c48a25fb709f885ec8 |
| Document hash | a70069694d95ef852dc20b6f52fcd2f80d36a4b936d89b2b49605a06e4c93360 |
| Phishing v2 | [
"phishing"
] |
| Radar rank | {
"bucket": ">200000"
} |
| DNS 레코드 | [
{
"name": "pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev",
"type": "A",
"value": "104.18.54.45"
},
{
"name": "pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev",
"type": "A",
"value": "104.18.50.34"
},
{
"name": "pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev",
"type": "AAAA",
"value": "2606:4700:311b::6812:362d"
},
{
"name": "pub-4a59abe59ba64218a3f5b7b3ec5ae5ed.r2.dev",
"type": "AAAA",
"value": "2606:4700:311b::6812:3222"
}
] |
| DNSSEC 유효 | false |
| Ip | 104.18.54.45 |
| 등록 기록 | {
"registrar": "CloudFlare, Inc.",
"created": "2022-08-23T14:38:38Z",
"updated": "2026-05-31T12:00:41Z",
"expires": "2027-08-23T14:38:38Z",
"nameservers": [
"camilo.ns.cloudflare.com",
"raphaela.ns.cloudflare.com"
]
} |
아니요. PhishDestroy는 enam.co.za을(를) Adobe 사칭(으)로 분류합니다(위험도: 심각, 98/100). 처음 탐지된 날짜는 2026-09-07입니다. VirusTotal: 엔진 15/89개가 탐지. 안전하지 않은 사이트로 취급하세요.
아니요. enam.co.za에서 지갑을 연결하거나 메시지에 서명하거나 토큰을 승인하지 마세요. 피싱 사이트는 운영자가 자산을 옮길 수 있게 하는 승인(approve, setApprovalForAll, Permit2)을 요청하며, 확정된 거래는 되돌릴 수 없습니다.
그곳에 입력한 모든 비밀번호를 바꾸고 2단계 인증을 켜세요. 지갑을 연결했거나 무언가에 서명했다면 승인을 취소하고 남은 자금을 새 지갑으로 옮기세요. 시드 문구는 절대 공유하지 마세요. 단계별 안내: 긴급 대응 가이드.
linus.ns.1-grid.co.uklinus.ns.1-grid.co.zalinus.ns.1-grid.comlinus.ns.1-grid.net1-grid-mx01.co.zapriority 51-grid-mx03.co.zapriority 51-grid-mx04.compriority 51-grid-mx02.compriority 5위치는 IP 네트워크 기준입니다.
9a3c8d4dda917f5c3b60a7846a77a27cbc3b6883009d3984864d15cec518a66b*.sabcleaningnyc.comsabcleaningnyc.com저장된 인증서 메타데이터입니다. 시간대 정보가 없는 인증서 날짜는 저장된 그대로 표시됩니다. 전송 구간 암호화가 사이트의 신뢰성을 입증하지는 않습니다.
추정 시각은 관측 구간을 나타냅니다. 레지스트라의 조치나 사이트가 접속 불가 상태가 된 정확한 시점을 입증하지는 않습니다.
브라우저와 크롤러가 받는 응답을 비교하고 Keitaro 트래픽 라우팅 여부를 확인합니다.
captcha: raw=captcha; http=403; via=https_proxy; server=Caddy, BitNinja Captcha Server
enam.co.za
모니터와 출처 수집기가 보관한 날짜별 변경 기록입니다. 최신 관측이 먼저 표시되며, 출처 상태가 테이크다운을 입증하지는 않습니다.
알 수 없음→protected
captcha · challenge
알 수 없음→protected
captcha · challenge
알 수 없음→protected
captcha · challenge
알 수 없음→protected
captcha · challenge
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
captcha · challenge
알 수 없음→protected
captcha · challenge
알 수 없음→protected
captcha · challenge
알 수 없음→protected
captcha · challenge
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
captcha · challenge
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
captcha · challenge
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
http_access_restricted · access_restriction
알 수 없음→protected
http_access_restricted · access_restriction
protected
http_access_restricted · access_restriction
9→14
8→9
7→8
접속 가능
각 레인은 도메인이 이 호스트에 연결된 이유 중 하나를 나타냅니다. 노드의 크기는 VirusTotal 탐지 건수를 나타내며, 점선으로 표시된 노드는 이미 오프라인 상태입니다. 전체 목록은 아래와 같습니다.
이 호스트와 동일한 파비콘 해시이거나 동일한 페이지 제목을 가진 경우.
동일한 수집기 레이블이 붙은 보고서입니다. 레이블이 같다고 해서 사칭이나 동일 소유가 입증되지는 않습니다. 일치하는 보고서 보기 →
동일한 등록 기관을 통해 등록되었습니다. 등록 기관은 서로 관련이 없는 수백만 명의 고객을 상대하기 때문에, 이는 두 항목 간의 연관성을 입증하기보다는 단순히 보고를 묶어놓은 것에 불과합니다.
등재된 도메인에 대해서는 최소 1건의 악용 신고가 발송되지만, 이 항목에는 보관된 통지 기록이 없습니다.
계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.
공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.
Template-based draft · optional AI wording assistance requires separate consent
공유한 정보에 해당하는 조치를 선택하세요. 이 보고서 사본을 본인의 기록과 함께 보관하세요.
의심스러운 사이트 사용을 중단하세요. 실제 서비스는 공식 앱이나 이미 신뢰하는 주소를 통해 접속하세요.
원본 이메일, 영수증, 메시지, 스크린샷을 안전한 곳에 보관하세요. 사실에 기반한 시간순 기록은 접수 기관이 경위를 파악하는 데 도움이 됩니다. IC3 evidence guidance ↗
enam.co.za)비록 모든 세부 사항을 알지 못하더라도 — 어쨌든 신고를 하세요. 부분적인 정보라도 수사에 도움이 됩니다.
Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams
이 보고서는 저장된 페이지 캡처, 등록 및 네트워크 기록, 스캐너 결과, PhishDestroy 신고 이력을 종합한 것입니다. 각 출처는 고유한 관측일을 유지합니다. 원본 결과를 확인하려면 출처 보고서를 여세요.
AI 지원 분석 작성 시각: . 이 분석은 작성 당시 확보된 증거를 설명하며, 이후 출처 확인 결과는 달라질 수 있습니다.
캡처는 당시 표시된 내용을 기록한 것입니다. 스캐너 결과는 검사 시점의 해당 제공업체 평가를 기록한 것입니다. 유효한 인증서나 탐지 0건 결과 모두 안전을 보장하지 않습니다.