보안 보고서로 이동
도메인 보안 및 위협 인텔리전스
breachrbh.com 파비콘

breachrbh.com

요약

breachrbh.com: American express 사칭.

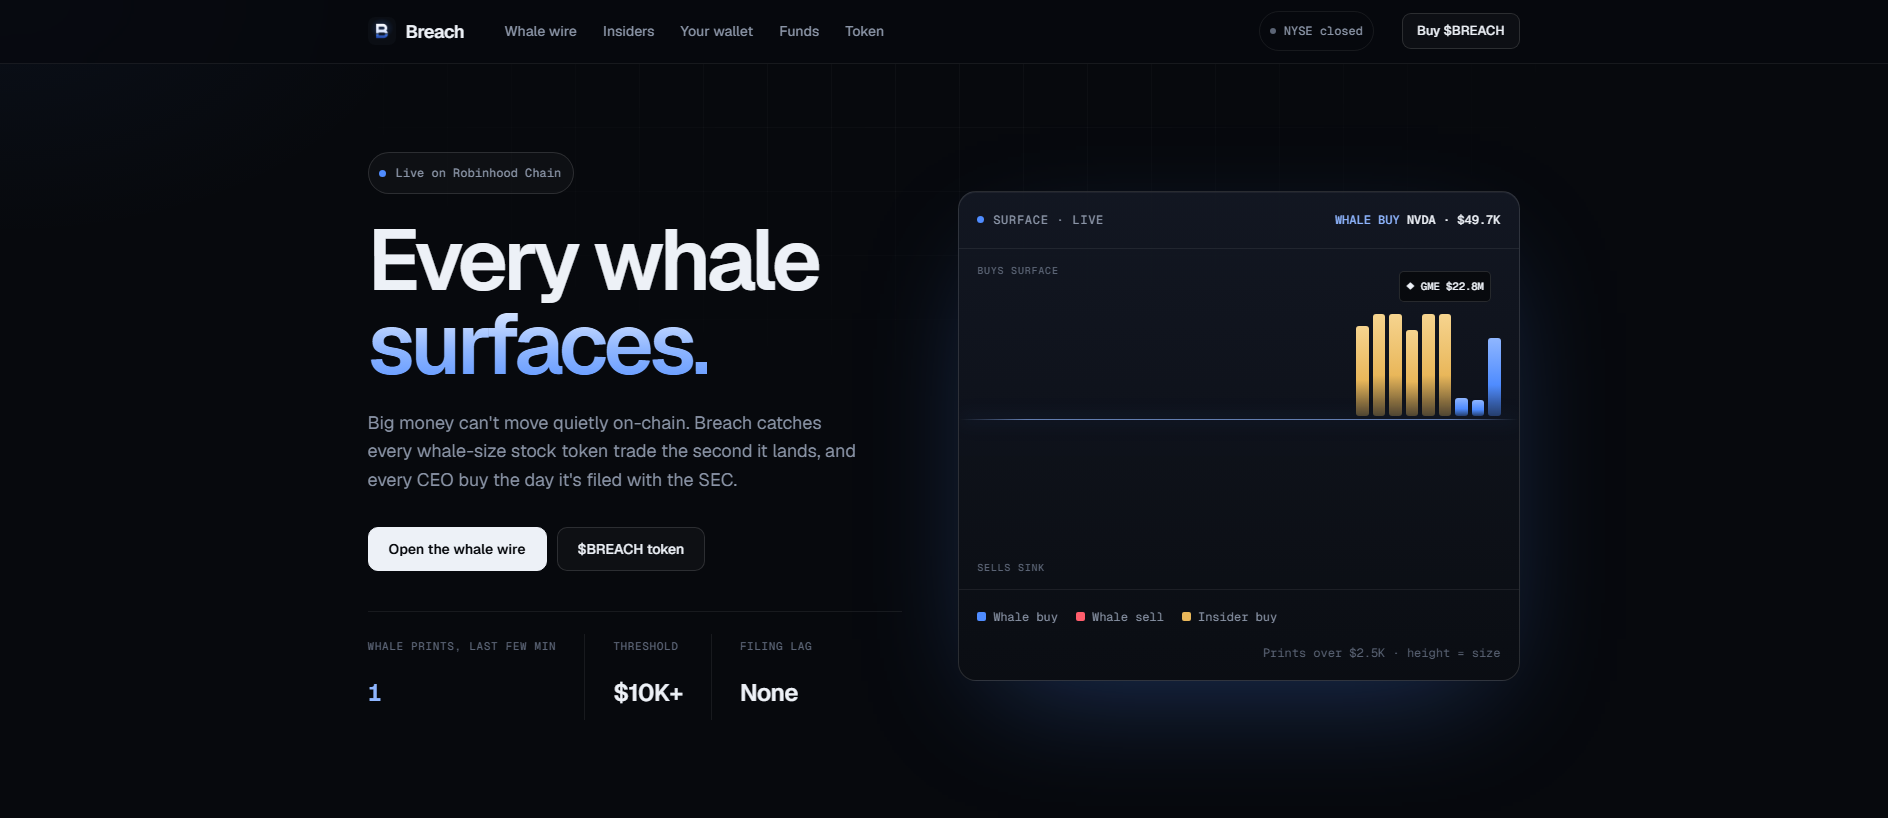
“Breach — every whale surfaces”

등록기관
NiceNIC
Resolved IP
188.114.96.3
Registered
2026년 10월 22일
PhishDestroy assessment 심각
가용성 마지막으로 알려진 활성 최근에 저장된 도달 가능성 관찰 관측됨 · HTTP probe
Spamhaus DBL: DBL_SPAM 자동 브랜드 라벨: American express 젊은 도메인: 2일 전
VirusTotal
engine detections ·
OTX
community references
Cloudflare Radar
source verdict
페이지 캡처
갤러리 열기
도메인 연령
발송된 신고
No sent record
2026년 10월 25일 CDN
API
이 도메인은 악성 도메인으로 표시되었습니다.
PhishDestroy 법의학 분석에서 이 도메인에 플래그를 지정했습니다. 극도의 주의를 기울이십시오 — 자격 증명이나 개인 정보를 입력하지 마십시오.
보고서 요약

American express 사칭: breachrbh.com — 마지막으로 알려진 활성 (HTTP 200). 증거 요약: VirusTotal 0/92; URLScan capture; Spamhaus DBL_SPAM; PhishDestroy score 100/100. 등록기관…

원본 포렌식 기록을 보존하기 위해 아래의 상세 PhishDestroy AI 분석은 영어로 유지됩니다.

Analysis

Domain summary

breachrbh.com: American express 사칭. PhishDestroy가 2026-10-25에 탐지했습니다. 위험도: 심각 (100/100). 등록 대행자: NiceNIC. 상태: 마지막으로 알려진 활성. 호스팅: CloudFLARENET-EU. Spamhaus DBL에 등재. 로그인 정보를 입력하거나 지갑을 연결하지 마세요.

심각
VirusTotal
0 / 92
페이지 캡처
4

PhishDestroy threat report

Overview

PhishDestroy’s intake AI classified breachrbh.com as malicious because the site mimics Robinhood and markets a “Breach” token that claims to track whale‑size stock token trades, presenting a “Connect wallet” or “Check” button. The domain was first observed by PhishDestroy on 2026-10-25, three days after its registration on 2026-10-22.

How the scam works

In this type of scheme the attacker copies a well‑known brand’s look and name to lend credibility, then offers a token or investment that appears exclusive or high‑value. By prompting visitors to connect a crypto wallet, the attacker can request token approvals or transfer permissions, enabling potential fund drainage without any on‑site transaction.

Evidence

The page title recorded as “Breach — every whale surfaces” and the excerpt describing a “Breach” token on a “Robinhood Chain” match the impersonation concern. VirusTotal scanned the domain on 2026-10-25 with 92 engines and reported zero detections. Google Safe Browsing checked the same day and did not flag the URL. Urlscan captured a clean verdict on 2026-10-23, and OTX listed no pulses. PhishDestroy’s internal blocklist marks the domain as malicious while external blocklists returned no hits.

Infrastructure

The domain was registered on 2026-10-22 through NICENIC INTERNATIONAL GROUP CO., LIMITED and is protected by Cloudflare’s CDN, resolving to IPv4 188.114.96.3/188.114.97.3 and IPv6 2a06:98c1:3121::3. TLS is provided by a Let’s Encrypt certificate valid until 2027-01-20. The registrar record shows client‑delete and client‑transfer prohibitions, and the hosting network is identified as CloudFLARENET‑EU in Great Britain.

What to do

Visitors should avoid clicking the “Connect wallet” button and never approve any transaction on the site. Organizations should block breachrbh.com at DNS or proxy level, add it to threat feeds, and review logs for connections to the recorded IP addresses.

출처 증거VirusTotal 0 / 92 8 sources

Cloudflare Radar

Suspicious

기록 없음
보고서 열기
Cloudflare RadarOriginal source recordRetrieved: 12 fields

관측됨: · Retrieved:

Uuid
490f660c-059d-4828-b7dc-ba76f8efe27b
Final url
https://breachrbh.com/
상태
200
History
[
    {
        "url": "https://breachrbh.com/",
        "status": 200
    }
]
DOM structure hash
54f5ad9c3bd99b50b66490def235ad4c5e1cba97d7b39eda7a95f2a6a5694c05
Document hash
38778622720e18d05f13f244a9ffee8d71afb1d74cceca881d9aeee97013e87a
도메인 위험 요소
[
    "Newly Seen Domains",
    "Security Risks",
    "New Domains"
]
Radar rank
{
    "bucket": ">200000"
}
DNS 레코드
[
    {
        "name": "breachrbh.com",
        "type": "A",
        "value": "104.21.55.2"
    },
    {
        "name": "breachrbh.com",
        "type": "A",
        "value": "172.67.143.193"
    },
    {
        "name": "breachrbh.com",
        "type": "AAAA",
        "value": "2606:4700:3033::6815:3702"
    },
    {
        "name": "breachrbh.com",
        "type": "AAAA",
        "value": "2606:4700:3034::ac43:8fc1"
    }
]
DNSSEC 유효
false
Ip
104.21.55.2
등록 기록
{
    "registrar": "NICENIC INTERNATIONAL GROUP CO., LIMITED",
    "created": "2026-10-22T20:51:06Z",
    "updated": "2026-10-22T20:51:07Z",
    "expires": "2027-10-22T20:51:06Z",
    "nameservers": [
        "archer.ns.cloudflare.com",
        "zainab.ns.cloudflare.com"
    ]
}

Spamhaus DBL

DBL_SPAM

VirusTotal

0 / 92 engine detections · stored summary

보고서 열기
VirusTotalOriginal source recordRetrieved: 13 fields

관측됨: · Retrieved:

Vendor result counts
{
    "timeout": 0,
    "harmless": 55,
    "malicious": 0,
    "suspicious": 0,
    "undetected": 37
}
Reputation
0
등록기관
NICENIC INTERNATIONAL GROUP CO., LIMITED
생성됨
2026-10-22T20:51:07Z
Expires
2027-10-22T20:51:06Z
Updated
2026-10-22T20:51:07Z
최초 발견
2026-10-22T21:01:28Z
DNS 레코드
[
    {
        "ttl": 1800,
        "type": "SOA",
        "rname": "dns.cloudflare.com",
        "value": "archer.ns.cloudflare.com"
    },
    {
        "ttl": 300,
        "type": "A",
        "value": "172.67.143.193"
    },
    {
        "ttl": 300,
        "type": "AAAA",
        "value": "2606:4700:3033::6815:3702"
    },
    {
        "ttl": 300,
        "type": "A",
        "value": "104.21.55.2"
    },
    {
        "ttl": 300,
        "type": "AAAA",
        "value": "2606:4700:3034::ac43:8fc1"
    },
    {
        "ttl": 21600,
        "type": "NS",
        "value": "archer.ns.cloudflare.com"
    },
    {
        "ttl": 21600,
        "type": "NS",
        "value": "zainab.ns.cloudflare.com"
    }
]
Dns at
2026-10-25T08:48:53Z
Jarm
27d40d40d00040d1dc42d43d00041d6183ff1bfae51ebd88d70384363d525c
Certificate
{
    "san": [
        "*.breachrbh.com",
        "breachrbh.com"
    ],
    "issuer": "Let's Encrypt / YE1",
    "serial": "63d647d576aa1763423815cc925d21387cf",
    "sha256": "52c1de6c1de7d8cecd621d84dfc7e6223ebea4d341043a350bc0230137a12bc6",
    "subject": "breachrbh.com",
    "valid_to": "2027-01-20T19:56:55Z",
    "valid_from": "2026-10-22T19:56:56Z"
}
등록 기록
{
    "registrar": "NICENIC INTERNATIONAL GROUP CO., LIMITED",
    "registrar_iana_id": "3765",
    "registrar_url": "https://nicenic.com",
    "created": "2026-10-22T20:51:06Z",
    "updated": "2026-10-22T20:51:07Z",
    "expires": "2027-10-22T20:51:06Z",
    "status": [
        "clientDeleteProhibited",
        "clientTransferProhibited"
    ],
    "nameservers": [
        "archer.ns.cloudflare.com",
        "zainab.ns.cloudflare.com"
    ],
    "dnssec": "unsigned"
}
Registry data
{
    "status": [
        "client delete prohibited",
        "client transfer prohibited"
    ],
    "events": {
        "expiration": "2027-10-22T20:51:06Z",
        "registration": "2026-10-22T20:51:07Z",
        "registrar expiration": "2027-10-22T20:51:06Z",
        "last update of RDAP database": "2026-10-22T20:51:07Z"
    }
}
Separate source record · 0 malicious + 0 suspicious / 92 · 2026-10-25 08:36:15 UTC

The summary above and this provider record were collected at different times. Both remain available; malicious and suspicious classifications are shown separately.

record_source
collected_observations.vt
analysis_at
2026-10-25T08:36:15Z
fetched_at
2026-10-25T08:51:37Z
stats
{"timeout":0,"harmless":55,"malicious":0,"suspicious":0,"undetected":37}

URLScan

페이지 캡처

보고서 열기
URLScanOriginal source recordRetrieved: 20 fields

관측됨: · Retrieved:

Uuid
01a17247-3947-727f-8468-a1ebb2b84a55
Final url
https://breachrbh.com/
상태
200
Ip
172.67.143.193
Contacted domains
[
    "rpc.mainnet.chain.robinhood.com",
    "fonts.gstatic.com",
    "static.cloudflareinsights.com",
    "fonts.googleapis.com"
]
Contacted IP addresses
[
    "104.20.46.209",
    "104.16.80.73",
    "142.251.16.94",
    "142.250.217.10",
    "172.67.143.193"
]
Asns
[
    "13335",
    "15169"
]
Countries
[
    "US"
]
Linked domains
[
    "ponsfamily.com",
    "robinhoodchain.blockscout.com",
    "www.sec.gov",
    "x.com"
]
Social
[
    "https://x.com/intent/post",
    "https://x.com/breach_rbh"
]
Document hash
38778622720e18d05f13f244a9ffee8d71afb1d74cceca881d9aeee97013e87a
Globals
[
    "BREACH_CONFIG",
    "BREACH_DATA",
    "changeLabel",
    "tokenChip",
    "allocation",
    "renderBrand",
    "renderStats",
    "renderTabs",
    "renderFund",
    "renderAlloc",
    "renderMoves",
    "renderInsiders",
    "loadData",
    "initInsiders",
    "marketState",
    "startMarketClock",
    "seedBreach",
    "copy",
    "init",
    "encodeAggregate3",
    "decodeAggregate3",
    "ethCalls",
    "loadHoldings",
    "overlap",
    "renderScore",
    "check",
    "connect",
    "renderVote",
    "loadResults",
    "castVote",
    "chain",
    "refreshPrices",
    "classify",
    "readRange",
    "markFlippers",
    "visibleEvents",
    "renderWhaleStats",
    "renderWhales",
    "renderWhaleControls",
    "pollWhales"
]
Tls
{
    "san": [
        "*.breachrbh.com",
        "breachrbh.com"
    ],
    "cipher": "AES_128_GCM",
    "issuer": "YE1",
    "subject": "breachrbh.com",
    "protocol": "QUIC",
    "valid_to": "2027-01-20T19:56:55Z",
    "valid_from": "2026-10-22T19:56:56Z"
}
도메인 연령(일)
2
Apex age days
2
Tls age days
2
TLS 유효 일수
89
Requests
38
Provider verdicts
{
    "engines": {
        "tags": [
            "urlscan-ml",
            "urlscan-ml-60c5e22"
        ],
        "score": 96,
        "malicious": true
    },
    "overall": {
        "score": 0,
        "malicious": false
    }
}
HTTP headers
{
    "server": "cloudflare",
    "content-type": "text/html",
    "x-powered-by": "PleskLin"
}
Separate monitor record · date not recorded

Separate stored monitor snapshot; does not replace the primary report record or establish current availability.

record_source
domain_monitor.urlscan
uuid
01a1668b-7c24-7445-be8e-c69cbdb2ed1c
score
null
malicious
null
result_at
null
enriched_at
2026-10-25T09:10:44Z
source_timestamps
{"urlscan_result_at":null,"urlscan_enriched_at":"2026-10-25 10:10:44"}
timestamp_basis
Europe/Berlin, as used by the existing report; source timestamps are retained verbatim

PhishDestroy DOM

100 / 100 · heuristic score · 10 brand references · 1 classifications

보고서 열기

PhishDestroy narrative

Narrative generation metadata

보고서 열기
Title, description and generation record

The narrative generation date is separate from observation dates. These are the retained publication fields, not an additional independent detection.

ai_title
breachrbh.com — Robinhood Impersonation Scam
ai_description
PhishDestroy flagged breachrbh.com as malicious for impersonating Robinhood and promoting a fraudulent “Breach” token that asks users to connect wallets.
ai_generated_at
2026-10-25T08:56:24Z
ai_generated_by
threat-v3-groq
interpretation
Narrative generation metadata, separate from provider observation dates.

결과는 각 출처의 수집 시점을 기준으로 합니다. 탐지 0건이 안전을 보장하지는 않습니다. OTX 참조는 커뮤니티 게시물입니다.

수집된 출처 세부 정보

저장된 페이지, 네트워크, 스캐너 관측 결과를 출처와 관측 시각별로 묶어 보여 줍니다.

Every stored field, with its source and date
Website checksOriginal source recordRetrieved: 25 fields
Mail configuration
{
    "spf_lookups": 0
}
CAA 레코드
{
    "domain": "breachrbh.com"
}
Protective DNS results
{
    "resolvers": 12,
    "blocked_count": 0
}
Web archive observations
{
    "last": "2026-10-25T08:49:18Z",
    "first": "2026-10-25T08:49:18Z",
    "changes": 0,
    "days_archived": 1,
    "avg_page_bytes": 139630
}
페이지 제목 및 메타데이터
{
    "title": "Breach — every whale surfaces",
    "ogTitle": "Breach — every whale surfaces",
    "description": "Breach watches Robinhood Chain and the SEC at once: every whale-size stock token trade the second it lands, and every CEO buy the day it is filed.",
    "twitterCard": "summary",
    "ogDescription": "Live whale trades of stock tokens on Robinhood Chain, plus insider and fund filings from the SEC."
}
Trackers
{
    "requests": 6,
    "trackers": [
        {
            "name": "Google Fonts",
            "company": "Google",
            "country": "US",
            "category": "Hosting",
            "requests": 1
        },
        {
            "name": "Google Static",
            "company": "Google",
            "country": "US",
            "category": "Hosting",
            "requests": 2
        }
    ]
}
양식 및 혼합 콘텐츠
{
    "third_party_scripts": 0
}
상태
{
    "up": true,
    "code": 200,
    "timings": {
        "dns": 14,
        "tls": 63,
        "wait": 152,
        "connect": 6,
        "download": 119
    },
    "response_ms": 354
}
TLS connection
{
    "alpn": "h2",
    "cipher": "TLS_AES_256_GCM_SHA384",
    "protocol": "TLSv1.3",
    "versions": [
        "TLSv1",
        "TLSv1.1",
        "TLSv1.2",
        "TLSv1.3"
    ],
    "authorized": true,
    "forward_secrecy": true
}
Ports
{
    "open": [
        80,
        443,
        8080
    ]
}
Carbon
{
    "bytes": 398515,
    "co2_grams": 0.0146,
    "cleaner_than": 1
}
Dns server
{
    "ns": [
        {
            "ip": "162.159.44.136",
            "host": "archer.ns.cloudflare.com"
        },
        {
            "ip": "162.159.38.149",
            "host": "zainab.ns.cloudflare.com"
        }
    ],
    "zone": "breachrbh.com"
}
Location
{
    "ip": "2a06:98c1:3121::3",
    "asn": "13335",
    "org": "CloudFLARENET-EU",
    "city": "London",
    "country": "GB"
}
Ssl
{
    "issuer": "Let's Encrypt / YE1",
    "subject": "breachrbh.com"
}
DNS 레코드
{
    "A": [
        "188.114.96.3",
        "188.114.97.3"
    ],
    "NS": [
        "archer.ns.cloudflare.com",
        "zainab.ns.cloudflare.com"
    ],
    "SOA": "{\"nsname\": \"archer.ns.cloudflare.com\", \"hostmaster\": \"dns.cloudflare.com\", \"serial\": 2418391231, \"refresh\": 10000, \"retry\": 2400, \"expire\": 604800, \"minttl\": 1800}",
    "AAAA": [
        "2a06:98c1:3121::3",
        "2a06:98c1:3120::3"
    ]
}
Dnssec
{
    "ds": false,
    "rrsig": false,
    "dnskey": false
}
Hsts
{
    "message": "Site does not serve any HSTS headers."
}
HTTP security policies
{
    "xFrameOptions": false,
    "referrerPolicy": false,
    "xXSSProtection": false,
    "permissionsPolicy": false,
    "xContentTypeOptions": false,
    "contentSecurityPolicy": false,
    "strictTransportPolicy": false,
    "crossOriginOpenerPolicy": false,
    "crossOriginEmbedderPolicy": false,
    "crossOriginResourcePolicy": false
}
Firewall
{
    "waf": "Cloudflare",
    "has_waf": true
}
Get ip
{
    "ip": "2a06:98c1:3121::3",
    "family": 6
}
Redirects
{
    "chain": [
        "https://breachrbh.com"
    ]
}
하위 도메인
{
    "count": 1,
    "subdomains": [
        "www.breachrbh.com"
    ]
}
Page links
{
    "internal_count": 6
}
등록 기록
{
    "registrar": "NICENIC INTERNATIONAL GROUP CO., LIMITED",
    "created": "2026-10-22T20:51:06Z",
    "updated": "2026-10-22T20:51:07Z",
    "expires": "2027-10-22T20:51:06Z",
    "status": [
        "clientDeleteProhibited https://icann.org/epp",
        "clientTransferProhibited https://icann.org/epp"
    ],
    "nameservers": [
        "archer.ns.cloudflare.com",
        "zainab.ns.cloudflare.com"
    ]
}
HTTP headers
{
    "headers": {
        "server": "cloudflare",
        "content-type": "text/html",
        "x-powered-by": "PleskLin"
    }
}
네트워크 보안 인텔리전스 레지스트라 관련 정보
레지스트라 관련 정보 NiceNIC
Stored registration data identifies NICENIC INTERNATIONAL GROUP CO., LIMITED (IANA 3765) as the registrar. PhishDestroy maintains separate NiceNIC abuse-report research; registrar association is contextual and is not an independent detection for this domain.
NiceNIC Verdict Full Investigation

breachrbh.com 관련 질문

breachrbh.com은(는) 정상적인 사이트인가요?

아니요. PhishDestroy는 breachrbh.com을(를) American express 사칭(으)로 분류합니다(위험도: 심각, 100/100). 처음 탐지된 날짜는 2026-10-25입니다. Spamhaus DBL에 등재. 안전하지 않은 사이트로 취급하세요.

breachrbh.com에 지갑을 연결해도 안전한가요?

아니요. breachrbh.com에서 지갑을 연결하거나 메시지에 서명하거나 토큰을 승인하지 마세요. 피싱 사이트는 운영자가 자산을 옮길 수 있게 하는 승인(approve, setApprovalForAll, Permit2)을 요청하며, 확정된 거래는 되돌릴 수 없습니다.

breachrbh.com을(를) 이용했다면 어떻게 해야 하나요?

그곳에 입력한 모든 비밀번호를 바꾸고 2단계 인증을 켜세요. 지갑을 연결했거나 무언가에 서명했다면 승인을 취소하고 남은 자금을 새 지갑으로 옮기세요. 시드 문구는 절대 공유하지 마세요. 단계별 안내: 긴급 대응 가이드.

더 보기

Blocklist matchesPhishDestroy 1
PhishDestroy PhishDestroy list 출처 보기

저장된 캡처 · 캡처 4개

All capture links and hashes (4)

도메인 상세 정보

도메인
IP Context Cloudflare shared edge origin IP hidden Edge-IP 평판은 이 도메인에 귀속되지 않습니다.
등록기관 NiceNIC RU(RU) PhishDestroy Investigation
악용 신고 연락처abuse@nicenic.net
ICANN 레지스트리ICANN Lookup (RDAP) →
등록 정보생성됨 2026년 10월 22일 (2d · Brand New!) — Expires 2027년 10월 22일
HTTP 상태200
기술 세부 정보Provenance & timestamps
최초 발견2026년 10월 25일
DOM Analysisanalyzed 2026년 10월 25일score 100/10010 brand signals
Submitted URLhttps://breachrbh.com/
Favicon Hash
Observed page title
Breach — every whale surfaces
Automated brand references
Across Amazon American Express Apple Chainlink Chase Microsoft Morpho +2
TLS 인증서
발급자 Let's Encrypt / YE1 · 저장된 유효 기간이 87일 후 만료

네트워크 & 인증서

저장된 기술 증거

네트워크 & DNS

Shared CDN edge
Resolved IP
188.114.96.3
네트워크 ASN
AS13335
Organization
CloudFLARENET-EU
Observed location
London, GB
Server header
cloudflare

Edge-IP 평판은 이 도메인에 귀속되지 않습니다.

네임서버 2

  • archer.ns.cloudflare.com
  • zainab.ns.cloudflare.com

위치는 IP 네트워크 기준입니다.

TLS 인증서

Issuer
Let's Encrypt / YE1
유효 기간 시작
2026-10-22 19:56:56
유효 기간 만료
2027-01-20 19:56:55
Hostname coverage
저장된 인증서 날짜 기준 유효
Validity
저장된 유효 기간 내
수집 출처
PhishDestroy collector
인증서 지문52c1de6c1de7d8cecd621d84dfc7e6223ebea4d341043a350bc0230137a12bc6
인증서 이름 · SAN 2개
  • *.breachrbh.com
  • breachrbh.com

저장된 인증서 메타데이터입니다. 시간대 정보가 없는 인증서 날짜는 저장된 그대로 표시됩니다. 전송 구간 암호화가 사이트의 신뢰성을 입증하지는 않습니다.

Recorded subdomains1

Hostnames retained in the domain record or Certificate Transparency cache. A hostname alone does not establish current availability or malicious activity.

  • www.breachrbh.comDomain record

The original observation time is not recorded for these hostnames.

기술 · 4 identified
Detected via Cloudflare Radar · Wappalyzer engine
이 도메인 신고하기 증거를 제출하고 다른 사람들을 보호하는 데 힘을 보태주세요

보관된 증거

Wayback Machine Snapshot
아카이브 보기
사이트 성능 분석

Google PageSpeed Insights — 다음 도메인의 모바일 성능 감사: breachrbh.com · checked Oct 25, 2026

87
Needs Work
Performance
FCP
3.16 s
콘텐츠가 포함된 첫 페인트
LCP
3.16 s
Largest Contentful Paint
CLS
0.006
Cumulative Layout Shift
TBT
0 ms
Total Blocking Time
SI
3.43 s
Speed Index
데이터 제공: Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
저장된 캡처 증거 1 snapshot

로컬 수집 파이프라인이 보관한 타임스탬프 포함 응답 메타데이터입니다. 아래의 각 값은 표시된 아카이브 시각을 기준으로 합니다.

Archived HTTP response HTTP 200
Requested URL: https://breachrbh.com/
Breach — every whale surfaces
Breach watches Robinhood Chain and the SEC at once: every whale-size stock token trade the second it lands, and every CEO buy the day it is filed.
대응
HTTP 200
HTML body
389.5 KB
Compressed
134.8 KB
Links
8 internal · 0 external
Detected technologies
vuecloudflare
Selected response headers
Content-Type: text/html
Server: cloudflare
X-Powered-By: PleskLin
CF-Cache-Status: DYNAMIC
Content-Encoding: gzip
HSTS: 관측되지 않음 DNSSEC: 관측되지 않음 WAF / firewall: observed 클로킹 플래그: 관측되지 않음
Open Graph 제목: Breach — every whale surfaces
Open Graph 설명: Live whale trades of stock tokens on Robinhood Chain, plus insider and fund filings from the SEC.
Twitter card: summary
Saved response-header values · 15
alt-svc
h3=":443"; ma=86400
cf-cache-status
DYNAMIC
CF-RAY
a4fff6ac8eb871ff-YYZ
Connection
keep-alive
Content-Encoding
gzip
Content-Type
text/html
Date
Sun, 25 Oct 2026 08:48:40 GMT
Last-Modified
Thu, 22 Oct 2026 21:33:16 GMT
Nel
{"report_to":"cf-nel","success_fraction":0.0,"max_age":604800}
Report-To
{"group":"cf-nel","max_age":604800,"endpoints":[{"url":"https://a.nel.cloudflare.com/report/v4?s=%2Ff%2BgSrSDLTs0FlIq1FEjGC%2BxtB4opq5nM6kEZZUGBLnqy1tCDSOs8V4JHEdC05bNghFMOObO%2B9%2F%2BFBsP2nUh2X4rQRrdZV%2BndTJb67sd81z%2BBvpuOZ5y0GWf51S2jLj
Server
cloudflare
Server-Timing
cfCacheStatus;desc="DYNAMIC"
Transfer-Encoding
chunked
Vary
accept-encoding
X-Powered-By
PleskLin

수집기가 보관한 값입니다. 긴 값은 수집 과정에서 축약될 수 있습니다.

All retained availability observations1

Source: availability monitor. Every retained observation remains separate, including records with the same date or evidence hash but different sources or DNS states. An unknown state is not proof that the site is offline.

  1. current_state_backfillunknown
    Observation source
    current_state_backfill
    원인
    stale_current_evidence
    Availability state
    unknown
    Content state
    unknown
    DNS state
    stale
    Registration state
    unknown
    RDAP statuses
    []
    Recorded actor type
    unknown
    Monitor confidence
    0
    Provider action verified
    false
    Registrar mechanism verified
    false
    Linked to a report
    false
    Original source timestamp
    2026-10-25 09:54:03.296450
    증거 SHA-256
    f3049ef8aa957a0c75d1f37b703ae6008630522768f5aca88bbd9915c9e1400b
    DNS evidence marked stale
    true
    HTTP evidence marked stale
    true

기록된 활동

4 entries
  1. URLScan

    Page captured

    출처 보기
  2. VirusTotal

    0/92 engine detections

    출처 보기
  3. 웨이백 머신

    Page archived

    출처 보기
  4. PhishDestroy에 등록됨

    breachrbh.com

    출처 보기

클로킹 확인

브라우저와 크롤러가 받는 응답을 비교하고 Keitaro 트래픽 라우팅 여부를 확인합니다.

breachrbh.com

증거 및 외부 보고서

심층 분석
Help & reporting

이 사이트로 인해 영향을 받으셨나요?

2 개의 증거 신호 그룹 연결됨 마지막으로 알려진 활성
계정 정보가 유출되었다면 즉시 신고하세요. 피해 복구를 빙자한 사기범에게 응하지 마세요.

계정 자격 증명, 개인 정보 또는 결제 정보를 입력했거나 이 도메인에서 파일을 다운로드한 경우 즉시 조치를 취하세요. 다음은 사건을 신고하고 자신을 보호하는 데 도움이 되는 리소스입니다.

지역 당국에 신고하십시오

공식 사이버 범죄 연락처 또는 불만사항 초안 작성 →를 받으려면 국가를 선택하세요.

97개국 디렉토리

AI 지원 초안 - 사고 세부정보는 AI 제공업체에서 처리됩니다.

직접 검토하고 제출하세요.
After a phishing incident

피해자를 위한 권고 사항 및 조언

공유한 정보에 해당하는 조치를 선택하세요. 이 보고서 사본을 본인의 기록과 함께 보관하세요.

지금 당장 어떻게 해야 할까요?

긴급

의심스러운 사이트 사용을 중단하세요. 실제 서비스는 공식 앱이나 이미 신뢰하는 주소를 통해 접속하세요.

  • 모든 비밀번호 변경 — 이메일, 익스체인지 계정 등, 동일한 비밀번호를 사용하는 모든 것
  • 2단계 인증 활성화 인증 앱(SMS 제외)을 사용합니다. SMS 기반 복구 기능을 비활성화하세요.
  • 카드 동결 피싱 사이트에 은행 계좌 정보를 입력한 경우

보고서를 작성하기 위해 어떤 정보를 수집해야 할까요?

FBI 지침

원본 이메일, 영수증, 메시지, 스크린샷을 안전한 곳에 보관하세요. 사실에 기반한 시간순 기록은 접수 기관이 경위를 파악하는 데 도움이 됩니다. IC3 evidence guidance ↗

  • 결제 기록 — 결제했다면 영수증, 금액, 날짜, 결제 서비스 및 수취인 정보를 보관하세요.
  • 정확한 날짜 및 시간 — 각 거래 내역 및 사기범과의 첫 접촉 시점
  • 스크린샷 — 사기 웹사이트, 채팅 메시지, 이메일, 지갑 거래, 소셜 미디어
  • 모든 URL 및 도메인 사기꾼이 사용한 (다음과 같은 것들을 포함하여 breachrbh.com)
  • 커뮤니케이션 — 사기꾼이 사용한 이메일, 문자, 전화번호, 사용자 이름

비록 모든 세부 사항을 알지 못하더라도 — 어쨌든 신고를 하세요. 부분적인 정보라도 수사에 도움이 됩니다.

이 사기 사건을 어디에 신고해야 할까요?

  • FBI IC3 — 인터넷 범죄 신고 센터 (미국 연방 신고 창구)
  • 유로폴 — 유럽 사이버 범죄 신고 (EU)
  • Your bank or payment provider — 돈을 송금했거나 카드 정보가 노출되었다면 공식 연락처를 통해 즉시 사기 대응팀에 연락하세요.
  • 지역 경찰 — 비록 당장 조치를 취할 수는 없더라도 공식 기록을 남깁니다

신고한다고 해서 피해 회복이나 수사가 보장되지는 않지만, 신속하고 정확한 거래 데이터는 당국과 서비스 제공업체가 사건을 추적하는 데 도움이 될 수 있습니다.

How do phishing scams typically work?

  • 가짜 웹사이트 — 도메인을 약간만 변경한, 정식 사이트와 픽셀 단위로 완벽하게 일치하는 복제 사이트
  • pig butchering — Telegram·왓츠앱·데이트 앱을 통해 몇 주에 걸쳐 신뢰를 쌓은 뒤, 돈을 훔쳐갔다
  • 회복 사기 — 사기범이 자금 회수 대행업체로 위장해 선불 수수료를 요구합니다. 업체를 독립적으로 확인하기 전에는 절대 시드 구문을 공유하거나 돈을 지불하지 마세요
  • AI를 이용한 사기 — 딥페이크, 자동화된 피싱, AI로 생성된 사이트 등으로 인해 사기 행각을 적발하기가 더 어려워지고 있다

앞으로 어떻게 하면 스스로를 지킬 수 있을까요?

  • 공식 사이트 즐겨찾기 추가 — 이메일, DM 또는 광고에 포함된 링크는 절대 클릭하지 마세요
  • 도메인 확인 — 확인하기 PhishDestroy 상호작용을 시작하기 전에 HTTPS, 맞춤법, 도메인 등록 기간을 확인하세요.
  • "너무 좋아서 믿기 힘들다" = 사기 — 수익 보장, 유명인의 추천, 촉박한 마감 기한

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

최신 정보를 확인하고, 안전을 지키세요

실시간 위협을 모니터링하거나, 오탐이라고 판단될 경우 이 목록에 이의를 제기하십시오.

Official reporting routes

회복 사기꾼들을 조심하세요! 범죄자는 수사관, 변호사, 회복요원인 척 하면서 피해자에게 다시 연락할 수도 있습니다. 선불 비용을 지불하거나 자격 증명을 공유하지 마십시오. 회복 관련 사기에 대해 자세히 알아보기 →
이 보고서 정보출처, 관측일 및 정정 사항

이 보고서는 저장된 페이지 캡처, 등록 및 네트워크 기록, 스캐너 결과, PhishDestroy 신고 이력을 종합한 것입니다. 각 출처는 고유한 관측일을 유지합니다. 원본 결과를 확인하려면 출처 보고서를 여세요.

AI 지원 분석 작성 시각: . 이 분석은 작성 당시 확보된 증거를 설명하며, 이후 출처 확인 결과는 달라질 수 있습니다.

캡처는 당시 표시된 내용을 기록한 것입니다. 스캐너 결과는 검사 시점의 해당 제공업체 평가를 기록한 것입니다. 유효한 인증서나 탐지 0건 결과 모두 안전을 보장하지 않습니다.

이 보고서 삽입증거 링크가 포함된 간단한 위젯
HTML · IFRAME

이 보고서 삽입하기

이 위협 정보를 귀하의 웹사이트나 블로그에 공유하세요

embed.html
<iframe
  src="https://phishdestroy.io/ko/embed/domain/breachrbh.com"
  title="PhishDestroy threat report for breachrbh.com"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>