セキュリティレポートへ移動
ドメインのセキュリティと脅威インテリジェンス
goldangel.lol favicon

goldangel.lol

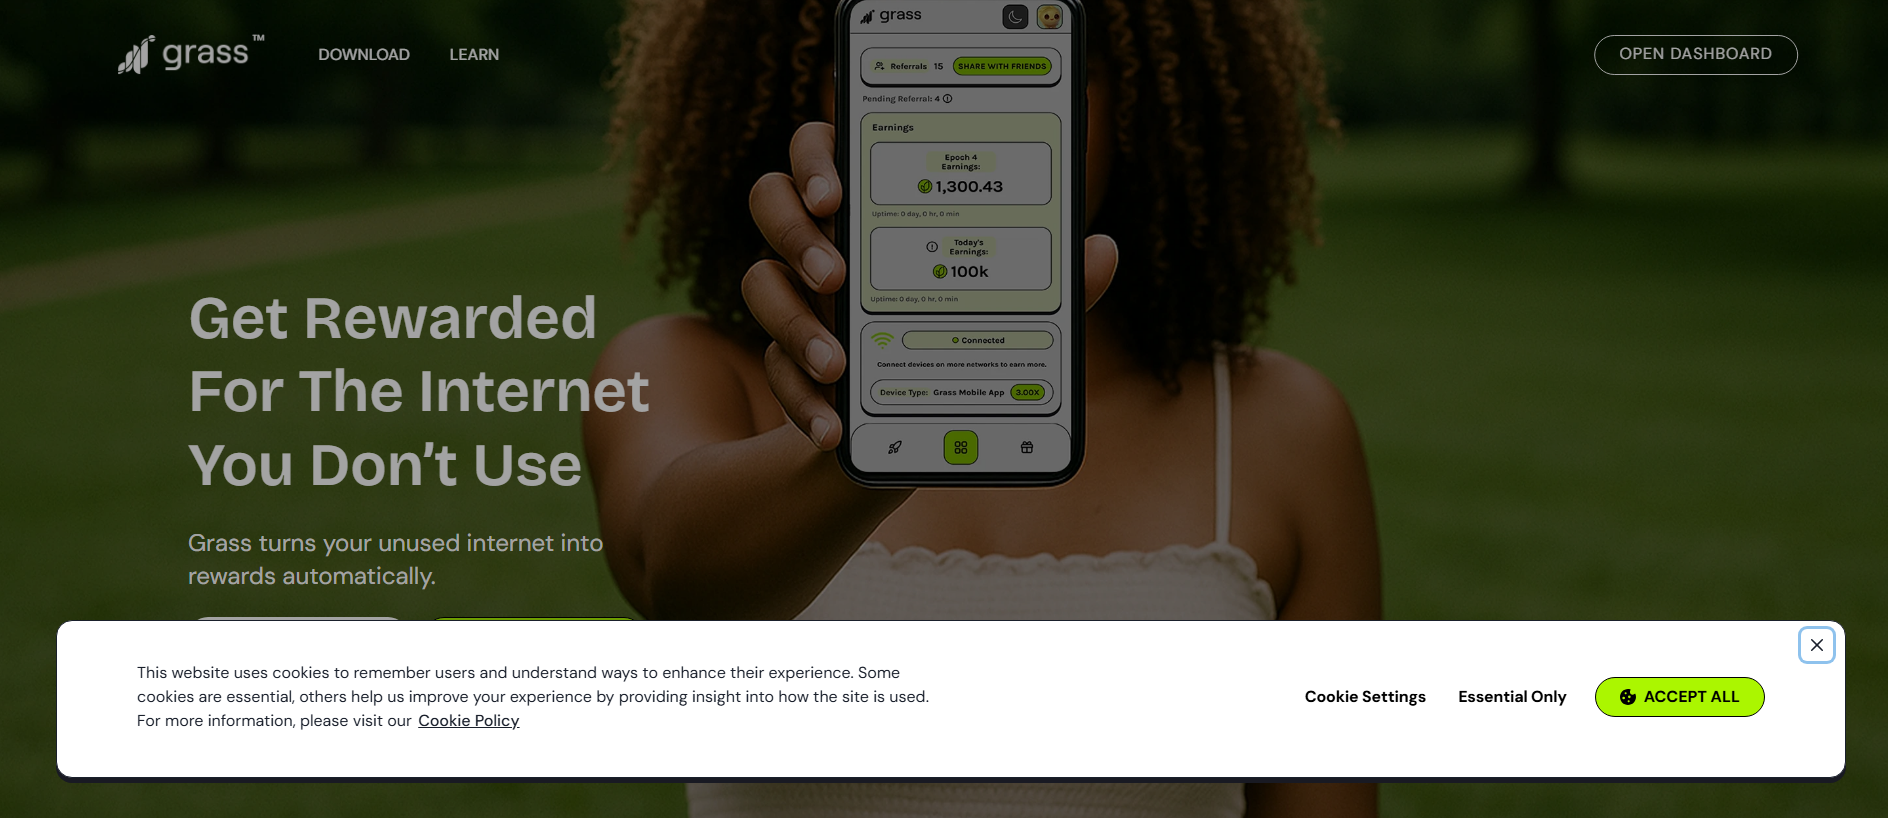
“Get rewarded for the internet you don't use”

レジストラ
Global Domain Group
Resolved IP
188.114.96.3
Registered
2026年9月12日
PhishDestroy assessment クリティカル
可用性 コンテンツが利用できません 最新の観測ではコンテンツが利用できませんでした 観測された · HTTP probe
VirusTotal 検出数: 4/89 保存されたブロックリストの一致: 2 自動ブランドラベル:MetaMask
OTX: 4 refs 2026年9月15日 1 Report Sent CDN
API
このドメインは悪意のあるものとして報告されています
検出を報告するセキュリティ エンジン: 4。 一致を報告する公開ブロックリスト: 2。 細心の注意を払ってください — 資格情報や個人情報を入力しないでください。
VirusTotal
engine detections
Google Safe Browsing
OTX
community references
Page captures
open gallery
Domain age
Reports sent
view timeline
レポート概要

暗号資産ウォレットドレイナー: goldangel.lol — コンテンツが利用できません. 証拠の概要: VirusTotal 4/89 (alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, VIPRE); 2 external blocklist…

元のフォレンジック記録を保持するため、下の PhishDestroy AI 詳細分析は英語のままです。

Source evidenceVirusTotal 4 / 89 · OTX 4 references 6 sources

Results reflect each source’s collection time. Zero detections do not guarantee safety. OTX references are community publications.

Analysis

クリティカル
VirusTotal
4 / 89
OTX
4 community refs
Page captures
3

PhishDestroy threat report

Overview

goldangel.lol is a crypto wallet drainer that ran the Angel Drainer kit, targeting anyone who connected a Web3 wallet to the page. PhishDestroy first detected it on 2026-09-15, three days after the domain was registered on 2026-09-12. The site went offline almost immediately, becoming DNS-inactive by 2026-09-16, and remained dead as of the last check on 2026-10-17. Despite its brief window, it was picked up by multiple threat-intelligence sources before going dark.

How the scam works

The page title — "Get rewarded for the internet you don't use" — presents the site as a passive-income or bandwidth-sharing platform, which conflicts with its classification as a wallet drainer; what the page displayed versus what the kit actually does are two different things. Angel Drainer is a well-documented malicious toolkit that, once a visitor connects their crypto wallet, silently requests sweeping token-approval transactions. Approving those requests hands the drainer contract permission to transfer tokens and NFTs out of the wallet without any further confirmation. Victims typically lose all approved assets within seconds.

Evidence

VirusTotal flagged goldangel.lol on 2026-09-15 with 4 detections out of 89 engines queried; the vendors that flagged it were alphaMountain.ai, Forcepoint ThreatSeeker, Gridinsoft, and VIPRE. While 4 detections is a relatively low count, the specific vendors involved specialize in phishing and malicious-URL detection. The domain also appears in four OTX threat-intelligence pulses and is actively blocked by PhishDestroy, MetaMask, and SEAL, providing independent corroboration of the classification.

Infrastructure

The domain was registered on 2026-09-12 through Global Domain Group LLC and resolved to an IP on Cloudflare's network in Canada. TLS was provisioned through Let's Encrypt, issuer YE2. The combination of a fresh domain, commodity hosting, and a free certificate is consistent with short-lived drainer infrastructure.

What to do

If you visited goldangel.lol and connected a wallet, immediately open a tool such as Revoke.cash or your wallet's built-in approval manager and revoke every token approval granted around that date. If you signed any transaction while on the site, assume all approved assets are at risk and move remaining funds to a new wallet address without delay. Do not reuse the compromised wallet for high-value holdings. Security teams and wallet providers should ensure goldangel.lol and its associated IP are present in their blocklists; the domain is already covered by PhishDestroy, MetaMask, and SEAL.

Blocklist matchesMetaMask · PhishDestroy · SEAL 3
MetaMask 掲載あり View source
PhishDestroy PhishDestroy list View source
SEAL 掲載あり View source

Last checked

保存済みキャプチャ · 3 captures

Observed page title
Get rewarded for the internet you don't use
Automated brand references
Foundation
TLS証明書
発行者 Let's Encrypt / YE2 · stored validity ends in 52 days

Domain details

ドメイン
URLScan verdict 分析完了 score 0 report ↗
IP Context Cloudflare shared edge origin IP hidden Edge-IP の評判はこのドメインに起因しません。
OTX tags 2026-09activeall-domainsblocklistcontentcryptoドメインdrainerfraudlivemonthlyphishdestroyphishingscam
レジストラ Global Domain Group (Unknown)
不正利用連絡先abuse@globaldomaingroup.com
ICANNレジストリICANN Lookup (RDAP) →
登録情報作成日 2026年9月12日 (37d · New) — Expires 2027年9月12日
初回利用不能までの時間 9h
集計対象 最初に保存された不正使用レポートから、コンテンツが利用できないことが最初に観察されるまでの経過時間。これでは原因は特定されません。
各レポートの内容 保存された送信レポートの記録は、ベンダーの評決、登録データ、ホスティングの詳細、分類、スクリーンショットなど、その時点で入手可能な証拠を参照する場合があります。このページは、配信された正確なペイロード、受信者による受信、確認、またはアクションを推測するものではありません。
技術詳細Provenance & timestamps
初確認2026年9月15日
DOM Analysisanalyzed 2026年9月15日score 100/1001 brand signal
Submitted URLhttp://goldangel.lol/
Favicon Hash
ケース ID
ICANN OVERSIGHT

認定と RAA の背景

Registrar accreditation and DNS abuse obligations

For this gTLD, the registrar above operates under an ICANN accreditation agreement. The links below provide the official fee schedule and current DNS abuse compliance guidance.

Accreditation is a contract, not a safety certification.

RAA §3.18 establishes abuse-contact and handling requirements. This report can document stored outbound notices and later technical observations; it does not by itself establish receipt, investigation, remediation, or contractual non-compliance.

Accountability draft 自動送信は一切行われません。

Network & certificates

Stored technical evidence

Network & DNS

Shared CDN edge
Resolved IP
188.114.96.3
Network ASN
AS13335
Organization
CloudFlare, Inc.
Observed location
Toronto, CA
Server header
cloudflare

Edge-IP の評判はこのドメインに起因しません。

ネームサーバー 2

  • jacob.ns.cloudflare.com
  • lina.ns.cloudflare.com

Location describes the IP network.

TLS証明書

Issuer
Let's Encrypt / YE2
Valid from
2026-09-12 21:14:40
Valid until
2026-12-11 21:14:39
Validity
Within stored validity dates
Collection time
2026-09-15 16:02:05 UTC
Collection source
PhishDestroy collector
Certificate fingerprintf7dbe2a0424660b49bd9299ebeb08f0f165bef38215b9ea48e4c8e2c2a0fd2e5

Saved certificate metadata. Certificate dates without a timezone are shown as stored. Transport encryption does not establish that the site is trustworthy.

Latest Classified Outcome 2026-10-20 08:21:37 UTC

Primary outcome DNS 非アクティブ reason: DNS NXDOMAIN 80% confidence
Attribution source: Dns Cache
Evidence layers Availability: DNS inactive Content: Unreachable DNS: NXDOMAIN Registration: Unknown
Latest HTTP observation 不明 Probe Inconclusive 20% 2026-10-19 01:14:01 UTC
RDAP registration 不明
Observed timeline last reachable: 2026-09-15 22:17:58 UTC current episode first observed: 2026-09-30 16:14:55 UTC observed RIP window: 2026-09-15 22:17:58 UTC → 2026-09-30 16:14:55 UTC · 353.95h midpoint estimate ≈ 2026-09-23 07:16:26 UTC · precision low · basis bounded
Availability, content, DNS and registration are independent evidence layers. NXDOMAIN, an unreachable origin or missing content alone does not prove registrar action. A registrar or provider is credited only when a direct technical marker identifies that actor. Report causality is shown separately.
使用技術 · 6 identified
Detected via Cloudflare Radar · Wappalyzer engine
このドメインを報告する 証拠を提出し、他の人を守る手助けをしましょう

VirusTotalによる分析

4 / 89 セキュリティ ベンダーがこのドメインにフラグを立てました
View on VT
Last analyzed First positive detection Previous stored snapshot: 3 detections
alphaMountain.ai
Forcepoint ThreatSeeker
Gridinsoft
VIPRE
サイトパフォーマンス分析

Google PageSpeed Insights — mobile performance audit of goldangel.lol · checked Sep 15, 2026

36
Poor
Performance
FCP
1.35s
First Contentful Paint
LCP
13.51s
Largest Contentful Paint
CLS
0.218
Cumulative Layout Shift
TBT
1173ms
Total Blocking Time
SI
5.29s
Speed Index
Powered by Google PageSpeed Insights · Mobile strategy · Scores: 90-100 Good 50-89 Needs Work 0-49 Poor
Registration & observation details8

Availability observations

Last reachable observation
Outcome first observed
Observation window starts
Observation window ends
Estimated change time
Observation window · hours
353.95
Estimate basis
Bounded by observations
Estimate precision
Low

An estimated time describes an observation window. It does not prove a registrar action or the exact moment a site became unavailable.

Check for cloaking

Compare what a browser and a crawler receive, and check for Keitaro traffic routing.

goldangel.lol
保存済みの結果
到達不能
Stored observation history13

Dated changes retained by the monitor and source collectors. Newest observations appear first; source states are not proof of a takedown.

  1. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  2. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  3. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  4. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  5. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

Earlier observations 8
  1. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  2. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  3. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  4. Availability monitor · Recorded state

    不明→dns_inactive

    dns_nxdomain

  5. Availability monitor · Recorded state

    dns_inactive

    dns_nxdomain

  6. Availability monitor · Recorded state

    到達可能→利用不可

  7. VirusTotal · Detection count

    3→4

  8. Availability monitor · First collection record

    到達可能

Recorded activity

6 entries
  1. AlienVault OTX

    4 community references

    View source
  2. Google Safe Browsing

    No threat flag

    View source
  3. VirusTotal

    4/89 engine detections

    View source
  4. Abuse report sent

    PD-20260915-C7A6AF

    abuse@globaldomaingroup.com
  5. Added to PhishDestroy

    goldangel.lol

    View source
  6. URLScan

    Page captured

    View source

類似ドメイン

保存された類似ドメイン:79 件

すべて表示(67)
metasmask.io insertion 内部レポート metramask.io insertion 内部レポート mewtamask.io insertion 内部レポート mmetamask.io homoglyph 内部レポート mtamask.io omission 内部レポート mwetamask.io insertion 内部レポート nmetamask.io homoglyph 内部レポート metamark.io bitsquatting 内部レポート metamaskj.io addition 内部レポート metammask.io homoglyph 内部レポート metamnask.io homoglyph 内部レポート emtamask.io transposition m-etamask.io hyphenation meamask.io omission meatmask.io transposition meramask.io replacement mertamask.io insertion metaamask.io repetition metaamsk.io transposition metaask.io omission metalmask.io insertion metamaask.io insertion metamadsk.io insertion metamaek.io replacement metamak.io omission metamas.io omission metamasak.io insertion metamasdk.io insertion metamask-io.com various metamasl.io replacement metamasm.io replacement metamsak.io transposition metamsk.io omission metamusk.io vowel-swap metamzsk.io replacement metarnask.io homoglyph metmaask.io transposition metmask.io omission metsamask.io insertion metsmask.io replacement mettamask.io repetition metwmask.io replacement metyamask.io insertion metzmask.io replacement meyamask.io replacement meytamask.io insertion mitamask.io vowel-swap mnetamask.io homoglyph mretamask.io insertion mrtamask.io replacement mstamask.io replacement mteamask.io transposition mwtamask.io replacement rnetamask.io homoglyph matamask.io bitsquatting mdtamask.io bitsquatting metamasi.io bitsquatting metamasj.io bitsquatting metamaska.io addition metamaskk.io addition metamaskl.io addition metamaso.io bitsquatting metamesk.io bitsquatting metamqsk.io bitsquatting metemask.io bitsquatting netamask.io homoglyph xn--metamas-bhb.io homoglyph

証拠および外部報告書

送信済み証拠のスナップショット
Sent: Ledger records: 1 Case ID: PD-20260915-C7A6AF Recipient: abuse@globaldomaingroup.com
Page title stored with report: Get rewarded for the internet you don't use
PDF notice generated
詳細な分析
レポート
Help & reporting

このサイトによって何か影響を受けましたか?

6 evidence signal groups linked 1 stored notification records コンテンツが利用できません
If credentials were compromised, report immediately. Do not engage with recovery scammers.

このドメインを操作したり、個人情報を入力したり、暗号通貨ウォレットに接続したりした場合は、直ちに行動を起こしてください。インシデントを報告し、自分自身を守るのに役立つリソースを以下に示します。

Official reporting routes

復旧を装った詐欺に注意! 犯罪者は、捜査員、弁護士、または回収業者を装い、被害者に再び連絡を取る可能性があります。 前払い料金を支払ったり、資格情報を共有したりしないでください。 盗まれた暗号通貨の回復を保証できる正規のサービスはありません。 回復詐欺について詳しくはこちら →

お住まいの地域の当局へ報告してください

サイバー犯罪の公式連絡先 または 苦情草稿を作成する → を取得するには、国を選択してください。

97か国のディレクトリ

Template-based draft · optional AI wording assistance requires separate consent

AI 支援ドラフト — インシデントの詳細は AI プロバイダーによって処理されます · 自分で確認して送信する
After a phishing incident

被害者への推奨事項とアドバイス

Choose the steps that match what you shared. Keep a copy of this report alongside your own records.

推定では $51 billion 2024年に違法な暗号資産ウォレットへと流出した(source). もしあなたが goldangel.lol — 今すぐ行動しましょう。

Wallet-specific steps below apply if you connected a wallet, signed a transaction, or exposed a wallet secret.

今すぐ何をすべきでしょうか?

至急

Stop using the suspicious site. Open the real service through its official app or an address you already trust.

  • トークンの承認を取り消す — use revoke.cash 悪意のあるスマートコントラクトに付与されたアクセス権を取り消す
  • 残りの資金を移動する まったく新しいウォレットへ。セキュリティが侵害されたウォレットは、もはや安全ではありません
  • すべてのパスワードを変更する — メール、Exchangeアカウントなど、同じパスワードを使用しているものすべて
  • 2段階認証を有効にする 認証アプリ(SMSではない)を使用する。SMSによる復旧機能を無効にする
  • カードの凍結 フィッシングサイトに銀行口座情報を入力してしまった場合

レポート作成のために、どのような情報を収集すべきでしょうか?

FBIのガイドライン

によると、 FBI、最も重要な詳細はトランザクションデータです:

  • Payment records — if you paid, save the receipt, amount, date, payment provider and recipient details.
  • 仮想通貨アドレス — 詐欺師の財布(例: 0x5856...35985)
  • 金額および仮想通貨の種類 — 正確な金額(例:1.02345 ETH、0.5 BTC、500 USDT)
  • トランザクションID(ハッシュ) — ブロックチェーン上の取引を識別するための固有の識別子
  • 正確な日時 — 各取引および詐欺師との最初の接触について
  • スクリーンショット — 詐欺サイト、チャットメッセージ、メール、ウォレットでの取引、ソーシャルメディア
  • すべてのURLおよびドメイン 詐欺師が使用した(以下を含む) goldangel.lol)
  • コミュニケーション — 詐欺師が使用したメール、テキストメッセージ、電話番号、ユーザー名

たとえすべての詳細がわかっていなくても―― とにかく報告を提出する. 不完全な情報であっても、捜査には役立つ。

この詐欺はどこに通報すればいいですか?

  • FBI IC3 — インターネット犯罪通報センター(米国連邦政府の通報窓口)
  • ユーロポール — 欧州におけるサイバー犯罪の報告(EU)
  • Chainabuse — 取引所やプラットフォーム間で詐欺ウォレットを特定する
  • あなたの仮想通貨取引所 — notify its fraud team immediately; it may be able to preserve records or restrict funds held on its platform
  • Your bank or payment provider — contact its fraud team promptly through official contact details if money or card information was exposed.
  • 地元の警察 — たとえ直ちに行動を起こせなくても、公式な記録が残される

A report is not a guarantee of recovery or investigation, but prompt, accurate transaction data can help authorities and service providers trace the incident.

仮想通貨詐欺は通常、どのような手口で行われるのでしょうか?

  • 偽のウェブサイト — 正規サイトのドメインをわずかに変更した、ピクセル単位で完璧に再現されたクローンサイト
  • 悪意のある承認 — 「connect wallet」というプロンプトが表示されると、攻撃者にトークンの無制限な使用権限が与えられてしまう
  • pig butchering — TelegramやWhatsApp、出会い系アプリを通じて数週間にわたって信頼関係を築き、その後、金銭をだまし取られる
  • 詐欺による金銭の返還を装った詐欺 — fraudsters pose as recovery agents and demand upfront fees. Never share a seed phrase or pay before independently verifying the provider
  • 偽の広告とエアドロップ — Googleやソーシャルメディアの広告、および「無料トークン」のオファーが、財布を空にするようなアプリへと誘導している
  • AIを利用した詐欺 — ディープフェイク、自動化されたフィッシング、AI生成サイトにより、詐欺の発見が難しくなっている

今後、どうすれば身を守ることができるでしょうか?

  • ハードウェアウォレットを使用する (Ledger、Trezor)。ブラウザウォレットには決して多額の資産を保管しないでください
  • 公式サイトをブックマークする — メール、DM、広告に含まれるリンクは絶対にクリックしないでください
  • すべての承認内容を確認する — 署名する前に権限を確認してください。無制限の承認は拒否してください
  • ドメインの確認 — 確認する PhishDestroy 操作を行う前に、HTTPS、スペル、ドメインの登録期間を確認してください。
  • 「良すぎて怪しい」=詐欺 — 確実なリターン、有名人の推薦、差し迫った締め切り

Further guidance: NIST · phishing responseFBI IC3 · reports & evidenceFTC · recovery scams

最新情報を入手し、安全を確保しましょう

リアルタイムの脅威を監視するか、誤検知だと思われる場合はこのリストに異議を申し立ててください

リアルタイム脅威情報フィード この掲載情報について異議を申し立てる
About this reportSources, observation dates and corrections

This report combines saved page captures, registration and network records, scanner results and PhishDestroy reporting history. Each source keeps its own observation date. Open a source report to inspect the original result.

The AI-assisted analysis was written on . It describes the evidence available at that time; later source checks can change.

A capture documents what was shown. A scanner result records that provider’s assessment at the time of its check. Neither a valid certificate nor a zero-detection result is a guarantee of safety.

Embed this reportA compact widget with a link to the evidence
HTML · IFRAME

このレポートを埋め込む

この脅威情報を、ご自身のウェブサイトやブログで共有してください

embed.html
<iframe
  src="https://phishdestroy.io/ja/embed/domain/goldangel.lol"
  title="PhishDestroy threat report for goldangel.lol"
  width="100%" height="320"
  loading="lazy"
  referrerpolicy="no-referrer"
  sandbox="allow-same-origin allow-popups allow-popups-to-escape-sandbox"
  style="border:0;border-radius:12px;max-width:100%"
></iframe>